
CVE-2025-25614
 armaansidana2003/cve-2025-25614
Proof-of-concept exploit for CVE-2025-25614, an incorrect access control vulnerability in Unifiedtransform v2.0 allowing teachers to modify fellow…
exploitationmisconfigurationpenetration-testing+3
armaansidana2003/cve-2025-25614Proof-of-concept exploit for CVE-2025-25614, an incorrect access control vulnerability in Unifiedtransform v2.0 allowing teachers to modify fellow…
 armaansidana2003/cve-2025-25616
Proof-of-concept demonstrating incorrect access control in Unifiedtransform v2.0, allowing students to modify exam rules via the /exams/edit-rule…
 spbavarva/cve-2025-46203
PoC of CVE-2025-46203
 nightwatchcybersecurity/truegaze
Static analysis tool for Android/iOS apps focusing on security issues outside the source code
 xuwu-xuwu/cve-2026-68004
Standalone PoC for unauthenticated RTMP publish in SRS media servers; verifies the vulnerability, supports HTTP API side-channel check, and enables…
 stampery/mongoaudit
🔥 A powerful MongoDB auditing and pentesting tool 🔥
 firefart/stunner
Test and exploit STUN/TURN servers for misconfigurations, enabling internal network pivoting via SOCKS proxy, memory leak attacks, and internal port…
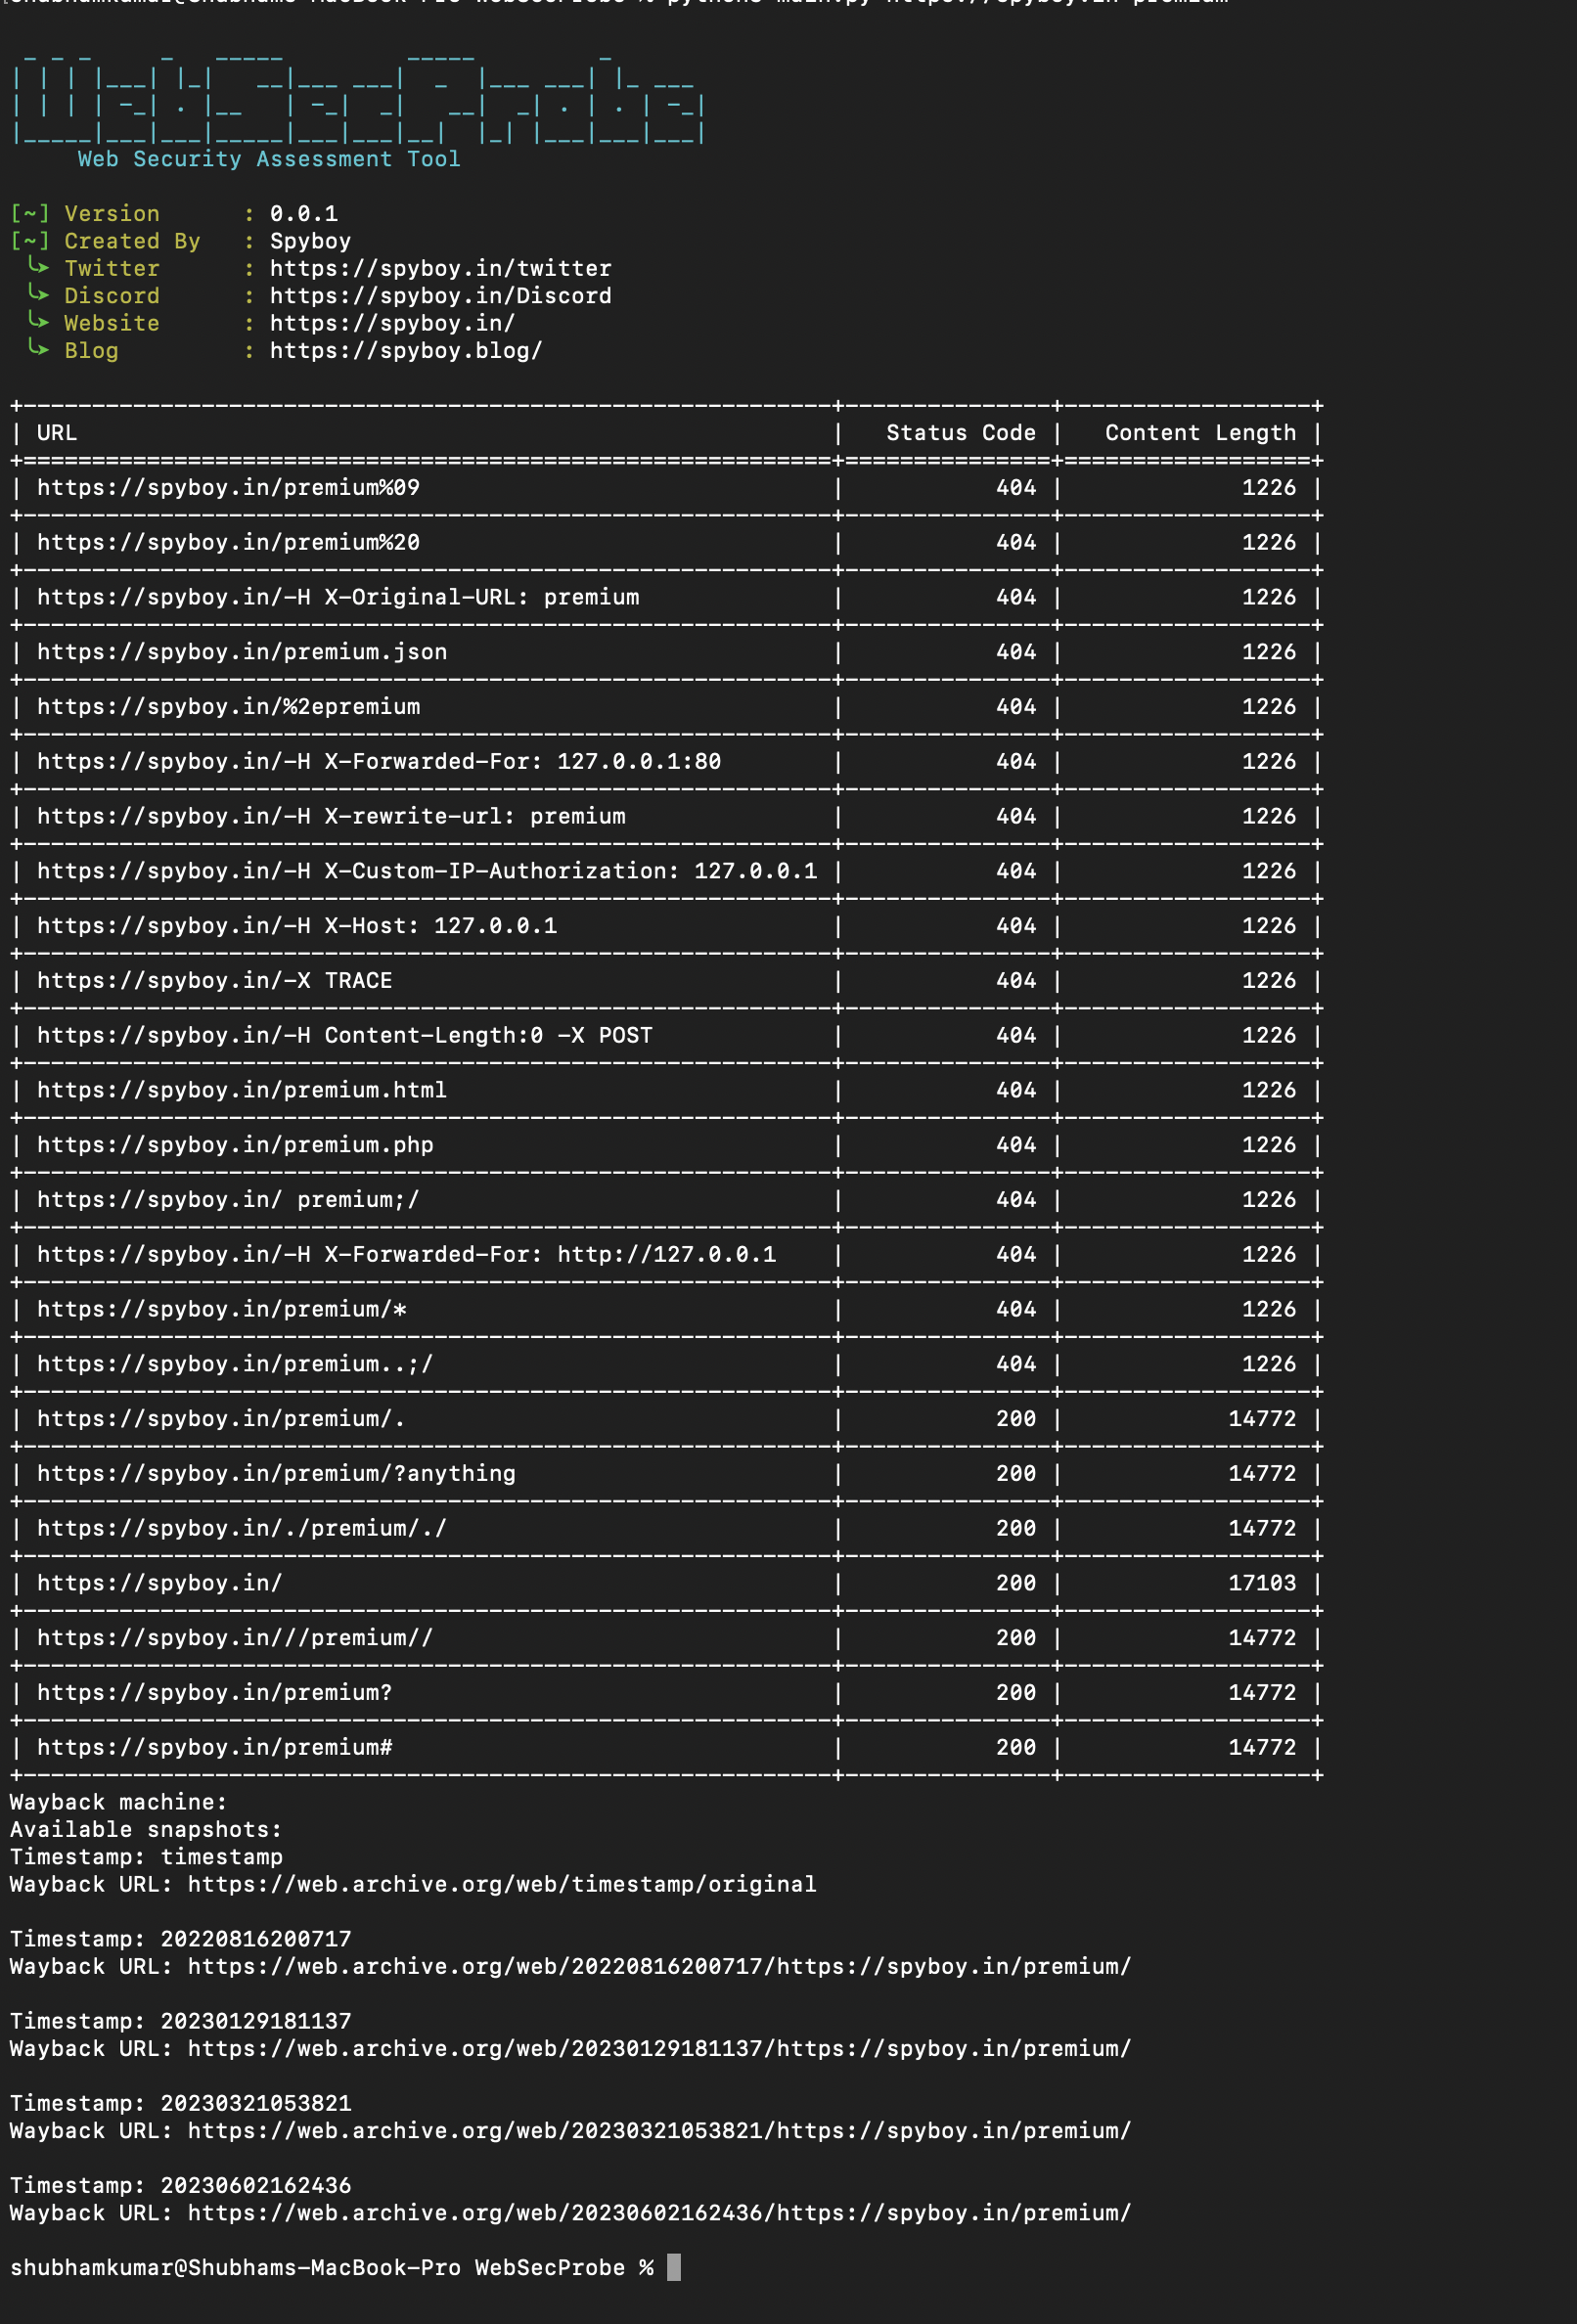 spyboy-productions/websecprobe
Security testing tool for analyzing HTTP 403 responses and identifying access control misconfigurations in web applications.
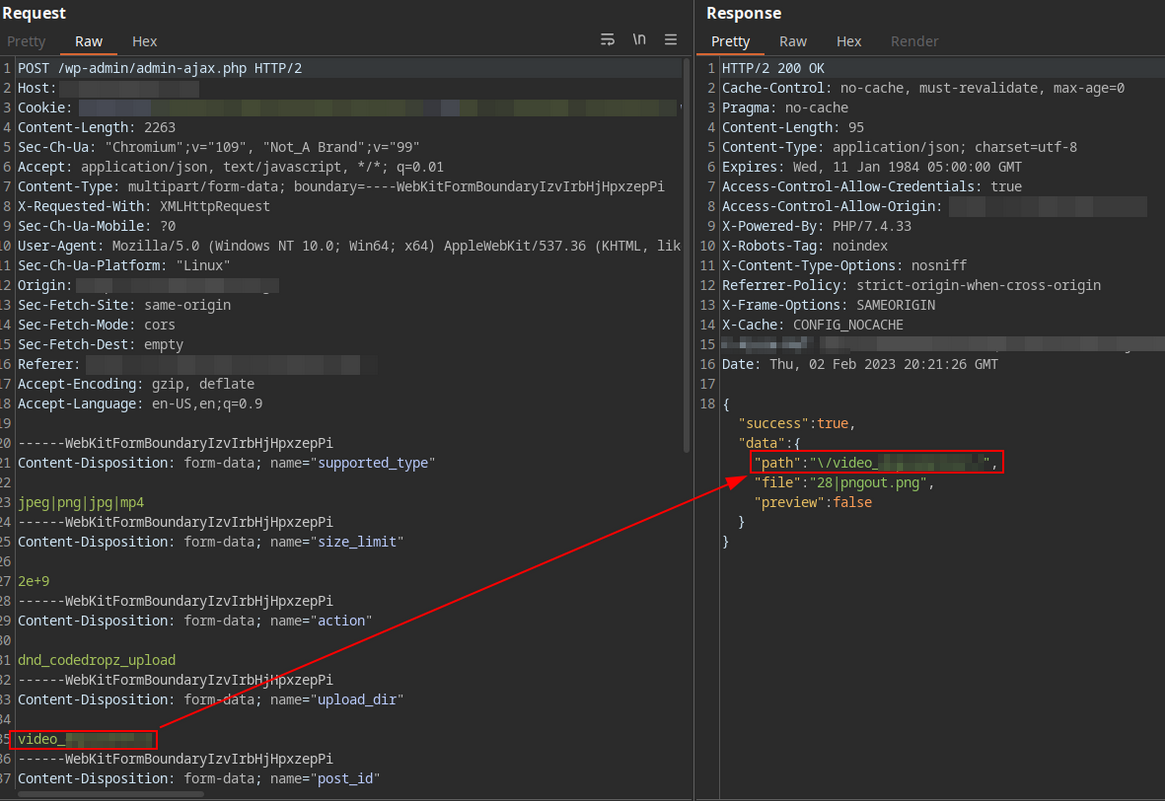 nickguitar/drag-and-drop-multiple-file-uploader-pro-path-traversal
Drag and Drop Multiple File Uploader PRO - Contact Form 7 v5.0.6.1 Path Traversal (CVE-2023-1112)
 d3n14ld15k/cve-2024-11680_poc_exploit
This repository contains a Proof of Concept (PoC) exploit for CVE-2024-11680, a critical vulnerability in ProjectSend r1605 and older versions. The…
 unix13/metasploitable2
PHP-CGI-REMOTE_CVE-2012-1823, UnrealIRCd, MySQL, PostgreSQL and SSH bruteforce, VSFTPD2.3.4, samba CVE-2007-2447, JAVA RMI Server, distcc daemon,…
 xiaoxiaoranxxx/cve-2025-56815
Datart 1.0.0-rc.3 is vulnerable to Directory Traversal in the POST /viz/image interface, since the server directly uses MultipartFile.transferTo() to…
 comparedarray/printix-cve-2022-25089
An "Incorrect Use of a Privileged API" vulnerability in PrintixService.exe, in Printix's "Printix Secure Cloud Print Management", Version 1.3.1106.0…
 comparedarray/printix-cve-2022-29552
A "Incorrect Use of Privileged APIs" vulnerability in PrintixService.exe, in Kofax Printix's "Printix Secure Cloud Print Management", Version…
 sanupl/cve-2021-46075
CVE-2021-46075 - A Privilege Escalation vulnerability exists in Sourcecodester Vehicle Service Management System 1.0. Staff account users can access…
 kaleth4/cve-2026-5465
Exploit and analysis for CVE-2026-5465, an IDOR in Amelia WordPress plugin allowing authenticated Provider role to escalate privileges and achieve…
 gregk4sec/cve-2025-31651
Original CVE-2025-31651 disclosure with proof-of-concept exploit for Apache Tomcat rewrite rule bypass. Includes technical analysis, reproduction…
 sibikrish001/cve-2025-55462
Technical documentation and proof-of-concept for CVE-2025-55462, a CORS misconfiguration in Eramba v3.26.0 allowing cross-origin authentication…