
CVE-2023-22515
 kh4sh3i/cve-2023-22515
CVE-2023-22515 - Broken Access Control Vulnerability in Confluence Data Center and Server
exploitationinformation-gatheringmisconfiguration+3
6
kh4sh3i/cve-2023-22515CVE-2023-22515 - Broken Access Control Vulnerability in Confluence Data Center and Server
 ricardojoserf/cve-2019-19033
CVE-2019-19033 description and scripts to check the vulnerability in Jalios JCMS 10 (Authentication Bypass)
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
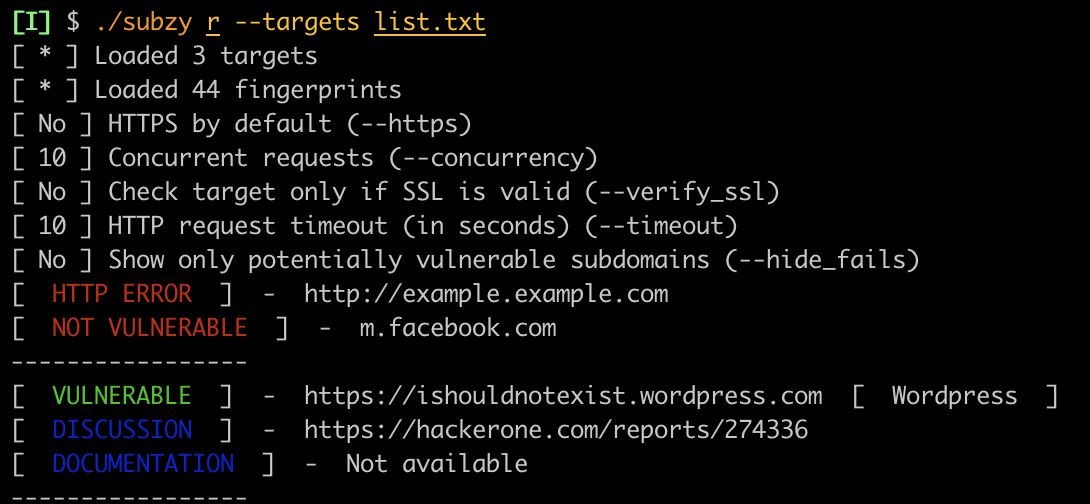 pentestpad/subzy
Subdomain takeover vulnerability checker
 owasp/joomscan
Perl-based Joomla CMS vulnerability scanner automating version enumeration, component detection, exploit matching, firewall identification, and…
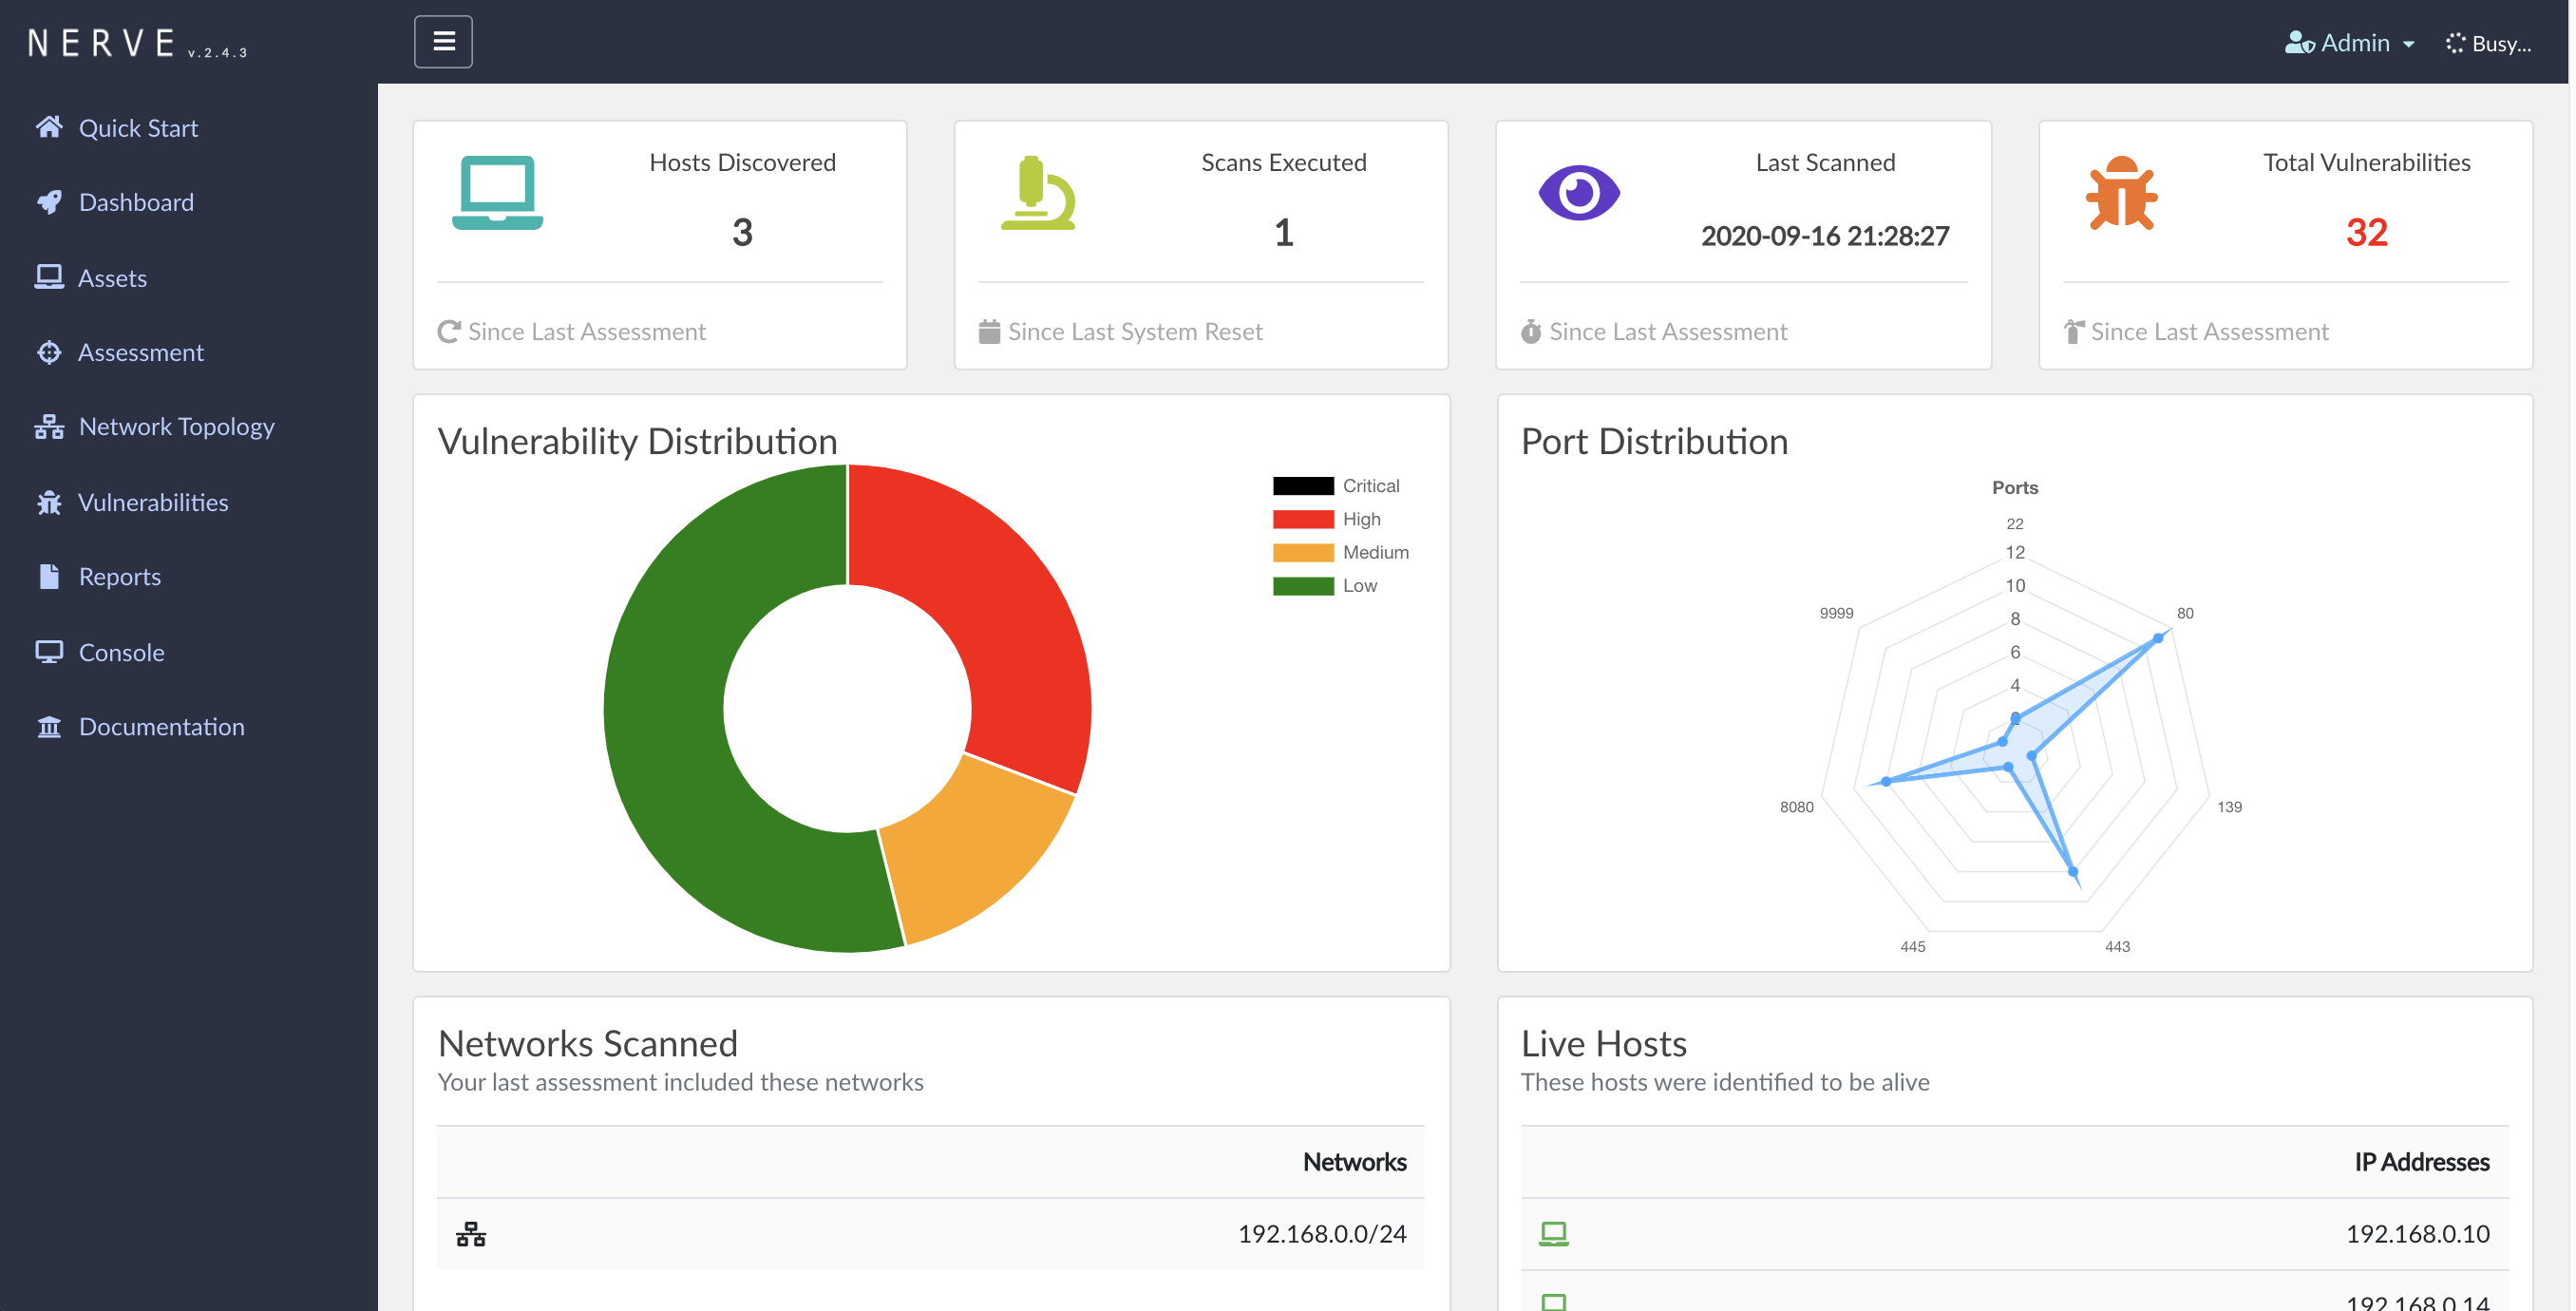 paytmlabs/nerve
NERVE Continuous Vulnerability Scanner
 bitthebyte/eagle
Multithreaded Plugin based vulnerability scanner for mass detection of web-based applications vulnerabilities
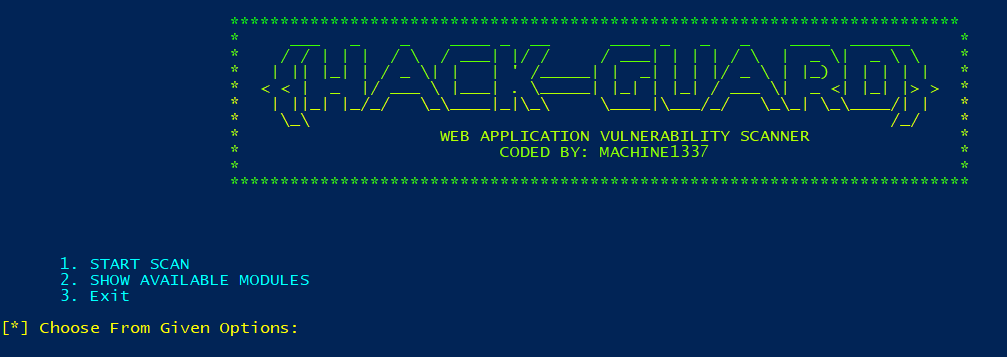 machine1337/hackguard
FAST WEB APPLICATION VULNERABILITY SCANNER written in python3
 xiaojiangxl/cve-2021-21234
Proof-of-concept exploit for CVE-2021-21234, a directory traversal vulnerability in spring-boot-actuator-logview allowing unauthorized file read via…
 stolichnayer/cve-2025-22828
Apache CloudStack vulnerability allows unauthorized access to annotations on certain resources.
 redteambrasil/cve-2020-24029
Detailed disclosure of an unauthenticated password change vulnerability in ForLogic Qualiex v1 and v3, enabling remote privilege escalation and…
 simeononsecurity/cve-2020-1350-fix
A registry-based workaround can be used to help protect an affected Windows server, and it can be implemented without requiring an administrator to…
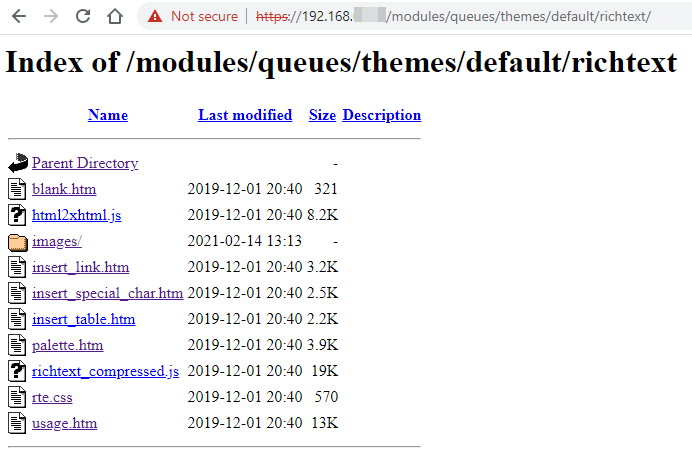 sahiloj/cve-2023-37599
Issabel-pbx version 4.0.0-6 contains a Broken Access Control vulnerability that manifests as unauthenticated Directory Listing on the web interface.
 unicorn-hyh/cve-2026-31156
There is a path injection vulnerability in OpenPLC-v3, which arises from the program not performing any validity checks on the file path parameters…
 jasetpen/cve-2025-69428
A critical access control vulnerability in locally deployed Pro-Bit application in versions less than v1.77.4 allows unauthenticated attackers to…
 josephgodwinkimani/cloudpanel-2.4.2-cve-2024-44765-recovery
How to "recover" a CloudPanel server affected by the CVE-2024-44765 vulnerability
 h1thub/cve-2024-46635
Proof-of-concept for CVE-2024-46635: an improper input validation vulnerability in GongZhiDao System's API endpoint that exposes sensitive user…
 0xdeku/cve-2021-42671
CVE-2021-42671 - Broken access control vulnerability in the Engineers online portal system.