
lynis
 cisofy/lynis
Agentless security auditing tool for Linux, macOS, and UNIX systems. Performs in-depth scans for vulnerabilities, configuration issues, and…
configuration-auditingdatabase-securitydefensive-tools+5
16.5k
cisofy/lynisAgentless security auditing tool for Linux, macOS, and UNIX systems. Performs in-depth scans for vulnerabilities, configuration issues, and…
 rhinosecuritylabs/cloudgoat
CloudGoat is Rhino Security Labs' "Vulnerable by Design" AWS deployment tool
 th3xace/sudo_killer
A tool designed to exploit a privilege escalation vulnerability in the sudo program on Unix-like systems. It takes advantage of a specific…
 nightwatchcybersecurity/truegaze
Static analysis tool for Android/iOS apps focusing on security issues outside the source code
 gensecaihq/cve-2024-3094-vulnerability-checker-fixer
Shell script and Ansible playbook to detect and remediate CVE-2024-3094 in xz-utils by checking package versions, upgrading or downgrading to a…
 mattaperkins/fix-cve-2024-2961
Quick mitigation script
 jimywork/djangohunter
Tool designed to help identify incorrectly configured Django applications that are exposing sensitive information.
 firefart/stunner
Test and exploit STUN/TURN servers for misconfigurations, enabling internal network pivoting via SOCKS proxy, memory leak attacks, and internal port…
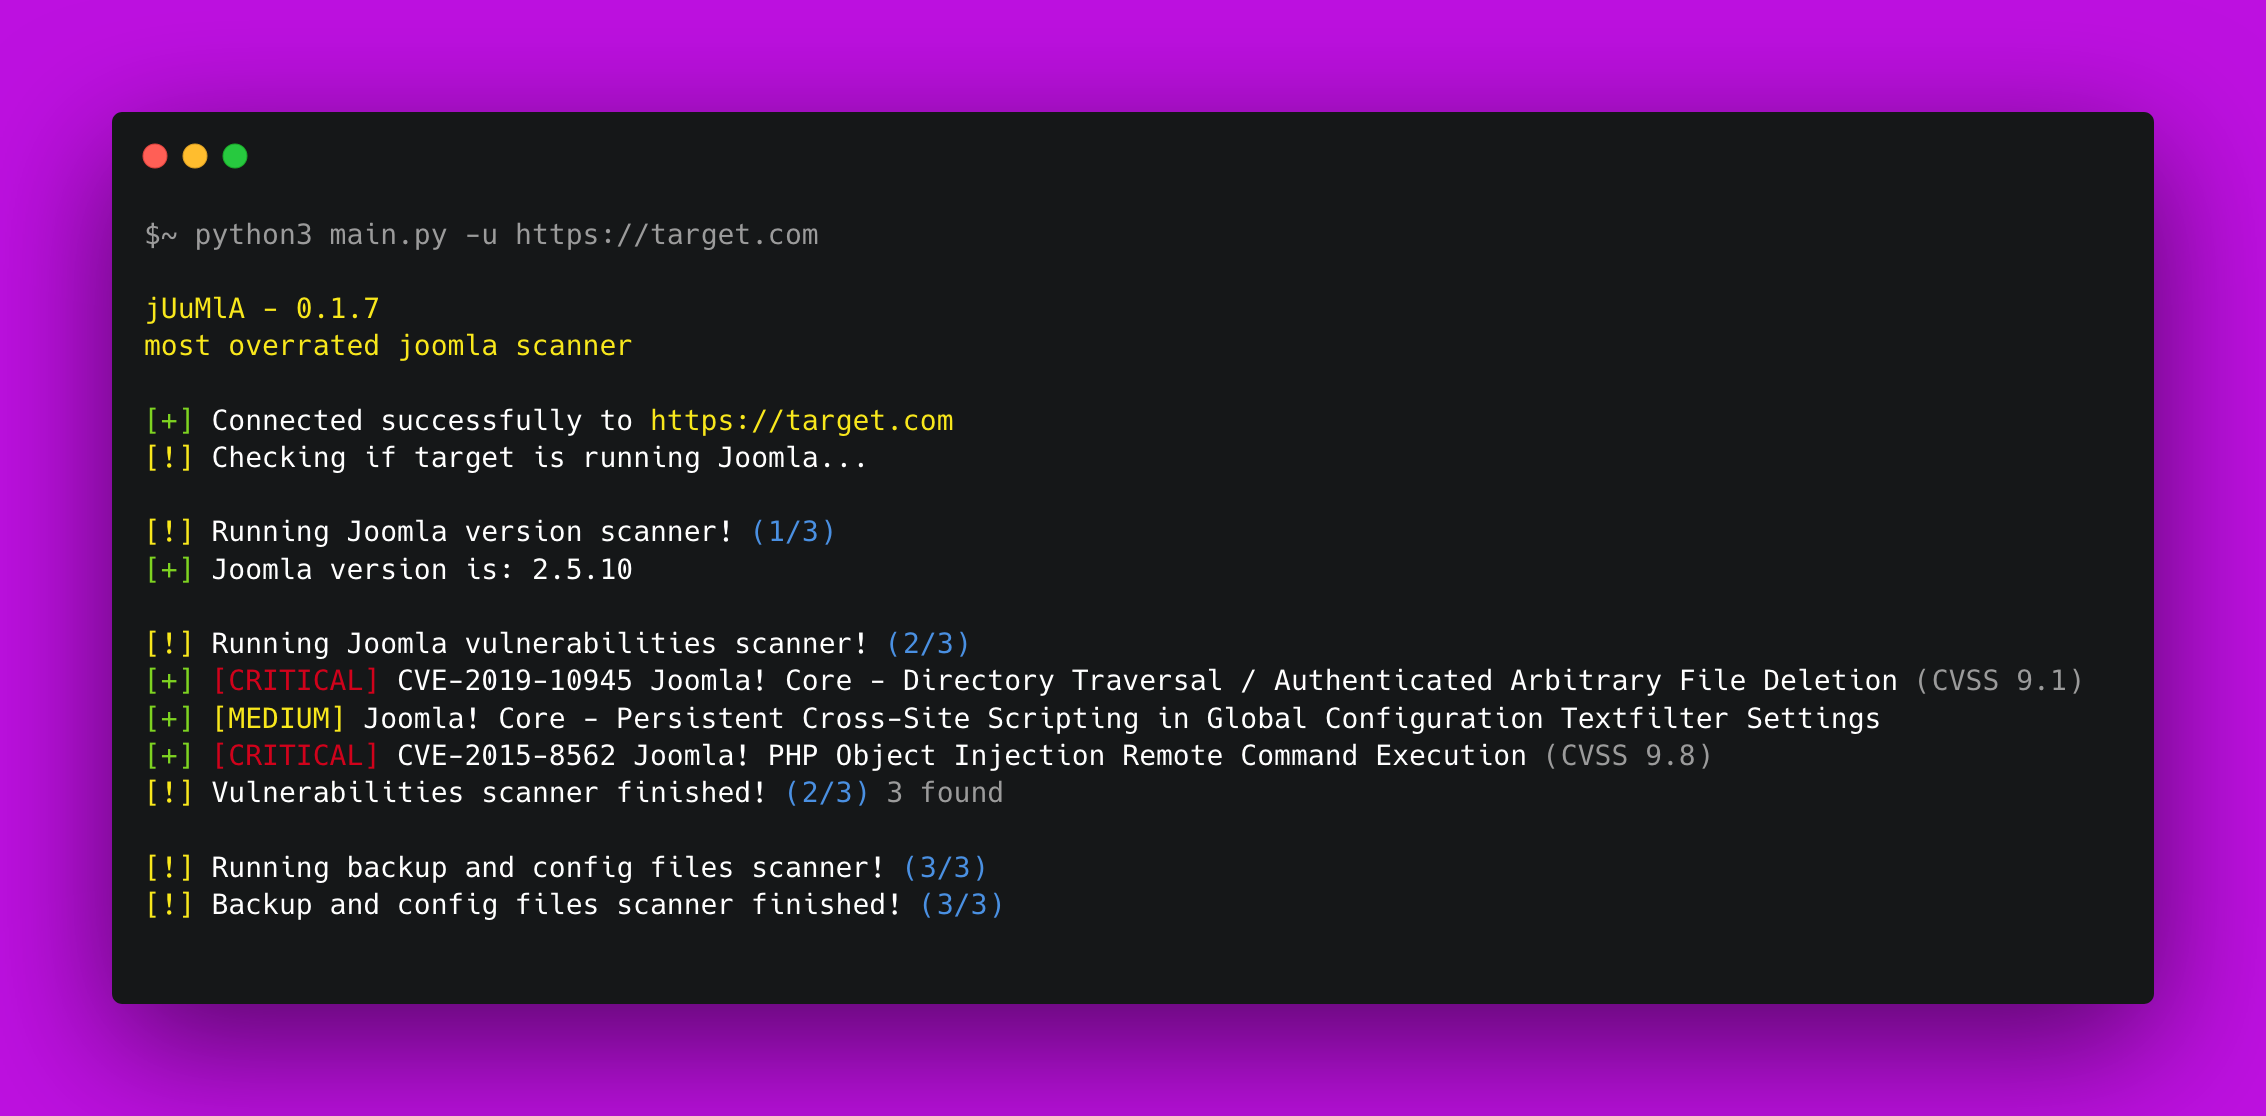 0xdsm/juumla
🦁 Python project to identify and scan for vulnerabilities related to the Joomla CMS project. It scans for common misconfigurations and public…
 cyberark/kubiscan
A tool to scan Kubernetes cluster for risky permissions
 funoverip/mcafee-sitelist-pwd-decryption
Password decryption tool for the McAfee SiteList.xml file
 6mile/gimmepatz
Personal Access Token (PAT) recon tool for bug bounty hunters, pentesters & red teams
 synacktiv/kcmapper
KcMapper is a security auditing tool for Keycloak. It exports your Keycloak configuration (realms, clients, users, roles, etc.) into a Neo4j graph…
 spring-io/cve-2022-22976-bcrypt-skips-salt
CLI tool to detect and update BCrypt password hashes with vulnerable work factor 31, integrating with Spring Security databases for CVE-2022-xxxx…
 sudo-wp/sudowp-adminer
A secure, zero-trust database management tool for WordPress. Fixes critical SSRF vulnerabilities (CVE-2021-21311) by enforcing local connections only.
 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
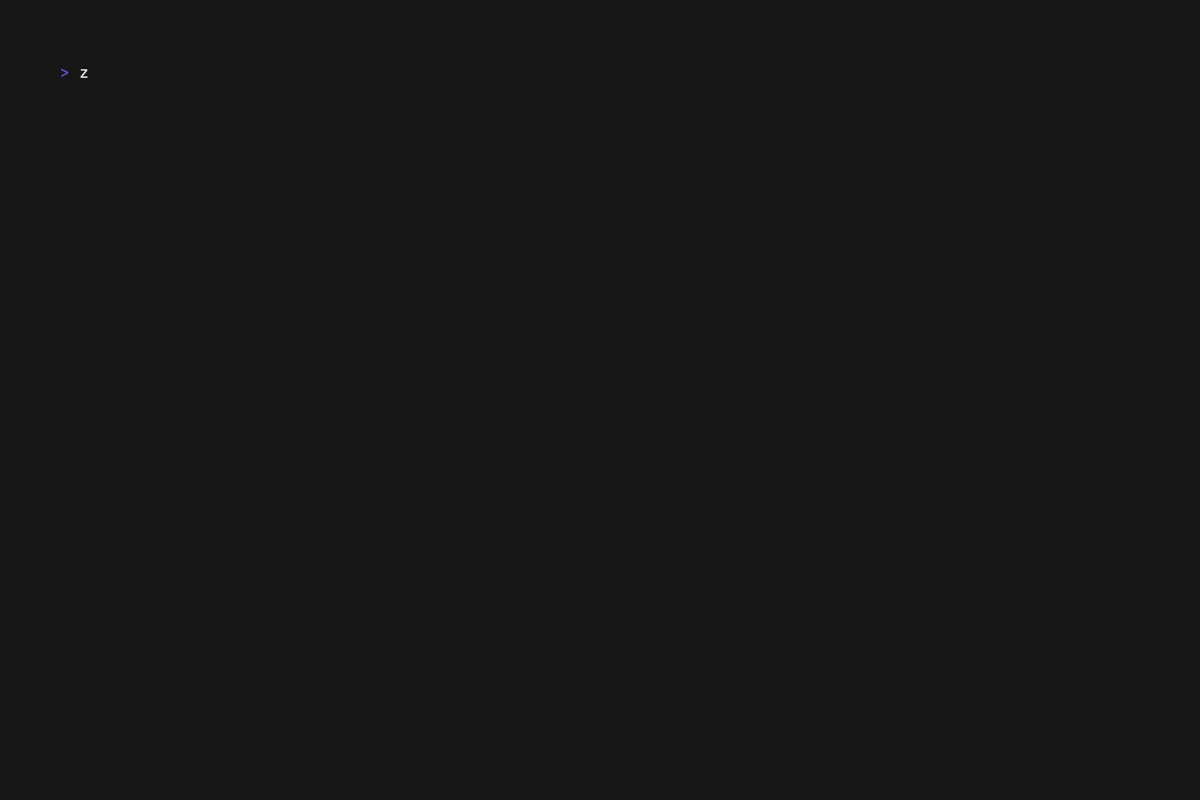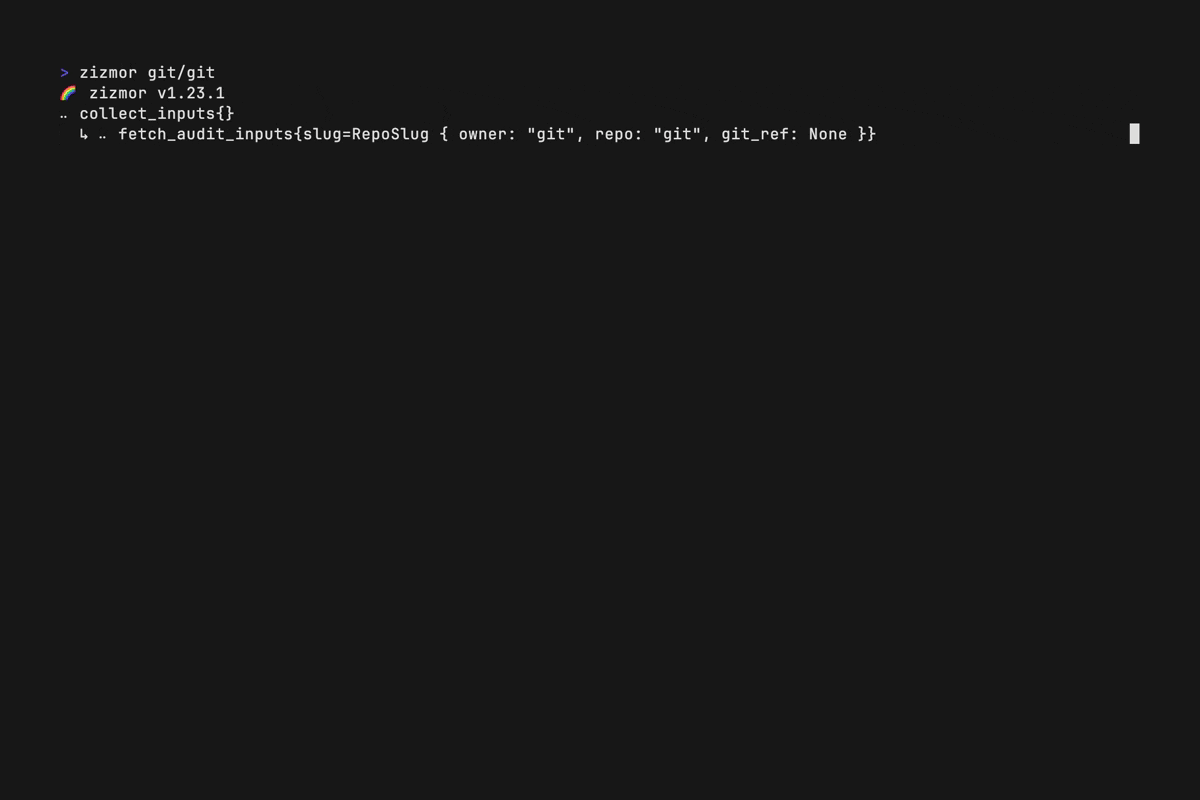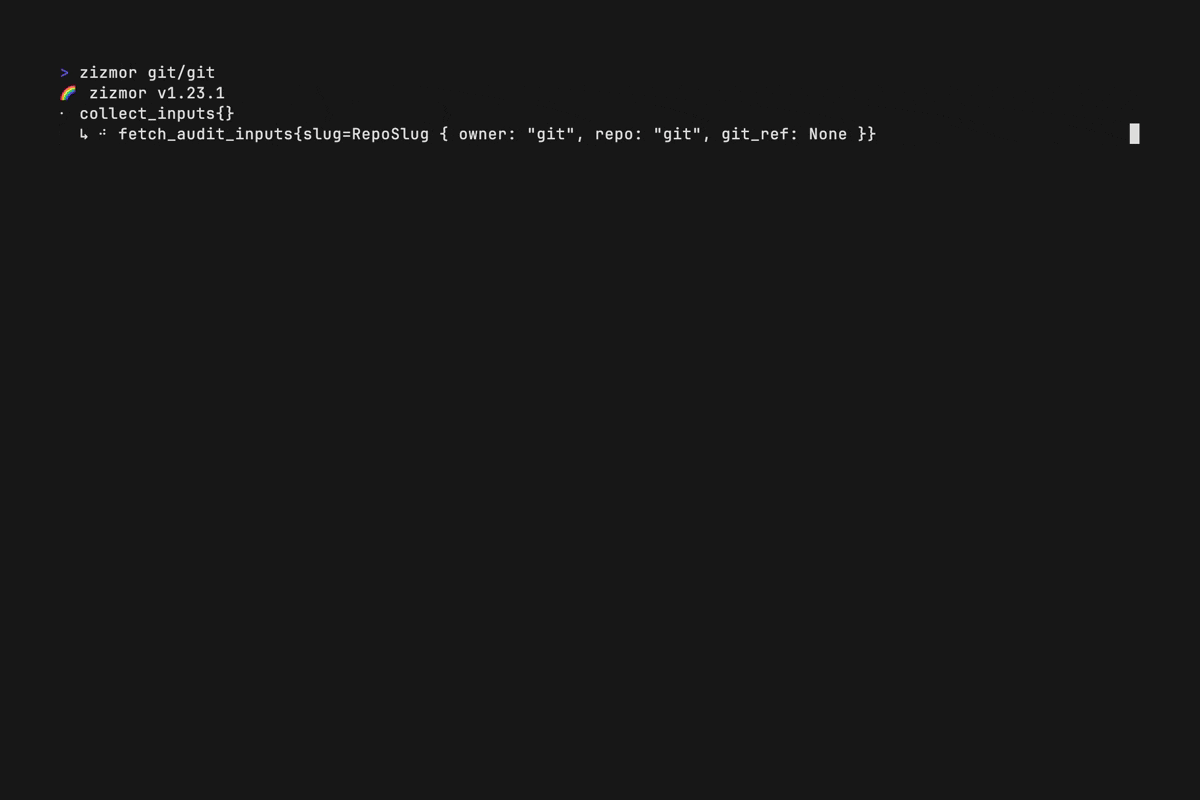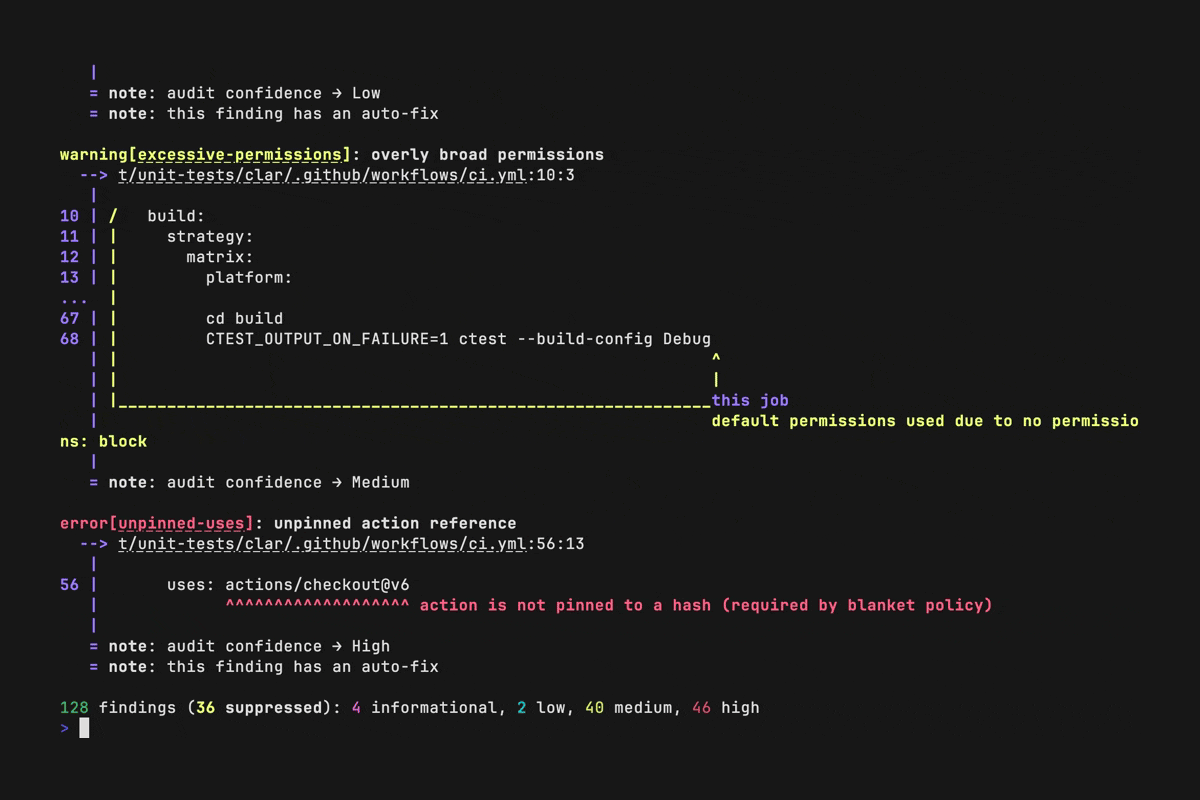 zizmorcore/zizmor
Static analysis tool for CI/CD systems that detects and fixes security issues in GitHub Actions, Dependabot, and pre-commit configurations, including…
 nccgroup/scoutsuite
Multi-cloud security auditing tool that leverages cloud provider APIs to gather configuration data, assess security posture, and generate HTML…