

coraza
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
api-securityapi-security-testingdefensive-tools+7
3.9k
corazawaf/corazaGo-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
 coreruleset/coreruleset
Generic attack detection rule set for web application firewalls, protecting against OWASP Top Ten and common vulnerabilities with minimal false…
 nozaq/terraform-aws-secure-baseline
Terraform module to set up your AWS account with the secure baseline configuration based on CIS Amazon Web Services Foundations and AWS Foundational…
 maxwitat/cve-2023-36884-scripts-for-intune-remediation-sccm-compliance-baseline
The remediation script should set the reg entries described in https://msrc.microsoft.com/update-guide/vulnerability/CVE-2023-36884 . The detection…
 abraxas/sonic-gnmi-noauth
Documents and reproduces a fail-open authentication flaw in SONiC gNMI where an empty UserAuth map allows unauthenticated gNMI Set and gNOI writes,…
 irgoncalves/f5-waf-quick-patch-cve-2021-44228
This tool creates a custom signature set on F5 WAF and apply to policies in blocking mode
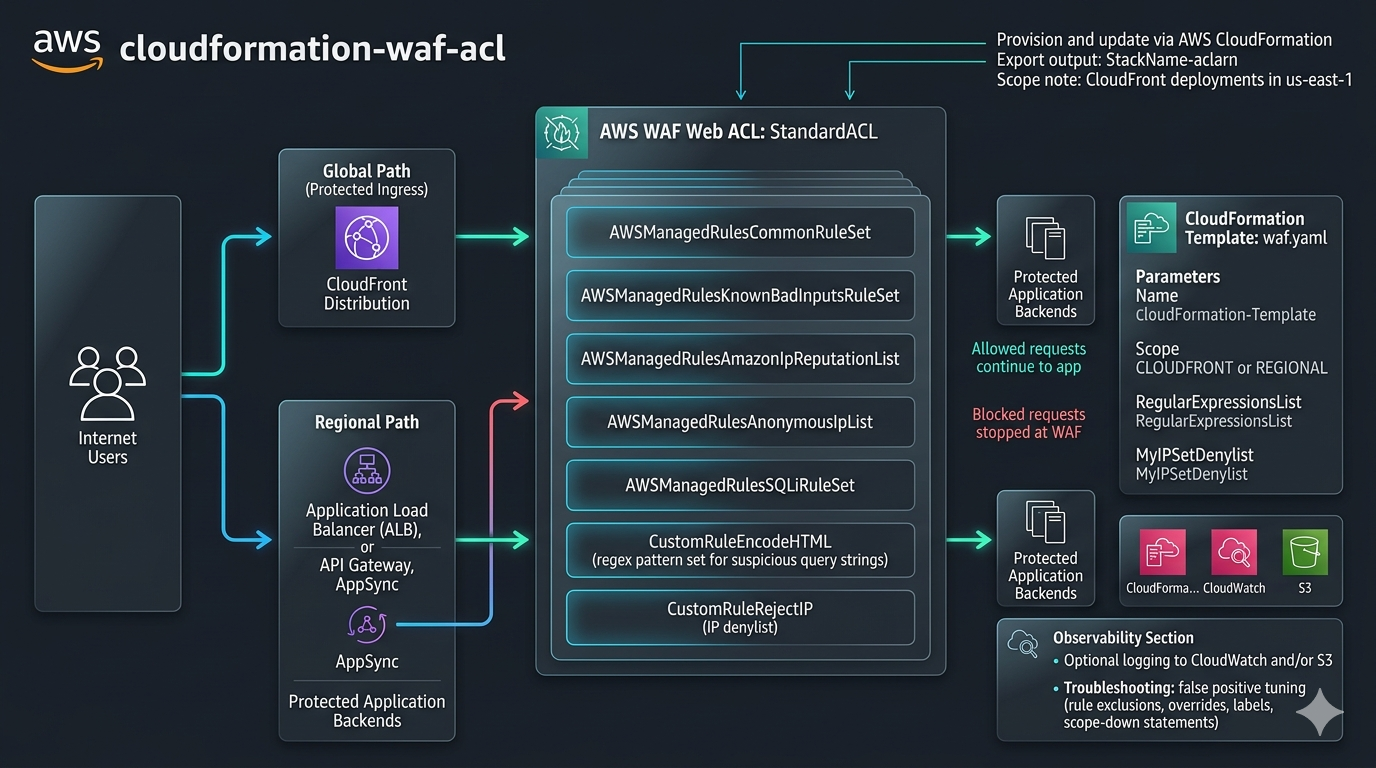
 fer1035_aws/cloudformation/cloudformation-waf-acl
An AWS CloudFormation template used to provision and manage AWS WAFv2 resources, including a Web ACL, managed rule groups, a custom regex pattern…
 syntaxbearror/powershell-printnightmare
A collection of scripts to help set the appropriate registry keys for CVE-2021-34527
 spiderlabs/owasp-modsecurity-crs
OWASP ModSecurity Core Rule Set (CRS) Project (Official Repository)
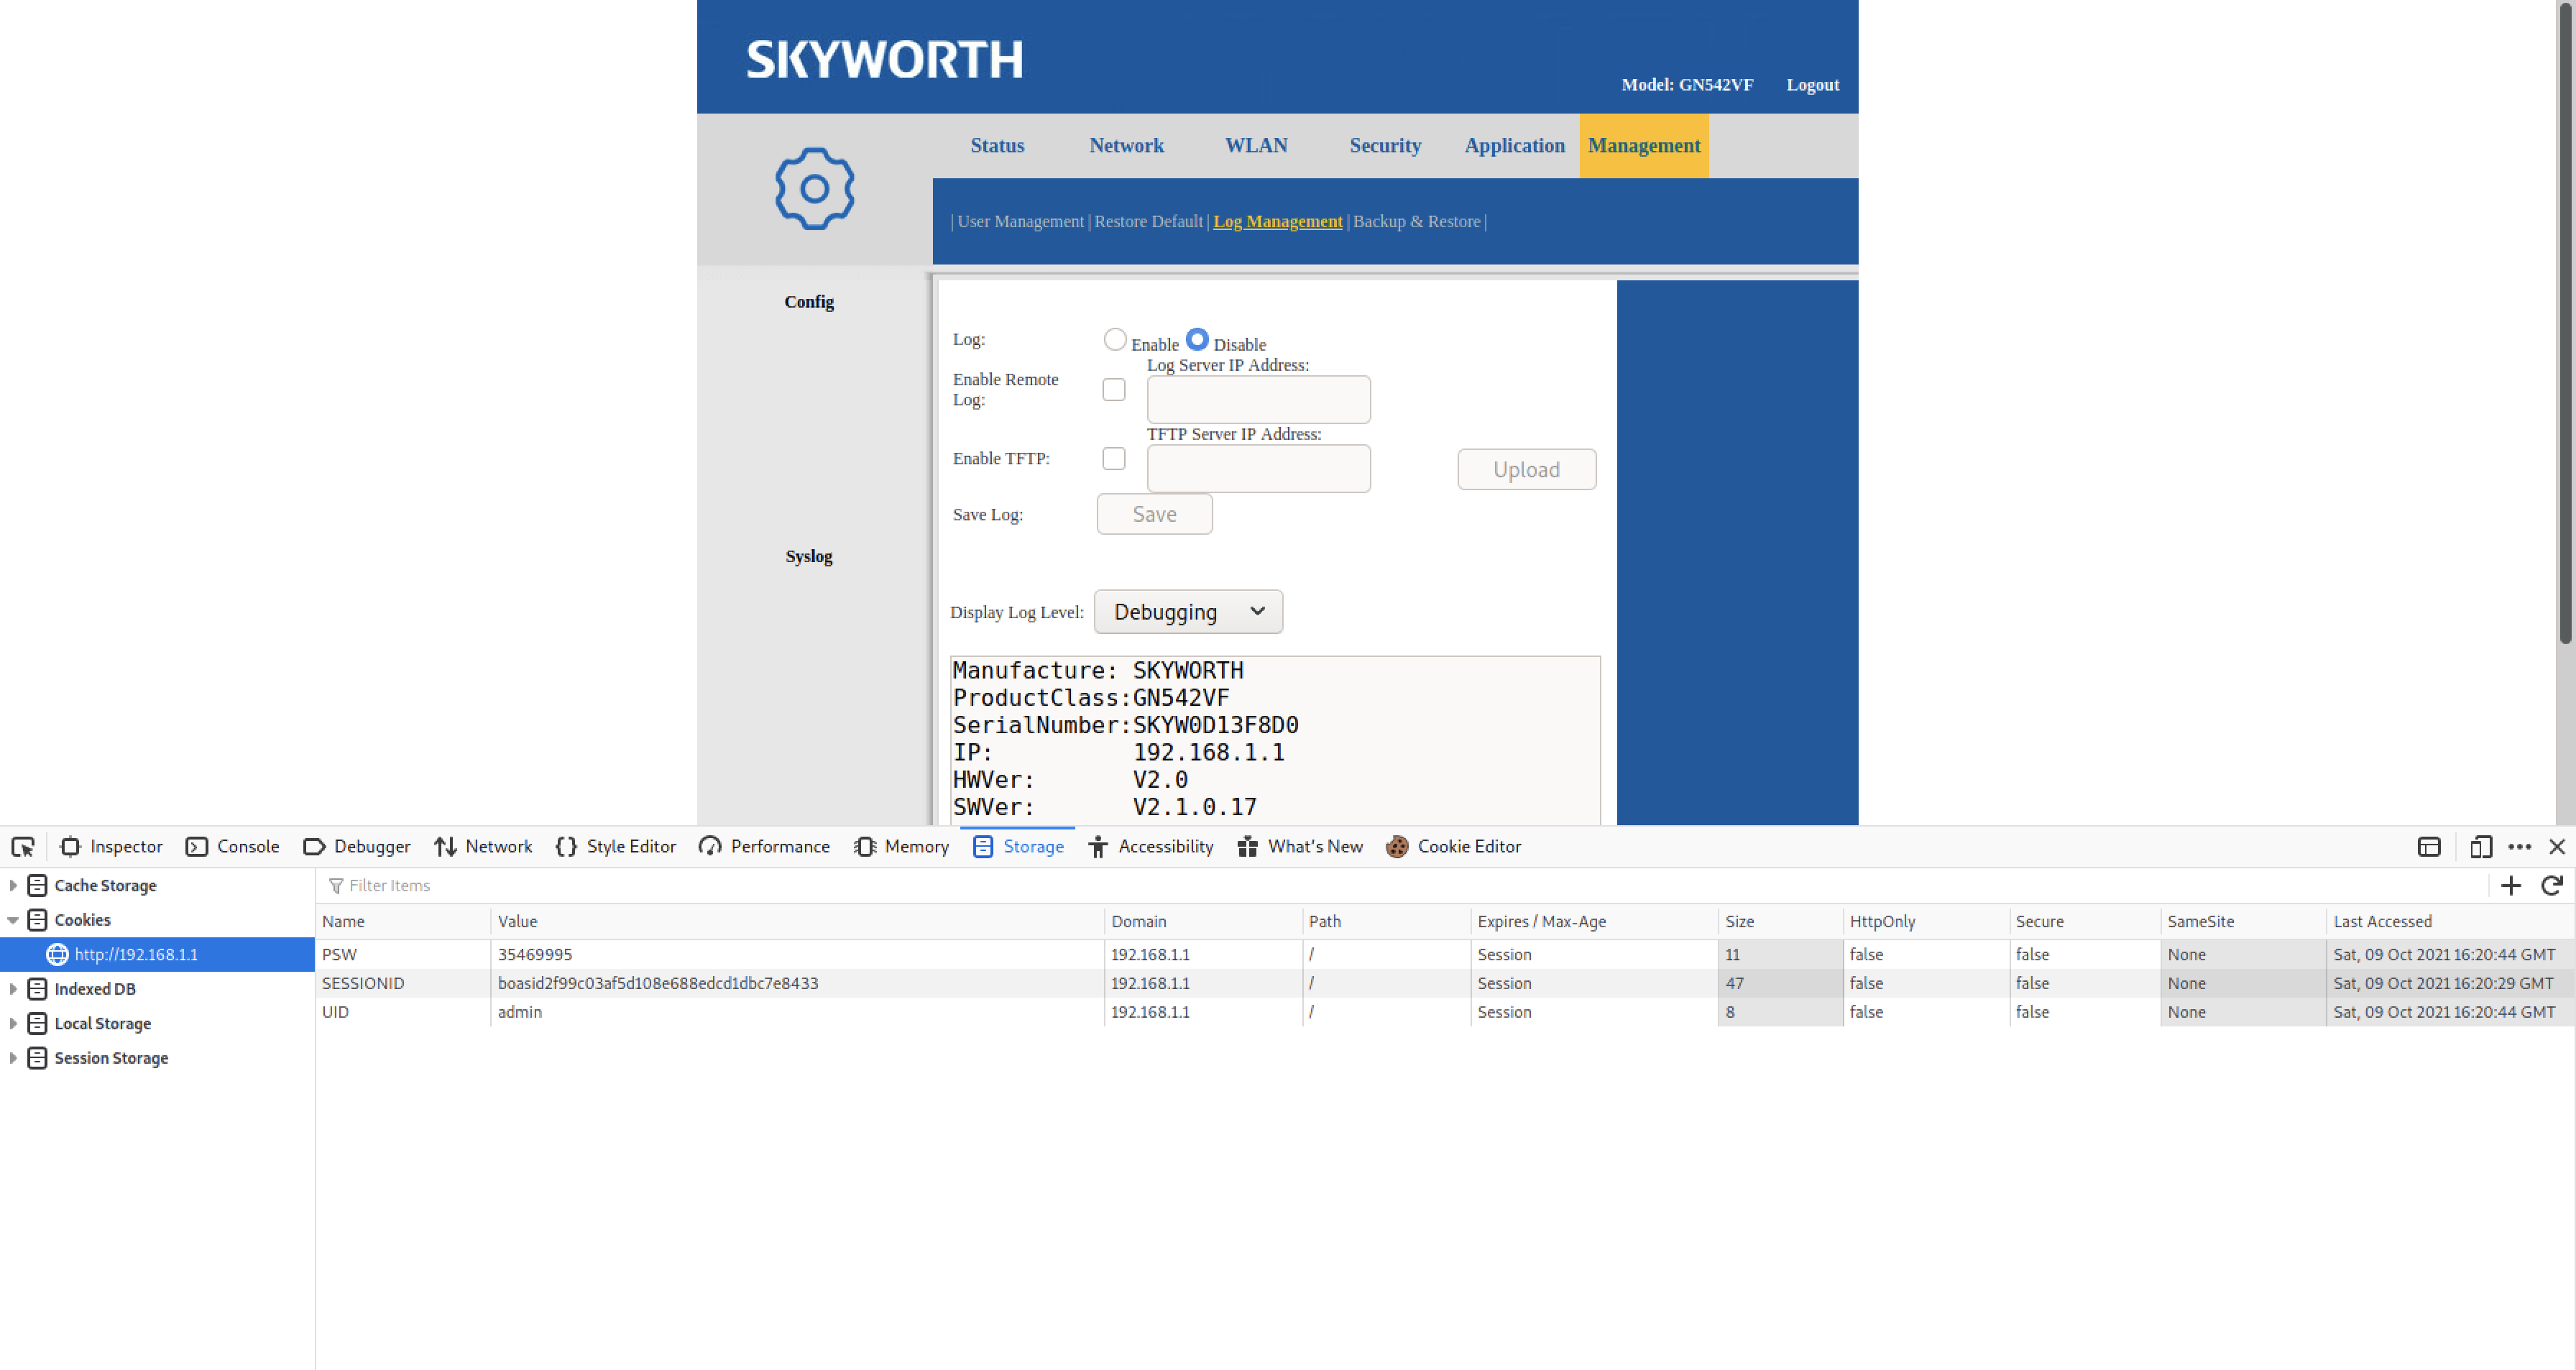 swzhouu/cve-2020-26732
SKYWORTH GN542VF Hardware Version 2.0 and Software Version 2.0.0.16 does not set the Secure flag for the session cookie in an HTTPS session
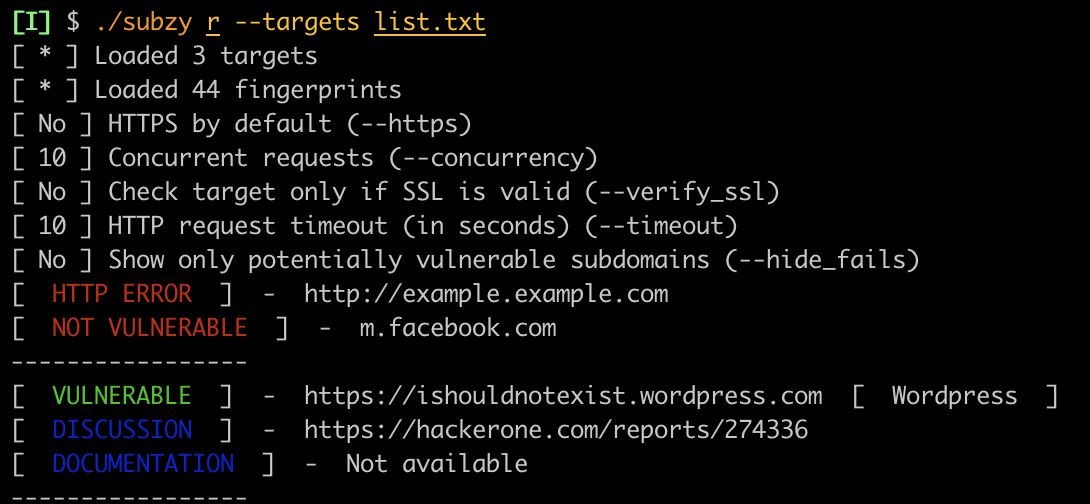 pentestpad/subzy
Subdomain takeover vulnerability checker
 olafhartong/mde-auditcheck
MDE relies on some of the Audit settings to be enabled
 dev-sec/chef-mysql-hardening
This chef cookbook provides security configuration for mysql.
 george0papasotiriou/cve-2026-22015-serverless-function-environment-variable-injection-via-event
PoC for CVE-2026-22015: malicious event injects environment variables into serverless functions, overwriting secrets and enabling privilege…
 chandru-gunasekaran/log4j-fix-cve-2021-44228
Windows Batch Scrip to Fix the log4j-issue-CVE-2021-44228
 nikip72/cve-2021-39273-cve-2021-39274
Two security issues identified in Sn1per v9.0 free version by XeroSecurity
 gmo-ierae/cve-2024-26144-test
Test tool for CVE-2024-26144 that checks if web servers and CDNs improperly cache HTTP responses containing Set-Cookie headers, revealing cache…