
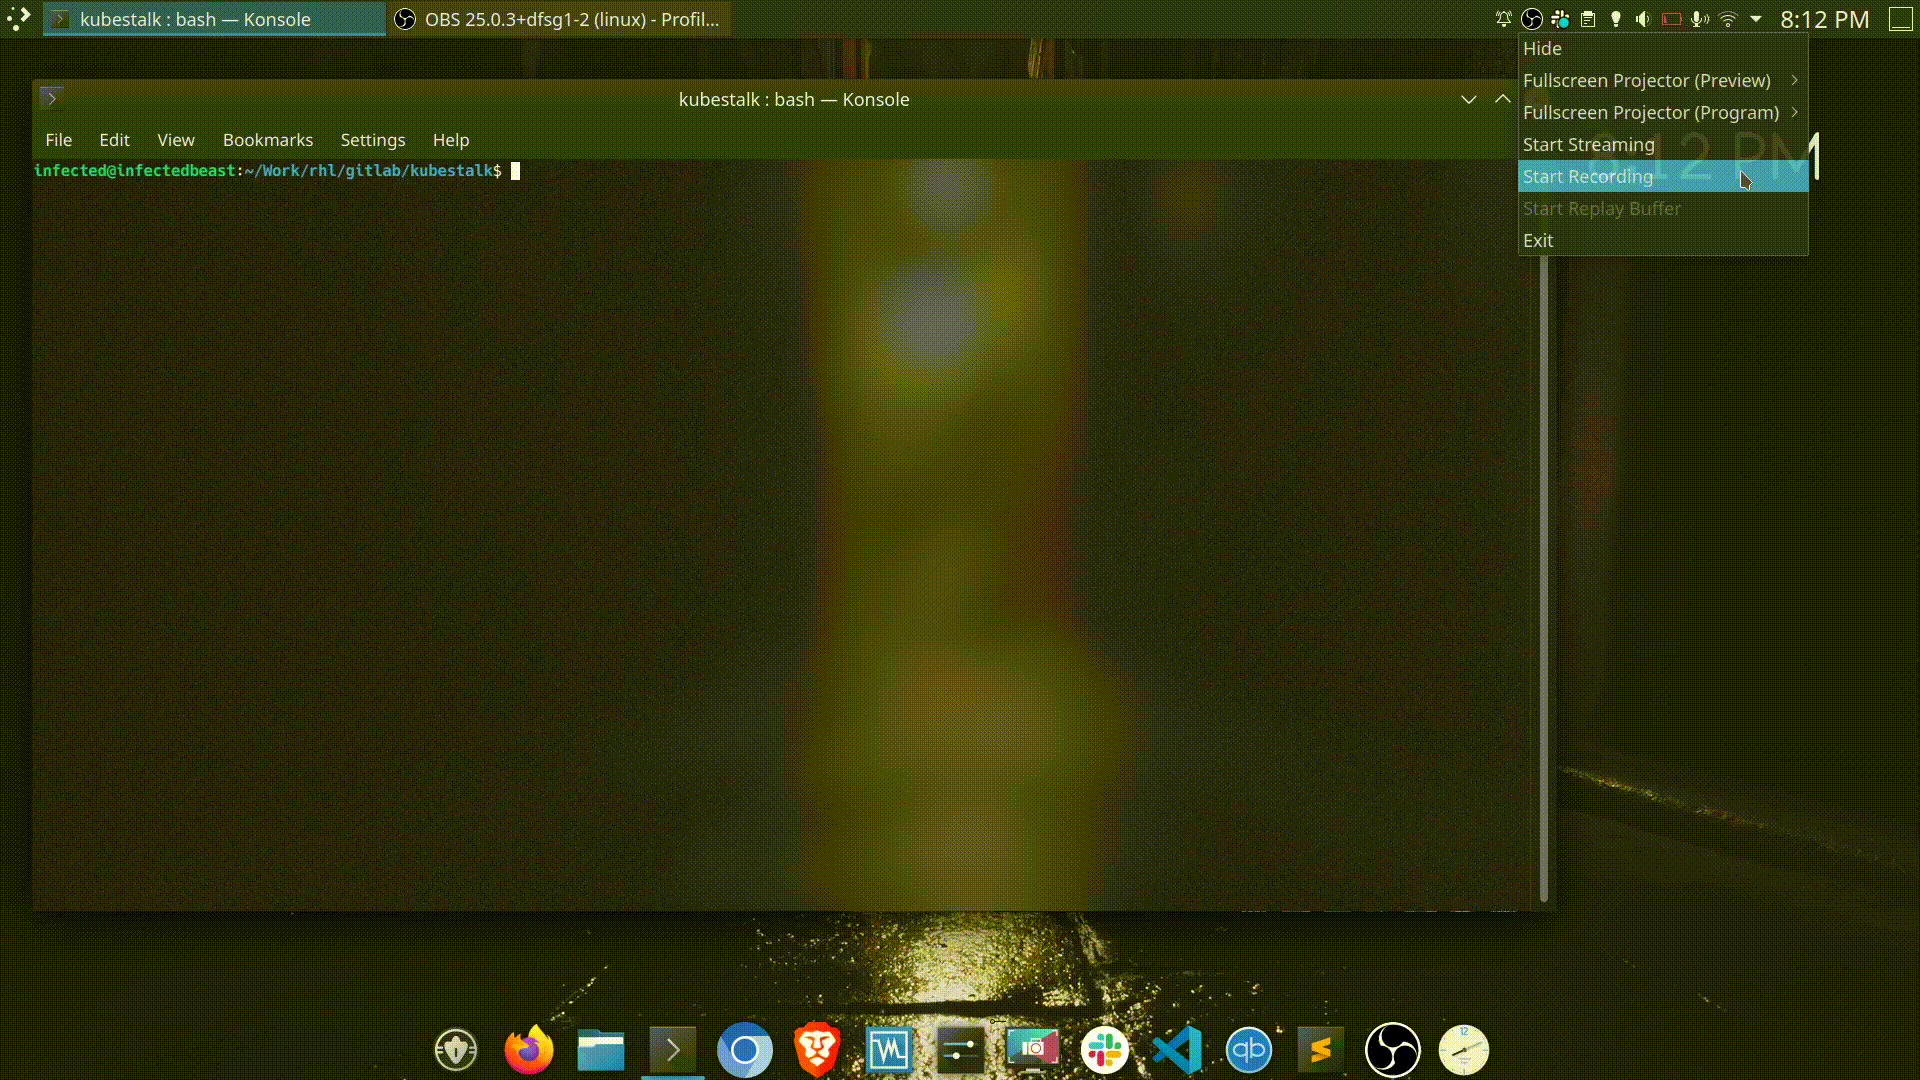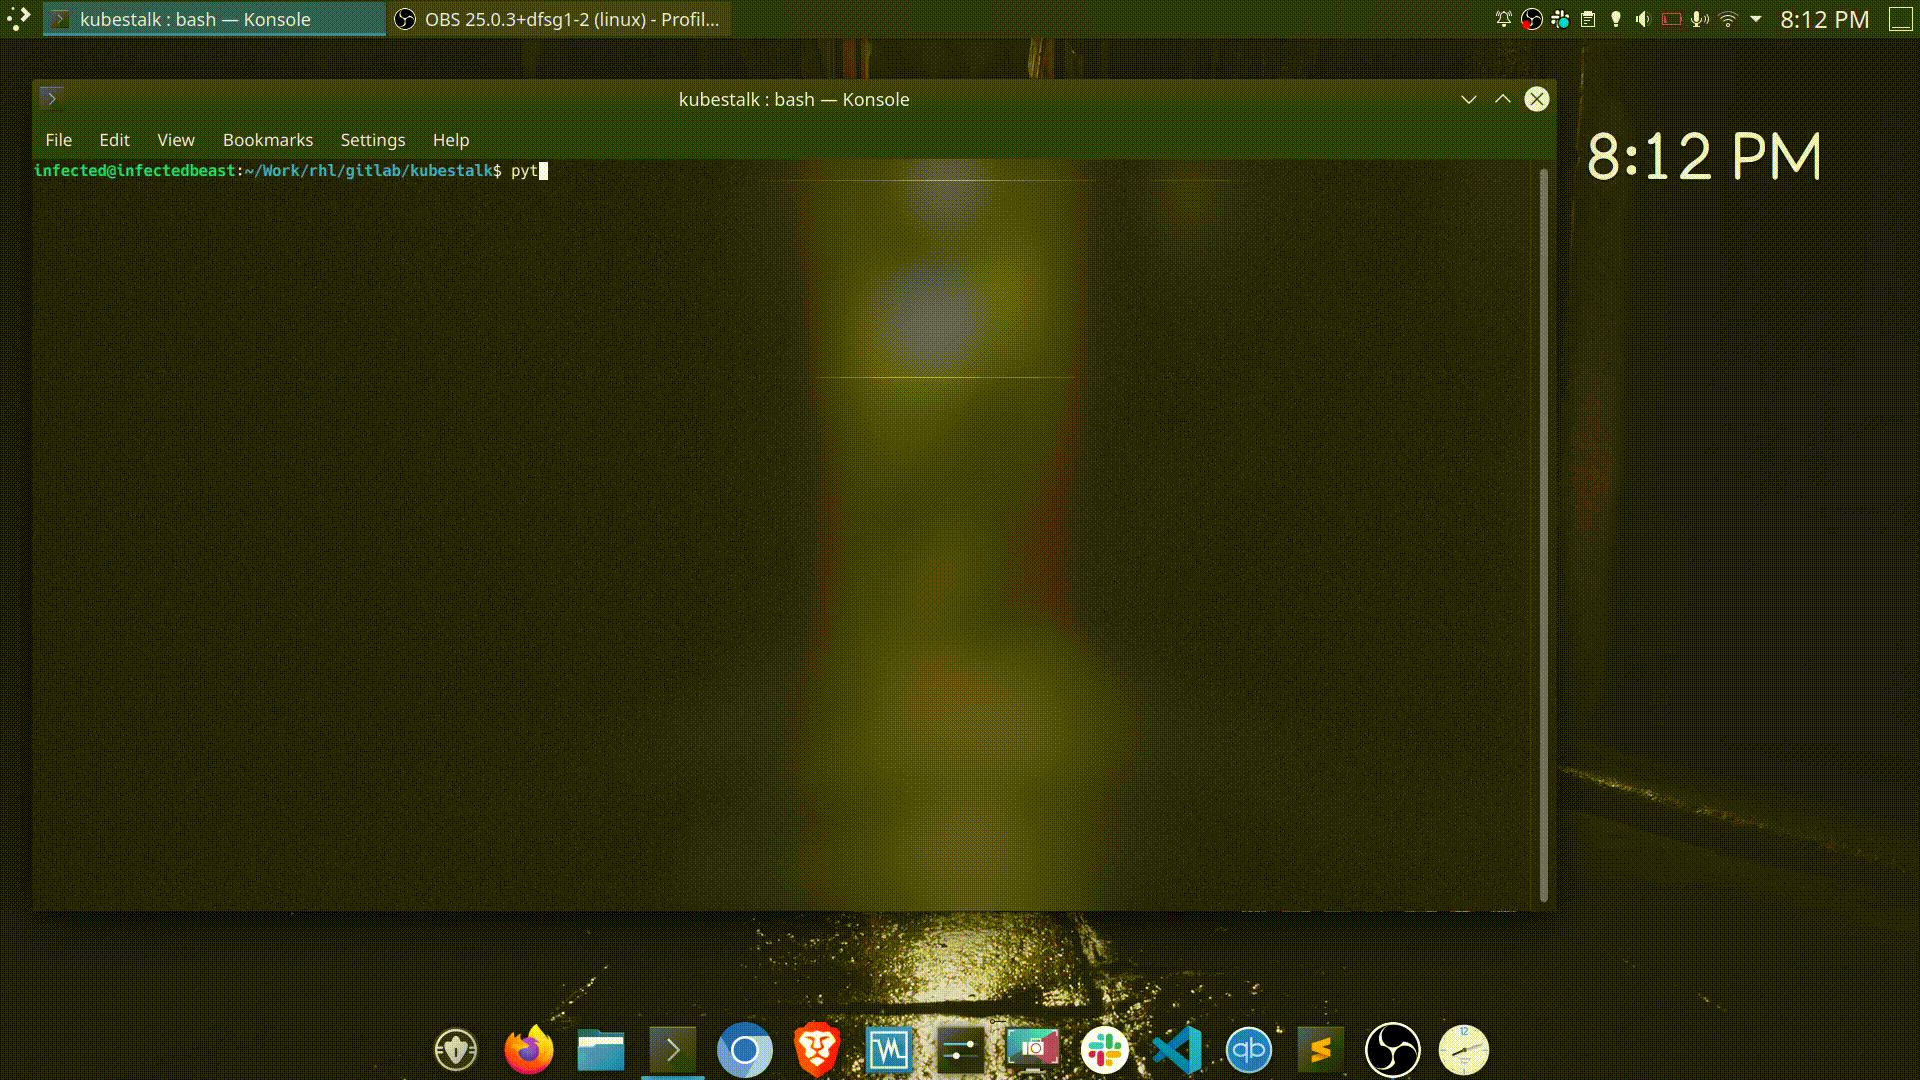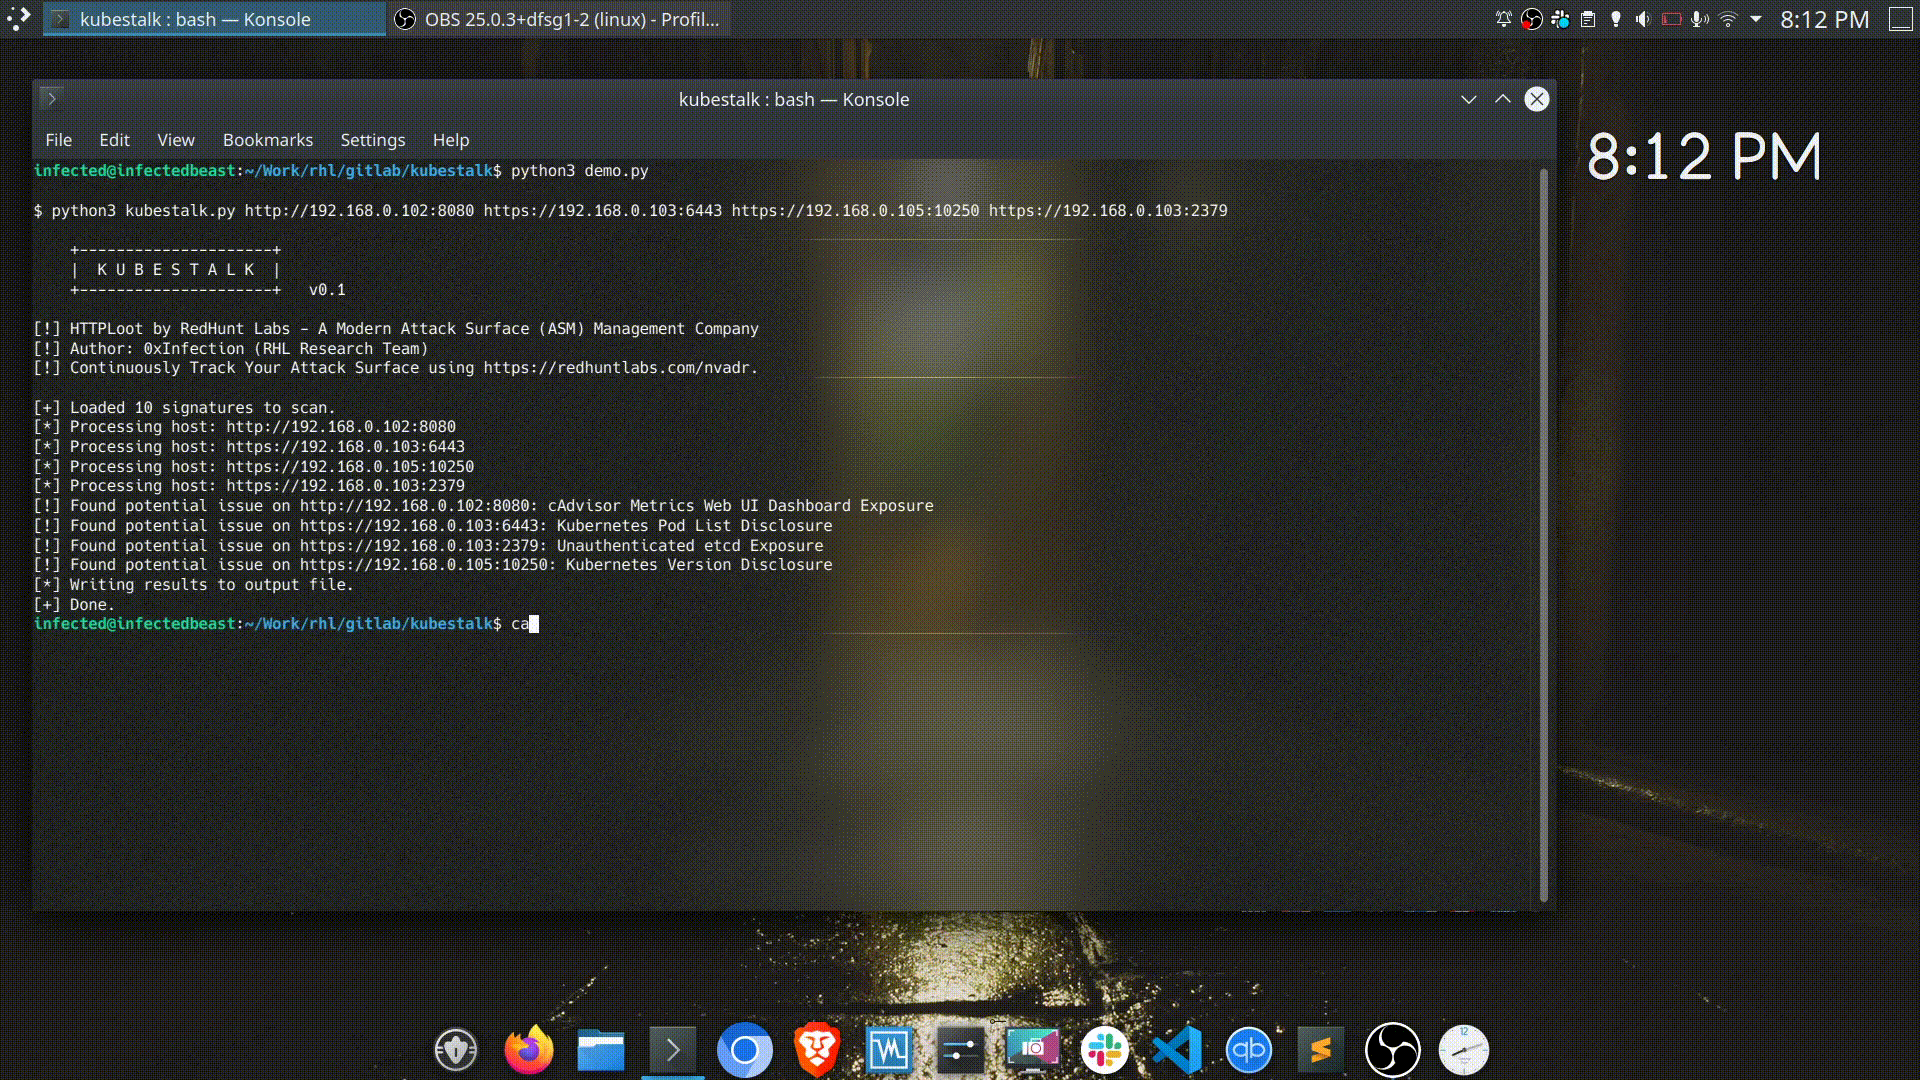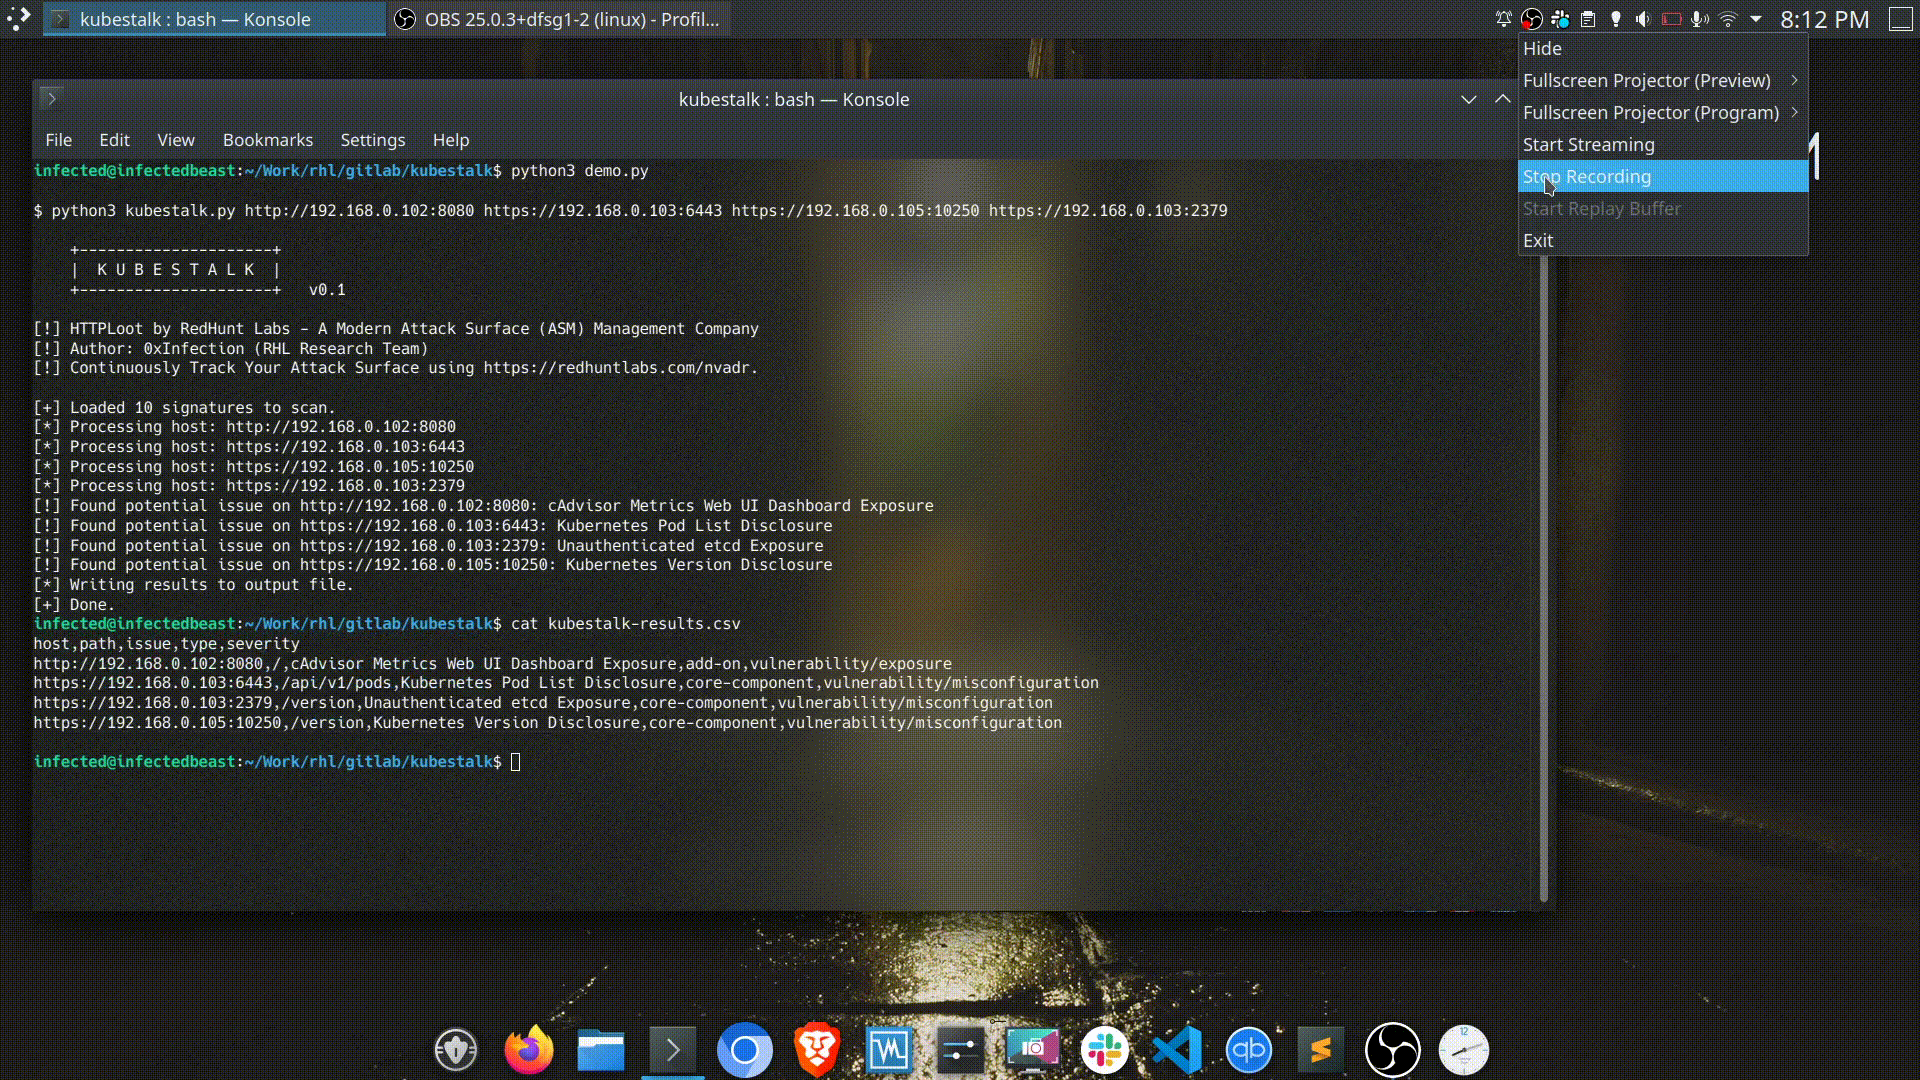
KubeStalk
 redhuntlabs/kubestalk
Black-box Kubernetes attack surface discovery tool that probes for unsecured clusters, exposed dashboards, and misconfigurations using…
cloud-securitycontainer-securityinformation-gathering+3
180
redhuntlabs/kubestalkBlack-box Kubernetes attack surface discovery tool that probes for unsecured clusters, exposed dashboards, and misconfigurations using…
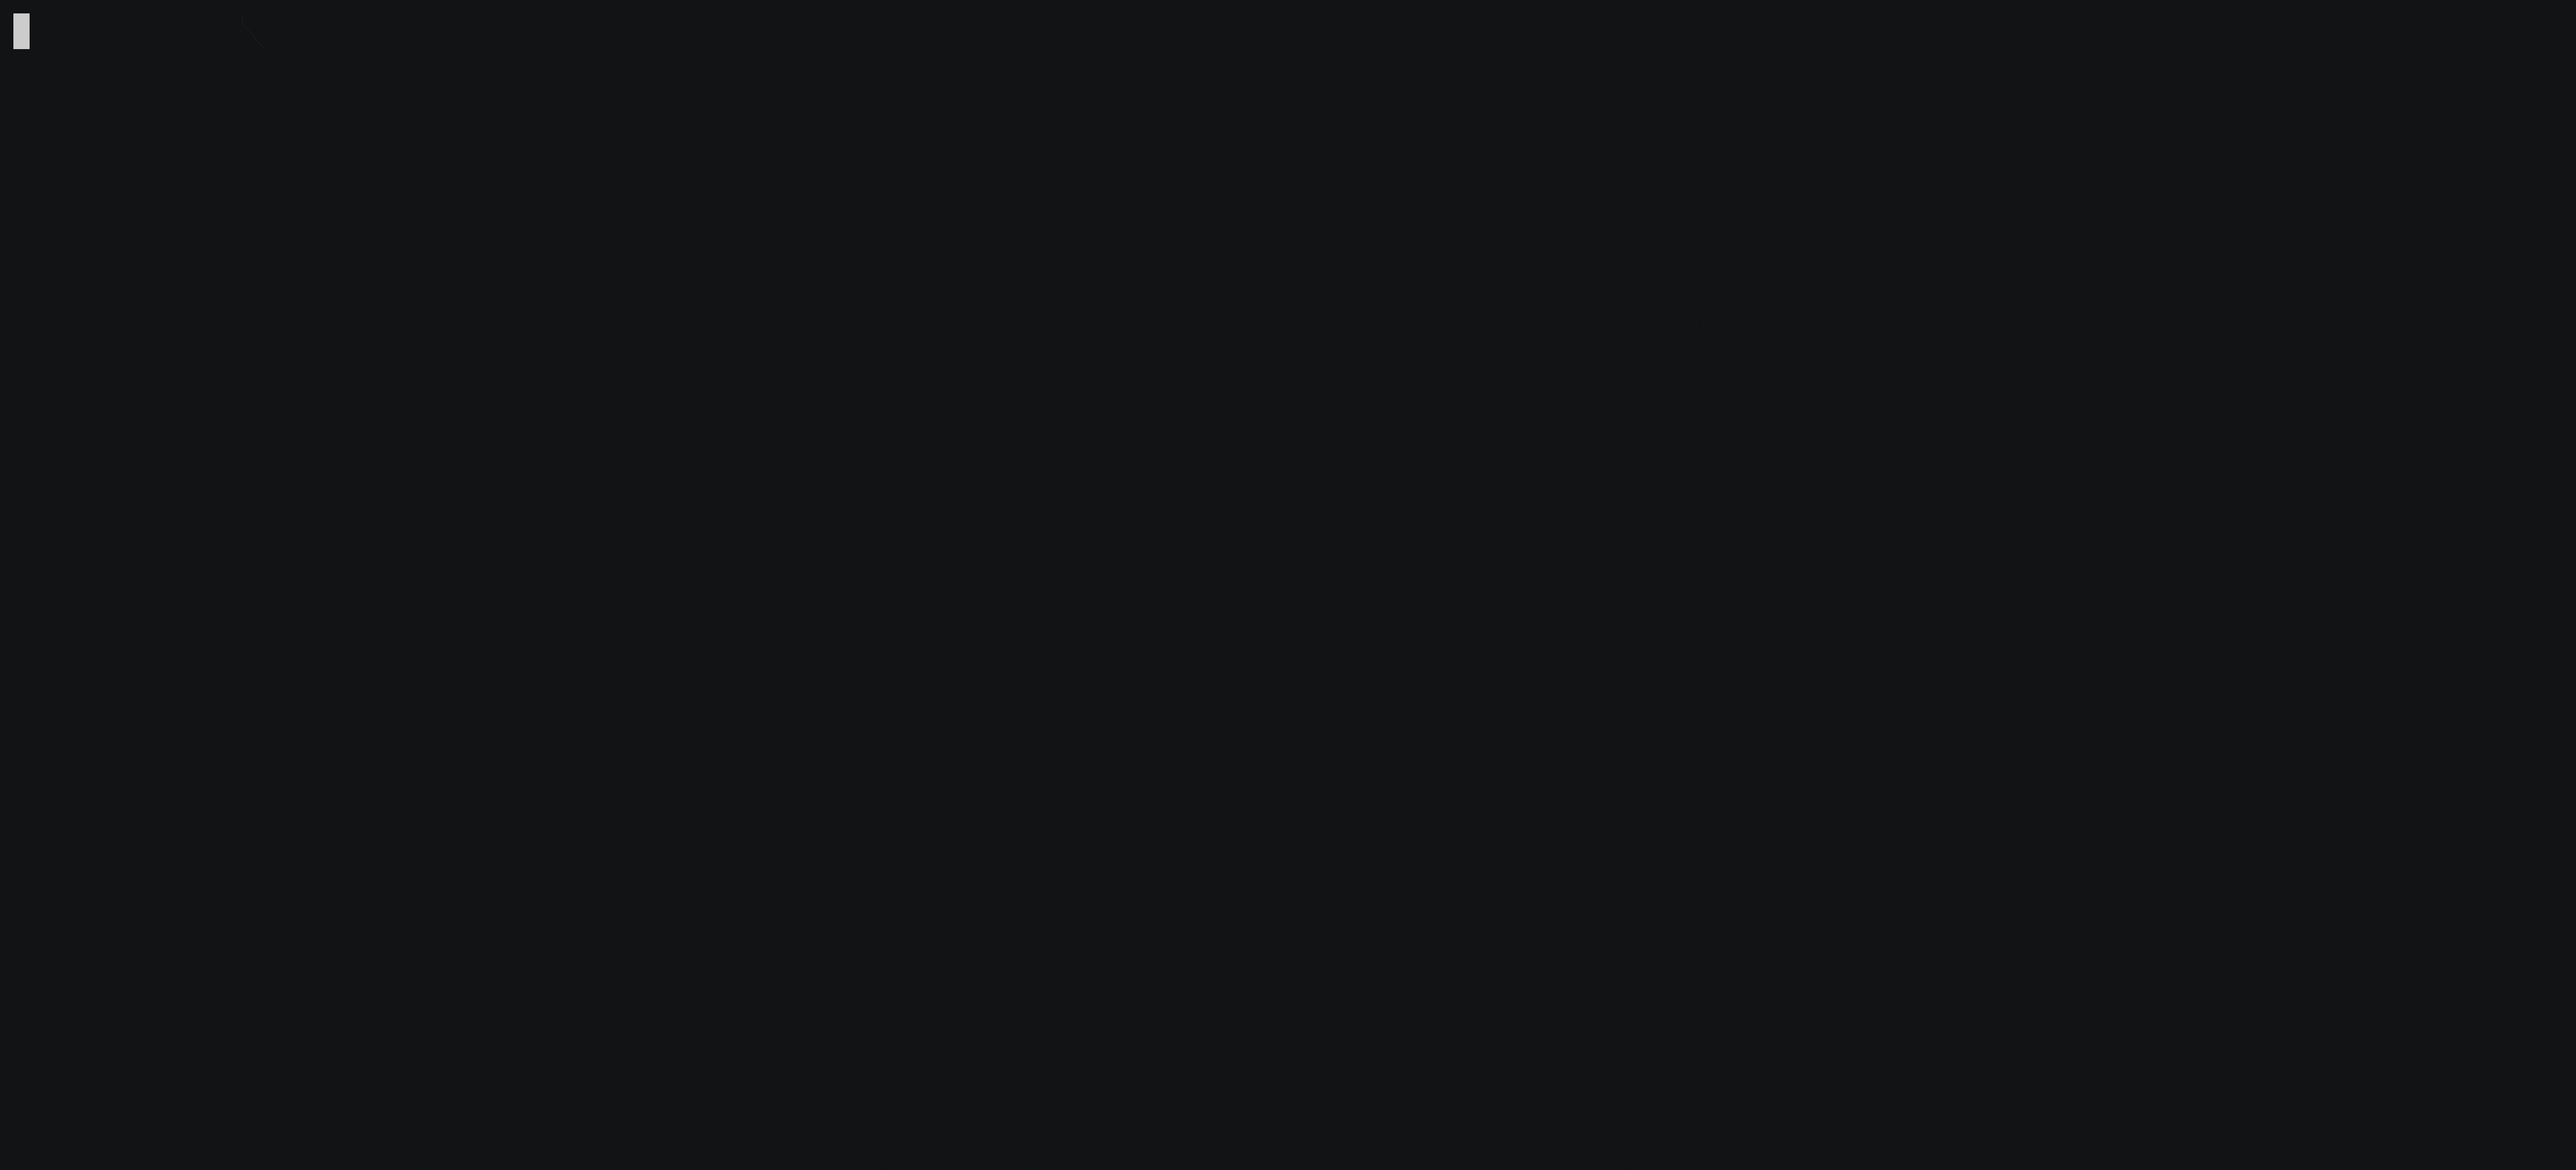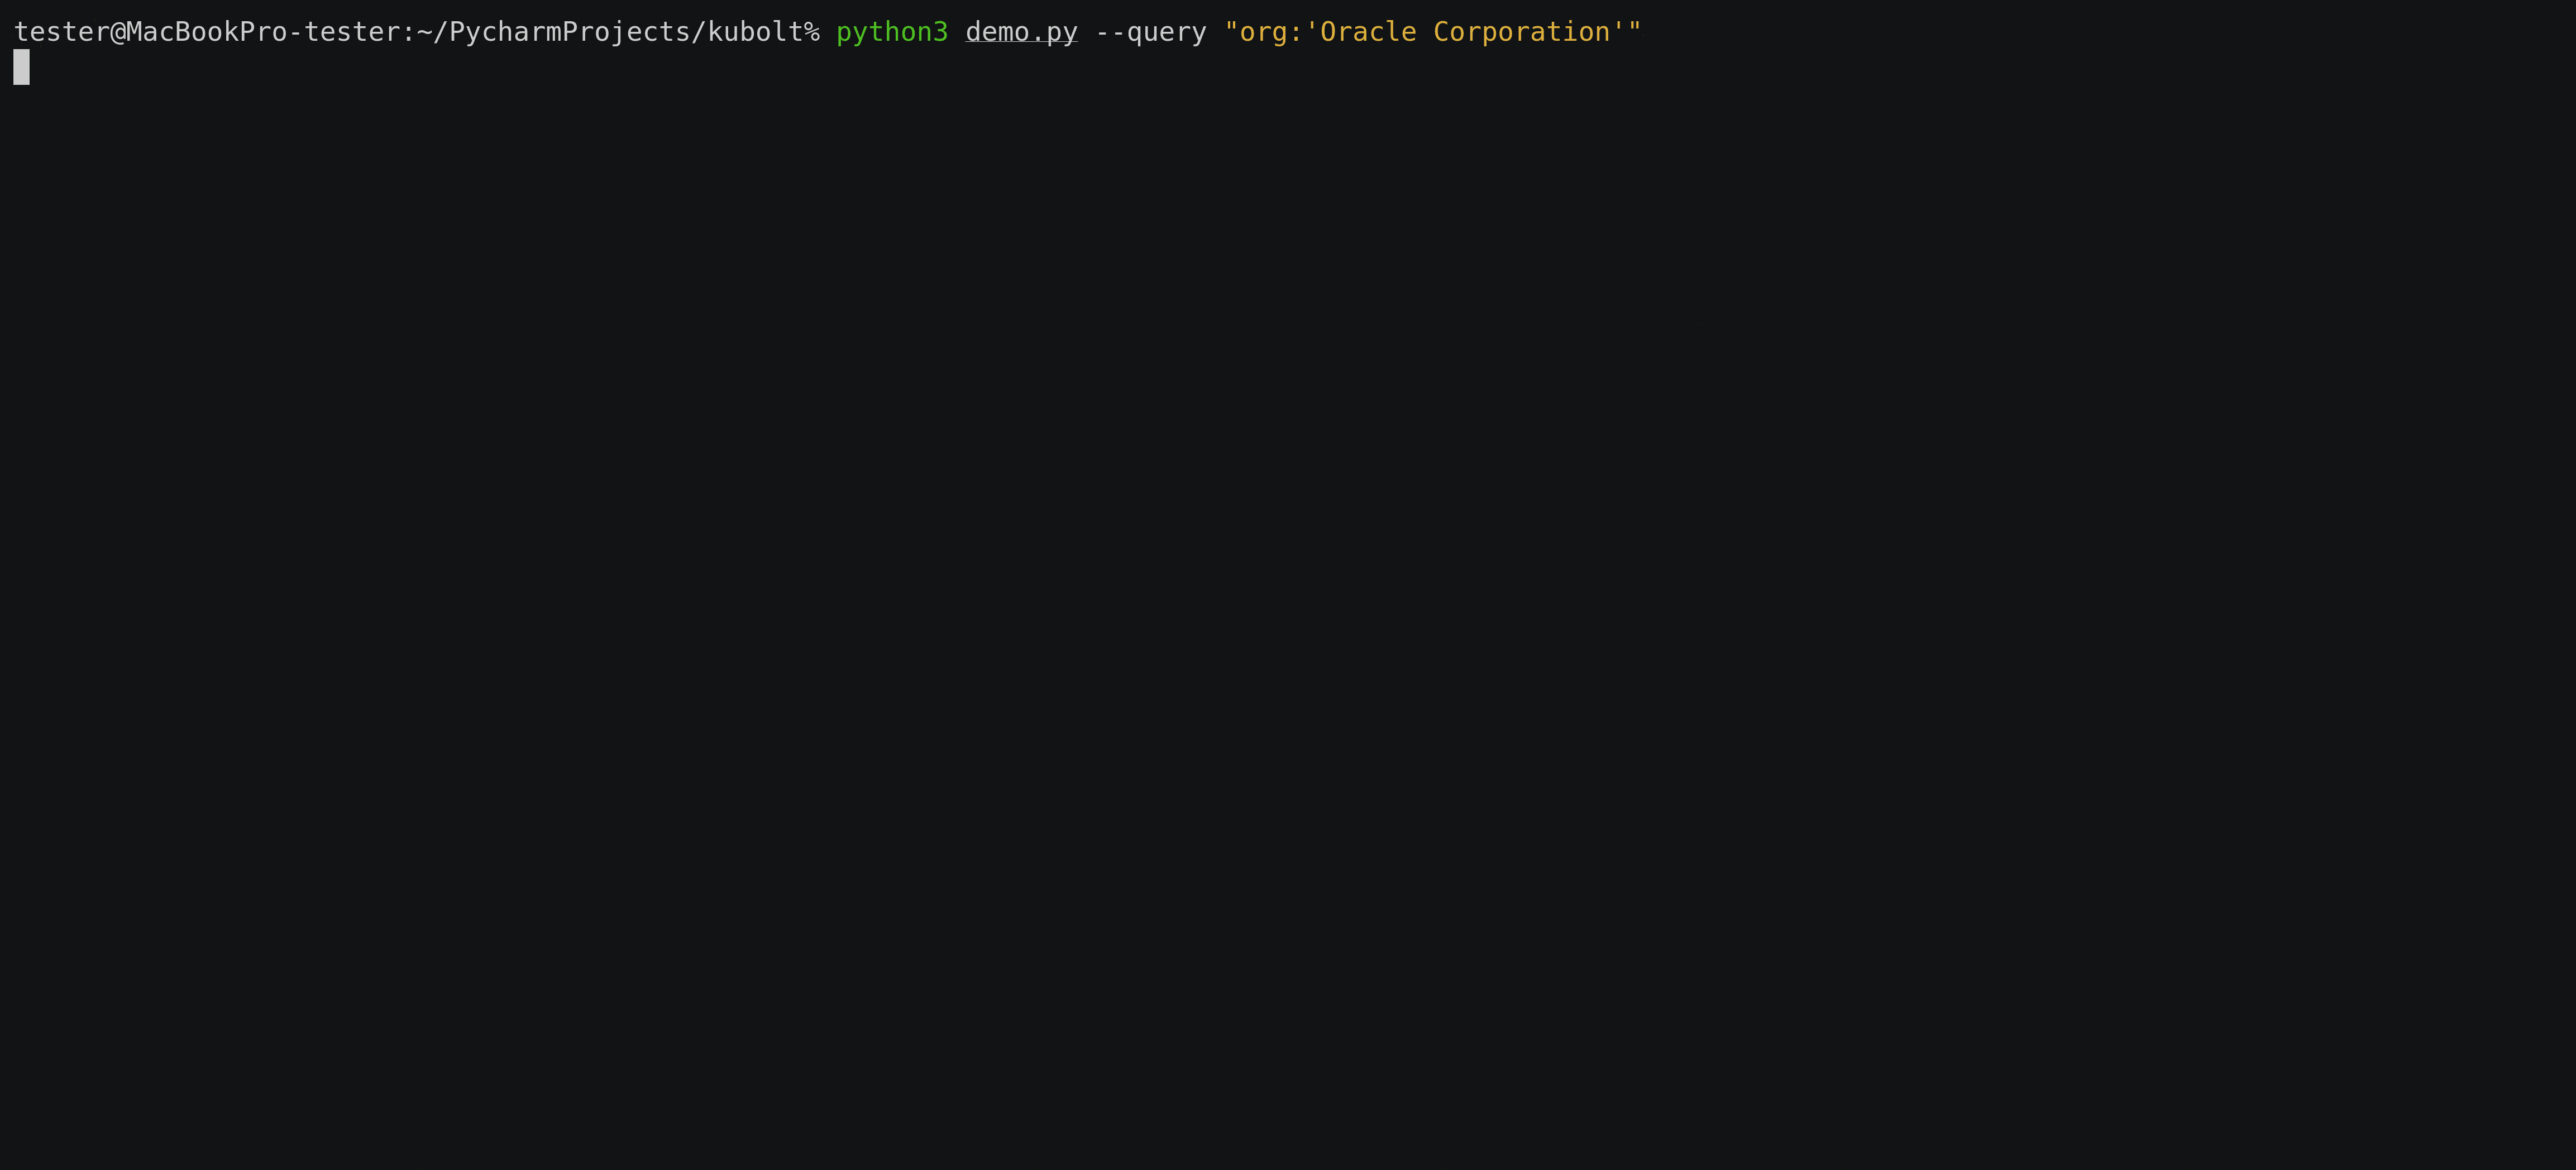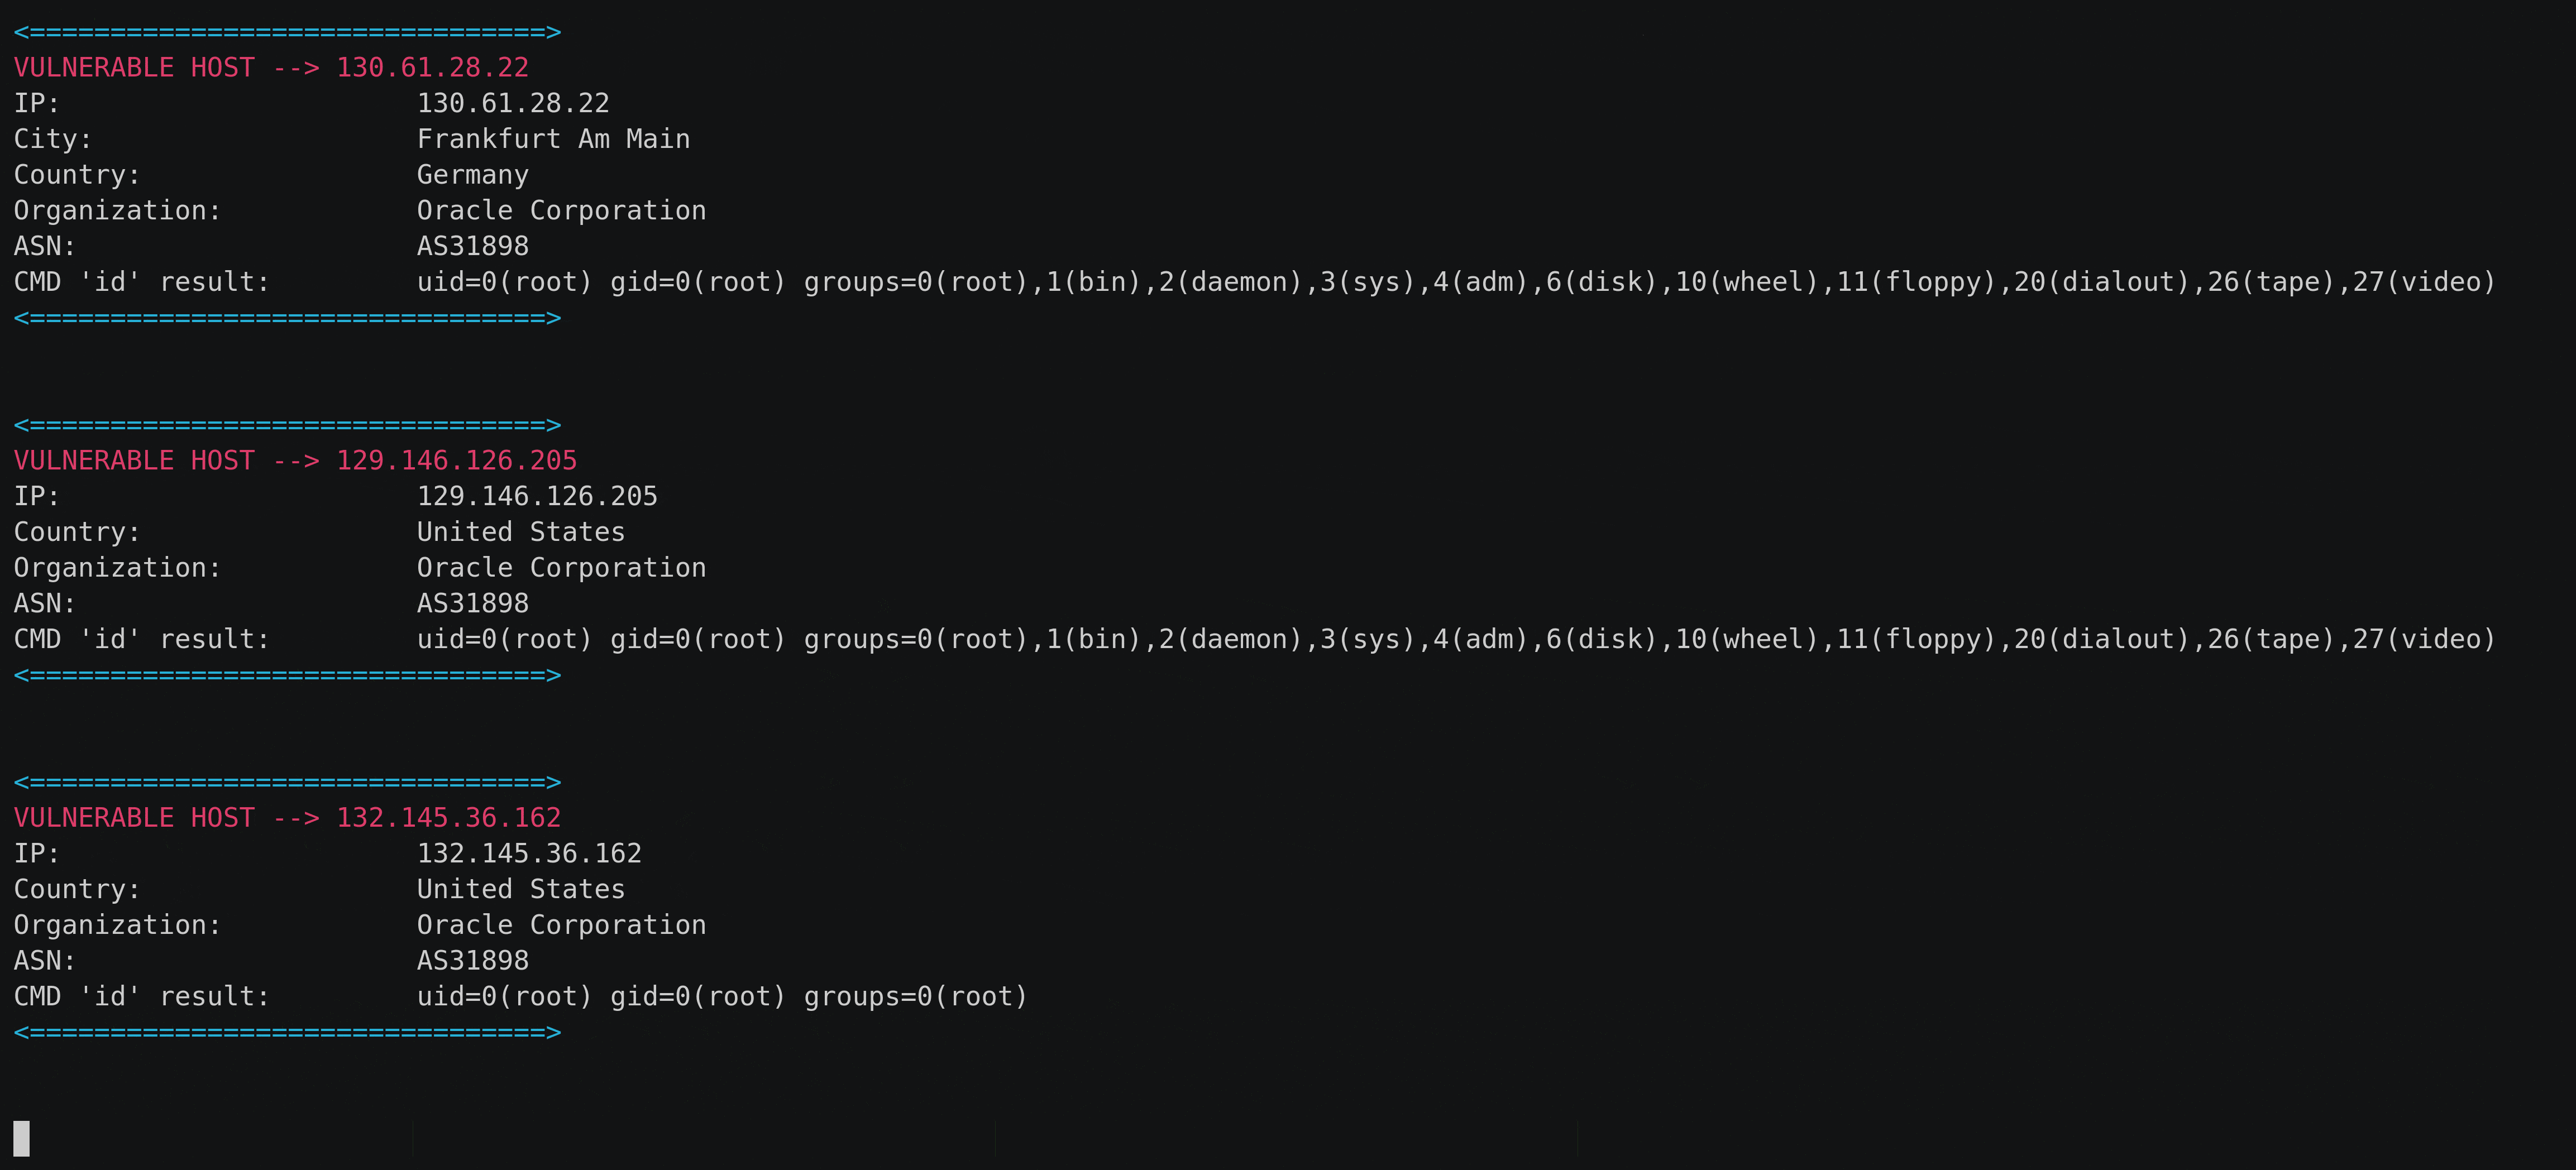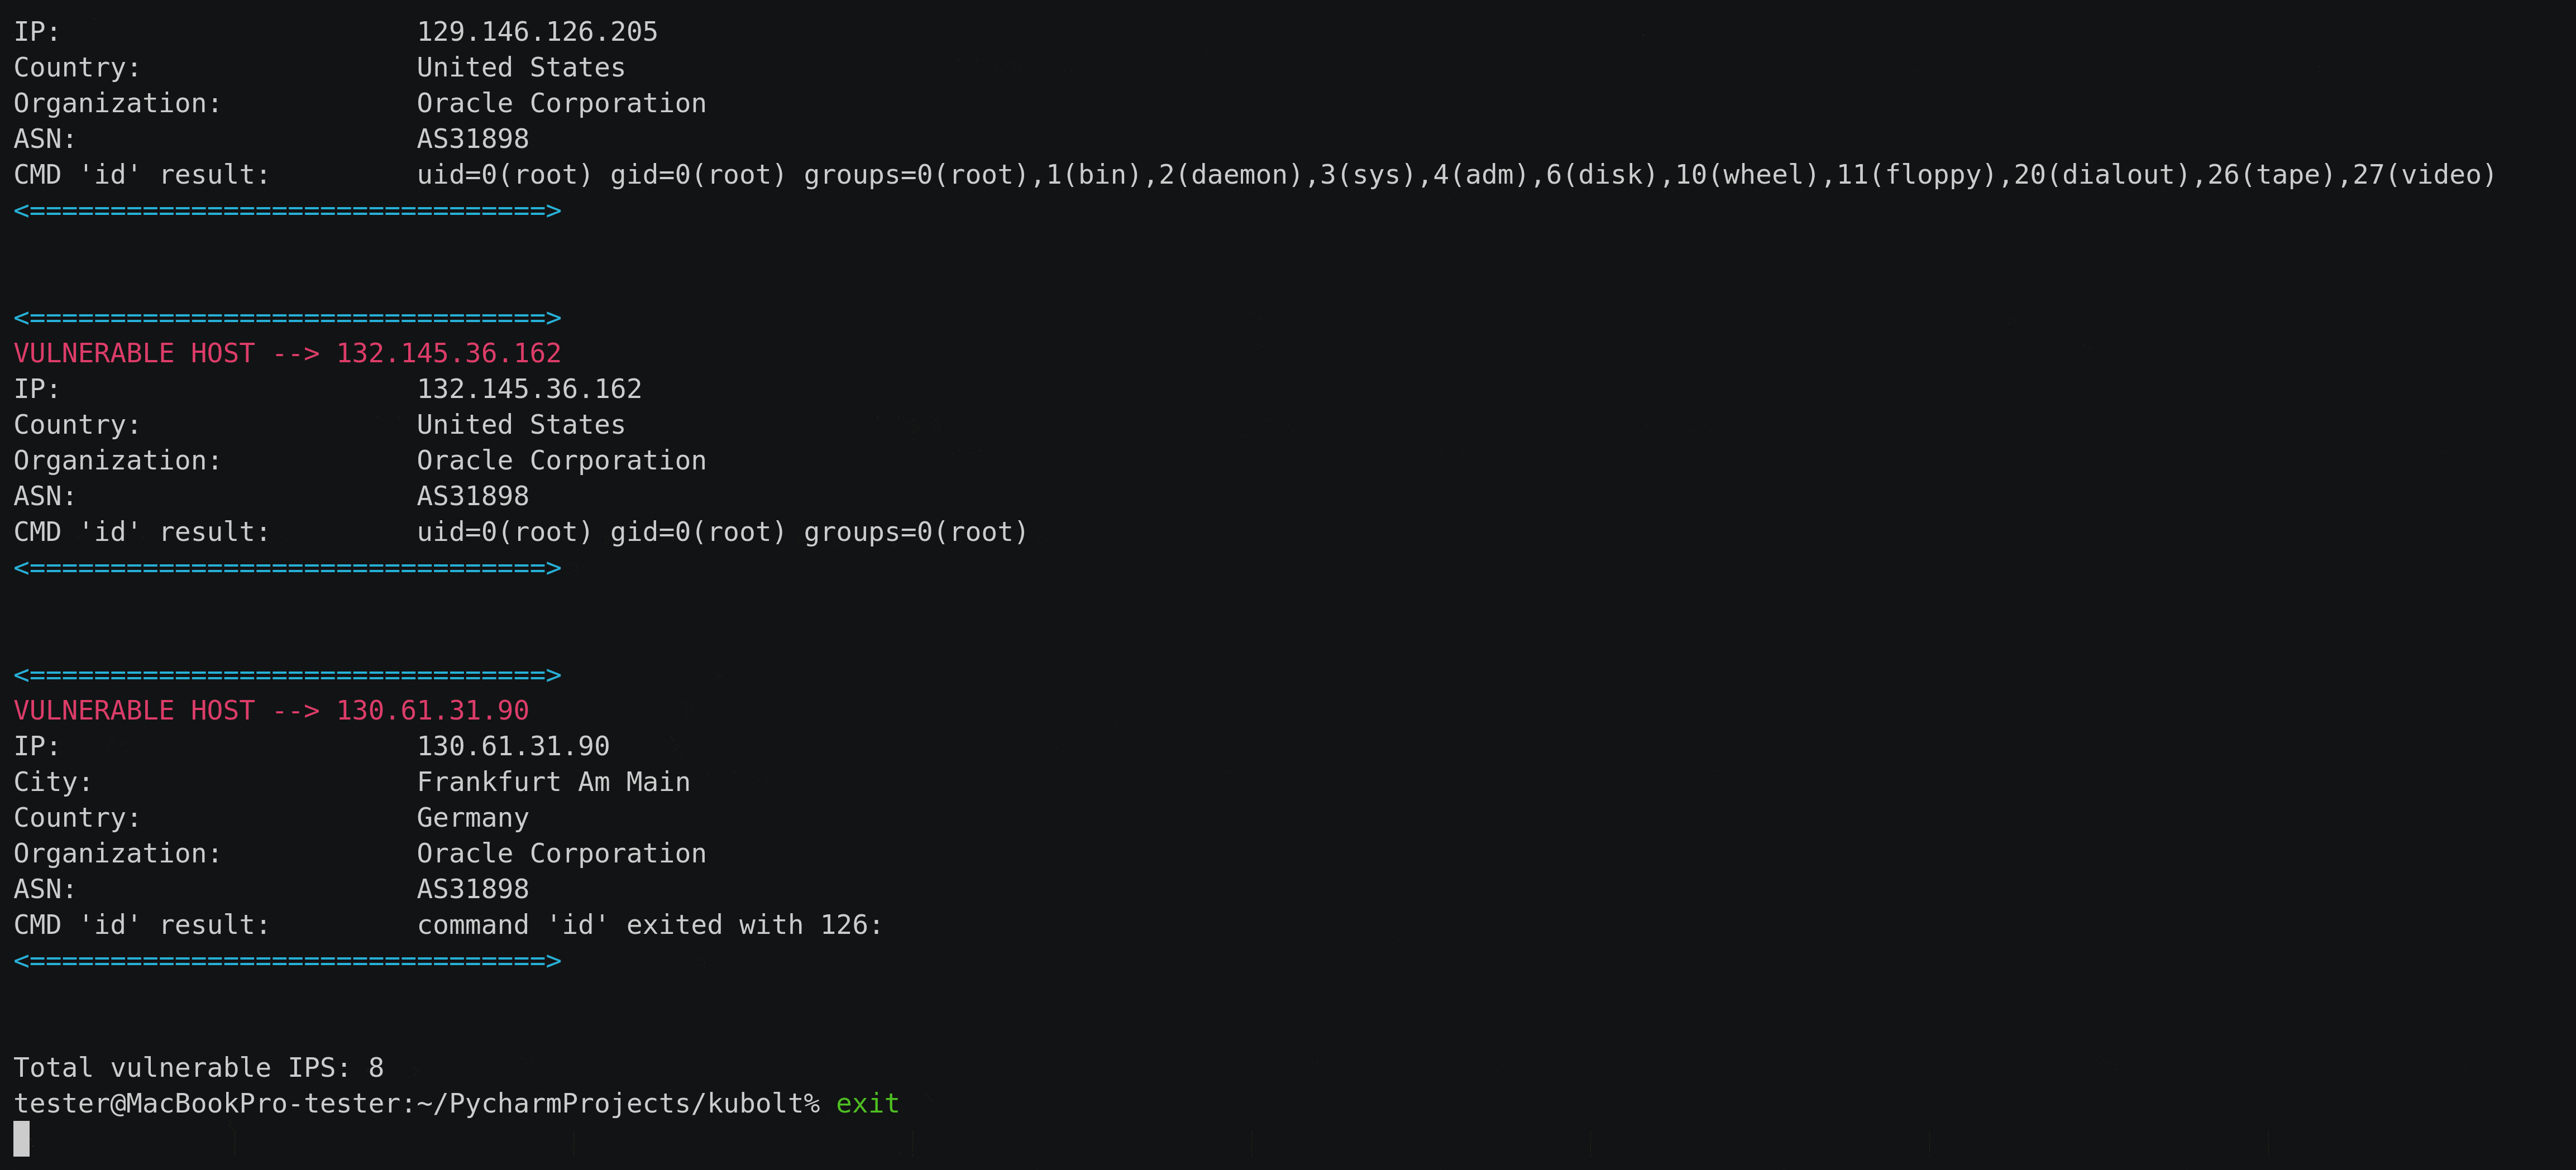 averonesis/kubolt
Kubolt utility for scanning public kubernetes clusters
 christophetd/cloudflair
🔎 Find origin servers of websites behind CloudFlare by using Internet-wide scan data from Censys.
 subat0mik/misconfiguration-manager
Misconfiguration Manager is a central knowledge base for all known Microsoft Configuration Manager tradecraft and associated defensive and hardening…
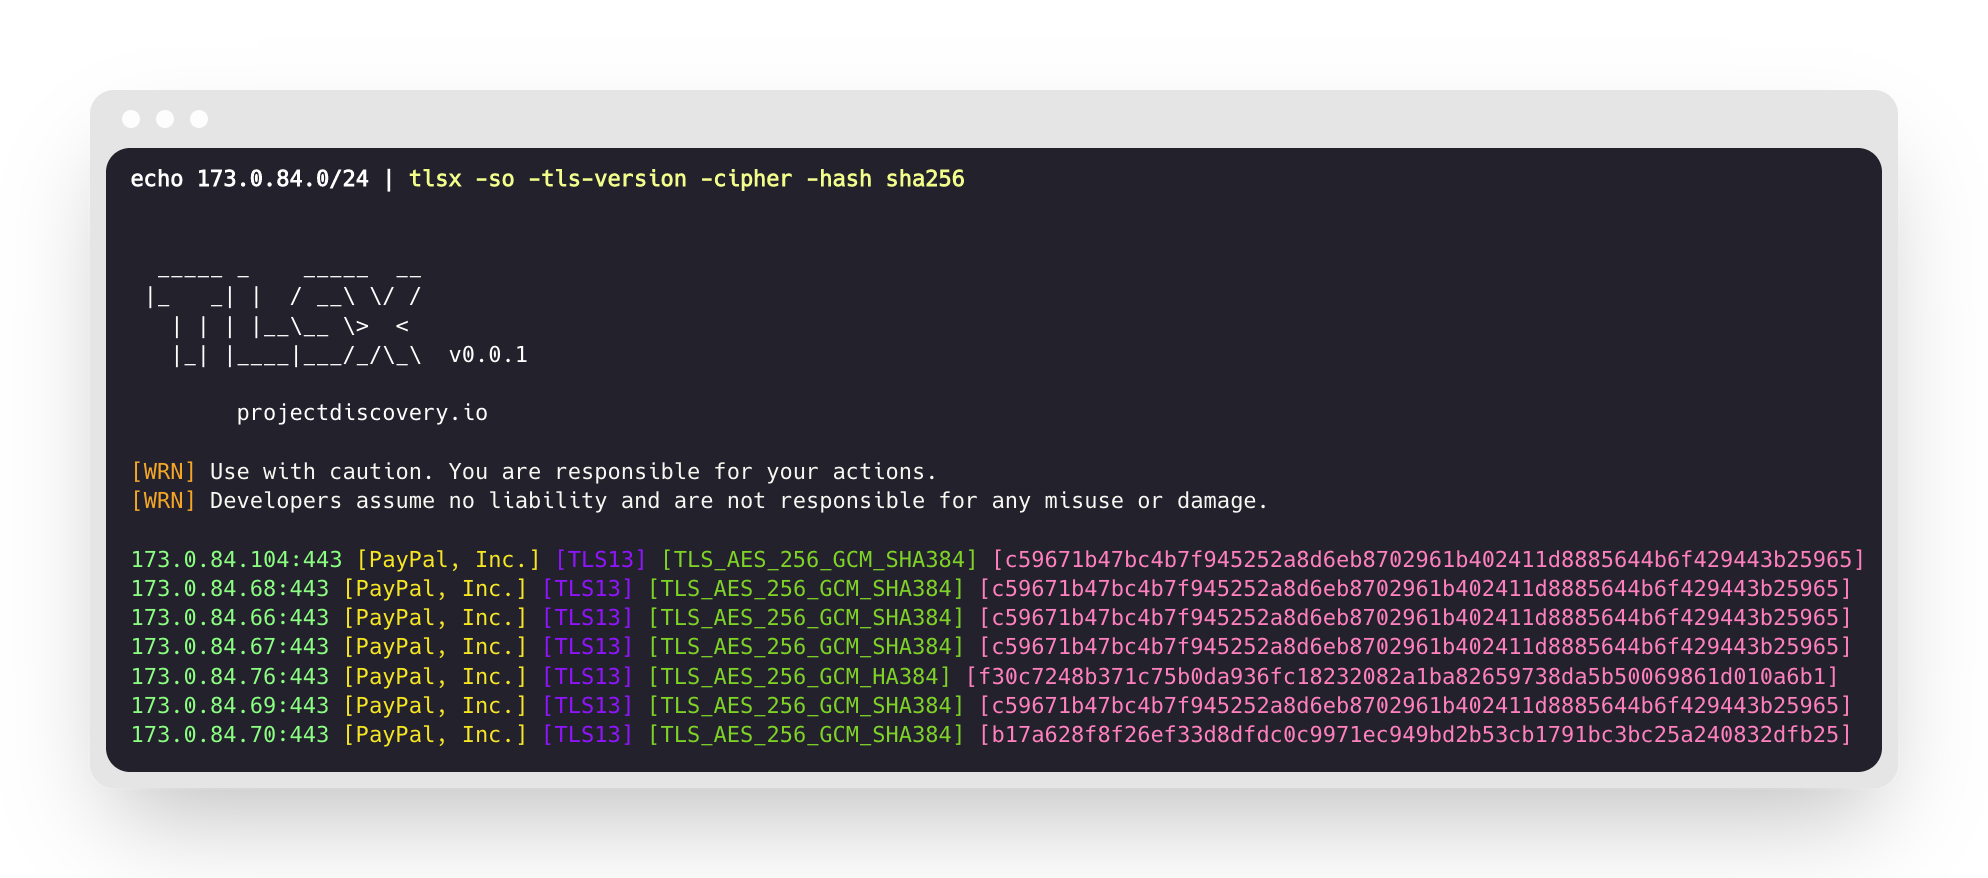 projectdiscovery/tlsx
Fast and configurable TLS grabber focused on TLS based data collection.
 ad-security/ad_miner
AD Miner is an Active Directory audit tool that leverages cypher queries to crunch data from the #Bloodhound graph database to uncover security…
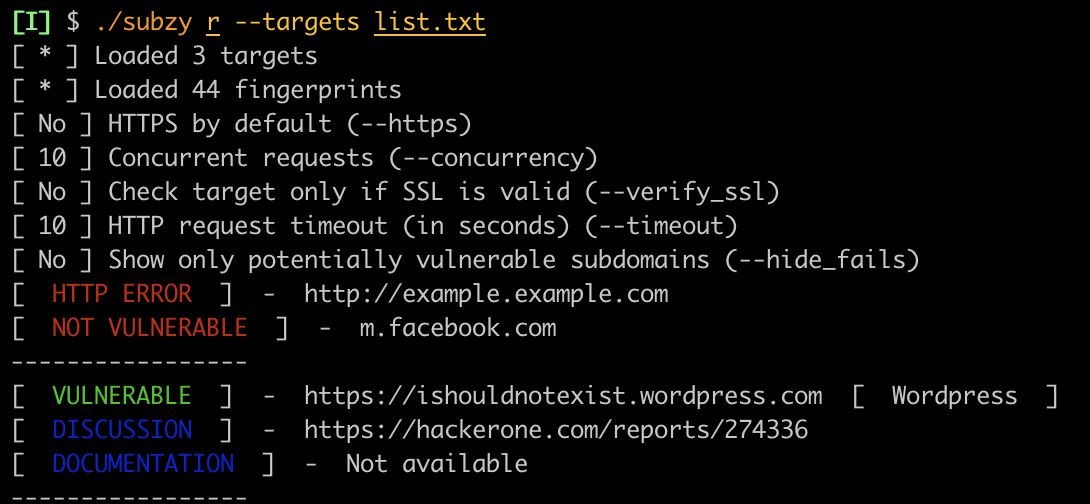 pentestpad/subzy
Subdomain takeover vulnerability checker
 nickvourd/windows-local-privilege-escalation-cookbook
Windows Local Privilege Escalation Cookbook
 cogiceo/gpohound
Offensive GPO dumping and analysis tool that leverages and enriches BloodHound data
 synacktiv/gpoparser
gpoParser is a tool designed to extract and analyze configurations applied through Group Policy Objects (GPOs) in an Active Directory environment.
 neffisback/wsuks
Automating the MITM attack on WSUS
 cynative/cynative
Read-only AI agent that queries your cloud, code, and runtime infrastructure to surface misconfigurations, leaked secrets, and privilege escalation…
 k8scout/k8scout
Drop a single binary into a compromised Kubernetes pod and instantly map every realistic attack path to cluster-admin, node escape, secret theft,…
 404tk/cloudtoolkit
Authorized cloud adversary simulation and validation toolkit
 nccgroup/go-pillage-registries
Pentester-focused Docker registry tool to enumerate and pull images
 jhs/audit_couchdb
Detect security issues in an Apache CouchDB server
 reverseclabs/azuredevops-enum
Read-only Azure DevOps enumeration tool that queries the REST API to surface projects, repositories, service connections, builds, pipeline secrets,…
 ovotech/domain-protect
Automated detection of vulnerable domain configurations and subdomain takeover risks across cloud environments, with continuous monitoring and…