
reposherlock
 kemal-arslan/reposherlock
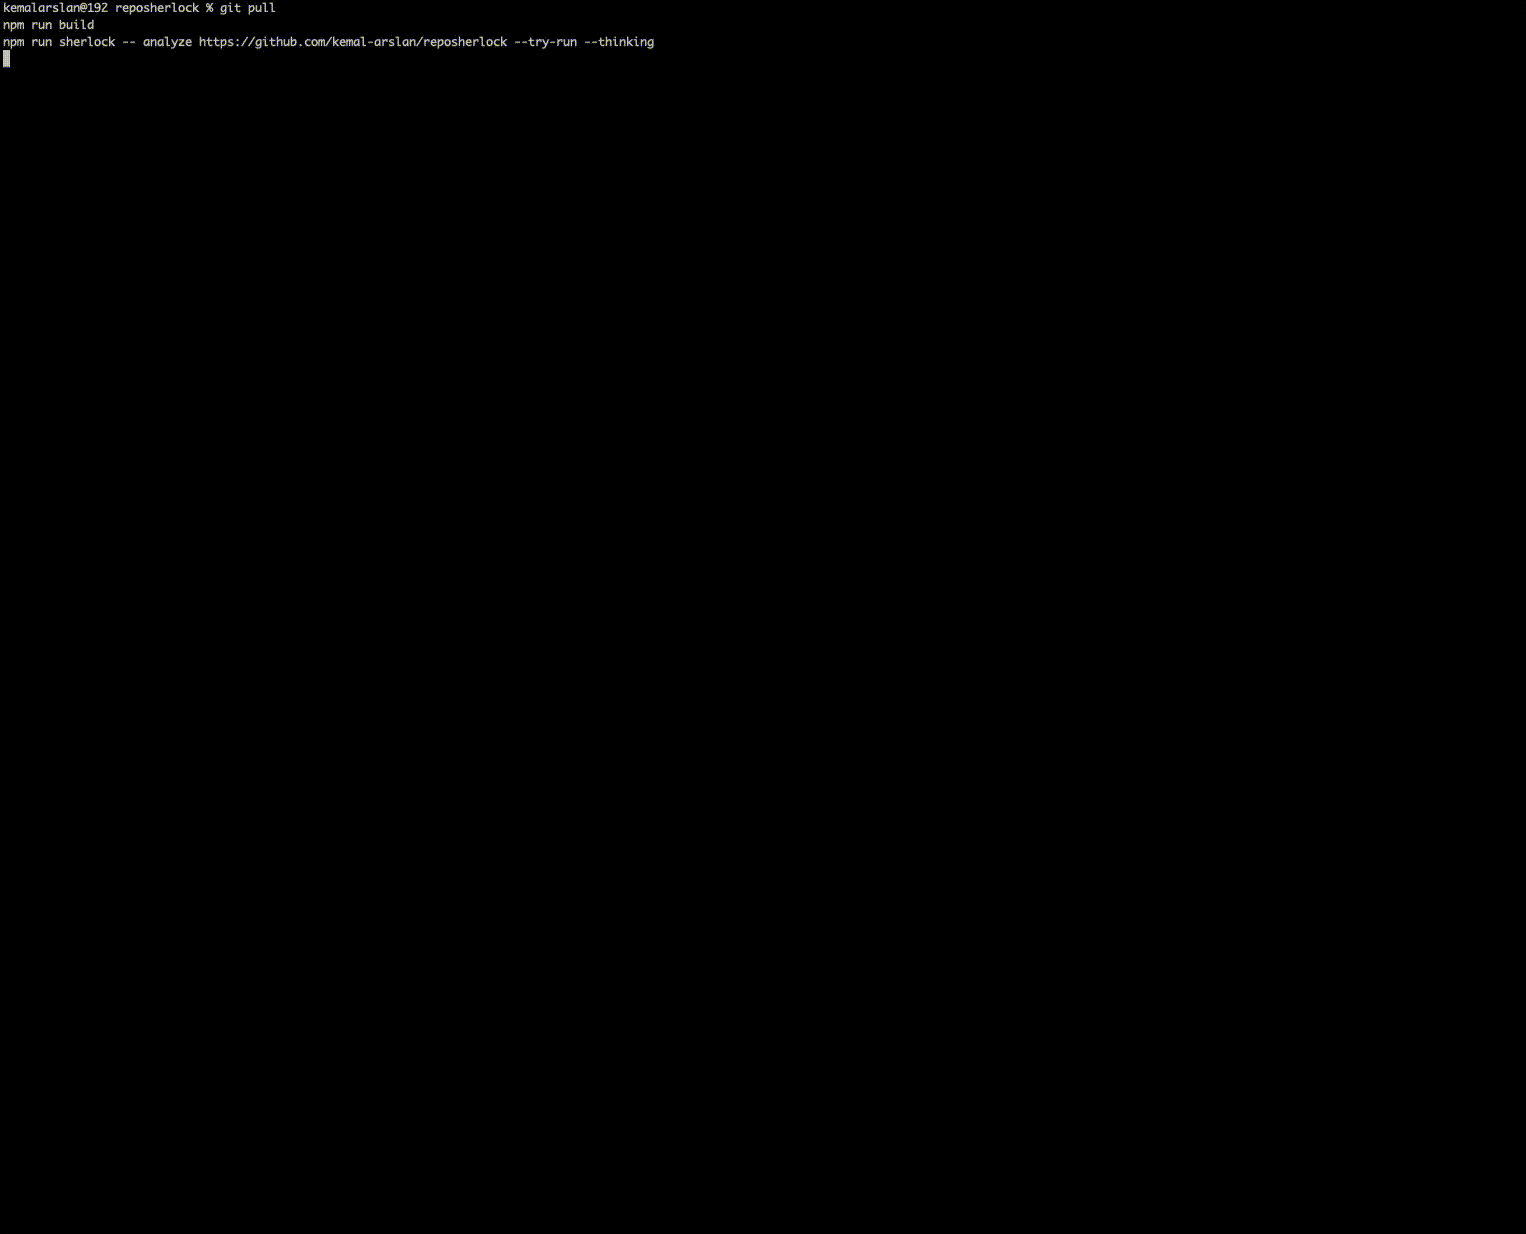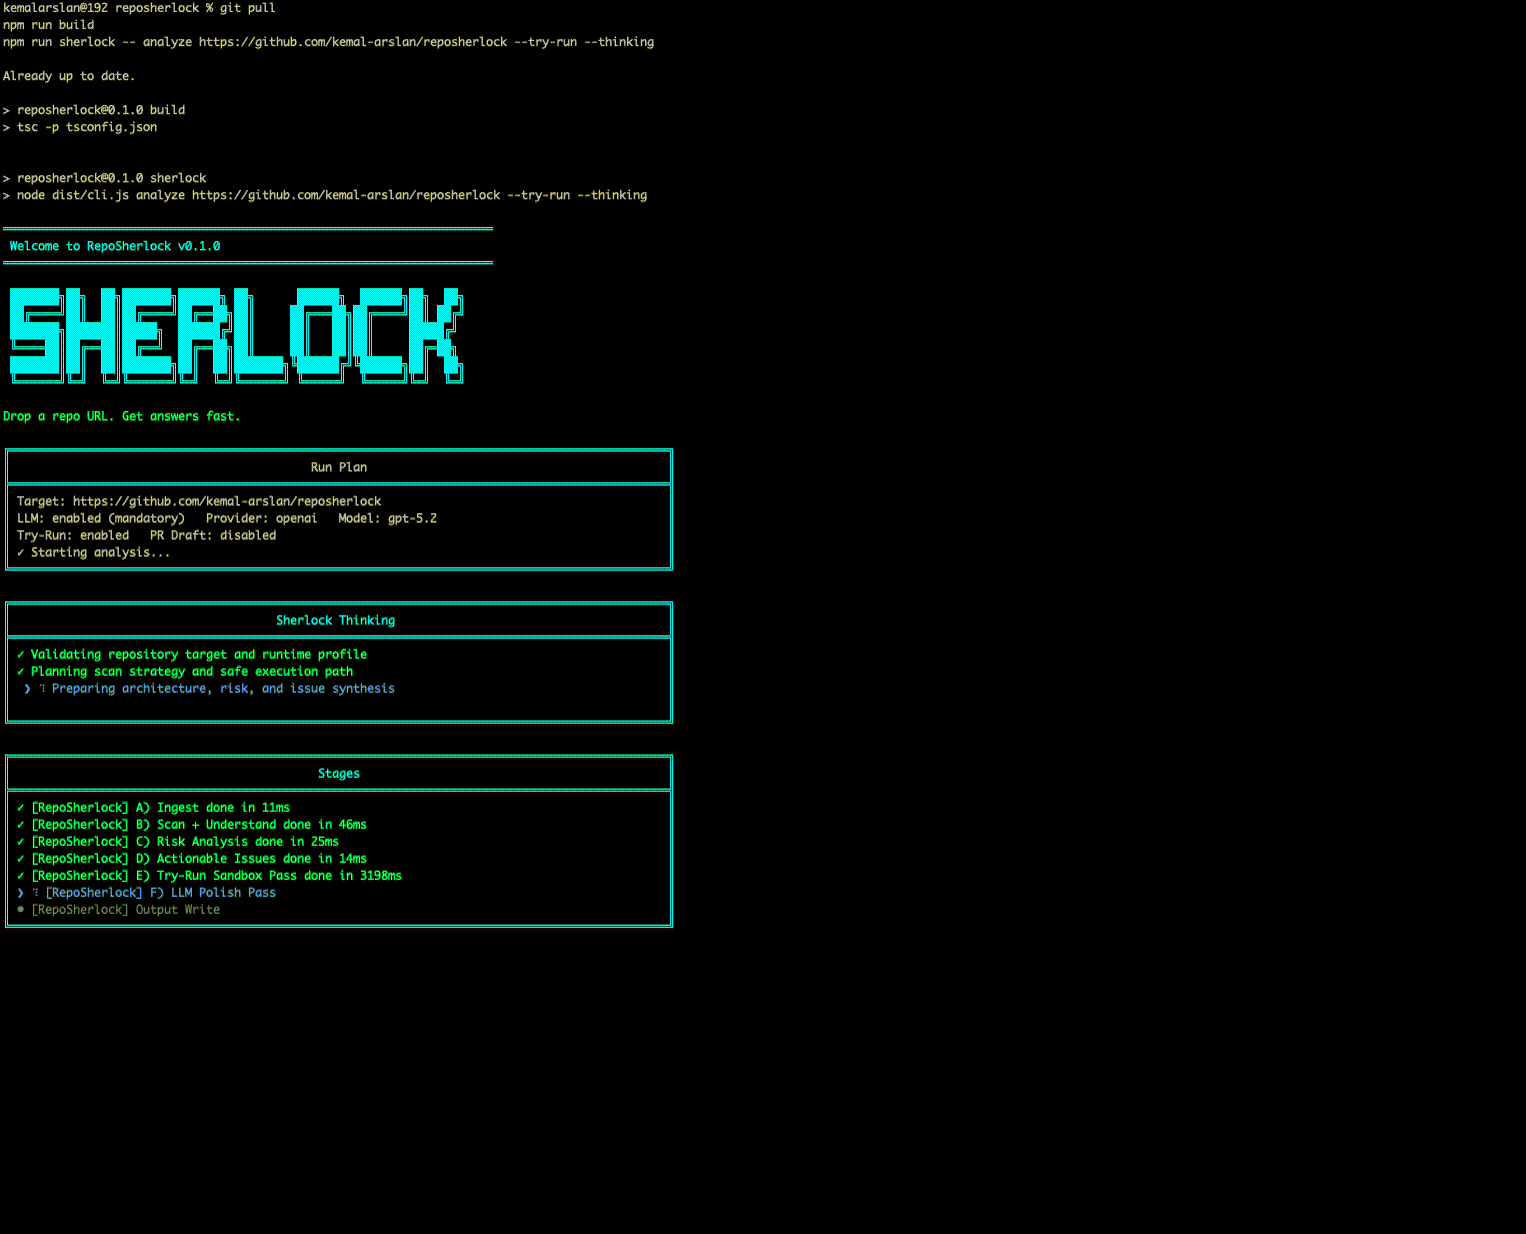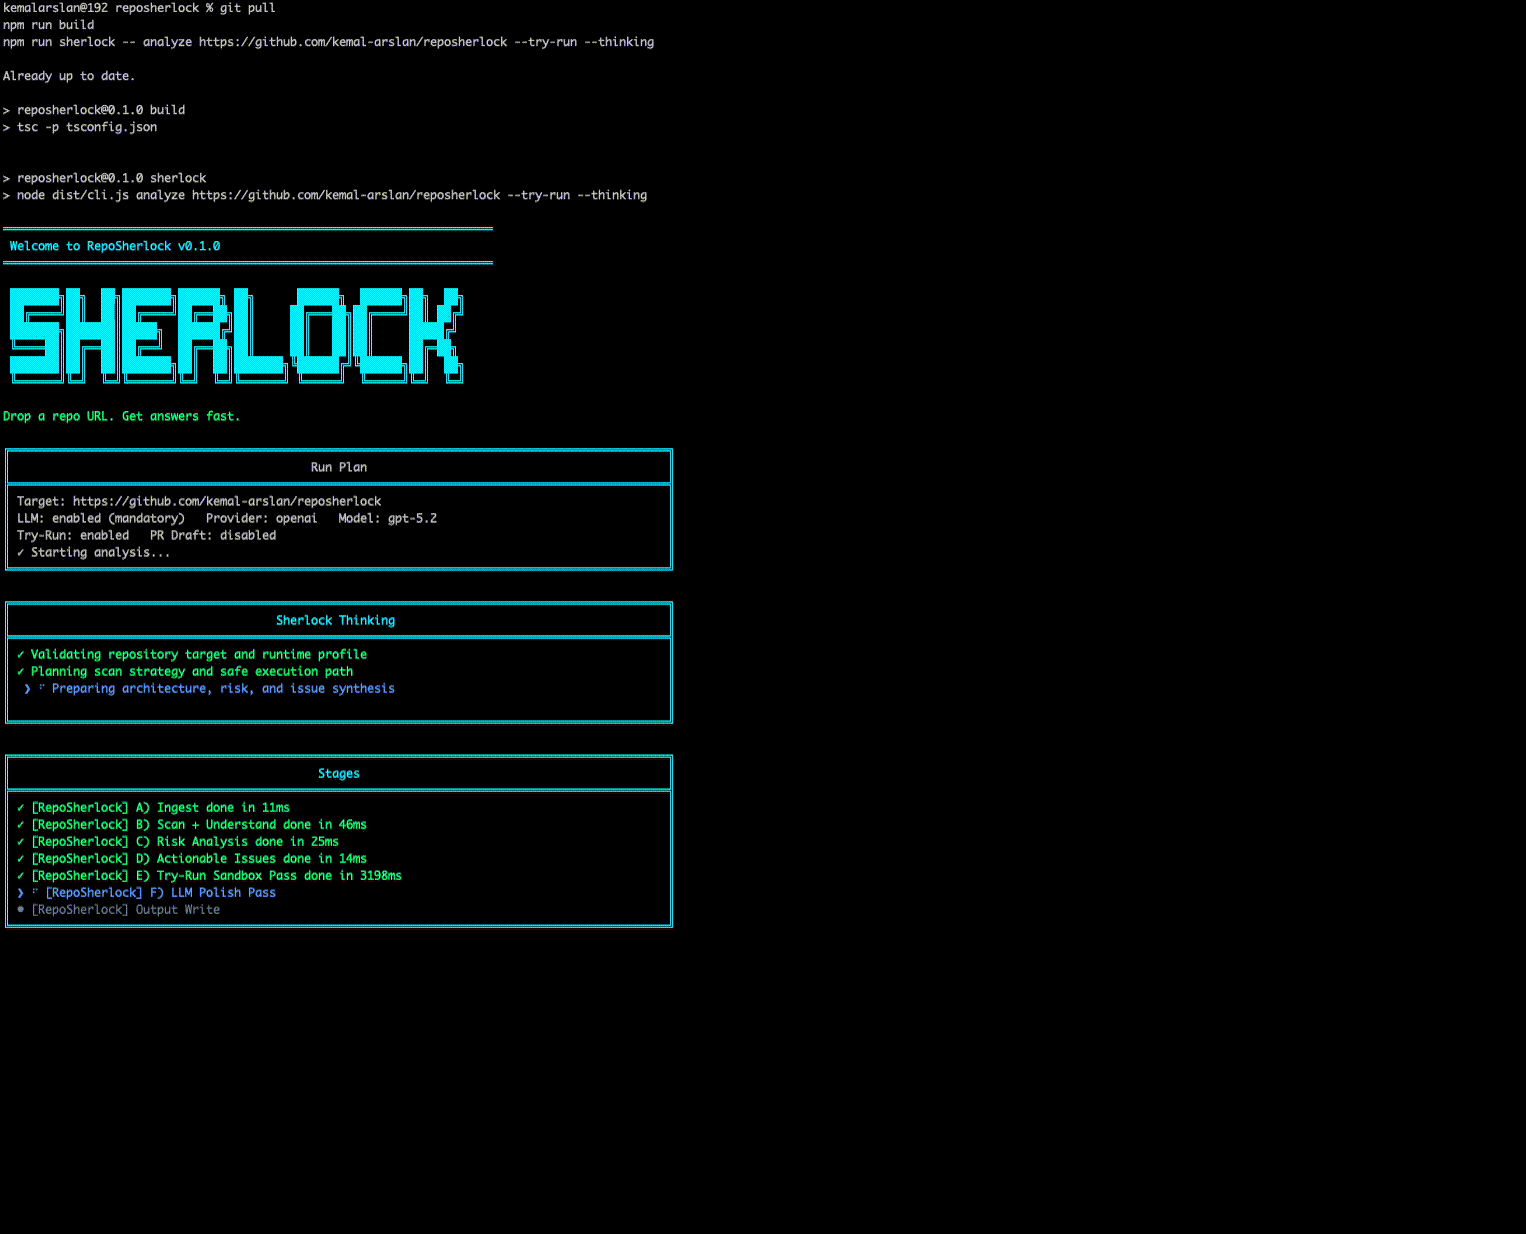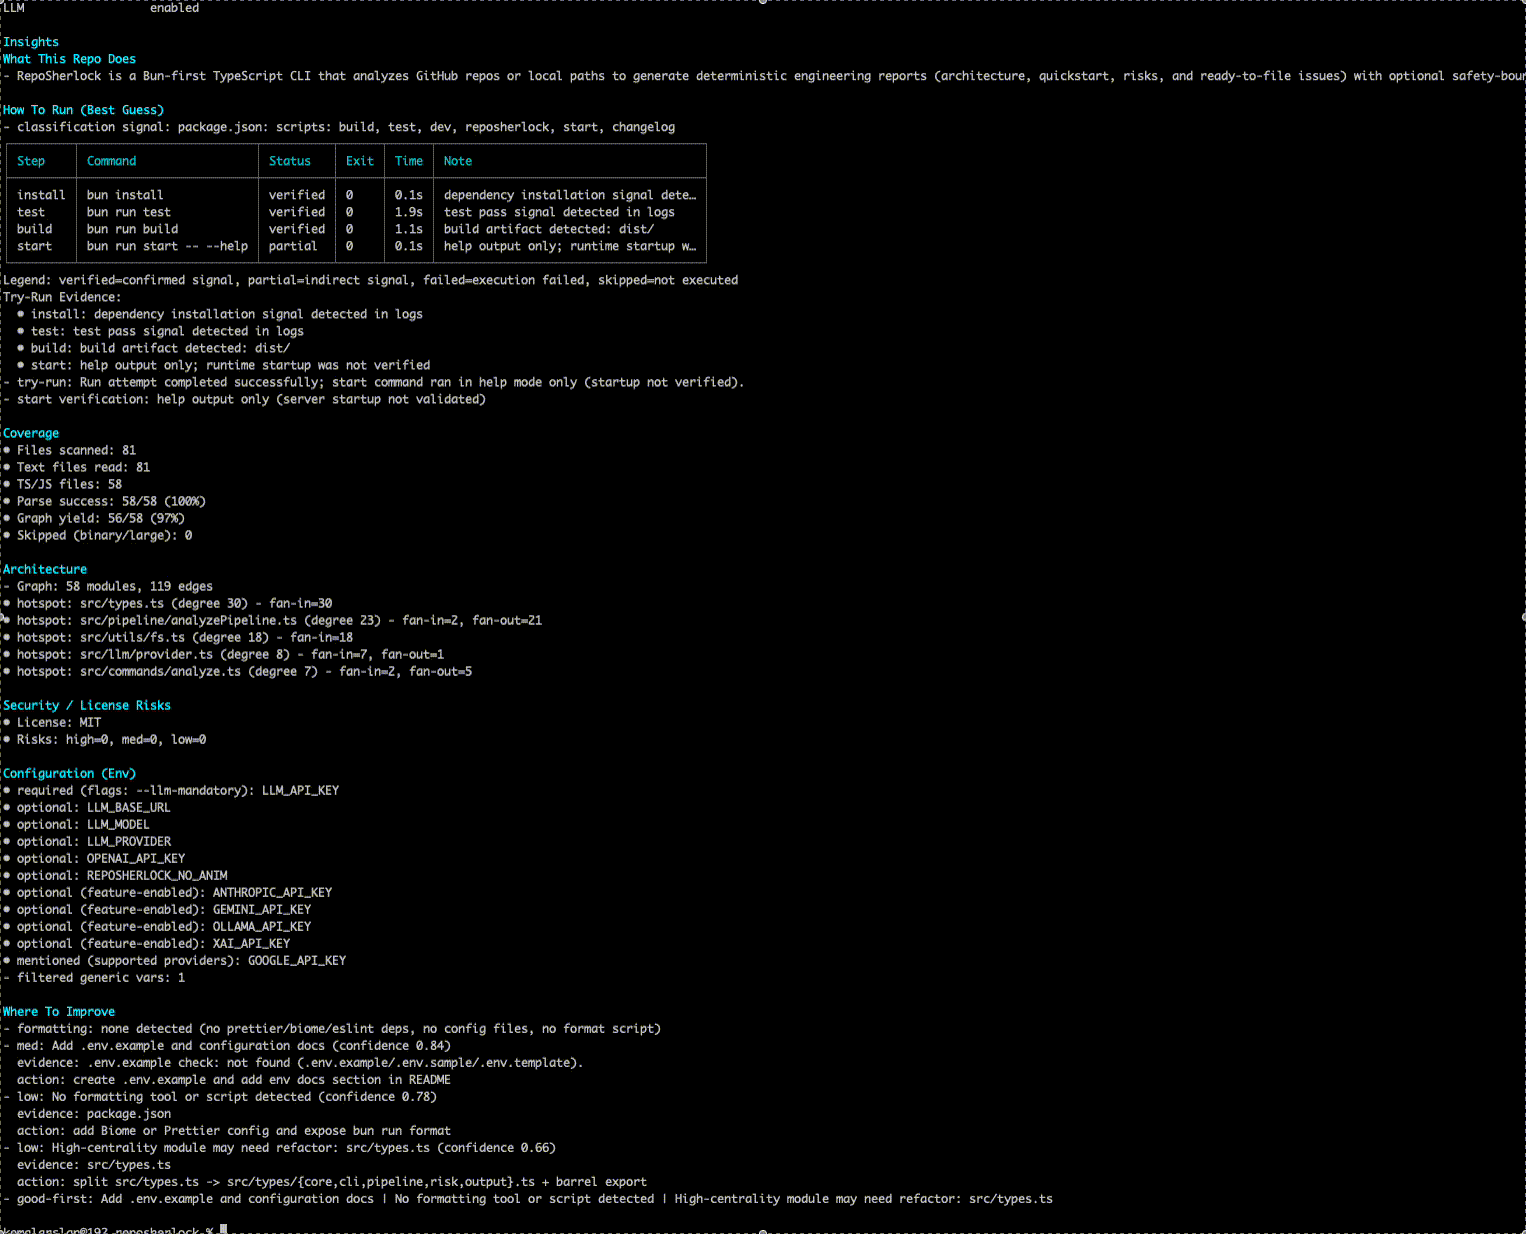
Analyze any GitHub repo (URL or local path) → architecture map, verified run commands, risks, and actionable issues - in minutes.
code-analysisdevsecopsmisconfiguration+4
2
kemal-arslan/reposherlockAnalyze any GitHub repo (URL or local path) → architecture map, verified run commands, risks, and actionable issues - in minutes.
 0xdsm/juumla
🦁 Python project to identify and scan for vulnerabilities related to the Joomla CMS project. It scans for common misconfigurations and public…
 nccgroup/go-pillage-registries
Pentester-focused Docker registry tool to enumerate and pull images
 zenzue/cve-2025-9074
Proof-of-concept exploit for CVE-2025-9074 demonstrating container-to-host file write via exposed Docker Engine API on Windows. For authorized…
 admin2099/penetration-testing-assessment-23-04-2026
Penetration testing assessment of a vulnerable IIS 6.0 WebDAV server, demonstrating reconnaissance, enumeration, exploitation (CVE-2017-7269), and…
 tsiddiquea/cve-reproduction-lab
Cybersecurity lab demonstrating Apache CVE-2021-41773 path traversal vulnerability with vulnerable server simulation, scanner, and security reporting.
 meganekos/secure-by-default-rce-demo
Secure-by-default demo lab showing how container hardening (distroless images, non-root, read-only filesystem, runtime-injected secrets) can…
 dev0558/cve-2023-32243-detection-and-mitigation-in-wordpress
Educational lab demonstrating detection and mitigation of CVE-2023-32243 privilege escalation in WordPress Essential Addons for Elementor, using…
 teycir/diffcatcher
A Rust CLI tool that recursively discovers Git repositories, captures state changes, generates diffs, extracts code elements with full snippets, and…
 yijikeji/cve-2022-29170
Grafana is an open-source platform for monitoring and observability. In Grafana Enterprise, the Request security feature allows list allows to…
 nickops87/spring4shell-python-firewall-poc
Proof-of-Concept (POC) of a simple firewall in Python designed to mitigate the Spring4Shell (CVE-2022-22965) RCE attack by inspecting and blocking…
 owasp/owasp-subtractive-hardening-top-10
The OWASP Subtractive Security Top 10 Project is an initiative to identify, document, and promote the highest-impact opportunities for reducing cyber…
 yagnikkrish/metasploitable-penetration-testing-lab
Controlled penetration testing lab demonstrating CVE-2011-2523 exploitation and mitigation techniques.
 bitnesswise/jquery-prototype-pollution-fix
A fix for CVE-2019-11358 (prototype pollution in jquery)
 ovotech/domain-protect
Automated detection of vulnerable domain configurations and subdomain takeover risks across cloud environments, with continuous monitoring and…
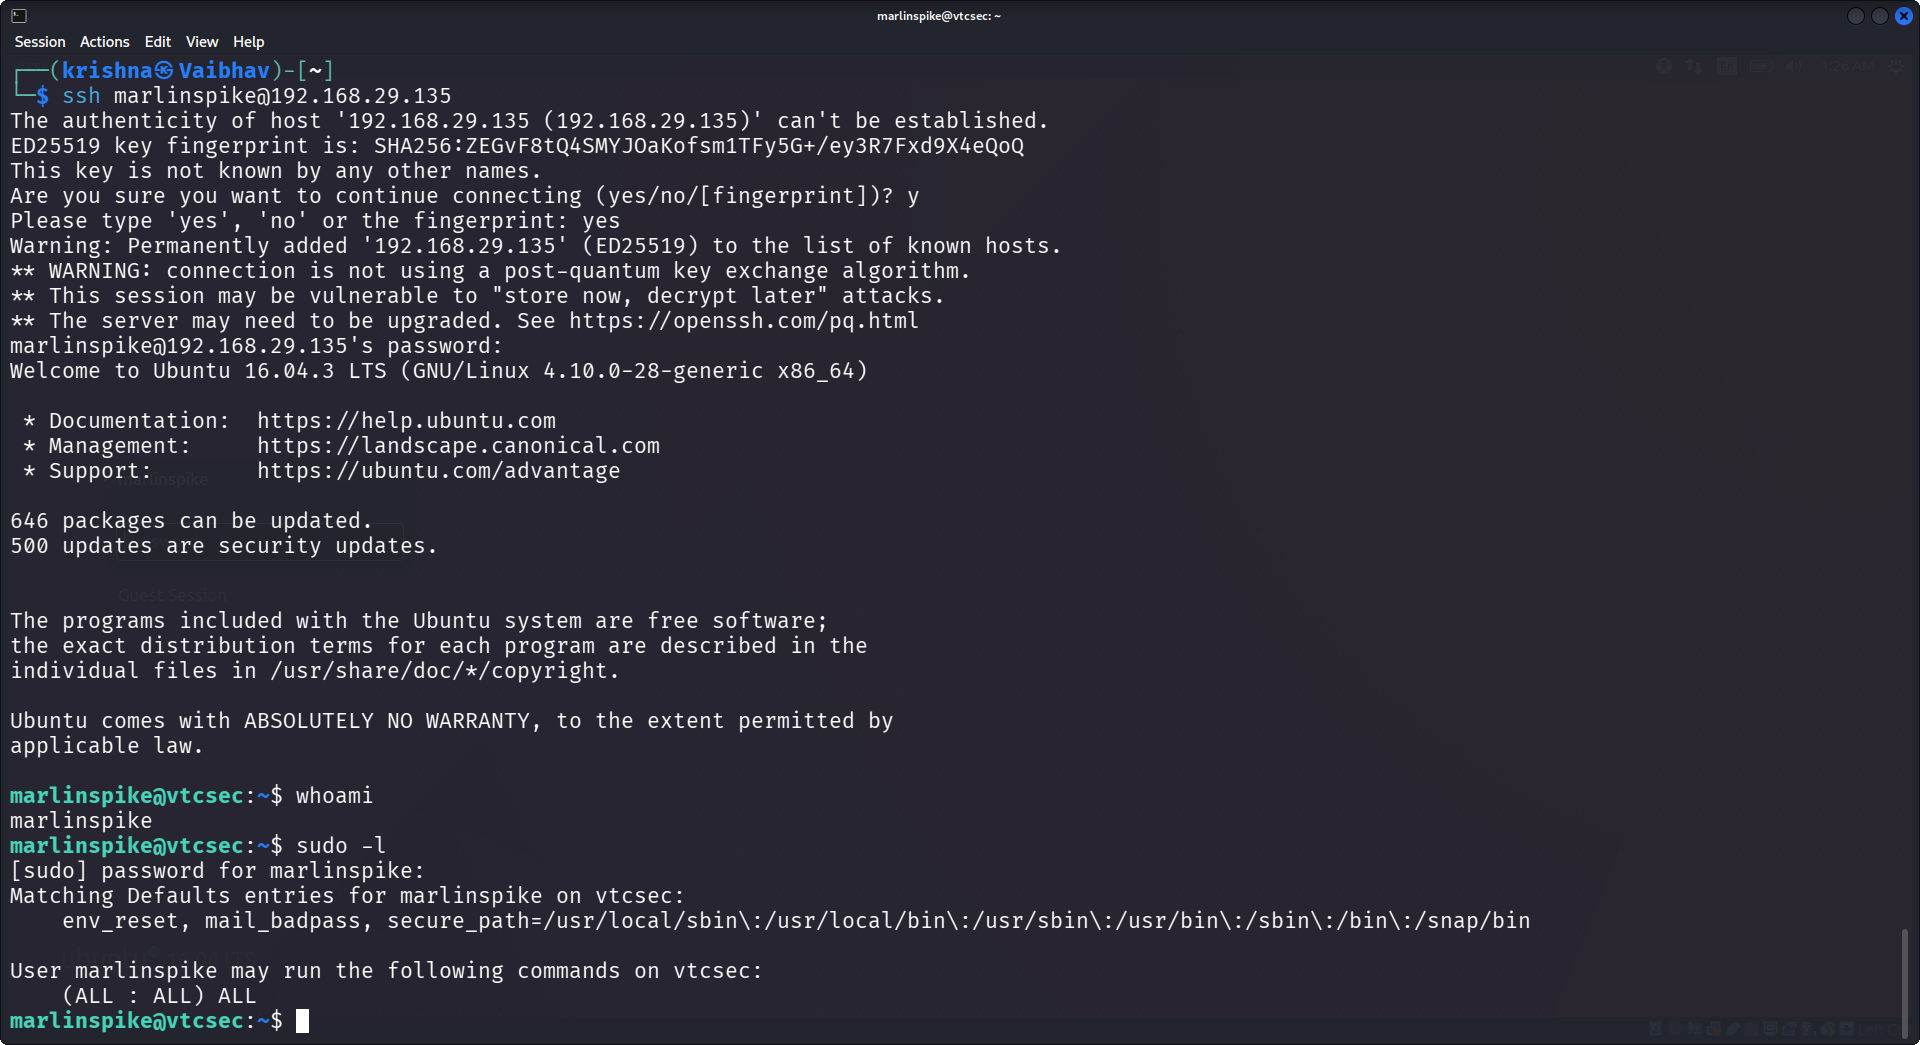 vaibhavkrishna12004/ubuntu-privesc-lab
Full penetration testing workflow: credential brute force, SSH access and privilege escalation (CVE-2021-4034)
 nccgroup/crosssitecontenthijacking
Content hijacking proof-of-concept using Flash, PDF and Silverlight
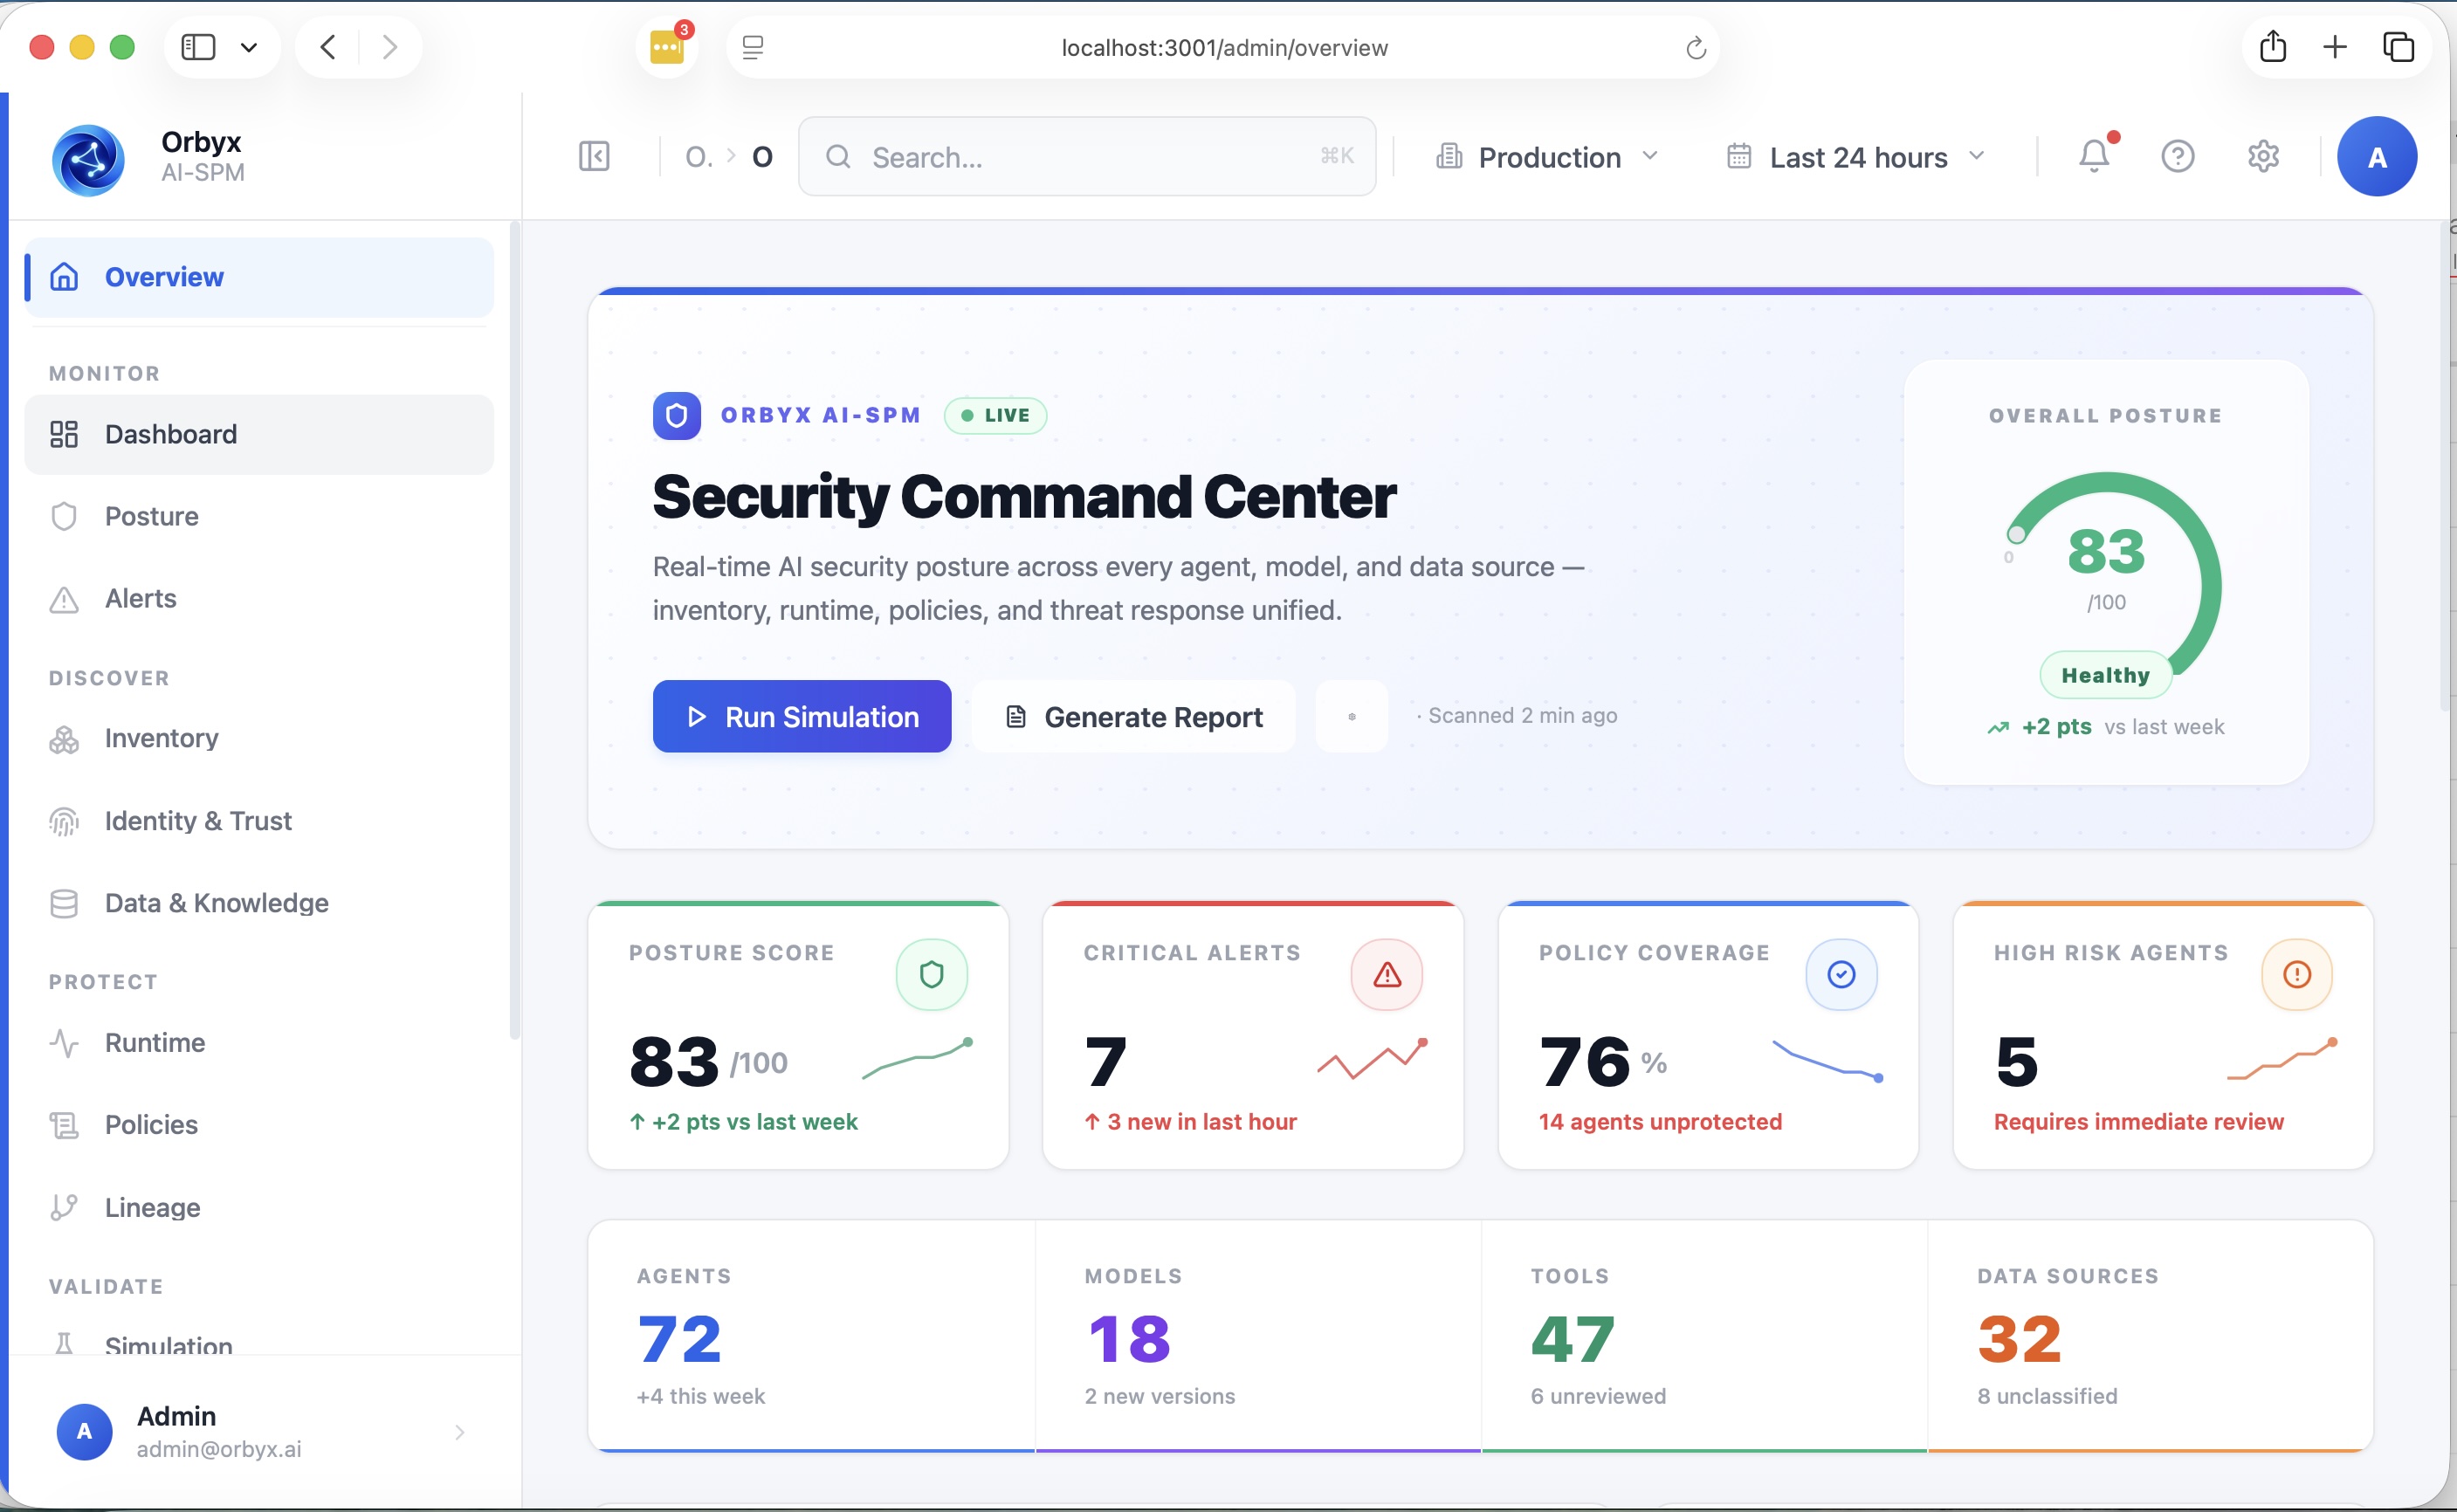 dshapi/ai-spm
This opensource project dedicated to implementing Enterprise level AI-SPM. By doing so organizations can proactively protect their AI systems from…