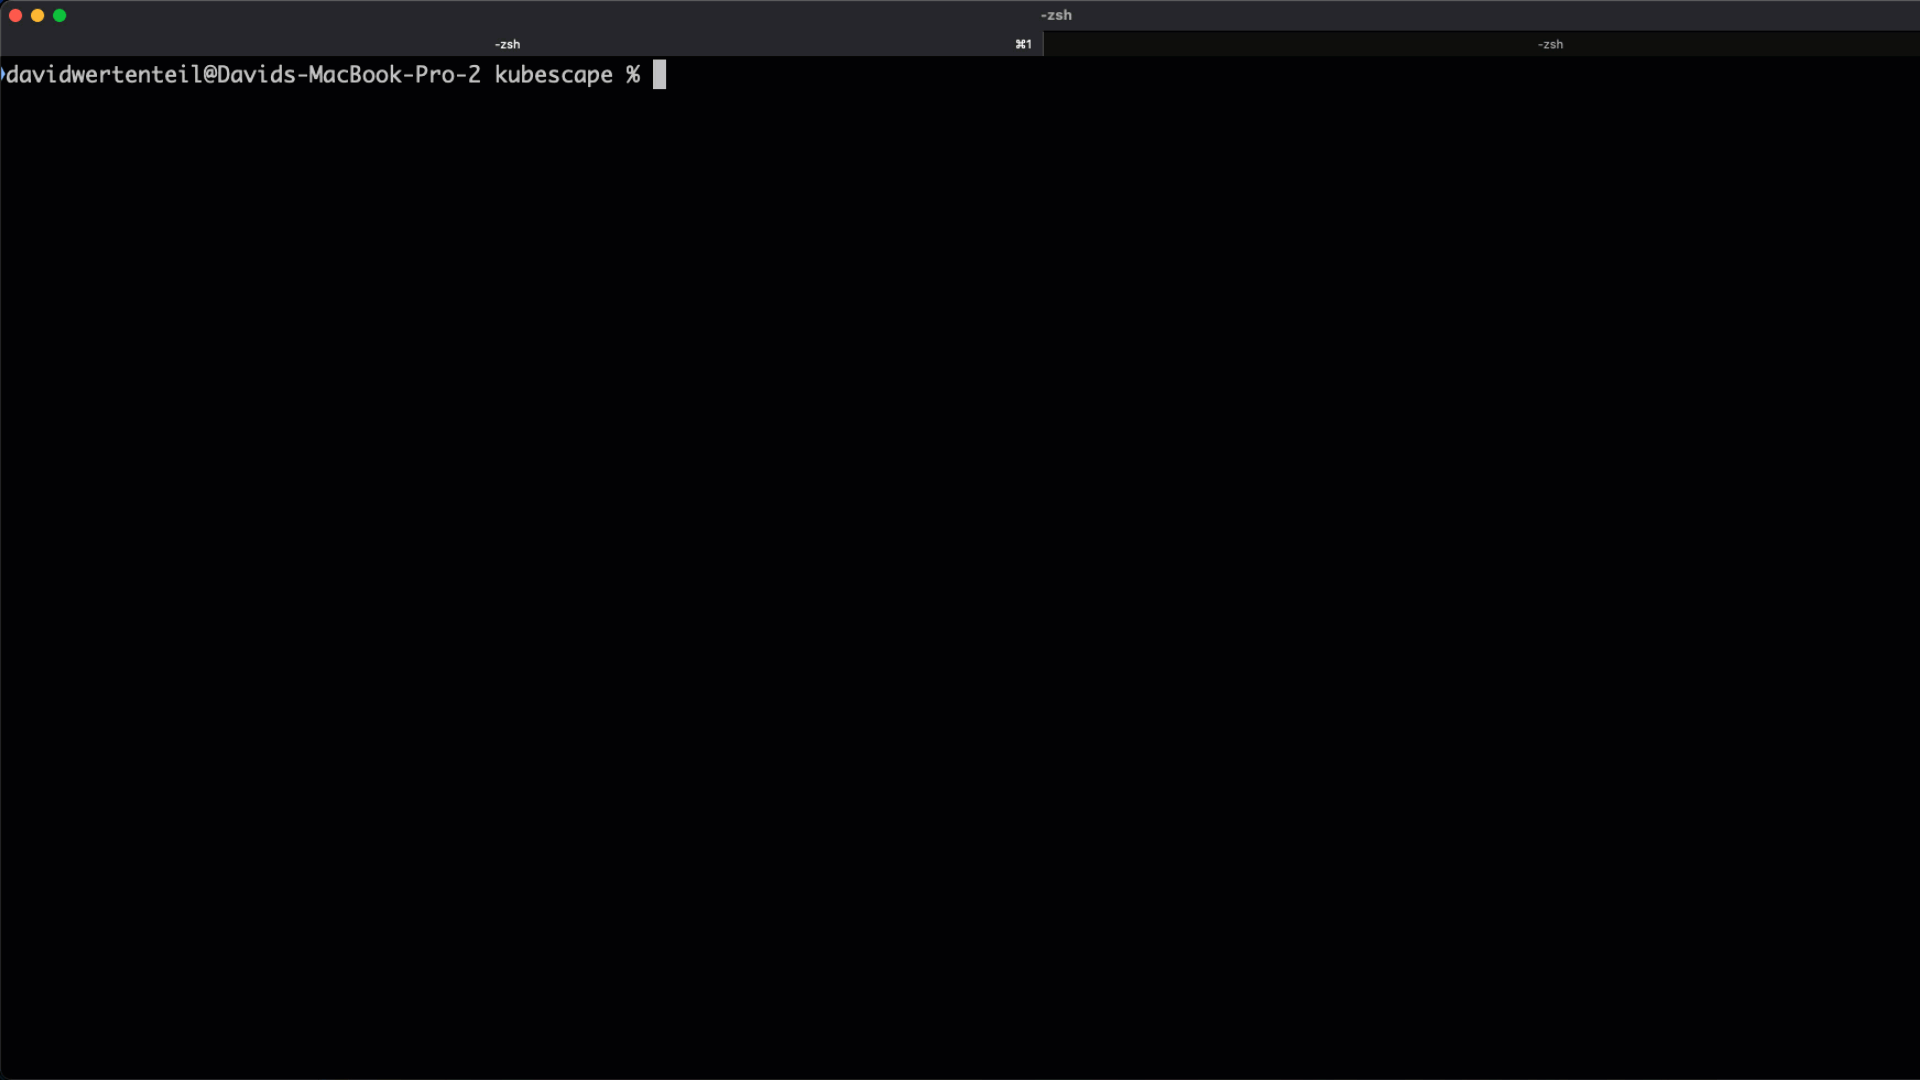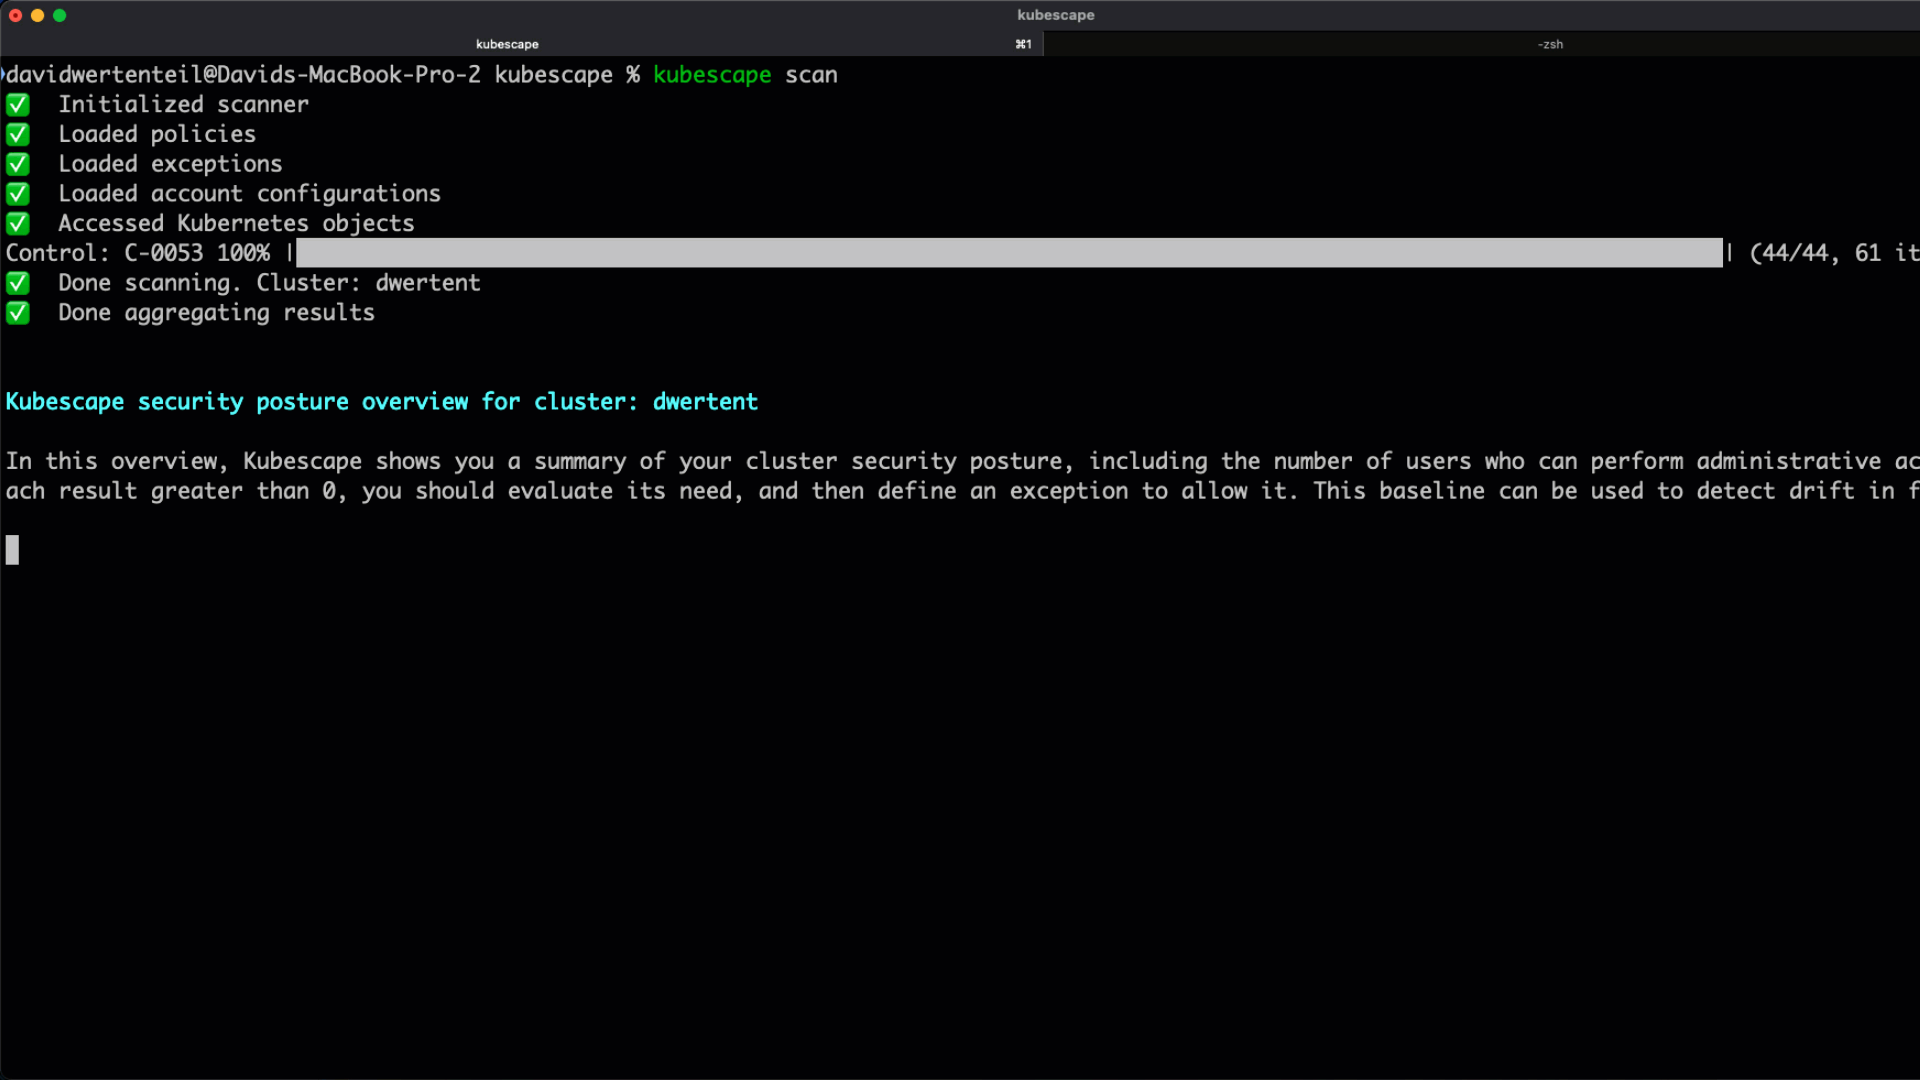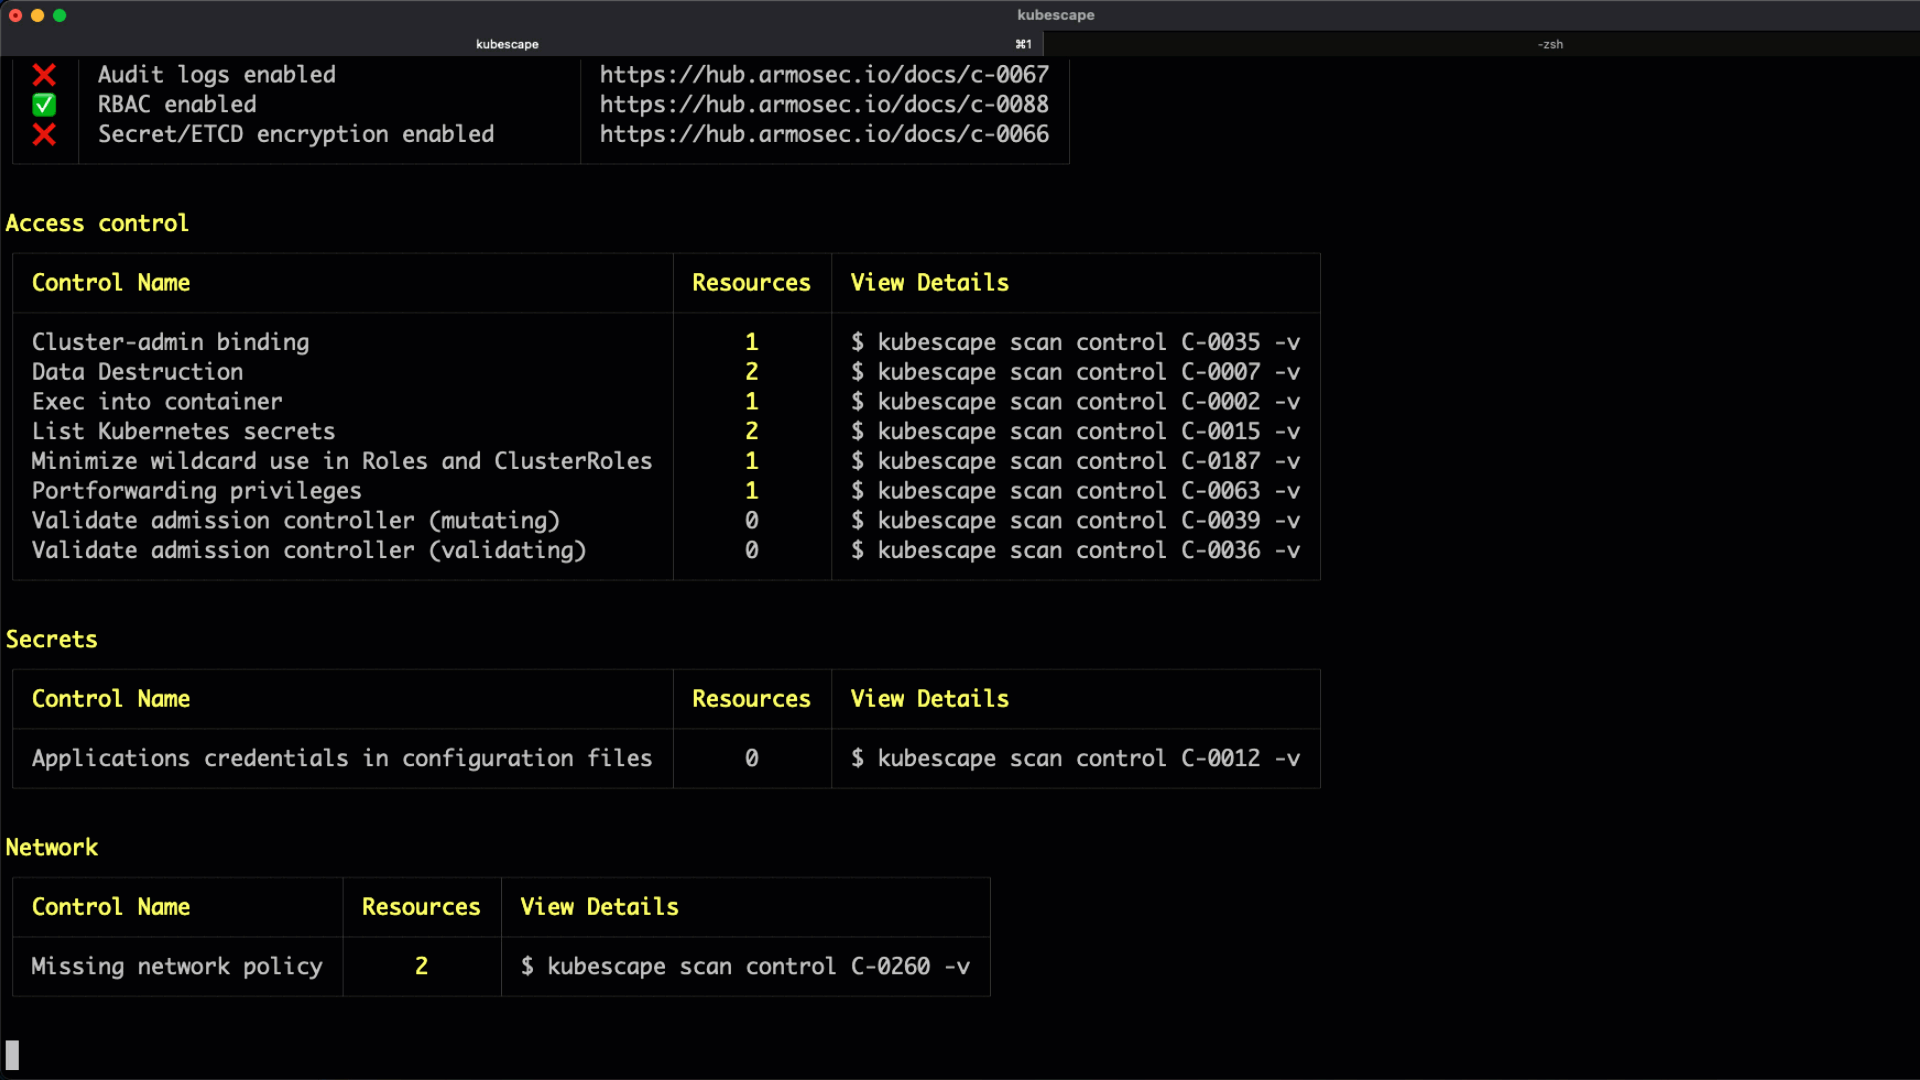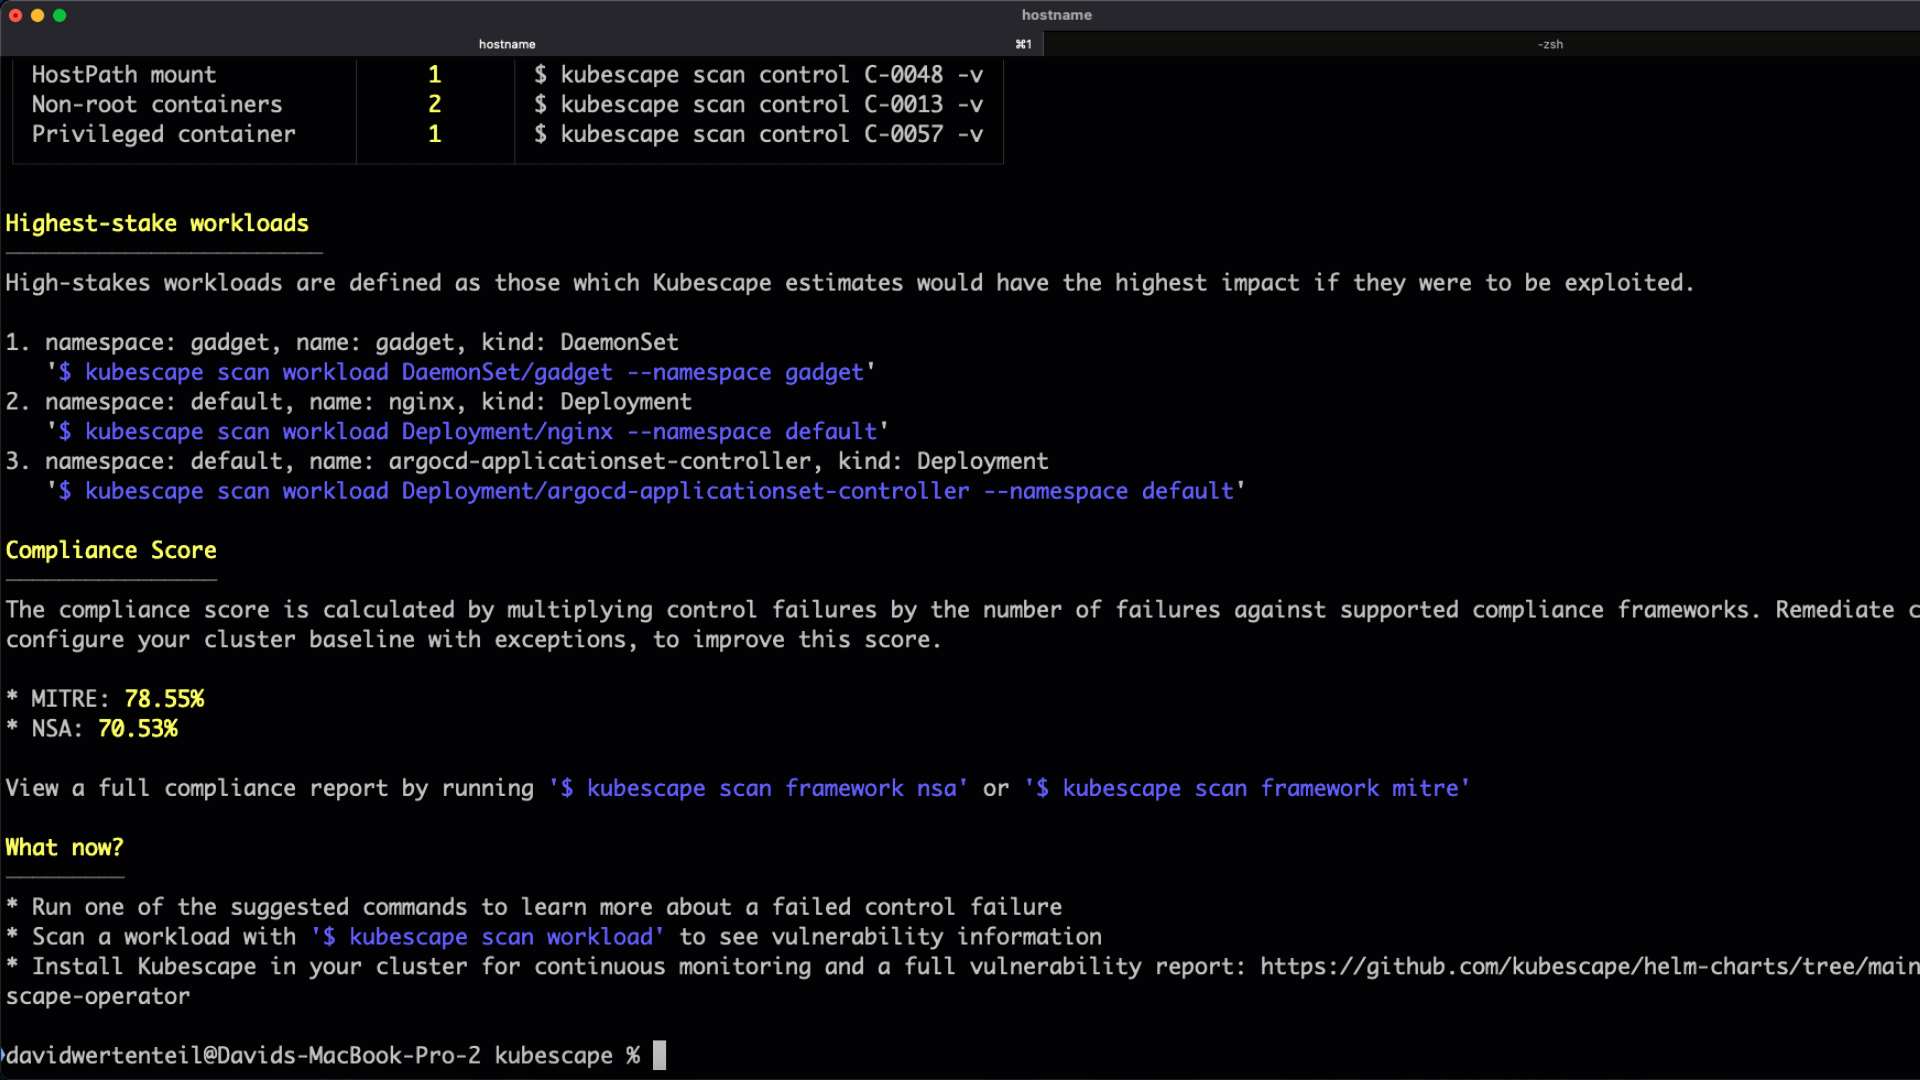

kubescape
Open-source Kubernetes security platform scanning clusters, manifests, and images for misconfigurations, vulnerabilities, and compliance against NSA,…

Open-source Kubernetes security platform scanning clusters, manifests, and images for misconfigurations, vulnerabilities, and compliance against NSA,…

Full VAPT writeup of OWASP CICD-Goat — 9 CTFd flags captured, 4 critical + 5 high findings (incl. CVE-2024-23897) mapped to the OWASP Top 10 CI/CD…

A Rust CLI tool that recursively discovers Git repositories, captures state changes, generates diffs, extracts code elements with full snippets, and…

WP Full Stripe Free <= 8.4.3 - Missing Authorization

This Bash script checks domains for DNS zone transfer misconfigurations (CVE-1999-0532). It queries name servers and attempts AXFR requests; if…

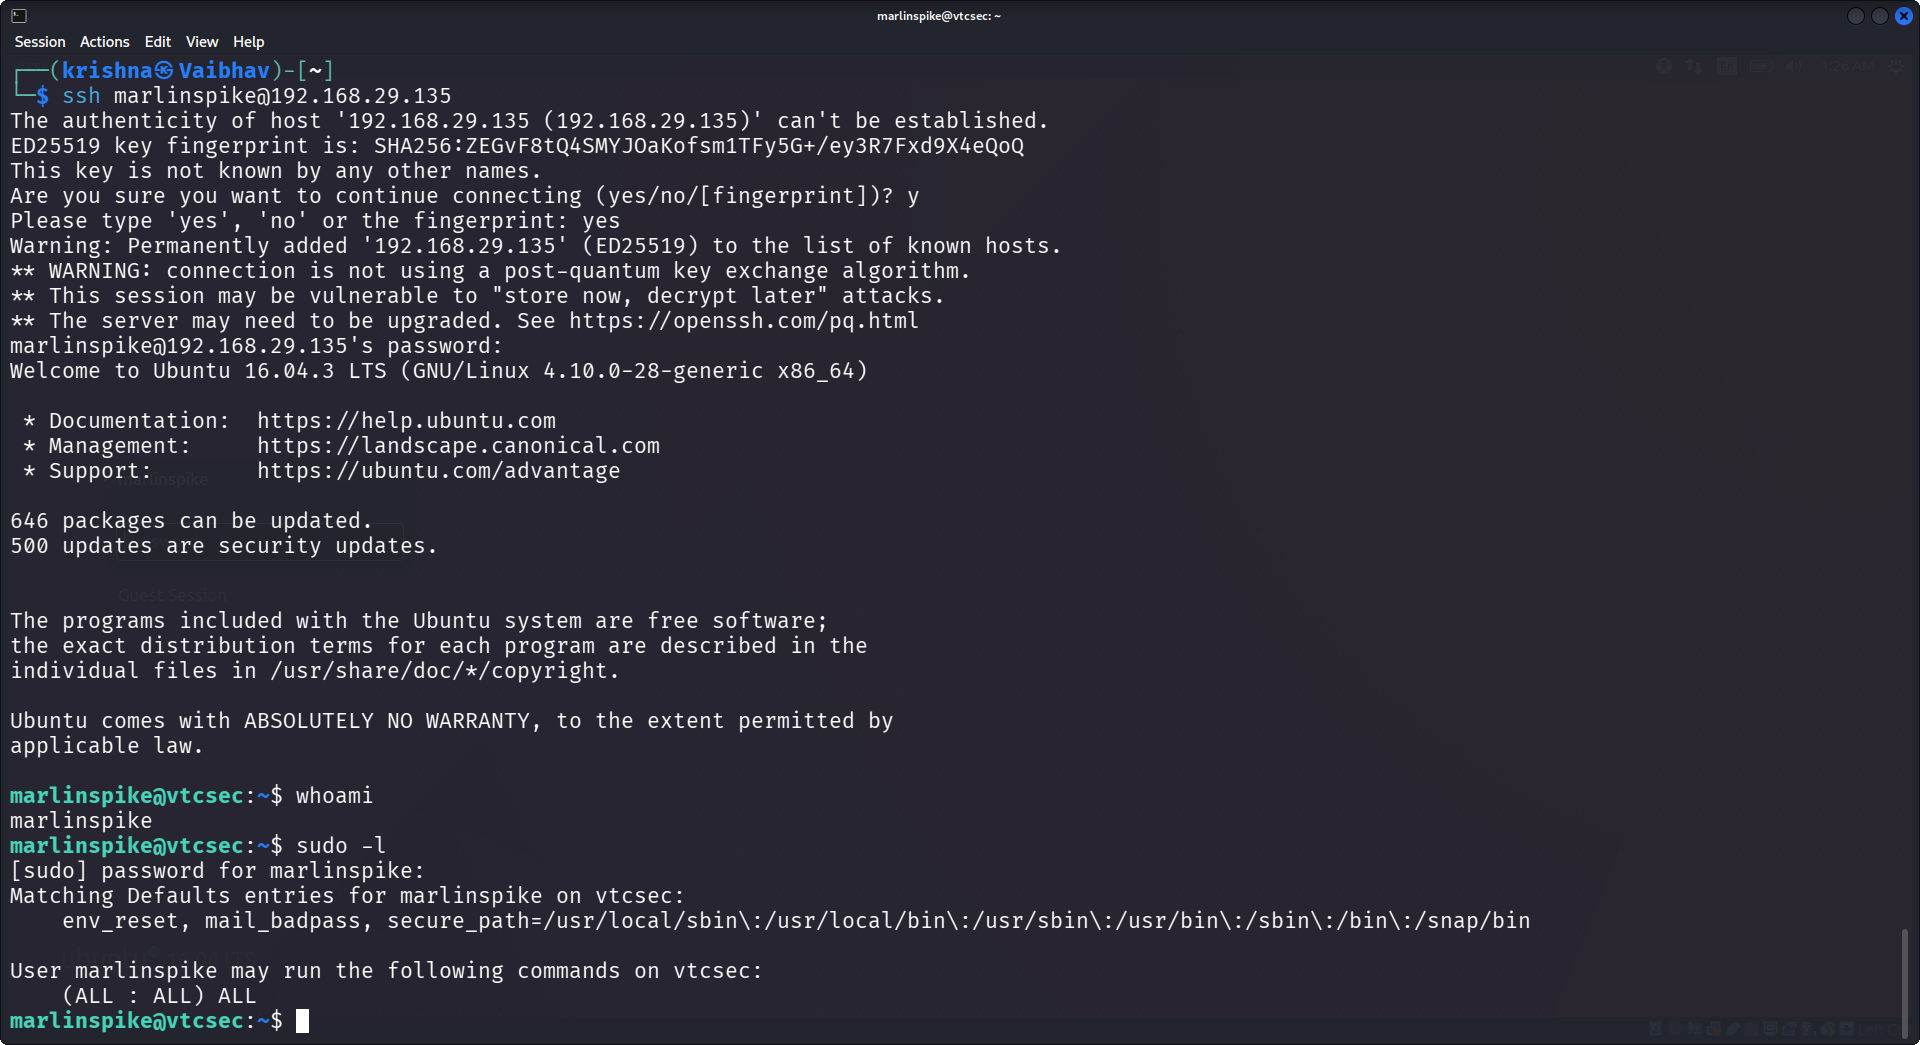
Full penetration testing workflow: credential brute force, SSH access and privilege escalation (CVE-2021-4034)

AdmirorFrames Joomla! Extension < 5.0 - Full Path Disclosure

A fast, portable, and lightweight COSE + CBOR implementation for embedded systems. Supports PQC, FIPS 140-3, DO-178, and MISRA C. Powered by wolfSSL.

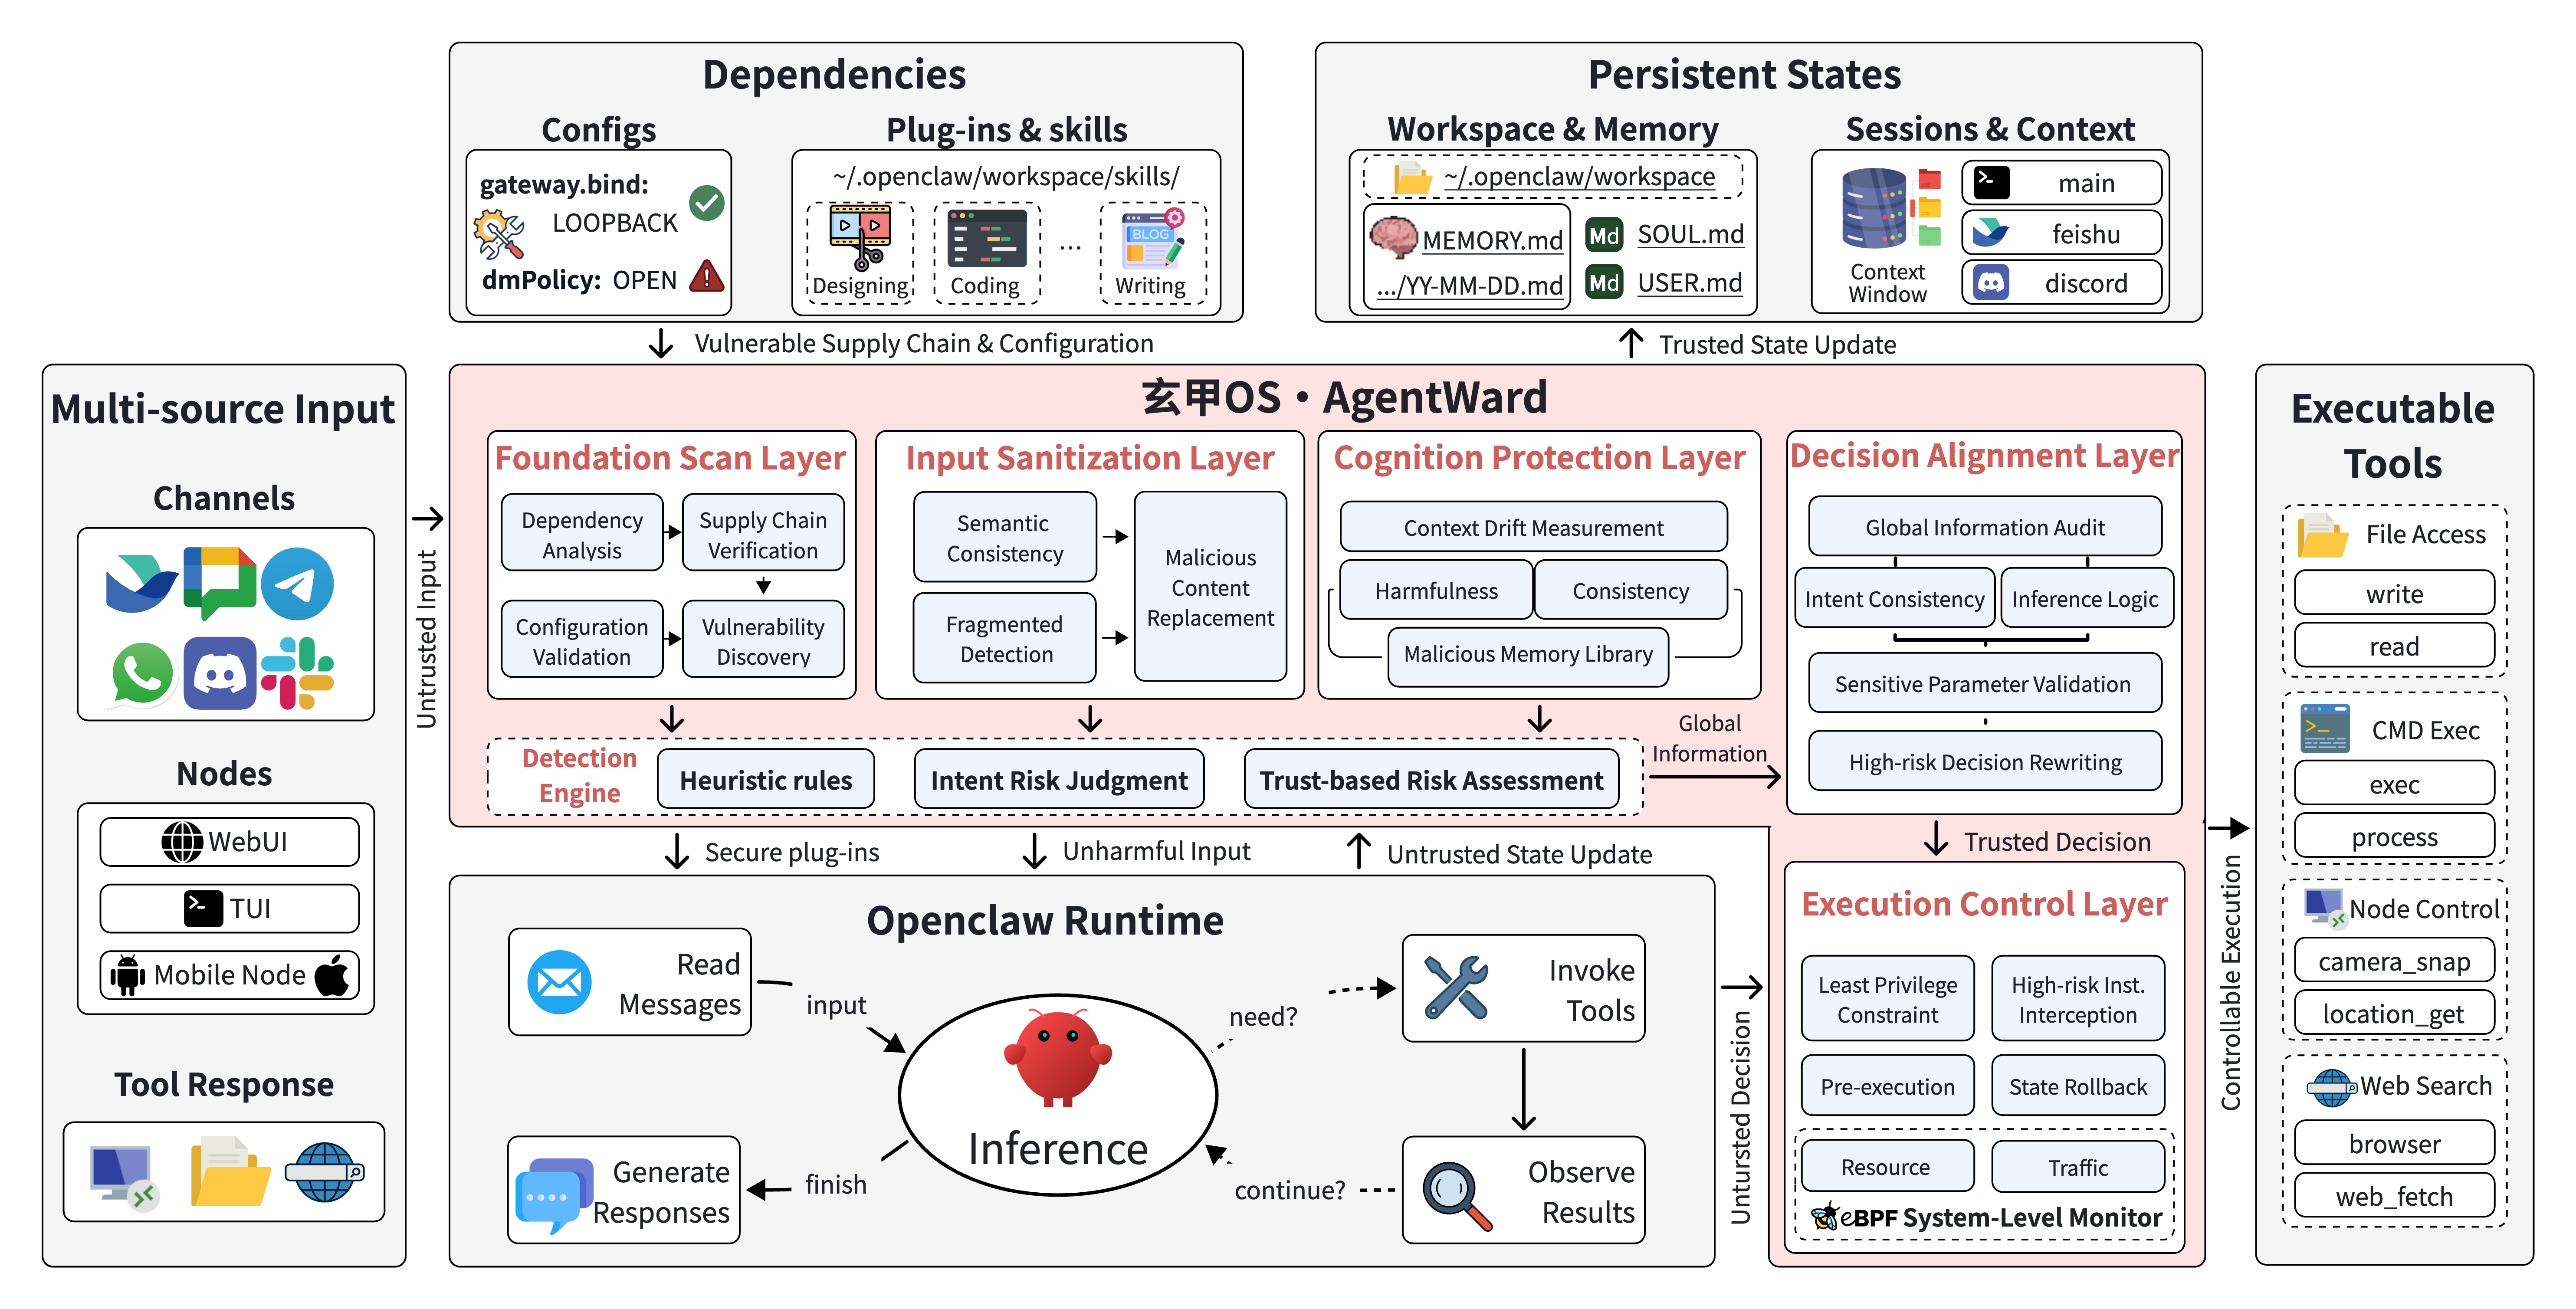
Full-stack security OS for AI agents with five-layer defense-in-depth architecture covering foundation scan, input sanitization, cognition…

Full-stack platform for authorized web application security scanning with a detector-based engine, async Celery workers, and a React dashboard for…

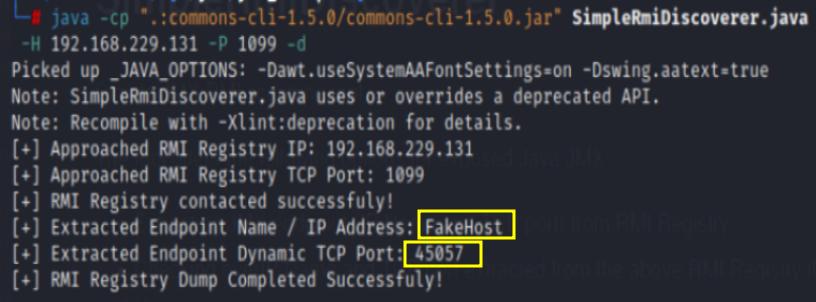
Simple JMX RMI scanning tool

Cisco CVE-2023-20198

Azure IoT Hub where exposure of an owner-level Shared Access Key enables unauthenticated remote code execution (RCE) against connected IoT devices.…

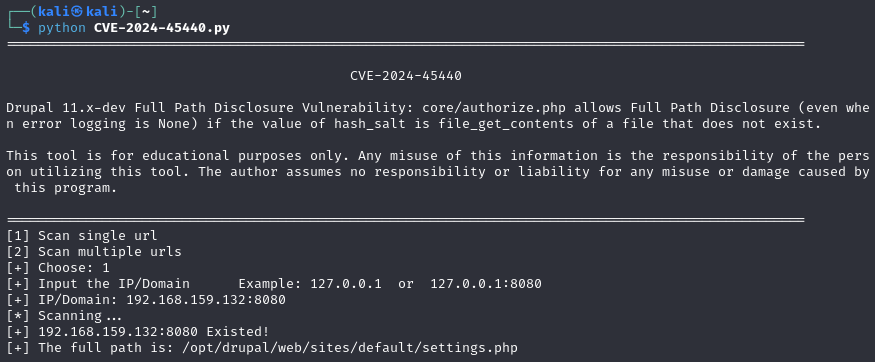
Drupal CVE-2024-45440

Proof-of-concept exploit for CVE-2026-21994, demonstrating unauthenticated admin session forgery via a hardcoded Flask SECRET_KEY and SSH host…

Unauthenticated disclosure of internal folder path, client email, and upload policy for FileRise Pro client portals via /api/pro/portals/get.php