
prowler
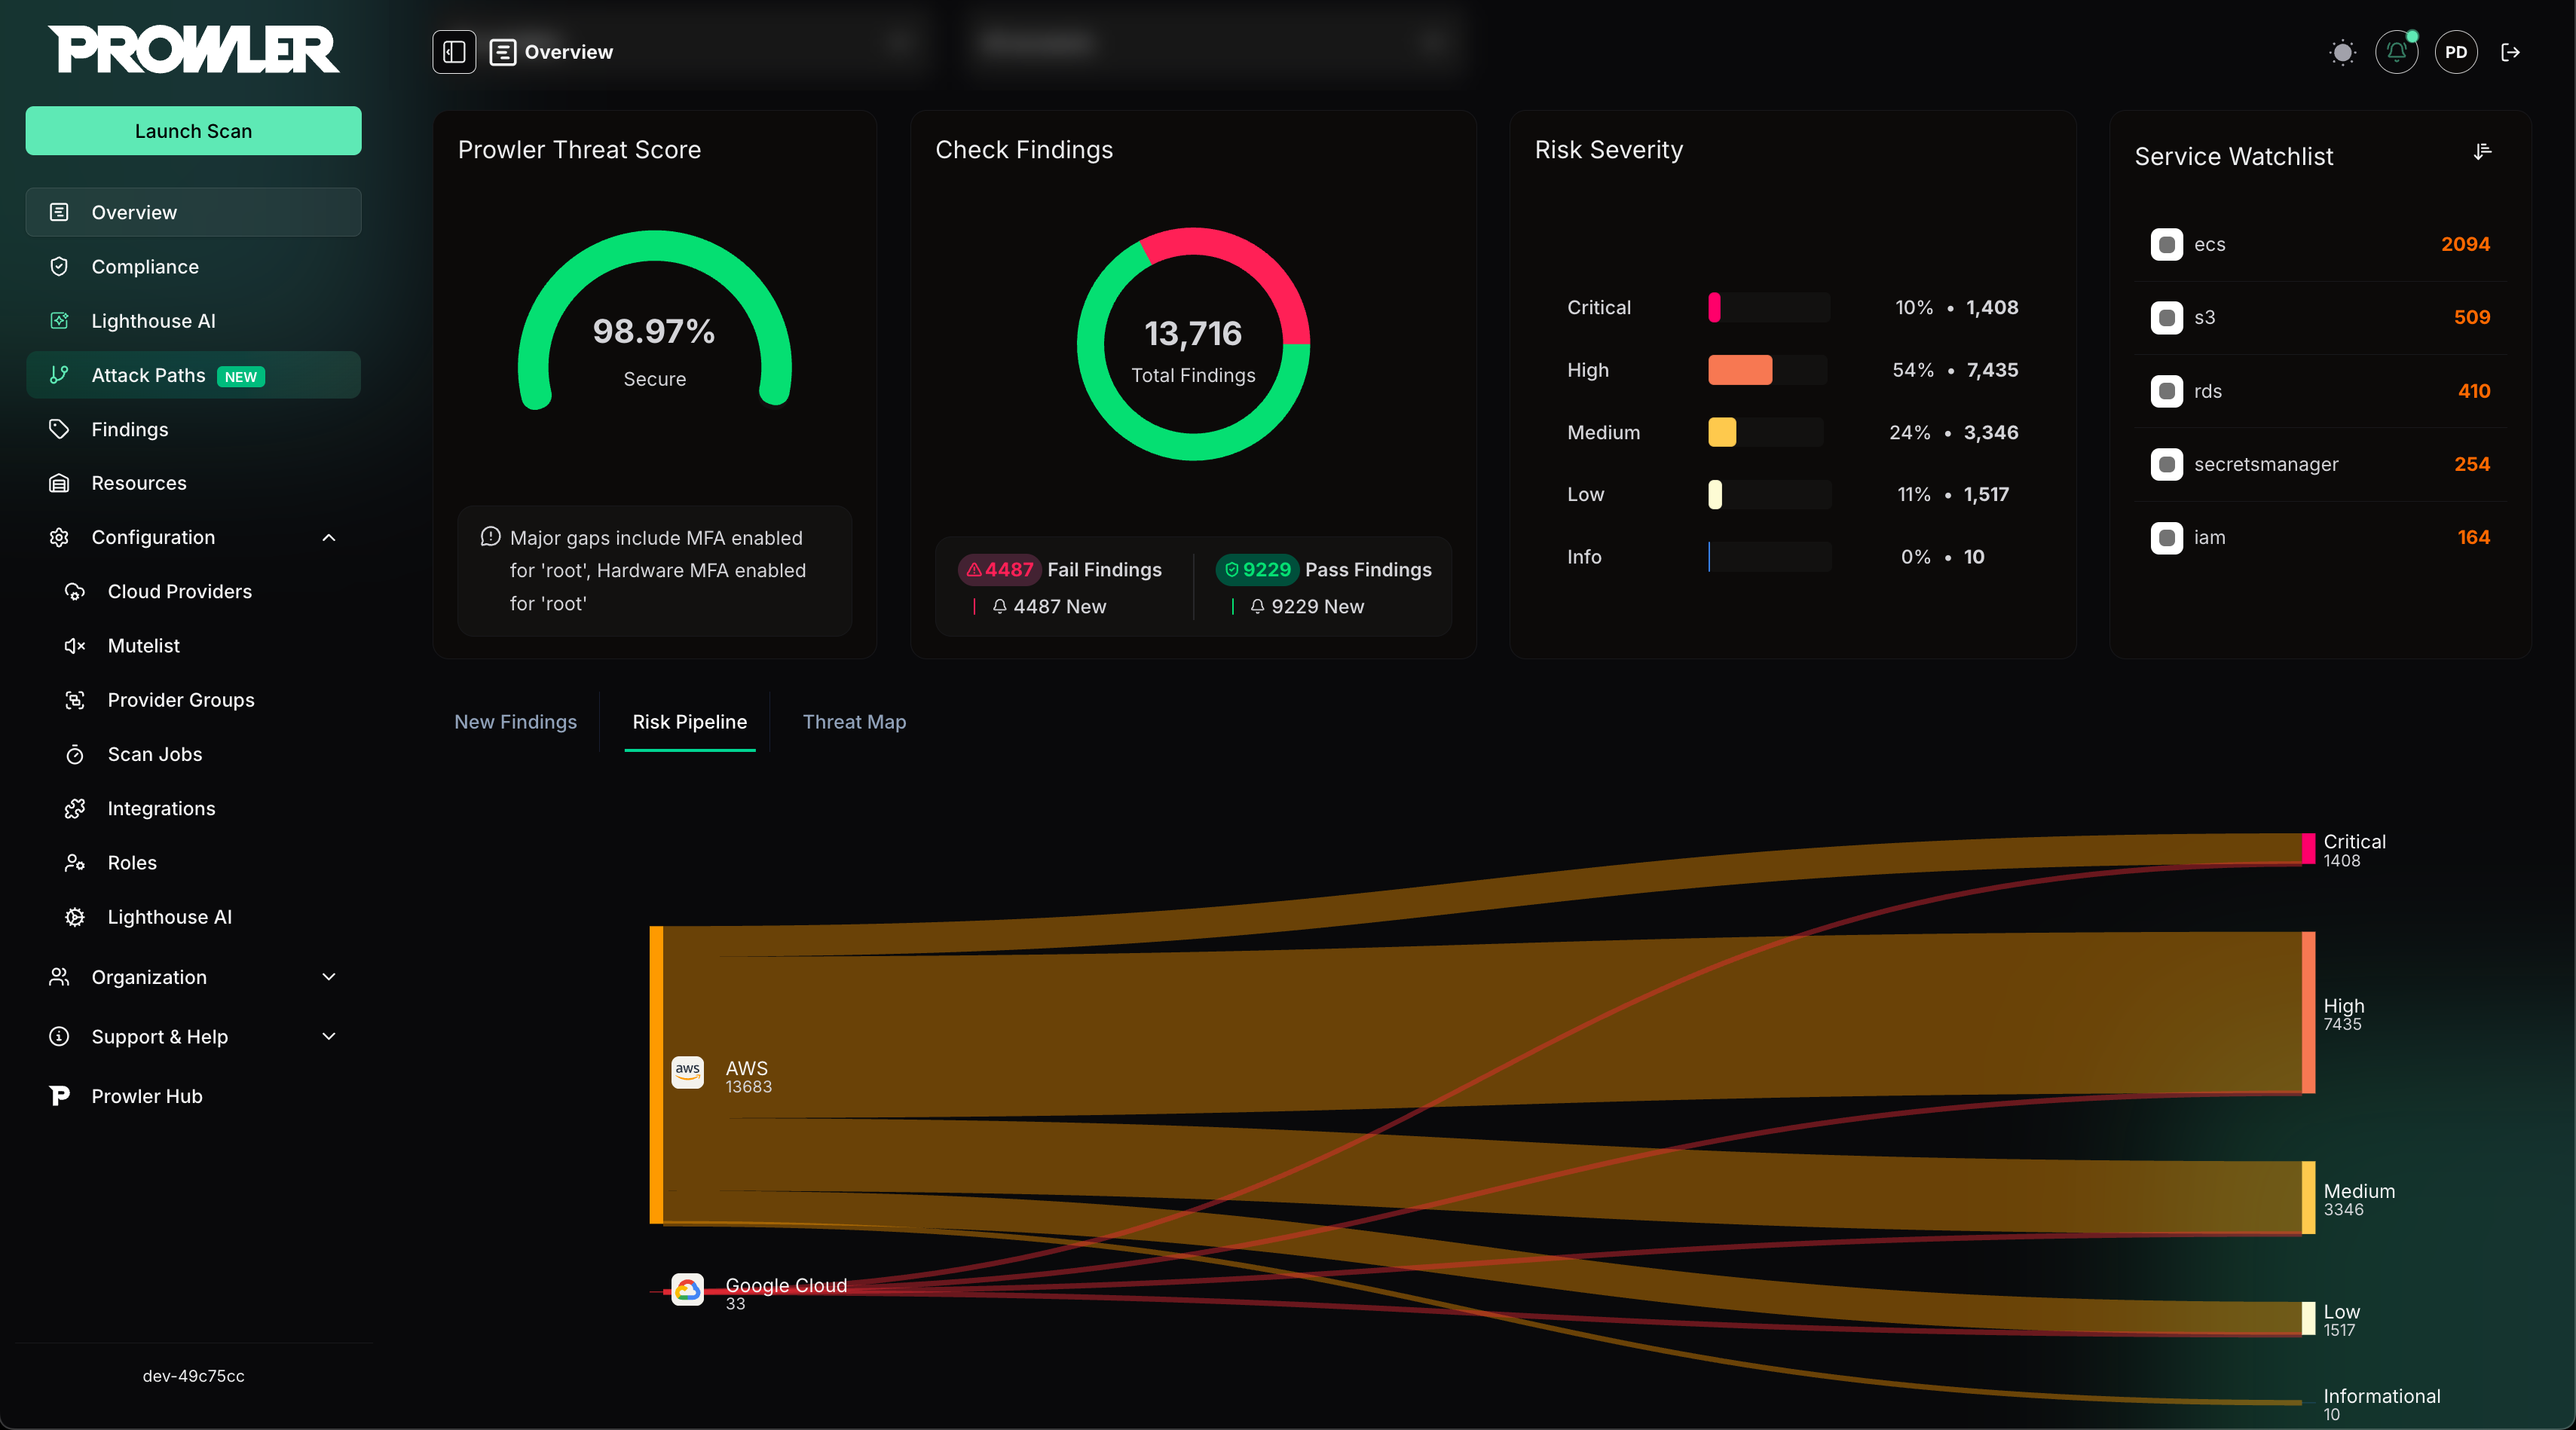
Prowler is the world’s most widely used open-source cloud security platform that automates security and compliance across any cloud environment.…

Prowler is the world’s most widely used open-source cloud security platform that automates security and compliance across any cloud environment.…

Open-source Kubernetes security platform scanning clusters, manifests, and images for misconfigurations, vulnerabilities, and compliance against NSA,…

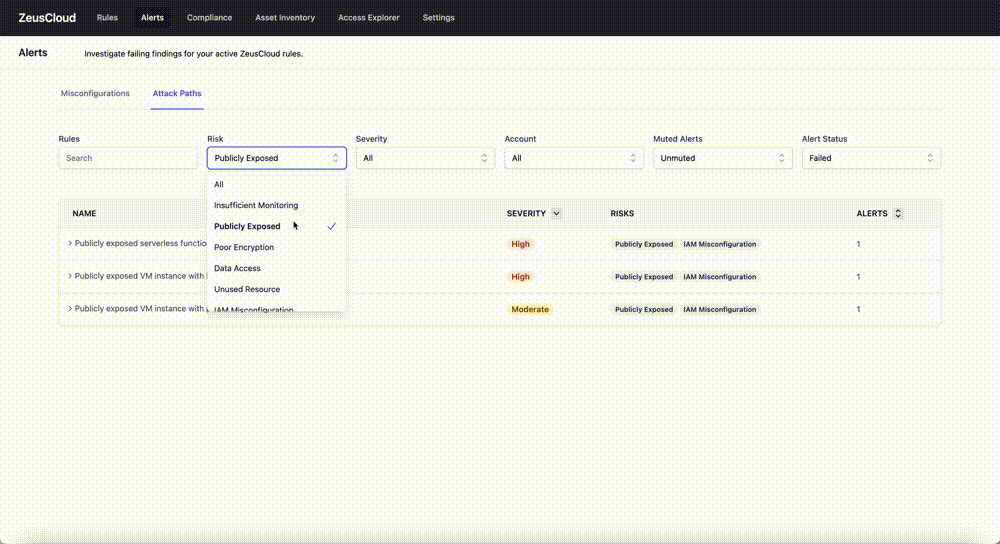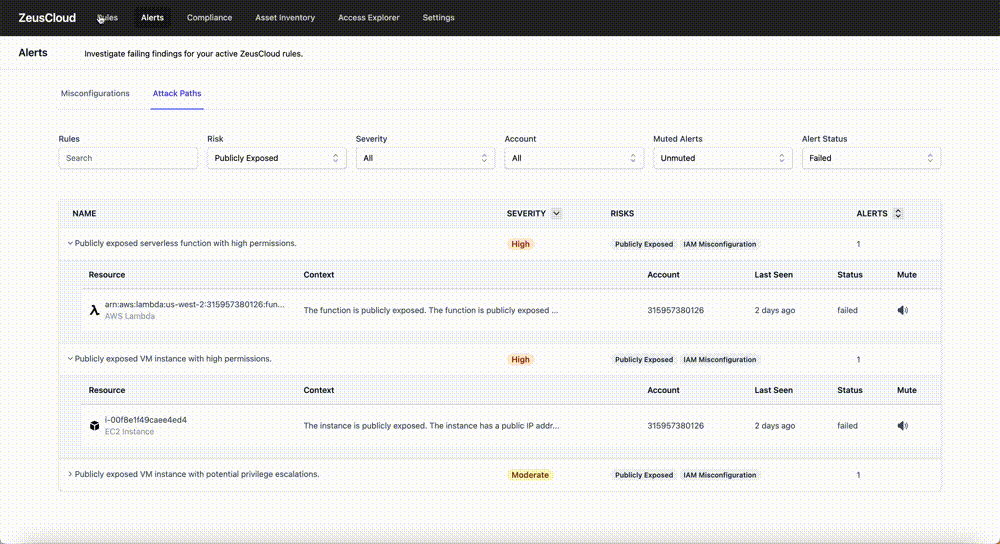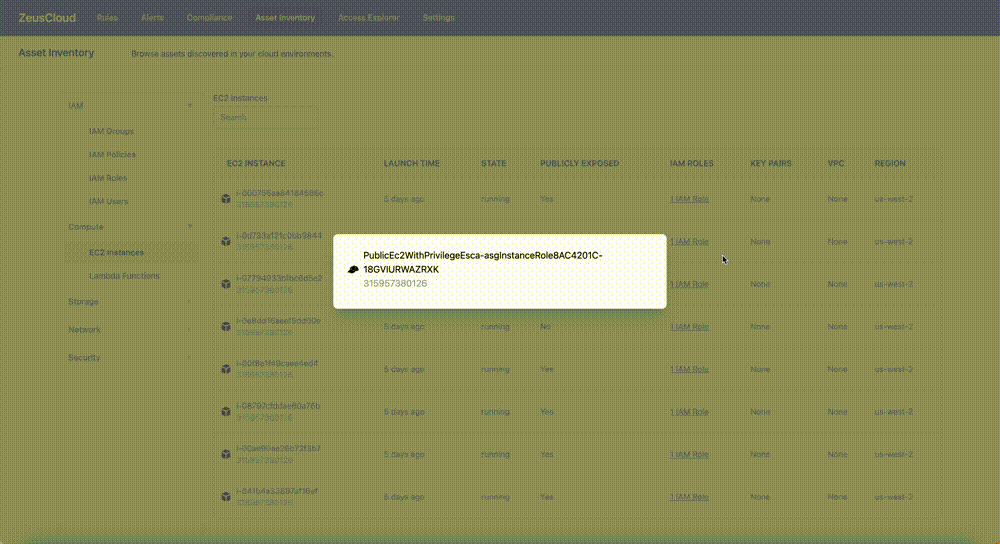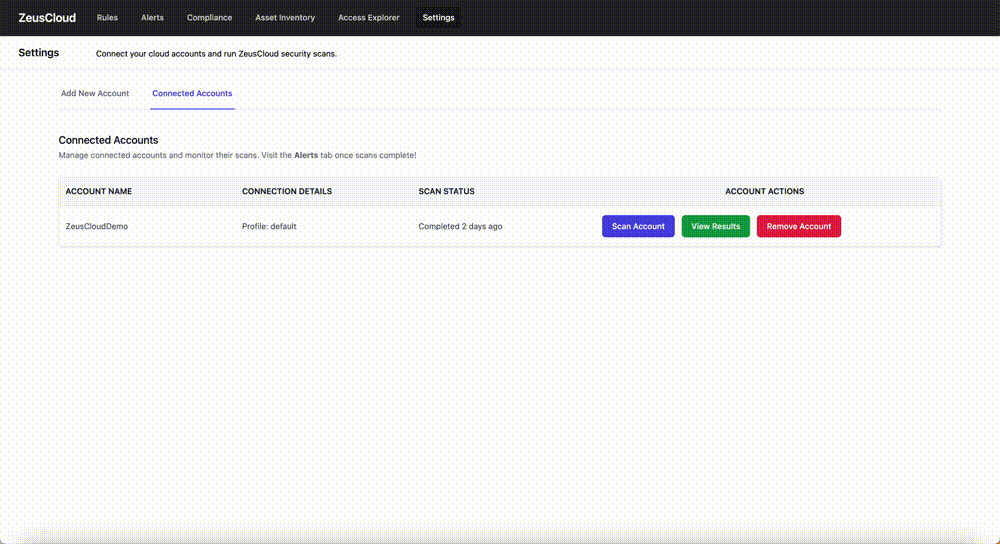
Open-source cloud security platform that discovers attack paths, identifies misconfigurations, visualizes IAM access, and provides step-by-step…

Kubernetes Security Training Platform - focusing on security mitigation

An open testing platform that probes HTTP/1.1 servers against RFC 9110/9112 requirements, smuggling vectors, and malformed input handling. Add your…

Full-stack platform for authorized web application security scanning with a detector-based engine, async Celery workers, and a React dashboard for…

Aurea is an open-source, AI-powered platform that secures infrastructure-as-code (IaC) across Terraform, Kubernetes, Docker, and Ansible. It…

CVE-2024-55963, allows unauthenticated remote code execution on Appsmith Enterprise platform due to a misconfigured PostgreSQL database included by…

RSA NetWitness Platform EDR Agent / Incorrect Access Control - Code Execution

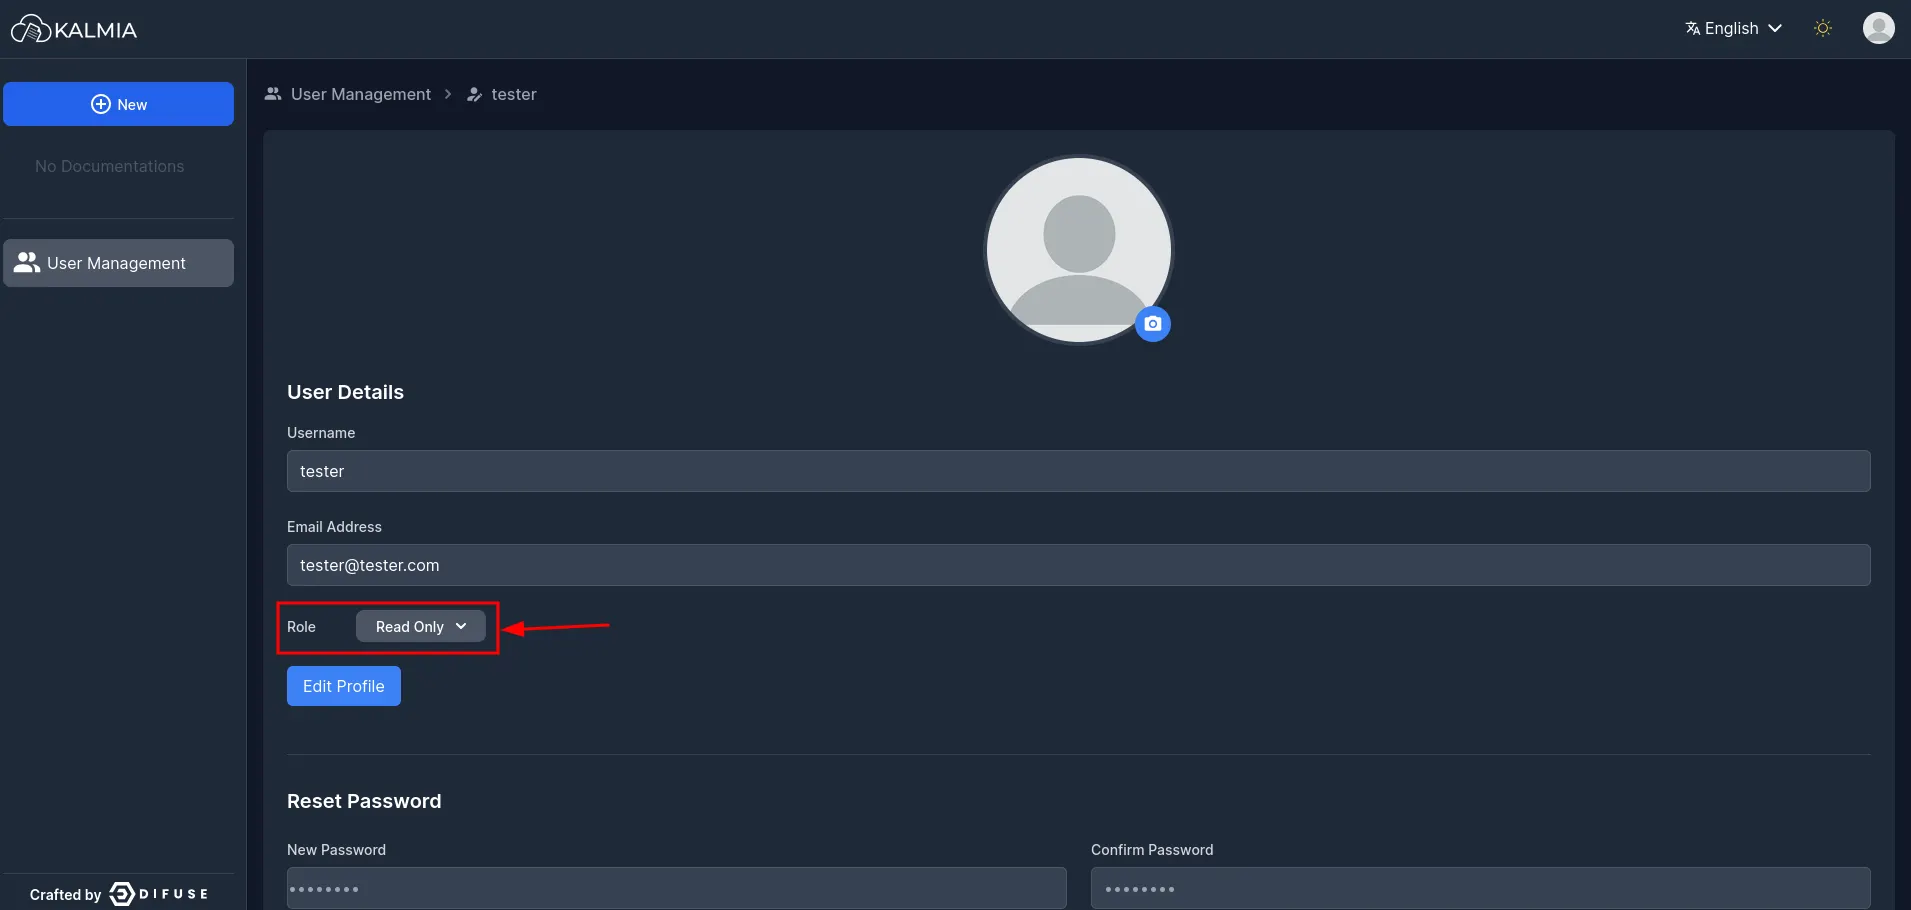
DifuseHQ Kalmia CMS version 0.2.0 contains an Incorrect Access Control vulnerability in the /kal-api/auth/users API endpoint. Due to insufficient…

Grafana is an open-source platform for monitoring and observability. In Grafana Enterprise, the Request security feature allows list allows to…

OpenClarity is an open source platform built to enhance security and observability of cloud native applications and infrastructure

Enforce security and compliance on Kubernetes clusters via admission controls, resource mutation, background scans, and container image signature…

An offensive/defense security toolset for discovery, recon and ethical assessment of AI Agents

Reproducer for CVE-2026-40022: Apache Camel camel-platform-http-main authentication bypass on non-root context paths

Proof-of-concept for CVE-2024-46635: an improper input validation vulnerability in GongZhiDao System's API endpoint that exposes sensitive user…

CVE-2025-54554 – Unauthenticated Access in tiaudit REST API leading to Sensitive Information Disclosure

Jakarta EE and MicroProfile application server runtime for development and containerized deployments, supporting cloud-native middleware with…