
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
160 results
jdwp-shellifier preview

jdwp-shellifier

GitHubioactive/jdwp-shellifier

Exploitation script for exposed Java Debug Wire Protocol (JDWP) services, enabling pentesters to inject Java code and execute arbitrary OS commands…

debuggersexploitationmisconfiguration+1
917
9 years ago
CVE-2020-14965 preview

CVE-2020-14965

GitHubg-rubert/cve-2020-14965

TP-LINK Multiple HTML Injection Vulnerabilities
embedded-systems-securityhardware-securityiot-security+3
6 years ago
CVE-2025-12135 preview

CVE-2025-12135

GitHubd0n601/cve-2025-12135

WPBookit <= 1.0.6 - Unauthenticated Stored Cross-Site Scripting
authenticationcode-analysismisconfiguration+3
11 months ago
CVE-2025-34159 preview

CVE-2025-34159

GitHubeyodav/cve-2025-34159

A critical Remote Code Execution (RCE) vulnerability exists in Coolify's application deployment workflow. This flaw allows a low-privileged member to…
cloud-securitycontainer-securityexploitation+5
1 year ago
Ghost-CMS-Code-Injection-Audit-CVE-2026-26980 preview

Ghost-CMS-Code-Injection-Audit-CVE-2026-26980

GitHubkulik-labs-development/ghost-cms-code-injection-audit-cve-2026-26980

Outdated Ghost CMS websites that have fallen become compromised from CVE-2026-26980 can suffer from spam code injection to pages. Use this to mass…
code-analysisdefensive-toolsincident-response+3
1 month ago
kube-knark preview

kube-knark

GitHubchen-keinan/kube-knark

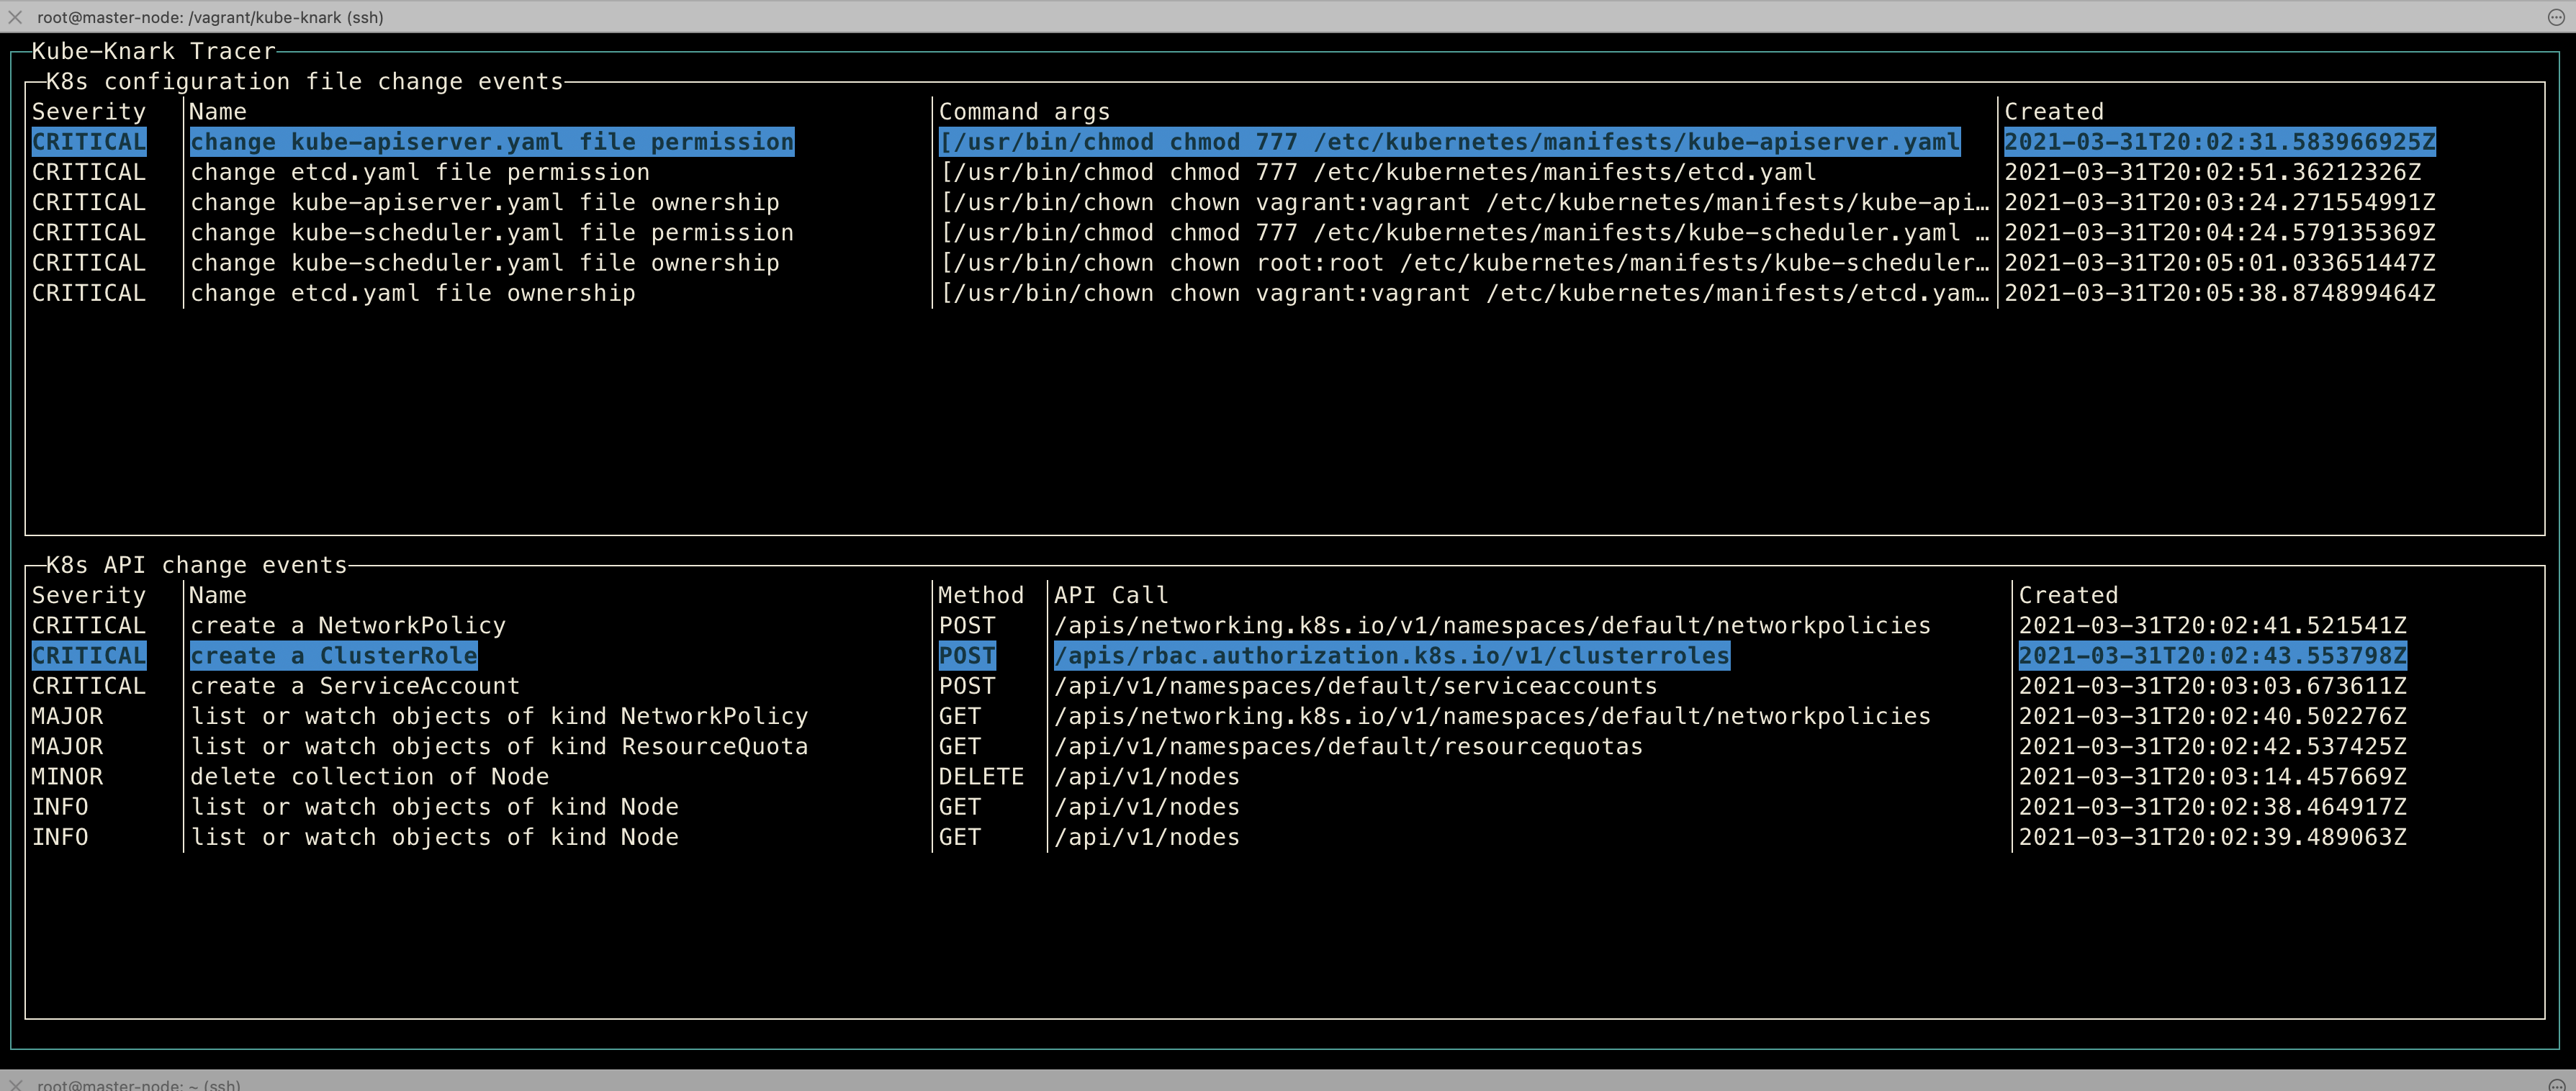
Open Source runtime tool which help to detect malware code execution and run time mis-configuration change on a kubernetes cluster
cloud-securitycontainer-securityintrusion-detection+1
364 years ago
truegaze preview

truegaze

GitHubnightwatchcybersecurity/truegaze

Static analysis tool for Android/iOS apps focusing on security issues outside the source code
android-securityios-securitymisconfiguration+3
1335 years ago
CVE-2023-36165 preview

CVE-2023-36165

GitHubtrailer2/cve-2023-36165

An issue in MiniTool Partition Wizard ShadowMaker v.12.7 allows an attacker to execute arbitrary code and gain privileges via the…
exploitationmisconfigurationprivilege-escalation+1
3 years ago
deepsec preview

deepsec

GitHubvercel-labs/deepsec

Agent-powered vulnerability scanner for large-scale codebases. Uses LLMs to find hard-to-detect security issues via regex matchers and AI…
ai-securitycode-analysisdevsecops+5
8.1k5 days ago
AWS-Key-Hunter preview

AWS-Key-Hunter

GitHubiamlucif3r/aws-key-hunter

[Just for fun] Find exposed AWS keys (VALID KEYS ONLY) on github
cloud-securitycode-analysisinformation-gathering+2
401 year ago
blmvuln preview

blmvuln

GitHubmathiasreker/blmvuln

Major Security Vulnerability on PrestaShop Websites - CVE-2022-31101
code-analysisincident-responsemalware-analysis+3
424 years ago
struts1filter preview

struts1filter

GitHubrgielen/struts1filter

A request parameter filter solution for Struts 1 CVE-2014-0114 based on the work of Alvaro Munoz and the HP Fortify team

code-analysisdevsecopsmisconfiguration+3
129 years ago
SECURITY-3430 preview

SECURITY-3430

GitHubjenkinsci-cert/security-3430

Java agent that transforms a vulnerable class to block exploitation of CVE-2024-43044 in Jenkins controllers, with optional forced shutdown on…

code-analysisdefensive-toolsexploitation+2
22 years ago
CVE-2026-31156 preview

CVE-2026-31156

GitHubunicorn-hyh/cve-2026-31156

There is a path injection vulnerability in OpenPLC-v3, which arises from the program not performing any validity checks on the file path parameters…
code-analysisexploitationinformation-gathering+3
4 months ago
springhound preview

springhound

GitHubmebibite/springhound

Created after the disclosure of CVE-2022-22965 and CVE-2022-22963. Bash script that detects Spring Framework occurrences in your projects and…

code-analysismisconfigurationstatic-analysis+2
4 years ago
CVE-2024-55963 preview

CVE-2024-55963

GitHubsuperswan/cve-2024-55963

CVE-2024-55963, allows unauthenticated remote code execution on Appsmith Enterprise platform due to a misconfigured PostgreSQL database included by…
database-securityexploitationmisconfiguration+5
21 year ago
Fix-CVE-2023-36884 preview

Fix-CVE-2023-36884

GitHubridsoliveira/fix-cve-2023-36884

PowerShell script to apply Microsoft's recommended registry-based workaround for CVE-2023-36884, mitigating remote code execution risk on Windows…
configuration-auditingdefensive-toolsincident-response+2
23 years ago
CVE-2021-25253 preview

CVE-2021-25253

GitHubmsd0pe-1/cve-2021-25253

Local privilege escalation exploit for Trend Micro OfficeScan Client <=10.0 via misconfigured ACLs on the installation folder, enabling system-level…

exploitationmisconfigurationpayload-generation+2
13 years ago
Previous12…9Next