Penetration-Testing-Assessment-23-04-2026

Penetration testing assessment of a vulnerable IIS 6.0 WebDAV server, demonstrating reconnaissance, enumeration, exploitation (CVE-2017-7269), and…

Penetration testing assessment of a vulnerable IIS 6.0 WebDAV server, demonstrating reconnaissance, enumeration, exploitation (CVE-2017-7269), and…

Hands-on lab reproducing CVE-2019-11043 PHP-FPM RCE behind nginx, demonstrating reverse-tunnel persistence, memory forensics, and network traffic…

Demonstrates CVE-2025-22235 Spring Boot authentication bypass via EndpointRequest.to() misconfiguration. Includes environment setup, reproduction…

This repository contains **research and analysis** related to CVE-2025-29927. It demonstrates safe, controlled testing approaches for a path…

Penetration tests guide based on OWASP including test cases, resources and examples.

A tool designed to exploit a privilege escalation vulnerability in the sudo program on Unix-like systems. It takes advantage of a specific…

Local Linux enumeration script that identifies privilege escalation vectors including misconfigurations, world-writable files, clear-text passwords,…

OWASP ServerlessGoat: a serverless application demonstrating common serverless security flaws

Detailed writeup and step-by-step proof-of-concept for CVE-2020-11107, a Windows XAMPP privilege escalation vulnerability allowing arbitrary command…

DonkAI is a hands-on lab for the OWASP Top 10 for LLM Applications (2025) - no real LLM required.

Public PoC and detector for CVE-2026-20896 ("Gitea Docker: One Header, Any User")

Full VAPT writeup of OWASP CICD-Goat — 9 CTFd flags captured, 4 critical + 5 high findings (incl. CVE-2024-23897) mapped to the OWASP Top 10 CI/CD…

Docker-based lab demonstrating Nginx CVE-2013-4547 URI parsing vulnerability with step-by-step exploitation for privilege bypass and code execution.

TikiWiki 21.2 allows to edit templates without the use of a CSRF protection.

Proof-of-concept exploit for CVE-2021-24006, demonstrating improper access control bypass in FortiManager SD-WAN Orchestrator (versions 6.4.0-6.4.3).…


Prestashop fix vulnerability CVE-2023-39526 & CVE-2023-39527

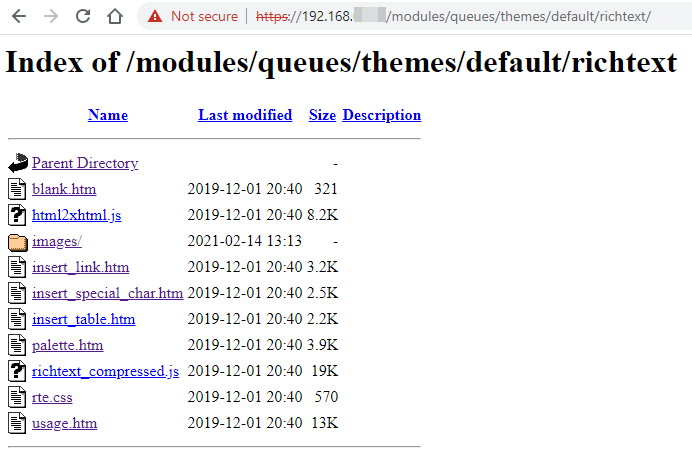
Issabel-pbx version 4.0.0-6 contains a Broken Access Control vulnerability that manifests as unauthenticated Directory Listing on the web interface.