

CVE-2020-23590
 huzaifahussain98/cve-2020-23590
CSRF leads to change the password for "WLAN SSID"
embedded-systems-securityexploitationiot-security+3
huzaifahussain98/cve-2020-23590CSRF leads to change the password for "WLAN SSID"
 leonardobg/cve-2023-36144
Proof-of-concept exploit for CVE-2023-36144 demonstrating unauthenticated backup file download on Intelbras SG 2404 MR L2+ switch, exposing device…
 huzaifahussain98/cve-2020-23586
CSRF allows to Add Network Traffic Control Type Rule
 remenis/cve-2025-67160
Vatilon-based IP cameras expose internal web directories without authentication, leading to information disclosure.
 jet-pentest/cve-2020-25747
Proof-of-concept exploit for CVE-2020-25747 demonstrating unauthenticated remote access to RTSP and ONVIF services on Rubetek RV-3406/3409/3411…
 wolfssl/wolfcose
A fast, portable, and lightweight COSE + CBOR implementation for embedded systems. Supports PQC, FIPS 140-3, DO-178, and MISRA C. Powered by wolfSSL.
 win3zz/cve-2023-43261
CVE-2023-43261 - Credential Leakage Through Unprotected System Logs and Weak Password Encryption
 hadimed/dsl-2750u-full-chain
CVE-2021-3707 , CVE-2021-3708
 aimoda/hitron-cfg-decrypter
CVE-2014-10069
 michaeladamgroberman/cve-2026-54477
CVE-2026-54477: Admin Panel Missing Security Headers (clickjacking/XSS) - Gardyn (ICSA-26-183-03)
 athos-zago/cve-2024-30973
POC VIDEO - https://youtu.be/hNzmkJj-ImM?si=NF0yoSL578rNy7wN
 redfox-security/digisol-dg-gr1321-s-improper-access-control-cve-2024-4231
Exploit for CVE-2024-4231, an improper access control vulnerability in Digisol DG-GR1321 routers, allowing unauthorized access to sensitive…
 redfox-security/digisol-dg--gr1321-s-password-storage-in-plaintext--cve-2024-4232
Proof-of-concept exploit for CVE-2024-4232 targeting plaintext password storage in Digisol DG-GR1321 routers. Demonstrates extraction of credentials…
 g-rubert/cve-2020-14965
TP-LINK Multiple HTML Injection Vulnerabilities
 redfox-security/digisol-dg-gr1321-s-password-storage-in-plaintext-cve-2024-4232
Proof-of-concept demonstrating plaintext password storage vulnerability in Digisol DG-GR1321 routers, enabling credential exposure and unauthorized…
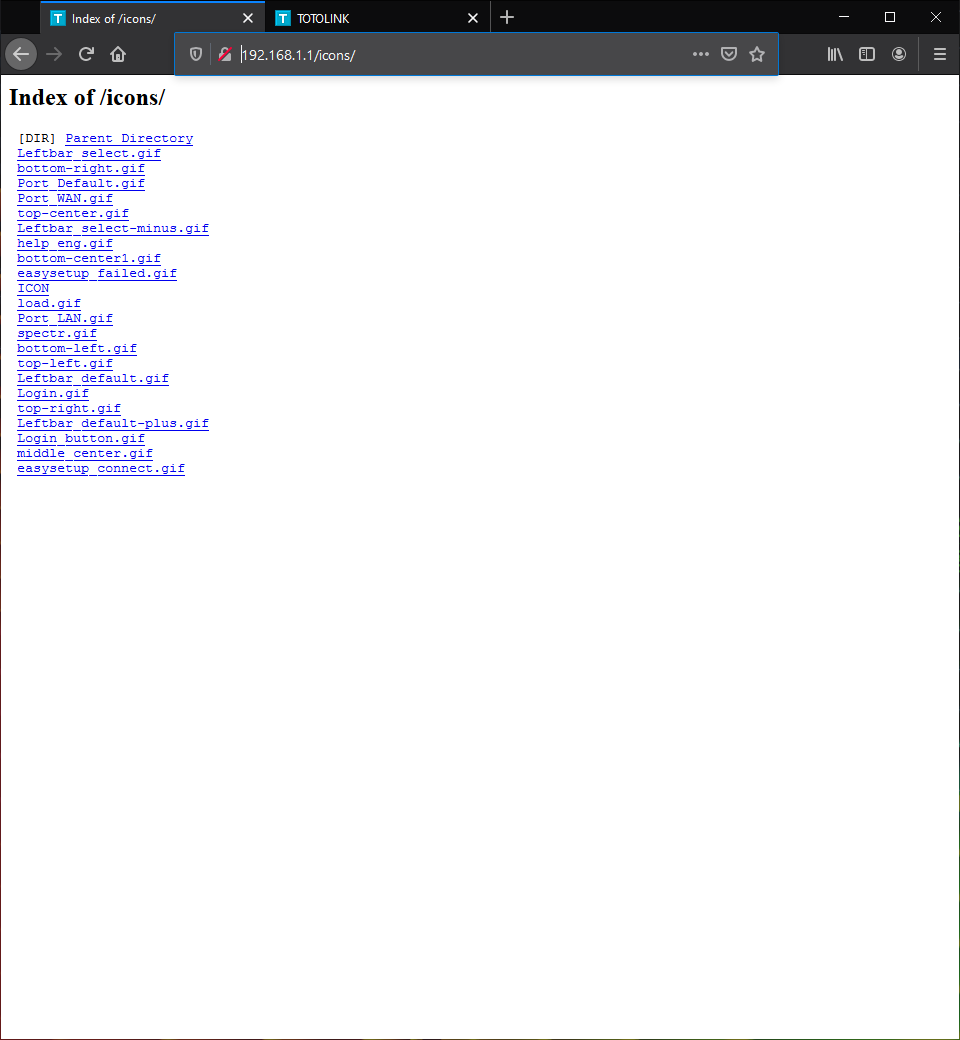 swzhouu/cve-2020-27368
TOTOLINK-A702R-V1.0.0-B20161227.1023 Directory Indexing Vulnerability