
CVE-2026-37072
 jfs-jfs/cve-2026-37072
Veno File Manager Project Veno File Manager Project 4.4.9 is vulnerable to Incorrect Access Control in admin-head-updates.php
authentication-authorizationexploitationmisconfiguration+3
jfs-jfs/cve-2026-37072Veno File Manager Project Veno File Manager Project 4.4.9 is vulnerable to Incorrect Access Control in admin-head-updates.php
 infosec4fun/cve-2020-10130
CVE-2020-10130 - SearchBlox Product before V-9.1 is vulnerable to Business logic bypass
 d34dun1c02n/cve-2023-31704
Proof-of-concept exploit for CVE-2023-31704: Incorrect access control in Sourcecodester Online Computer and Laptop Store 1.0 allows remote privilege…
 b0marek/cve-2023-4800
Repository for CVE-2023-4800 vulnerability.
 redteambrasil/cve-2019-19550
Proof-of-concept exploit for authentication bypass in Senior Rubiweb 6.2.34, enabling admin access to sensitive information via crafted URLs.
 enochgitgamefied/nextjs-cve-2025-29927-docker-lab
Docker-based lab for exploring and reproducing the Next.js CVE-2025-29927 middleware authorization bypass vulnerability. Includes vulnerable app,…
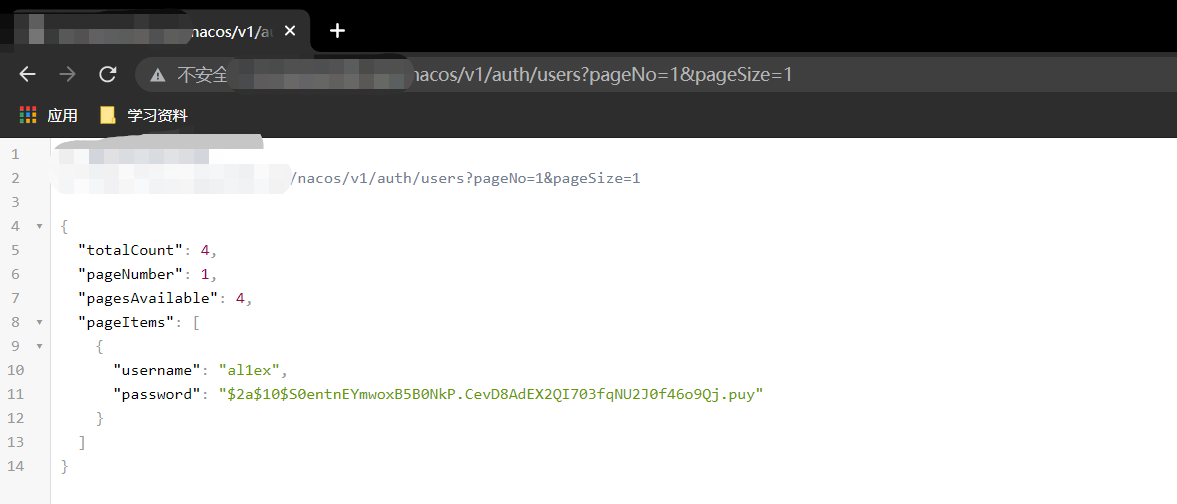 al1ex/alibab-nacos-unauthorized-reset-pwd
Alibab-Nacos-Unauthorized-Reset PWD