

teler-waf
 teler-sh/teler-waf
teler-waf is a Go HTTP middleware that protects local web services from OWASP Top 10 threats, known vulnerabilities, malicious actors, botnets,…
api-securitydefensive-toolsids-ips-evasion+5
408
teler-sh/teler-wafteler-waf is a Go HTTP middleware that protects local web services from OWASP Top 10 threats, known vulnerabilities, malicious actors, botnets,…
 bishopfox/smogcloud
Find cloud assets that no one wants exposed 🔎 ☁️
 rz1027/cve-2026-20896
Public PoC and detector for CVE-2026-20896 ("Gitea Docker: One Header, Any User")
 jp1337/easywall
Web interface for the nftables firewall on Linux, written in Go. The apply undoes itself after 120 seconds unless you confirm it — you cannot lock…
 elttam/semgrep-rules
Static analysis security rules for vulnerability detection and audit-focused code review across Java, Go, Python, C#, Kotlin, PHP, Kubernetes, and…
 momenbasel/vulnhawk
AI-powered SAST scanner that finds auth bypass, IDOR, and logic bugs Semgrep/CodeQL miss. Free GitHub Action. Supports Python, JS/TS, Go, PHP, Ruby.
 hakaioffsec/navgix
Multi-threaded Go tool to detect nginx alias traversal vulnerabilities using heuristic and brute-force techniques for identifying vulnerable…
 gagaltotal/cve-2026-42533-nginx
CVE-2026-42533 Nginx
 praetorian-inc/gokart
A static analysis tool for securing Go code
 aquasecurity/trivy
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
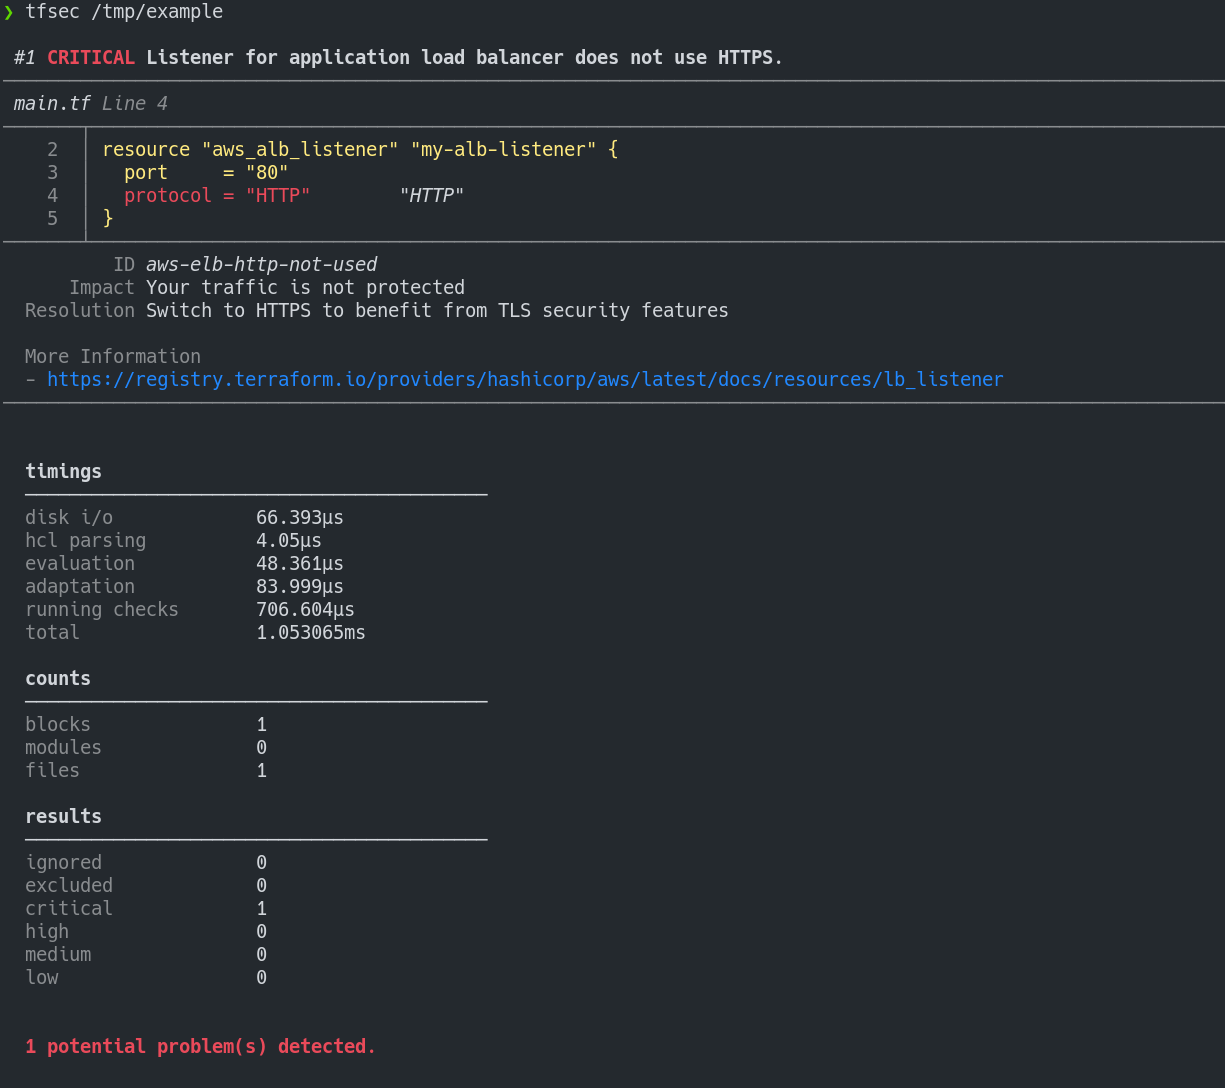
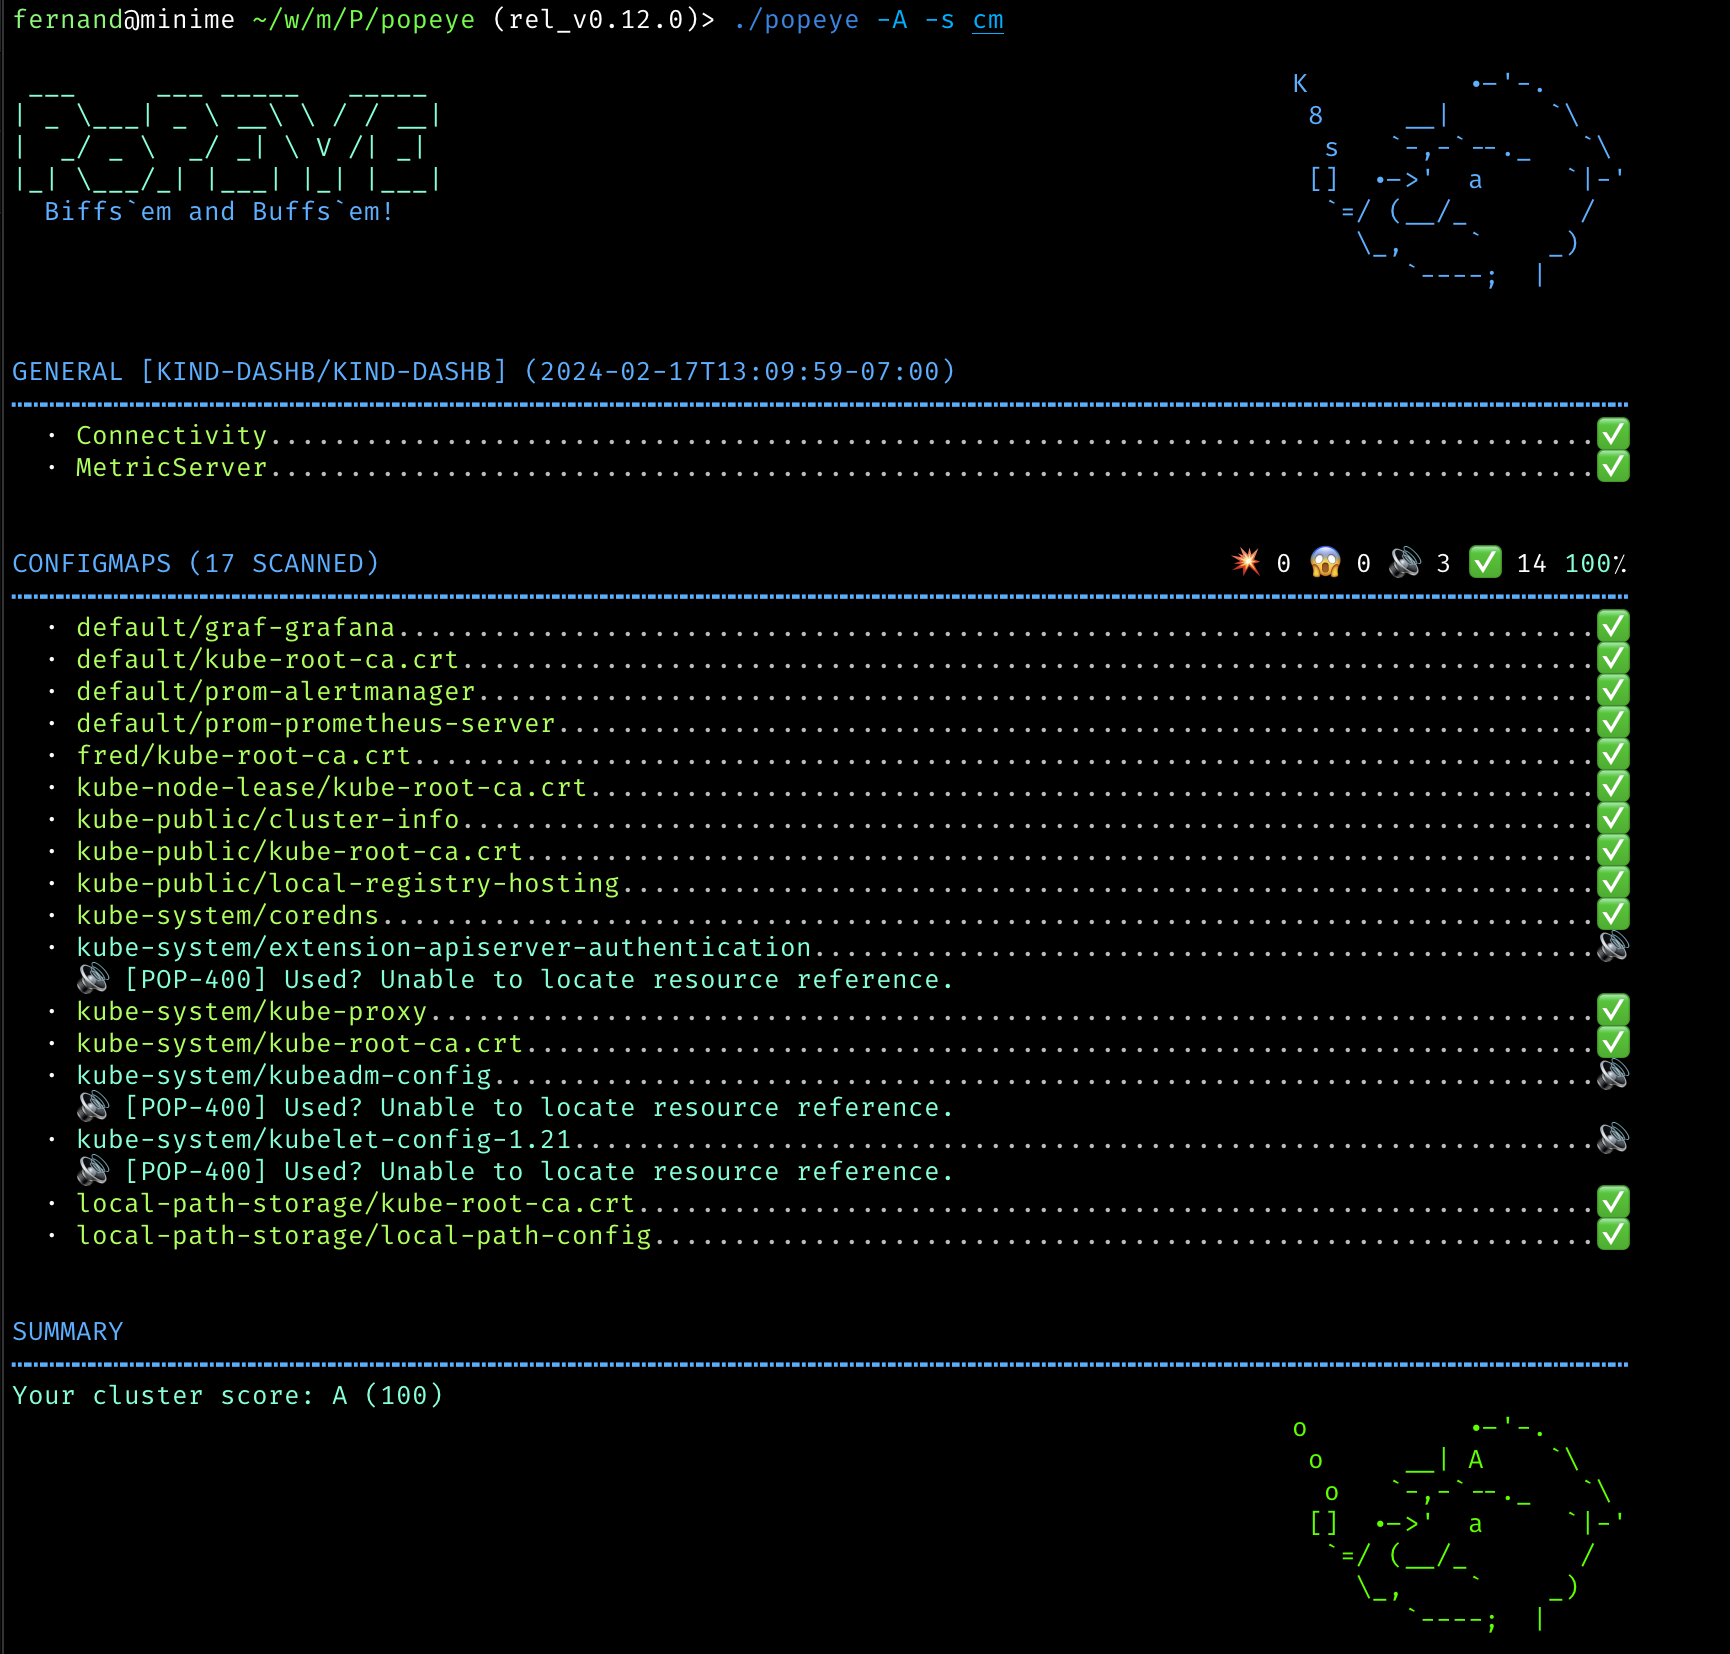 derailed/popeye
👀 A Kubernetes cluster resource sanitizer
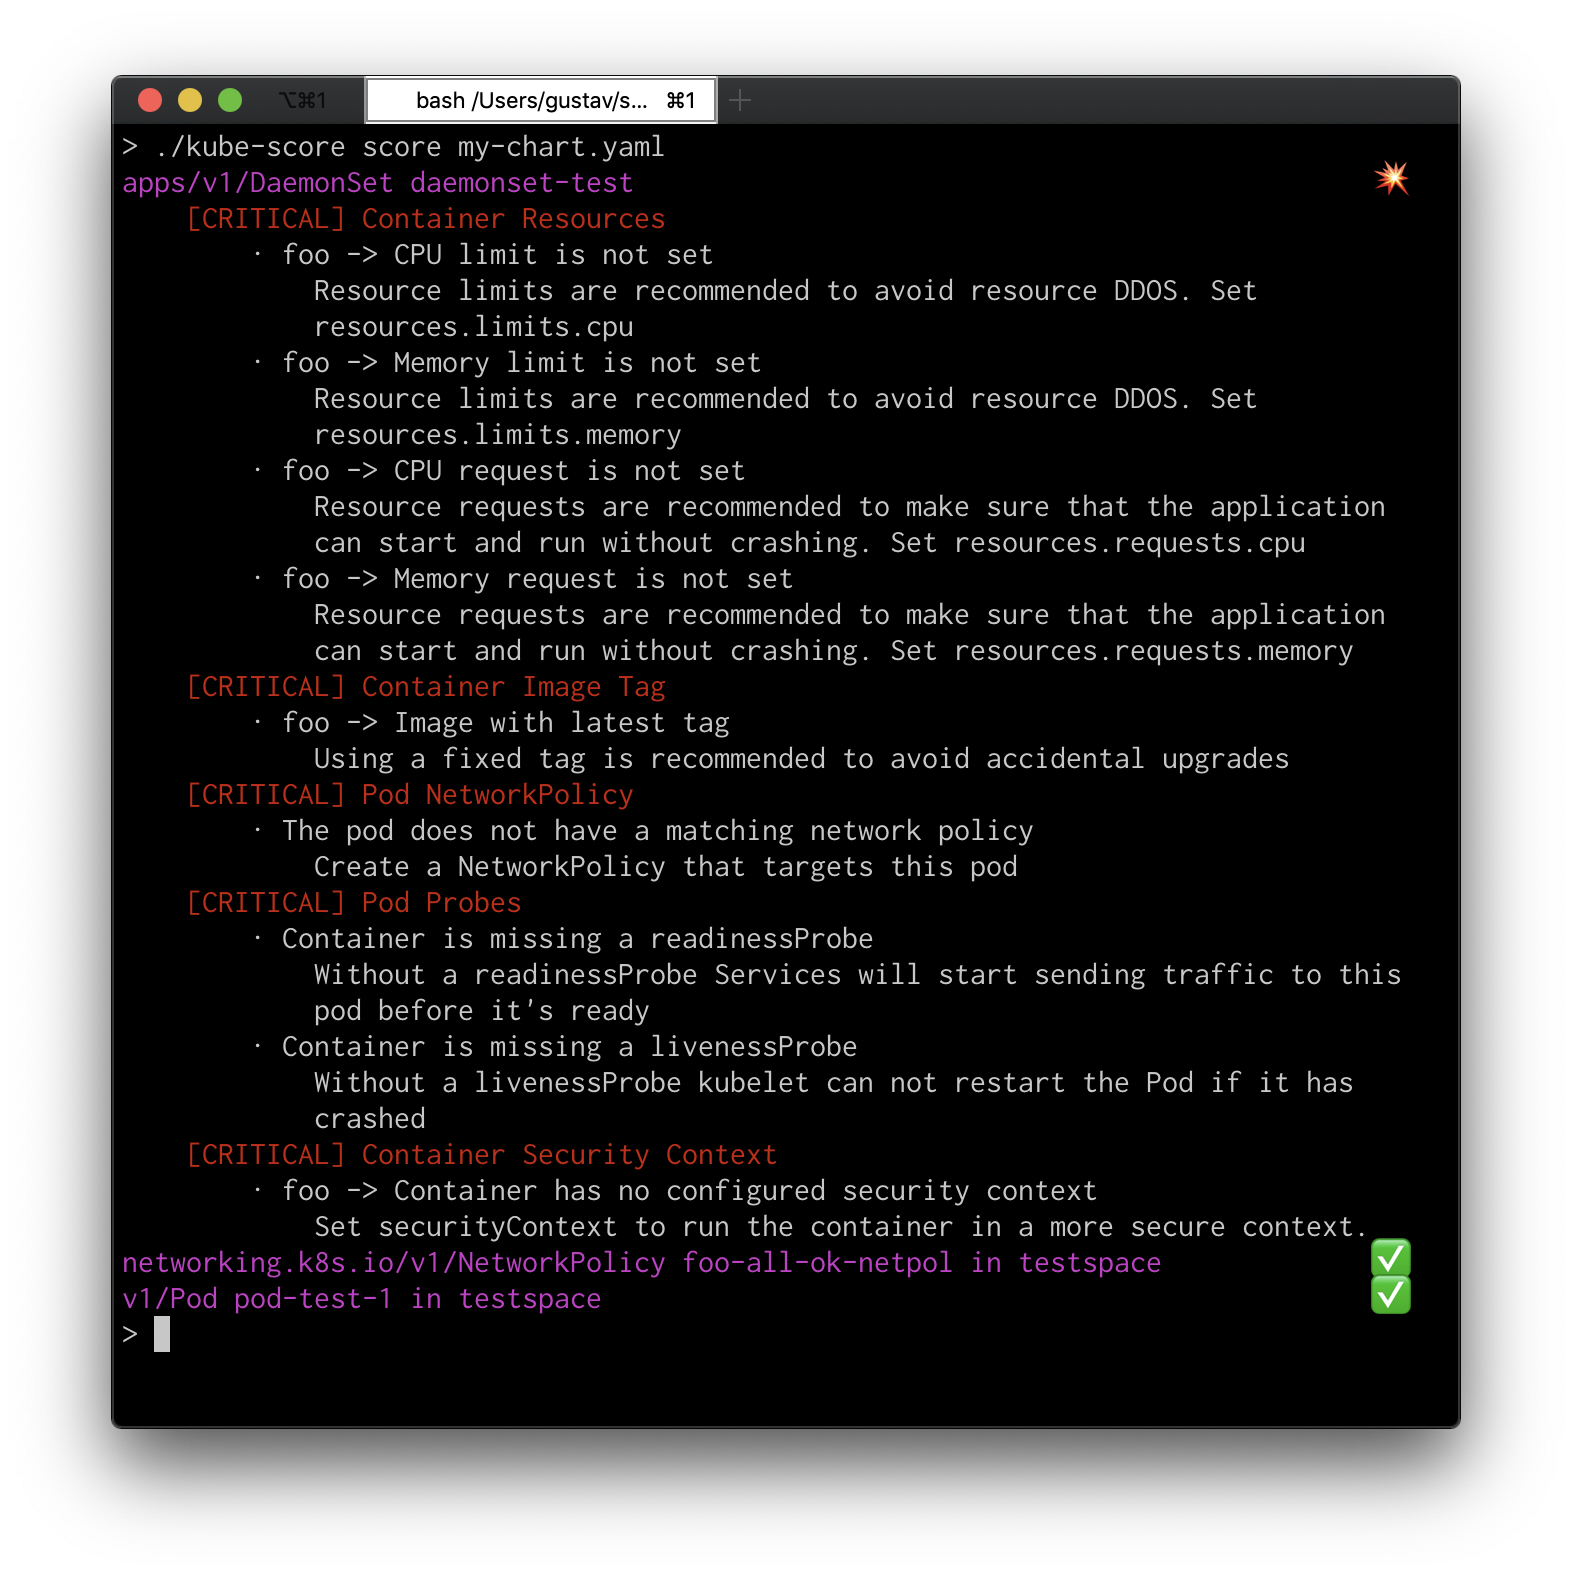 zegl/kube-score
Kubernetes object analysis with recommendations for improved reliability and security. kube-score actively prevents downtime and bugs in your…
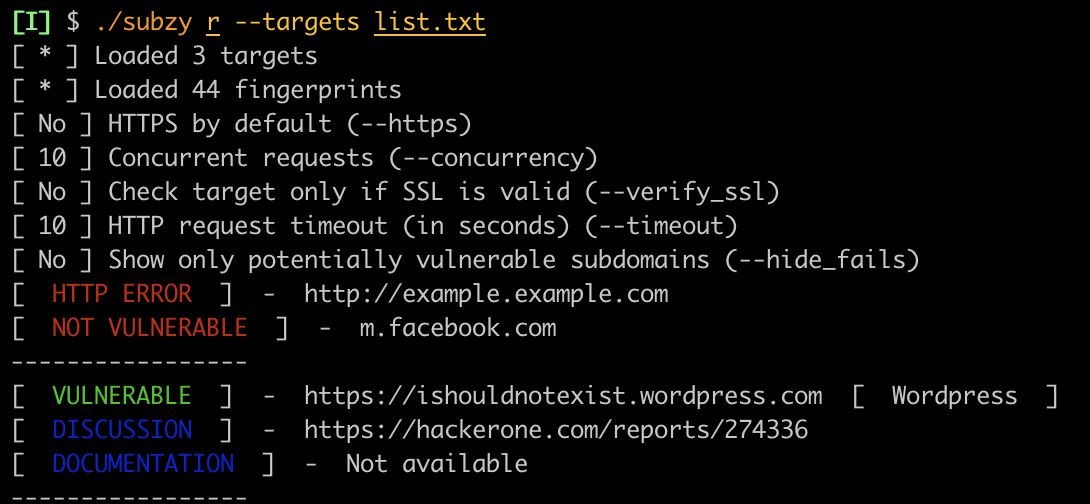 pentestpad/subzy
Subdomain takeover vulnerability checker
 praetorian-inc/nerva
Fast service fingerprinting CLI for 170+ protocols (TCP/UDP/SCTP) - built by Praetorian
 corgea/sighthound
Tree-sitter based static vulnerability scanner with pattern matching and taint-flow analysis for multi-language source code. Outputs findings as…
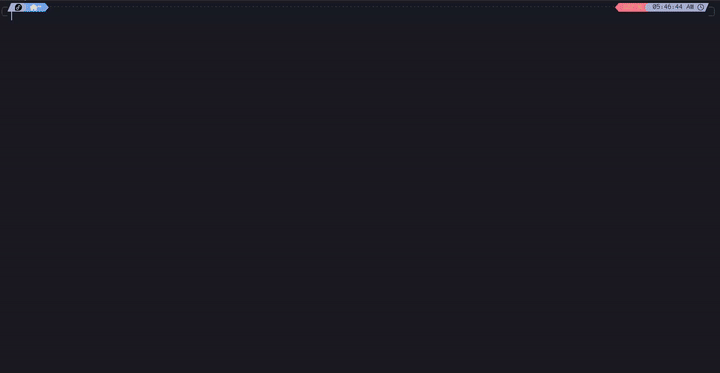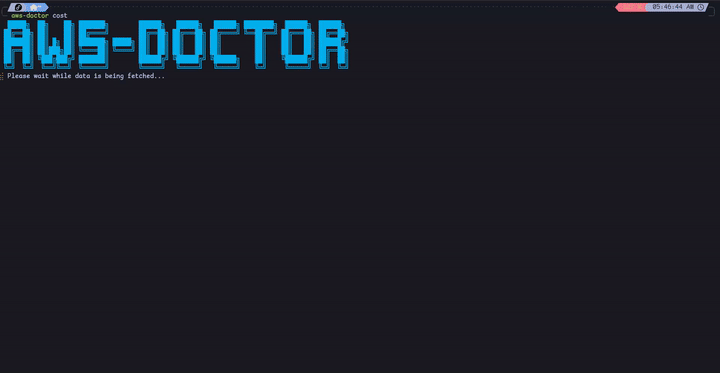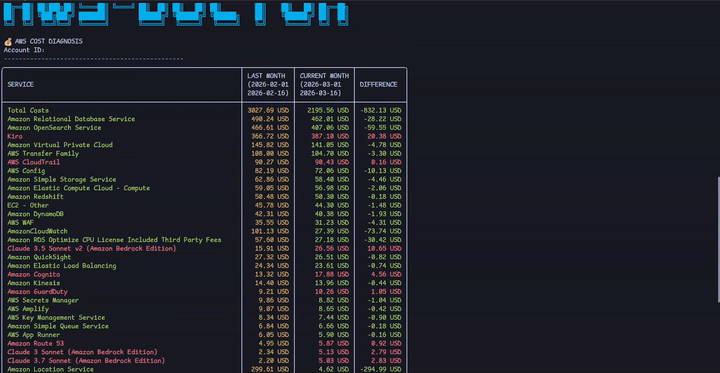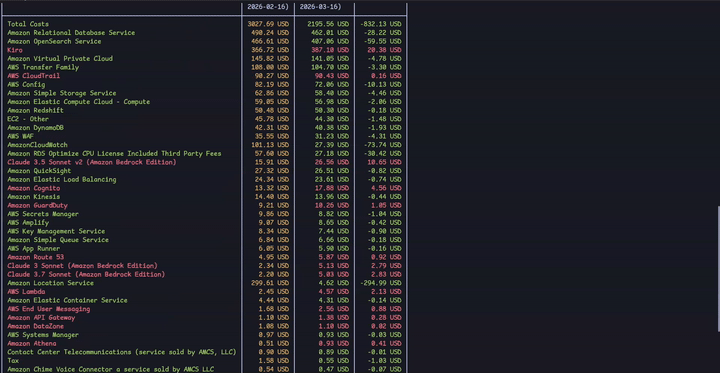 elc0mpa/aws-doctor
Powerful open-source CLI to audit security, costs, and best practices in AWS. 🩺 ☁️