
reposherlock
 kemal-arslan/reposherlock
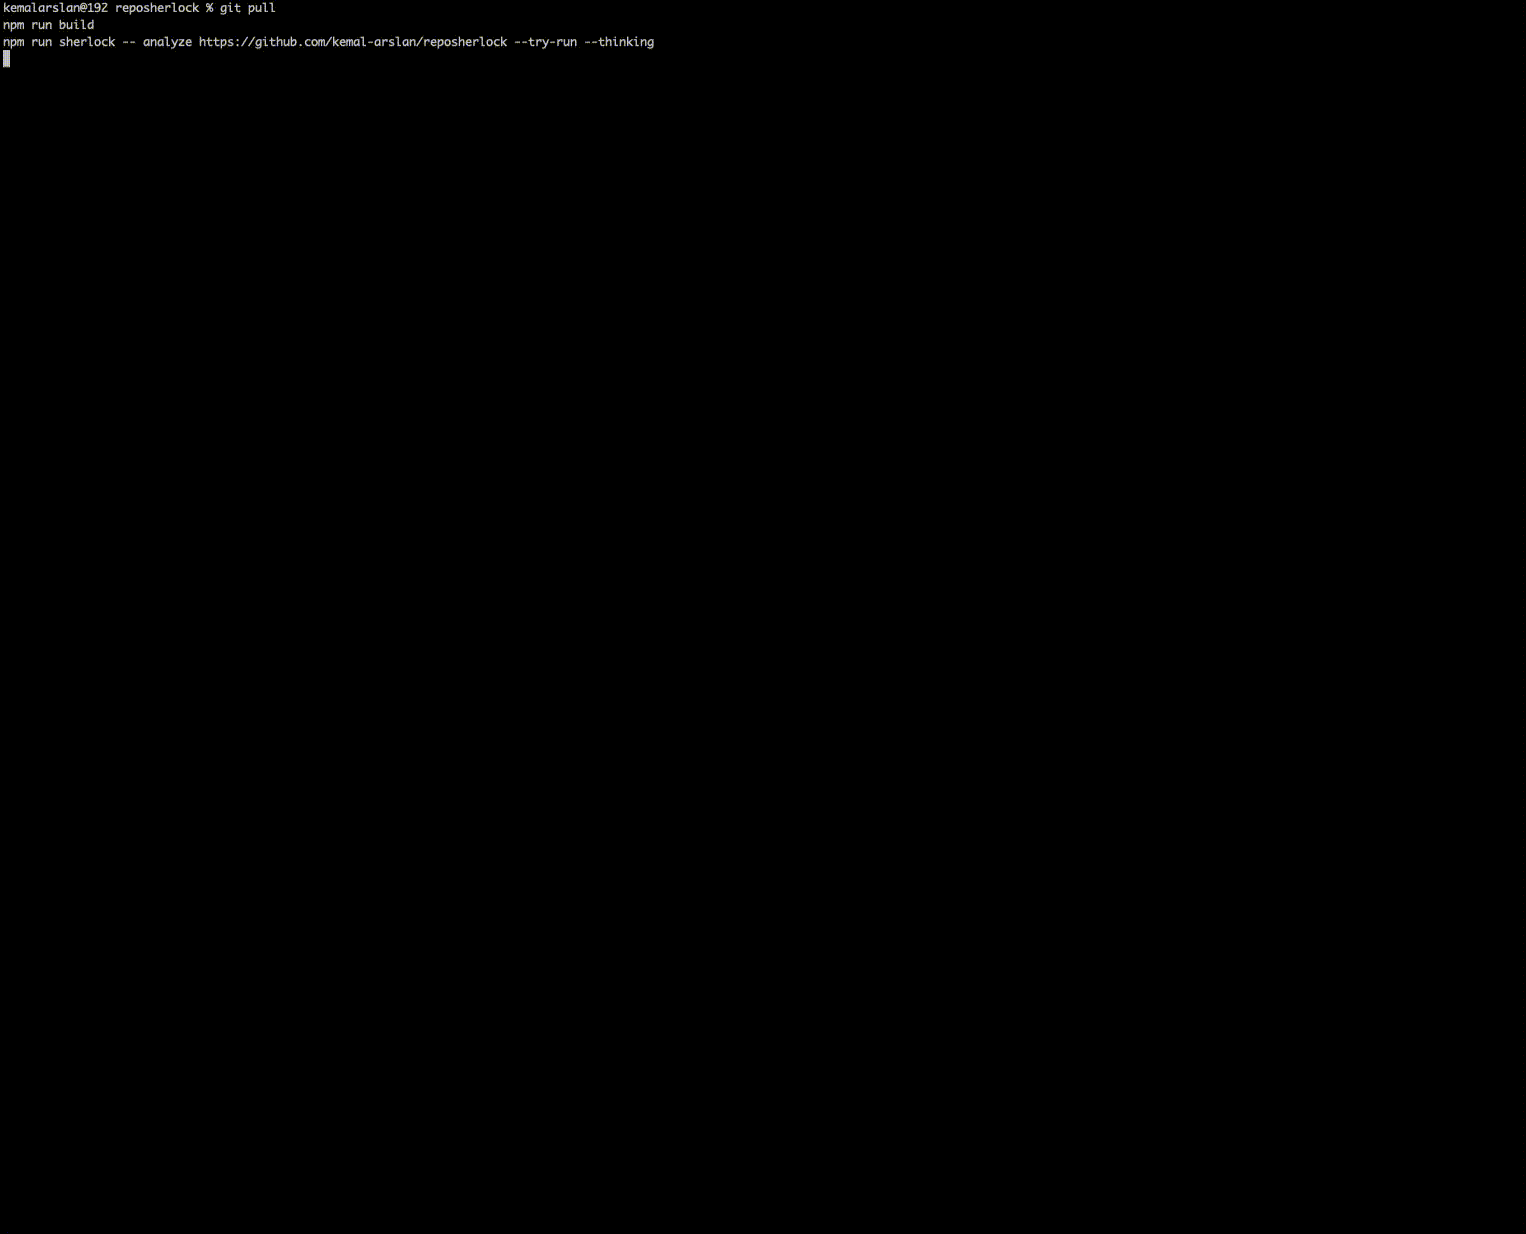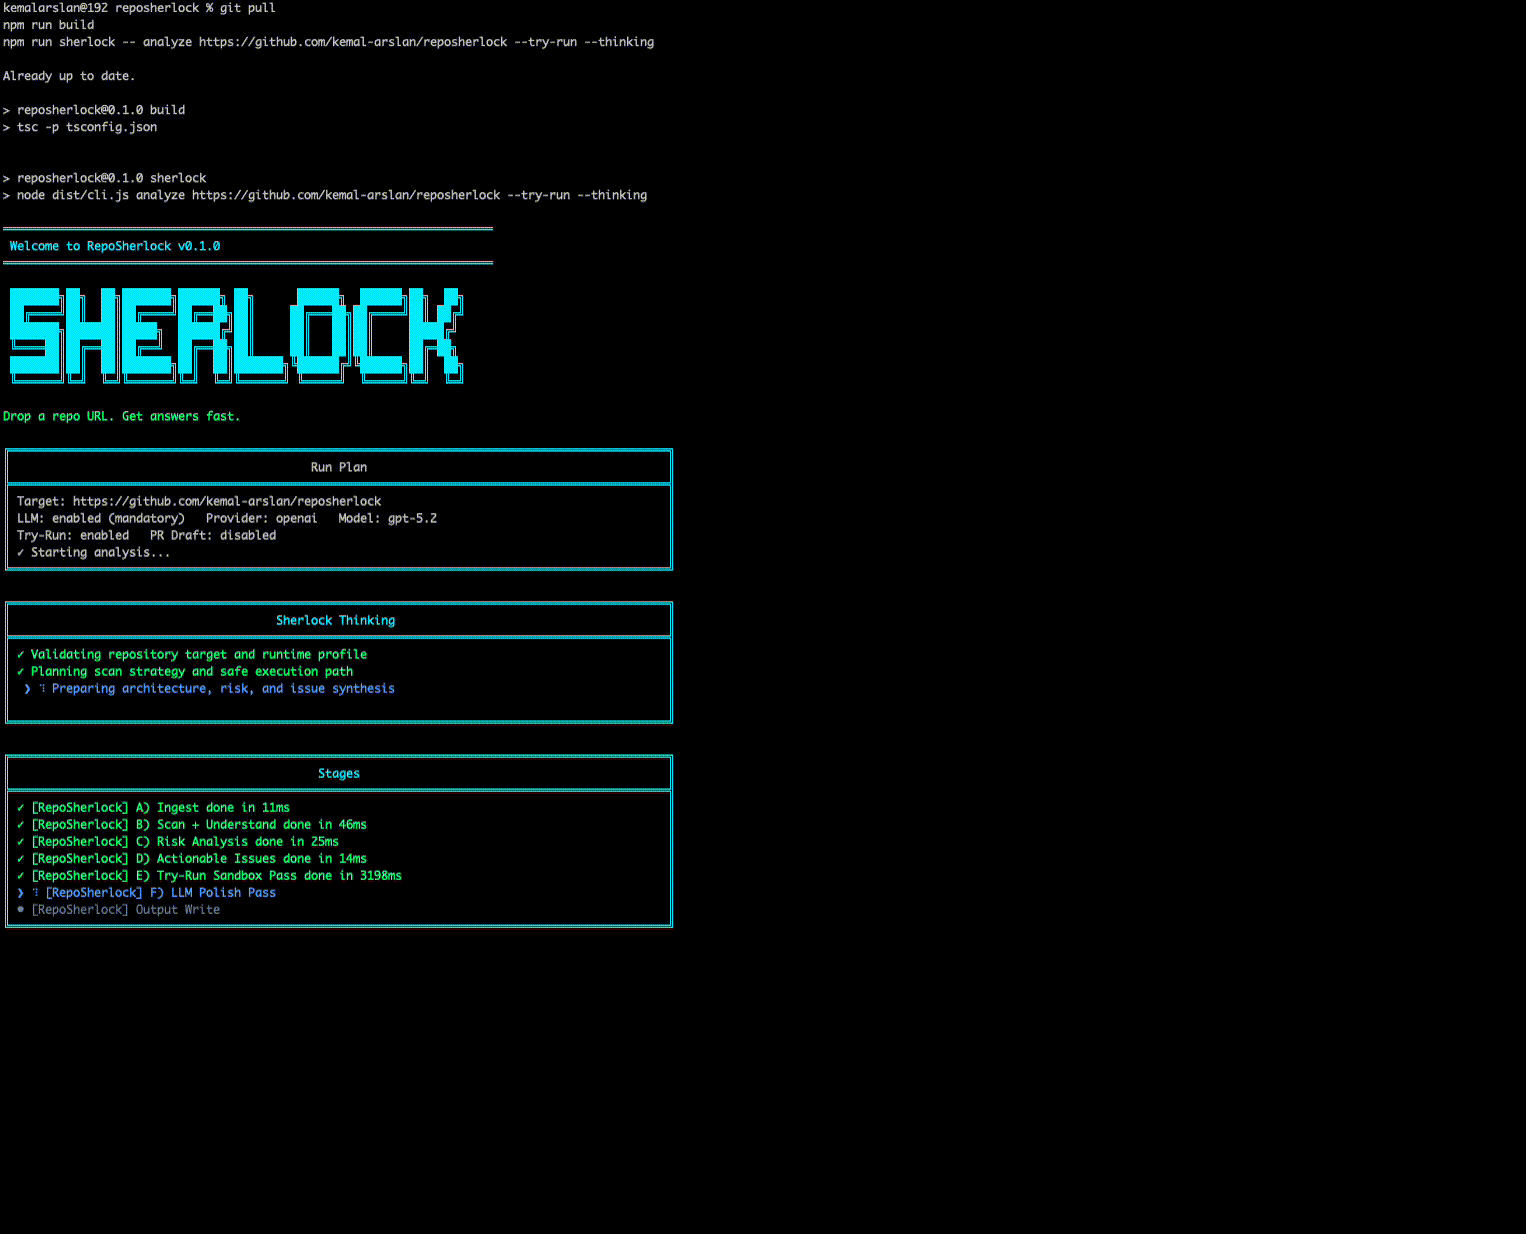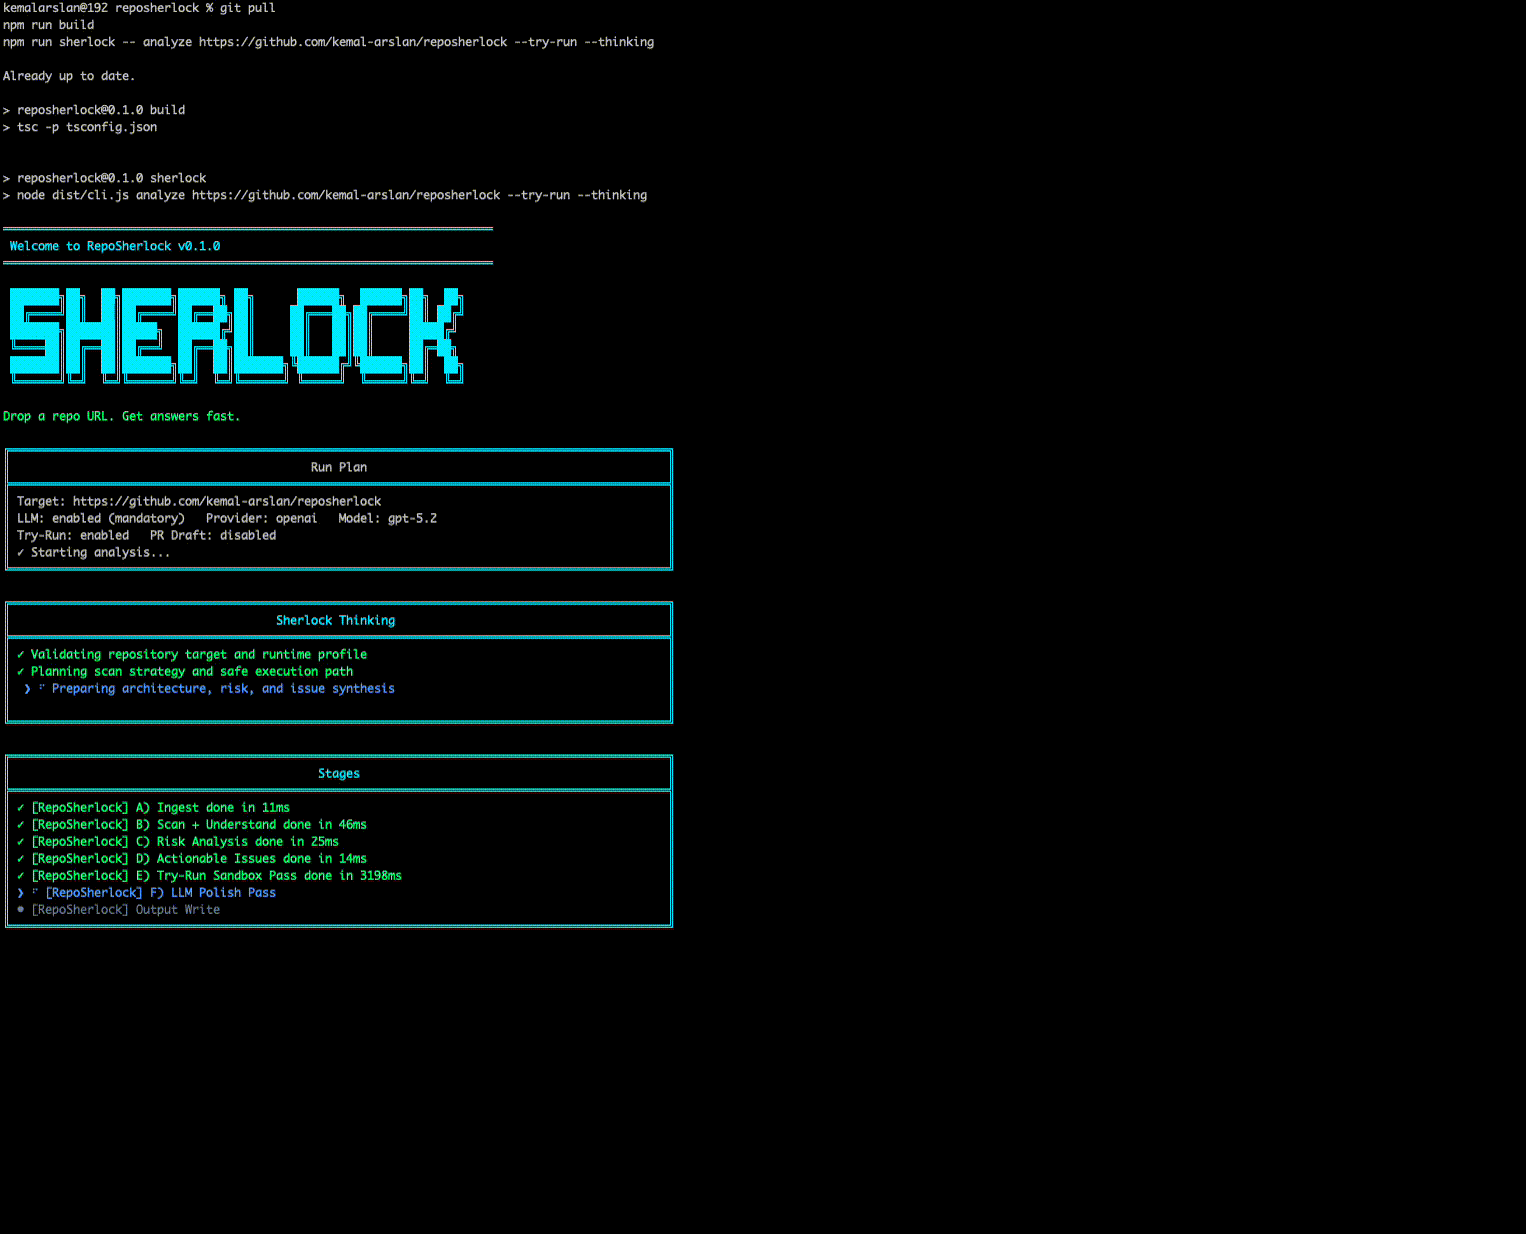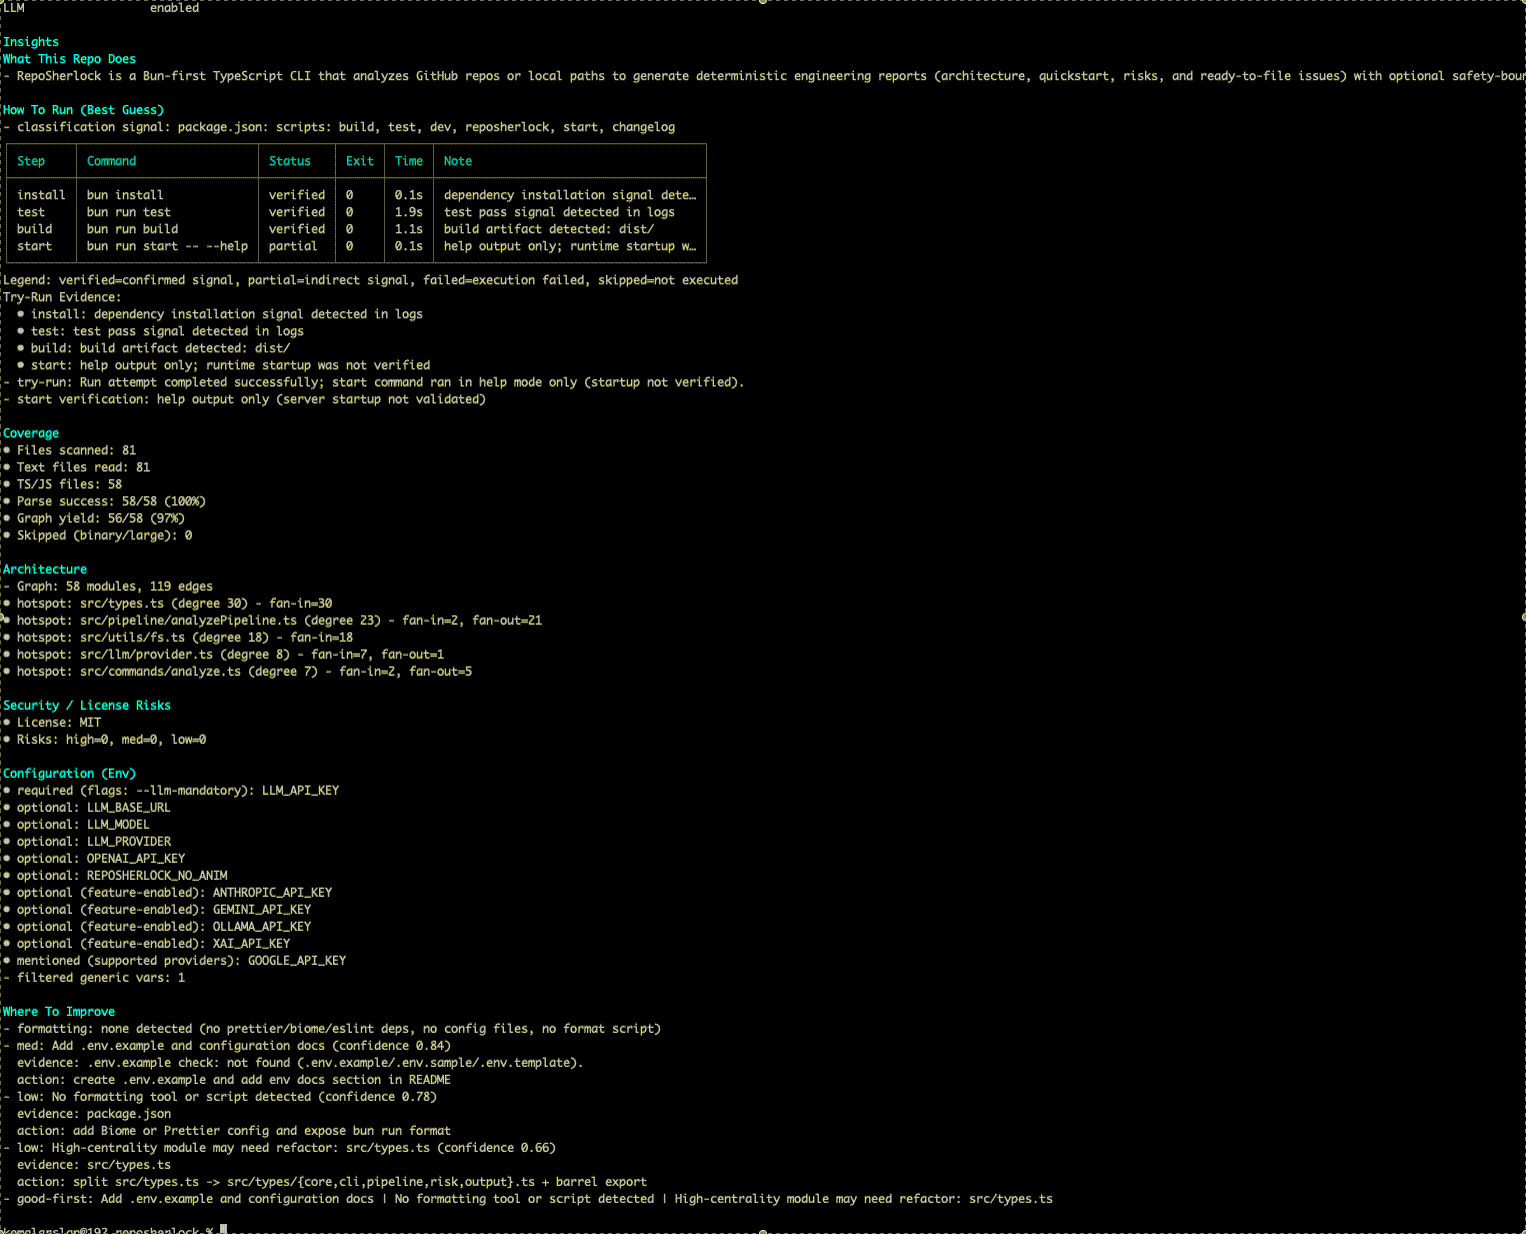
Analyze any GitHub repo (URL or local path) → architecture map, verified run commands, risks, and actionable issues - in minutes.
code-analysisdevsecopsmisconfiguration+4
2
kemal-arslan/reposherlockAnalyze any GitHub repo (URL or local path) → architecture map, verified run commands, risks, and actionable issues - in minutes.
 creeperhost/log4jpatcher
A mitigation for CVE-2021-44228 (log4shell) that works by patching the vulnerability at runtime. (Works with any vulnerable java software, tested…
 gagaltotal/cve-2026-42533-nginx
CVE-2026-42533 Nginx
 nizar0x1f/cve-2021-26084-patch-
CVE-2021-26084 patch as provided in "Confluence Security Advisory - 2021-08-25"
 bitthebyte/eagle
Multithreaded Plugin based vulnerability scanner for mass detection of web-based applications vulnerabilities
 burjoy/cve-2024-40275_scanner
Scanner for CVE-2024-40725 Apache HTTP Server source-code disclosure; probes direct and subrequest paths, fingerprints affected versions, and outputs…
 sleepthegod/dns-zone-audit
This Bash script checks domains for DNS zone transfer misconfigurations (CVE-1999-0532). It queries name servers and attempts AXFR requests; if…
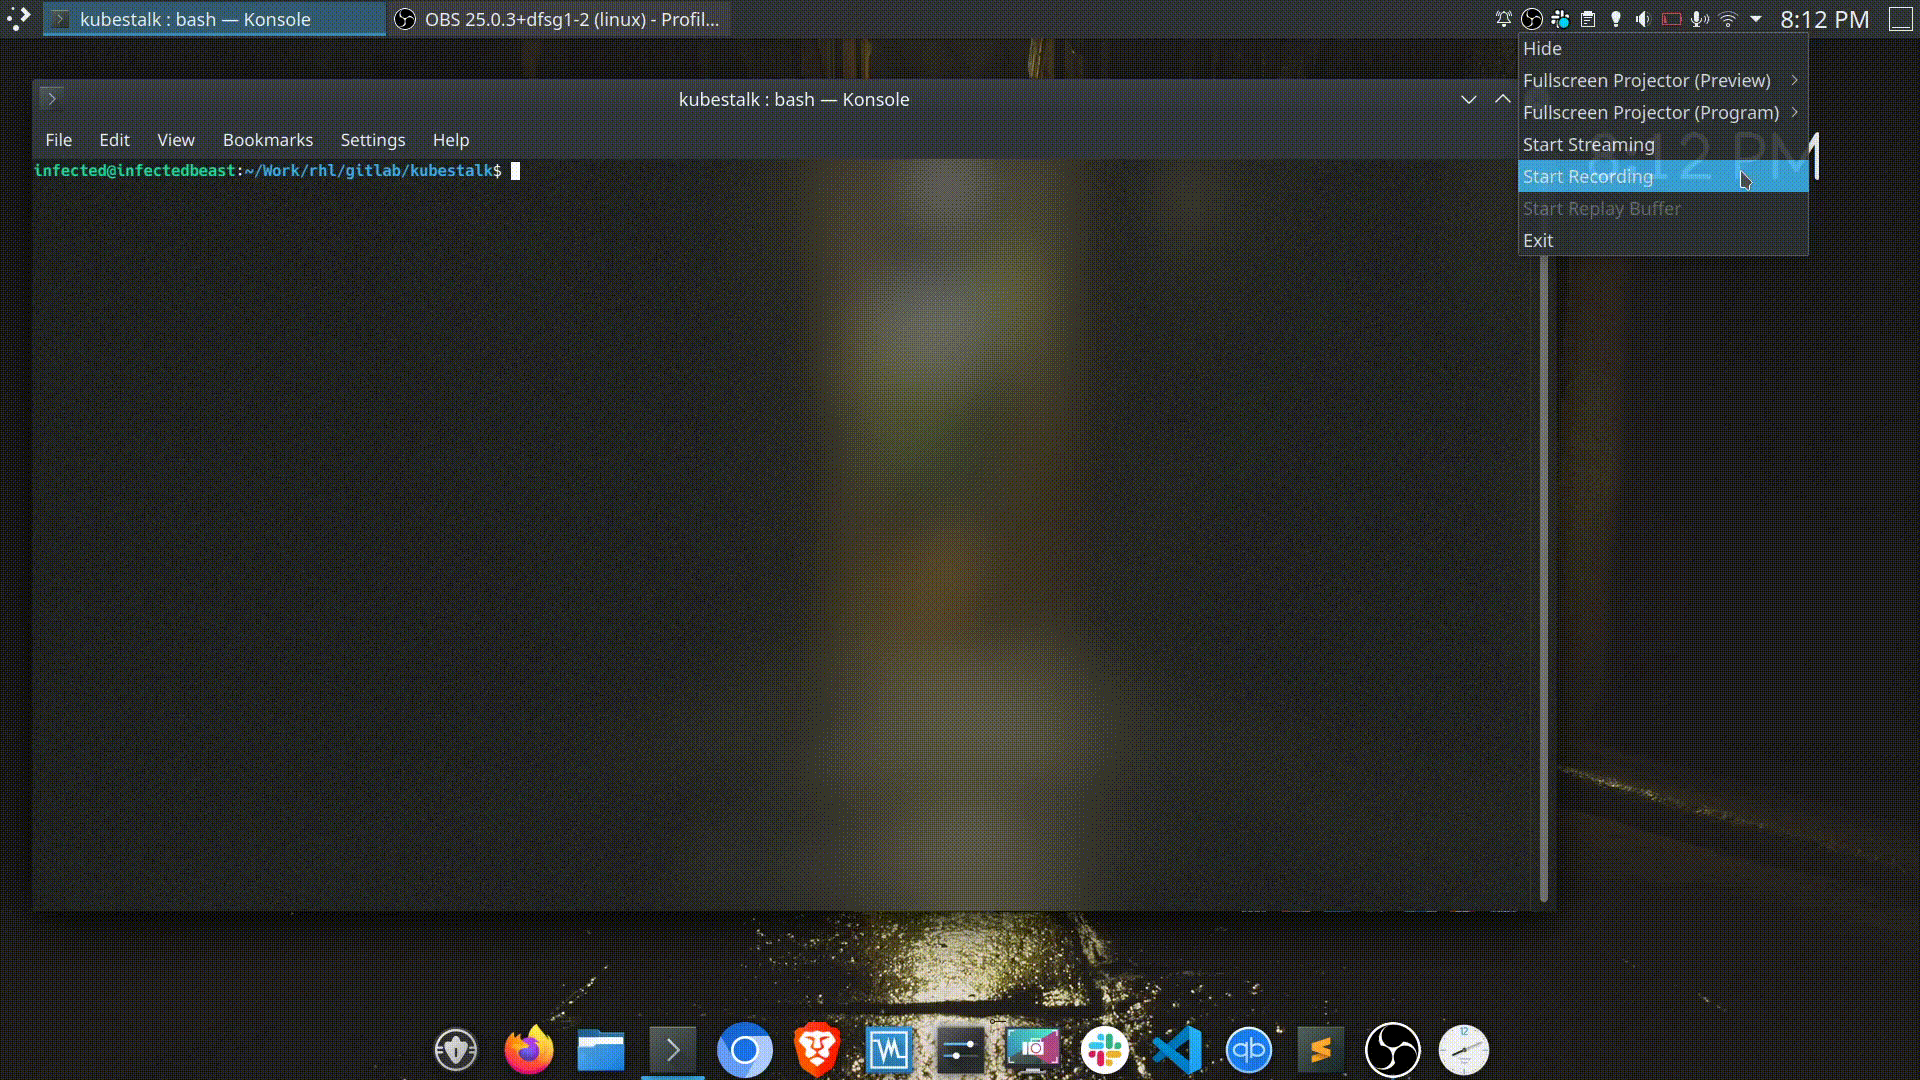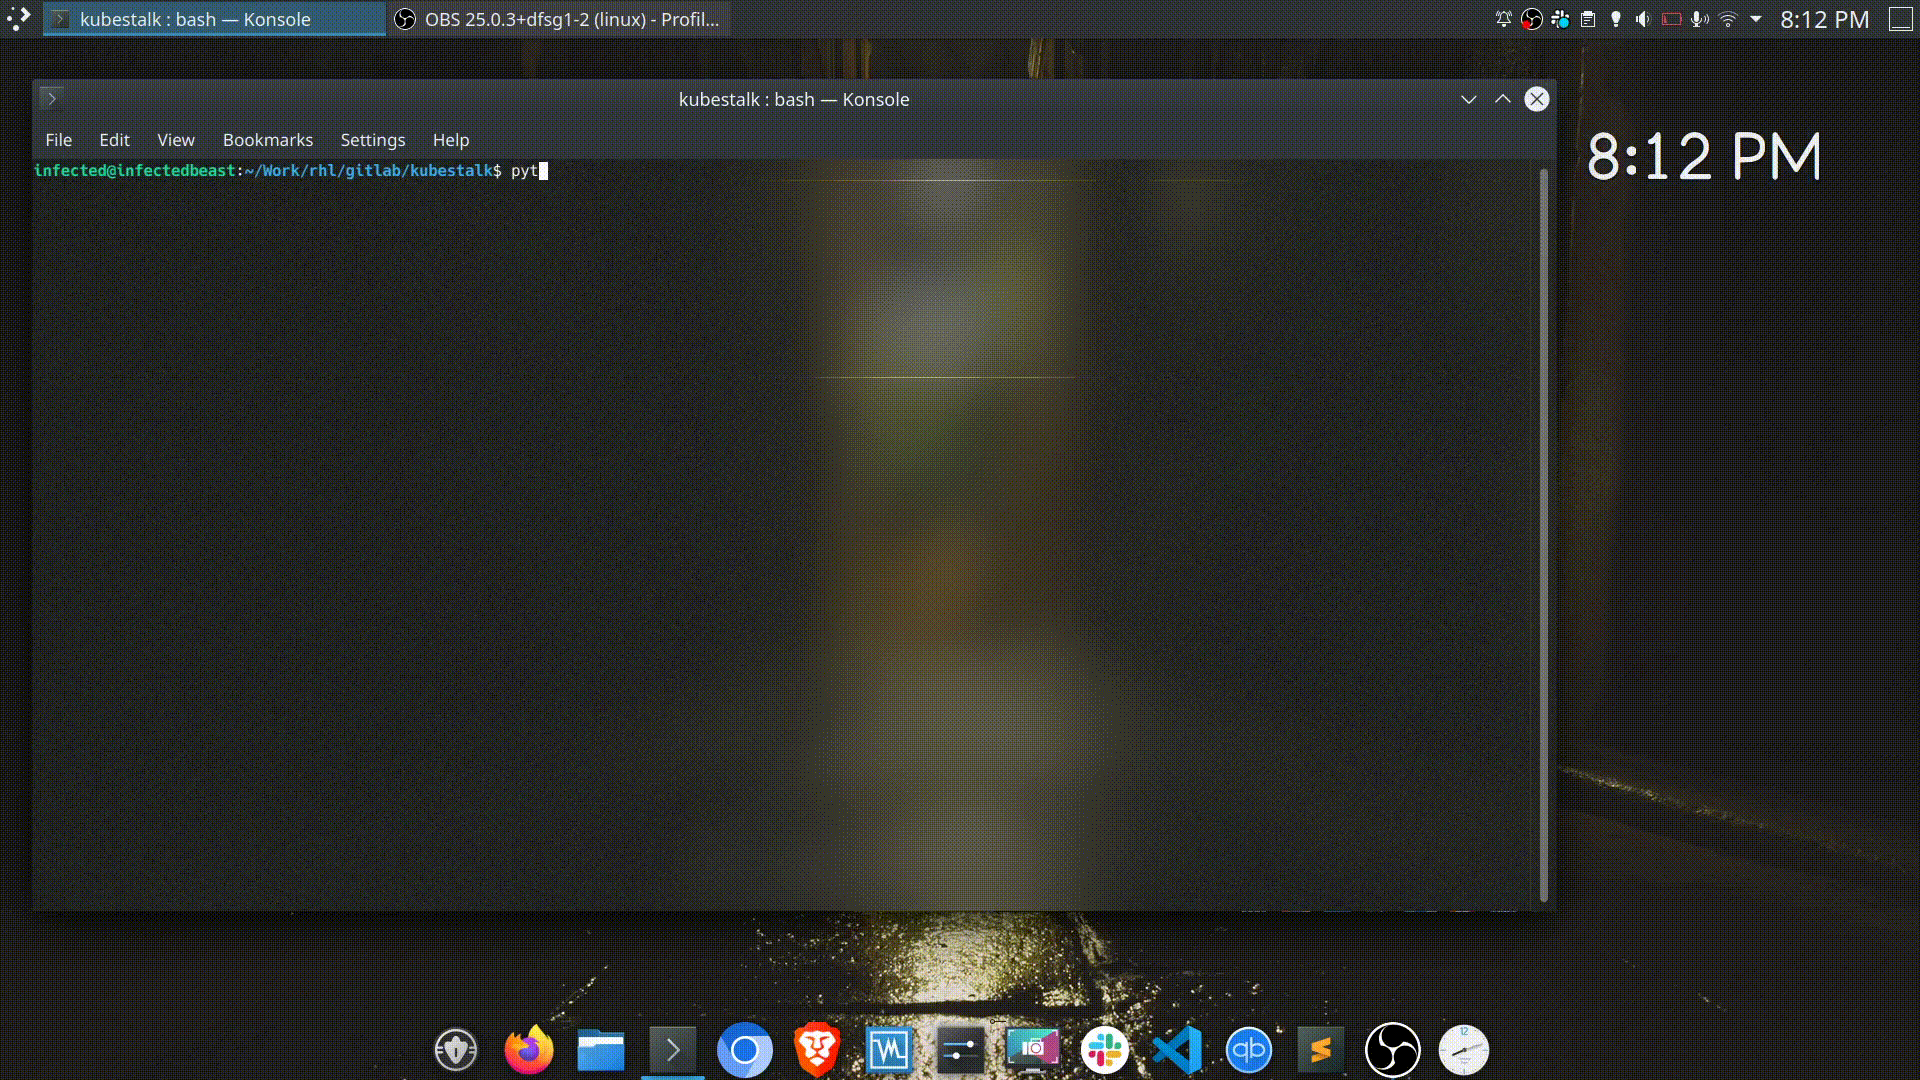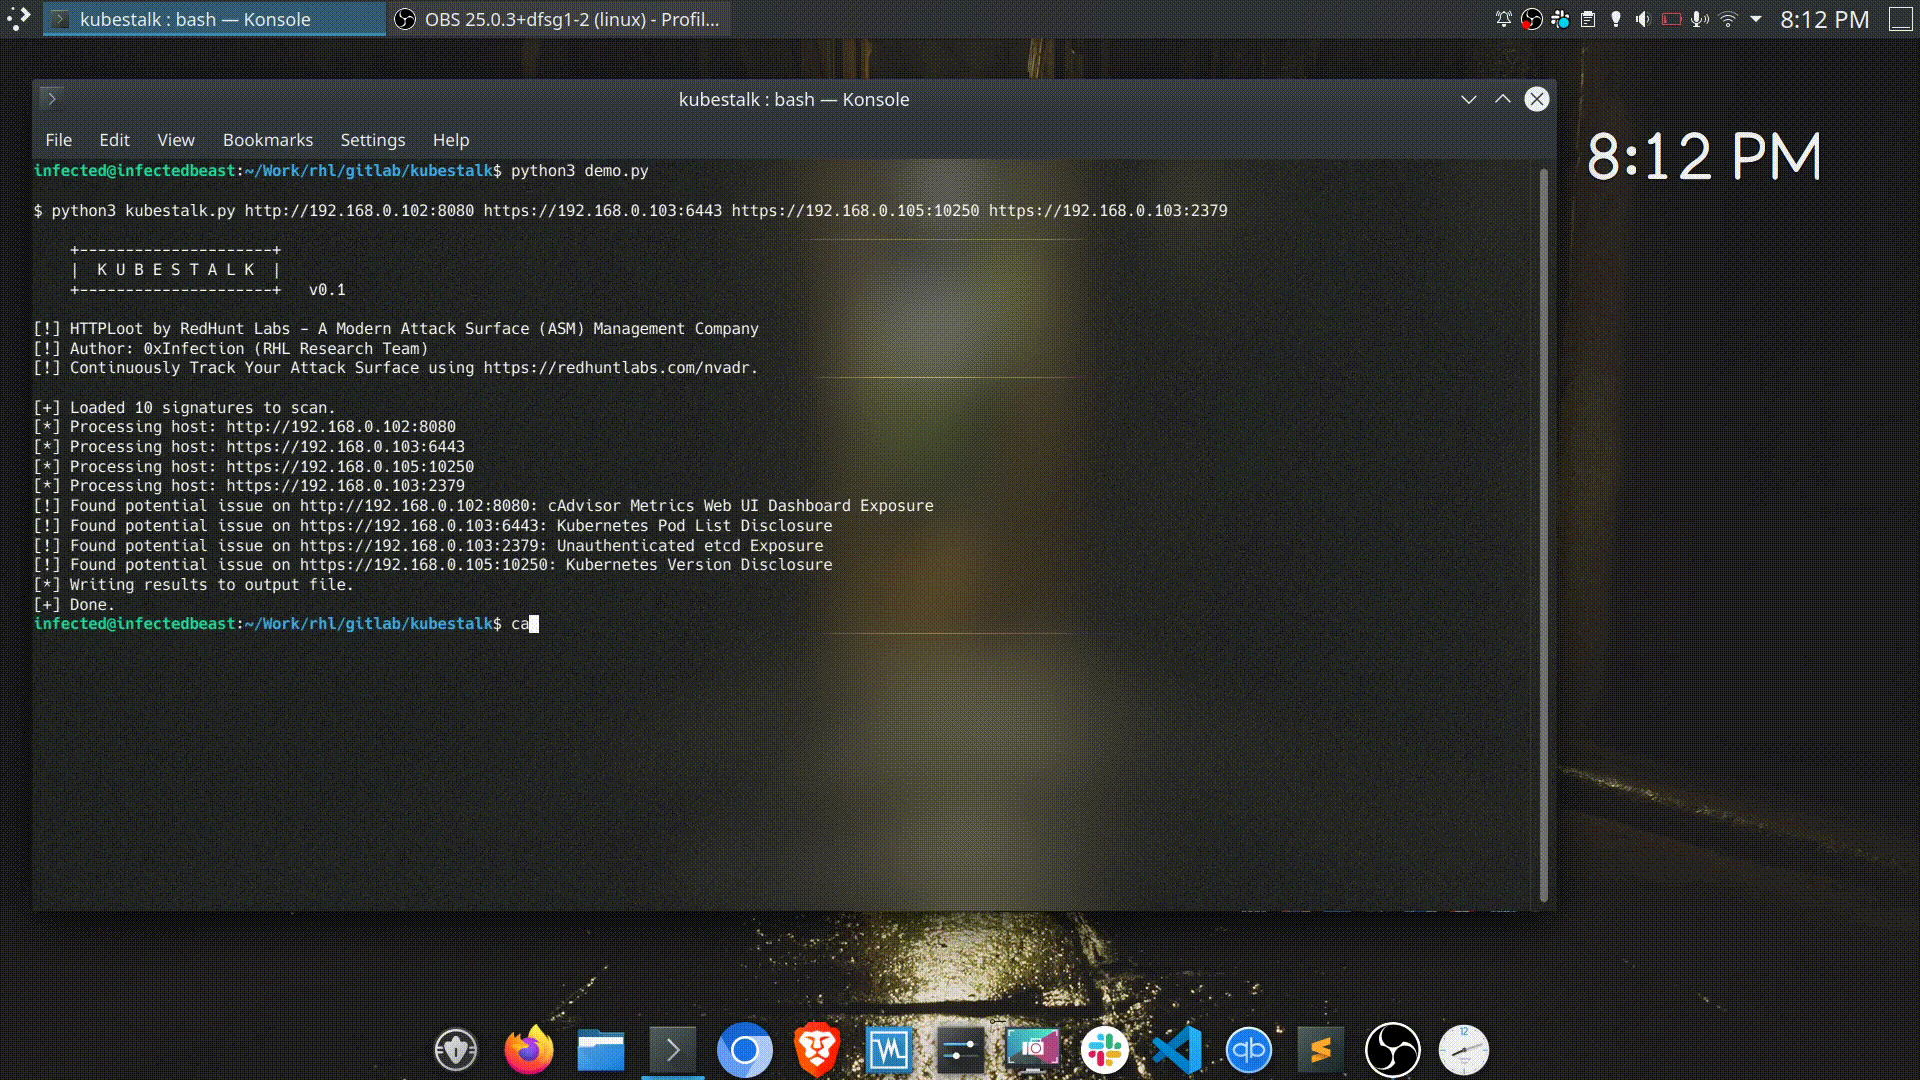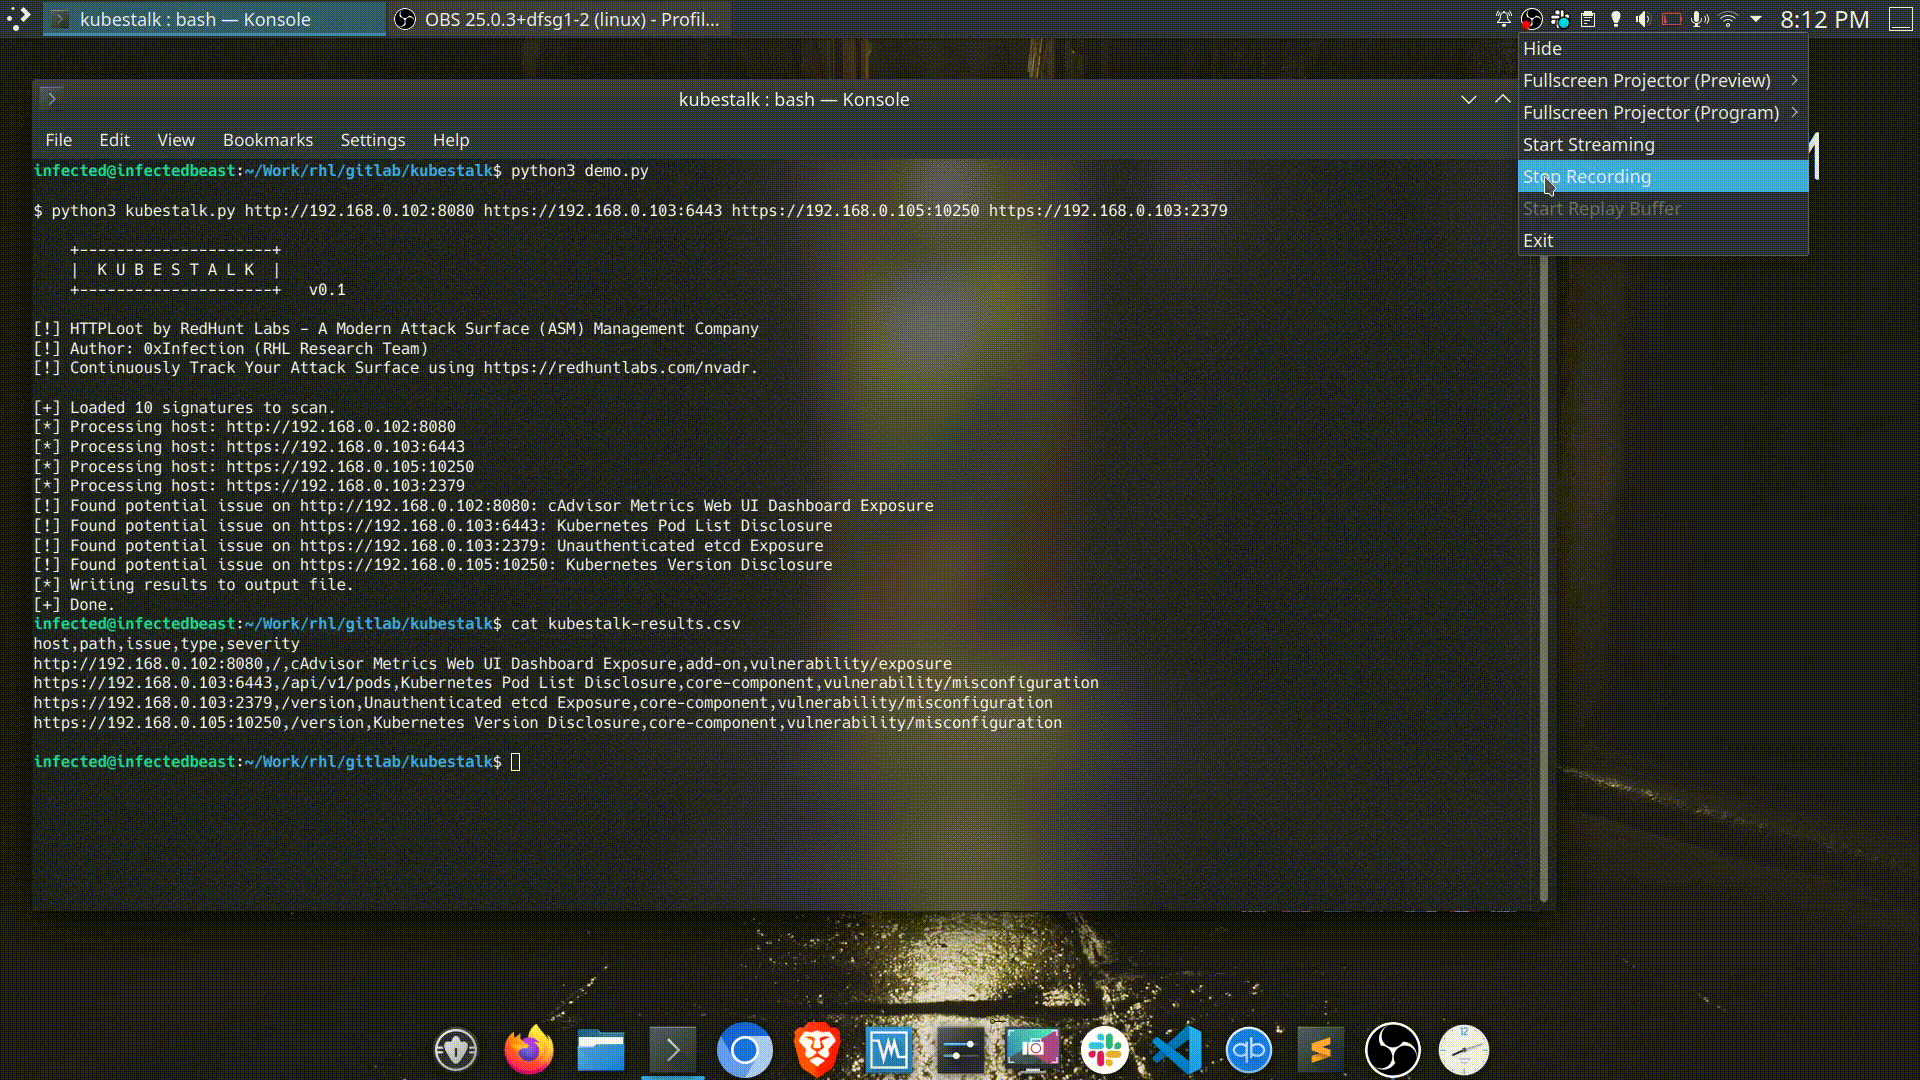 redhuntlabs/kubestalk
Black-box Kubernetes attack surface discovery tool that probes for unsecured clusters, exposed dashboards, and misconfigurations using…
 shiftleftsecurity/sast-scan
Scan is a free & Open Source DevSecOps tool for performing static analysis based security testing of your applications and its dependencies. CI and…
 rgielen/struts1filter
A request parameter filter solution for Struts 1 CVE-2014-0114 based on the work of Alvaro Munoz and the HP Fortify team
 amnnrth/cve-2025-34291_cors_security_scanner
A lightweight Python-based security assessment tool for detecting dangerous Cross-Origin Resource Sharing (CORS) misconfigurations - CVE-2025-34291.
 flyniu666/ingress-nginx-0.21-1.19.5
based on nginx 1.19.5 to fix for CVE-2018-16843, CVE-2018-16844, CVE-2019-9511, CVE-2019-9513, and CVE-2019-9516
 cyberark/kubiscan
A tool to scan Kubernetes cluster for risky permissions
 lightspin-tech/red-shadow
Scans AWS IAM configurations for shadow admins by detecting misconfigured deny policies that fail to restrict user actions on groups, enabling…
 jrmurray000/cve-2020-8554
OPA Gatekeeper-based policy templates to mitigate CVE-2020-8554 by restricting Kubernetes Service external IPs to an allow list, preventing traffic…
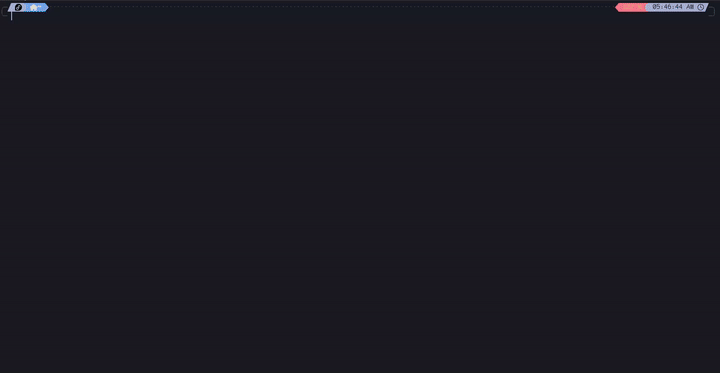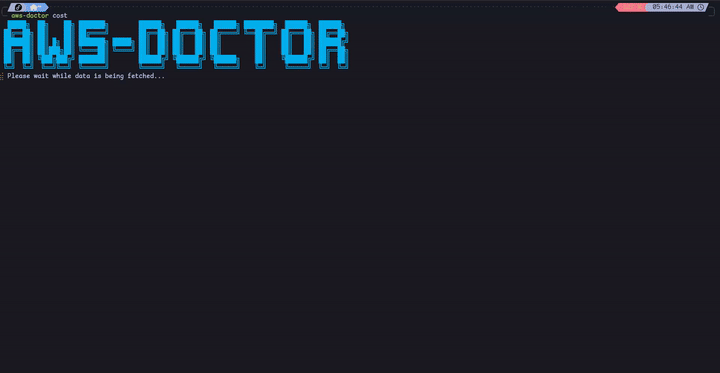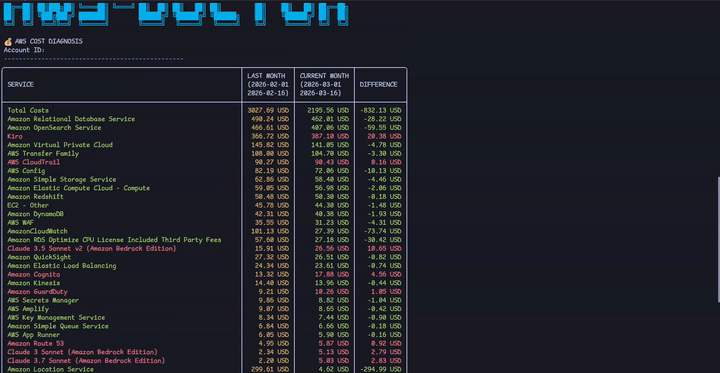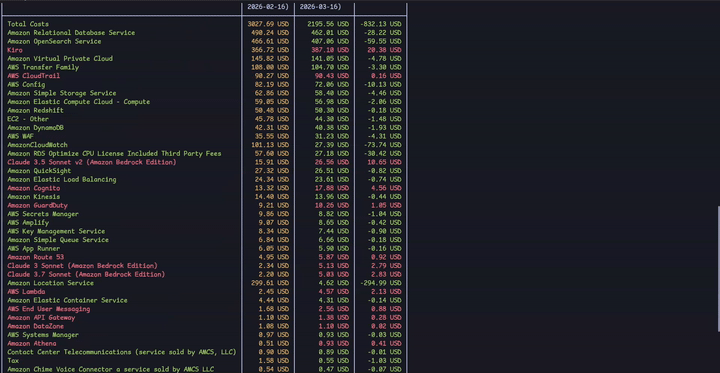 elc0mpa/aws-doctor
Powerful open-source CLI to audit security, costs, and best practices in AWS. 🩺 ☁️
 corgea/sighthound
Tree-sitter based static vulnerability scanner with pattern matching and taint-flow analysis for multi-language source code. Outputs findings as…
 voorivex/pentest-guide
Penetration tests guide based on OWASP including test cases, resources and examples.