CVE-2022-30190_Temporary_Fix_Source_Code

These are the source codes of the Python scripts to apply the temporary protection against the CVE-2022-30190 vulnerability (Follina)

These are the source codes of the Python scripts to apply the temporary protection against the CVE-2022-30190 vulnerability (Follina)

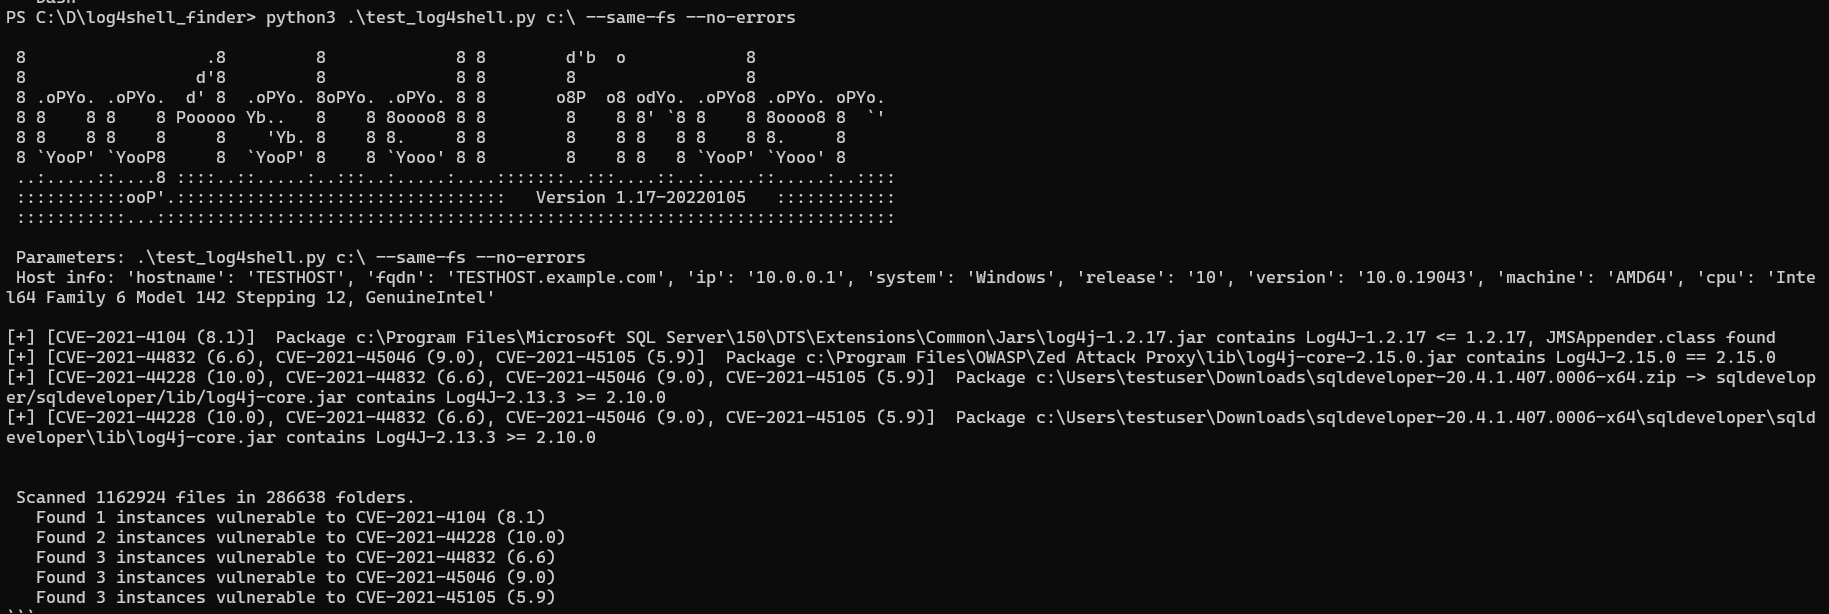
Fastest filesystem scanner for log4shell (CVE-2021-44228, CVE-2021-45046) and other vulnerable (CVE-2017-5645, CVE-2019-17571, CVE-2022-23305,…

CVE-2026-36213: MEmu Android Emulator 9.2.7.0 Local Privilege Escalation

Proof-of-Concept (POC) of a simple firewall in Python designed to mitigate the Spring4Shell (CVE-2022-22965) RCE attack by inspecting and blocking…

Python-based web security scanner that analyzes HTTP headers, SSL/TLS, DNS records, and common misconfigurations to generate a scored security report…

Here's a Python script that checks if the polyfill.io domain is present in the Content Security Policy (CSP) header of a given web application.

This script is a tool to recursively download the contents of the '.git' directory from a website. Using Python and libraries like 'requests' and…

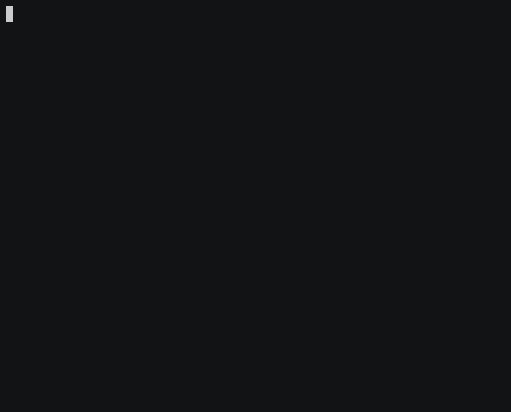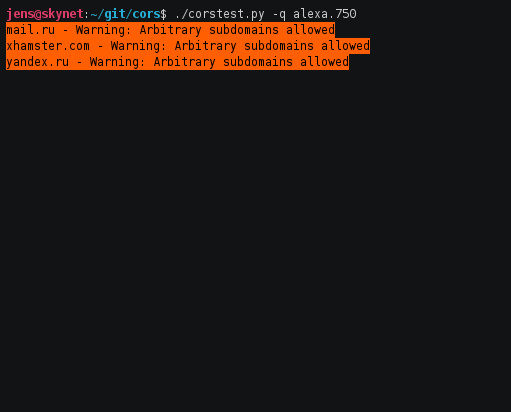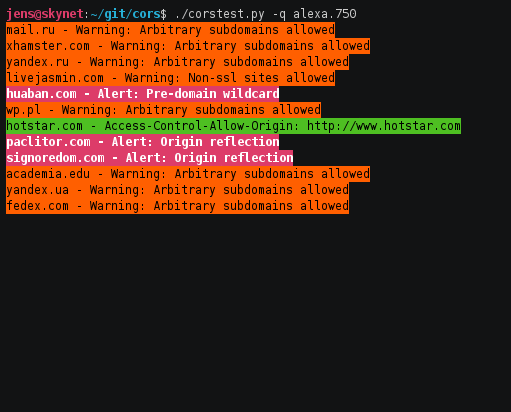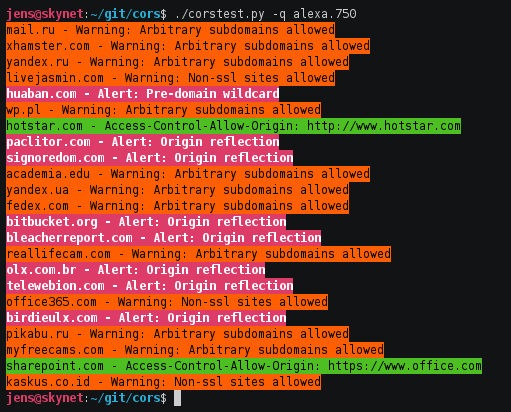
A simple CORS misconfiguration scanner

Vajra is a UI-based tool with multiple techniques for attacking and enumerating in the target's Azure and AWS environment. It features an intuitive…

Proof-of-concept exploit for Kubernetes service-account token disclosure via hostPath mounts; includes vulnerable pod YAML and Python token-theft…

Python script to bypass Azure APIM signup when UI is disabled, this is different from the CVE-2025-66390 as it does not require you to setup anything…

Lightweight Python script to detect CVE-2017-9798 in shared hosting environments by scanning for vulnerable .htaccess files, exiting with code 1 if…

AD Enum is a pentesting tool that allows to find misconfiguration through the the protocol LDAP and exploit some of those weaknesses with kerberos.

Multithreaded Plugin based vulnerability scanner for mass detection of web-based applications vulnerabilities

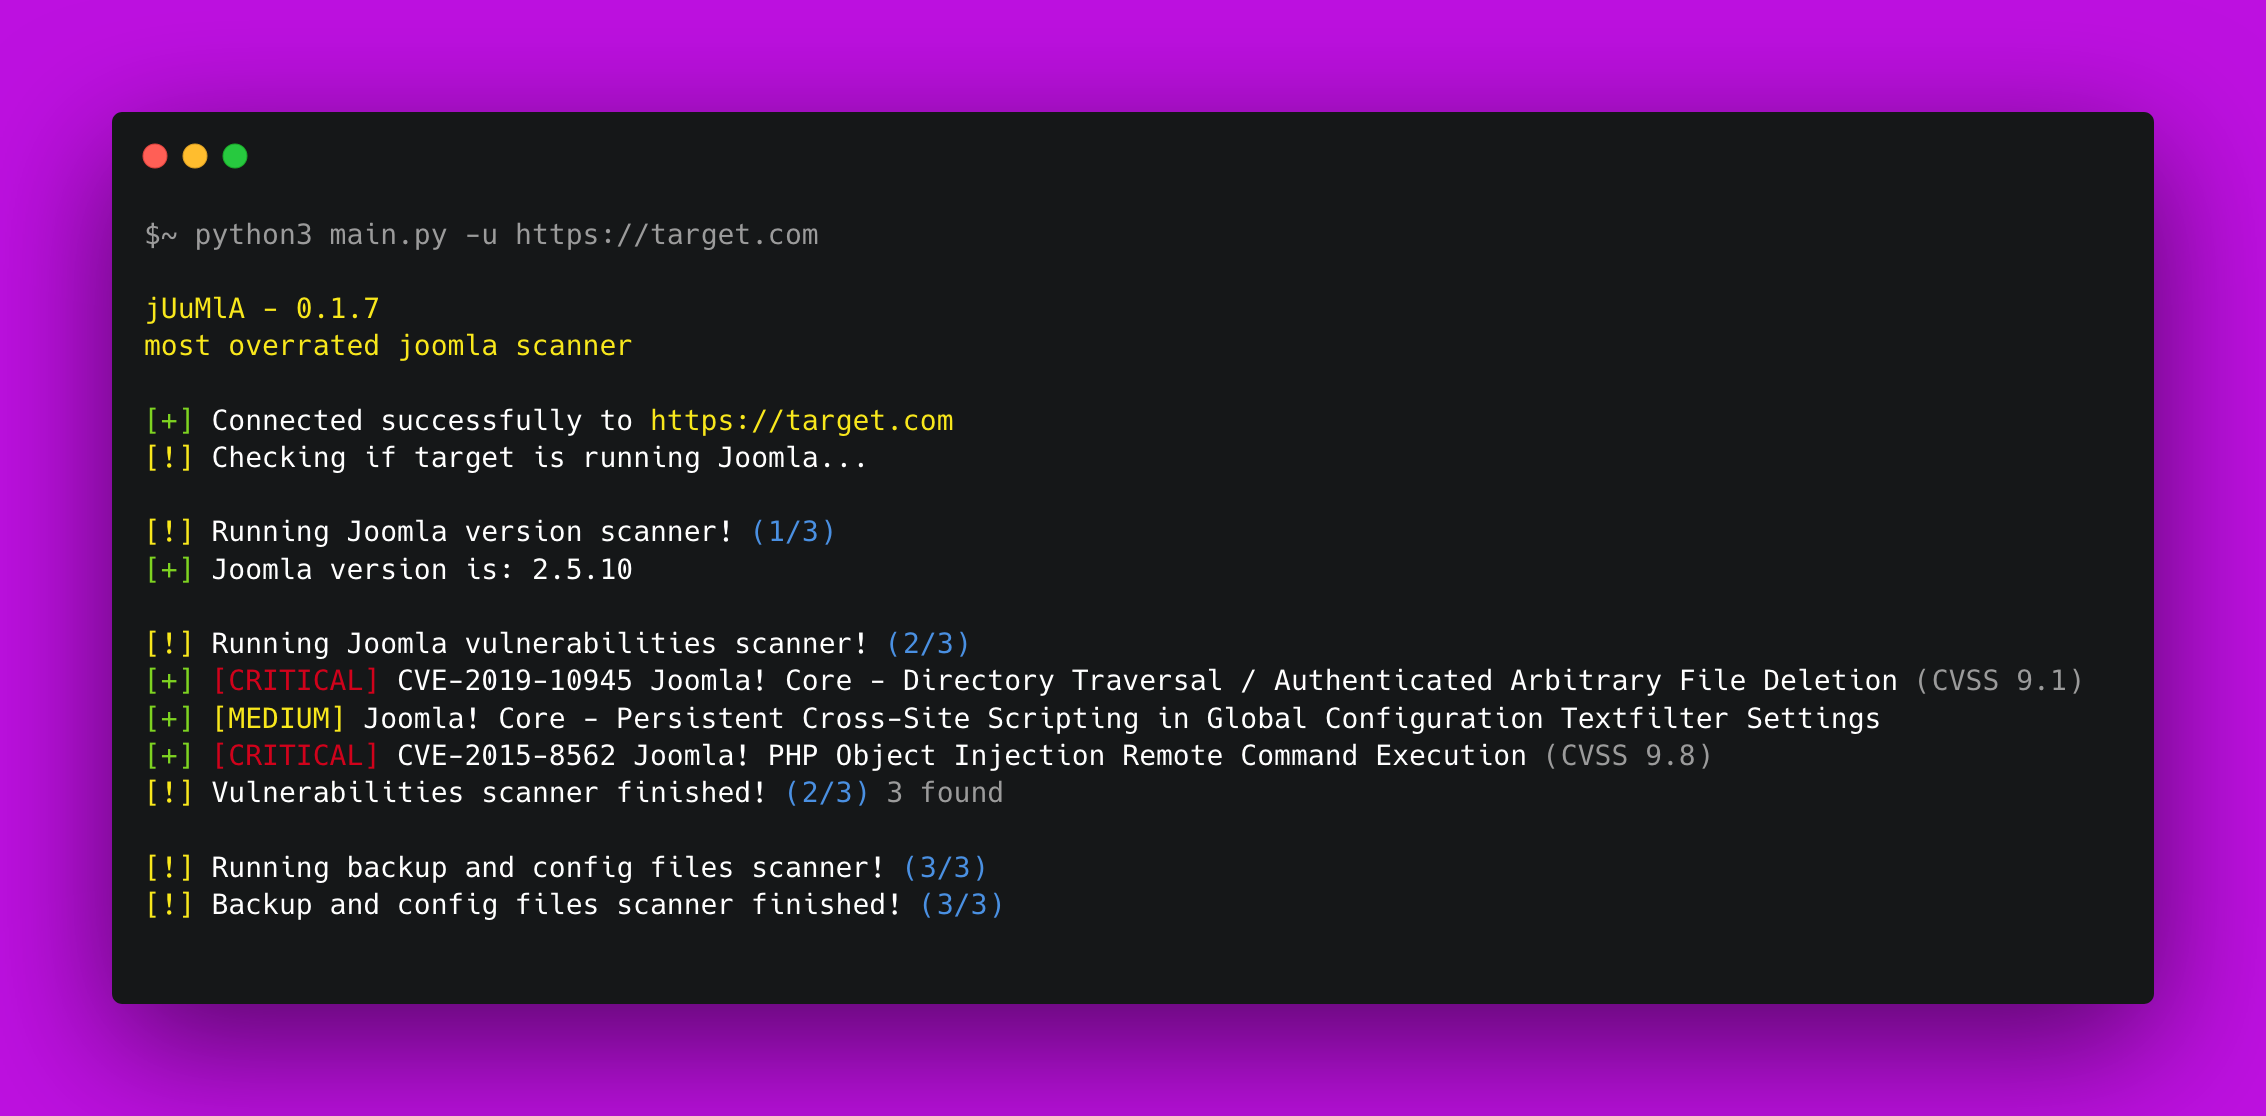
🦁 Python project to identify and scan for vulnerabilities related to the Joomla CMS project. It scans for common misconfigurations and public…

AI-powered SAST scanner that finds auth bypass, IDOR, and logic bugs Semgrep/CodeQL miss. Free GitHub Action. Supports Python, JS/TS, Go, PHP, Ruby.

Scanner: CVE-2025-34291 Langflow Origin Validation Error / CORS Misconfiguration — Python checker (CISA KEV)

🔎 Find origin servers of websites behind CloudFlare by using Internet-wide scan data from Censys.