CVE-2024-11680_PoC_Exploit

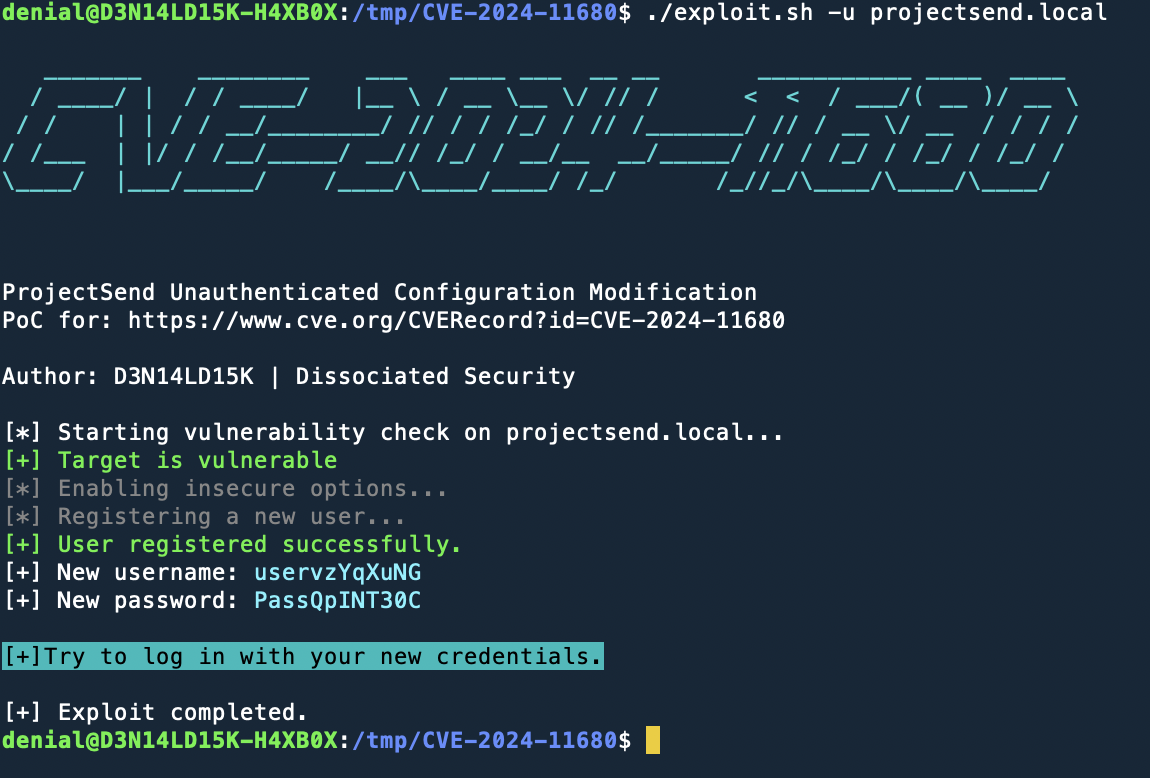
This repository contains a Proof of Concept (PoC) exploit for CVE-2024-11680, a critical vulnerability in ProjectSend r1605 and older versions. The…

This repository contains a Proof of Concept (PoC) exploit for CVE-2024-11680, a critical vulnerability in ProjectSend r1605 and older versions. The…

Exploit for CVE-2024-31989.

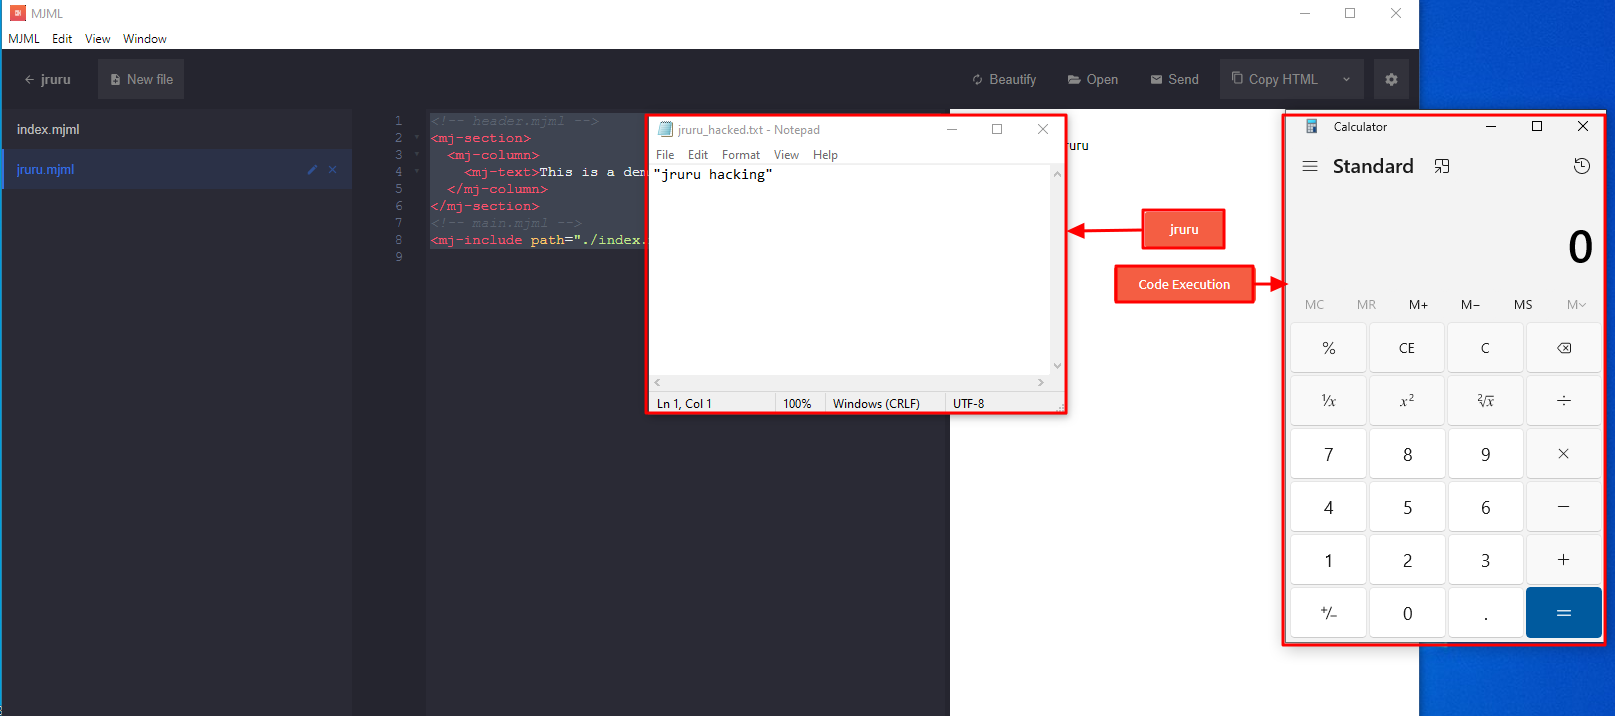
mjml-app v3.0.4 & 3.1.0-beta RCE exploit

Scanner for CVE-2024-40725 Apache HTTP Server source-code disclosure; probes direct and subrequest paths, fingerprints affected versions, and outputs…

Hands-on lab demonstrating CVE-2024-38819 Spring Framework path traversal vulnerability with vulnerable and patched Spring Boot deployments for…

Proof-of-concept exploit for CVE-2024-23733: Incorrect Access Control in Software AG webMethods Integration Server 10.15.0 allowing remote attackers…

Proof-of-concept exploit for CVE-2024-4898, a missing authorization vulnerability in InstaWP Connect WordPress plugin allowing unauthenticated API…

Proof-of-concept exploit for CVE-2024-1302 demonstrating unauthenticated log file download in Badgermeter moni:tool, exposing sensitive information…

Proof-of-concept exploit for CVE-2024-5326, a missing authorization vulnerability in the PostX WordPress plugin allowing authenticated attackers to…

Step-by-step tutorial for detecting CVE-2024-3094 (XZ Backdoor) in container images using Trend Micro Vision One TMAS CLI, with automated scanning…

Python-based scanner that checks Docker hosts for CVE-2024-41110 by detecting vulnerable Docker versions and AuthZ plugin usage.

Nuclei template to detect Apache servers vulnerable to CVE-2024-38473

Shell script and Ansible playbook to detect and remediate CVE-2024-3094 in xz-utils by checking package versions, upgrading or downgrading to a…

A specialized vulnerability scanner designed to detect CVE-2024-38526, the Polyfill.io Supply Chain Attack, helping organizations identify and…

A script to detect if xz is vulnerable - CVE-2024-3094

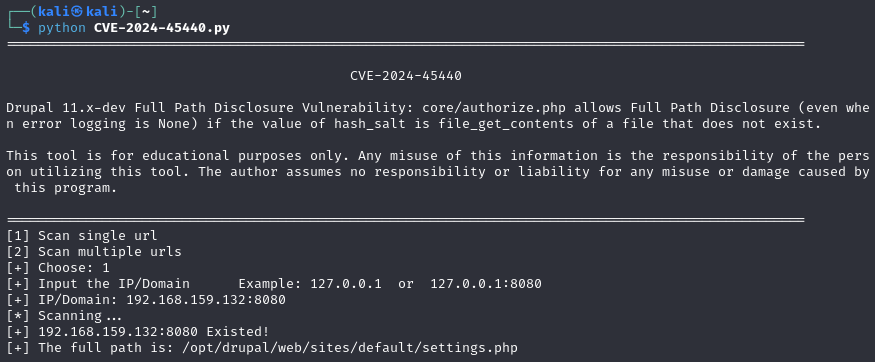
Drupal CVE-2024-45440

Best house rental management system Local file contains vulnerability

Secure fork of Startklar Elementor Addons. Patched CVE-2024-5153 & File Upload vulnerabilities.