
CVE-2023-5044
 kubernetesbachelor/cve-2023-5044
Poc for CVE 2023 5044
cloud-infrastructure-securitycloud-securitycontainer-security+4
kubernetesbachelor/cve-2023-5044Poc for CVE 2023 5044
 kh4sh3i/cve-2023-22515
CVE-2023-22515 - Broken Access Control Vulnerability in Confluence Data Center and Server
 horizon3ai/cve-2023-27524
Basic PoC for CVE-2023-27524: Insecure Default Configuration in Apache Superset
 oligocybersecurity/shelltorchchecker
A tool that checks if a TorchServe instance is vulnerable to CVE-2023-43654
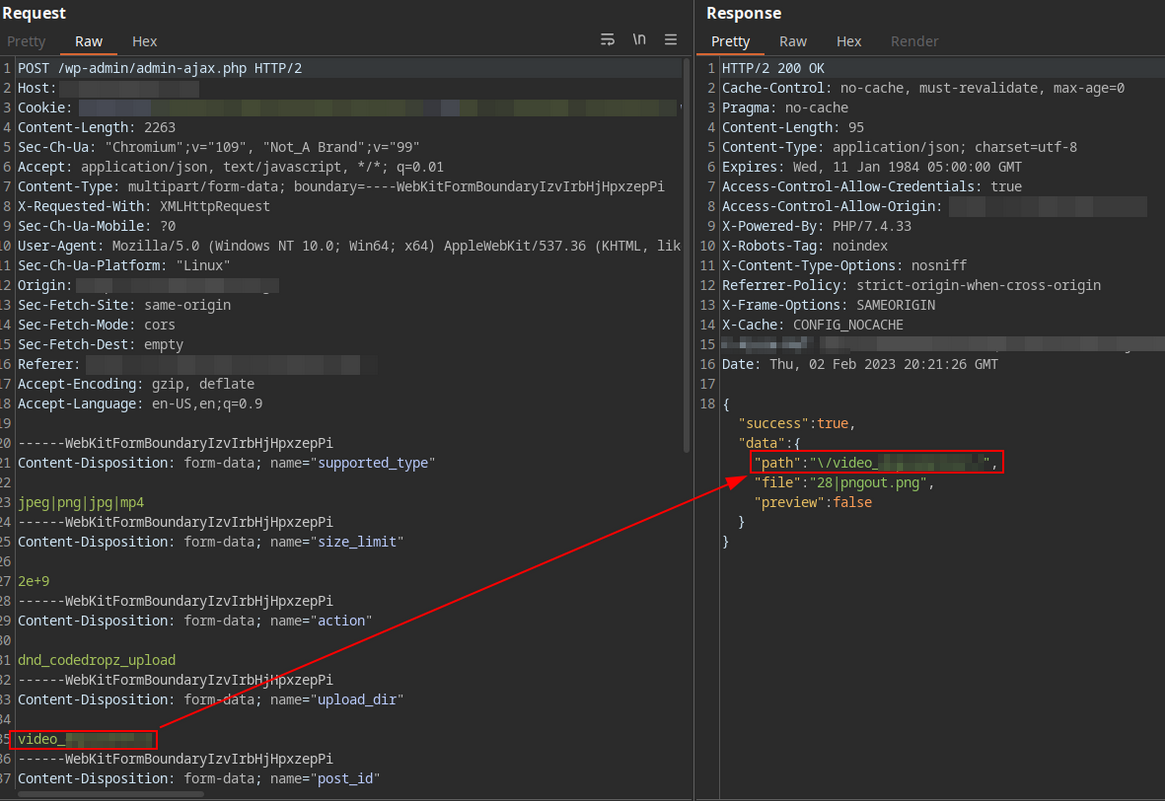 nickguitar/drag-and-drop-multiple-file-uploader-pro-path-traversal
Drag and Drop Multiple File Uploader PRO - Contact Form 7 v5.0.6.1 Path Traversal (CVE-2023-1112)
 acheiii/cve-2023-28432
CVE-2023-28432 POC
 tarraschk/cve-2023-36884-checker
Script to check for CVE-2023-36884 hardening
 ajf8729/blacklotus
BlackLotus aka CVE-2023-24932 Detection/Remediation Scripts for Intune, ConfigMgr, and generic use
 vulnmachines/cisco_cve-2023-20198
Cisco CVE-2023-20198
 maniak-academy/mitigate-cve-2023-46747
Ansible playbook to automate mitigation of CVE-2023-46747 (BIG-IP unauthenticated RCE) by applying F5's official script across multiple devices.
 dnkhack/fixcve2023_39526_2023_39527
Prestashop fix vulnerability CVE-2023-39526 & CVE-2023-39527
 drkbcn/lblfixer_cve_2023_28447
Module for PrestaShop 1.7.X to fix CVE-2023-28447 vulnerability (Smarty XSS)
 ridsoliveira/fix-cve-2023-36884
PowerShell script to apply Microsoft's recommended registry-based workaround for CVE-2023-36884, mitigating remote code execution risk on Windows…
 vulnmachines/confluence-cve-2023-22515
Confluence Broken Access Control
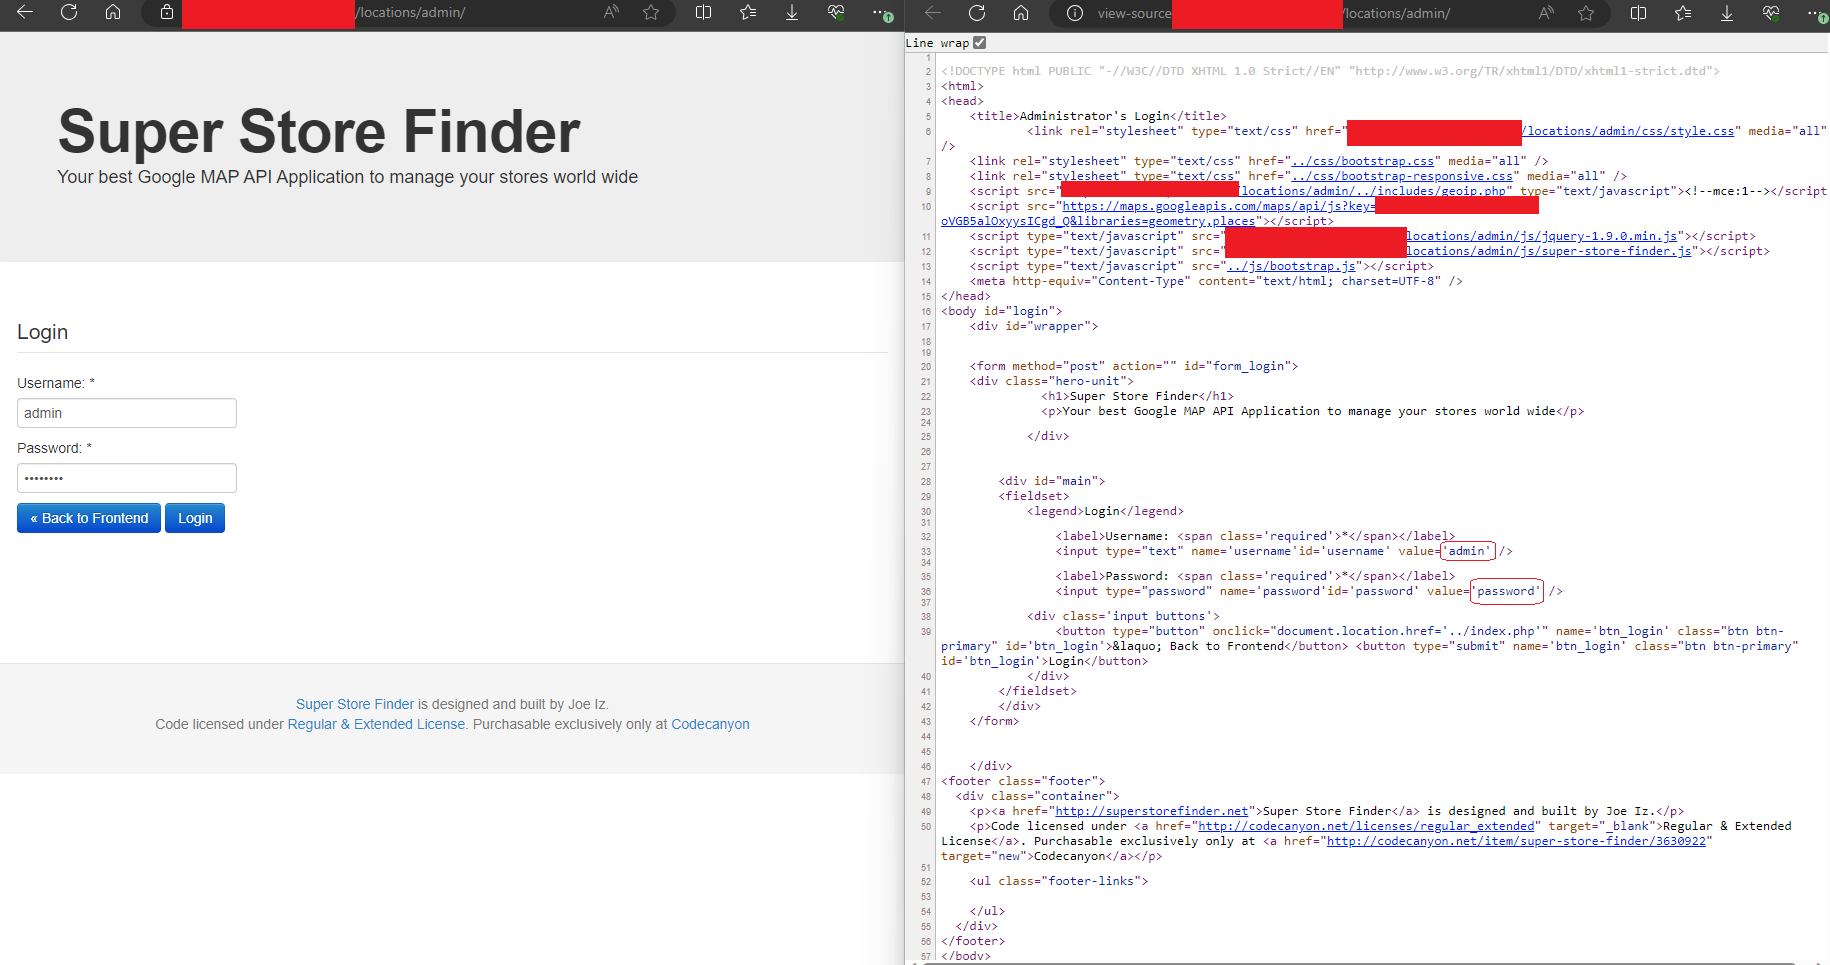 redblueteam/cve-2023-41508
CVE-2023-41508 - A hard-coded password in Super Store Finder v3.6 allows attackers to access the administration panel.
 trackflaw/cve-2023-25202
CVE-2023-25202: Insecure file upload mechanism
 ysaxon/pyrocms-ssti-fix
A drop-in fix for CVE-2023-29689 - SSTI in PyroCMS, via a custom Twig Sandbox implementation
 skr11lex/cve-2023-33477
Exploit for CVE-2023-33477, an unauthorized configuration file download vulnerability in Harmonic NSG 9000-6G modulator, allowing remote attackers to…