

metasploitable-penetration-testing-lab
 yagnikkrish/metasploitable-penetration-testing-lab
Controlled penetration testing lab demonstrating CVE-2011-2523 exploitation and mitigation techniques.
defensive-toolseducationexploitation+8
yagnikkrish/metasploitable-penetration-testing-labControlled penetration testing lab demonstrating CVE-2011-2523 exploitation and mitigation techniques.
 alessandroz/beroot
Privilege Escalation Project - Windows / Linux / Mac
 machine1337/hackguard
FAST WEB APPLICATION VULNERABILITY SCANNER written in python3
 visaicyber/cve-2025-27591-below-
Local Privilege Escalation vai `below` (CVE-2025-27591) - PoC Exploit
 nizar0x1f/cve-2021-26084-patch-
CVE-2021-26084 patch as provided in "Confluence Security Advisory - 2021-08-25"
 denoland/clawpatrol
Wire-level proxy firewall for AI agents that intercepts and gates SQL, Kubernetes, and HTTP traffic using HCL rules, with per-process tunnel…
 raffaele-forte/climber
Check UNIX/Linux systems for privilege escalation
 sobri3195/pegasus-pentest-arsenal
A comprehensive web application security testing toolkit that combines 10 powerful penetration testing features into one tool.
 xuwu-xuwu/cve-2026-68004
Standalone PoC for unauthenticated RTMP publish in SRS media servers; verifies the vulnerability, supports HTTP API side-channel check, and enables…
 voorivex/pentest-guide
Penetration tests guide based on OWASP including test cases, resources and examples.
 logisek/evilmist
EvilMist is a collection of scripts and utilities designed to support cloud penetration testing & red teaming. The toolkit helps identify…
 nixwizard/kube-alien
Automated Kubernetes cluster penetration testing tool that exploits misconfigurations in API, Kubelet, etcd, and Dashboard to achieve node takeover…
 admin2099/penetration-testing-assessment-23-04-2026
Penetration testing assessment of a vulnerable IIS 6.0 WebDAV server, demonstrating reconnaissance, enumeration, exploitation (CVE-2017-7269), and…
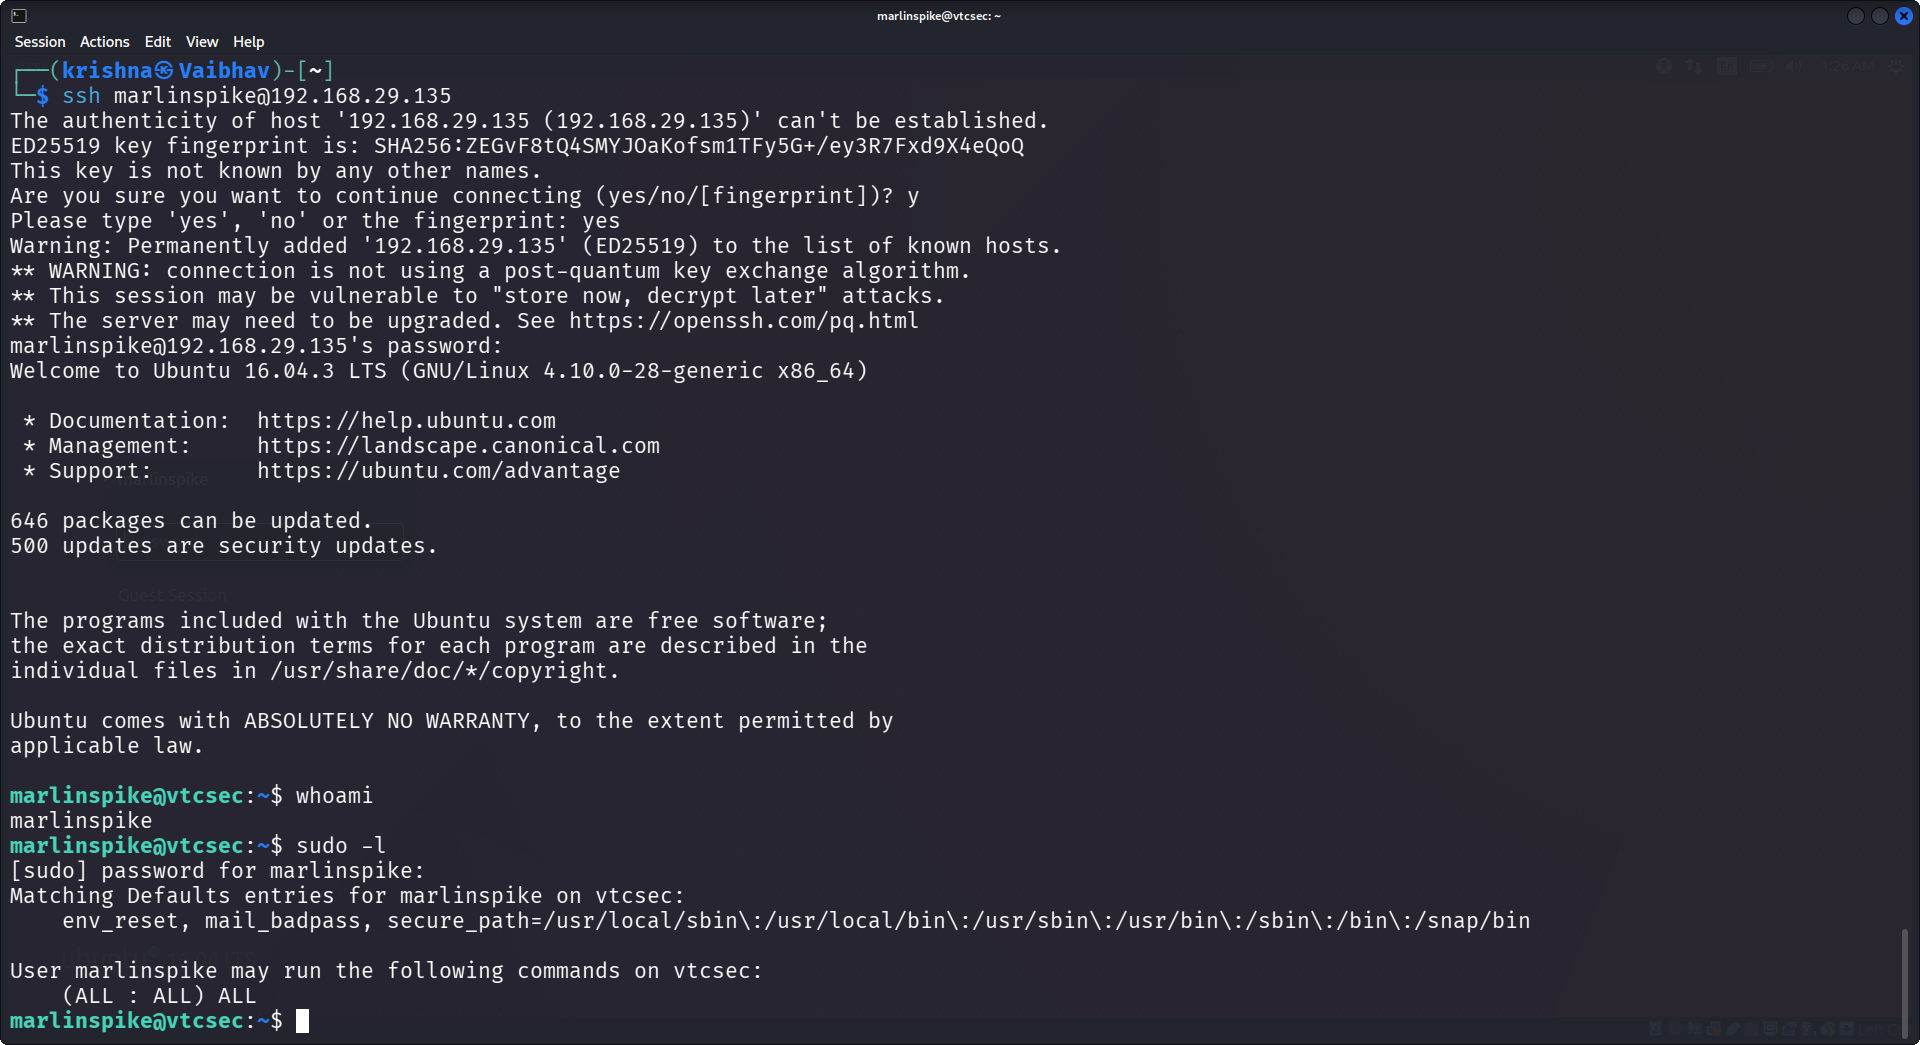 vaibhavkrishna12004/ubuntu-privesc-lab
Full penetration testing workflow: credential brute force, SSH access and privilege escalation (CVE-2021-4034)
 stampery/mongoaudit
🔥 A powerful MongoDB auditing and pentesting tool 🔥
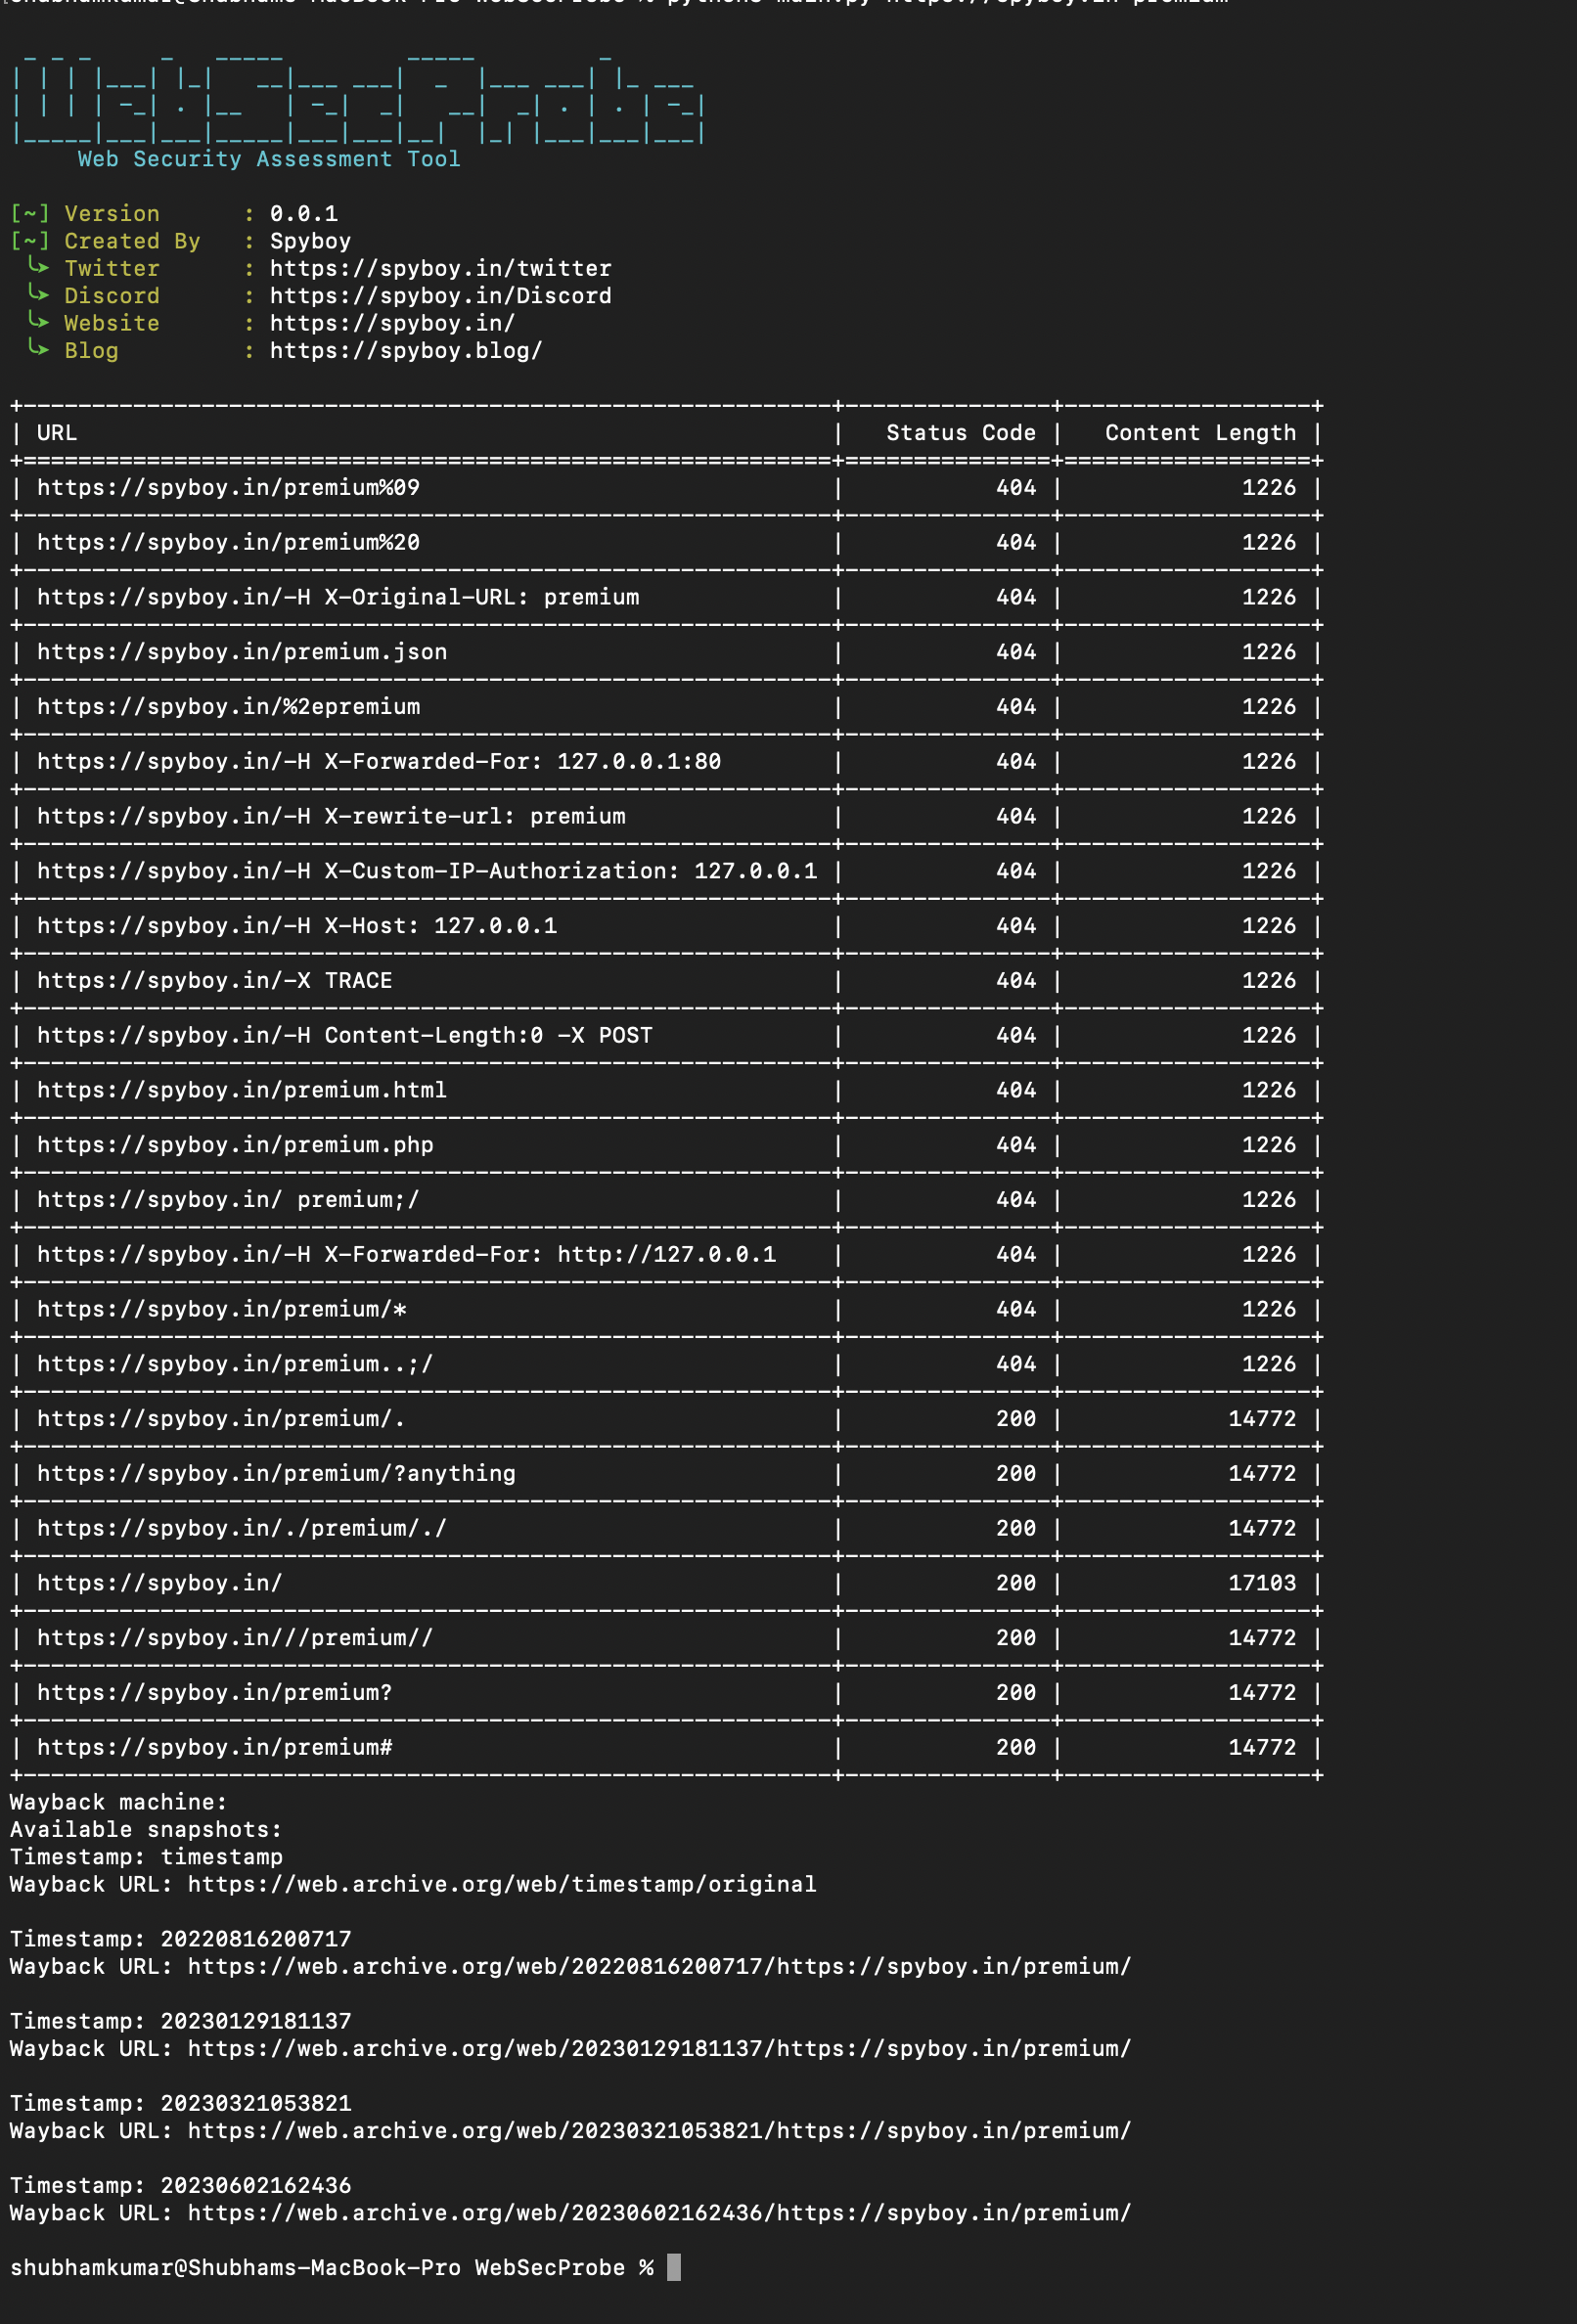 spyboy-productions/websecprobe
Security testing tool for analyzing HTTP 403 responses and identifying access control misconfigurations in web applications.
 akabe1/oauthscan
Burp Suite Extension useful to verify OAUTHv2 and OpenID security
 skokoo/imcurvin
Automated web security auditing tool that detects environment misconfigurations, probes backend vulnerabilities, and bypasses WAF/IDS protections…