
CVE-2025-65900
 noxurge/cve-2025-65900
DifuseHQ Kalmia CMS version 0.2.0 contains an Incorrect Access Control vulnerability in the /kal-api/auth/users API endpoint. Due to insufficient…
authenticationexploitationmisconfiguration+3
noxurge/cve-2025-65900DifuseHQ Kalmia CMS version 0.2.0 contains an Incorrect Access Control vulnerability in the /kal-api/auth/users API endpoint. Due to insufficient…
 moniik/poc_salesforce_lightning
Academic purposes only. Attack against Salesforce lightning with guest privilege.
 praetorian-inc/trajan
A multi-platform CI/CD vulnerability detection and attack automation tool for identifying security weaknesses in pipeline configurations.
 thirukguru/aws-perimeter
A terminal-based AWS Security Scanner with 102+ security checks across VPC, IAM, S3, CloudTrail, containers (ECS/EKS), and AI attack detection.…
 coreruleset/coreruleset
Generic attack detection rule set for web application firewalls, protecting against OWASP Top Ten and common vulnerabilities with minimal false…
 mandiant/azure_workshop
Terraform-deployable vulnerable-by-design Azure lab with realistic attack paths and common misconfigurations for practicing red teaming and security…
 nccgroup/scoutsuite
Multi-cloud security auditing tool that leverages cloud provider APIs to gather configuration data, assess security posture, and generate HTML…
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
 xmcyber/xmgoat
Terraform-based Azure security lab with intentionally misconfigured environments for hands-on attack and compromise practice. Includes scenario flows…
 mvelazc0/badzure
BadZure automates the deployment of intentionally misconfigured Entra ID tenants and Azure subscriptions, populating them with diverse entities and…
 padayali-jd/pollyscan
A specialized vulnerability scanner designed to detect CVE-2024-38526, the Polyfill.io Supply Chain Attack, helping organizations identify and…
 yolabingo/wordpress-fix-cve-2018-6389
Apache RewriteRule to mitigate potential DoS attack via Wordpress wp-admin/load-scripts.php file
 naveenbana5250/cve-2023-34362-defense-package
Threat-Informed Detection & Mitigation Package for MOVEit Transfer Vulnerability
 biitts/cve-2026-56423-misp-deleteselection-brokenaccesscontrol
PoC for CVE-2026-56423: MISP deleteSelection broken access control (CWE-862, contributor hard-deletes other orgs' Event Reports/Sharing Groups, CVSS…
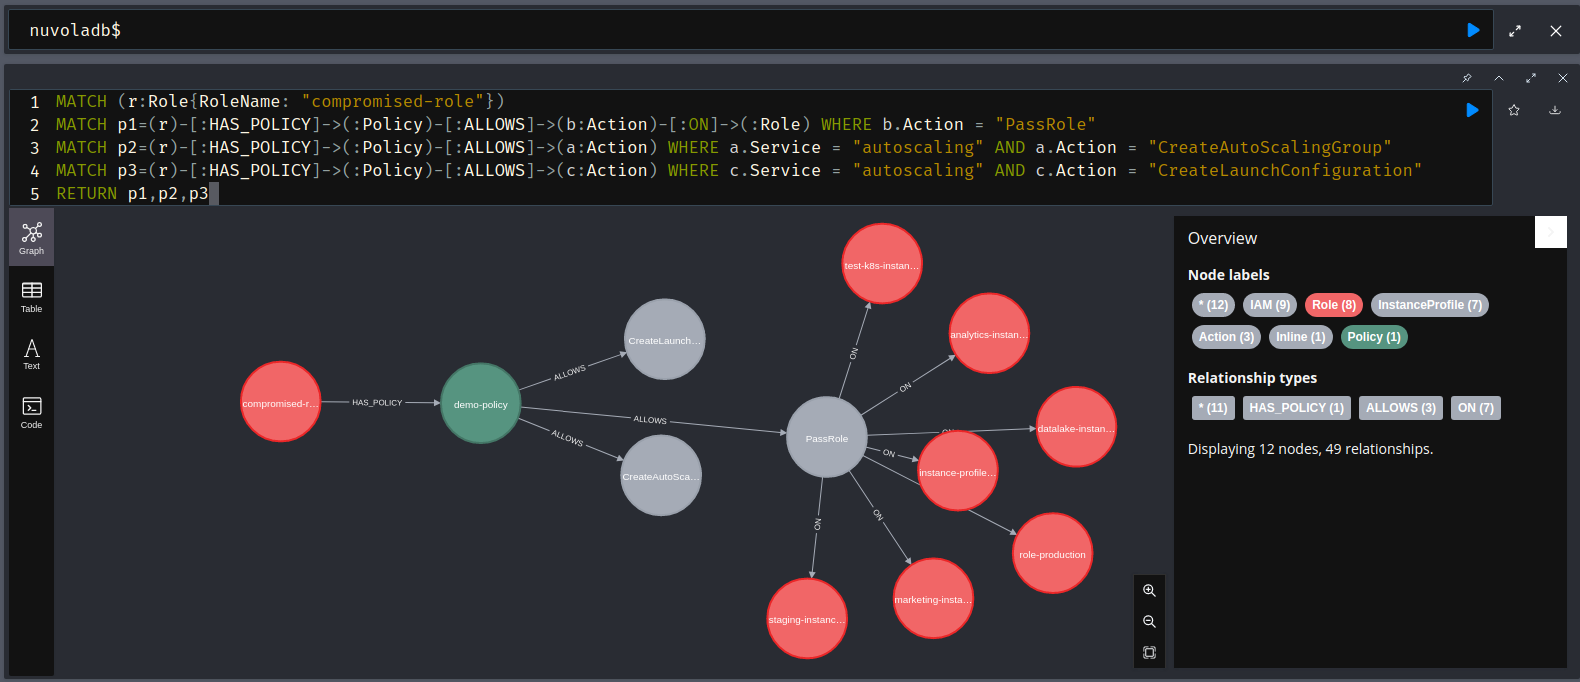 primait/nuvola
Graph-based AWS security analysis tool that dumps cloud configurations, detects misconfigurations, and maps attack paths using a Neo4j digital twin…
 logisek/evilmist
EvilMist is a collection of scripts and utilities designed to support cloud penetration testing & red teaming. The toolkit helps identify…
 zsxen/cve-2025-1974
Windows 11-first educational lab for studying CVE-2025-1974 in ingress-nginx. Provides safe attack emulation and defense validation with local…
 fdzdev/cve-2024-50964
Documentation of CVE-2024-50964: critical DMARC policy bypass in DonWeb MX server allowing email spoofing, with low attack complexity and no required…