

CVE-2023-49981
 geraldoalcantara/cve-2023-49981
School Fees Management System v1.0 - Incorrect Access Control - Directory Listing
information-gatheringmisconfigurationpenetration-testing+2
geraldoalcantara/cve-2023-49981School Fees Management System v1.0 - Incorrect Access Control - Directory Listing
 geraldoalcantara/cve-2023-49980
Proof-of-concept for CVE-2023-49980: directory listing vulnerability in Best Student Result Management System 1.0 allowing unauthorized access to…
 austino2000/cve-2024-22534
Proof-of-concept demonstrating information leakage in OneinStack deployment tool via exposed endpoints (phpinfo.php, xprober.php, ocp.php) leading to…
 afine-com/cve-2024-5735
AdmirorFrames Joomla! Extension < 5.0 - Full Path Disclosure
 moften/cve-2021-21424
El WebProfiler de Symfony expone rutas internas del servidor si no está deshabilitado en producción
 geraldoalcantara/cve-2023-49545
Customer Support System 1.0 - Directory Listing
 infosec4fun/cve-2020-10132
CVE-2020-10132 - SearchBlox product before V-9.1 is vulnerable to CORS misconfiguration.
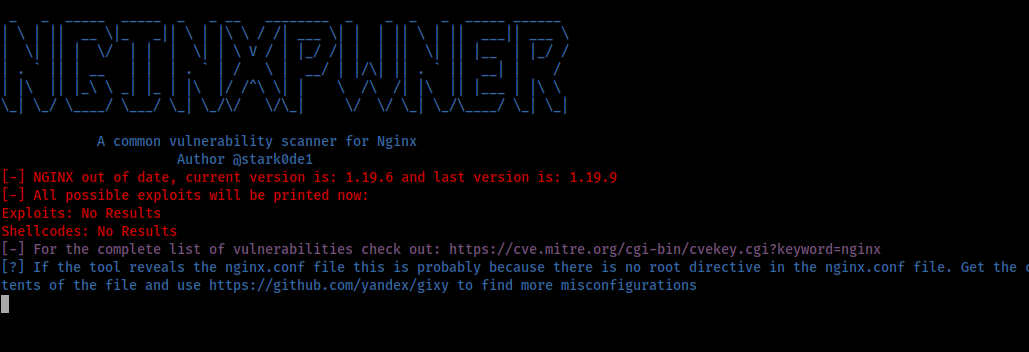 stark0de/nginxpwner
Nginxpwner is a simple tool to look for common Nginx misconfigurations and vulnerabilities.
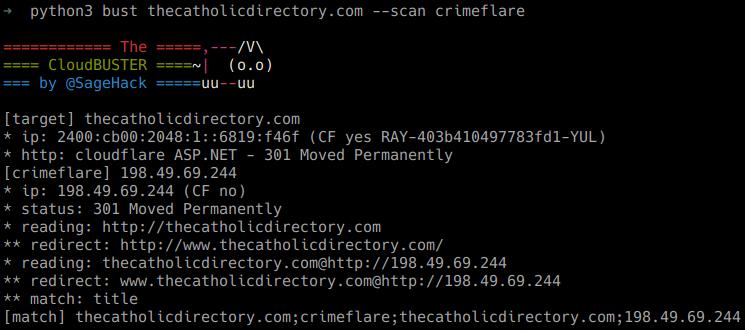 sagehack/cloud-buster
A Cloudflare resolver that works
 swzhouu/cve-2020-26732
SKYWORTH GN542VF Hardware Version 2.0 and Software Version 2.0.0.16 does not set the Secure flag for the session cookie in an HTTPS session
 edoverflow/megplus
Automated reconnaissance wrapper — TomNomNom's meg on steroids. [DEPRECATED]
 abraxas/ats-jsonrpc-unrestricted
Apache Traffic Server 10.2.0 - High - Local - Privilege leftover - JSON-RPC unix socket unrestricted mode 0777
 christophetd/cloudflair
🔎 Find origin servers of websites behind CloudFlare by using Internet-wide scan data from Censys.
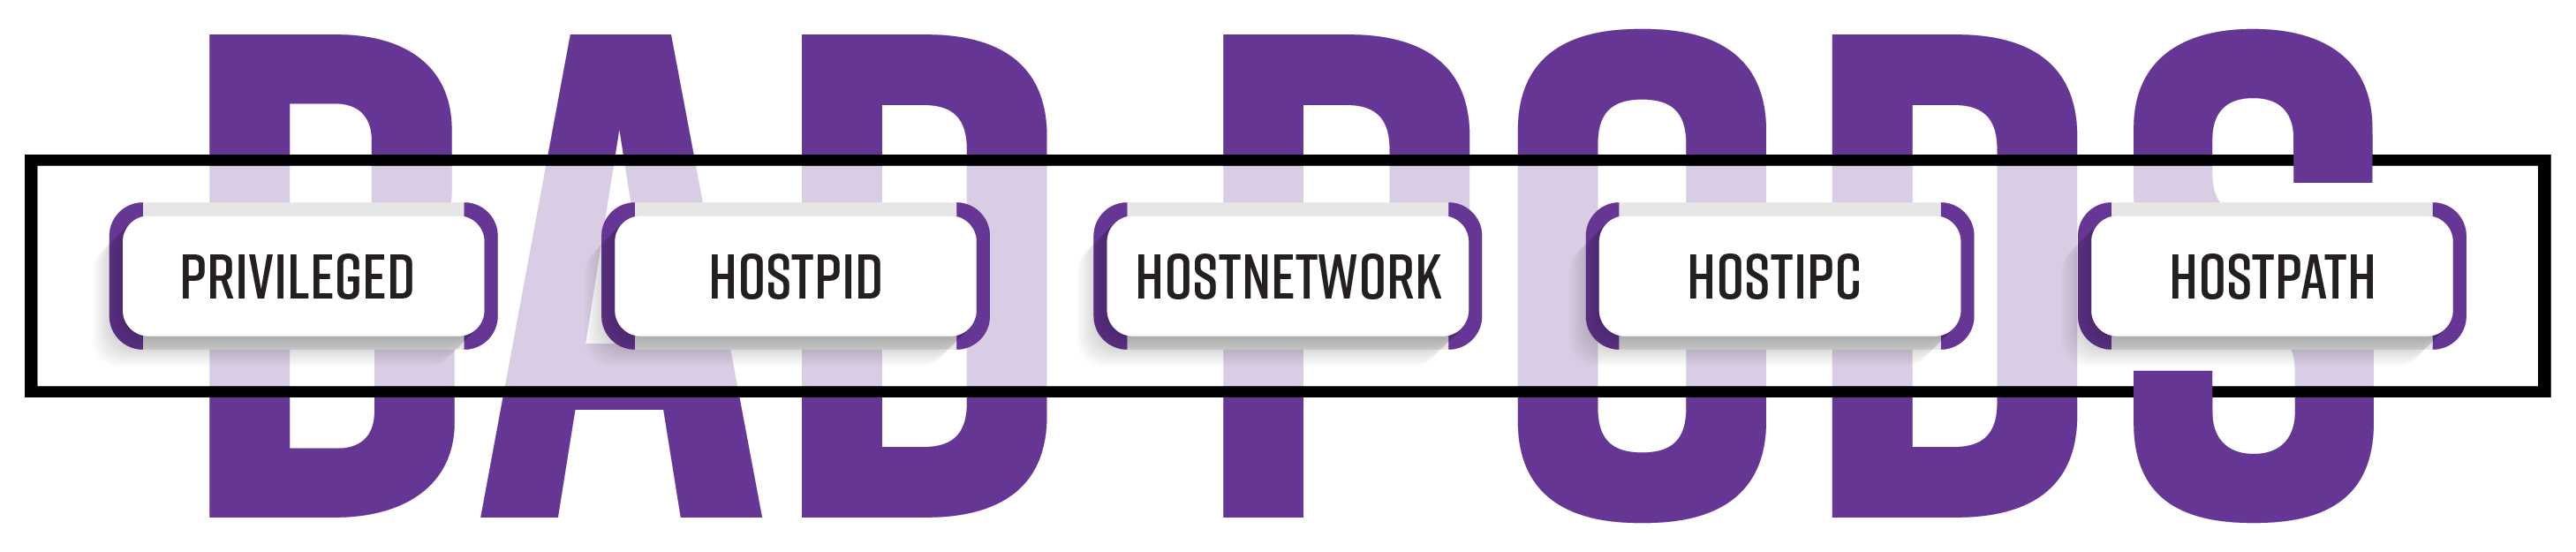 bishopfox/badpods
A collection of manifests that will create pods with elevated privileges.
 ekitji/siem
Curated SIEM queries and techniques for offensive discovery of Windows privilege escalation, misconfigured ACLs, services, scheduled tasks, and…
 blacksky-algorithms/atproto
Fork of the AT Protocol reference implementation with performance-optimized AppView, Rust-based firehose indexer, Redis caching, and community…
 nccgroup/s3_objects_check
Whitebox evaluation of effective S3 object permissions, to identify publicly accessible files.
 owasp/owasp-subtractive-hardening-top-10
The OWASP Subtractive Security Top 10 Project is an initiative to identify, document, and promote the highest-impact opportunities for reducing cyber…