
mitigate-folina
 derco0n/mitigate-folina
Mitigates the "Folina"-ZeroDay (CVE-2022-30190)
defensive-toolsincident-responsemisconfiguration+1
14 years ago
derco0n/mitigate-folinaMitigates the "Folina"-ZeroDay (CVE-2022-30190)
 edgarloyola/cve-2021-40904
Proof-of-concept for remote code execution in CheckMK Raw Edition 1.5.0–1.5.0p25 via misconfigured Dokuwiki embedded application allowing PHP code…
 randomrobbiebf/cve-2024-43998
Blogpoet <= 1.0.2 - Missing Authorization via blogpoet_install_and_activate_plugins()
 huzaifahussain98/cve-2020-23586
CSRF allows to Add Network Traffic Control Type Rule
 ready2disclose/cve-2022-43110
CVE-2022-43110
 centariscyber/cve-2022-41040_mitigation
PowerShell script to mitigate CVE-2022-41040 on affected Exchange servers by applying recommended configuration changes.
 codepontiff/next_js_poisoning
The CVE-2024-46982 is cache poisoning of next_js some site have API to load their image
 mbadanoiu/cve-2019-14222
CVE-2019-14222: Default Certificate in Alfresco Community
 0xbytehunter/cve-2024-50967
DATAGERRY Broken Access Control
 stefandorresteijn/cve-2021-39409
Admin account registration in Online Student Rate System
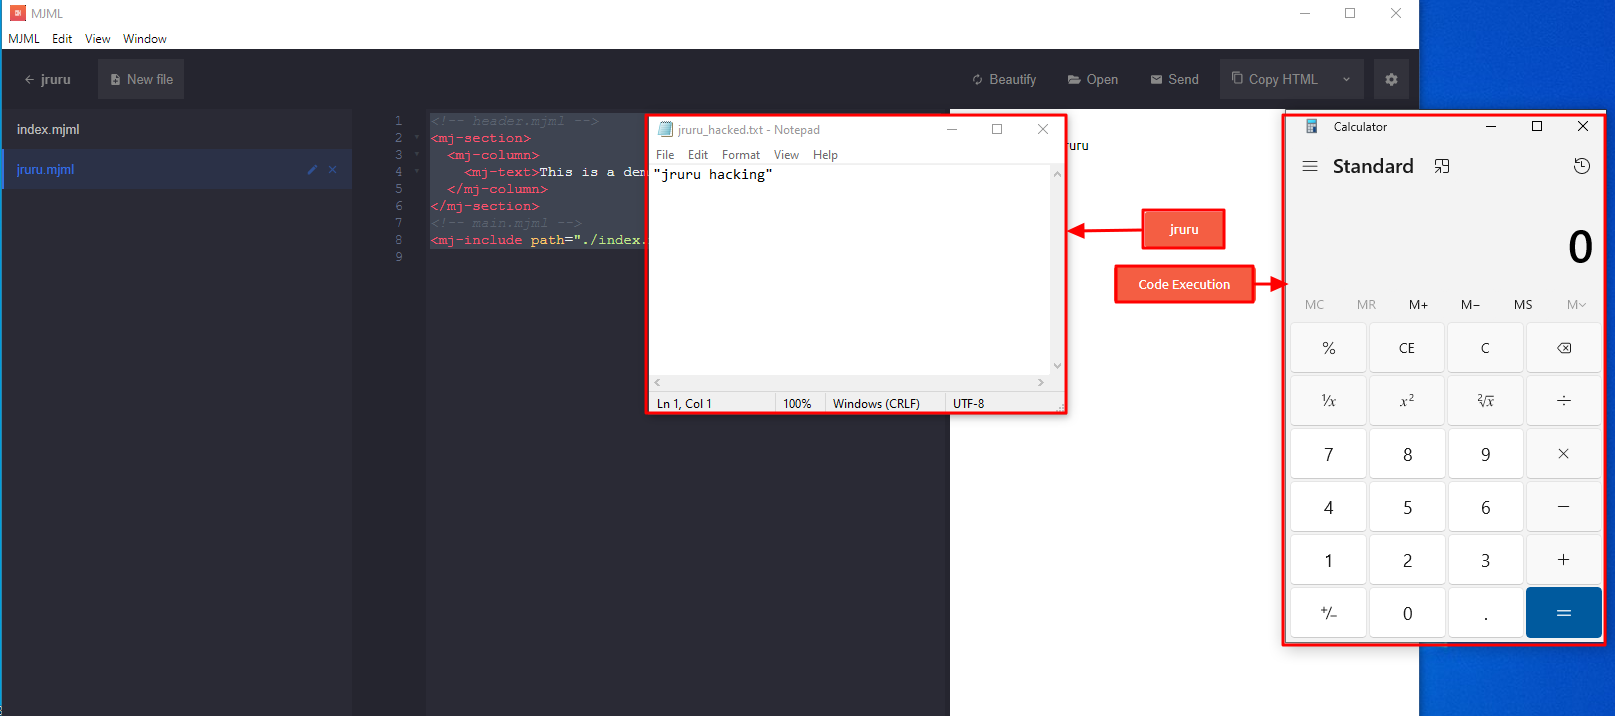 eqstlab/cve-2024-25293
mjml-app v3.0.4 & 3.1.0-beta RCE exploit
 tpdlshdmlrkfmcla/2023-2245
cve-2023-2245
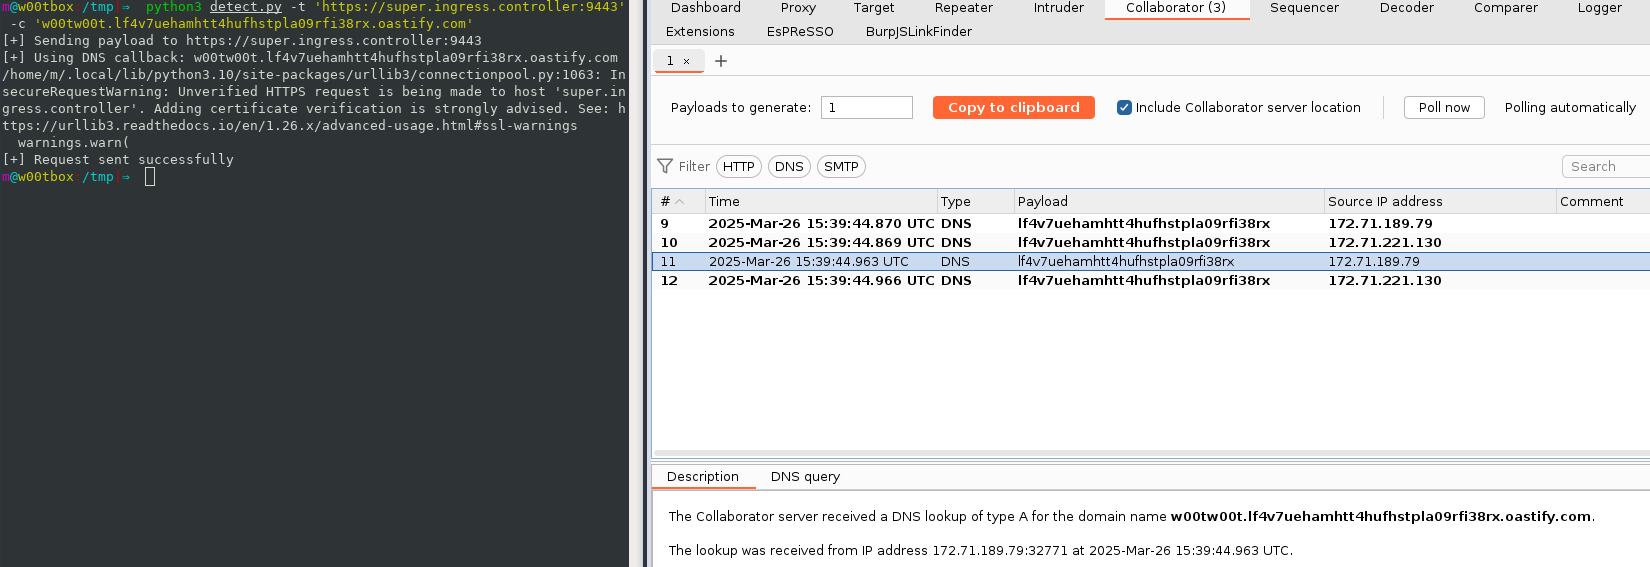 m-q-t/ingressnightmare-detection-poc
Proof-of-Concept Tool to detect IngressNightmare (CVE-2025-1974) via (non-intrusive) active means.
 afine-com/cve-2024-5737
AdmirorFrames Joomla! Extension < 5.0 - HTML Injection
 randomrobbiebf/cve-2024-43919
YARPP <= 5.30.10 - Missing Authorization

 lc/theftfuzzer
TheftFuzzer is a tool that fuzzes Cross-Origin Resource Sharing implementations for common misconfigurations.
 rub-nds/corstest
A simple CORS misconfiguration scanner