
sadcloud
 nccgroup/sadcloud
A tool for standing up (and tearing down!) purposefully insecure cloud infrastructure
cloud-infrastructure-securitycloud-securityeducation+3
7845 years ago
nccgroup/sadcloudA tool for standing up (and tearing down!) purposefully insecure cloud infrastructure
 nagwww/s3-leaks
Curated timeline of AWS S3 bucket misconfigurations, exposed data, and leaked IAM credentials, with incident links for cloud security defenders and…
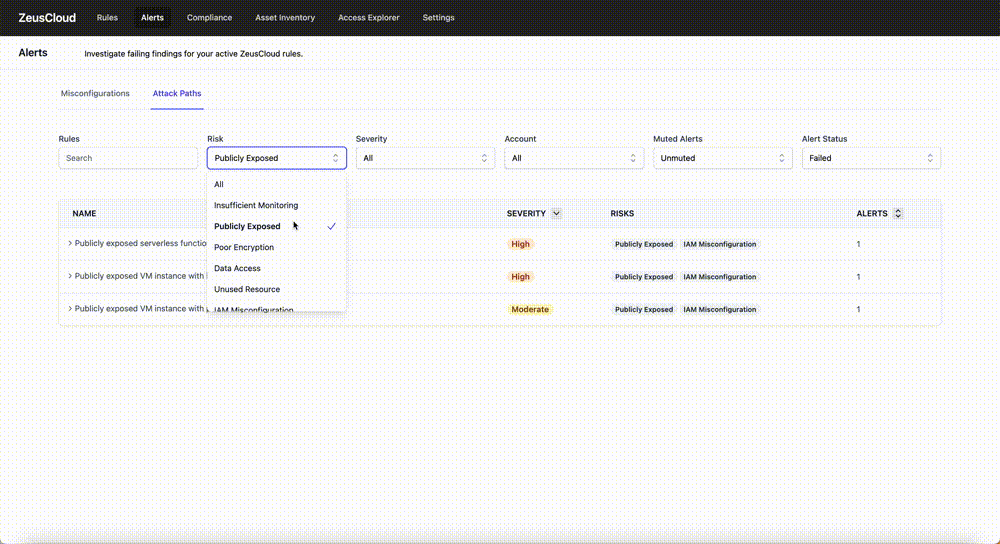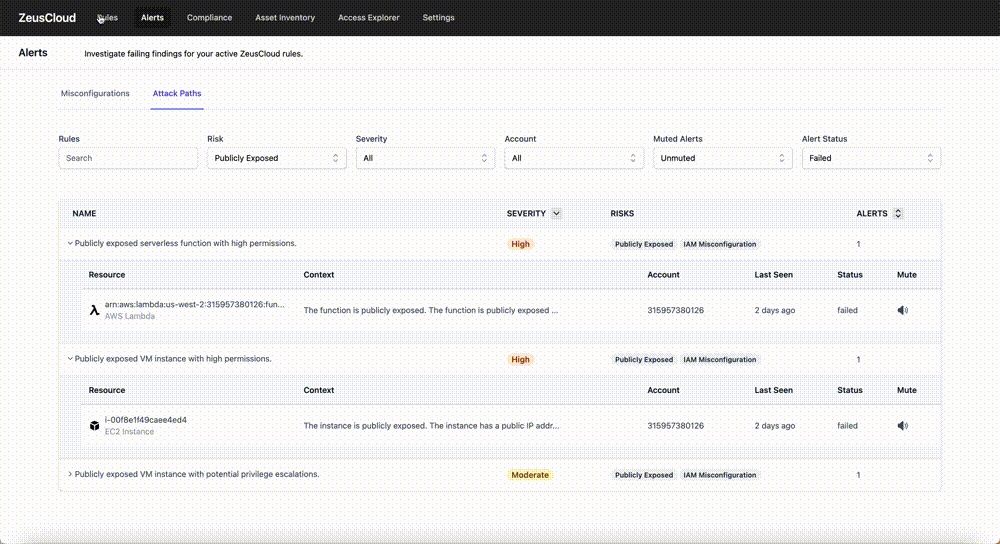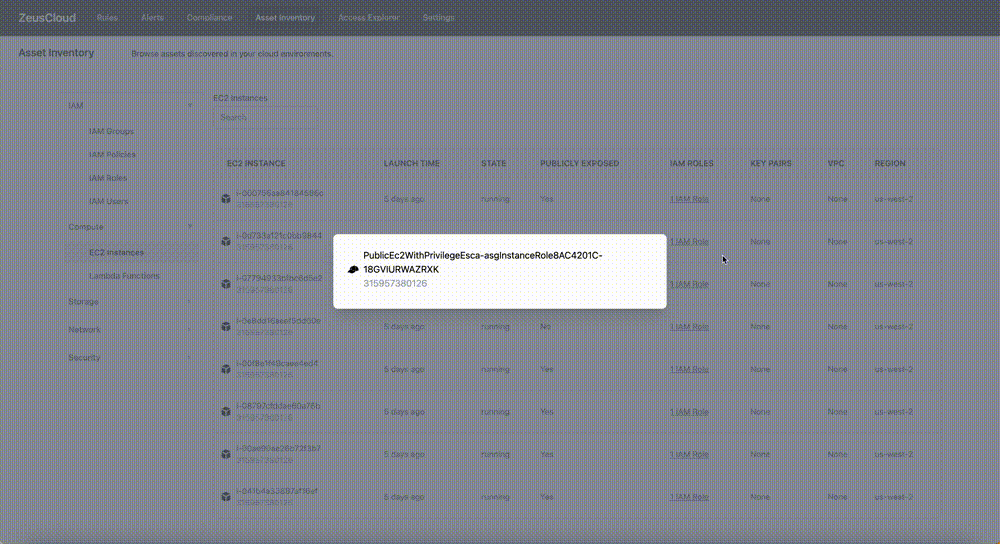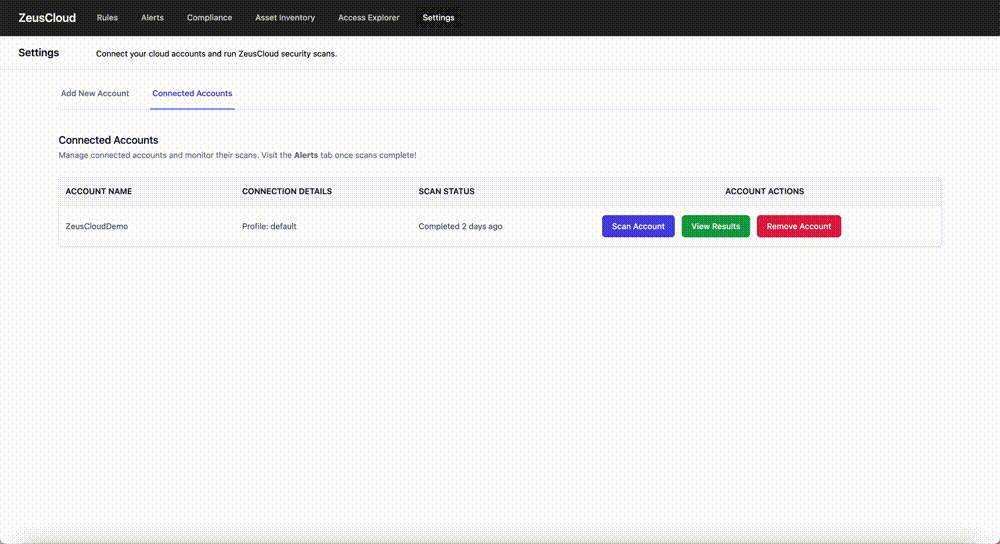 zeus-labs/zeuscloud
Open-source cloud security platform that discovers attack paths, identifies misconfigurations, visualizes IAM access, and provides step-by-step…
 mvelazc0/badzure
BadZure automates the deployment of intentionally misconfigured Entra ID tenants and Azure subscriptions, populating them with diverse entities and…
 shiftleftsecurity/sast-scan
Scan is a free & Open Source DevSecOps tool for performing static analysis based security testing of your applications and its dependencies. CI and…
 adversis/tailsnitch
A security auditor for Tailscale configurations. Scans your tailnet for misconfigurations, overly permissive access controls, and security best…
 kubesphere/kubeeye
Cloud-native Kubernetes cluster inspection tool that detects application misconfigurations, unhealthy components, and node problems using custom OPA,…
 skyscanner/cfripper
Library and CLI tool for analysing CloudFormation templates and check them for security compliance.
 trailofbits/semgrep-rules
Collection of Semgrep rules for static code analysis, detecting security vulnerabilities, and enforcing secure coding practices across multiple…
 nahamsec/hostilesubbruteforcer
Subdomain brute-forcing tool that enumerates existing subdomains and detects misconfigured cloud-hosted subdomains vulnerable to takeover across AWS,…
 legit-labs/legitify
Detect and remediate misconfigurations and security risks across all your GitHub and GitLab assets
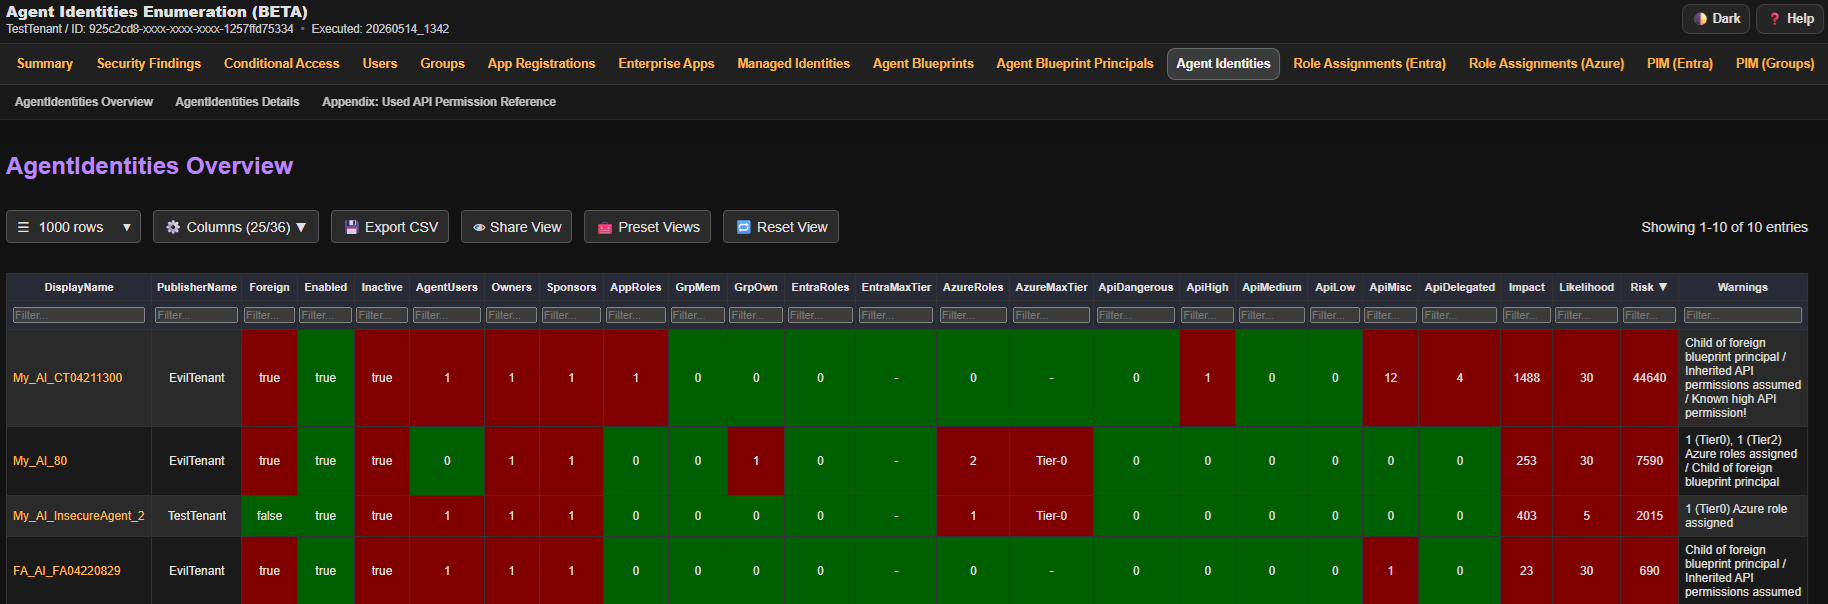 compasssecurity/entrafalcon
A lightweight PowerShell tool for assessing the security posture of Microsoft Entra ID environments. It helps identify privileged objects, risky…
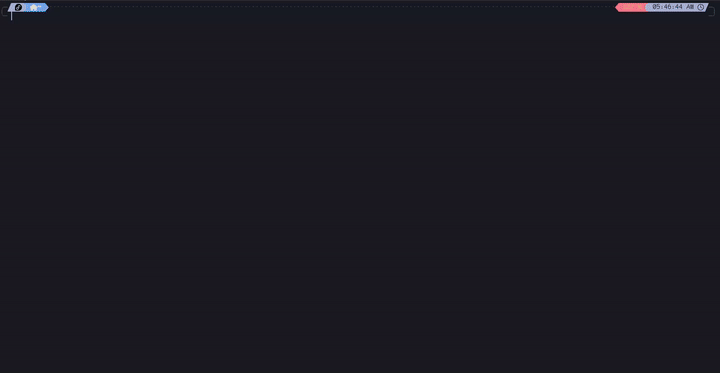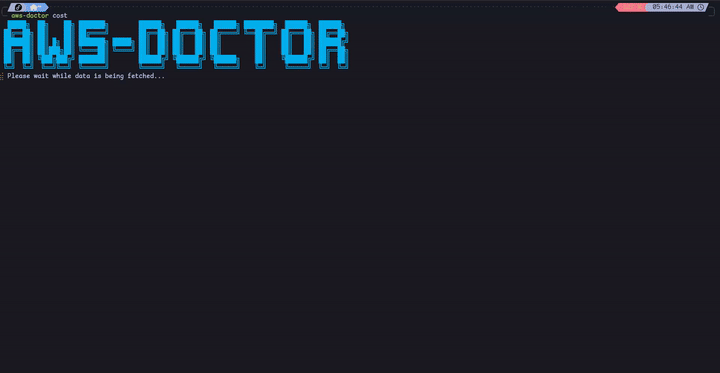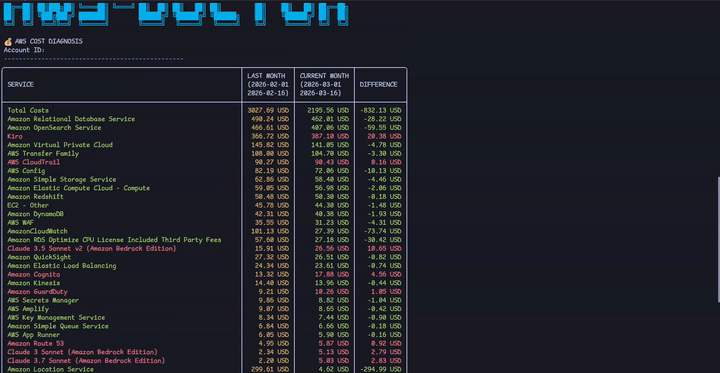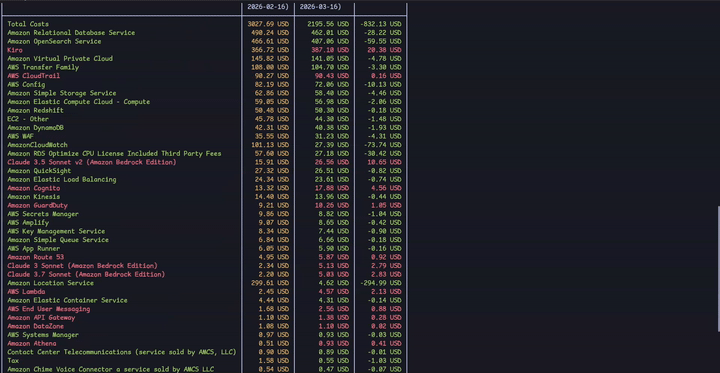 elc0mpa/aws-doctor
Powerful open-source CLI to audit security, costs, and best practices in AWS. 🩺 ☁️
 nccgroup/crosssitecontenthijacking
Content hijacking proof-of-concept using Flash, PDF and Silverlight
 cycodelabs/raven
Scans GitHub Actions CI/CD workflows for security vulnerabilities, indexes findings into a Neo4j graph database, and provides a query library for…
 hxsecurity/terraformgoat
Multi-cloud vulnerable-by-design deployment tool using Terraform to provision intentionally insecure cloud infrastructure for security training and…
 synacktiv/sccmsecrets
SCCMSecrets.py aims at exploiting SCCM policies distribution for credentials harvesting, initial access and lateral movement.
 elttam/semgrep-rules
Static analysis security rules for vulnerability detection and audit-focused code review across Java, Go, Python, C#, Kotlin, PHP, Kubernetes, and…