

CVE-2023-43261
 win3zz/cve-2023-43261
CVE-2023-43261 - Credential Leakage Through Unprotected System Logs and Weak Password Encryption
exploitationiot-securitymisconfiguration+3
57
win3zz/cve-2023-43261CVE-2023-43261 - Credential Leakage Through Unprotected System Logs and Weak Password Encryption
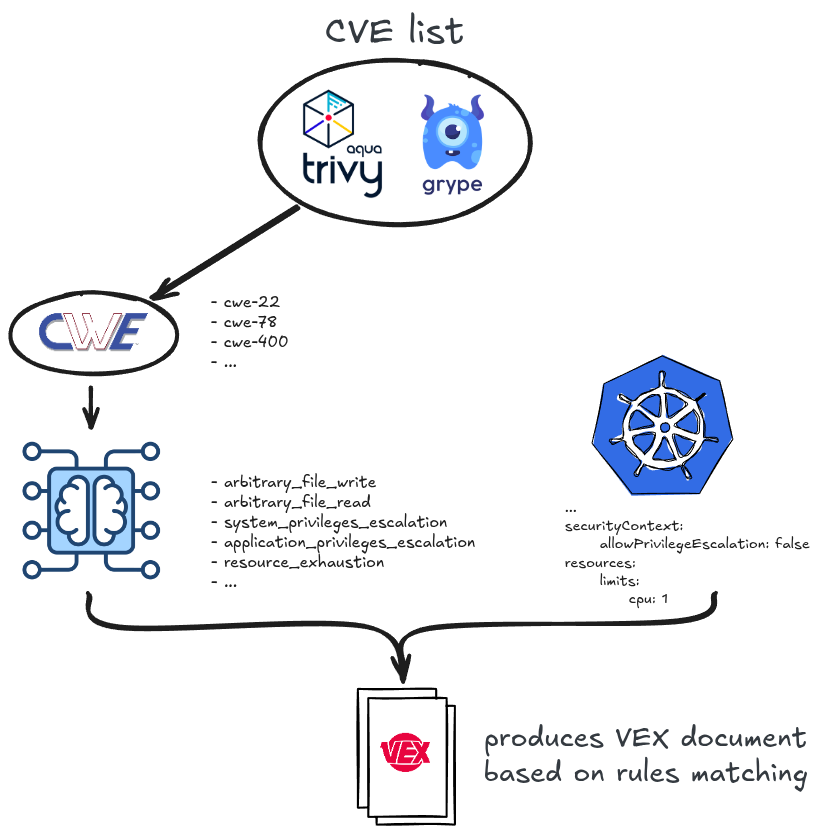 alegrey91/vex8s
Suppress vulnerabilities applying Kubernetes context to scans
 agentsid-dev/agentsid-scanner
Security scanner for MCP servers. Grades auth, permissions, injection risks, and tool safety. The Lighthouse of agent security.
 gensecaihq/cve-2024-3094-vulnerability-checker-fixer
Shell script and Ansible playbook to detect and remediate CVE-2024-3094 in xz-utils by checking package versions, upgrading or downgrading to a…
 jq6l43d1/proxmox-lxc-docker-fix
Workaround for CVE-2025-52881: Fixes Docker/Podman breakage in Proxmox LXC containers caused by AppArmor incompatibility with runc 1.2.7+. Universal…
 joranslingerland/cve-2021-36934
Fix for the CVE-2021-36934
 guettli/fix-cve-2020-15228
Python script that automatically patches GitHub Actions workflow files to replace deprecated and insecure ::set-env and ::add-path commands with the…
 alexandreheroux/fix-cve-2021-44228
Apply class remove process from ear/war/jar/zip archive, see https://logging.apache.org/log4j/2.x/
 bitnesswise/jquery-prototype-pollution-fix
A fix for CVE-2019-11358 (prototype pollution in jquery)
 heroku/heroku-cve-2013-0333
Scans Heroku applications for a critical Rails remote code execution vulnerability (CVE-2013-0333) and identifies unpatched instances requiring…
 teycir/diffcatcher
A Rust CLI tool that recursively discovers Git repositories, captures state changes, generates diffs, extracts code elements with full snippets, and…
 maxwitat/check-aad-connect-for-cve-2021-36949-vulnerability
check if Azure AD Connect is affected by the vulnerability described in CVE-2021-36949
 name/log4j-scanner
Discover Log4Shell vulnerability [CVE-2021-44832]
 spring-io/cve-2022-22976-bcrypt-skips-salt
CLI tool to detect and update BCrypt password hashes with vulnerable work factor 31, integrating with Spring Security databases for CVE-2022-xxxx…
 josephgodwinkimani/cloudpanel-2.4.2-cve-2024-44765-recovery
How to "recover" a CloudPanel server affected by the CVE-2024-44765 vulnerability
 galacticquest/cve-2024-3094-detect
Bash script to detect vulnerable XZ Utils versions (CVE-2024-3094) and downgrade to a safe release, supporting multiple Linux distributions and…
 atlassian/git-secrets-scan
Scans Git repositories for hardcoded secrets, keys, and passwords using Gitleaks, integrating security into Bitbucket Pipelines with Code Insights…
 shoucheng3/alibaba__nacos_cve-2021-44667_2-0-3
Exploit for CVE-2021-44667 targeting Alibaba Nacos 2.0.3, enabling unauthenticated remote code execution via a crafted request to the Derby database…