
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
66 results
CVE-2018-16373 preview

CVE-2018-16373

GitHubsnappyjack/cve-2018-16373

Frog CMS 0.9.5 has an Upload > vulnerability that can create files via > /admin/?/plugin/file_manager/save
exploitationmisconfigurationpenetration-testing+2
8 years ago
CVE-2025-46078 preview

CVE-2025-46078

GitHubyggcwhat/cve-2025-46078

Vulnerability Description
code-analysisexploitationmisconfiguration+3
1 year ago
2023-2245 preview

2023-2245

GitHubtpdlshdmlrkfmcla/2023-2245

cve-2023-2245
exploitationmisconfigurationvulnerability-analysis+2
1 year ago
CVE-2017-9798 preview
Archived

CVE-2017-9798

GitHubnitrado/cve-2017-9798

Checks a shared hosting environment for CVE-2017-9798
misconfigurationscripting-automationvulnerability-analysis+1
38 years ago
CVE-2025-9074 preview

CVE-2025-9074

GitHubzenzue/cve-2025-9074

Proof-of-concept exploit for CVE-2025-9074 demonstrating container-to-host file write via exposed Docker Engine API on Windows. For authorized…
cloud-securitycontainer-escapecontainer-security+6
101 year ago
CVE-NetScalerFileSystemCheck preview

CVE-NetScalerFileSystemCheck

GitHubdanielwep/cve-netscalerfilesystemcheck

This script checks the Citrix Netscaler if it has been compromised by CVE-2019-19781 attacks and collects all file system information

digital-forensicsforensicsincident-response+3
25 years ago
ai-ide-config-guard preview

ai-ide-config-guard

GitHubtrerb/ai-ide-config-guard

Scan a repo for AI-IDE config files that can trigger RCE via Claude Code hooks, Cursor rules, MCP auto-registration. Detects CVE-2025-59536,…
code-analysiseducationmisconfiguration+4
4 months ago
CVE-2024-57484 preview

CVE-2024-57484

GitHubyogeswaran6383/cve-2024-57484

Proof-of-concept for CVE-2024-57484: directory listing vulnerability in FoxyProxy extension exposing internal file structure and metadata, enabling…
information-gatheringmisconfigurationvulnerability-analysis+1
1 year ago
CVE-2023-47668 preview

CVE-2023-47668

GitHubrandomrobbiebf/cve-2023-47668

Restrict Content <= 3.2.7 - Information Exposure via legacy log file

information-gatheringlog-analysismisconfiguration+2
2 years ago
s3reverse preview

s3reverse

GitHubhahwul/s3reverse

The format of various s3 buckets is convert in one format. for bugbounty and security testing.
cloud-securityinformation-gatheringmisconfiguration+1
913 years ago
vibegate preview

vibegate

GitHubthemiddleblue/vibegate

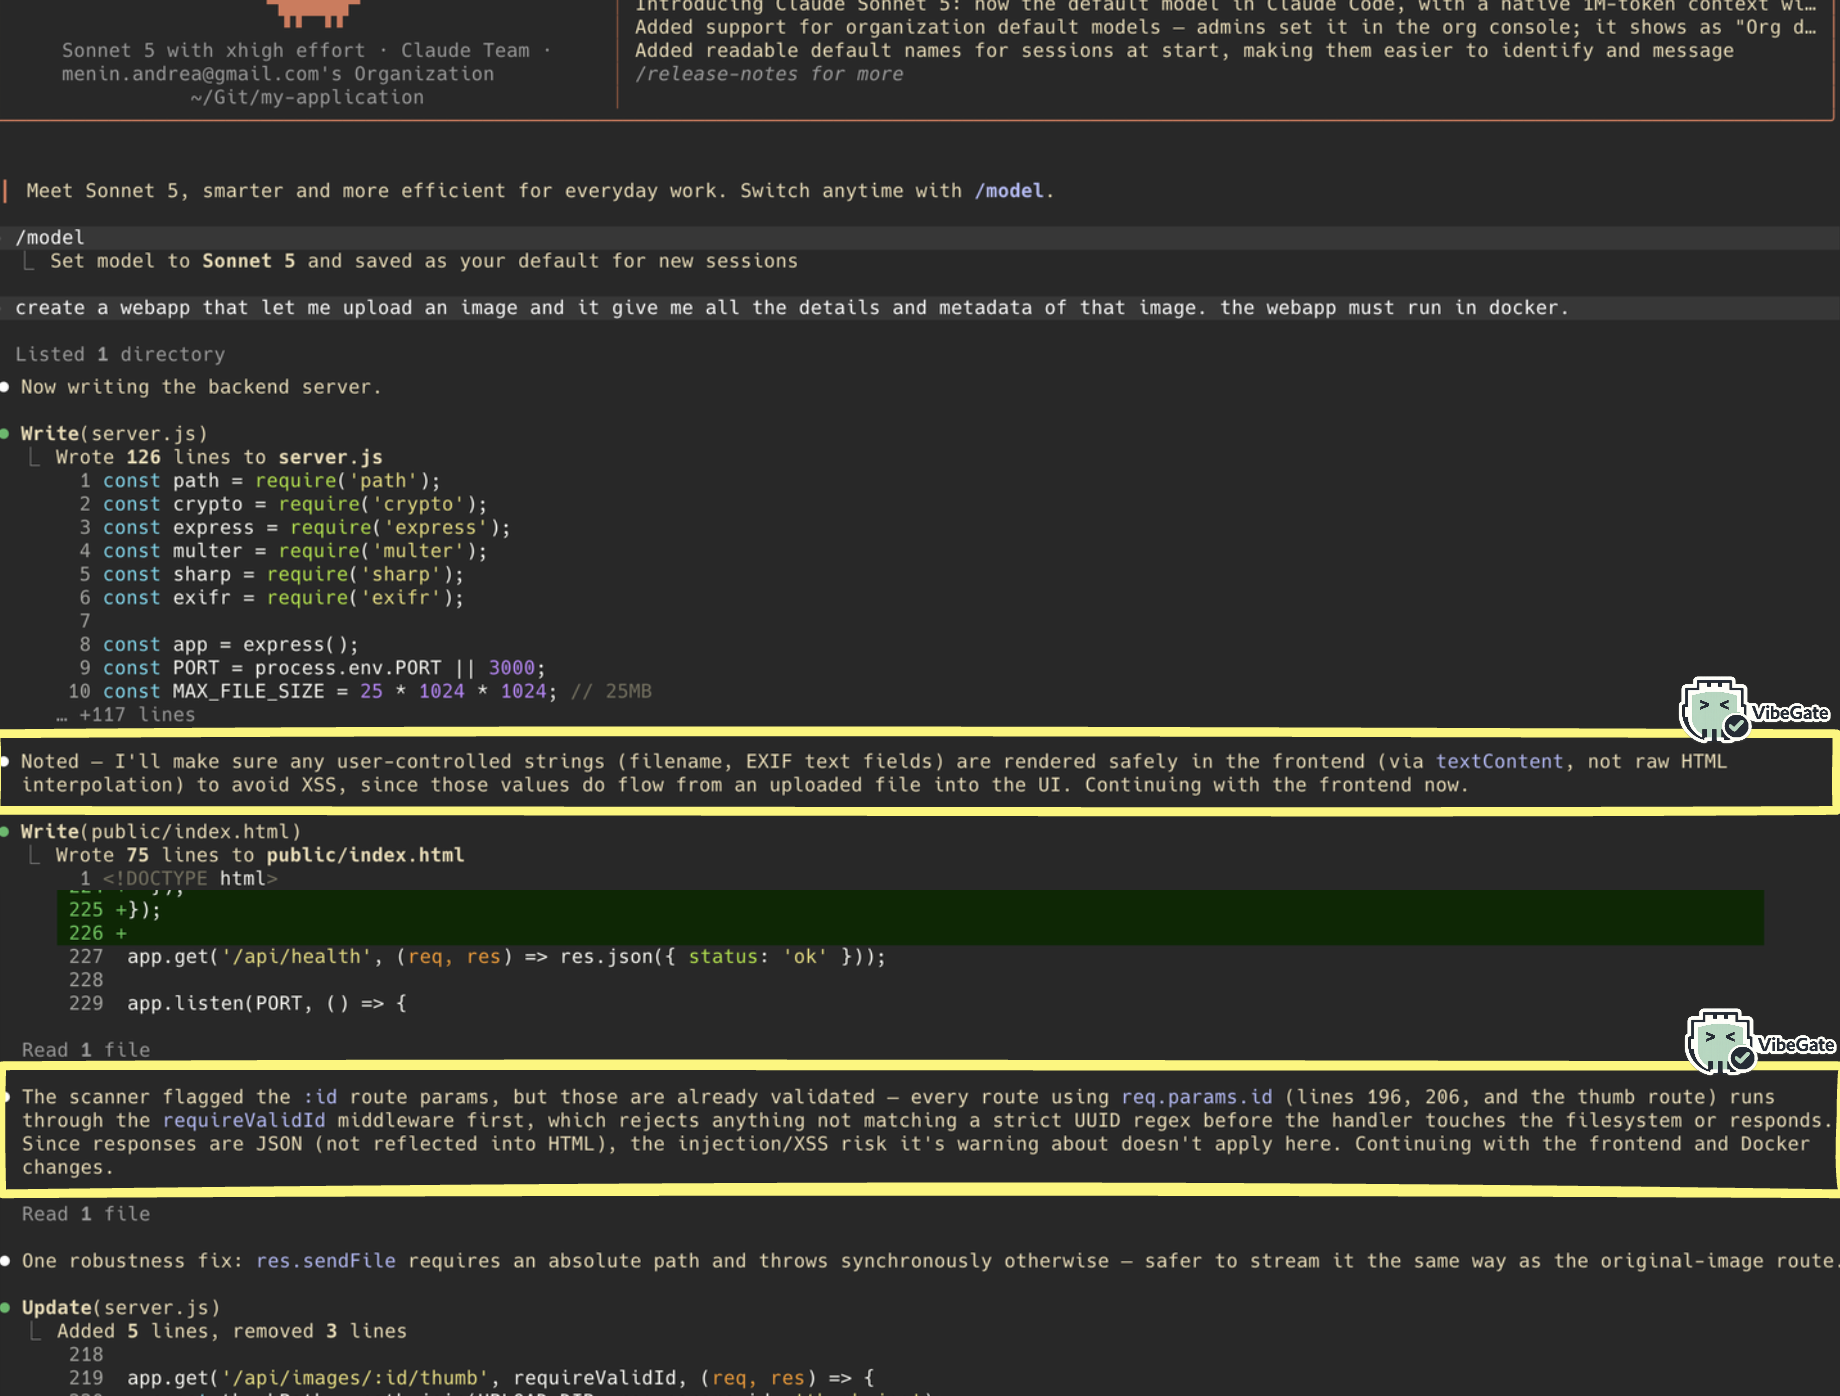
Host-agnostic pre-write security hook for coding agent: detects user-input patterns via Semgrep and emits deterministic, no-LLM security guidance.
ai-securitycode-analysisdevsecops+5
82 months ago
CVE-2024-10449-patch preview

CVE-2024-10449-patch

GitHubg-u-i-d/cve-2024-10449-patch

Patch for CVE-2024-10449: replaces vulnerable loginAction.php with a hardened version that requires database configuration for secure authentication.

authenticationcode-analysismisconfiguration+2
1 year ago
Previous1234Next