Penetration-Testing-Assessment-23-04-2026

Penetration testing assessment of a vulnerable IIS 6.0 WebDAV server, demonstrating reconnaissance, enumeration, exploitation (CVE-2017-7269), and…

Penetration testing assessment of a vulnerable IIS 6.0 WebDAV server, demonstrating reconnaissance, enumeration, exploitation (CVE-2017-7269), and…

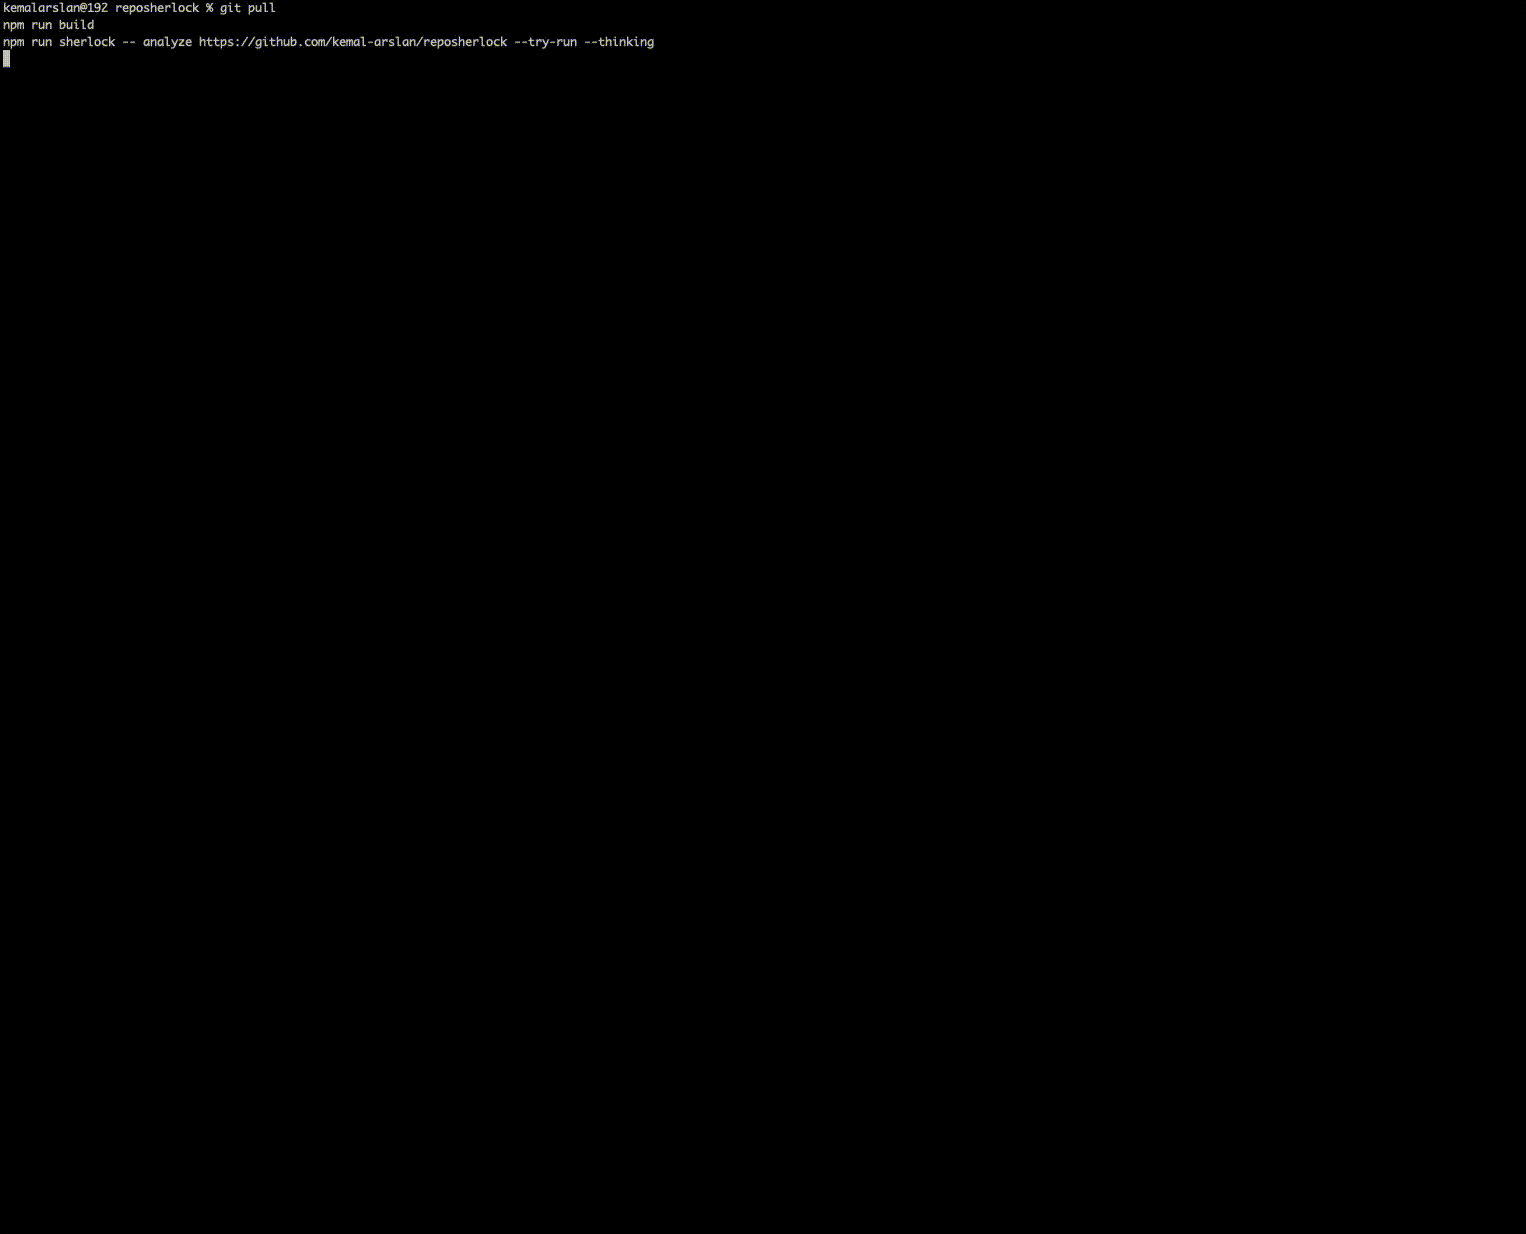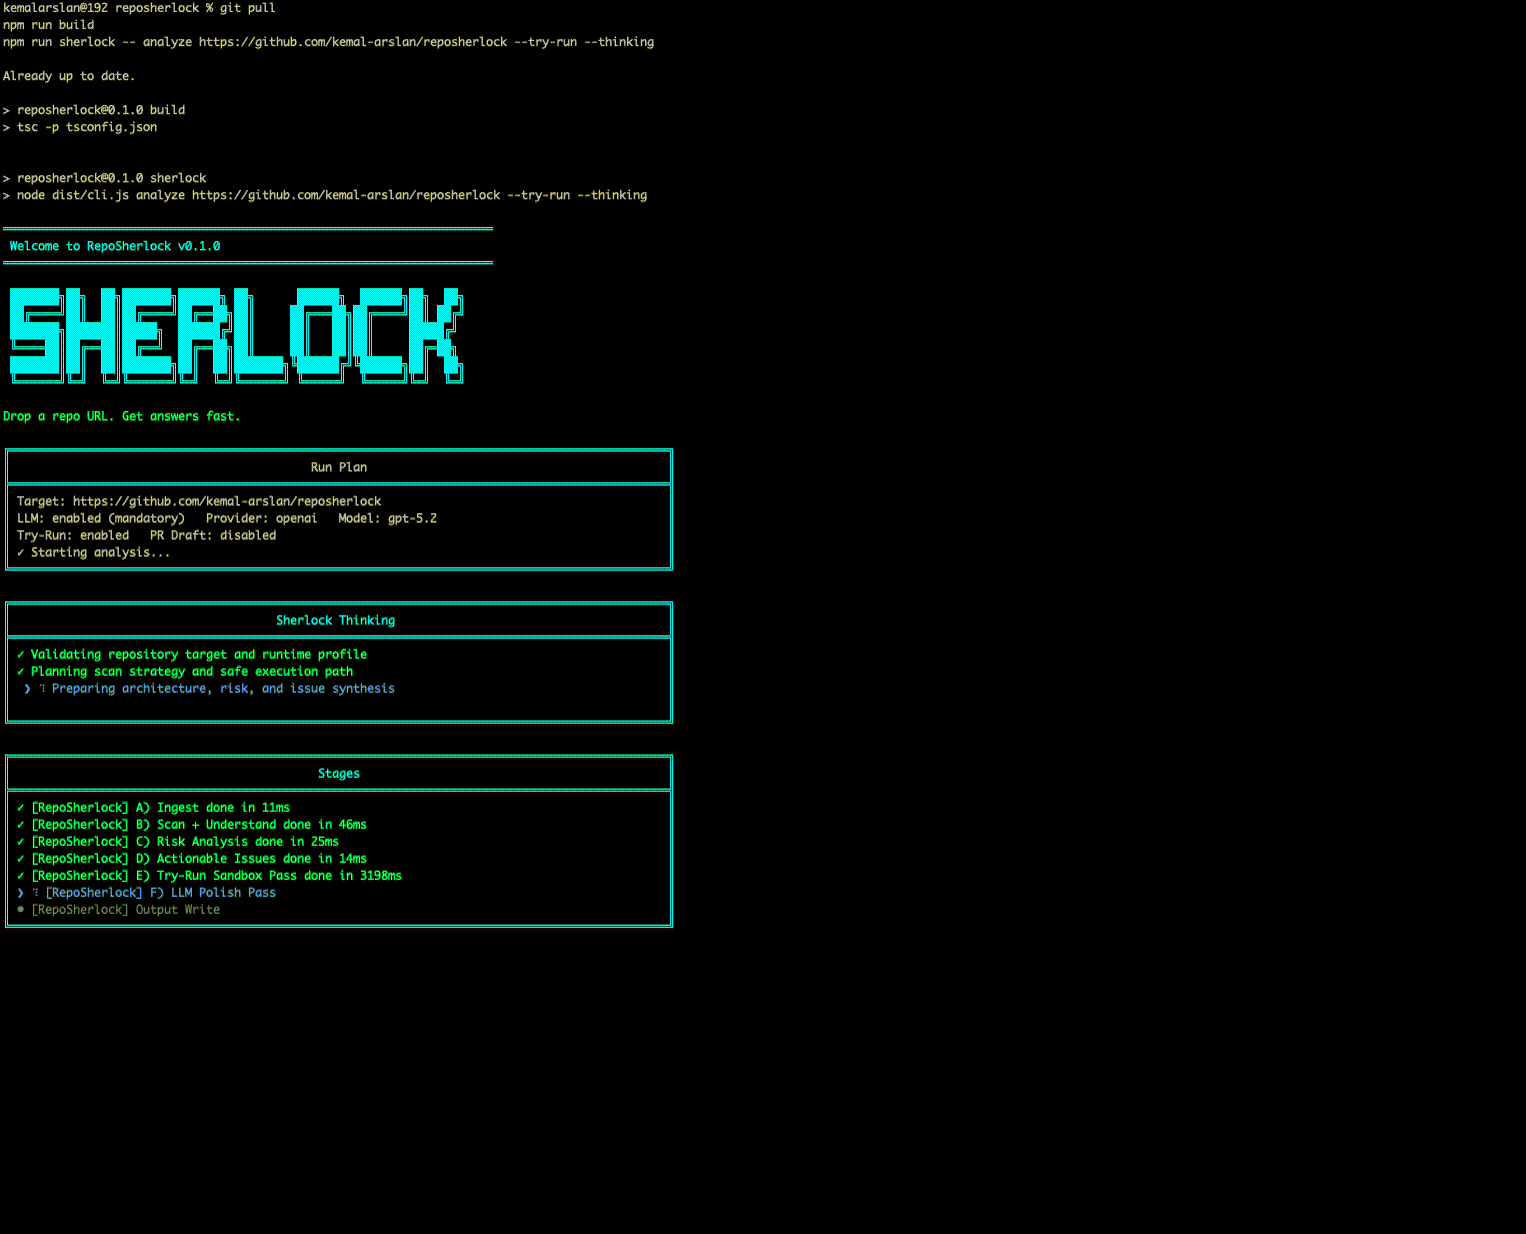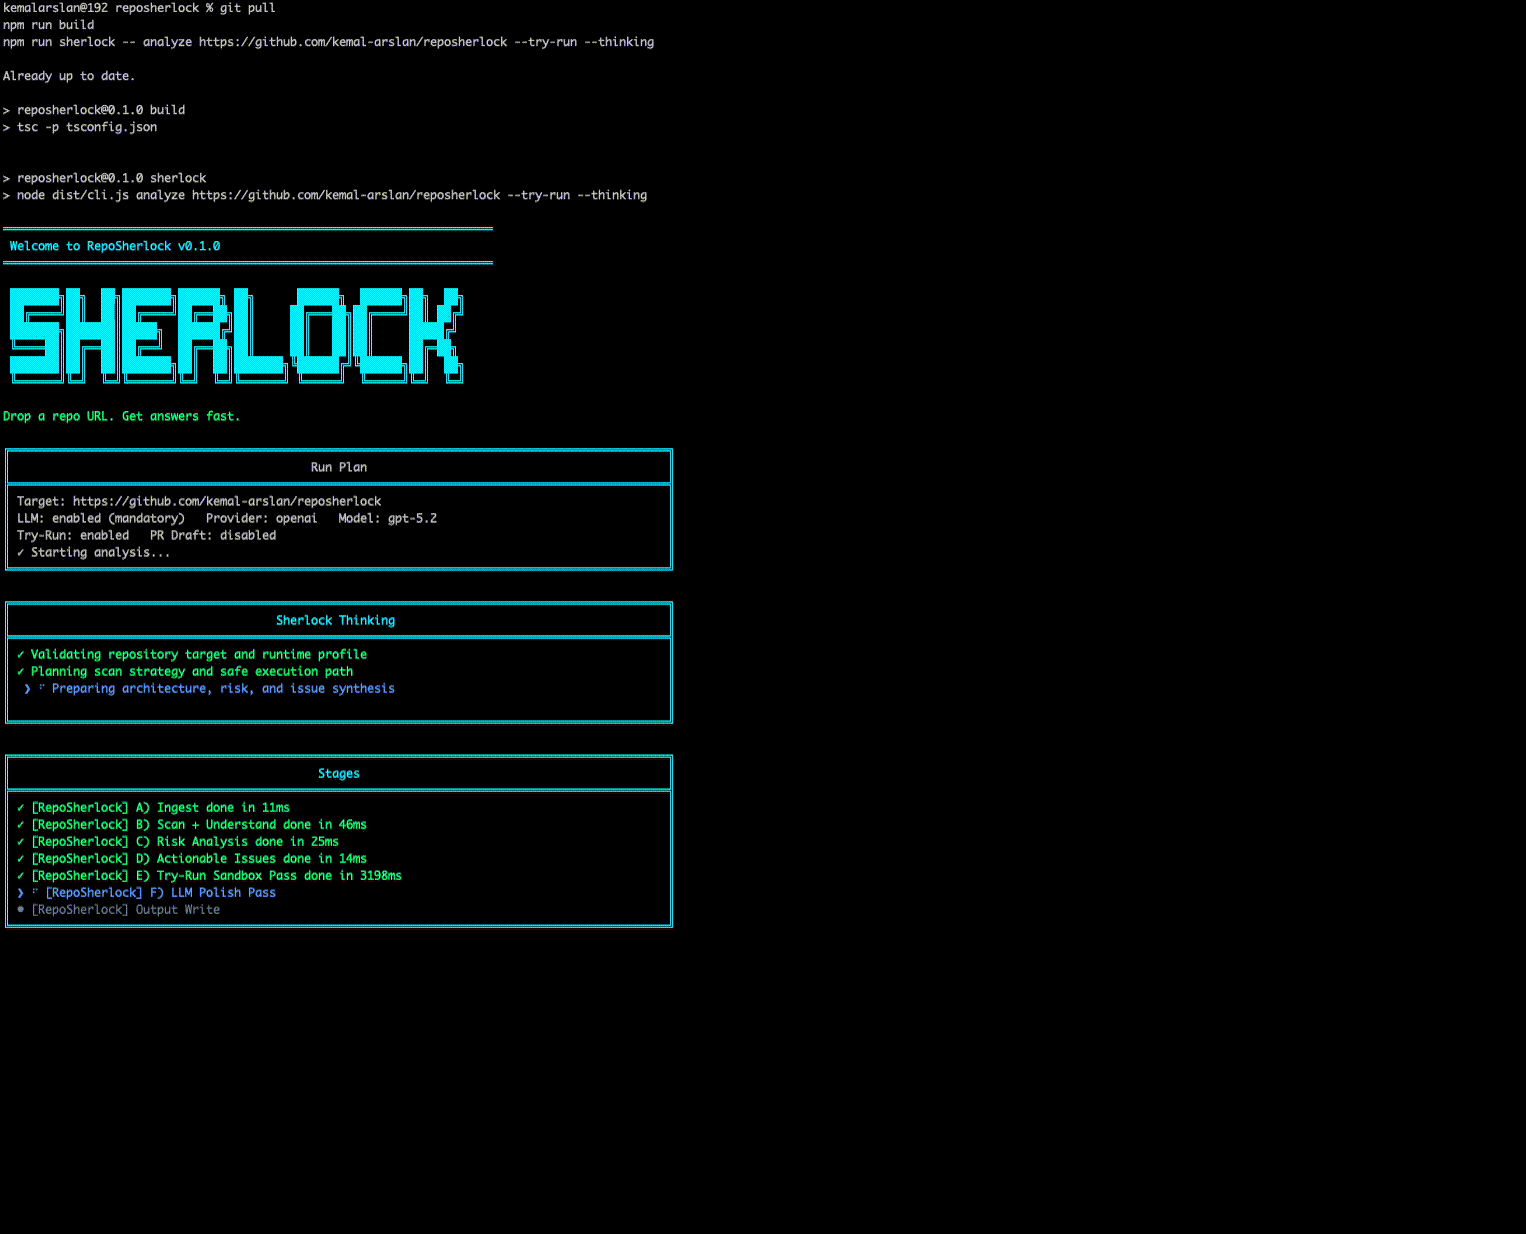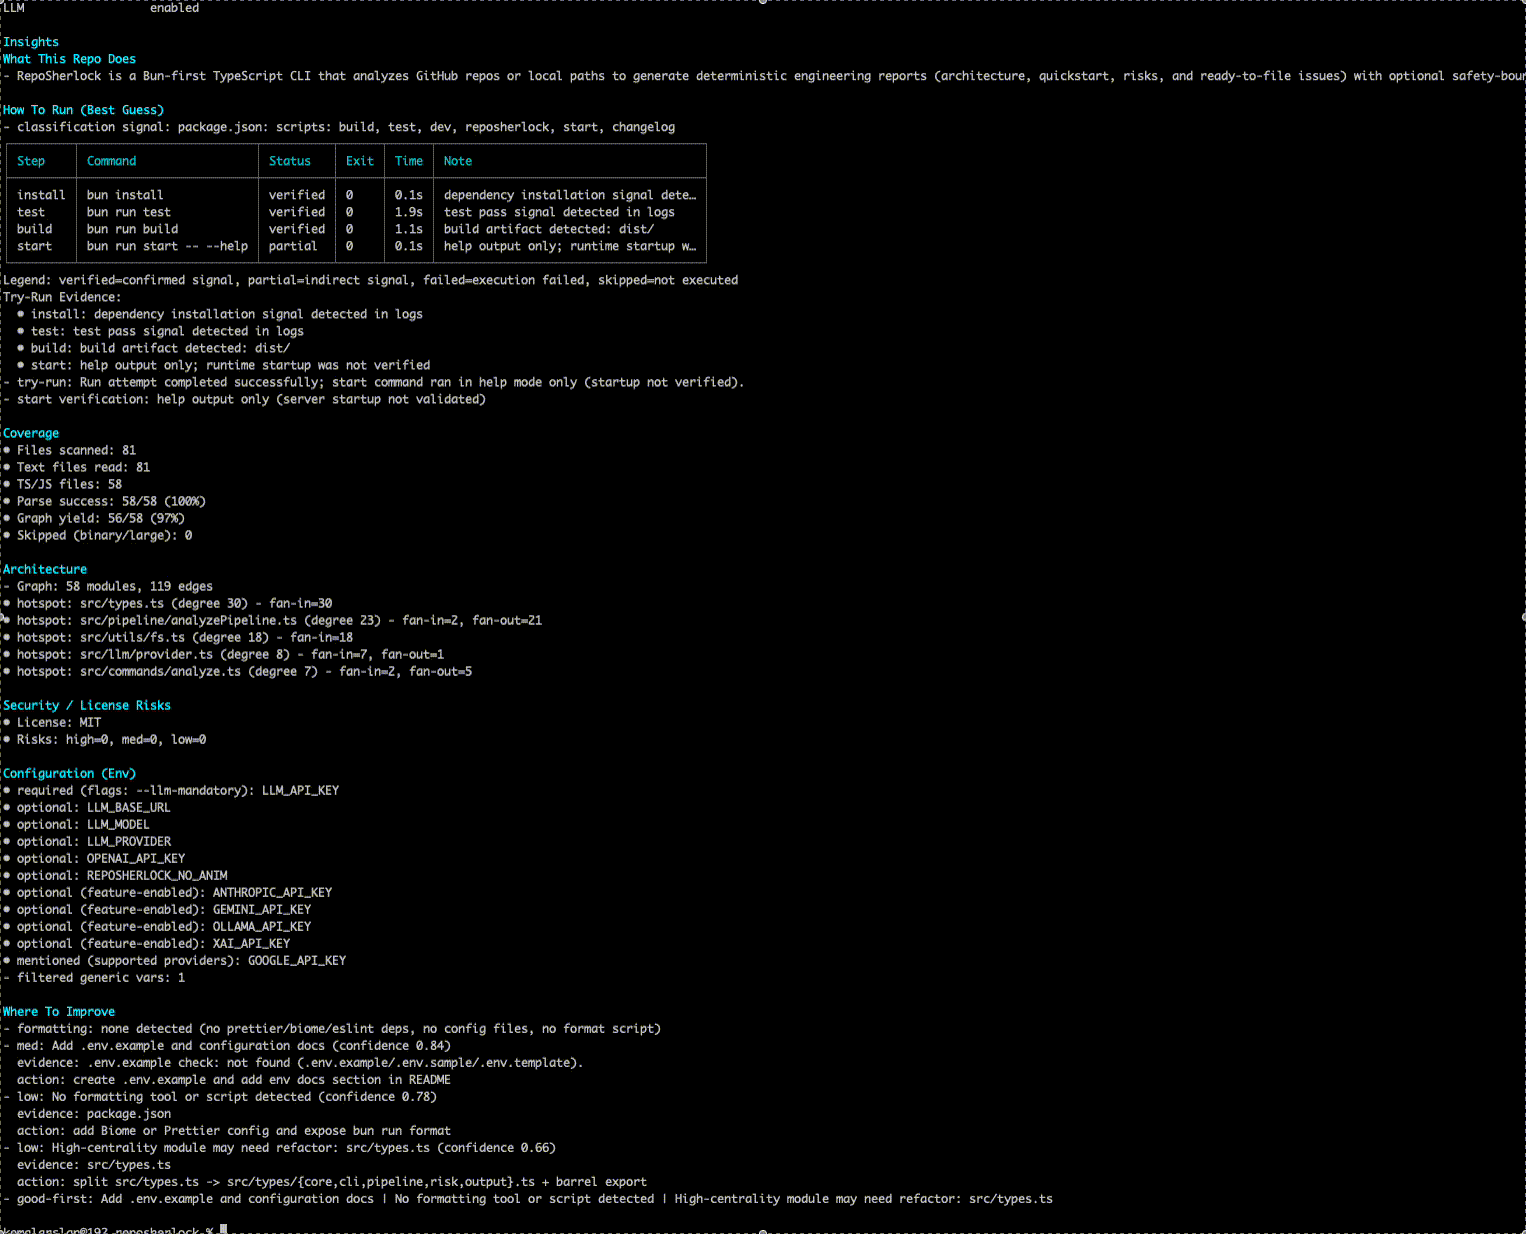
Analyze any GitHub repo (URL or local path) → architecture map, verified run commands, risks, and actionable issues - in minutes.

OPA Gatekeeper-based policy templates to mitigate CVE-2020-8554 by restricting Kubernetes Service external IPs to an allow list, preventing traffic…

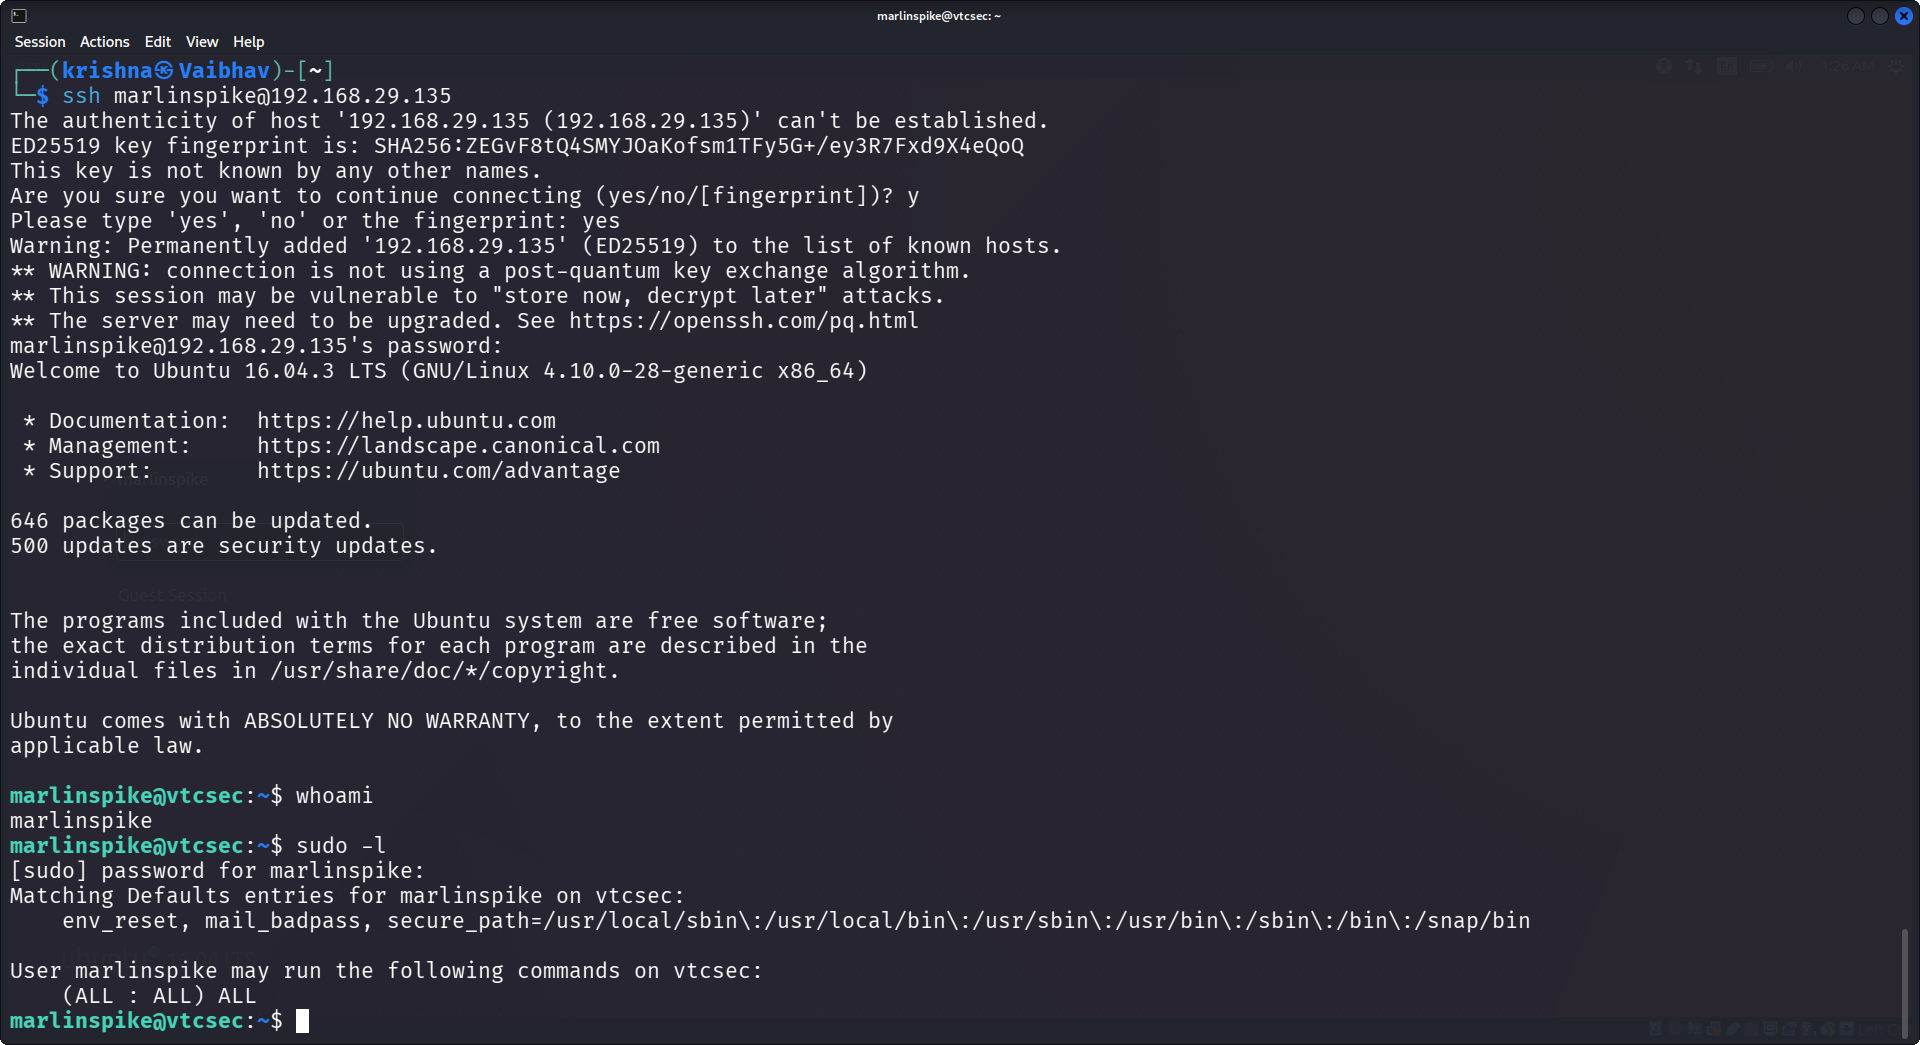
Full penetration testing workflow: credential brute force, SSH access and privilege escalation (CVE-2021-4034)

Runtime patches for algertc/alpr-dashboard: async logger fix and CVE-2025-29927 nginx mitigation

simple application with a CVE-2022-45688 vulnerability

SyncShield - Browser Extension to Detect Unsafe Rsync Commands (CVE-2018-5764)

Public Disclosure

Controlled penetration testing lab demonstrating CVE-2011-2523 exploitation and mitigation techniques.

Cybersecurity lab demonstrating Apache CVE-2021-41773 path traversal vulnerability with vulnerable server simulation, scanner, and security reporting.

Proof-of-Concept (POC) of a simple firewall in Python designed to mitigate the Spring4Shell (CVE-2022-22965) RCE attack by inspecting and blocking…

Exploit for CVE-2021-44667 targeting Alibaba Nacos 2.0.3, enabling unauthenticated remote code execution via a crafted request to the Derby database…

Secure-by-default demo lab showing how container hardening (distroless images, non-root, read-only filesystem, runtime-injected secrets) can…


This powershell script is intended to be used by anyone looking to remediate the Log4j Vulnerability within their environment. It can target multiple…

general purpose workaround for the log4j CVE-2021-44228 vulnerability

Educational lab demonstrating detection and mitigation of CVE-2023-32243 privilege escalation in WordPress Essential Addons for Elementor, using…

simple application with a (unreachable!) CVE-2022-45688 vulnerability