

trivy
 aquasecurity/trivy
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
cloud-infrastructure-securitycloud-securitycode-analysis+14
37.4k
aquasecurity/trivyFind vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
 cisofy/lynis
Agentless security auditing tool for Linux, macOS, and UNIX systems. Performs in-depth scans for vulnerabilities, configuration issues, and…
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 bunkerity/bunkerweb
🛡️ Open-source and cloud-native Web Application Firewall (WAF)
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
 coreruleset/coreruleset
Generic attack detection rule set for web application firewalls, protecting against OWASP Top Ten and common vulnerabilities with minimal false…
 fairwindsops/polaris
Validation of best practices in your Kubernetes clusters
 voorivex/pentest-guide
Penetration tests guide based on OWASP including test cases, resources and examples.
 aquasecurity/kube-hunter
Hunt for security weaknesses in Kubernetes clusters
 proviesec/google-dorks
Useful Google Dorks for WebSecurity and Bug Bounty
 christophetd/cloudflair
🔎 Find origin servers of websites behind CloudFlare by using Internet-wide scan data from Censys.
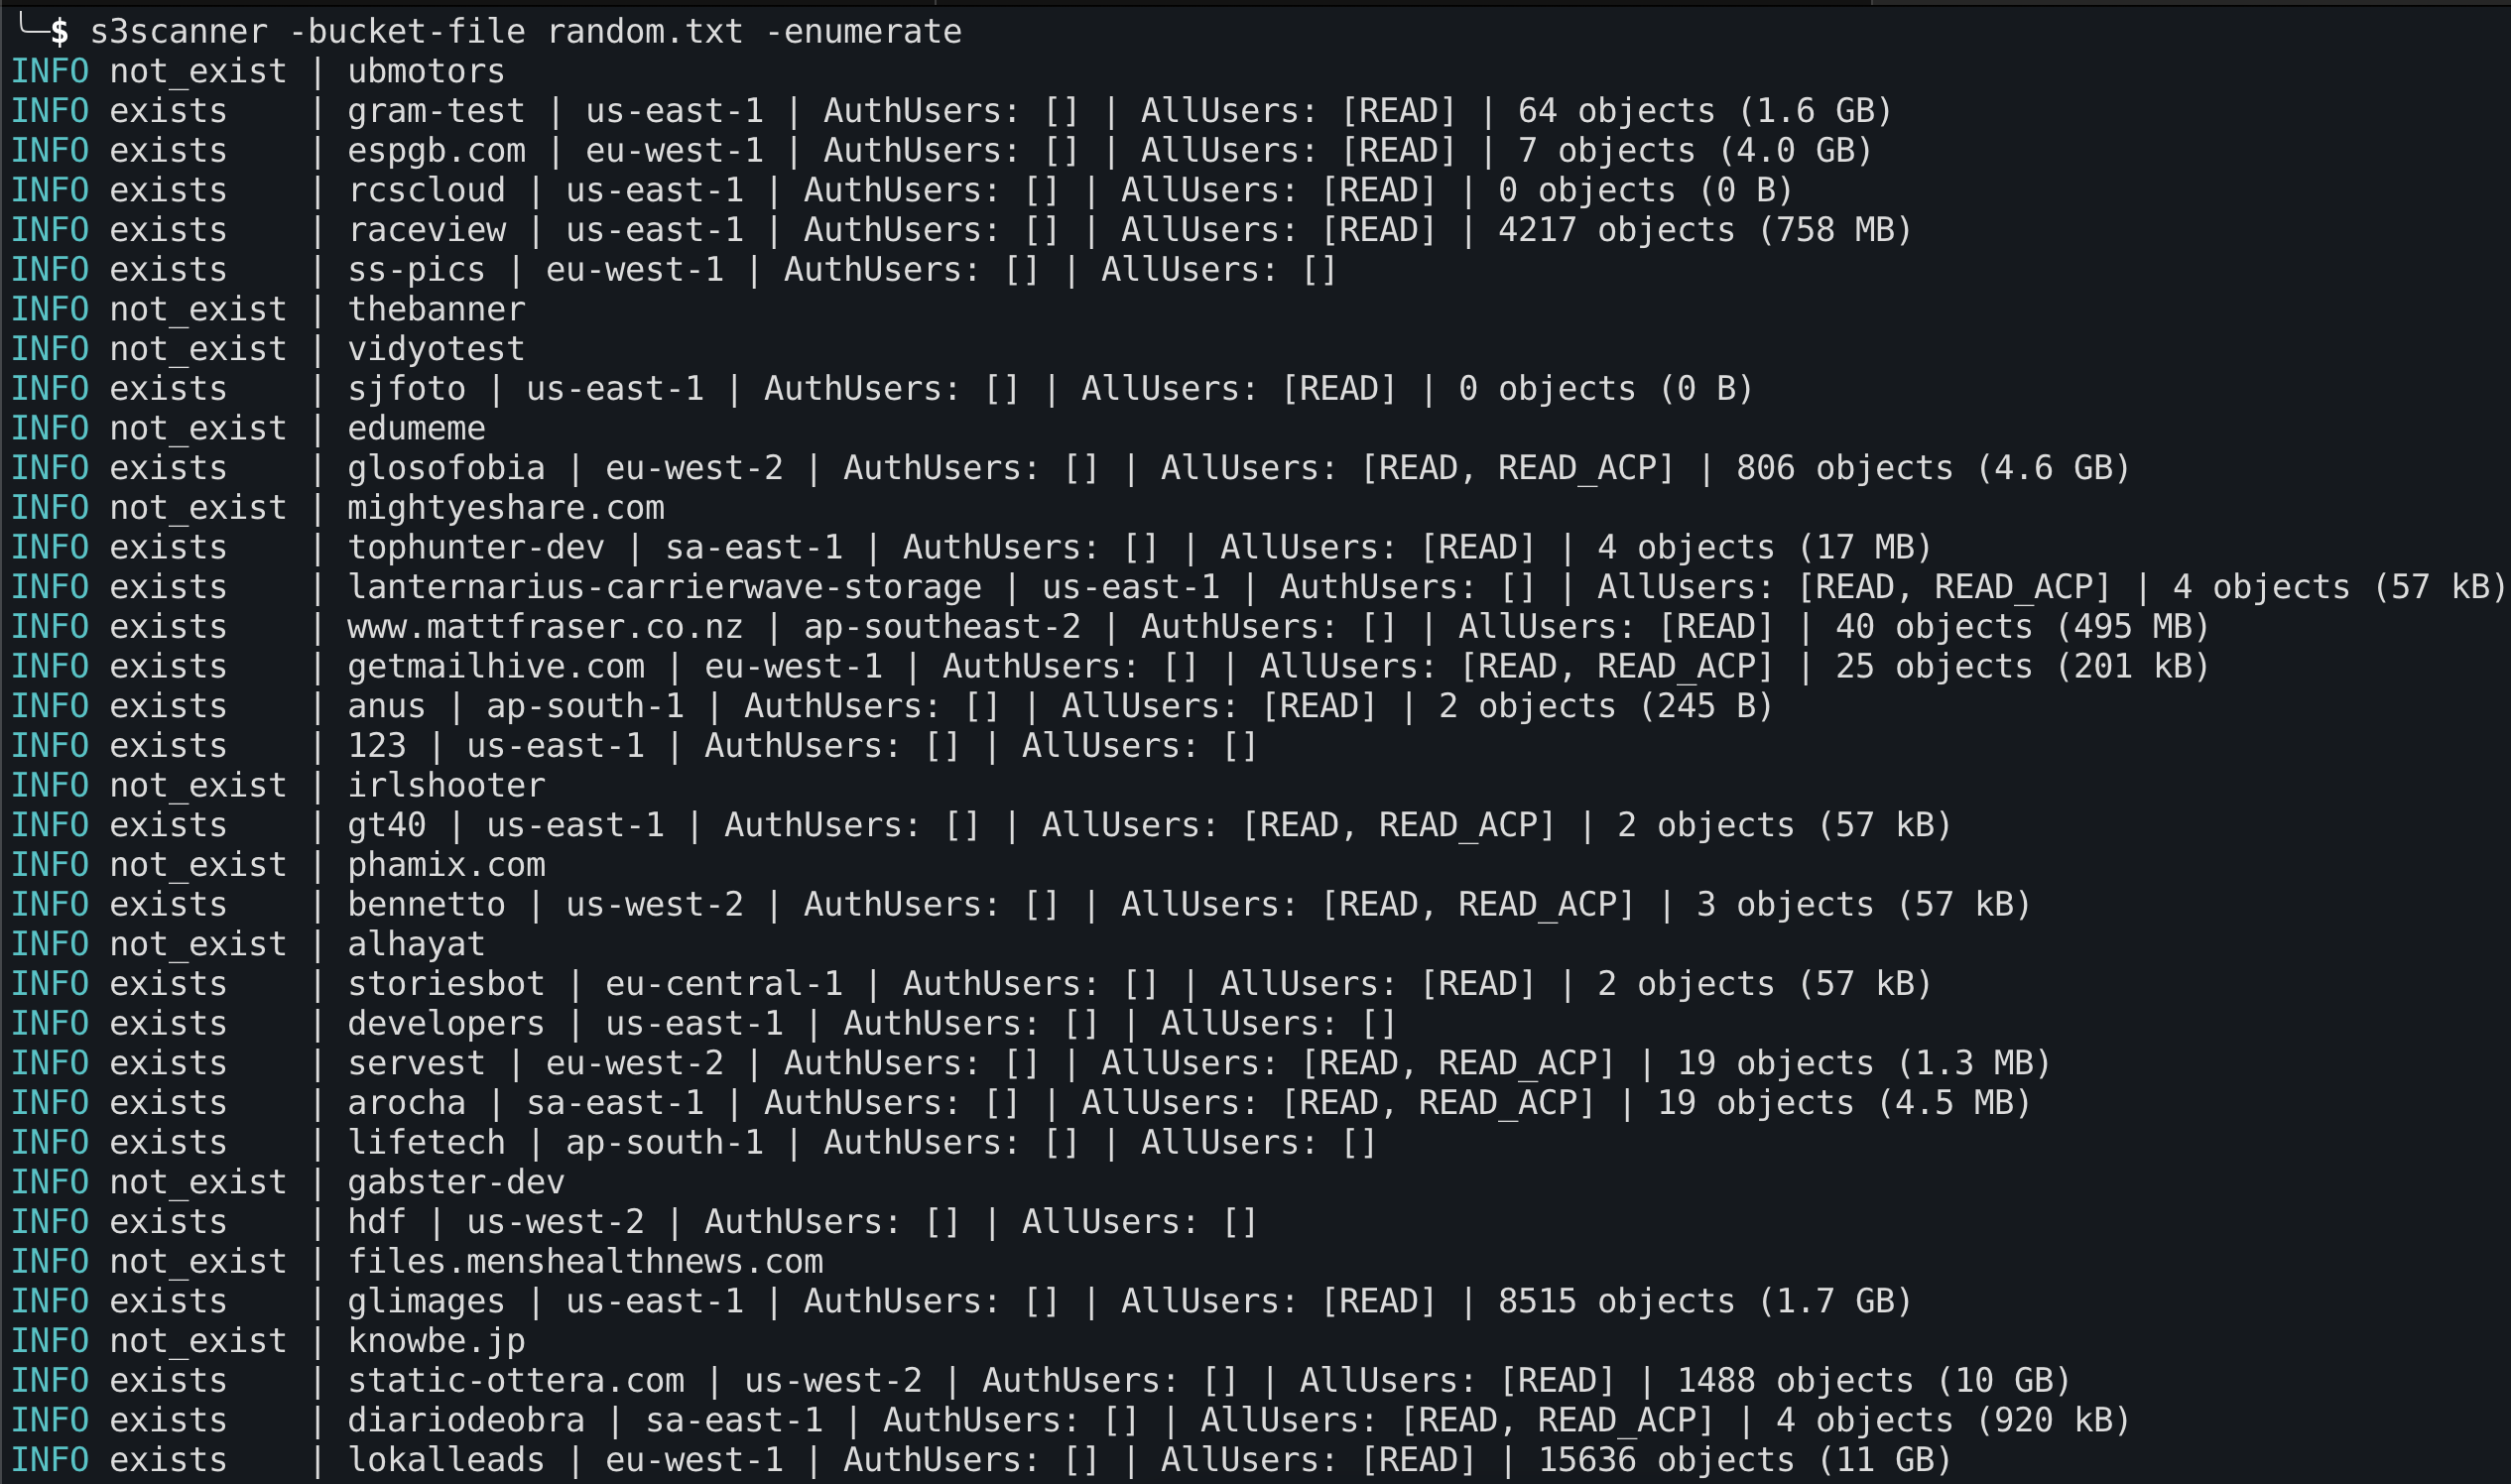 sa7mon/s3scanner
Scan for misconfigured S3 buckets across S3-compatible APIs!
 subat0mik/misconfiguration-manager
Misconfiguration Manager is a central knowledge base for all known Microsoft Configuration Manager tradecraft and associated defensive and hardening…
 sleventyeleven/linuxprivchecker
Local Linux enumeration script that identifies privilege escalation vectors including misconfigurations, world-writable files, clear-text passwords,…
 alessandroz/beroot
Privilege Escalation Project - Windows / Linux / Mac
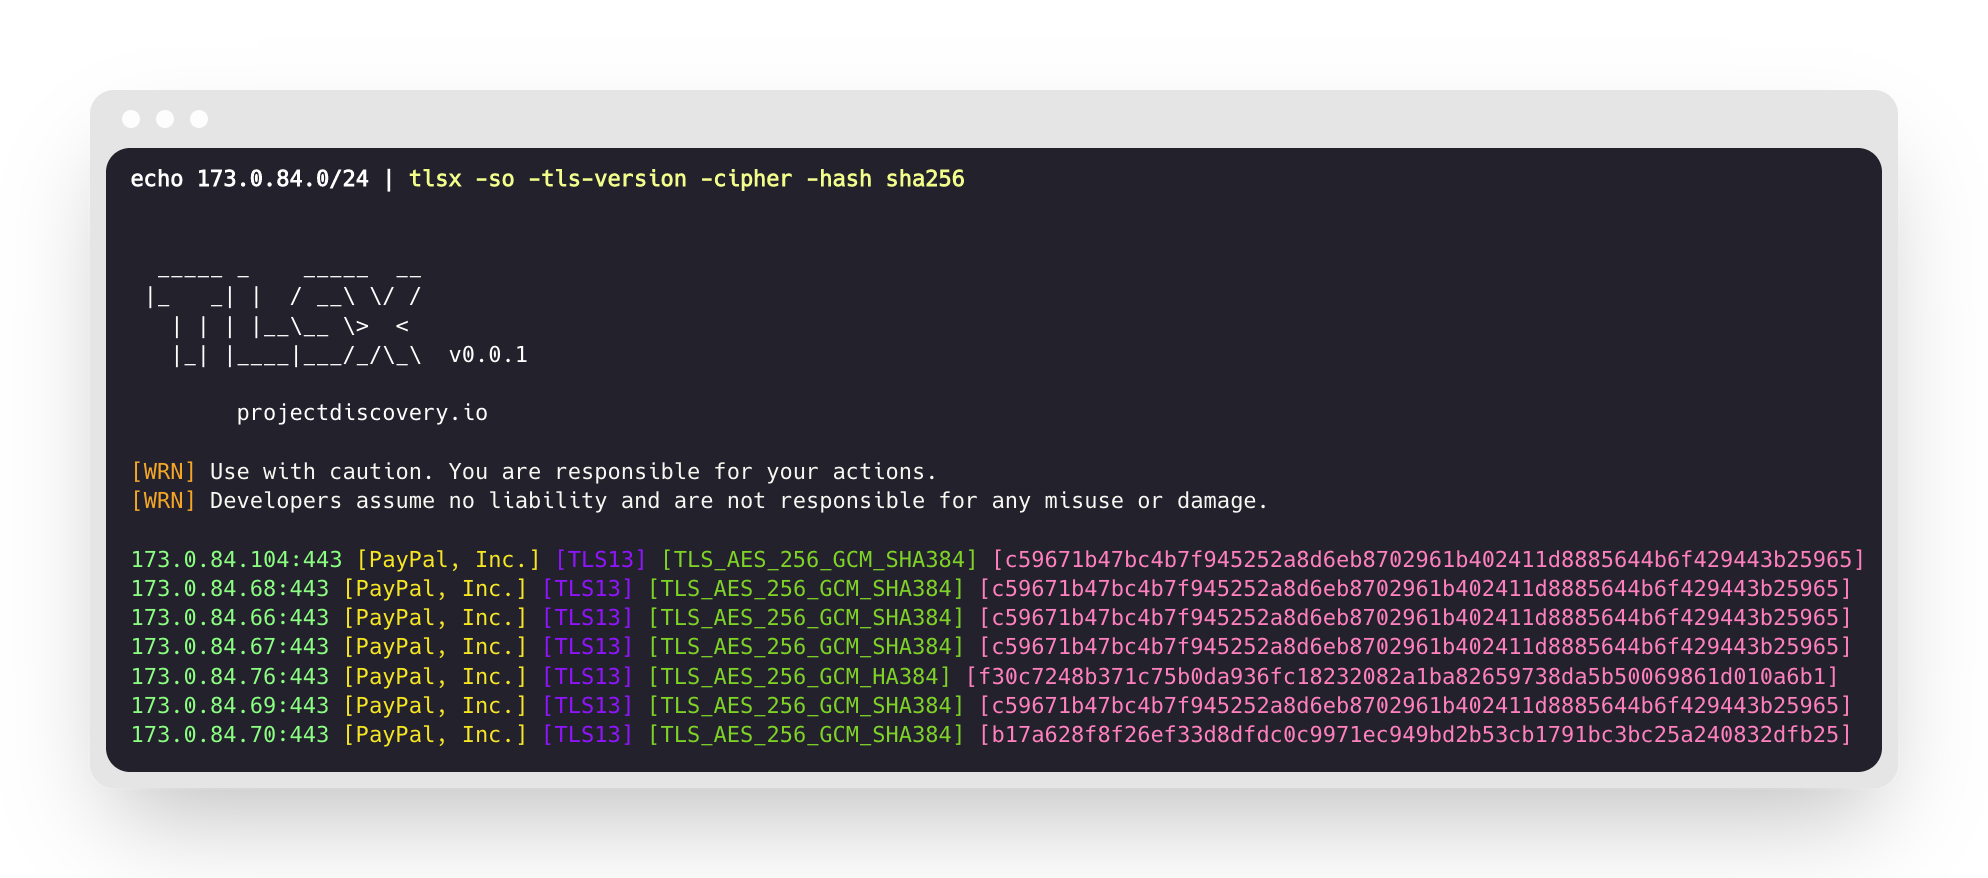 projectdiscovery/tlsx
Fast and configurable TLS grabber focused on TLS based data collection.
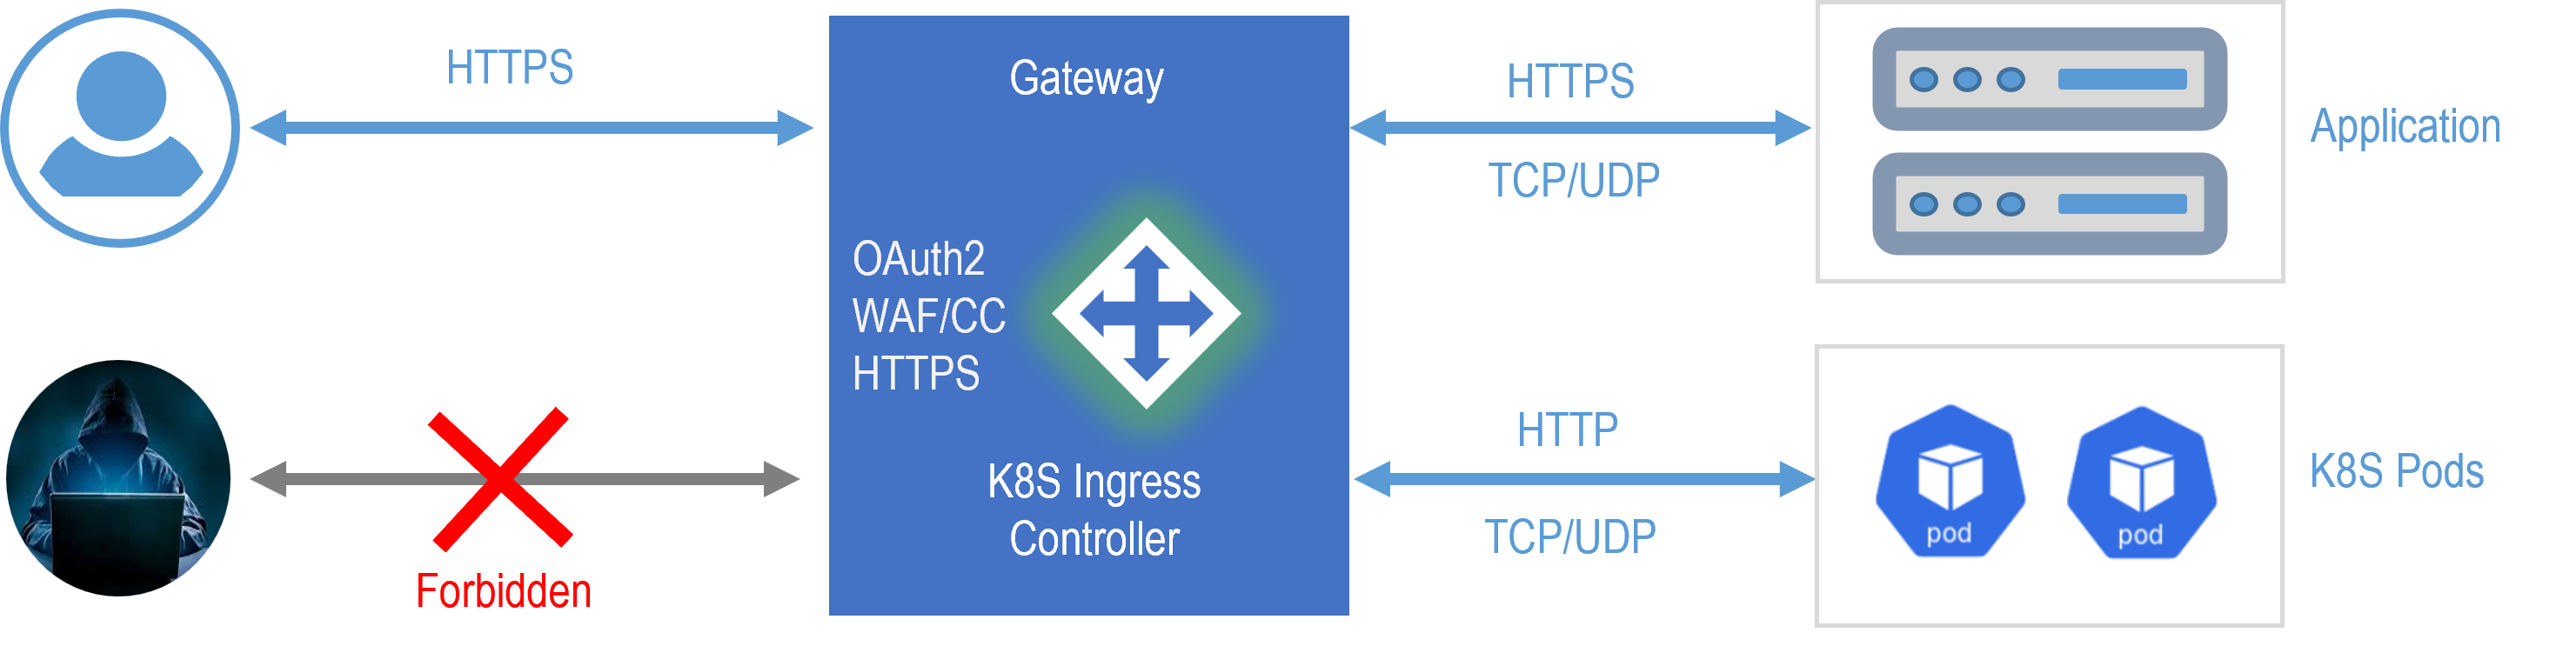 janusec/janusec
Unified application gateway providing reverse proxy, WAF, CC defense, OAuth2 authentication, ACME certificate automation, and GSLB for secure,…
 jsitech/jshielder
Hardening Script for Linux Servers/ Secure LAMP-LEMP Deployer/ CIS Benchmark