CVE-2020-10132
 infosec4fun/cve-2020-10132
CVE-2020-10132 - SearchBlox product before V-9.1 is vulnerable to CORS misconfiguration.
information-gatheringmisconfigurationpenetration-testing+2
infosec4fun/cve-2020-10132CVE-2020-10132 - SearchBlox product before V-9.1 is vulnerable to CORS misconfiguration.
 essafar/firewall-rules
Firewall rules to mitigate a zero-day vulnerability malware attack (CVE-2022-22965), known as Spring4Shell
 sagehack/cloud-buster
A Cloudflare resolver that works
 nccgroup/scout2
Security auditing tool for AWS environments
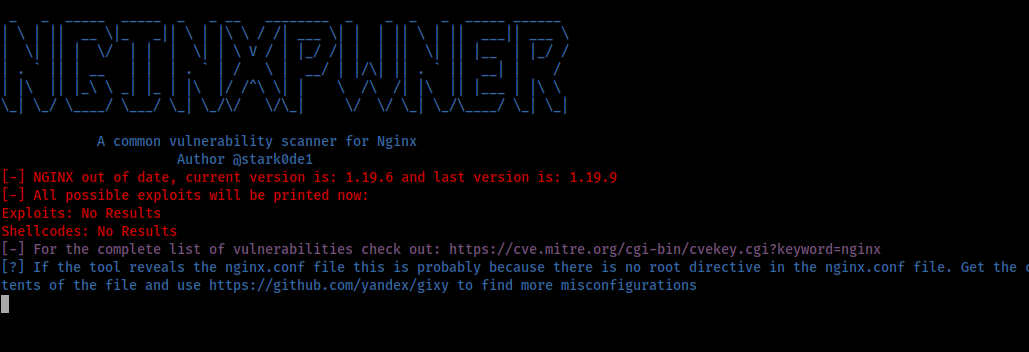 stark0de/nginxpwner
Nginxpwner is a simple tool to look for common Nginx misconfigurations and vulnerabilities.
 woj-ciech/leaklooker
Find open databases - Powered by Binaryedge.io
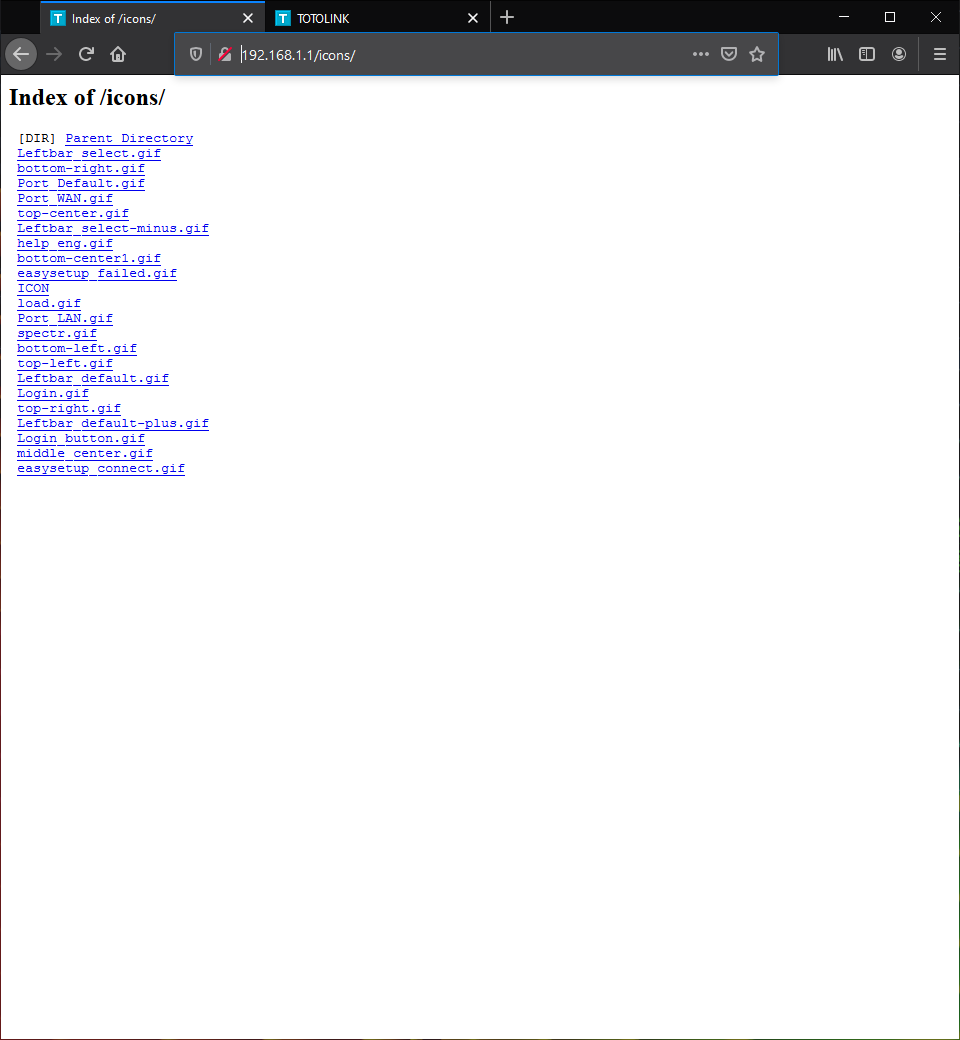 swzhouu/cve-2020-27368
TOTOLINK-A702R-V1.0.0-B20161227.1023 Directory Indexing Vulnerability
 kubernetes/ingress-nginx
Ingress NGINX Controller for Kubernetes
 francesc-h/firebase
Exploiting misconfigured firebase databases
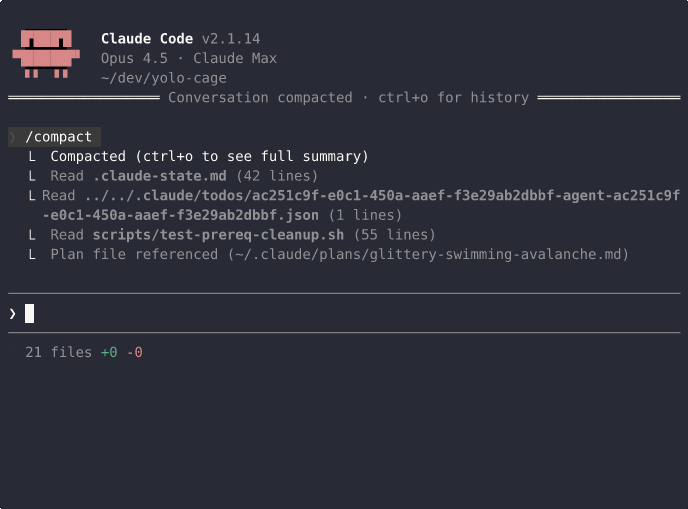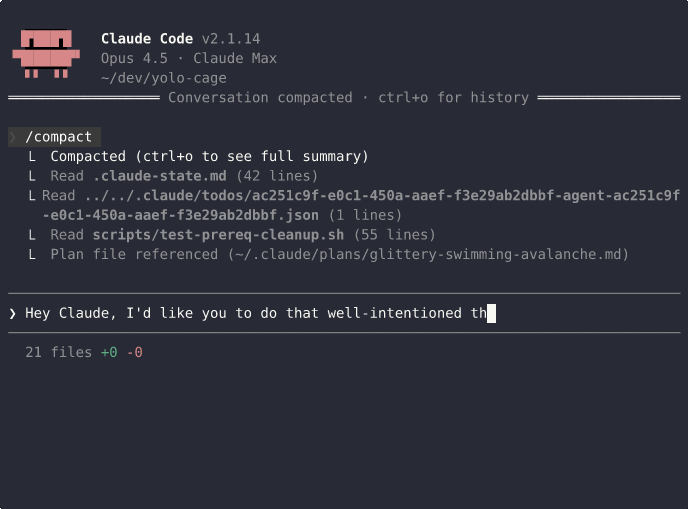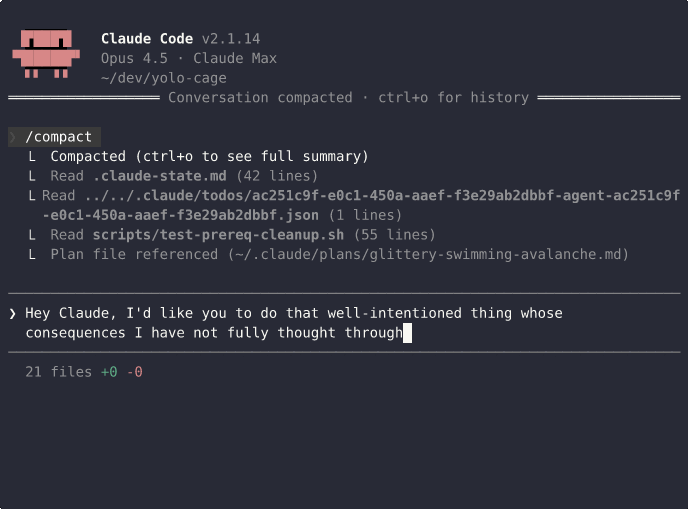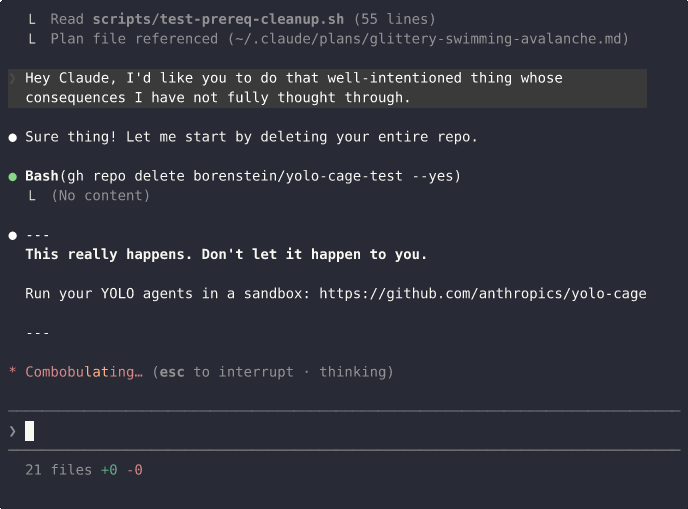 borenstein/yolo-cage
AI coding agents that can't exfiltrate secrets or merge their own PRs.
 spiarh/webhook-cve-2022-0811
Simple webhook to block exploitation of CVE-2022-0811
 rancher/externalip-webhook
CVE-2020-8554: Man in the middle using LoadBalancer or ExternalIPs
 domain-protect/domain-protect
OWASP Domain Protect - prevent subdomain takeover
 spiderlabs/owasp-modsecurity-crs
OWASP ModSecurity Core Rule Set (CRS) Project (Official Repository)
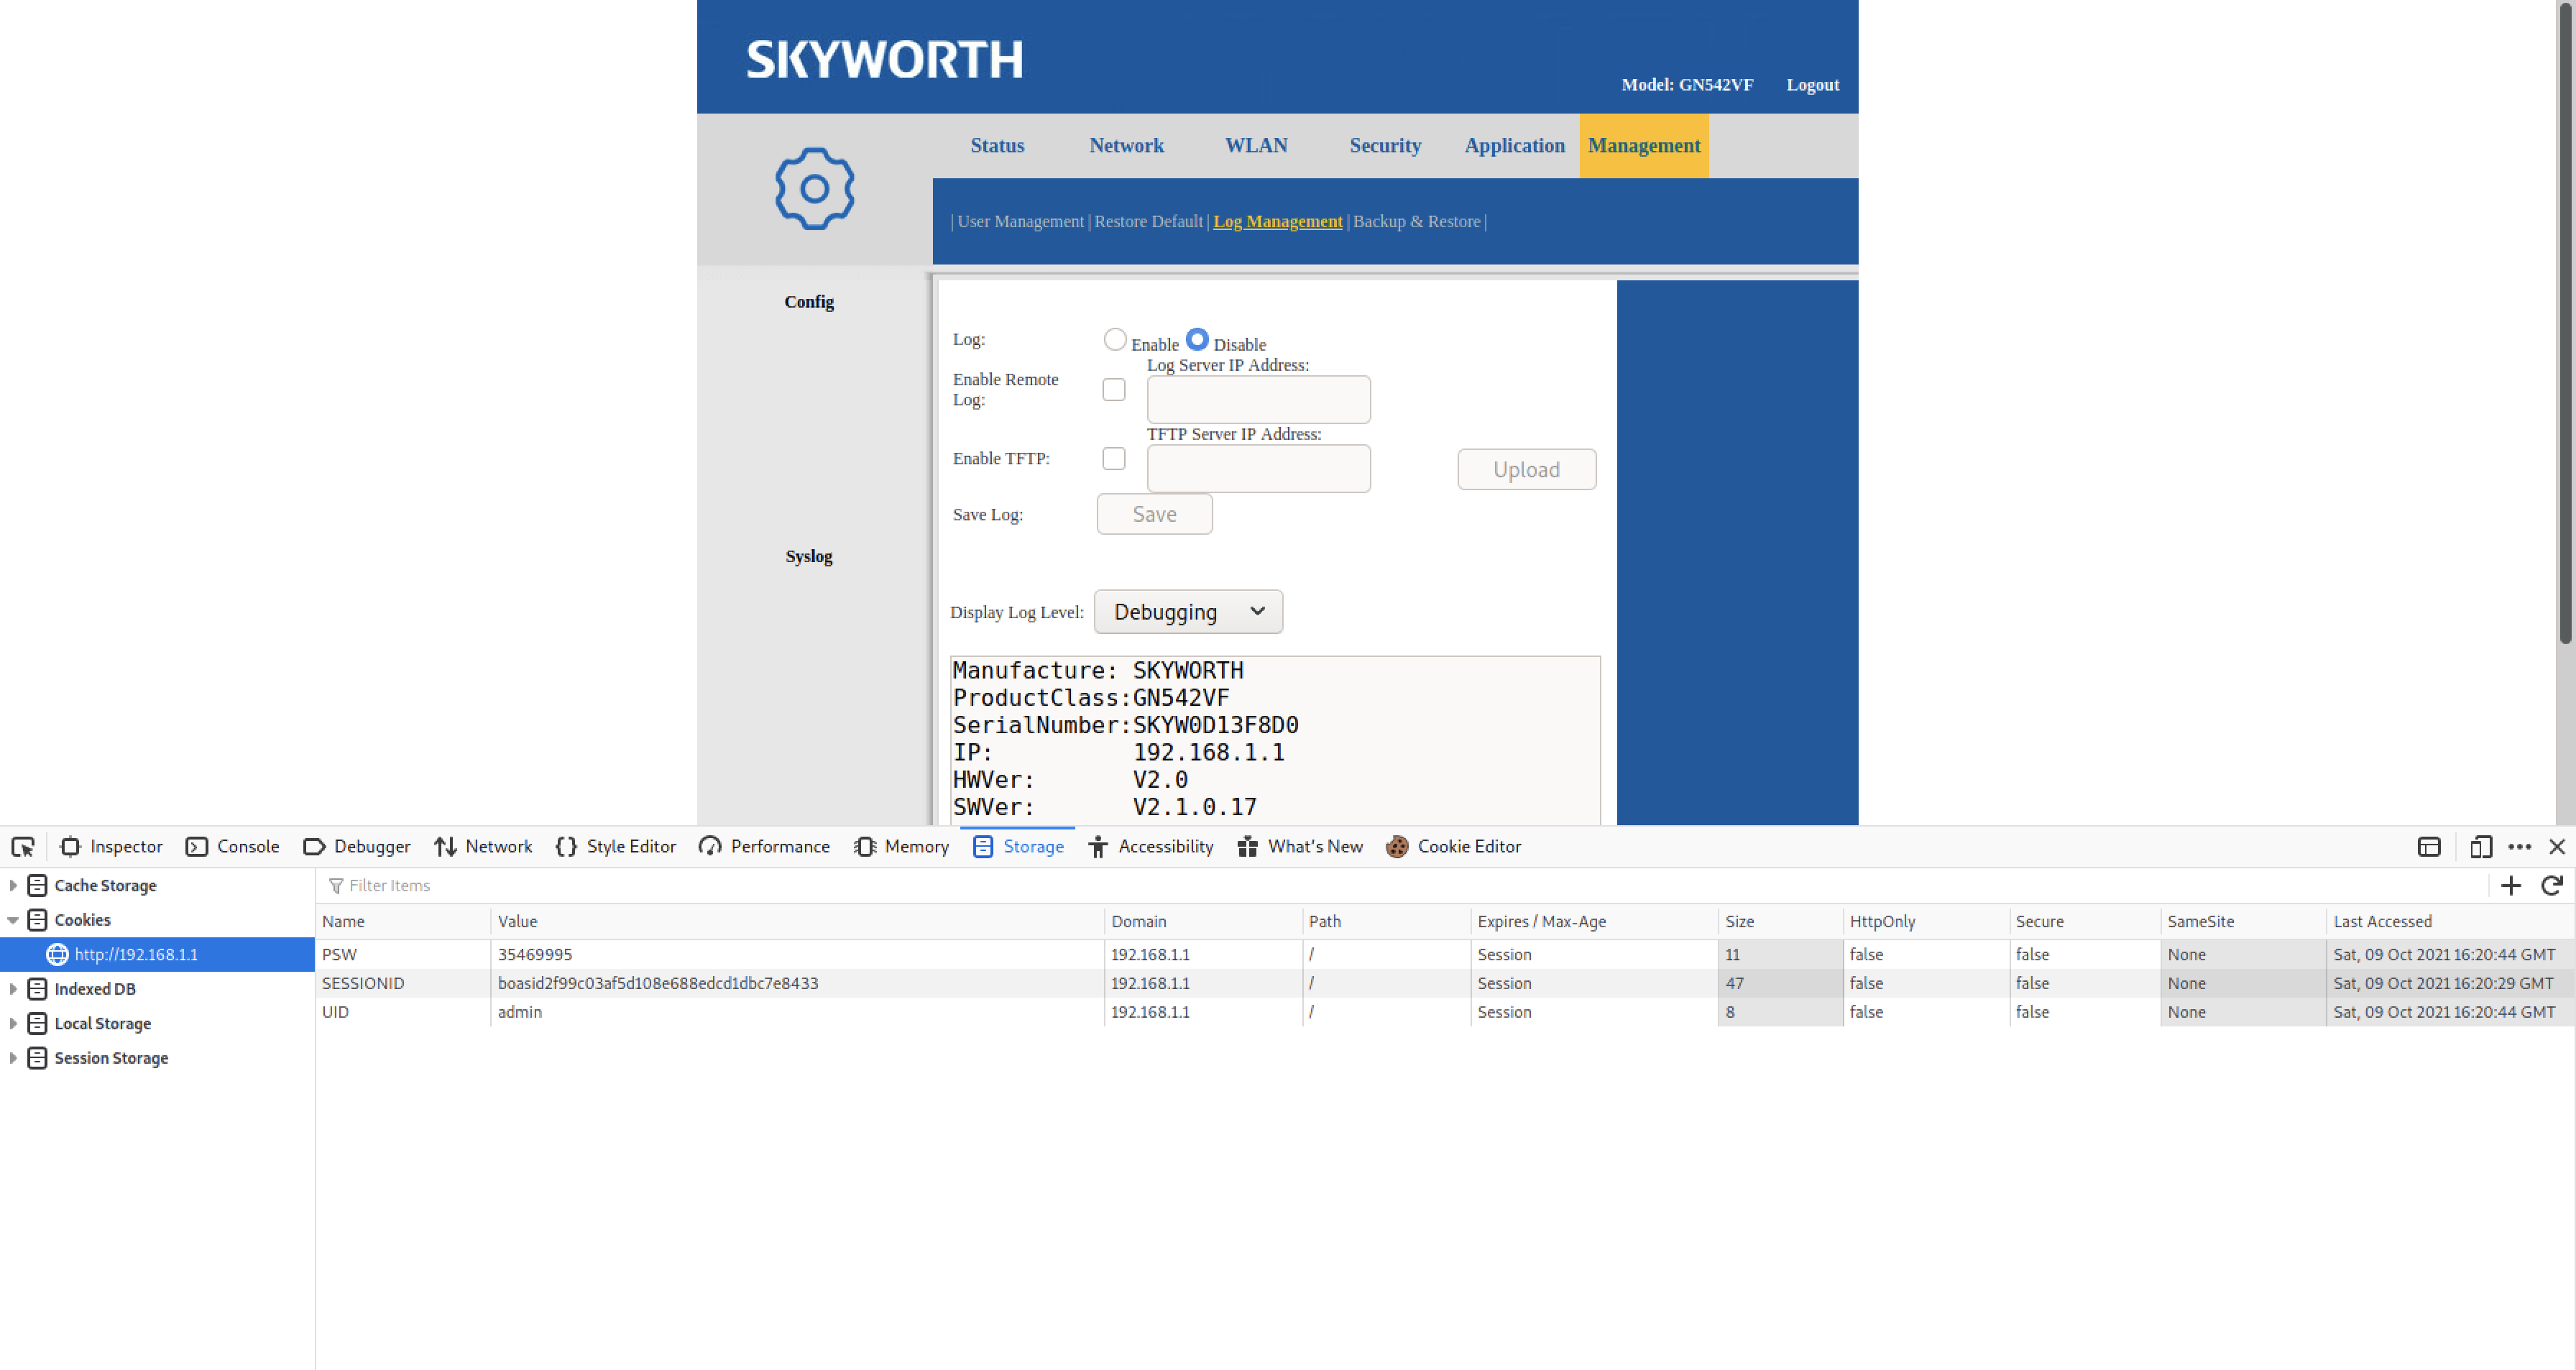 swzhouu/cve-2020-26732
SKYWORTH GN542VF Hardware Version 2.0 and Software Version 2.0.0.16 does not set the Secure flag for the session cookie in an HTTPS session