
GPOHound
 cogiceo/gpohound
Offensive GPO dumping and analysis tool that leverages and enriches BloodHound data
configuration-auditinginformation-gatheringmisconfiguration+4
4294 days ago
cogiceo/gpohoundOffensive GPO dumping and analysis tool that leverages and enriches BloodHound data
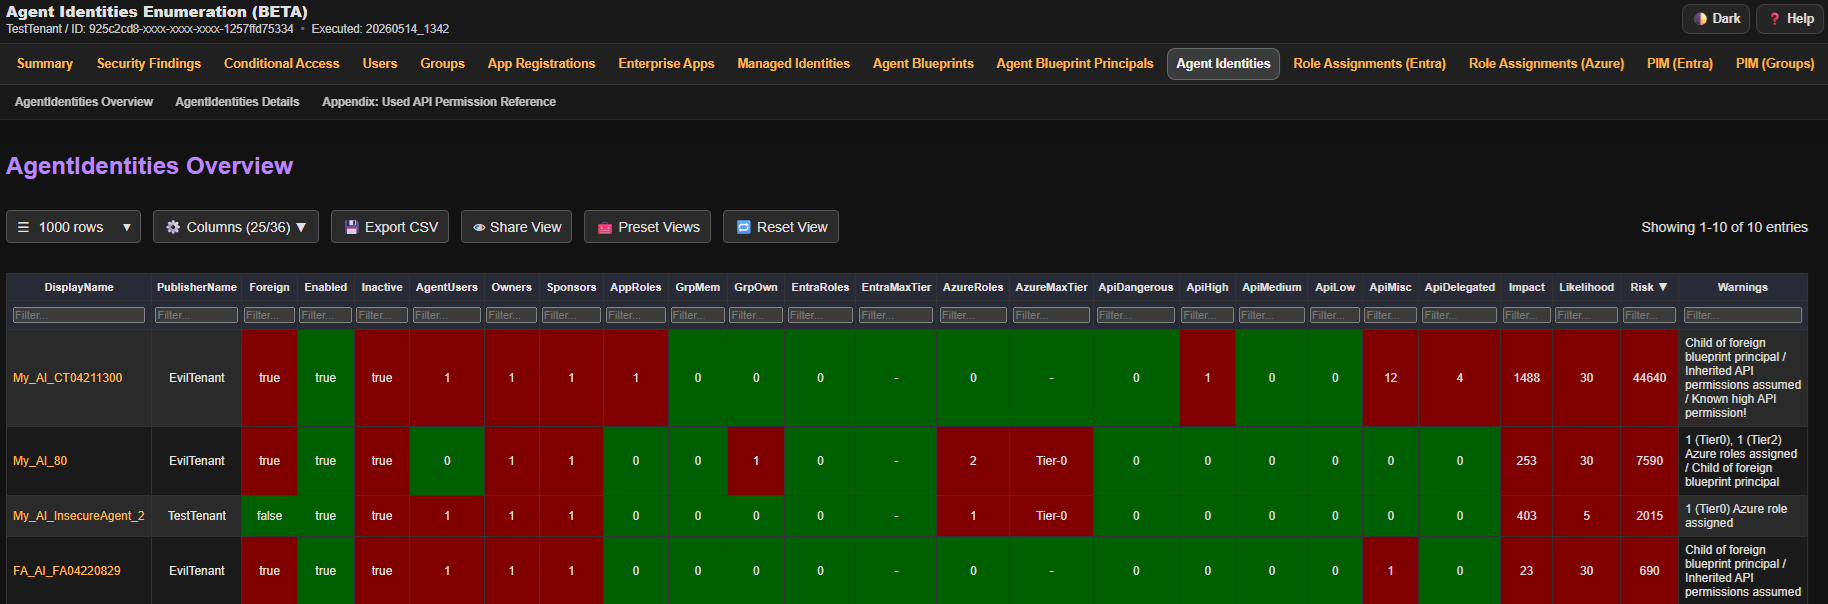 compasssecurity/entrafalcon
A lightweight PowerShell tool for assessing the security posture of Microsoft Entra ID environments. It helps identify privileged objects, risky…
 nahamsec/hostilesubbruteforcer
Subdomain brute-forcing tool that enumerates existing subdomains and detects misconfigured cloud-hosted subdomains vulnerable to takeover across AWS,…
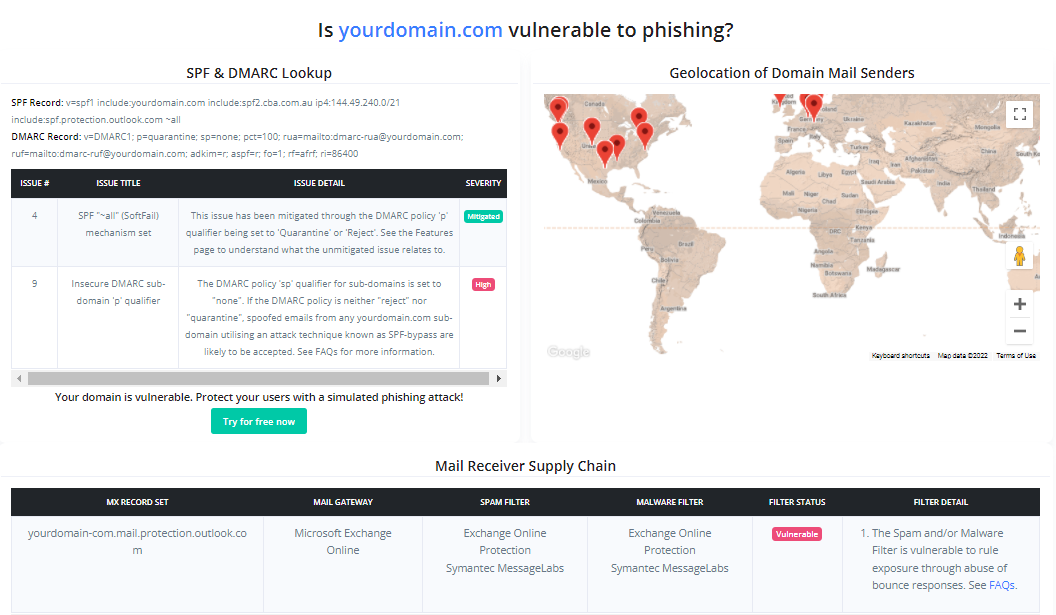 caniphish/phishious
An open-source Secure Email Gateway (SEG) evaluation toolkit designed for red-teamers.
 cycodelabs/raven
Scans GitHub Actions CI/CD workflows for security vulnerabilities, indexes findings into a Neo4j graph database, and provides a query library for…
 synacktiv/gpoparser
gpoParser is a tool designed to extract and analyze configurations applied through Group Policy Objects (GPOs) in an Active Directory environment.
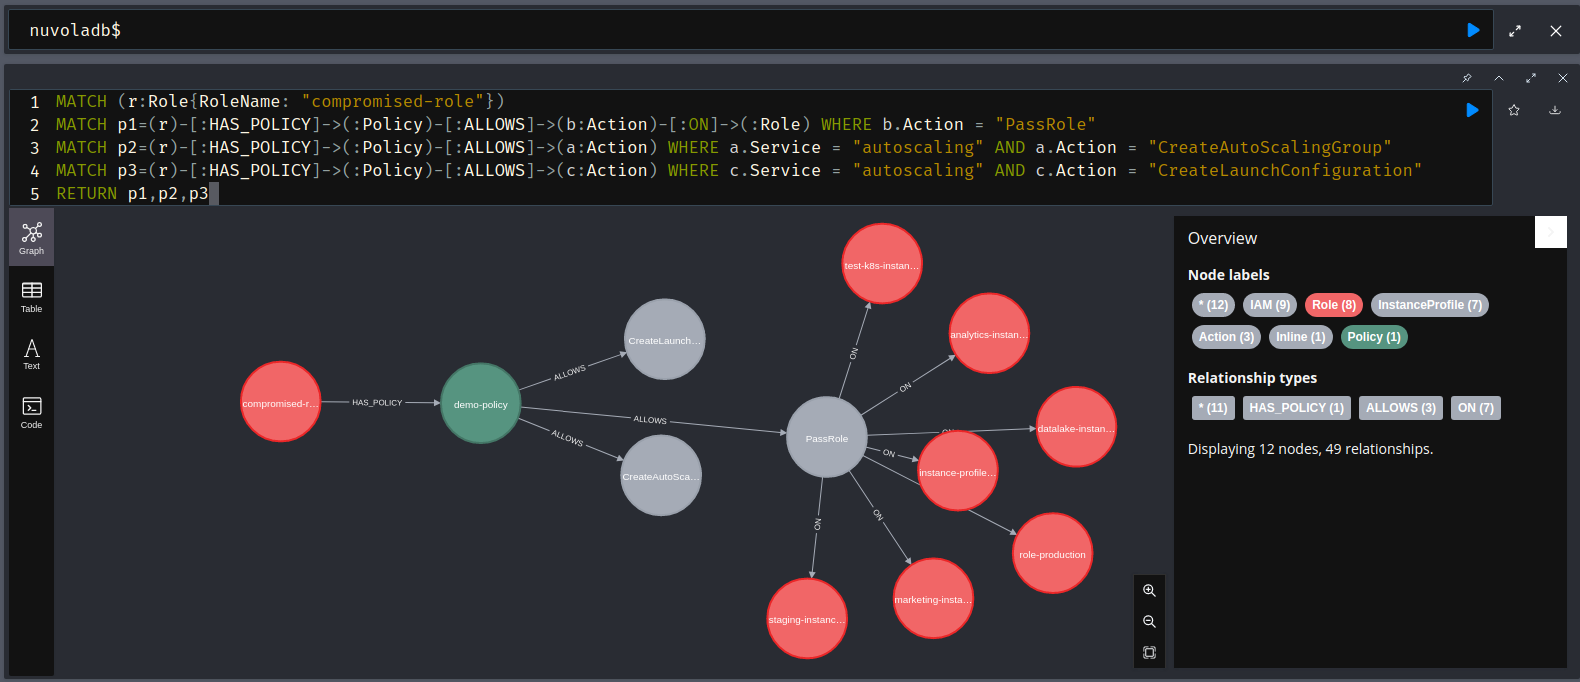 primait/nuvola
Graph-based AWS security analysis tool that dumps cloud configurations, detects misconfigurations, and maps attack paths using a Neo4j digital twin…
 neffisback/wsuks
Automating the MITM attack on WSUS
 cyberark/blobhunter
Find exposed data in Azure with this public blob scanner
 mindpointgroup/cloudfrunt
A tool for identifying misconfigured CloudFront domains
 secuproject/adenum
AD Enum is a pentesting tool that allows to find misconfiguration through the the protocol LDAP and exploit some of those weaknesses with kerberos.
 bishopfox/smogcloud
Find cloud assets that no one wants exposed 🔎 ☁️
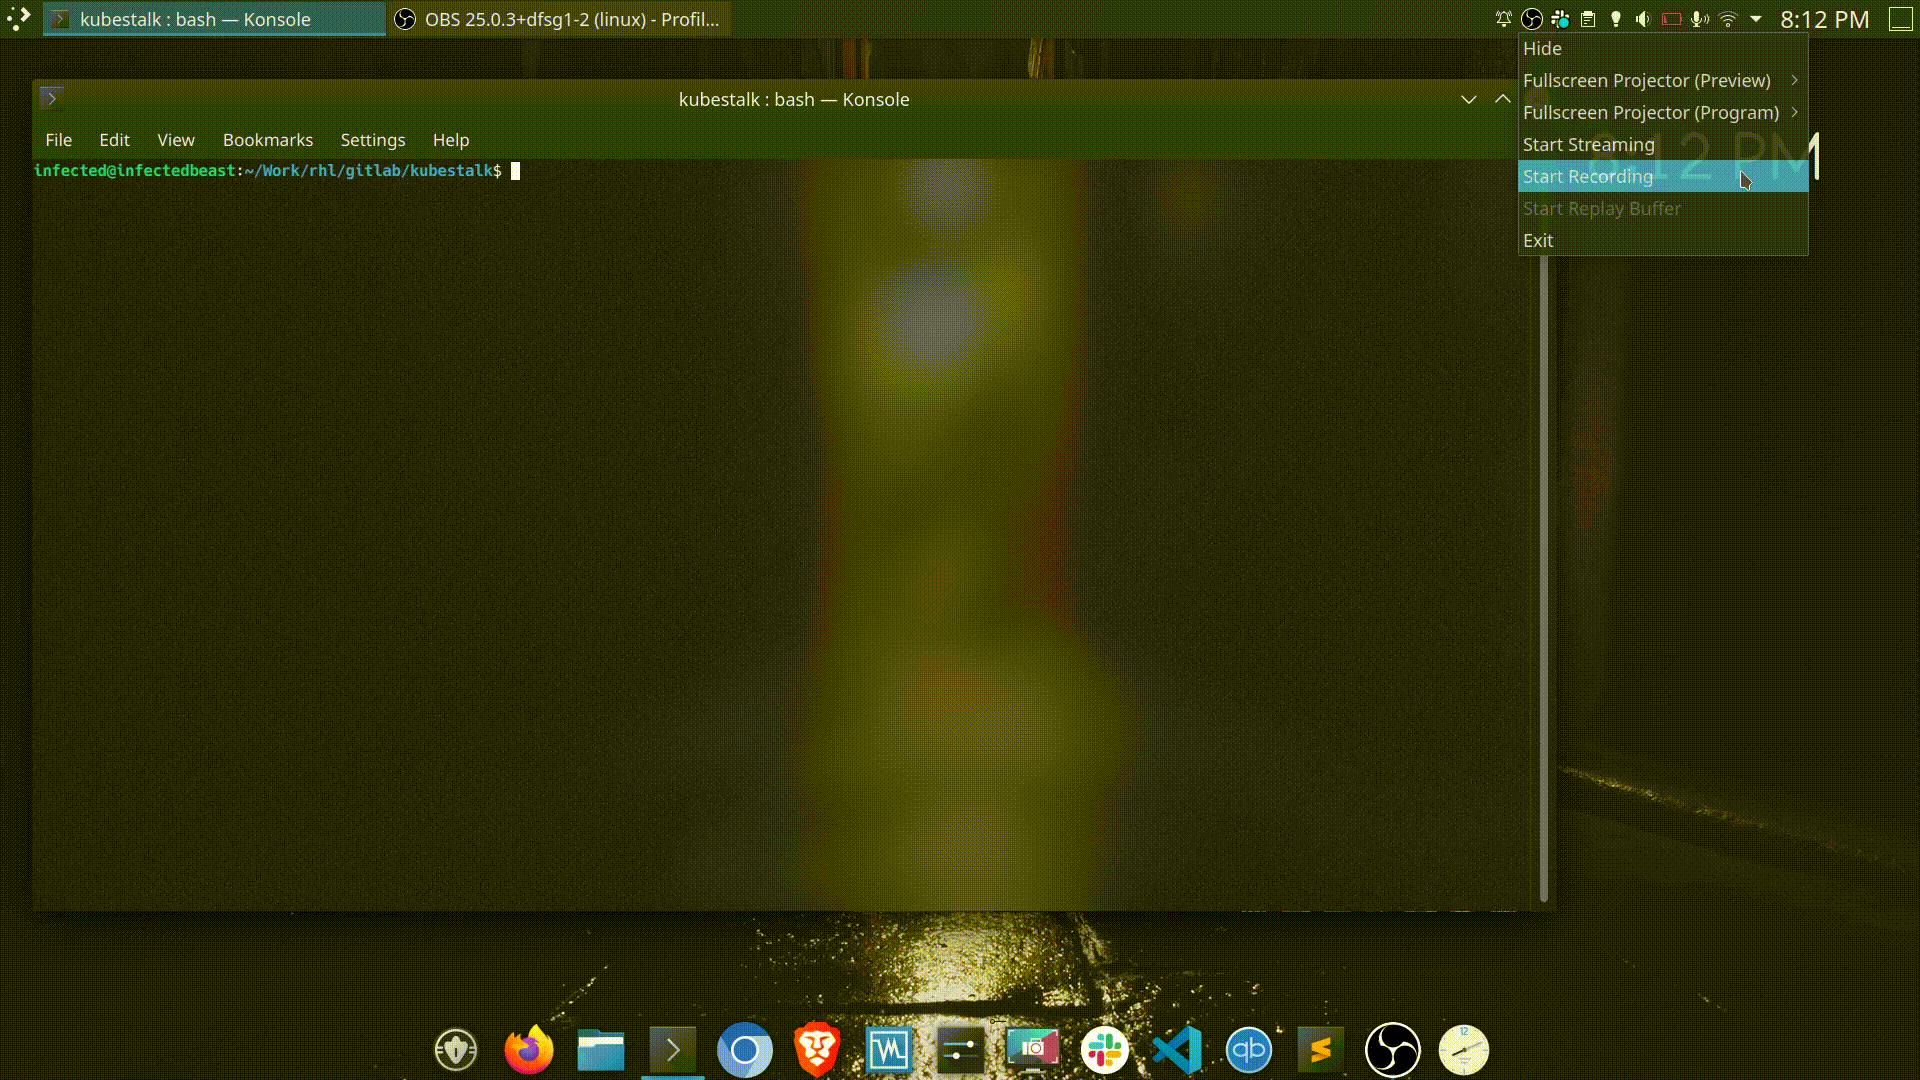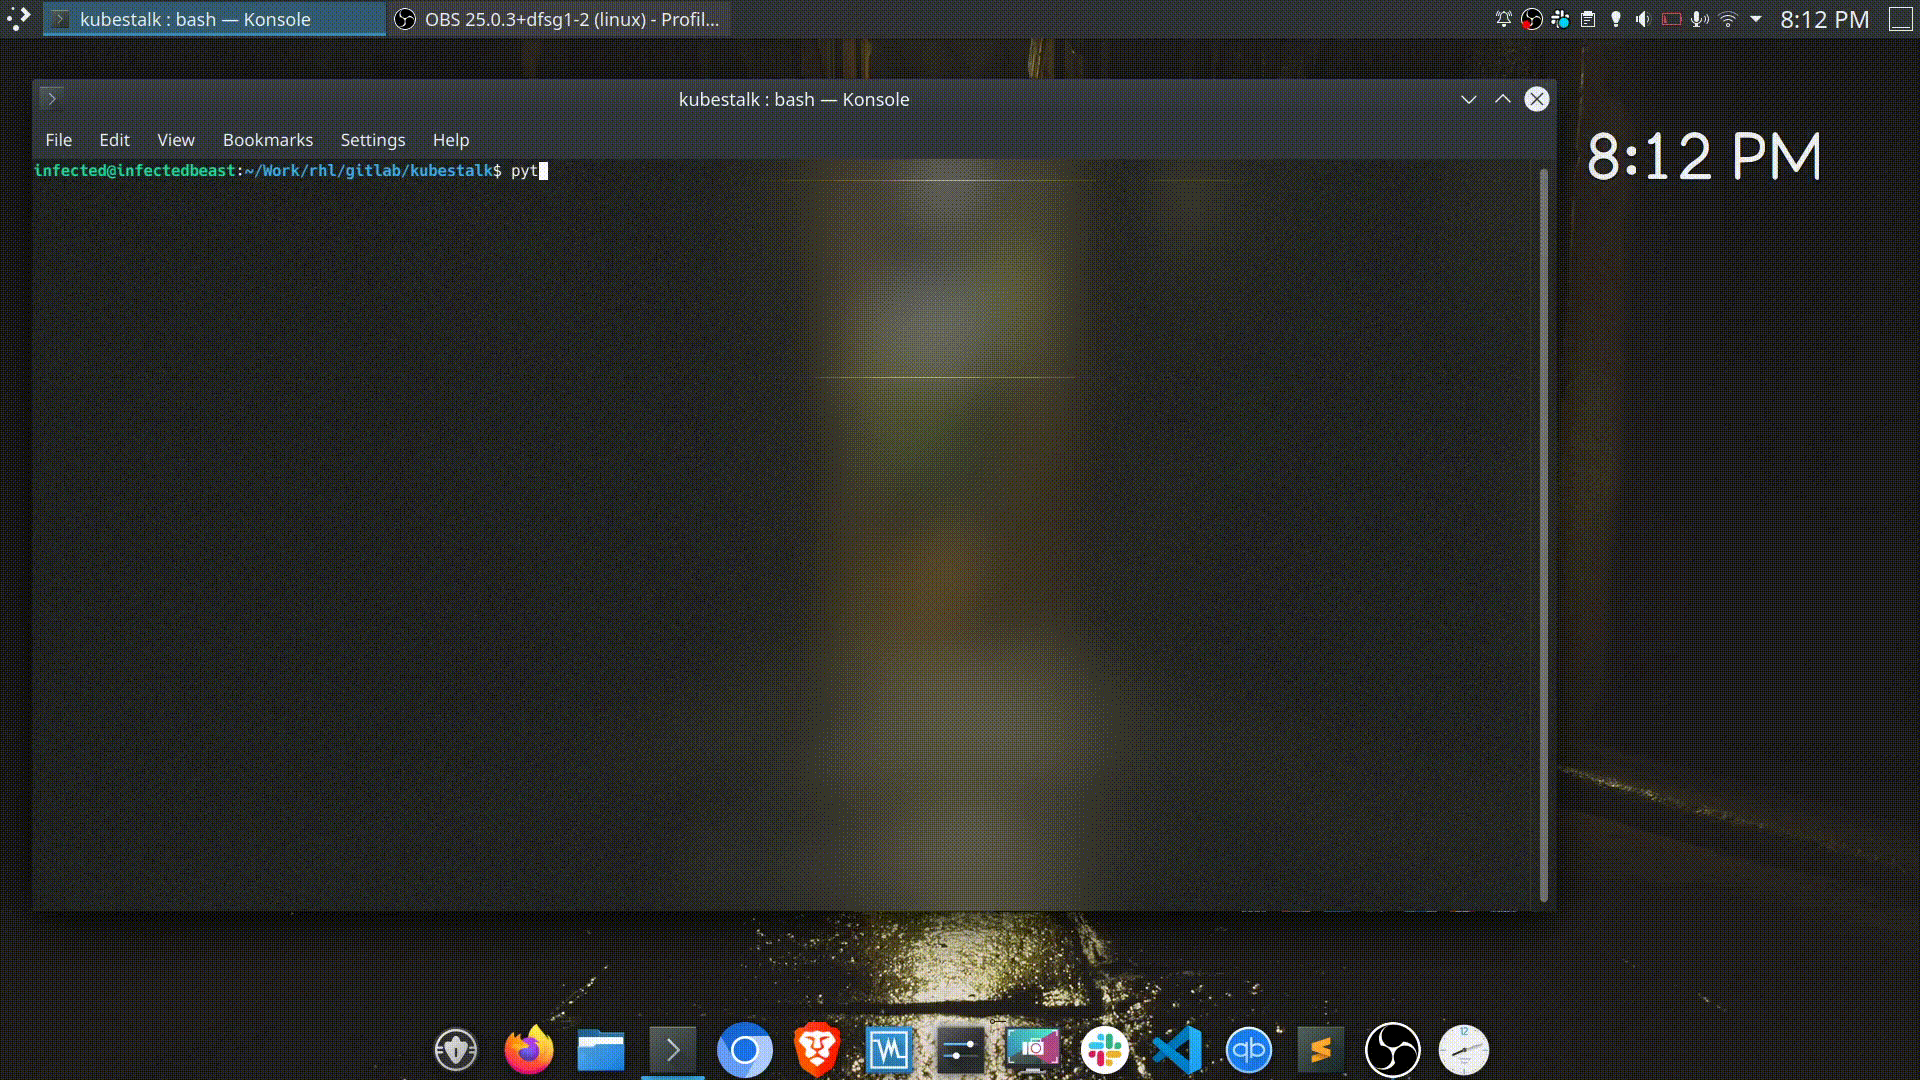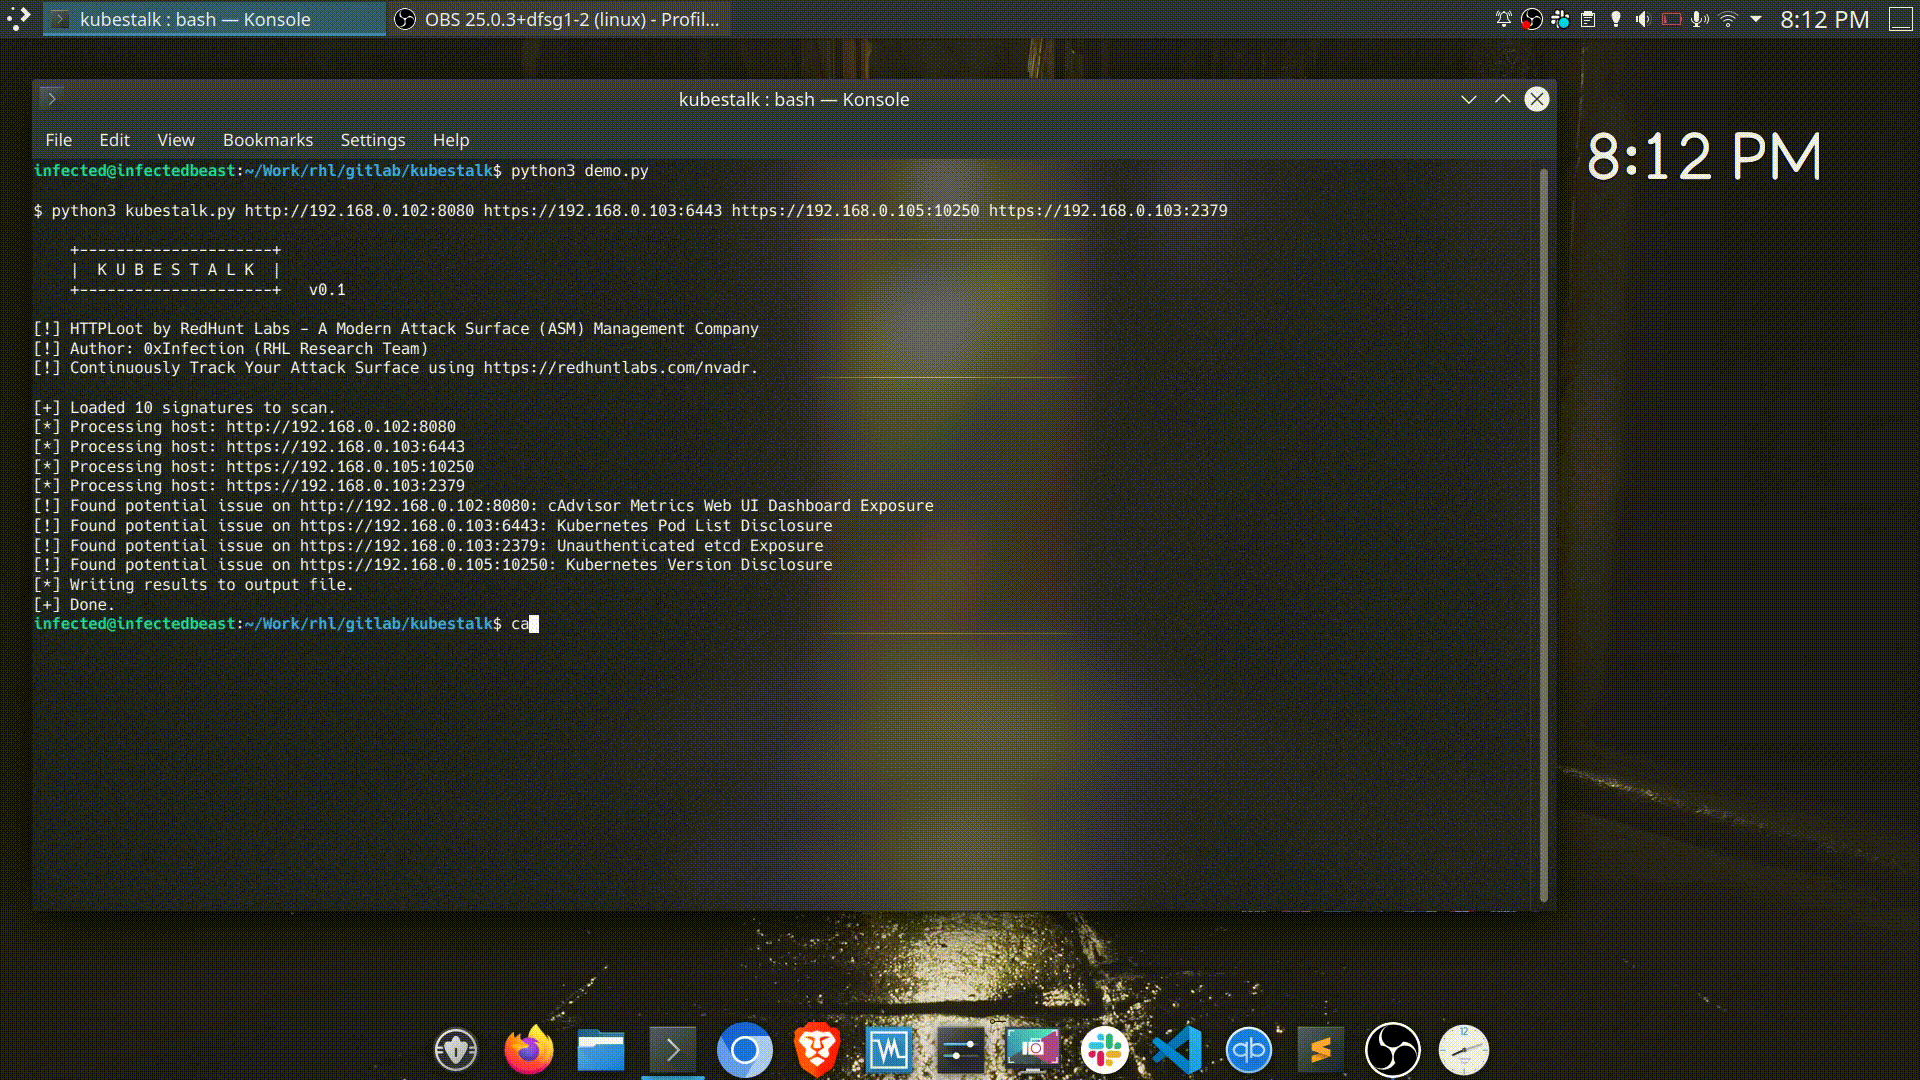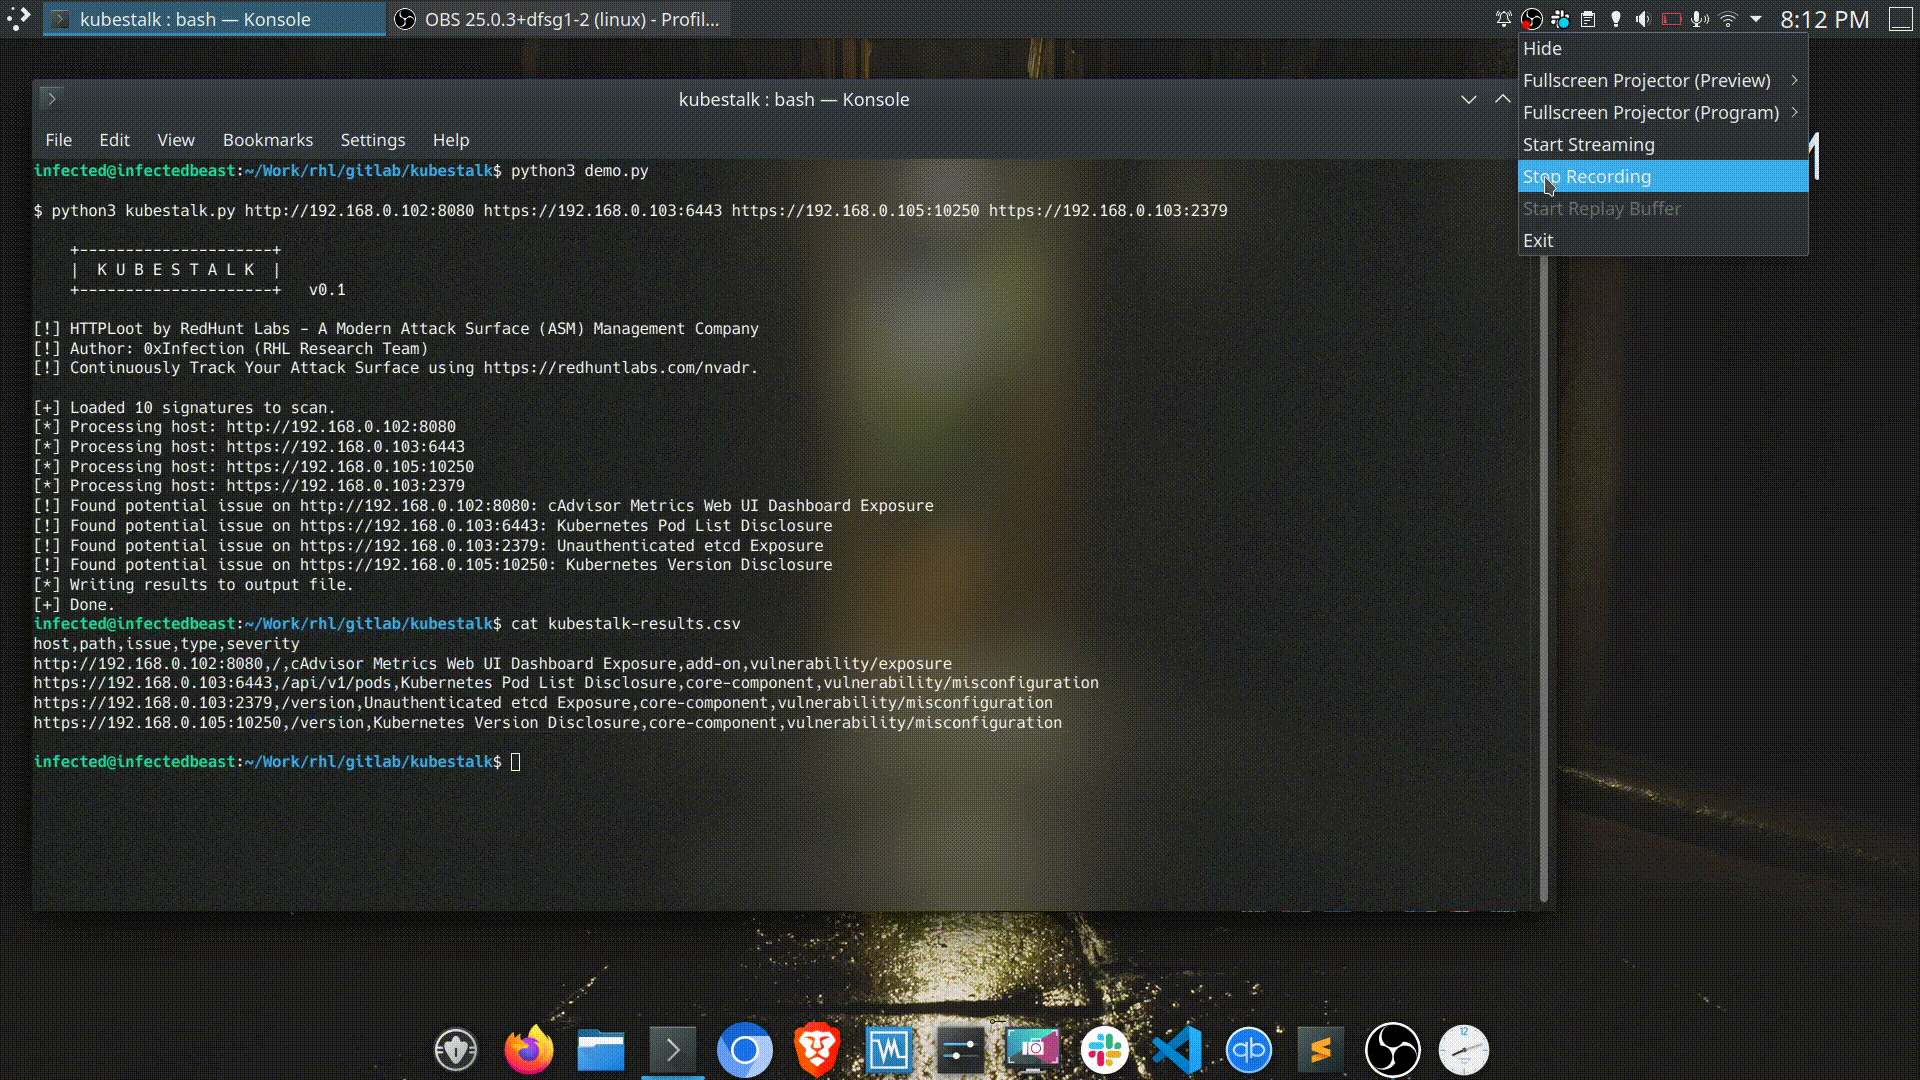 redhuntlabs/kubestalk
Black-box Kubernetes attack surface discovery tool that probes for unsecured clusters, exposed dashboards, and misconfigurations using…
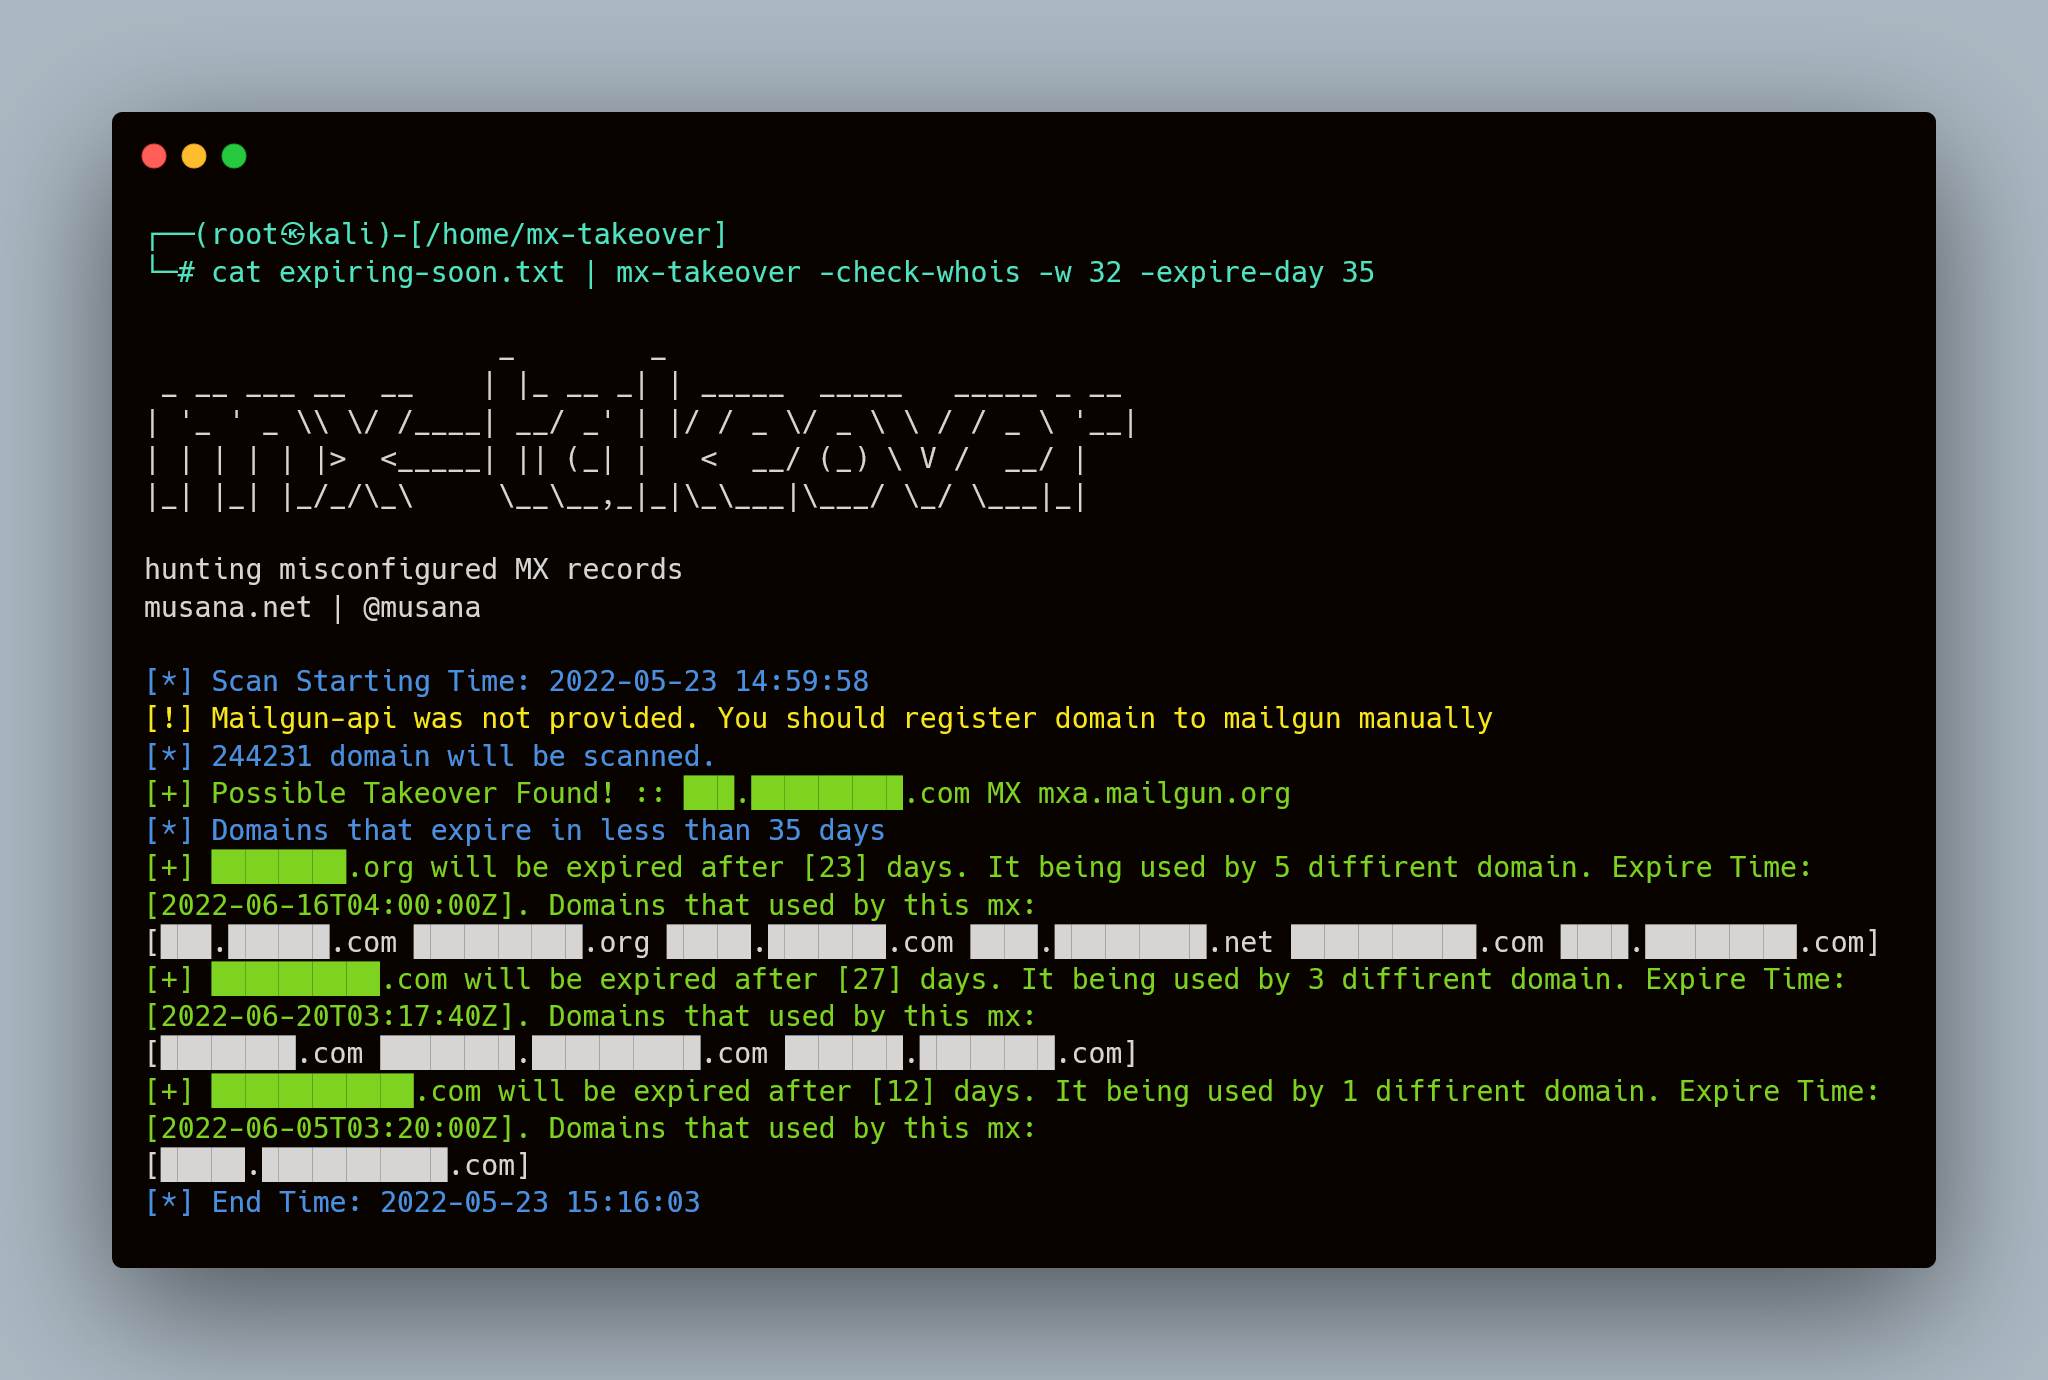 musana/mx-takeover
Scans DNS MX records to detect misconfigured, expiring, or unregistered domains vulnerable to email takeover, with automatic reclamation support for…
 k8scout/k8scout
Drop a single binary into a compromised Kubernetes pod and instantly map every realistic attack path to cluster-admin, node escape, secret theft,…
 404tk/cloudtoolkit
Authorized cloud adversary simulation and validation toolkit
 nccgroup/s3_objects_check
Whitebox evaluation of effective S3 object permissions, to identify publicly accessible files.
 nccgroup/go-pillage-registries
Pentester-focused Docker registry tool to enumerate and pull images