
pgedge-anonymizer
 pgedge/pgedge-anonymizer
An anonymizer tool for replacing PII and similar data in dev/test databases copied from production
database-securitydata-exfiltrationdevsecops+3
33
pgedge/pgedge-anonymizerAn anonymizer tool for replacing PII and similar data in dev/test databases copied from production
 preflightsh/preflight
Go-based CLI tool that scans codebases for launch readiness, detecting missing configuration, security hygiene issues, secret leaks, and integration…
 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
 firefart/stunner
Test and exploit STUN/TURN servers for misconfigurations, enabling internal network pivoting via SOCKS proxy, memory leak attacks, and internal port…
 facebook/mcpguard-dynamic
Kernel-level eBPF sandbox for securing LLM agent tool calls made through the Model Context Protocol (MCP)
 farenhytee/database-sentinel
Open-source security audits for Supabase: a read-only MCP server, a CLI agent and a Claude Skill. Finds RLS misconfigurations, exposed keys and risky…
 d3lightfu1/quietphase
Pwsh tool for AD Group Enumeration Auditing
 cisofy/lynis
Agentless security auditing tool for Linux, macOS, and UNIX systems. Performs in-depth scans for vulnerabilities, configuration issues, and…
 eh-amish/windows-defender-security-auditor-cve-2026-50656-
Read-only PowerShell security auditor for Windows endpoints and servers: checks Defender configuration, patch status, credentials, persistence,…
 neelkotnis/azure-security-auditor
CLI tool to audit Azure security posture, RBAC, NSGs, storage, identity, and encryption
 wadesweaponshed/check-point-trusted-access-review
Local web app for conducting a Check Point Trusted Access Review. This scanner is built specifically to look for configuration issues around…
 v1c0mmrt/redis-cve-2026-23479-scanner
CVE-2026-23479 Redis Use-After-Free vulnerability detection tool
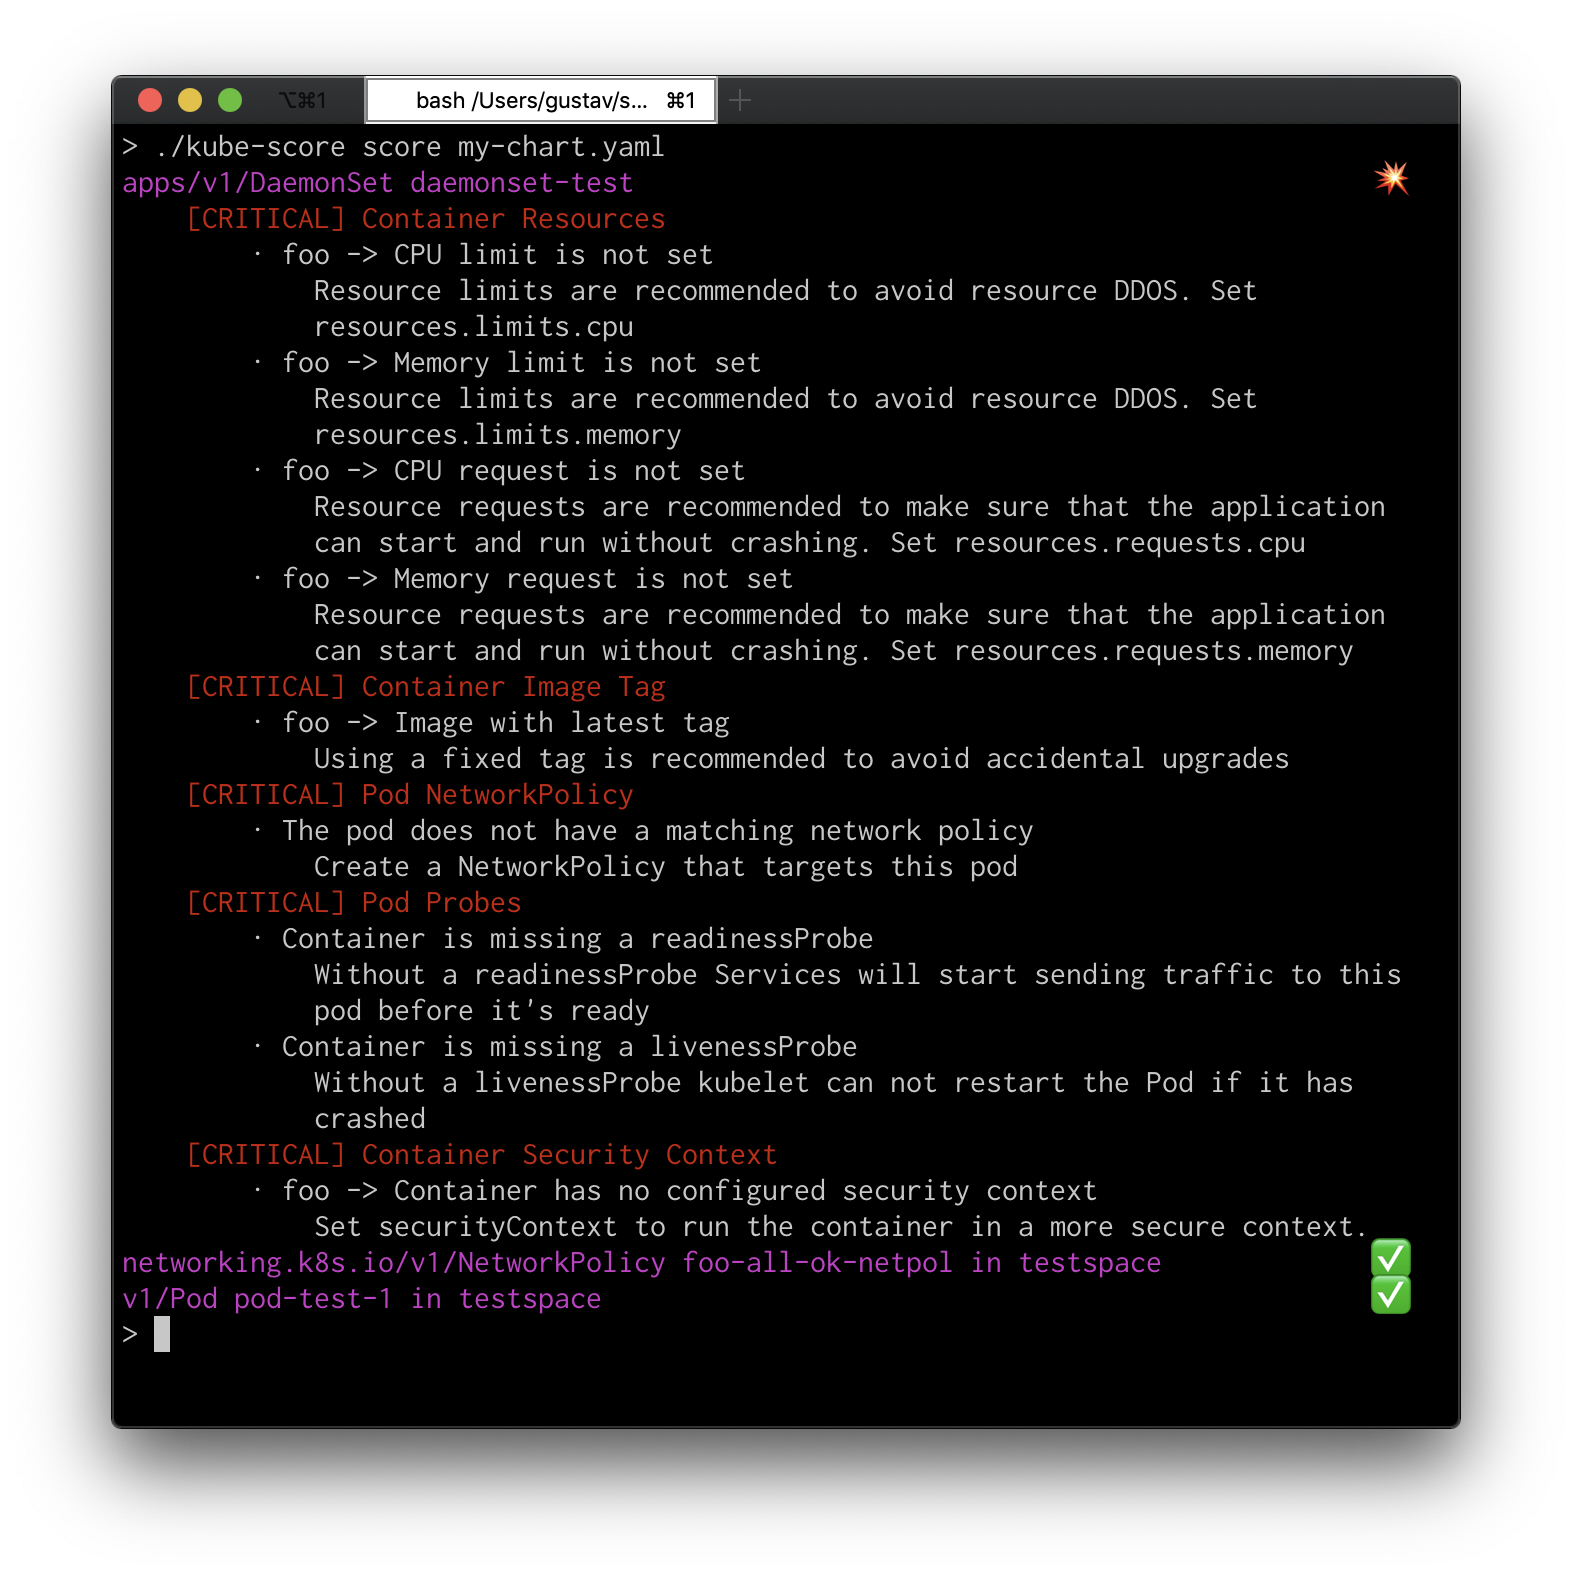 zegl/kube-score
Kubernetes object analysis with recommendations for improved reliability and security. kube-score actively prevents downtime and bugs in your…
 sleepthegod/dns-zone-audit
This Bash script checks domains for DNS zone transfer misconfigurations (CVE-1999-0532). It queries name servers and attempts AXFR requests; if…
 ad-security/ad_miner
AD Miner is an Active Directory audit tool that leverages cypher queries to crunch data from the #Bloodhound graph database to uncover security…
 sudo-wp/sudowp-adminer
A secure, zero-trust database management tool for WordPress. Fixes critical SSRF vulnerabilities (CVE-2021-21311) by enforcing local connections only.
 csuribird/cve-2025-2304
This Python script exploits a critical mass assignment vulnerability in Camaleon CMS version 2.9.0, allowing any registered user to escalate their…
 iamlucif3r/aws-key-hunter
[Just for fun] Find exposed AWS keys (VALID KEYS ONLY) on github