
cosmicsting-validator
 samjuk/cosmicsting-validator
CosmicSting (CVE-2024-34102) POC / Patch Validator
devsecopsexploitationmisconfiguration+3
samjuk/cosmicsting-validatorCosmicSting (CVE-2024-34102) POC / Patch Validator
 jfs-jfs/cve-2026-37067
Incorrect access control in /vfm-admin/admin-panel/view/save-cvs.php in Veno File Manager Project 4.4.9 allows an unauthenticated attacker to extract…
 heroku/heroku-cve-2013-0269
Inspect all of your Heroku apps for vulnerable versions of the JSON gem
 heroku/heroku-cve-2013-0333
Scans Heroku applications for a critical Rails remote code execution vulnerability (CVE-2013-0333) and identifies unpatched instances requiring…
 emresandikci/nextjs-cve-2026-23870-checker
Checker and fixer for all 13 vulnerabilities in the Next.js May 2026 security release (CVE-2026-23870)
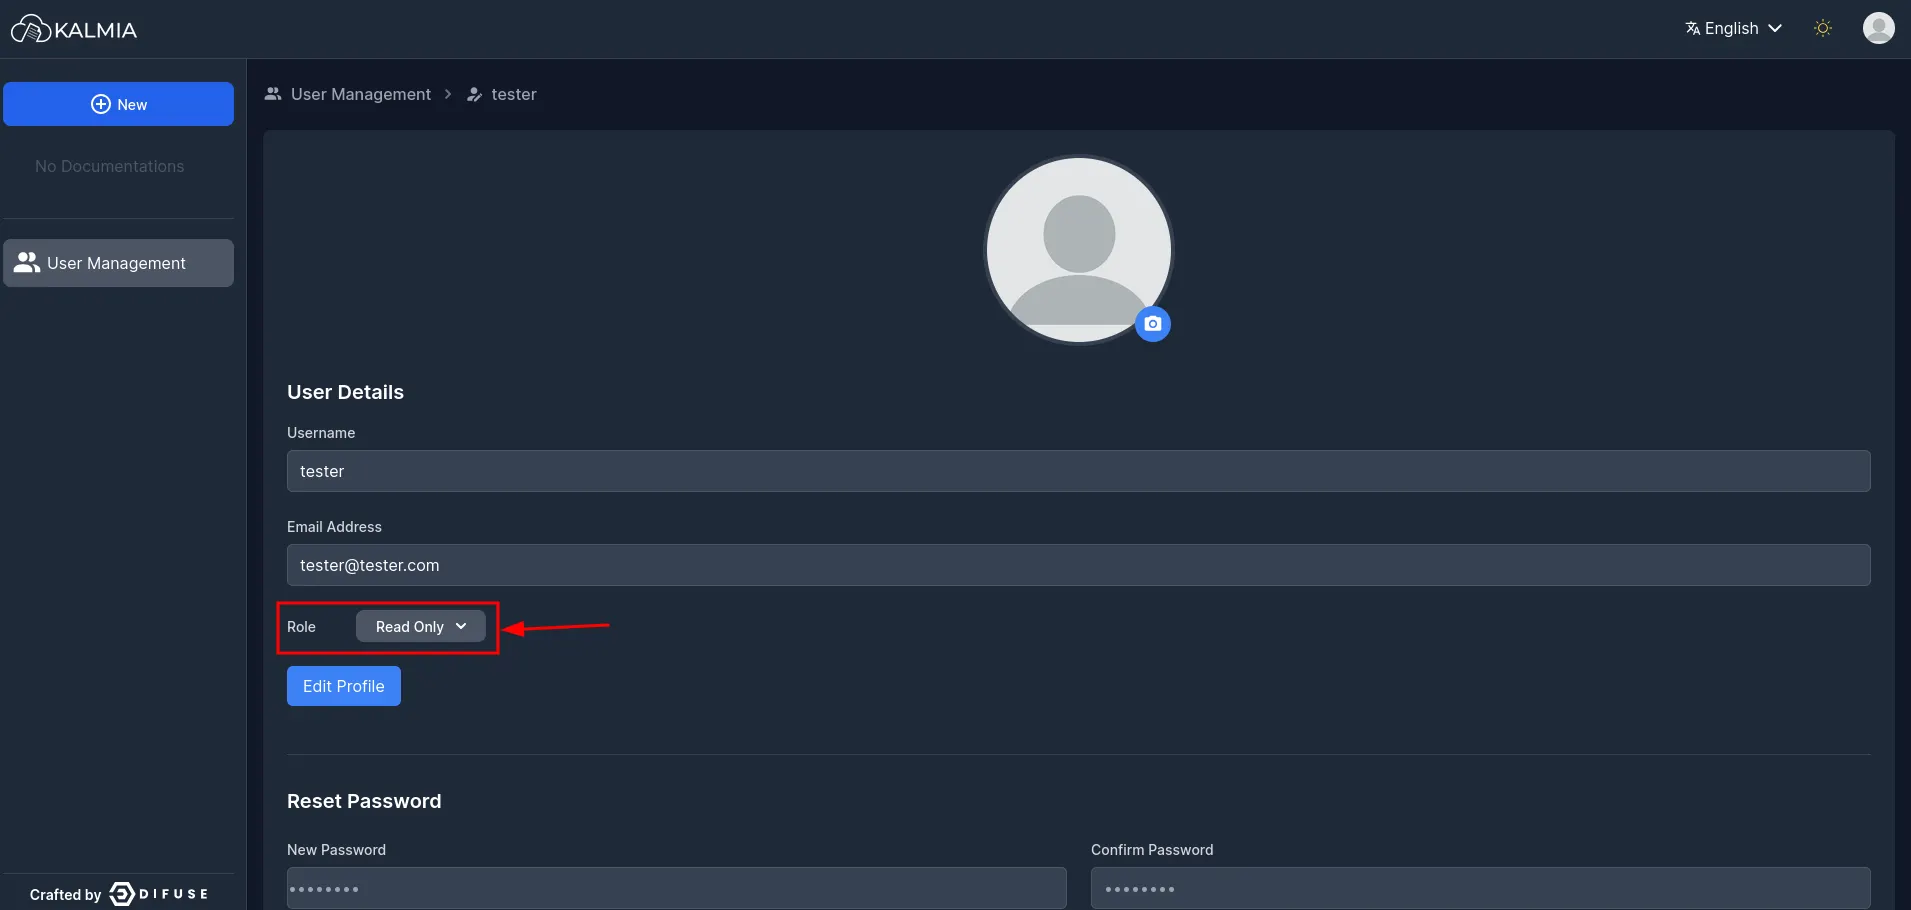 noxurge/cve-2025-65900
DifuseHQ Kalmia CMS version 0.2.0 contains an Incorrect Access Control vulnerability in the /kal-api/auth/users API endpoint. Due to insufficient…
 shoucheng3/spring-projects__spring-framework_cve-2022-22965_5-2-19-release
Exploit for CVE-2022-22965 (Spring4Shell) targeting Spring Framework versions vulnerable to remote code execution via classLoader manipulation.
 oiyl/cve-2025-46171
Writeup of a Denial of Service vulnerability in the vBulletin 3.8.7 friends list.
 nxploited/cve-2024-56071
Simple Dashboard <= 2.0 - Unauthenticated Privilege Escalation
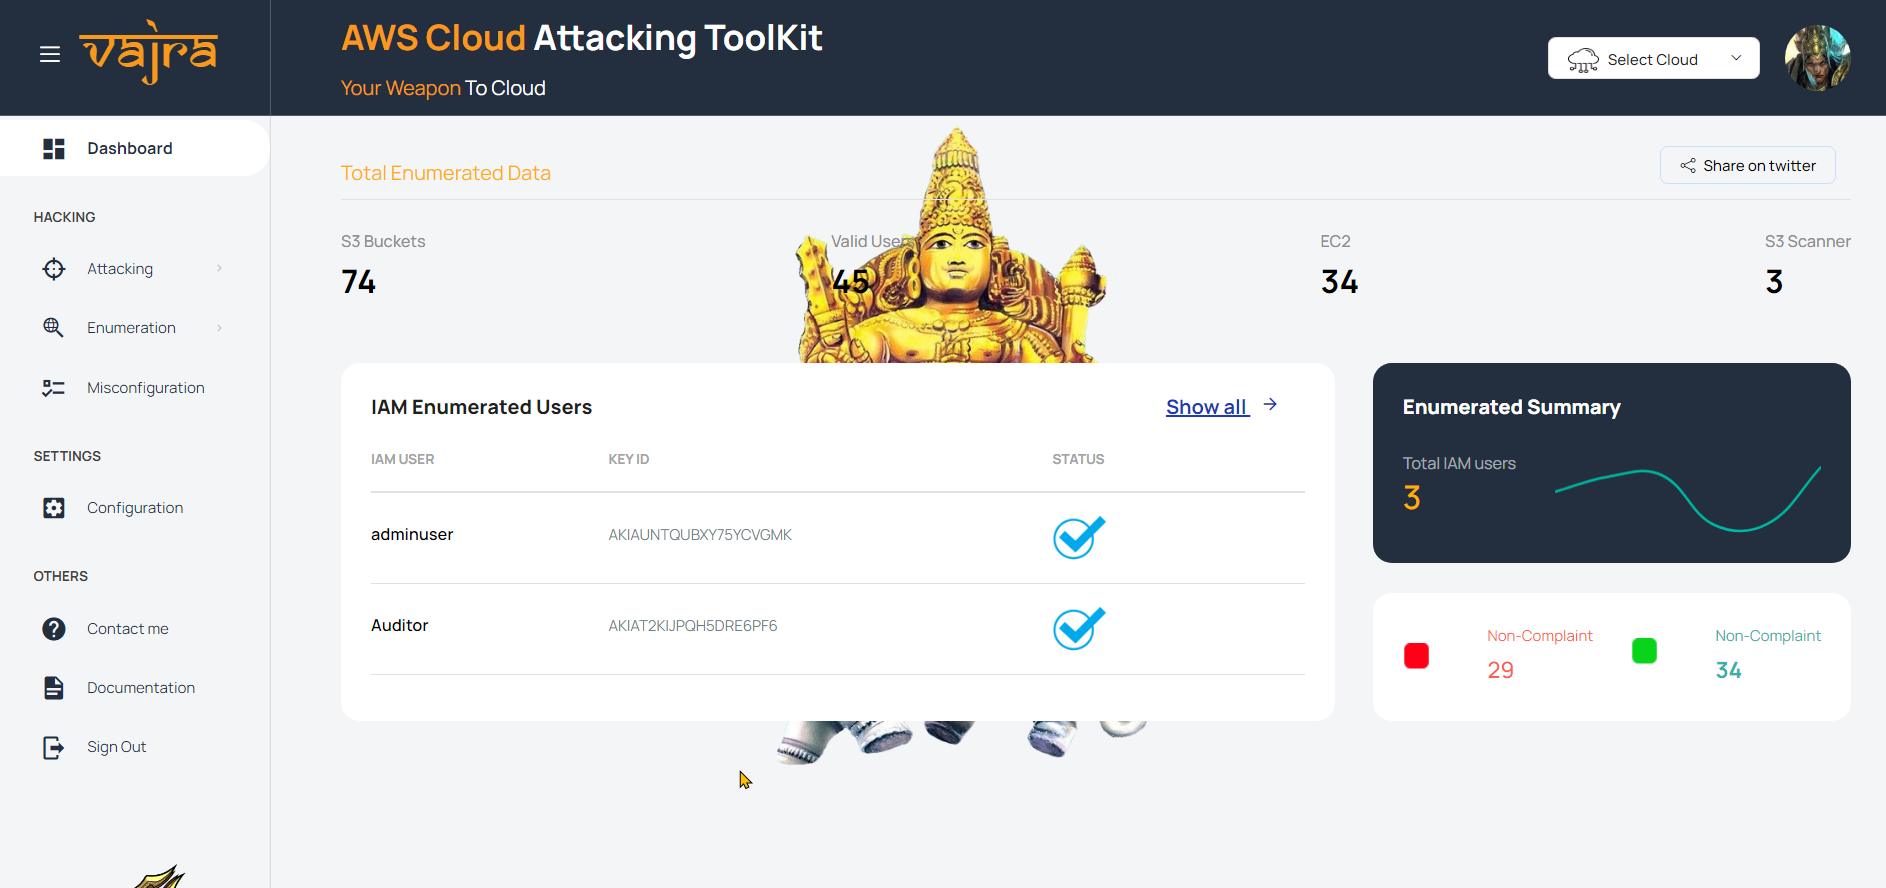 trouble-1/vajra
Vajra is a UI-based tool with multiple techniques for attacking and enumerating in the target's Azure and AWS environment. It features an intuitive…
 0xbytehunter/cve-2024-50967
DATAGERRY Broken Access Control
 randomrobbiebf/cve-2024-43919
YARPP <= 5.30.10 - Missing Authorization
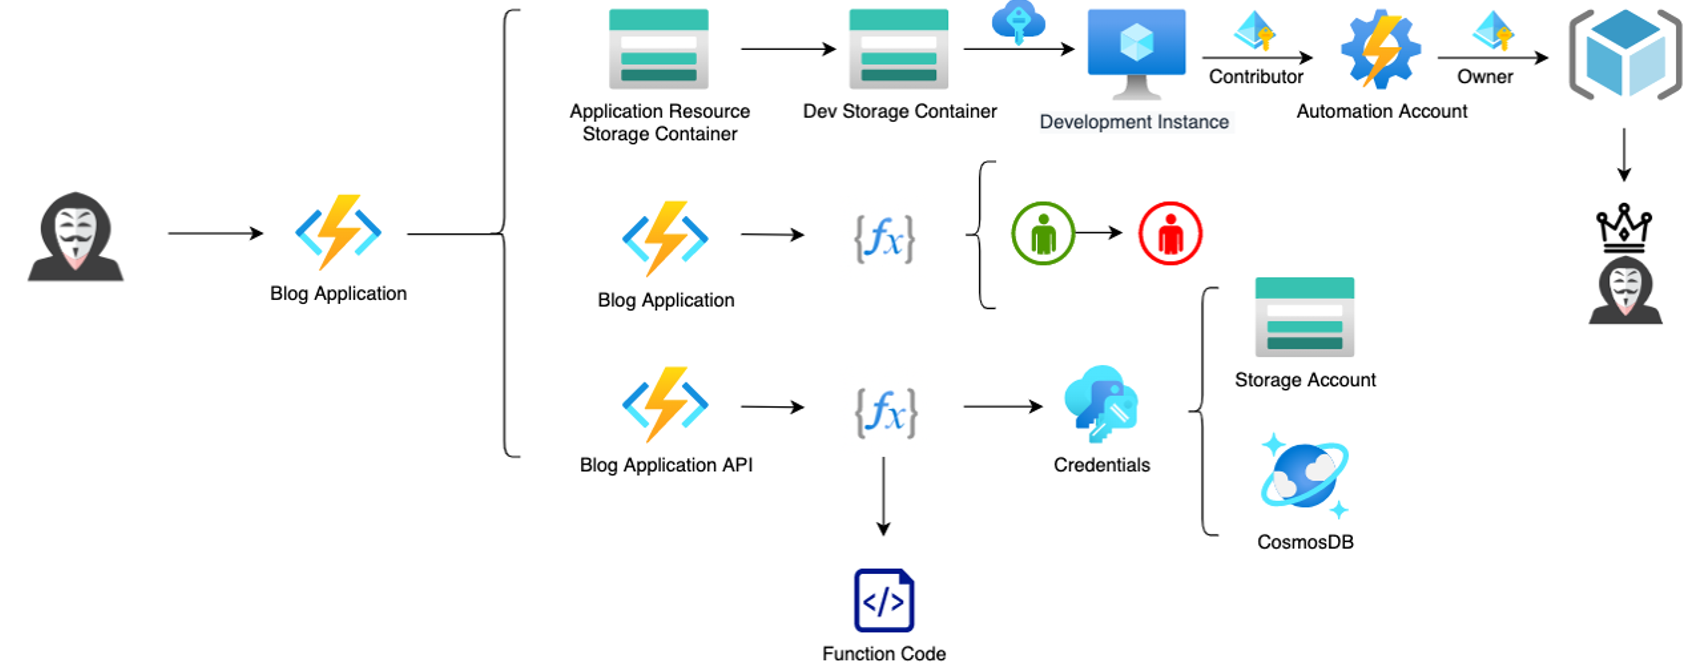 ine-labs/azuregoat
AzureGoat : A Damn Vulnerable Azure Infrastructure
 ine-labs/gcpgoat
GCPGoat : A Damn Vulnerable GCP Infrastructure
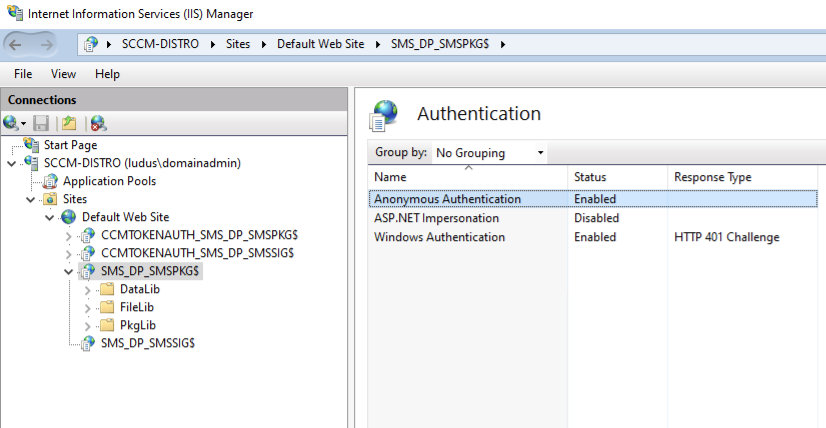 badsectorlabs/sccm-http-looter
Find interesting files stored on (System Center) Configuration Manager (SCCM/CM) shares via HTTP(s)
 legit-labs/legitify
Detect and remediate misconfigurations and security risks across all your GitHub and GitLab assets
 caffeinated-labs/cve-2023-36643
Proof-of-concept for CVE-2023-36643: an incorrect access control vulnerability in ITB-GmbH TradePro v9.5 that allows remote attackers to enumerate…
 shenhav12/cve-2024-22889-plone-v6.0.9
Proof-of-concept exploit for CVE-2024-22889, an incorrect access control vulnerability in Plone CMS v6.0.9 allowing remote attackers to view and list…