
java-html-sanitizer
 owasp/java-html-sanitizer
Takes third-party HTML and produces HTML that is safe to embed in your web application. Fast and easy to configure.
api-securitycode-analysisdefensive-tools+3
952
owasp/java-html-sanitizerTakes third-party HTML and produces HTML that is safe to embed in your web application. Fast and easy to configure.
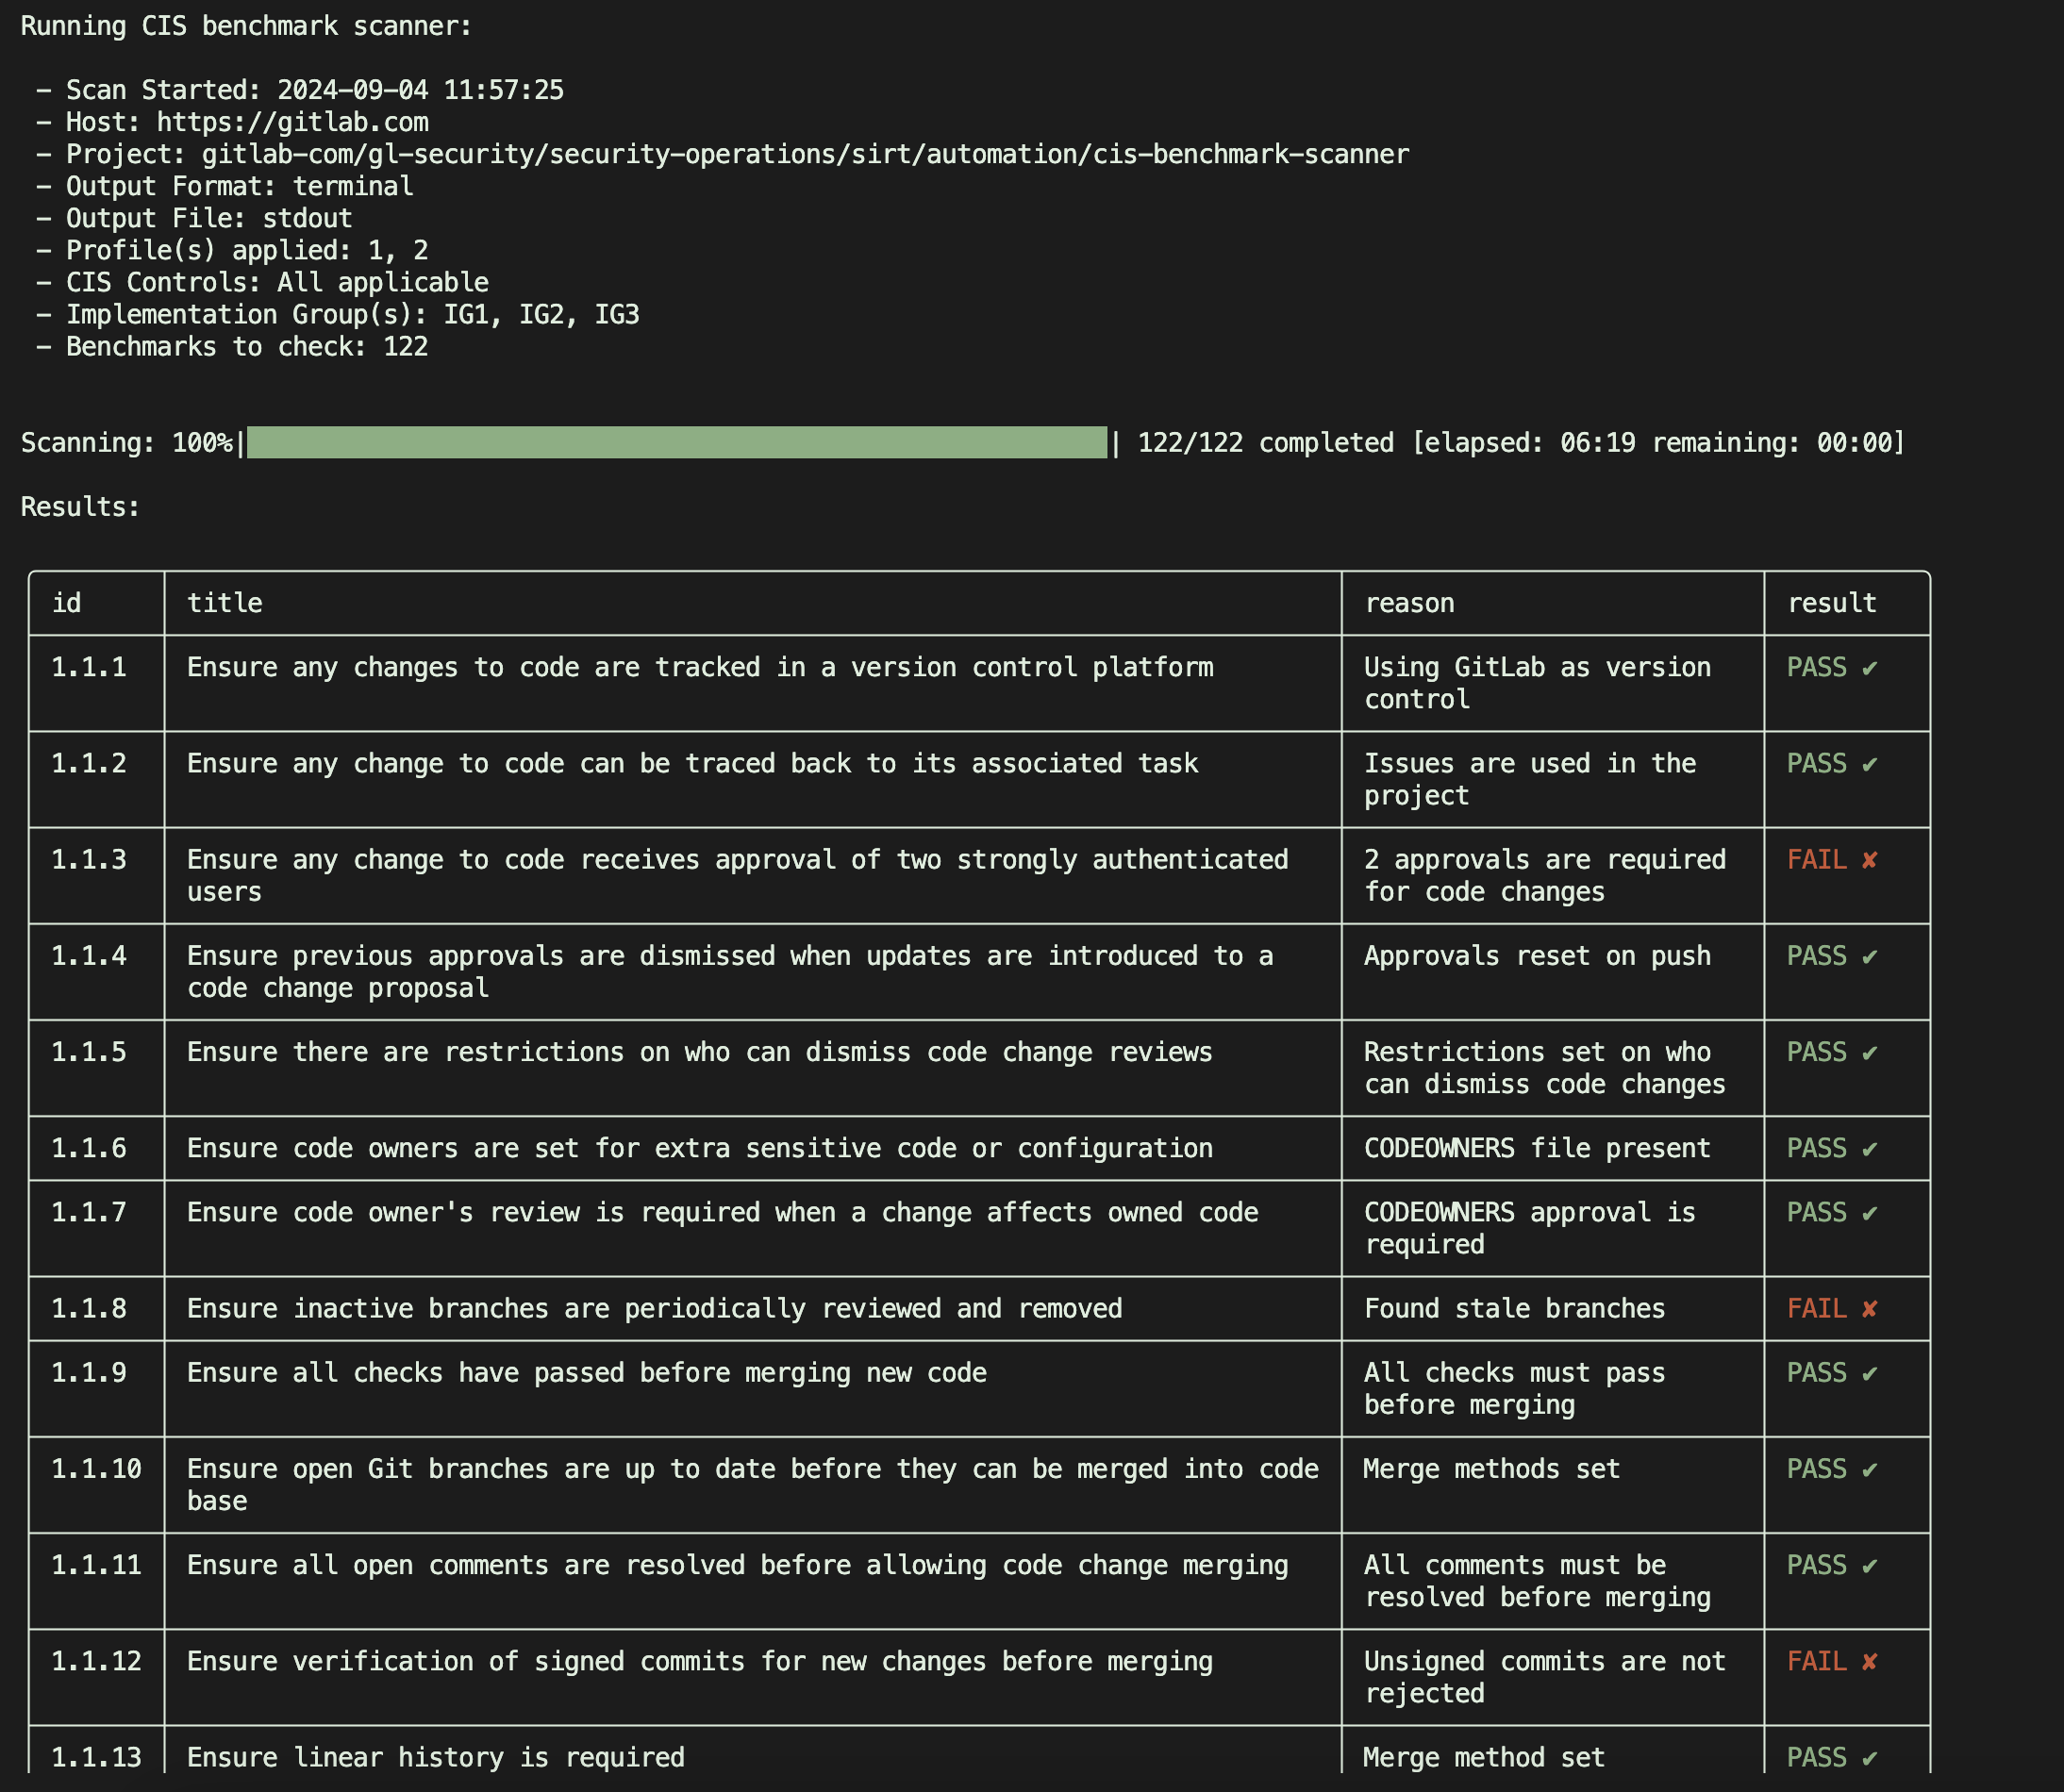
 gitlab-security-oss/cis/gitlabcis
Audits GitLab projects against the CIS GitLab Benchmark via read-only API checks, generating JSON reports on compliance and hardening recommendations.
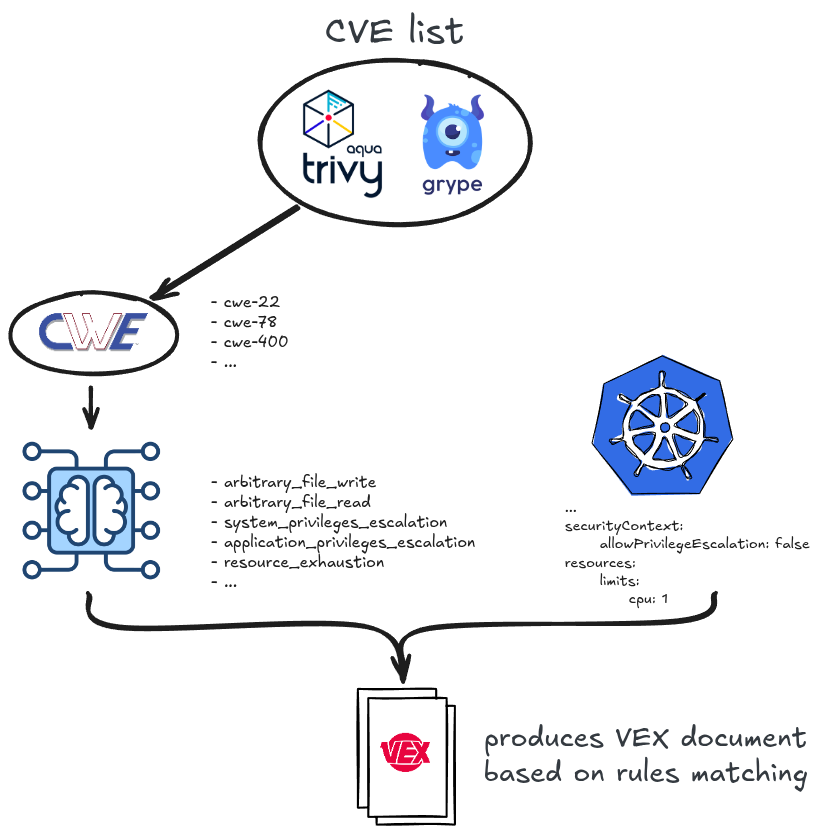 alegrey91/vex8s
Suppress vulnerabilities applying Kubernetes context to scans
 george0papasotiriou/cve-2026-21018-opc-ua-authentication-bypass-via-none-security-policy
Proof-of-concept exploit for OPC UA authentication bypass using None security policy, including a simulated server to demonstrate unauthorized…
 george0papasotiriou/cve-2026-21005-docker-registry-v2-schema-1-image-poisoning
Exploits CVE-2026-21005 by poisoning Docker Registry V2 Schema 1 manifests via unauthenticated pushes, enabling tag overwrite and supply-chain…
 coffinxp/google-api-key-scanner
Validates Google Maps API keys against 21 endpoints, revealing exposed services with PoC URLs, proxy support, and quiet mode for focused auditing.
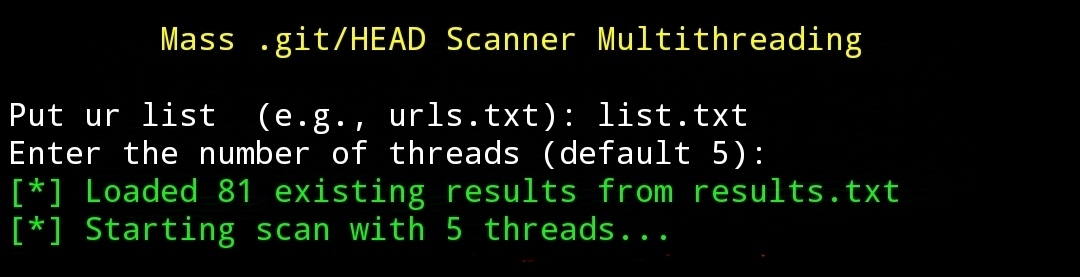 jenderal92/git-scan
This tool is designed to scan and identify whether a website has an exposed ".git" directory, which may contain sensitive information such as source…
 unicorn-hyh/cve-2026-31156
There is a path injection vulnerability in OpenPLC-v3, which arises from the program not performing any validity checks on the file path parameters…
 jyyjw/msxml4-remediation
PowerShell script to remediate CVE-2013-0007 by unregistering and renaming unsupported MSXML 4.0 DLLs, suppressing vulnerability scanner findings on…
 slicingmelon/haproxy-cve-2023-45539-poc
HAProxy-CVE-2023-45539-PoC
 dante01yoon/cve-2025-29927
Demonstration of CVE-2025-29927: Next.js middleware authentication bypass via x-middleware-subrequest header spoofing. Includes vulnerable and fixed…
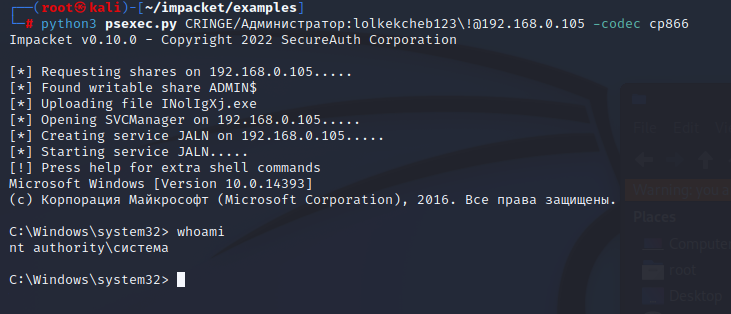 mzhmo/psexec_noinstall
Repository contains psexec, which will help to exploit the forgotten pipe
 akabe1/oauthscan
Burp Suite Extension useful to verify OAUTHv2 and OpenID security
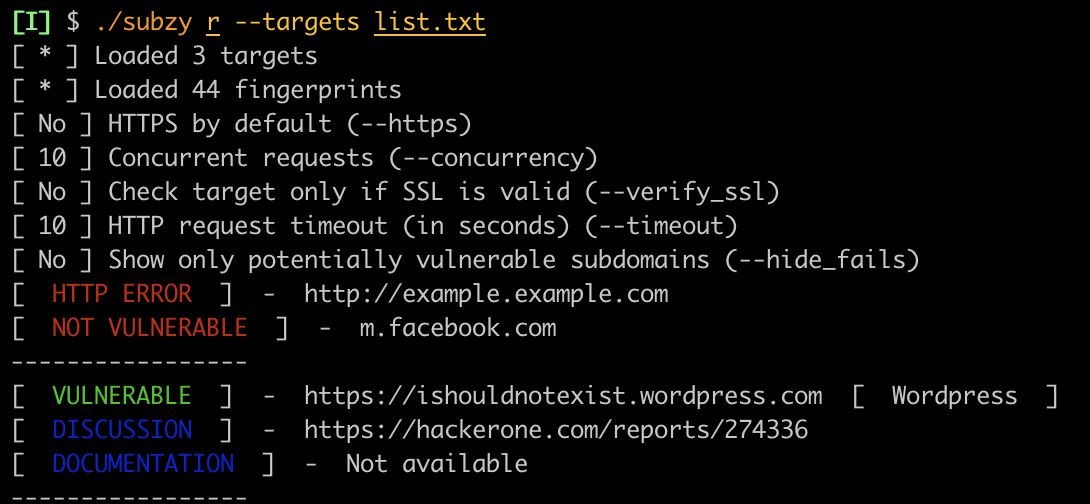 pentestpad/subzy
Subdomain takeover vulnerability checker
 mbadanoiu/cve-2021-42562
CVE-2021-42562: Improper Access Control in MITRE Caldera
 nccgroup/scoutsuite
Multi-cloud security auditing tool that leverages cloud provider APIs to gather configuration data, assess security posture, and generate HTML…
 alaatk/cve-2024-27462
Wondershare MobileTrans 4.5.6 - Unquoted Service Path