
prowler
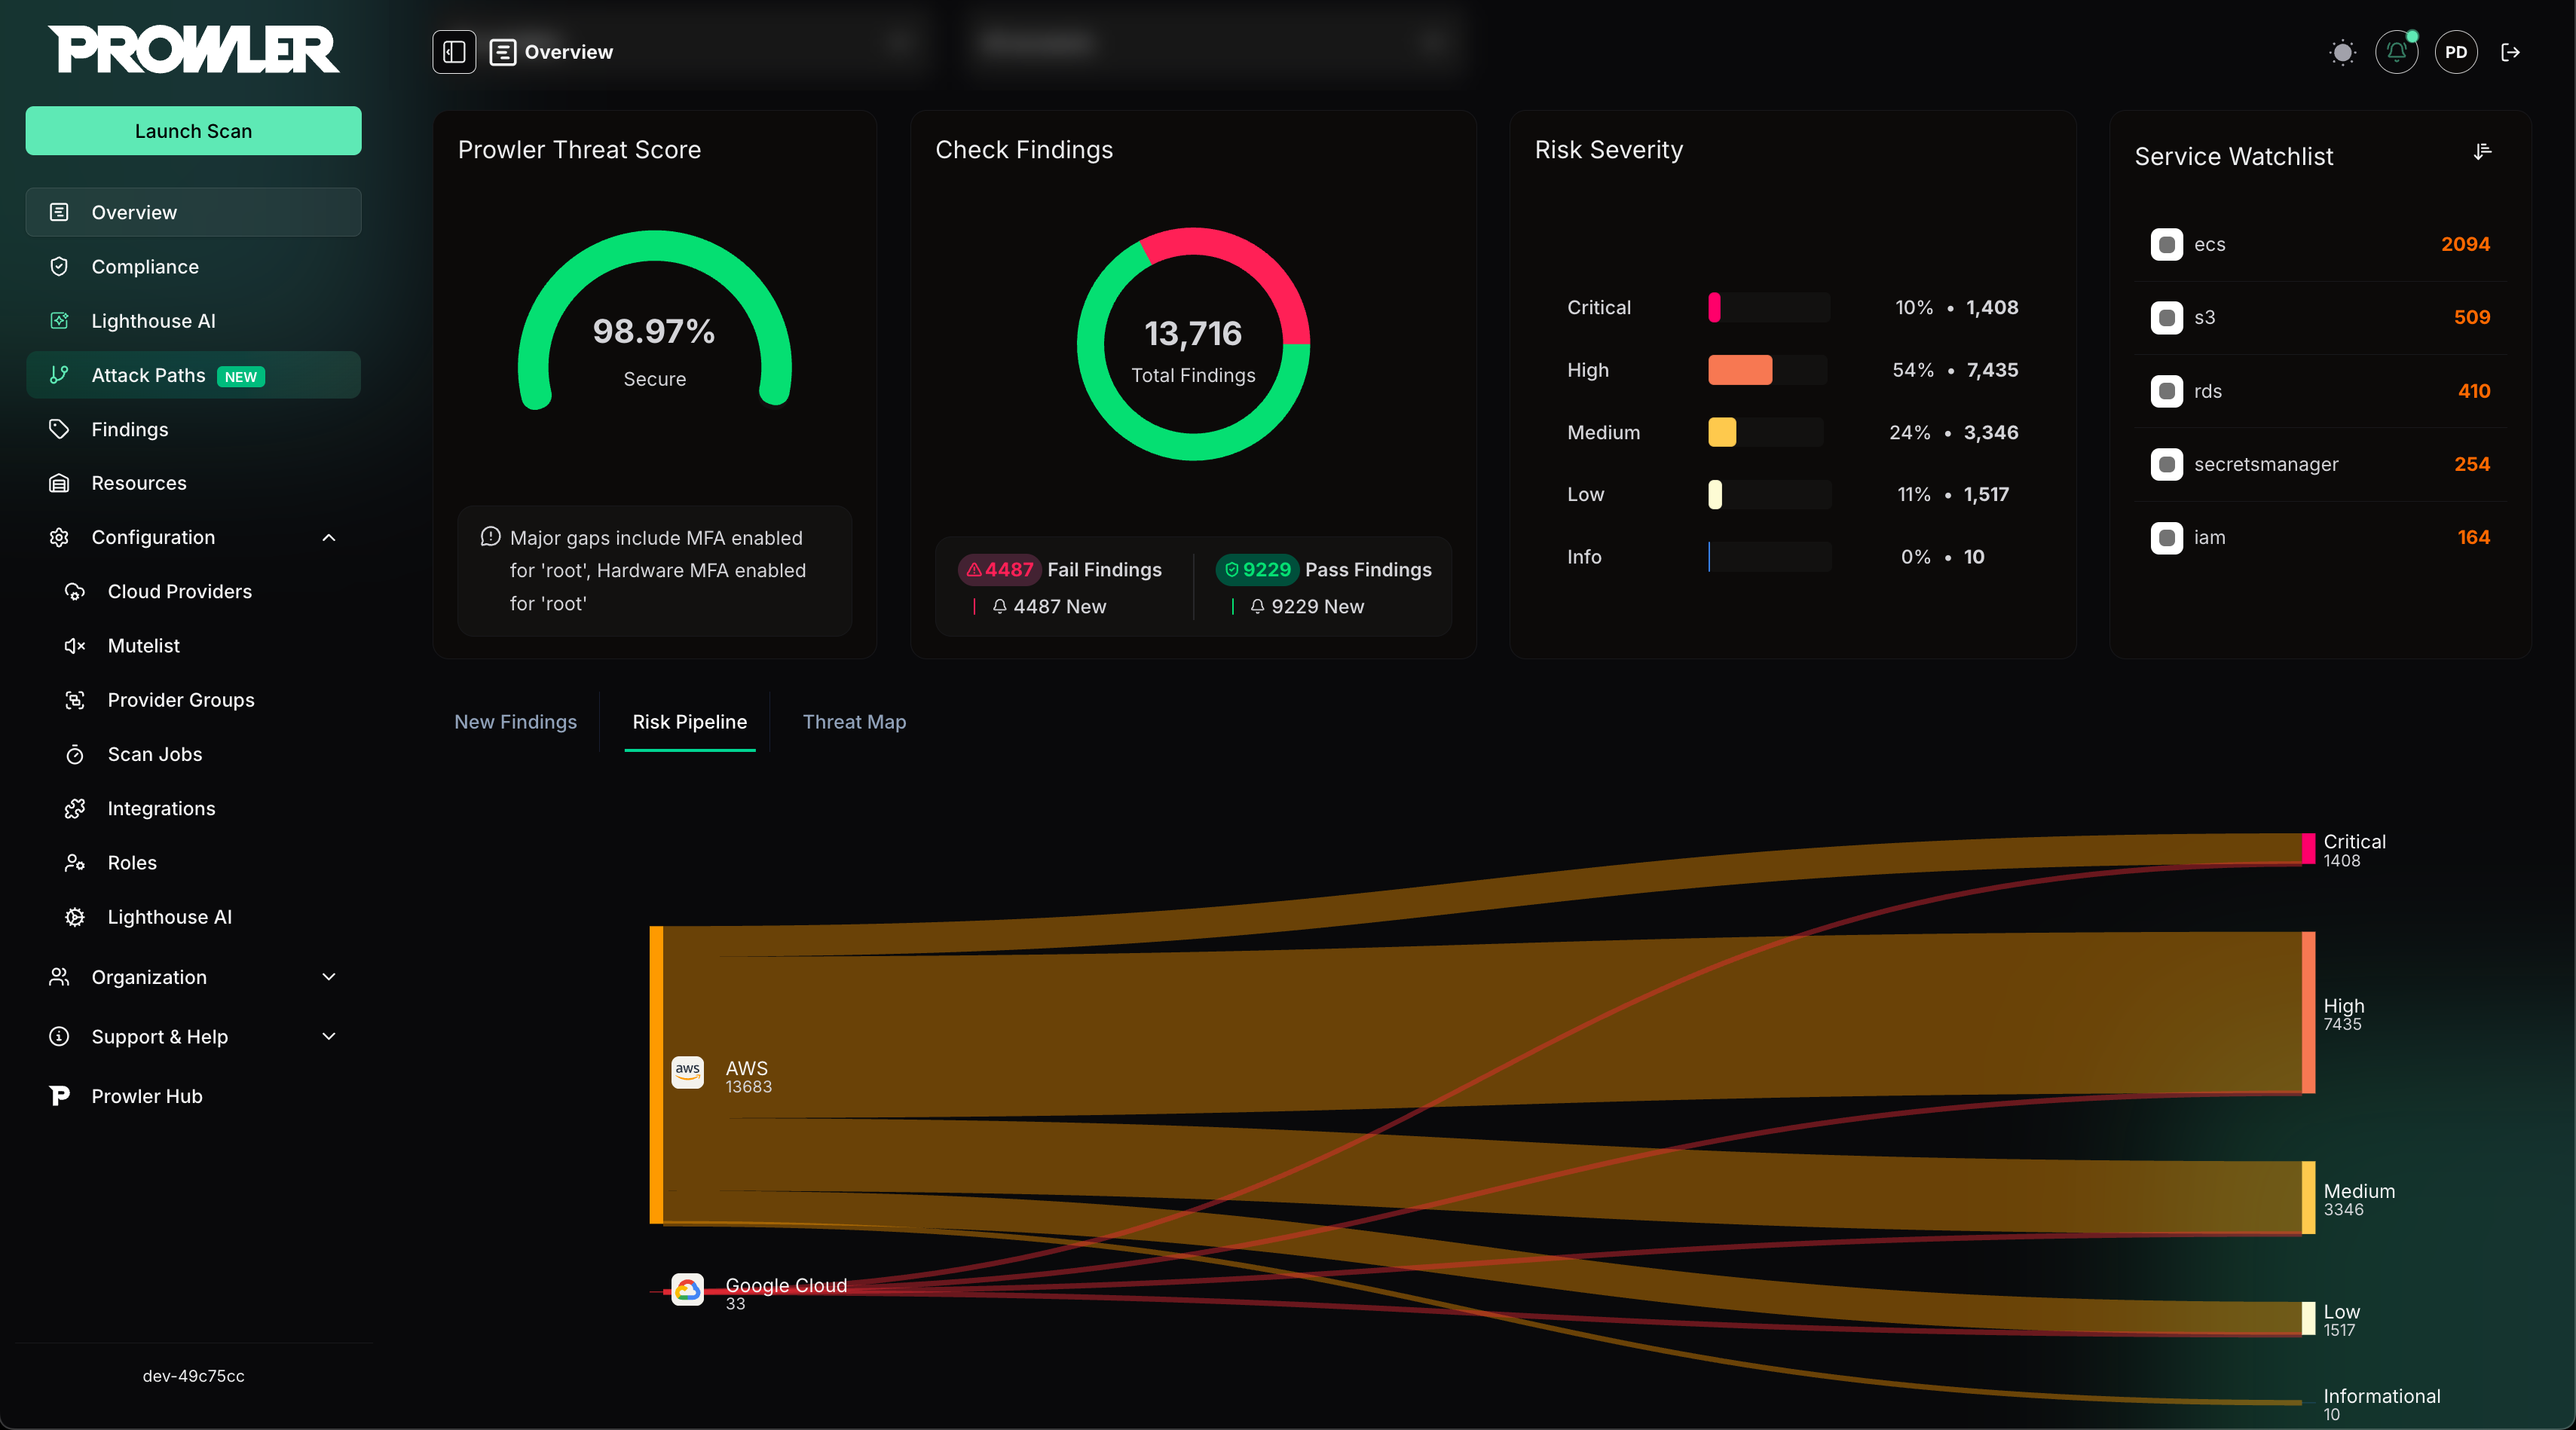
Prowler is the world’s most widely used open-source cloud security platform that automates security and compliance across any cloud environment.…

Prowler is the world’s most widely used open-source cloud security platform that automates security and compliance across any cloud environment.…

Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…

Open source CSPM for Azure - scan for misconfigurations and quantum-unsafe cryptography, map findings to CIS/NIST/ISO27001/SOC2, and fix them with…

Web interface for the nftables firewall on Linux, written in Go. The apply undoes itself after 120 seconds unless you confirm it — you cannot lock…

A fast universal code security scanner, written in Rust. Batteries included: supports 14 languages, TUI for triage, secrets, post-quantum audits,…

Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…

Tree-sitter based static vulnerability scanner with pattern matching and taint-flow analysis for multi-language source code. Outputs findings as…

This chef cookbook provides security configuration for mysql.

An anonymizer tool for replacing PII and similar data in dev/test databases copied from production

VampSecure Labs: FortiOS CVE scanner (CVE-2018-13379, CVE-2022-40684, CVE-2023-27997, CVE-2024-21762)

Proof-of-concept exploit for XenForo CVE-2026-73318, an authorization bypass allowing ACP administrators to trigger site-wide policy re-agreement.…

Full-stack platform for authorized web application security scanning with a detector-based engine, async Celery workers, and a React dashboard for…

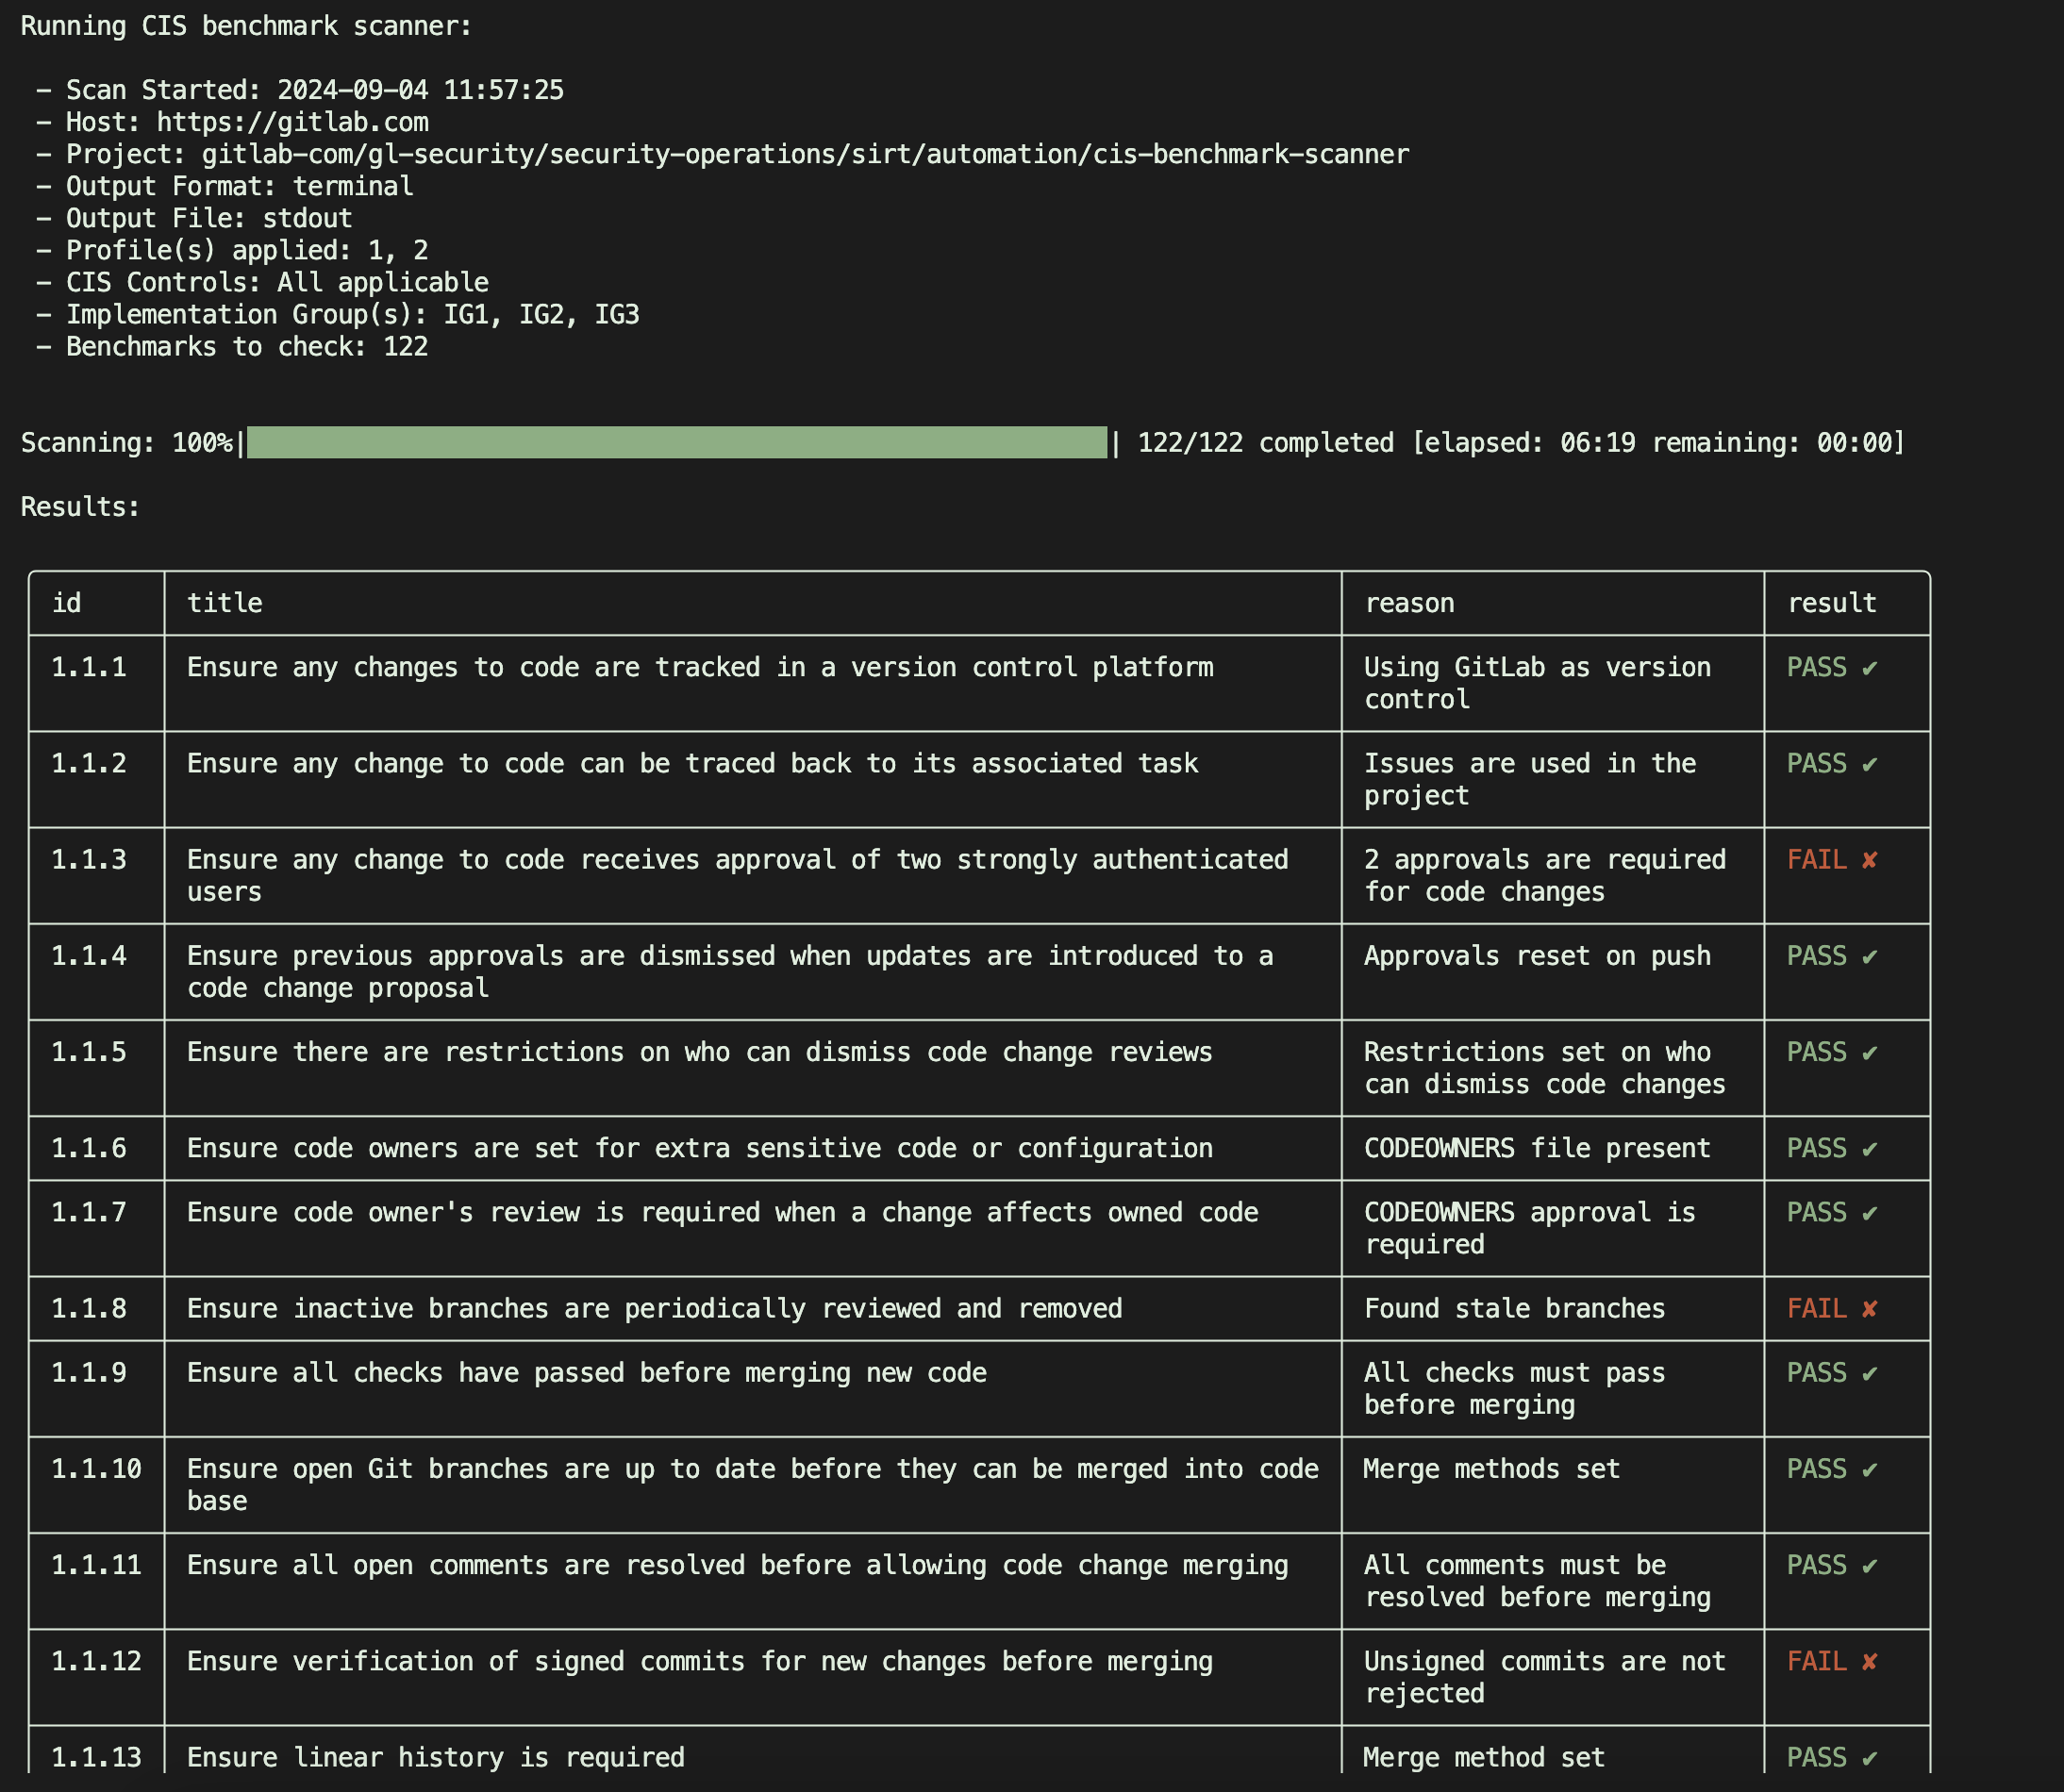
Audits GitLab projects against the CIS GitLab Benchmark via read-only API checks, generating JSON reports on compliance and hardening recommendations.

Scanner for CVE-2024-40725 Apache HTTP Server source-code disclosure; probes direct and subrequest paths, fingerprints affected versions, and outputs…

Standalone PoC for unauthenticated RTMP publish in SRS media servers; verifies the vulnerability, supports HTTP API side-channel check, and enables…

PoC exploit for CVE-2026-73678: unauthenticated RCE in MindsDB Cowork via attacker-supplied LLM key and unsandboxed scratchpad exec to run OS…

Scanner: CVE-2025-34291 Langflow Origin Validation Error / CORS Misconfiguration — Python checker (CISA KEV)

Scanner: CVE-2026-41091/45498 Microsoft Defender LPE/DoS — Python scanner for Windows Defender privilege escalation (CISA KEV)