
WP-CVE-2026-87902
 svtagan/wp-cve-2026-87902
Read-only PHP diagnostic script that checks WordPress version, core checksums, extra PHP files, and known plugin paths for CVE-2026-87902 exposure…
configuration-auditingdefensive-toolsincident-response+7
svtagan/wp-cve-2026-87902Read-only PHP diagnostic script that checks WordPress version, core checksums, extra PHP files, and known plugin paths for CVE-2026-87902 exposure…
 nt2dev/cve-2026-36213-poc
CVE-2026-36213: MEmu Android Emulator 9.2.7.0 Local Privilege Escalation
 minhhk68/cve-2026-13736
Proof-of-concept exploit and technical advisory for an unauthenticated member PII disclosure in a WordPress REST API directory plugin, including…
 xuwu-xuwu/cve-2026-68004
Standalone PoC for unauthenticated RTMP publish in SRS media servers; verifies the vulnerability, supports HTTP API side-channel check, and enables…
 hunt-benito/bring-your-own-key-cve-2026-73678-unauthenticated-rce-in-mindsdb-cowork
PoC exploit for CVE-2026-73678: unauthenticated RCE in MindsDB Cowork via attacker-supplied LLM key and unsandboxed scratchpad exec to run OS…
 ridhinva/defender-privilege-escalation-scanner
Scanner: CVE-2026-41091/45498 Microsoft Defender LPE/DoS — Python scanner for Windows Defender privilege escalation (CISA KEV)
 johenlastgen-jlg/cve-2026-11961
CVE-2026-11961 — UserRegistration: WordPress User Registration <= 5.2.2 Privilege Escalation. Misconfigured Membership Roles → Unauthenticated Admin…
 qianlijaingshan/milvus-auth-audit
Milvus 认证安全检测脚本:CVE-2025-64513 (sourceid后门) / CVE-2026-26190 (/expr弱token) / 内部端口53100
 shinthink/cve-2026-61424
DJ-Classifieds Joomla Component Unauthenticated File Upload RCE. 3-string filter bypass via PHP short tags. CVSS 10.0 | CWE-434 | com_djclassifieds <…
 chpratik/nginx_2026_cve_bundle_cti_report
Covered CVEs: CVE-2026-28755, CVE-2026-42926, CVE-2026-9256, CVE-2026-42055, CVE-2026-42533
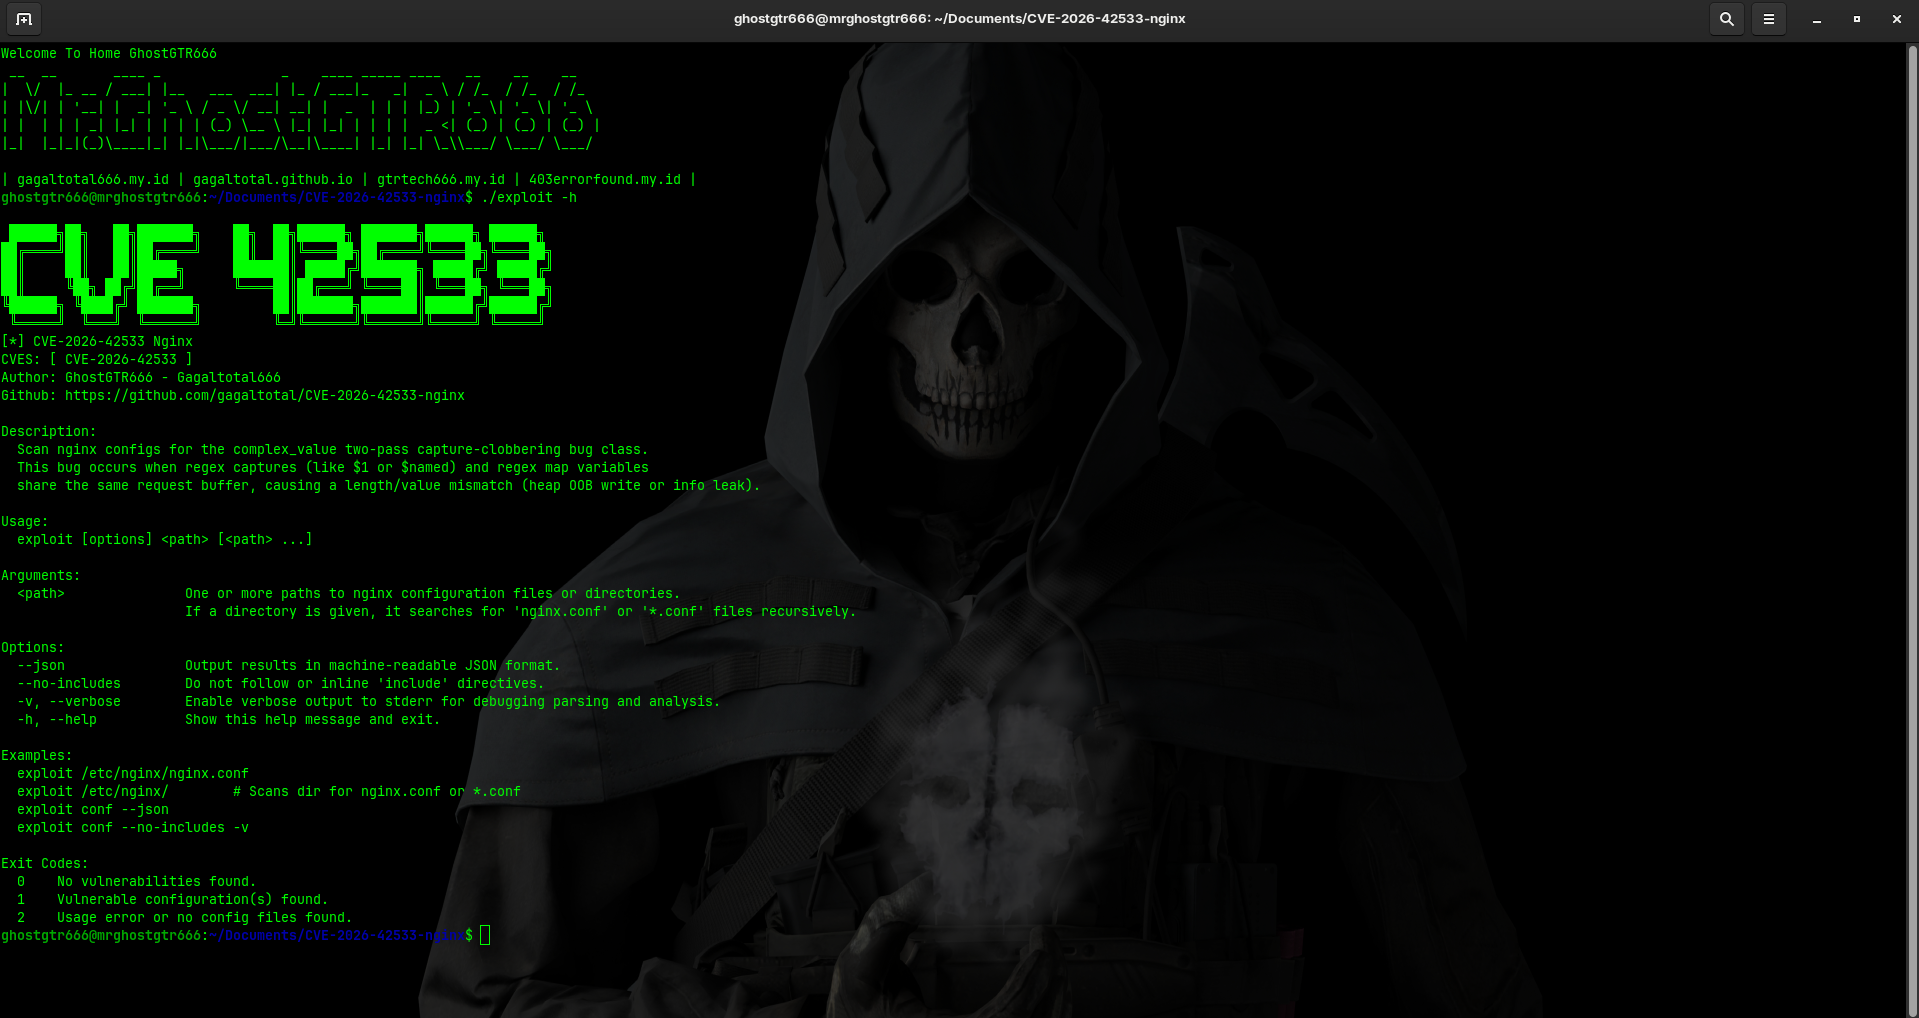 gagaltotal/cve-2026-42533-nginx
CVE-2026-42533 Nginx
 huseyn0vs/cve-2026-16540-simplyscheduleappointments
CVE-2026-16540 — Simply Schedule Appointments < 1.6.12.6 Unauthenticated Appointment Data Disclosure and Mass Deletion
 mrmtwoj/fix-cve-2026-60137-cve-2026-63030-in-wordpress
CVE-2026-60137Temporary Emergency Mitigation for CVE-2026-60137 & CVE-2026-63030 (wp2shell)
 csinexus/mcpshield
Drop-in fix for the unpatched MCP STDIO command-injection flaw (CVE-2026-30623 family)
 j4ck3lsyn-gen2/cve-2026-13768
Azure IoT Hub where exposure of an owner-level Shared Access Key enables unauthenticated remote code execution (RCE) against connected IoT devices.…
 tazmidev/cve-2026-53571
CVE-2026-53571 `server.fs.deny` bypass on Windows alternate paths PoC.
 oscerd/cve-2026-40022
Reproducer for CVE-2026-40022: Apache Camel camel-platform-http-main authentication bypass on non-root context paths
 michaeladamgroberman/cve-2026-54477
CVE-2026-54477: Admin Panel Missing Security Headers (clickjacking/XSS) - Gardyn (ICSA-26-183-03)