
CVE-2024-34474
 alaatk/cve-2024-34474
Clario through 2024-04-11 for Windows Desktop has weak permissions for %PROGRAMDATA%\Clario and tries to load DLLs from there as SYSTEM.
exploitationmisconfigurationprivilege-escalation+1
alaatk/cve-2024-34474Clario through 2024-04-11 for Windows Desktop has weak permissions for %PROGRAMDATA%\Clario and tries to load DLLs from there as SYSTEM.
 burjoy/cve-2024-40275_scanner
Scanner for CVE-2024-40725 Apache HTTP Server source-code disclosure; probes direct and subrequest paths, fingerprints affected versions, and outputs…
 trevorputbrese/cve-2024-38819-lab
Hands-on lab demonstrating CVE-2024-38819 Spring Framework path traversal vulnerability with vulnerable and patched Spring Boot deployments for…
 sudo-wp/sudowp-dropzone-elementor
Secure fork of Startklar Elementor Addons. Patched CVE-2024-5153 & File Upload vulnerabilities.
 helleflo1312/orchestrated-powershell-for-cve-2023-24932
Automated PowerShell orchestrator for applying Secure Boot mitigations against CVE-2023-24932 (BlackLotus). Handles registry changes, reboots,…
 mrk336/cve-2024-10220-kubernetes-gitrepo-volume-vulnerability
CVE-2024-10220 reveals a critical flaw in Kubernetes’ deprecated gitRepo volume type, allowing attackers to execute arbitrary commands via malicious…
 first-roman/sprig-mvc-demo-patch
This demo application partially covers the vulnerability CVE-2024-38828
 spyata123/cve-2024-12008-information-exposure-vulnerability-in-w3-total-cache
CVE-2024-12008 information exposure vulnerability in W3 Total Cache
 padayali-jd/pollyscan
A specialized vulnerability scanner designed to detect CVE-2024-38526, the Polyfill.io Supply Chain Attack, helping organizations identify and…
 wubinworks/magento2-cosmic-sting-patch
An alternative solution(as a Magento 2 extension) to fix the XXE vulnerability CVE-2024-34102(aka Cosmic Sting). If you cannot upgrade Magento or…
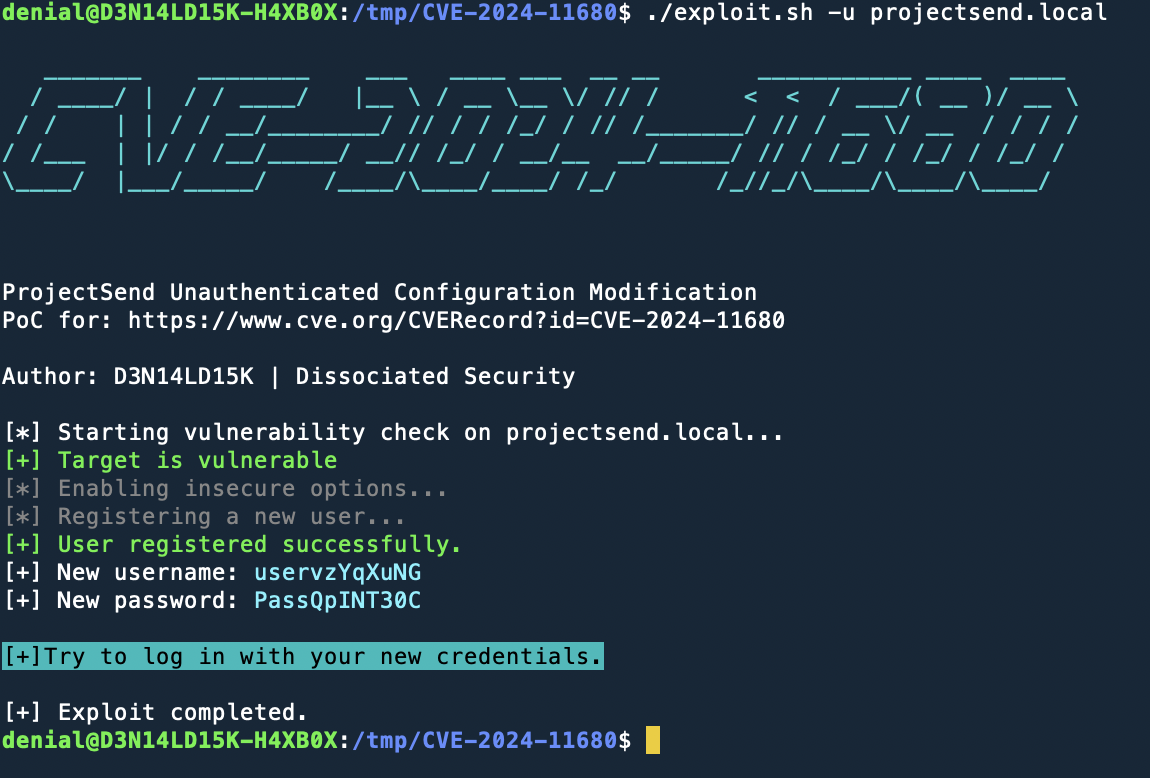 d3n14ld15k/cve-2024-11680_poc_exploit
This repository contains a Proof of Concept (PoC) exploit for CVE-2024-11680, a critical vulnerability in ProjectSend r1605 and older versions. The…
 ekcrsm/cve-2024-23733
Proof-of-concept exploit for CVE-2024-23733: Incorrect Access Control in Software AG webMethods Integration Server 10.15.0 allowing remote attackers…
 castro-ian/cve-2024-4573-mitigation-script
Detects NTLM authentication status by checking LmCompatibilityLevel registry value to assess exposure to CVE-2024-43451 and mitigate credential relay…
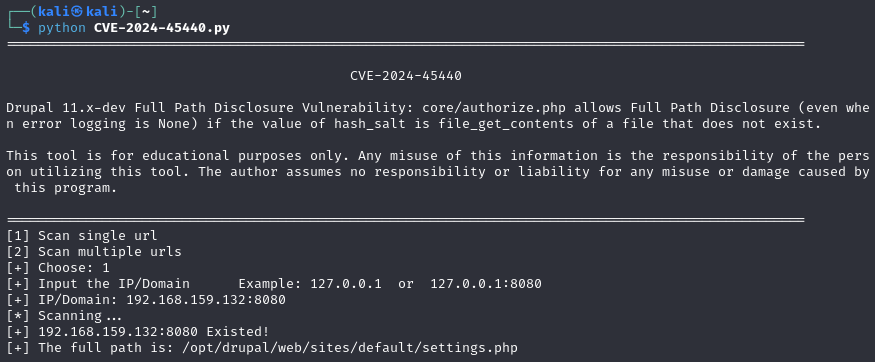 w0r1i0g1ht/cve-2024-45440
Drupal CVE-2024-45440
 codepontiff/next_js_poisoning
The CVE-2024-46982 is cache poisoning of next_js some site have API to load their image
 g-u-i-d/cve-2024-10449-patch
Patch for CVE-2024-10449: replaces vulnerable loginAction.php with a hardened version that requires database configuration for secure authentication.
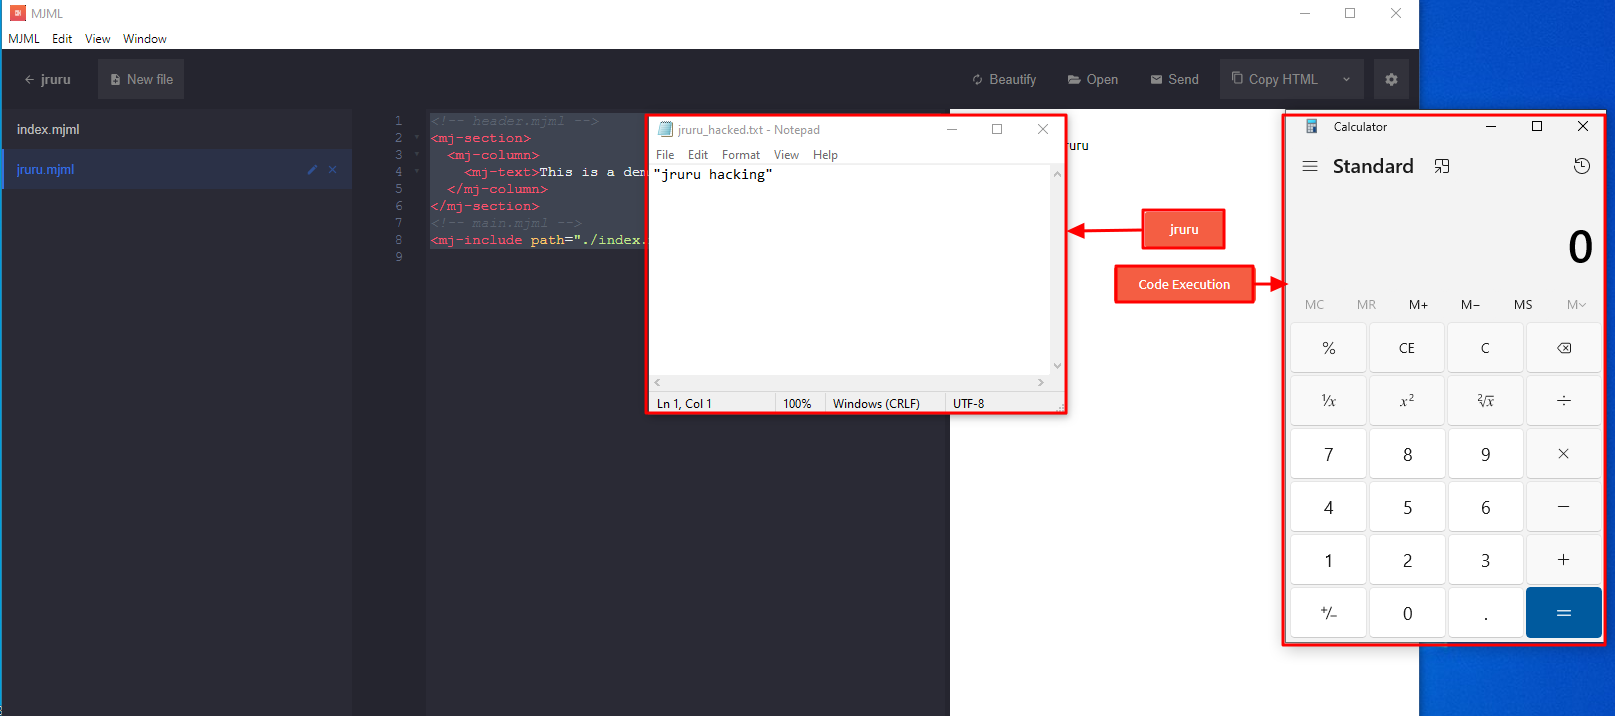 eqstlab/cve-2024-25293
mjml-app v3.0.4 & 3.1.0-beta RCE exploit
 juanschallibaum/cve-2024-38473-nuclei-template
Nuclei template to detect Apache servers vulnerable to CVE-2024-38473