
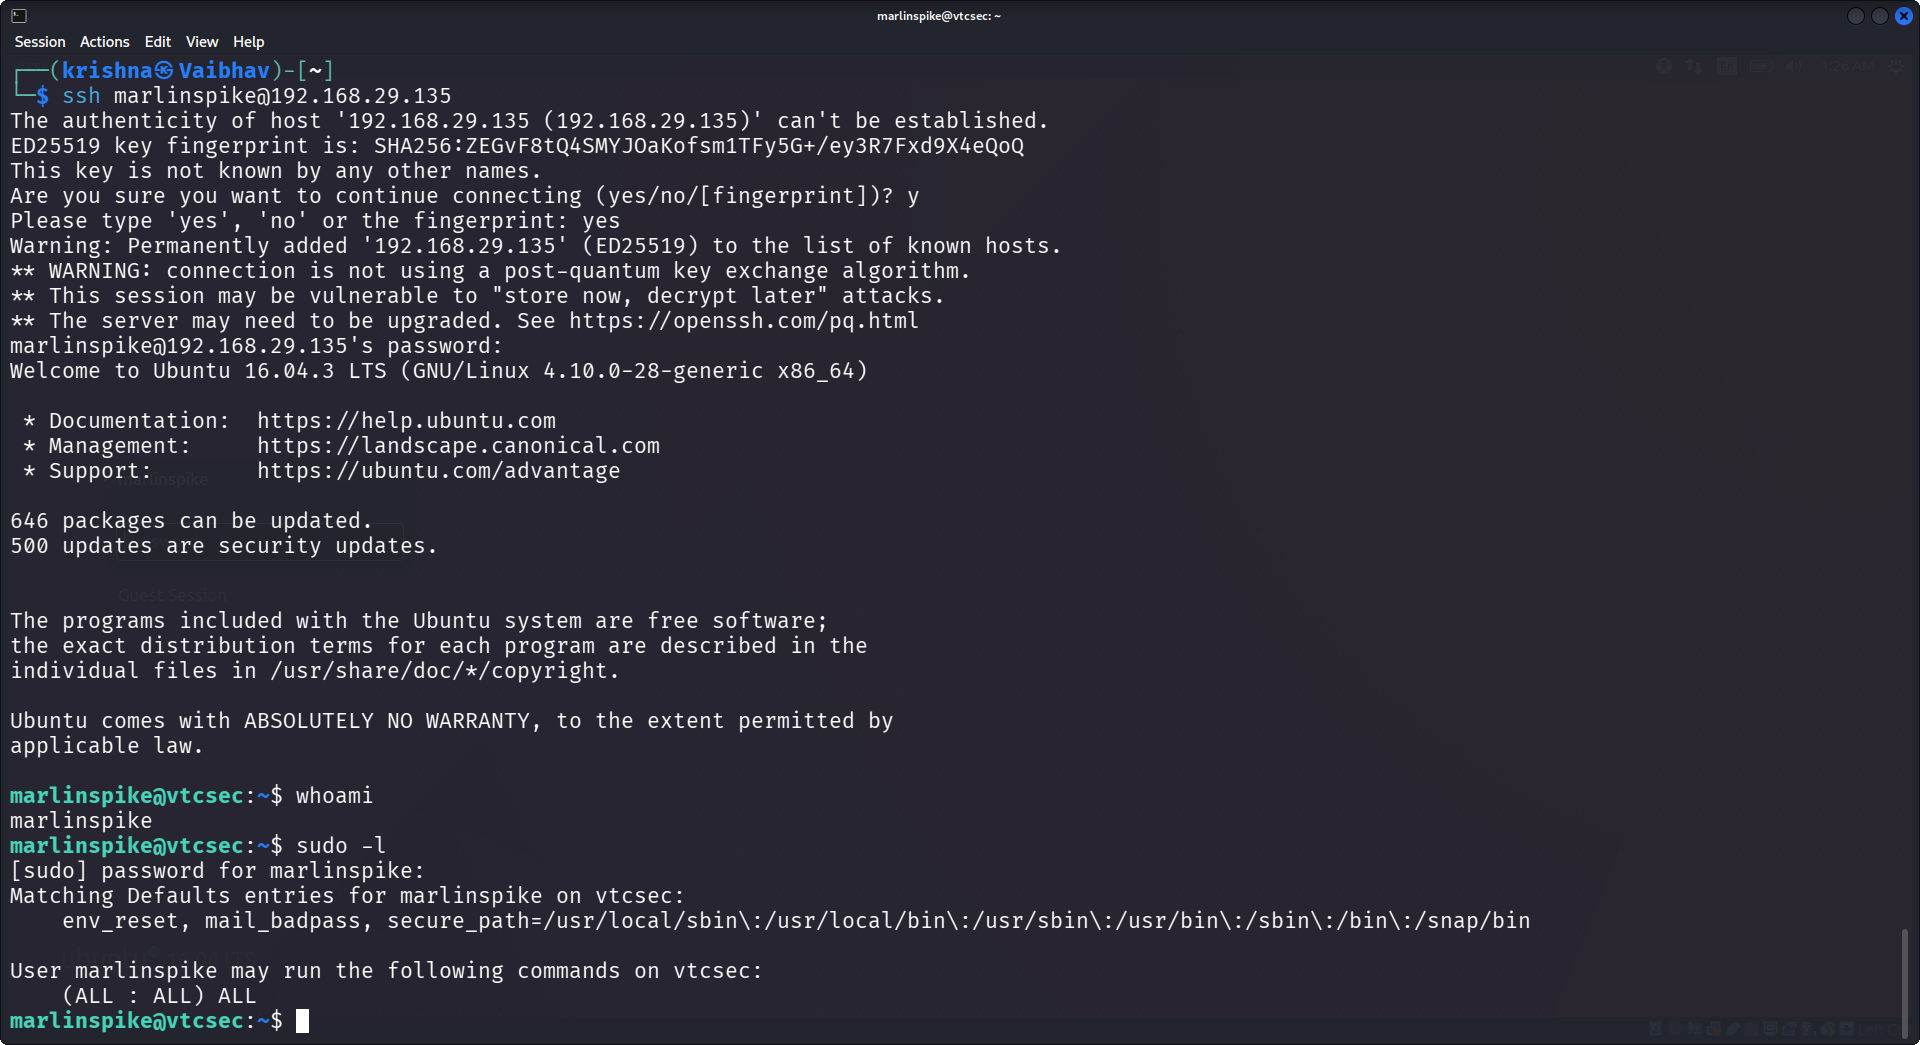
ubuntu-privesc-lab
 vaibhavkrishna12004/ubuntu-privesc-lab
Full penetration testing workflow: credential brute force, SSH access and privilege escalation (CVE-2021-4034)
educationexploitationlabs-practice+8
vaibhavkrishna12004/ubuntu-privesc-labFull penetration testing workflow: credential brute force, SSH access and privilege escalation (CVE-2021-4034)
 sudo-wp/sudowp-adminer
A secure, zero-trust database management tool for WordPress. Fixes critical SSRF vulnerabilities (CVE-2021-21311) by enforcing local connections only.
 axisops/cve-2021-44228
log4j mitigation work
 moften/cve-2021-21424
El WebProfiler de Symfony expone rutas internas del servidor si no está deshabilitado en producción
 fe-ax/tf-cve-2021-36782
A Terraform module to launch Rancher 2.6.6 for blog article about CVE-2021-36782
 digital-dev/log4j-cve-2021-44228-remediation
This powershell script is intended to be used by anyone looking to remediate the Log4j Vulnerability within their environment. It can target multiple…
 name/log4j-scanner
Discover Log4Shell vulnerability [CVE-2021-44832]
 ekamsinghwalia/detection-and-mitigation-script-for-cve-2021-42717
Detection and Mitigation script for CVE-2021-42717 -> ModSecurity DoS Vulnerability in JSON Parsing
 ekamsinghwalia/mitigation-apache-cve-2021-41773-
Mitigation/fix of CVE-2021-41773 A Path Traversal And File Disclosure Vulnerability In Apache
 captain-v-hook/poc-for-cve-2021-38540-
Missing Authentication on Critical component CVE-2021-38540
 emad-almousa/cve-2021-35576
Proof-of-concept exploit for CVE-2021-35576 demonstrating bypass of Oracle Unified Audit policy via a security vulnerability in database auditing.
 irgoncalves/f5-waf-quick-patch-cve-2021-44228
This tool creates a custom signature set on F5 WAF and apply to policies in blocking mode
 0xdeku/cve-2021-42671
CVE-2021-42671 - Broken access control vulnerability in the Engineers online portal system.
 hadimed/dsl-2750u-full-chain
CVE-2021-3707 , CVE-2021-3708
 fazmin/vcenter-server-workaround-script-cve-2021-44228
Script - Workaround instructions to address CVE-2021-44228 in vCenter Server
 lhotari/pulsar-docker-images-patch-cve-2021-44228
Patch Pulsar Docker images with Log4J 2.17.1 update to mitigate Apache Log4J Security Vulnerabilities including Log4Shell
 1lann/log4shelldetect
Rapidly scan filesystems for Java programs potentially vulnerable to Log4Shell (CVE-2021-44228) or "that Log4j JNDI exploit" by inspecting the class…
 dskho/cve-2021-45232
Proof-of-concept scanner for CVE-2021-45232, targeting unauthenticated API access and default credentials in Apache APISIX Dashboard.