
CVE-2026-32662
 xf-secops/cve-2026-32662
Advisory detailing active debug code in production Gardyn Home Kit cloud API, exposing development endpoints and embedded credentials, with…
cloud-securityconfiguration-auditingiot-security+3
xf-secops/cve-2026-32662Advisory detailing active debug code in production Gardyn Home Kit cloud API, exposing development endpoints and embedded credentials, with…
 olafhartong/mde-auditcheck
MDE relies on some of the Audit settings to be enabled
 subat0mik/misconfiguration-manager
Misconfiguration Manager is a central knowledge base for all known Microsoft Configuration Manager tradecraft and associated defensive and hardening…
 badsectorlabs/sccm-http-looter
Find interesting files stored on (System Center) Configuration Manager (SCCM/CM) shares via HTTP(s)
 nccgroup/aws-inventory
Discover resources created in an AWS account.
 shoucheng3/spring-projects__spring-framework_cve-2022-22965_5-2-19-release
Exploit for CVE-2022-22965 (Spring4Shell) targeting Spring Framework versions vulnerable to remote code execution via classLoader manipulation.
 danielwep/cve-netscalerfilesystemcheck
This script checks the Citrix Netscaler if it has been compromised by CVE-2019-19781 attacks and collects all file system information
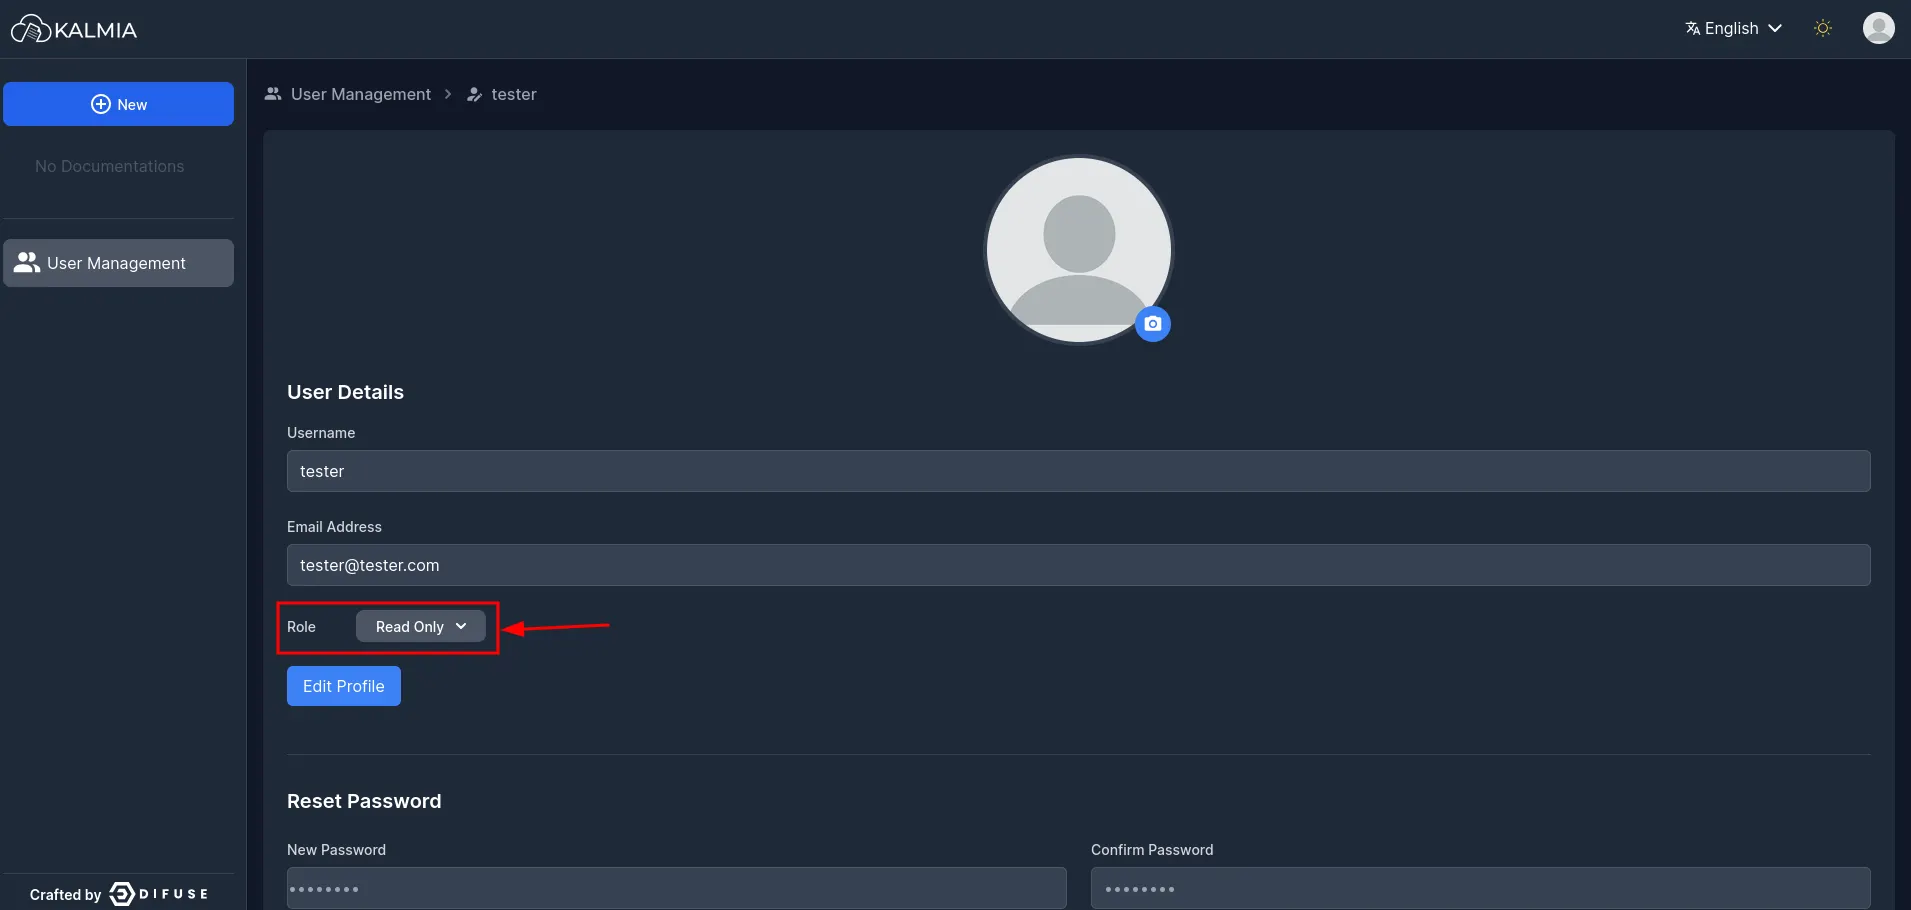 noxurge/cve-2025-65900
DifuseHQ Kalmia CMS version 0.2.0 contains an Incorrect Access Control vulnerability in the /kal-api/auth/users API endpoint. Due to insufficient…
 nxploited/cve-2024-56071
Simple Dashboard <= 2.0 - Unauthenticated Privilege Escalation
 shenhav12/cve-2024-22889-plone-v6.0.9
Proof-of-concept exploit for CVE-2024-22889, an incorrect access control vulnerability in Plone CMS v6.0.9 allowing remote attackers to view and list…
 nikip72/cve-2021-39273-cve-2021-39274
Two security issues identified in Sn1per v9.0 free version by XeroSecurity
 wolfssl/wolfcose
A fast, portable, and lightweight COSE + CBOR implementation for embedded systems. Supports PQC, FIPS 140-3, DO-178, and MISRA C. Powered by wolfSSL.
 seqred-s-a/cve-2020-10551
Privilege escalation in QQBrowser
 comparedarray/printix-cve-2022-25089
An "Incorrect Use of a Privileged API" vulnerability in PrintixService.exe, in Printix's "Printix Secure Cloud Print Management", Version 1.3.1106.0…
 irgoncalves/f5-waf-enforce-sig-cve-2021-44228
This enforces signatures for CVE-2021-44228 across all policies on a BIG-IP ASM device
 digital-dev/log4j-cve-2021-44228-remediation
This powershell script is intended to be used by anyone looking to remediate the Log4j Vulnerability within their environment. It can target multiple…
 chandru-gunasekaran/log4j-fix-cve-2021-44228
Windows Batch Scrip to Fix the log4j-issue-CVE-2021-44228