
synology-nas-cli
 aa22396584/synology-nas-cli
nas: a zero-dependency Python CLI + MCP server for Synology DSM 7. One-command audit and fix for the C3RB3R / .L0CK3D ransomware campaign; hand it to…
ai-securityauthenticationconfiguration-auditing+9
aa22396584/synology-nas-clinas: a zero-dependency Python CLI + MCP server for Synology DSM 7. One-command audit and fix for the C3RB3R / .L0CK3D ransomware campaign; hand it to…
 abraxas/signal-server-dropwizard-admin
Signal-Server v20261007.0.0 - High - Remote - Privilege leftover - unauth Dropwizard admin :8081
 burjoy/cve-2024-40275_scanner
Scanner for CVE-2024-40725 Apache HTTP Server source-code disclosure; probes direct and subrequest paths, fingerprints affected versions, and outputs…
 olafhartong/mde-auditcheck
MDE relies on some of the Audit settings to be enabled
 george0papasotiriou/cve-2026-21018-opc-ua-authentication-bypass-via-none-security-policy
Proof-of-concept exploit for OPC UA authentication bypass using None security policy, including a simulated server to demonstrate unauthorized…
 george0papasotiriou/cve-2026-22004-git-lfs-pointer-poisoning-supply-chain-
Proof-of-concept for Git LFS pointer poisoning, with Bash and Python scripts that create a malicious repository, simulate a rogue LFS server, and…
 george0papasotiriou/cve-2026-22007-ntp-monlist-amplification-over-ipv6
Python PoC for CVE-2026-22007: NTP monlist amplification over IPv6, including a simulated vulnerable server and spoofed UDP reflection attack.
 sibersan/web-server-audit_cve-2026-42945
Trigger-aware web server CVE audit for nginx and Apache. Goes beyond version matching by checking whether the vulnerable code path is actually…
 fazmin/vcenter-server-workaround-script-cve-2021-44228
Script - Workaround instructions to address CVE-2021-44228 in vCenter Server
 slicingmelon/haproxy-cve-2023-45539-poc
HAProxy-CVE-2023-45539-PoC
 oscerd/cve-2026-40022
Reproducer for CVE-2026-40022: Apache Camel camel-platform-http-main authentication bypass on non-root context paths
 xiaoxiaoranxxx/cve-2025-56815
Datart 1.0.0-rc.3 is vulnerable to Directory Traversal in the POST /viz/image interface, since the server directly uses MultipartFile.transferTo() to…
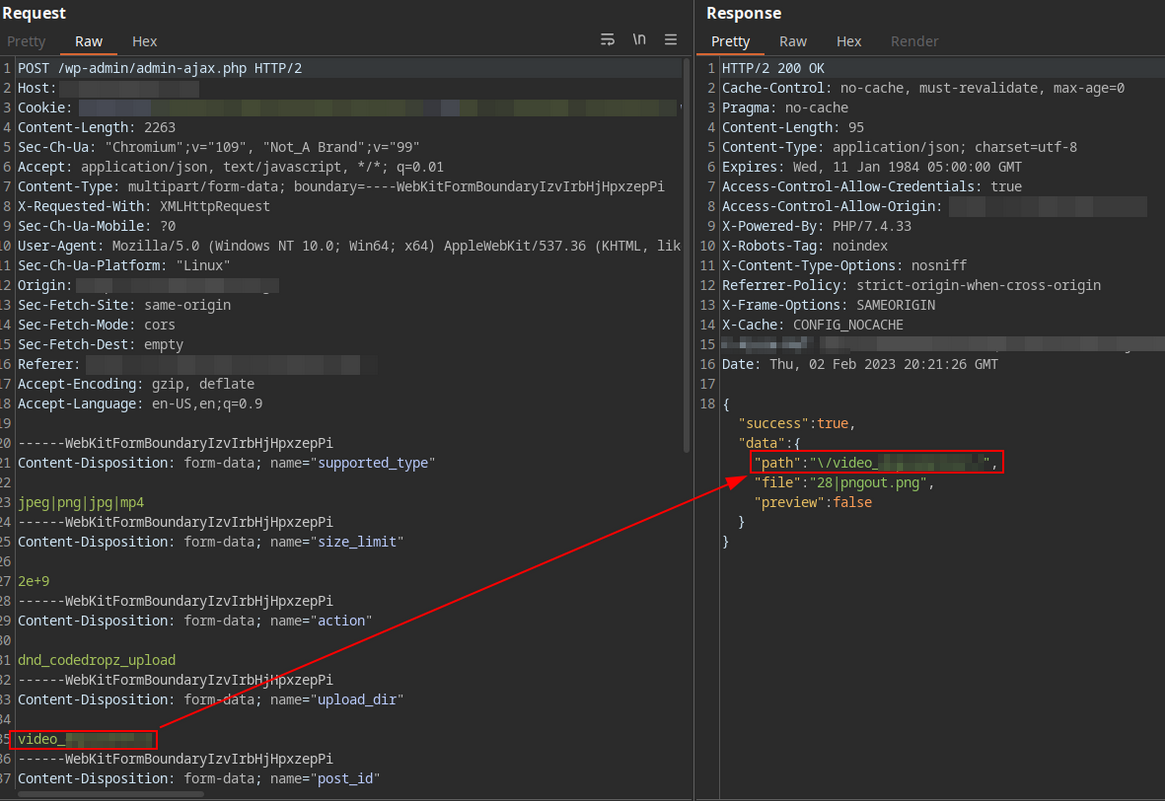 nickguitar/drag-and-drop-multiple-file-uploader-pro-path-traversal
Drag and Drop Multiple File Uploader PRO - Contact Form 7 v5.0.6.1 Path Traversal (CVE-2023-1112)
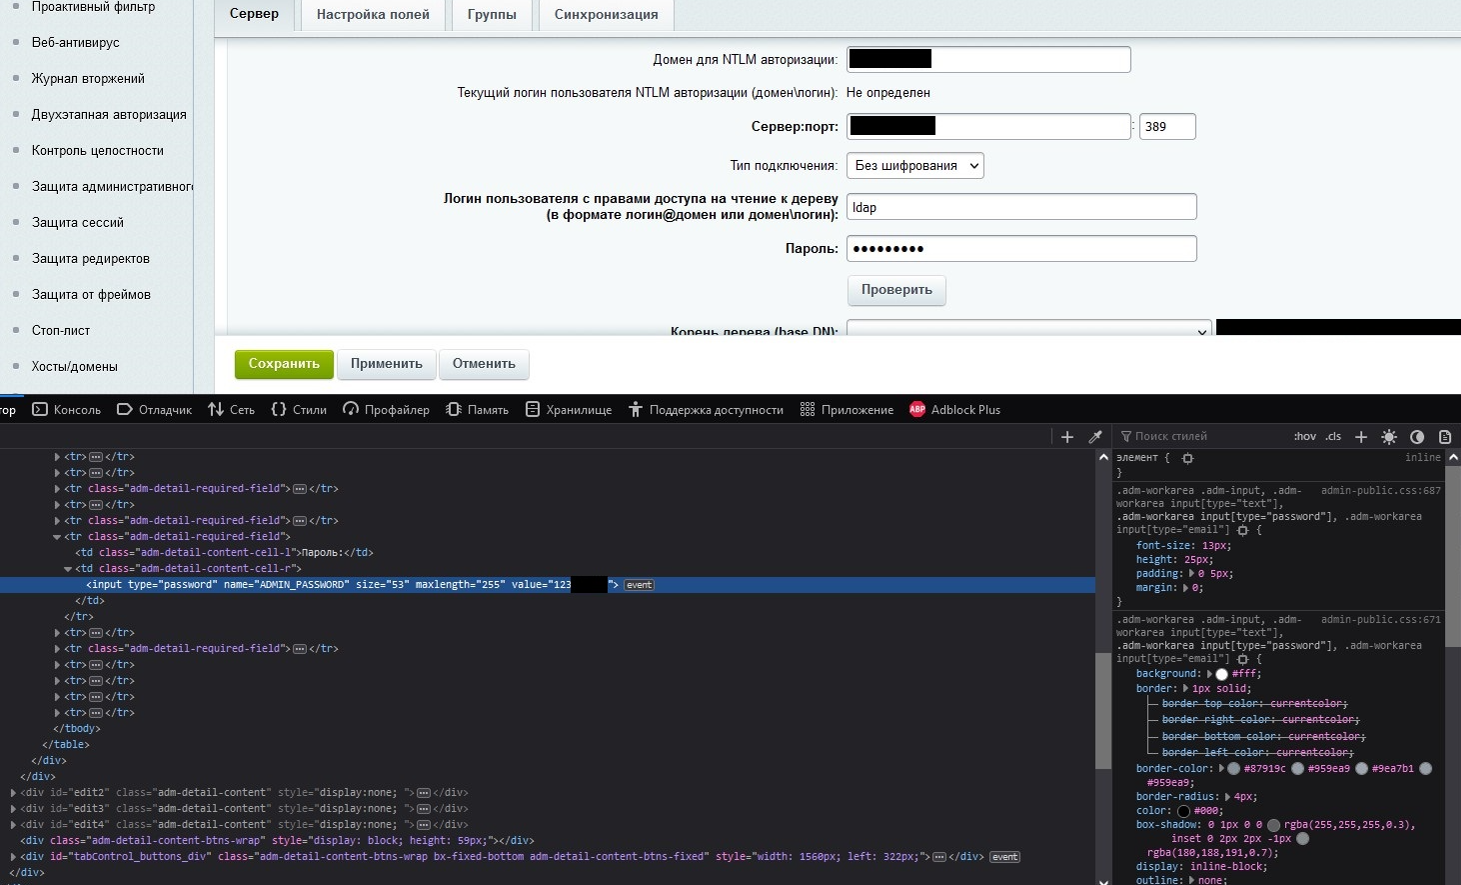 secware-ru/cve-2022-43959
Bitrix Vulnerability CVE-2022-43959
 networksecure/cve-2020-14066
Proof-of-concept exploit for CVE-2020-14066 targeting insecure permissions in Icewarp Email Server 12.3.0.1, enabling privilege escalation or…
 simeononsecurity/cve-2020-1350-fix
A registry-based workaround can be used to help protect an affected Windows server, and it can be implemented without requiring an administrator to…
 perufitlife/dotclaude-security
Scan a repo's .claude/ config (settings.json hooks, MCP servers, env, allowed-tools) for the RCE & API-key-exfiltration footguns (CVE-2025-59536,…
 josephgodwinkimani/cloudpanel-2.4.2-cve-2024-44765-recovery
How to "recover" a CloudPanel server affected by the CVE-2024-44765 vulnerability