
kafka-connect-filestream-win
 abraxas/kafka-connect-filestream-win
Kafka Connect 4.3.1 - High - Windows FileStream classpath leftover - unauth file read/write
exploitationinformation-gatheringlabs-practice+5
1
abraxas/kafka-connect-filestream-winKafka Connect 4.3.1 - High - Windows FileStream classpath leftover - unauth file read/write
 vulnz/sast
Free offline SAST engine for CI/CD: AST and cross-file taint analysis, secret detection with live validation, SCA/CVE, IaC misconfiguration, and…
 mondoohq/cnspec
An open source, cloud-native security to protect everything from build to runtime
 complianceascode/content
Generates SCAP, Ansible, Bash, and CEL security content for compliance evaluation and automated hardening across Linux hosts, containers, and…
 prapul1/vulnhub-dc1-writeup
VulnHub DC-1 boot-to-root — exploiting CVE-2018-7600 (Drupalgeddon2) for RCE, extracting DB credentials from settings.php, forging admin password…
 synacktiv/kcmapper
KcMapper is a security auditing tool for Keycloak. It exports your Keycloak configuration (realms, clients, users, roles, etc.) into a Neo4j graph…
 jp1337/easywall
Web interface for the nftables firewall on Linux, written in Go. The apply undoes itself after 120 seconds unless you confirm it — you cannot lock…
 jenderal92/s3-bucket-take-0v3r
AWS AMAZON S3 Bucket Takeover Scanner & Claim Tool
 owasp/serverless-goat
OWASP ServerlessGoat: a serverless application demonstrating common serverless security flaws
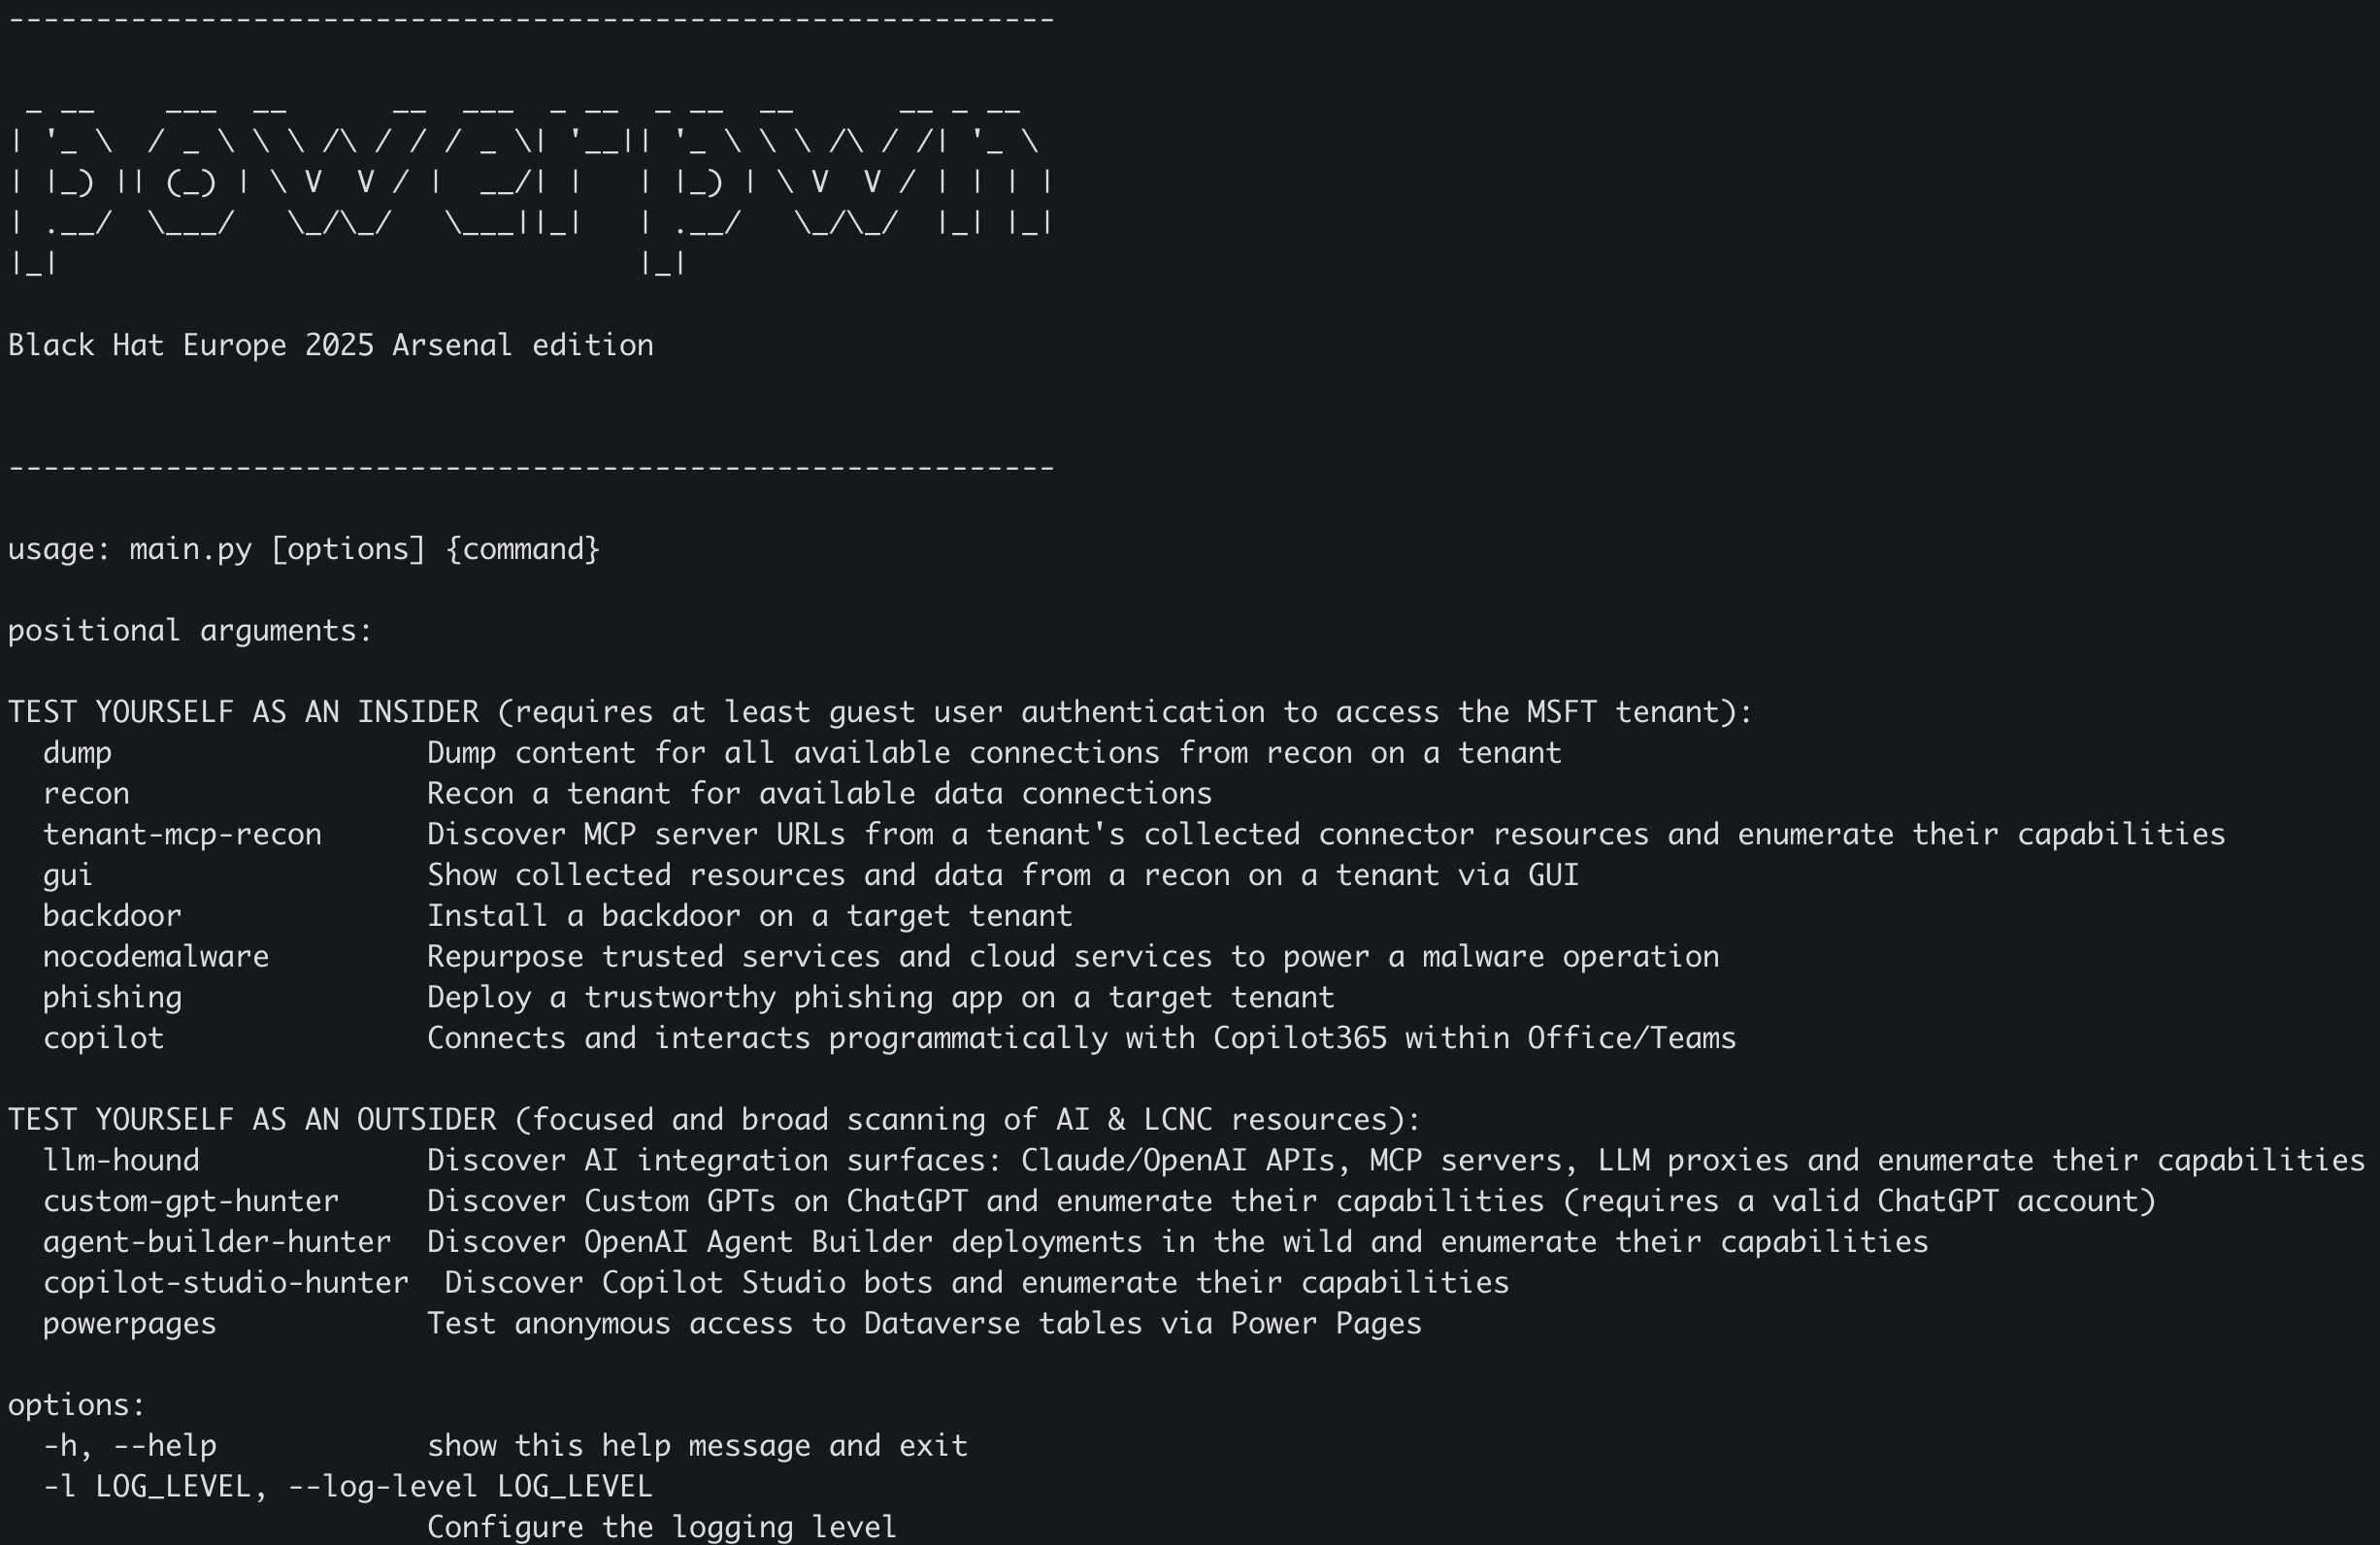 mbrg/power-pwn
An offensive/defense security toolset for discovery, recon and ethical assessment of AI Agents
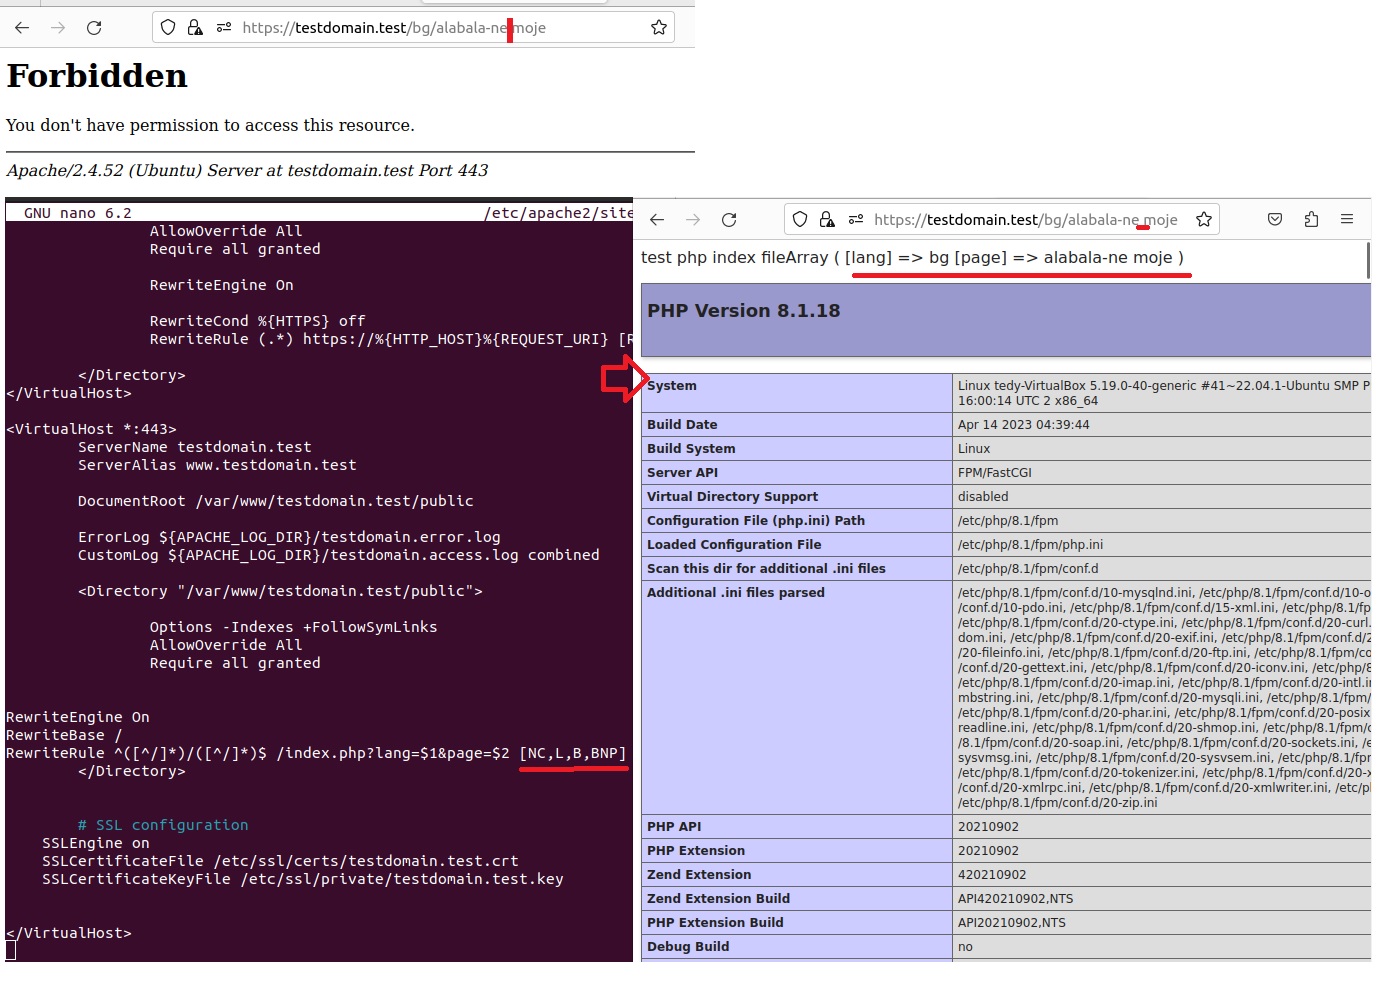 tbachvarova/linux-apache-fix-mod_rewrite-spaceinurl
Fix URL containing SPACES after Apache upgrade CVE-2023-25690
 coldfusionx/cve-2021-34429
POC for CVE-2021-34429 - Eclipse Jetty 11.0.5 Sensitive File Disclosure
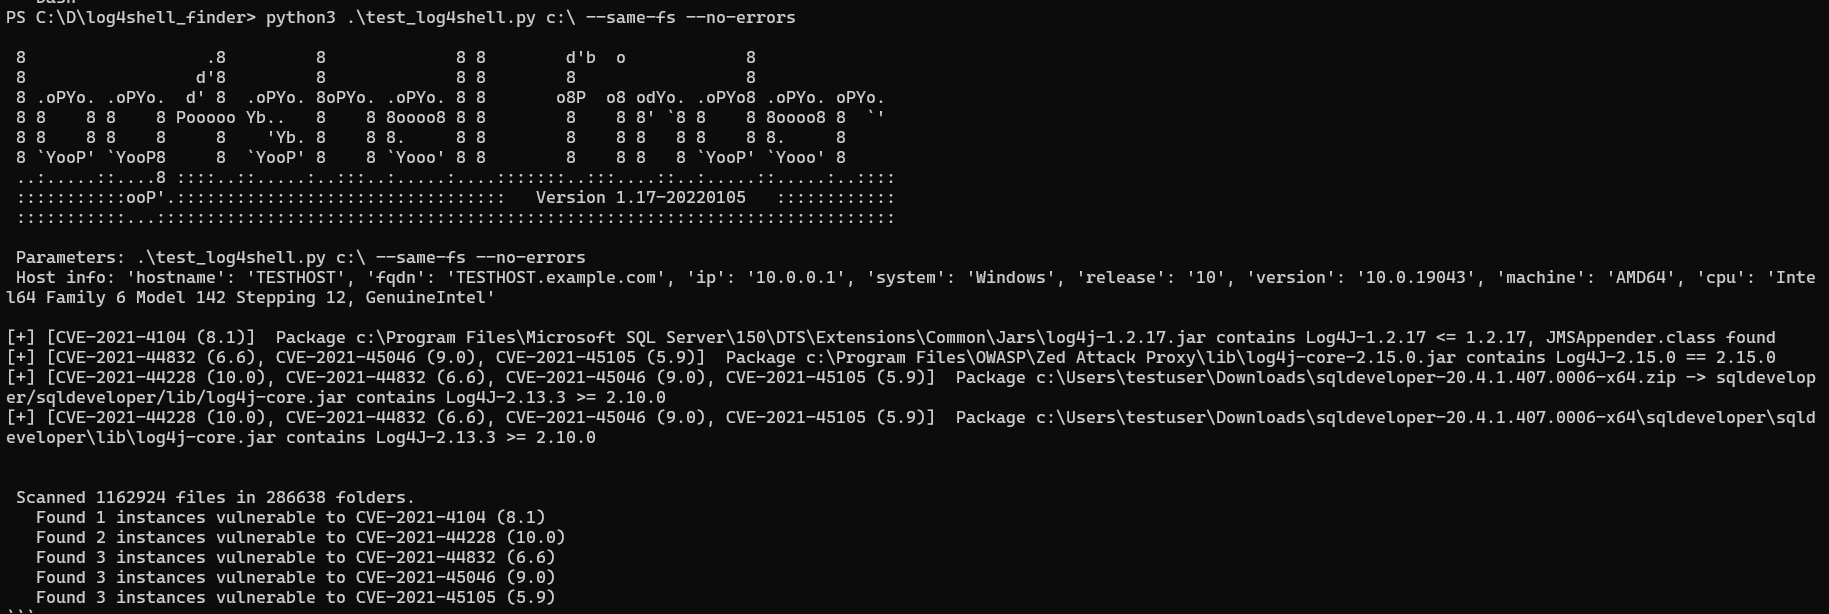 hynekpetrak/log4shell-finder
Fastest filesystem scanner for log4shell (CVE-2021-44228, CVE-2021-45046) and other vulnerable (CVE-2017-5645, CVE-2019-17571, CVE-2022-23305,…
 selectel/mks-copy-fail-mitigation
DaemonSet с реализацией временной меры для митигации уязвимости Copy Fail (CVE-2026-31431)
 yagnikkrish/metasploitable-penetration-testing-lab
Controlled penetration testing lab demonstrating CVE-2011-2523 exploitation and mitigation techniques.
 name/log4j-remediation
Discover and remediate Log4Shell vulnerability [CVE-2021-45105]
 lukepasek/log4jjndilookupremove
A simple script to remove Log4J JndiLookup.class from jars in a given directory, to temporarily protect from CVE-2021-45046 and CVE-2021-44228.