

semgrep-rules
 elttam/semgrep-rules
Static analysis security rules for vulnerability detection and audit-focused code review across Java, Go, Python, C#, Kotlin, PHP, Kubernetes, and…
cloud-infrastructure-securitycode-analysiscontainer-security+6
elttam/semgrep-rulesStatic analysis security rules for vulnerability detection and audit-focused code review across Java, Go, Python, C#, Kotlin, PHP, Kubernetes, and…
 akabe1/oauthscan
Burp Suite Extension useful to verify OAUTHv2 and OpenID security
 mogwaisec/mjet
Mogwai Java Management Extensions (JMX) Exploitation Toolkit
 schierlm/javapayload
JavaPayload is a collection of pure Java payloads to be used for post-exploitation from pure Java exploits or from common misconfigurations (like not…
 ioactive/jdwp-shellifier
Exploitation script for exposed Java Debug Wire Protocol (JDWP) services, enabling pentesters to inject Java code and execute arbitrary OS commands…
 nccgroup/vcg
VisualCodeGrepper - Code security scanning tool.
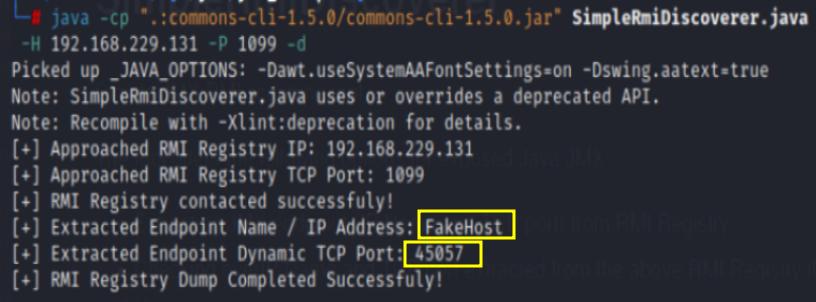 marcin-wolak/simplermidiscoverer
Simple JMX RMI scanning tool
 shoucheng3/esapi__esapi-java-legacy_cve-2022-24891_2-2-3-1
OWASP Enterprise Security API library providing security controls for Java web applications, including authentication, access control, input…
 shoucheng3/nahsra__antisamy_cve-2017-14735_1-5-6
Java library for fast, configurable HTML sanitization from untrusted sources. Uses policy-driven scanning to remove malicious JavaScript and CSS,…
 creeperhost/log4jpatcher
A mitigation for CVE-2021-44228 (log4shell) that works by patching the vulnerability at runtime. (Works with any vulnerable java software, tested…
 owasp/java-html-sanitizer
Takes third-party HTML and produces HTML that is safe to embed in your web application. Fast and easy to configure.
 jenkinsci-cert/security-3430
Java agent that transforms a vulnerable class to block exploitation of CVE-2024-43044 in Jenkins controllers, with optional forced shutdown on…
 irgoncalves/irule-cve-2022-22965
F5 BIG-IP iRule providing mitigation against CVE-2022-22965 (Spring4Shell) remote code execution vulnerability in Java Spring Framework. Tested on…
 unix13/metasploitable2
PHP-CGI-REMOTE_CVE-2012-1823, UnrealIRCd, MySQL, PostgreSQL and SSH bruteforce, VSFTPD2.3.4, samba CVE-2007-2447, JAVA RMI Server, distcc daemon,…
 dannyendortest/java-vulnerable
EXPOSURE demo target: Tomcat (CVE-2016-0714) + Apache Rave (CVE-2013-1814) + Java filter-padding deps
 1lann/log4shelldetect
Rapidly scan filesystems for Java programs potentially vulnerable to Log4Shell (CVE-2021-44228) or "that Log4j JNDI exploit" by inspecting the class…
 pwcno-cto/cve-2021-21234
Directory traversal vulnerability in the spring-boot-actuator-logview library
 corgea/sighthound
Tree-sitter based static vulnerability scanner with pattern matching and taint-flow analysis for multi-language source code. Outputs findings as…