

ats-realip-plugin-acl
 abraxas/ats-realip-plugin-acl
Apache Traffic Server 10.2.0 - High - Remote - Privilege leftover - realip PLUGIN ACL fail-open
authentication-authorizationlabs-practicemisconfiguration+4
abraxas/ats-realip-plugin-aclApache Traffic Server 10.2.0 - High - Remote - Privilege leftover - realip PLUGIN ACL fail-open
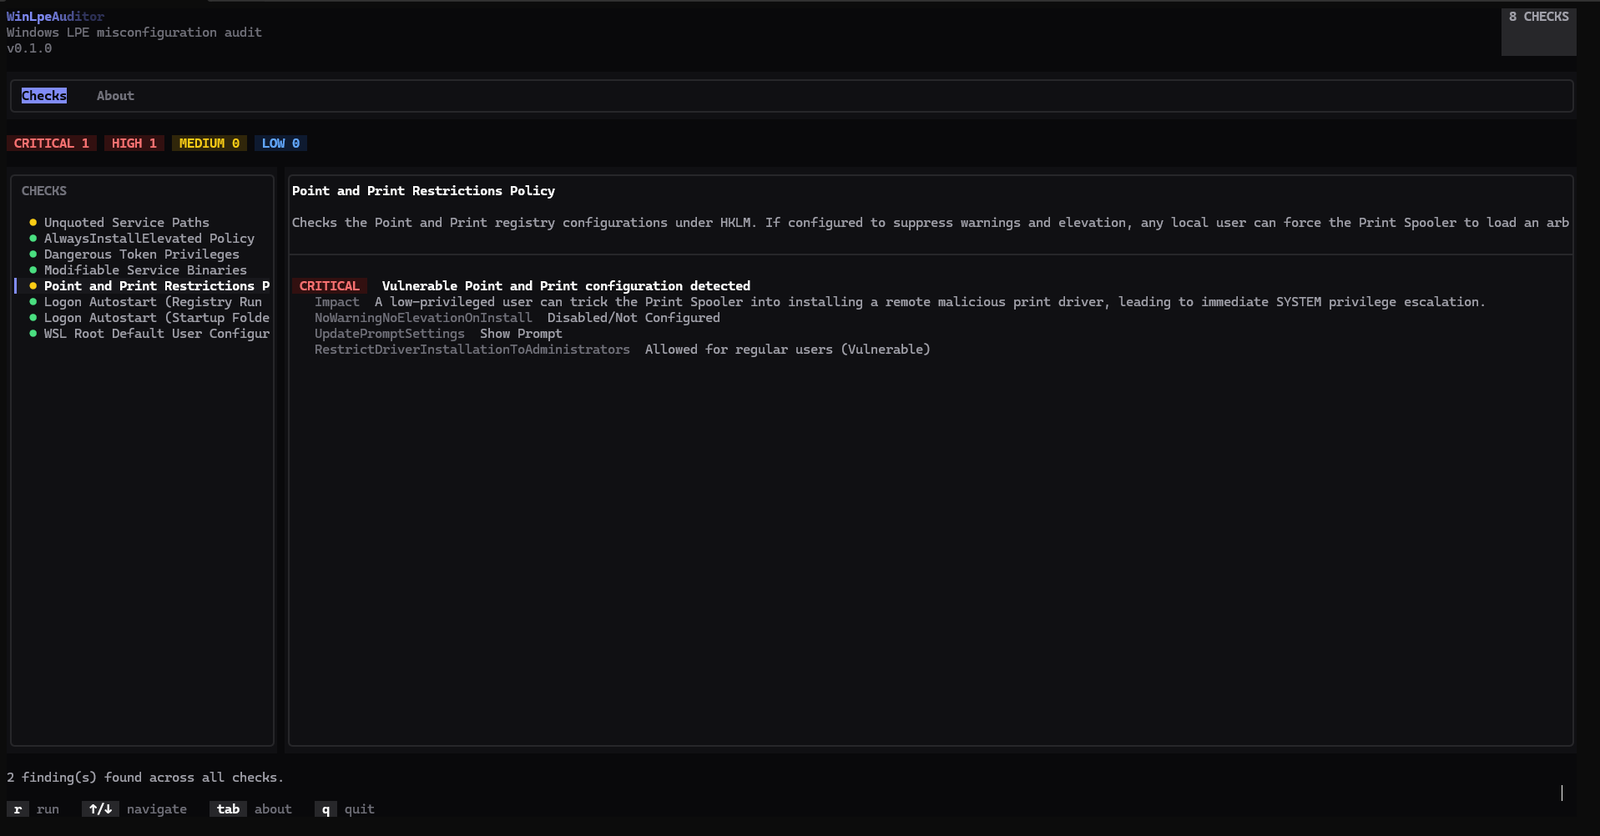 0xby7eme/windows-lpe-auditor
A small Windows local-privilege-escalation (LPE) misconfiguration auditor with a terminal UI, built with C++20 and FTXUI
 abraxas/spark-rest-auth-bypass
Apache Spark 4.2.0 - High - Remote - Privilege leftover - standalone REST ignores spark.authenticate
 hasanuyarrr/cve-2026-18783-trex-mes-uygulamalarinda-yetkisiz-nesne-erisimi
Advisory for CVE-2026-18783: missing server-side authentication on TREX MES /api/GetDataJSON3 allows unauthenticated data queries and arbitrary SQL…
 bombobombone/cve-2026-73317
Proof-of-concept exploit and technical write-up for CVE-2026-73317, an authorization bypass in XenForo allowing limited admins to approve content as…
 bombobombone/cve-2026-73318
Proof-of-concept exploit for XenForo CVE-2026-73318, an authorization bypass allowing ACP administrators to trigger site-wide policy re-agreement.…
 g0w6y/cve-2026-21994
Proof-of-concept exploit for CVE-2026-21994, demonstrating unauthenticated admin session forgery via a hardcoded Flask SECRET_KEY and SSH host…
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 ac8999/cve-2026-27344
Missing Authorization in inseriswiss inseri core inseri-core allows Exploiting Incorrectly Configured Access Control Security Levels.This issue…
 scipag/hardeningkitty
HardeningKitty - Checks and hardens your Windows configuration
 renniepak/cspbypass
CSPBypass.com, a tool designed to help ethical hackers bypass restrictive Content Security Policies (CSP) and exploit XSS (Cross-Site Scripting)…
 dz-y/azure-apim-dev-portal-signup-bypass
Python script to bypass Azure APIM signup when UI is disabled, this is different from the CVE-2025-66390 as it does not require you to setup anything…
 george0papasotiriou/cve-2026-21017-ldap-anonymous-bind-privilege-escalation
Python proof-of-concept for LDAP anonymous bind privilege escalation, simulating insecure ACLs to create admin users via unauthenticated LDAP binds.
 george0papasotiriou/cve-2026-21018-opc-ua-authentication-bypass-via-none-security-policy
Proof-of-concept exploit for OPC UA authentication bypass using None security policy, including a simulated server to demonstrate unauthorized…
 george0papasotiriou/cve-2026-5556-kubernetes-admission-controller-bypass-via-case-sensitivity
Exploit PoC and vulnerable admission webhook for CVE-2026-5556, demonstrating Kubernetes admission controller bypass via case-sensitive pod name…
 randomrobbiebf/cve-2024-12252
SEO LAT Auto Post <= 2.2.1 - Missing Authorization to File Overwrite/Upload (Remote Code Execution)
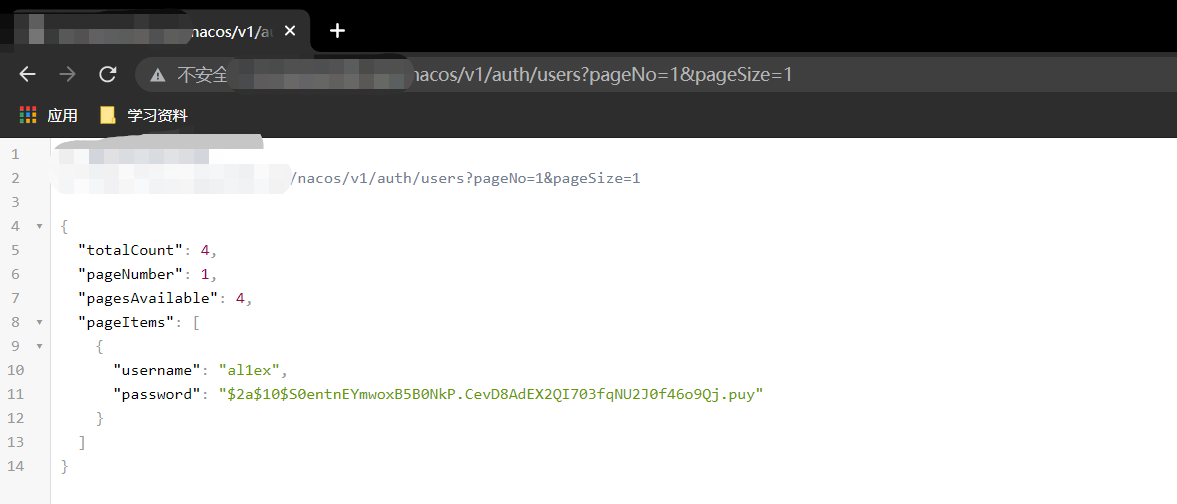 al1ex/alibab-nacos-unauthorized-reset-pwd
Alibab-Nacos-Unauthorized-Reset PWD
 synacktiv/sccmsecrets
SCCMSecrets.py aims at exploiting SCCM policies distribution for credentials harvesting, initial access and lateral movement.