
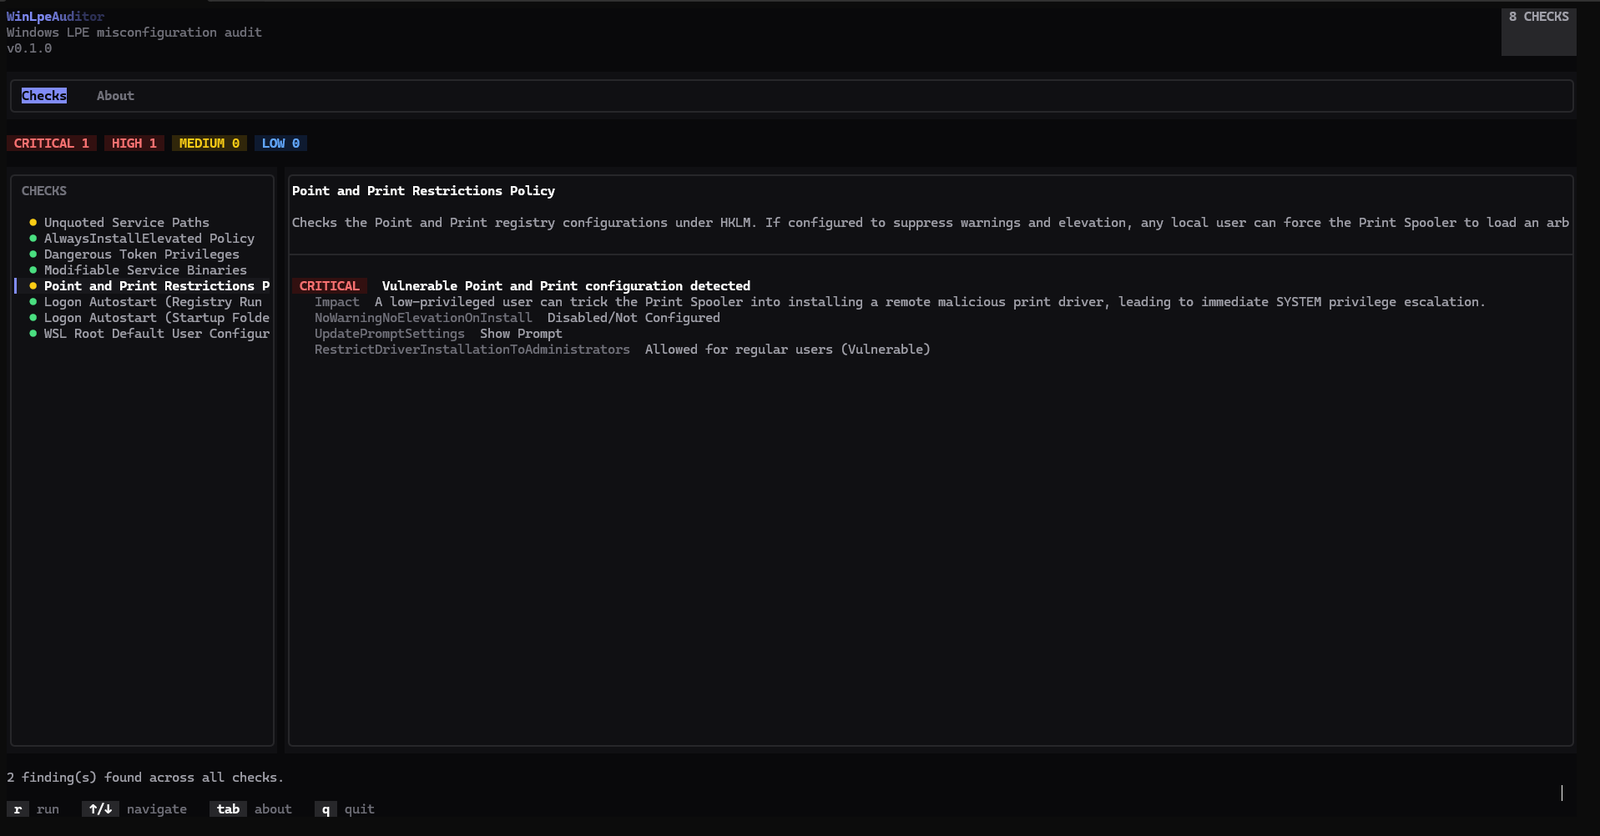
Windows-LPE-Auditor
 0xby7eme/windows-lpe-auditor
A small Windows local-privilege-escalation (LPE) misconfiguration auditor with a terminal UI, built with C++20 and FTXUI
authentication-authorizationconfiguration-auditingdefensive-tools+5
2
0xby7eme/windows-lpe-auditorA small Windows local-privilege-escalation (LPE) misconfiguration auditor with a terminal UI, built with C++20 and FTXUI
 ekitji/siem
Curated SIEM queries and techniques for offensive discovery of Windows privilege escalation, misconfigured ACLs, services, scheduled tasks, and…
 bombobombone/cve-2026-73318
Proof-of-concept exploit for XenForo CVE-2026-73318, an authorization bypass allowing ACP administrators to trigger site-wide policy re-agreement.…
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 moniik/poc_salesforce_lightning
Academic purposes only. Attack against Salesforce lightning with guest privilege.
 coffinxp/google-api-key-scanner
Validates Google Maps API keys against 21 endpoints, revealing exposed services with PoC URLs, proxy support, and quiet mode for focused auditing.
 nccgroup/sadcloud
A tool for standing up (and tearing down!) purposefully insecure cloud infrastructure
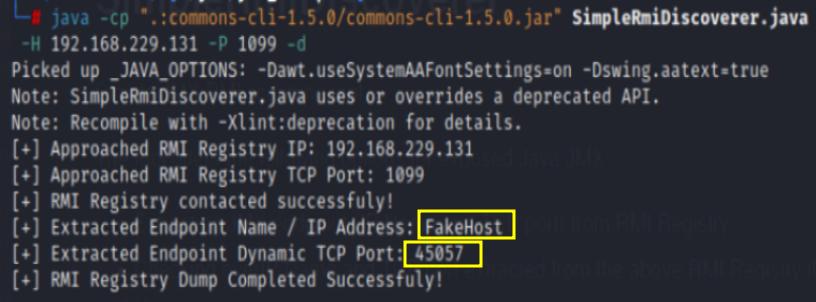 marcin-wolak/simplermidiscoverer
Simple JMX RMI scanning tool
 synacktiv/kcmapper
KcMapper is a security auditing tool for Keycloak. It exports your Keycloak configuration (realms, clients, users, roles, etc.) into a Neo4j graph…
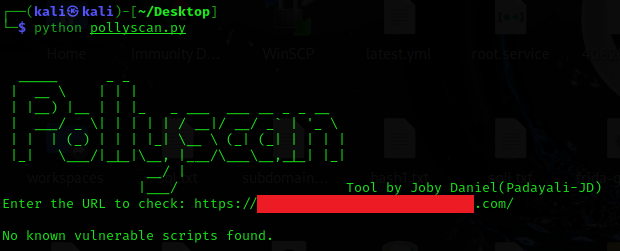 padayali-jd/pollyscan
A specialized vulnerability scanner designed to detect CVE-2024-38526, the Polyfill.io Supply Chain Attack, helping organizations identify and…
 farenhytee/database-sentinel
Open-source security audits for Supabase: a read-only MCP server, a CLI agent and a Claude Skill. Finds RLS misconfigurations, exposed keys and risky…
 yaupunal/cve-2025-55182-scanner
CVE-2025-55182-scanner with 2 different method
 nanitor/log4fix
Detect and fix log4j log4shell vulnerability (CVE-2021-44228)
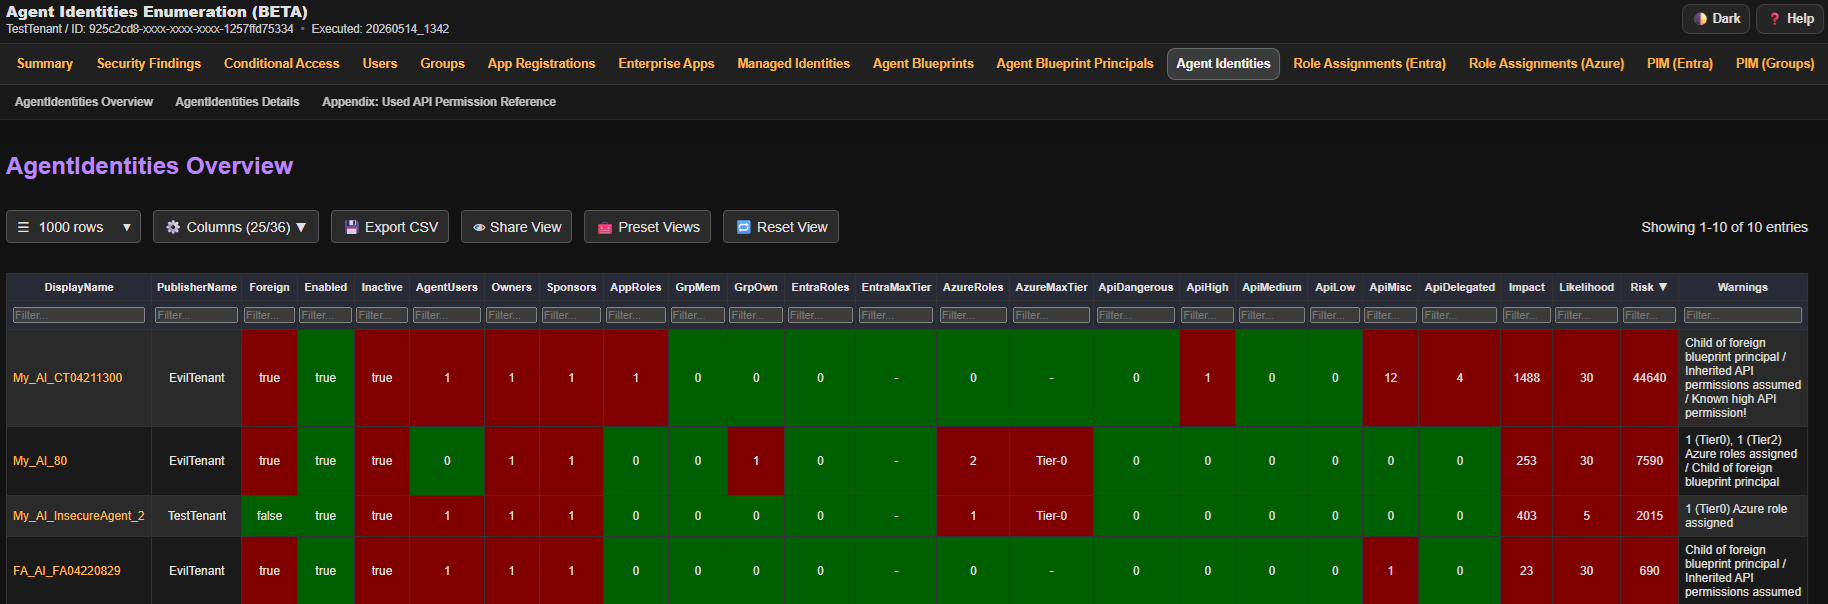 compasssecurity/entrafalcon
A lightweight PowerShell tool for assessing the security posture of Microsoft Entra ID environments. It helps identify privileged objects, risky…
 spring-io/cve-2022-22976-bcrypt-skips-salt
CLI tool to detect and update BCrypt password hashes with vulnerable work factor 31, integrating with Spring Security databases for CVE-2022-xxxx…
 ricardojoserf/cve-2019-19033
CVE-2019-19033 description and scripts to check the vulnerability in Jalios JCMS 10 (Authentication Bypass)
 mbadanoiu/cve-2019-12409
CVE-2019-12409: RCE Vulnerability Due to Bad Defalut Config in Apache Solr