
DB_Audit_Research
 mthamil107/db_audit_research
Self-Defeating Audits: reproducible lab showing a low-privilege PostgreSQL role reversibly blinding a trigger-based auditor + poisoning attribution…
adversarial-attackdatabase-securitydefensive-tools+4
mthamil107/db_audit_researchSelf-Defeating Audits: reproducible lab showing a low-privilege PostgreSQL role reversibly blinding a trigger-based auditor + poisoning attribution…
 moniik/poc_salesforce_lightning
Academic purposes only. Attack against Salesforce lightning with guest privilege.
 subat0mik/misconfiguration-manager
Misconfiguration Manager is a central knowledge base for all known Microsoft Configuration Manager tradecraft and associated defensive and hardening…
 pentestpad/subzy
Subdomain takeover vulnerability checker
 neffisback/wsuks
Automating the MITM attack on WSUS
 george0papasotiriou/cve-2026-22007-ntp-monlist-amplification-over-ipv6
Python PoC for CVE-2026-22007: NTP monlist amplification over IPv6, including a simulated vulnerable server and spoofed UDP reflection attack.
 george0papasotiriou/cve-2026-5556-kubernetes-admission-controller-bypass-via-case-sensitivity
Exploit PoC and vulnerable admission webhook for CVE-2026-5556, demonstrating Kubernetes admission controller bypass via case-sensitive pod name…
 owasp/owasp-subtractive-hardening-top-10
The OWASP Subtractive Security Top 10 Project is an initiative to identify, document, and promote the highest-impact opportunities for reducing cyber…
 saykino/cve-2026-31283
Documentation of CVE-2026-31283: an email bombing vulnerability in Totara LMS's forgot password API due to missing rate limiting, allowing…
 padayali-jd/pollyscan
A specialized vulnerability scanner designed to detect CVE-2024-38526, the Polyfill.io Supply Chain Attack, helping organizations identify and…
 edgarloyola/cve-2021-40904
Proof-of-concept for remote code execution in CheckMK Raw Edition 1.5.0–1.5.0p25 via misconfigured Dokuwiki embedded application allowing PHP code…
 yolabingo/wordpress-fix-cve-2018-6389
Apache RewriteRule to mitigate potential DoS attack via Wordpress wp-admin/load-scripts.php file
 nickops87/spring4shell-python-firewall-poc
Proof-of-Concept (POC) of a simple firewall in Python designed to mitigate the Spring4Shell (CVE-2022-22965) RCE attack by inspecting and blocking…
 saykino/cve-2025-66838
Documentation of CVE-2025-66838: a rate-limiting vulnerability in ARIS file upload API allowing authenticated remote attackers to cause denial of…
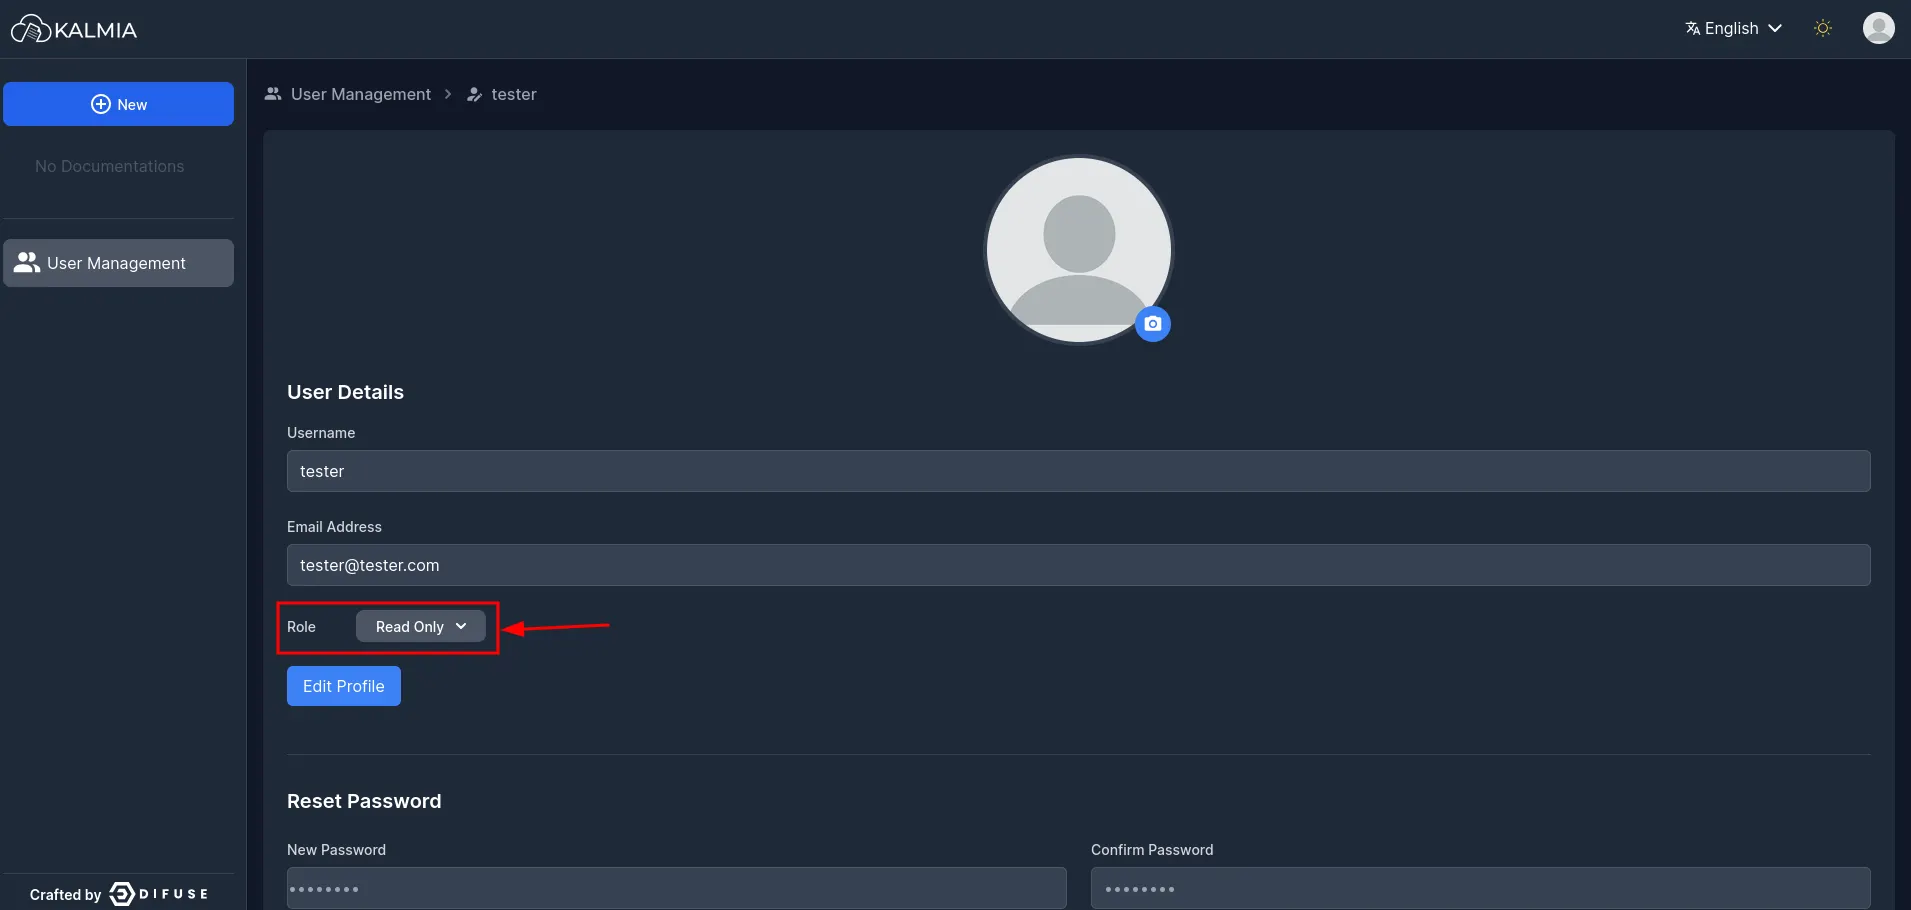 noxurge/cve-2025-65900
DifuseHQ Kalmia CMS version 0.2.0 contains an Incorrect Access Control vulnerability in the /kal-api/auth/users API endpoint. Due to insufficient…
 zsxen/cve-2025-1974
Windows 11-first educational lab for studying CVE-2025-1974 in ingress-nginx. Provides safe attack emulation and defense validation with local…
 essafar/firewall-rules
Firewall rules to mitigate a zero-day vulnerability malware attack (CVE-2022-22965), known as Spring4Shell
 naveenbana5250/cve-2023-34362-defense-package
Threat-Informed Detection & Mitigation Package for MOVEit Transfer Vulnerability